
 Threat Lifecycle Services Market | 2026-2036
Threat Lifecycle Services Market Size, Share, and Industry Trends Forecast 2026-2036
Threat Lifecycle Services Market Analytics
The EU NIS2 Directive is repositioning how European critical infrastructure operators procure security services, mandating 24-hour incident reporting and supply-chain risk audits. CrowdStrike Holdings Inc. leverages its native cloud architecture to capture managed detection contracts from regulated utilities. IBM anchors enterprise trust through its X-Force incident response retainers and threat intelligence feeds. Palo Alto Networks competes by bundling endpoint protection with automated SOC workflows for mid-market buyers.
Threat Lifecycle Services encompass continuous monitoring, detection engineering, incident containment, and post-breach forensics delivered across on-premise, cloud, and hybrid estates. These services integrate telemetry from SIEM platforms, endpoint agents, and network sensors to reduce mean-time-to-detect and mean-time-to-respond metrics for enterprise security teams. Cloud-Based deployment is pulling ahead as organizations retire legacy SIEM infrastructure and adopt elastic data lake architectures for threat hunting. Incident Response retainers command premium pricing due to finite certified responder capacity and strict SLA penalties. AI & Machine Learning segments within threat detection are expanding fastest as vendors automate alert triage and false-positive reduction at scale.
The SEC cybersecurity disclosure rules, EU NIS2 Directive, and Japan's METI critical infrastructure guidelines are converging to mandate board-level accountability for breach reporting and third-party risk management. These frameworks are elevating Compliance Monitoring and Vulnerability Assessment from optional consulting to contractual requirements in vendor and insurance agreements. Stakeholders must weigh whether to build in-house SOC capabilities or outsource to managed services providers as regulatory complexity outpaces internal staffing pipelines.
Market Dynamics
The EU NIS2 Directive and SEC cybersecurity disclosure rules are compressing procurement cycles for managed detection services as board-level accountability mandates force faster vendor selection and stricter SLA enforcement across critical infrastructure sectors.
Growth Catalysts
- Cloud migration acceleration:Organizations retiring legacy SIEM infrastructure are adopting elastic data lake architectures that require continuous threat hunting and managed detection engineering.
- EU NIS2 Directive mandates:European critical infrastructure operators must now maintain 24-hour incident reporting and supply-chain risk audits, converting compliance monitoring from optional consulting to contractual requirements.
- Attack surface expansion:Financial services firms widening their digital footprints are expanding procurement of managed detection and response services to cover hybrid cloud estates.
Market Restraints
- Certified responder scarcity:Finite global capacity of incident response professionals constrains service delivery and drives premium pricing for retainer contracts.
- Legacy system integration friction:On-premise security infrastructure in regulated utilities creates technical debt that slows cloud-native service deployment.
- False-positive management burden:Alert fatigue from poorly tuned detection rules consumes analyst hours and degrades mean-time-to-respond metrics.
Strategic Opportunities
- AI-driven alert triage automation:Machine learning convergence with SIEM platforms is creating white space for vendors that automate false-positive reduction at scale.
- Mid-market bundling:Automated SOC workflows combined with endpoint protection represent an underpenetrated segment between enterprise retainers and basic monitoring.
- Japan METI critical infrastructure guidelines:Regulatory tailwinds in Japanese energy and transportation sectors are elevating demand for localized incident response capabilities.
Industry Challenges
- Detection engineering talent gap:Shortage of professionals capable of building and tuning detection rules for cloud-native environments limits service scalability.
- Multi-telemetry correlation complexity:Integrating endpoint agents, network sensors, and cloud workload protection across hybrid estates requires specialized architecture expertise.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Threat Lifecycle Services Market |
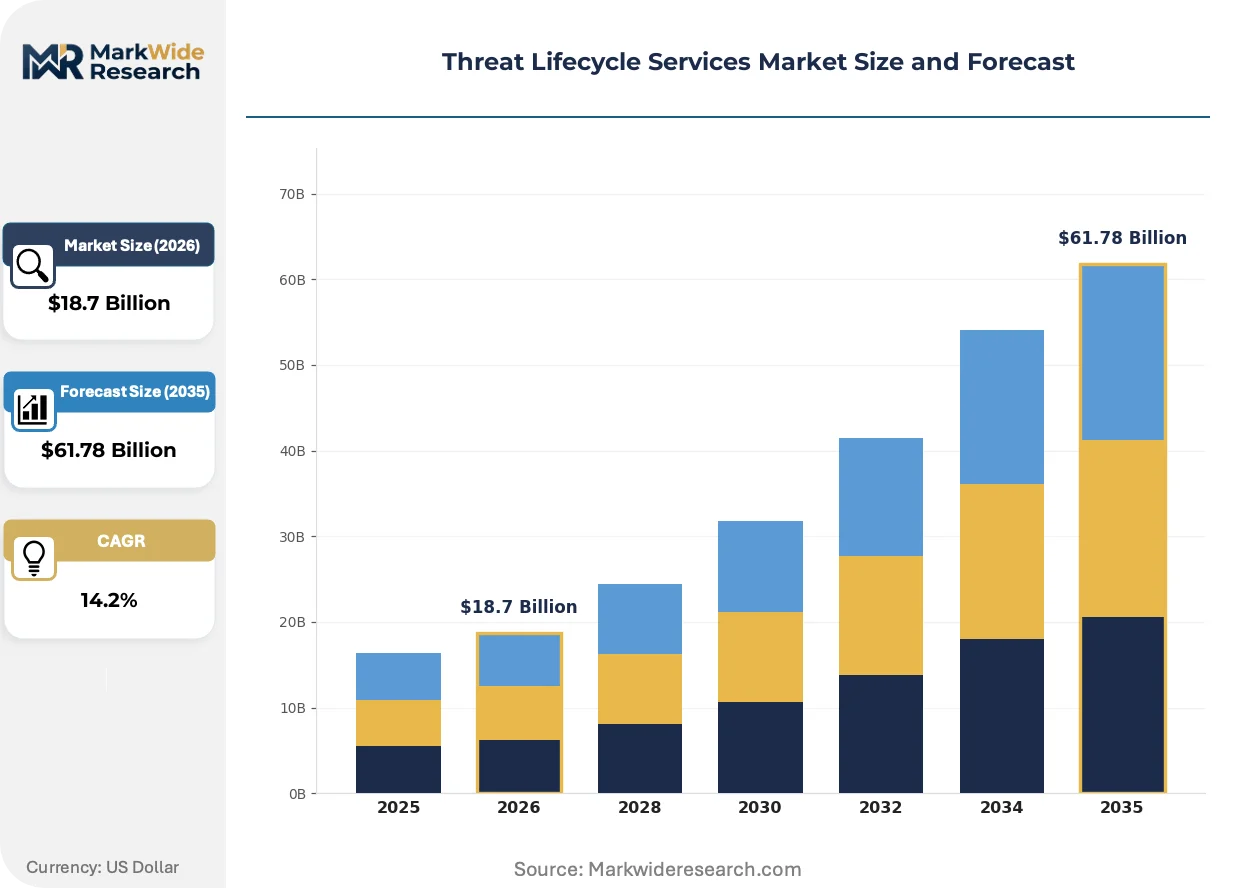
| Market Size in 2026 | $18.7 Billion |
| Market Size in 2035 | $61.78 Billion |
| CAGR (2026 – 2036) | 14.2% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Threat Detection, Incident Response, Vulnerability Assessment, Compliance Monitoring Deployment Model: On-Premise, Cloud-Based, Hybrid, Managed Services End User: Healthcare, Financial Services, Government, Retail Technology: AI & Machine Learning, SIEM, Endpoint Detection, Intrusion Detection Systems |
| Companies Covered | CrowdStrike Holdings Inc., SecureWorks, IBM, Cisco Systems Inc., Palo Alto Networks, Fortinet Inc., Google LLC, Symantec Corporation, Recorded Future Inc., Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Threat Lifecycle Services Market Evolving Landscape
Threat detection architectures are pivoting from rule-based correlation to behavioral analytics and autonomous response, reshaping how security operations centers prioritize alerts and contain breaches.
Extended detection and response platforms are integrating telemetry from endpoints, networks, cloud workloads, and identity systems into unified data lakes. Large enterprises with mature security teams are adopting these architectures fastest, compressing the traditional SIEM replacement cycle from five years to eighteen months. Native cloud architecture is integrating elastic storage and serverless compute to enable threat hunting across petabyte-scale datasets without capital infrastructure commitments.
The EU AI Act's risk classification framework for automated decision-making systems is mandating algorithmic transparency in security tools deployed across European critical infrastructure. Vendors must now document training data provenance and model performance metrics for high-risk AI applications including autonomous threat containment. Financial services and healthcare operators in Germany and France are responding by demanding audit trails for machine-generated alerts before contract execution.
Retainer-based incident response procurement is displacing hourly consulting arrangements as breach notification deadlines tighten. CISOs at utilities and energy firms are negotiating fixed-fee contracts with guaranteed response times rather than variable cost structures. This behavioral shift is most visible in the United States where SEC disclosure rules impose strict timelines for material incident reporting.
Threat Lifecycle Services Market Segmentation
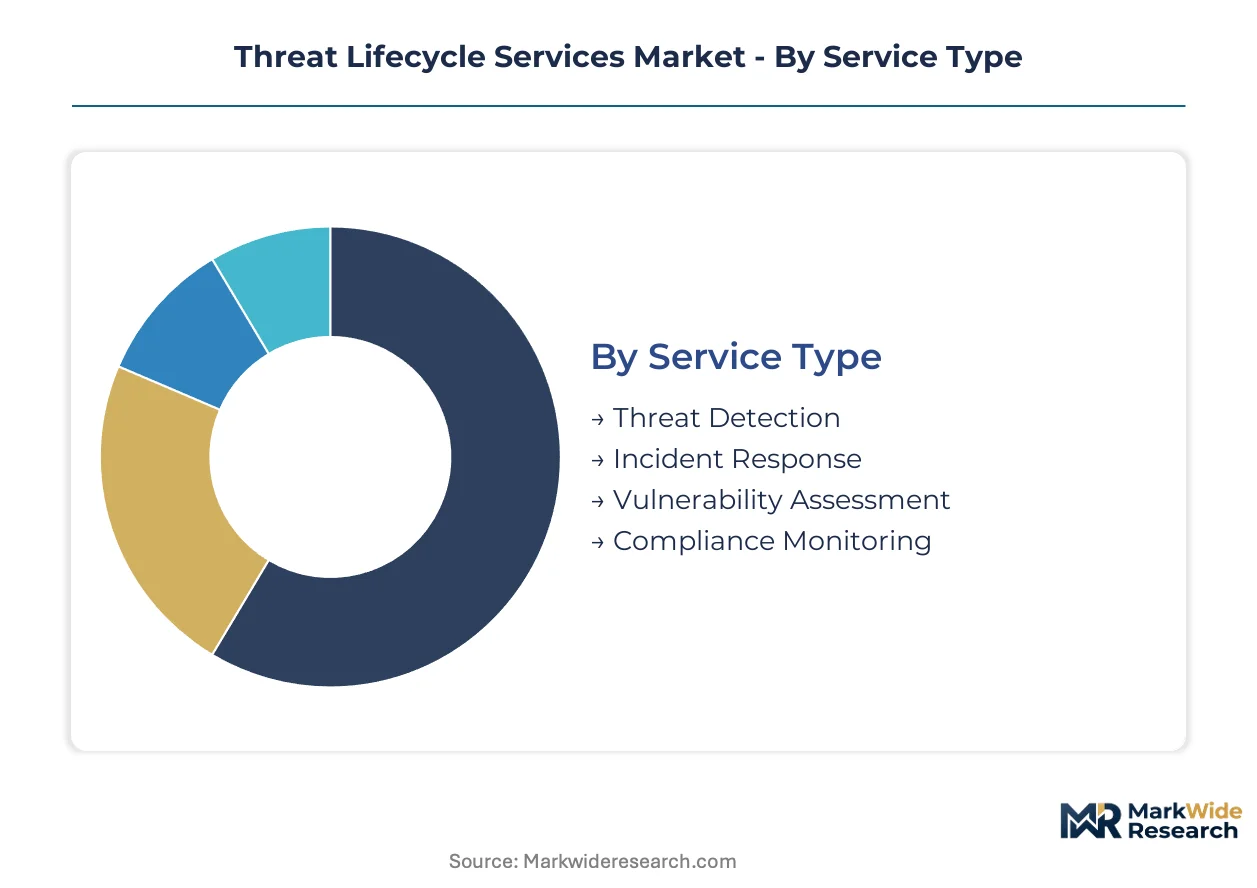
Threat lifecycle services fragment across four operational dimensions that determine procurement priorities and vendor selection criteria. Service type and deployment model together dictate pricing architecture, while end-user verticals and underlying technology platforms shape solution configuration and compliance obligations.
Service Type:
Volume concentrates in continuous monitoring contracts, while premium pricing attaches to discrete response capabilities with guaranteed SLAs.
- Threat Detection:Continuous monitoring and alert generation across endpoint, network, and cloud telemetry streams. Financial services firms in Germany and the United States dominate procurement as attack surface expansion forces 24/7 coverage mandates.
- Incident Response:Retainer-based breach containment and forensic investigation with guaranteed response windows. Scarcity of certified responders drives premium pricing, with utilities and energy operators under SEC disclosure rules converting from hourly to fixed-fee structures.
- Vulnerability Assessment:Systematic identification and prioritization of security weaknesses across hybrid estates.
- Compliance Monitoring:Continuous audit readiness and regulatory alignment verification for NIS2 and sector-specific frameworks.
Mature deployment sits with Threat Detection. Newer deployment is concentrated in Incident Response as breach notification deadlines compress procurement cycles.
Deployment Model:
Customer technical maturity and capital constraints split procurement between self-managed infrastructure and outsourced operations.
- Cloud-Based:Elastic data lake architectures enabling petabyte-scale threat hunting without capital infrastructure. Organizations retiring legacy SIEM infrastructure are adopting these architectures fastest, compressing replacement cycles from multi-year to eighteen-month horizons.
- Managed Services:Fully outsourced security operations with defined SLAs and staffing guarantees. Mid-market buyers lacking internal SOC capabilities are driving expansion here as regulatory complexity outpaces hiring pipelines.
- On-Premise:Self-hosted security infrastructure retained in regulated environments with strict data sovereignty requirements.
- Hybrid:Coordinated protection across cloud and on-premise estates with unified visibility.
Established deployment sits with On-Premise among regulated utilities. Steepest expansion trajectory belongs to Cloud-Based as elastic storage eliminates capital commitments.
End User:
Regulatory enforcement intensity and breach cost exposure concentrate demand in two verticals with divergent procurement patterns.
- Financial Services:Banks, insurers, and payment processors facing SEC disclosure rules and systemic risk oversight. Attack surface expansion across digital banking channels is widening procurement of managed detection and response services.
- Government:Federal, state, and local agencies with classified and citizen data protection mandates. Supply-chain risk audits and third-party vetting requirements are elevating compliance monitoring to contractual necessity.
- Healthcare:Hospitals, payers, and life sciences operators subject to HIPAA breach notification and patient data protection.
- Retail:Merchants and e-commerce platforms managing payment card environments and customer PII.
Deepest solution maturity sits with Financial Services. Fastest policy-driven expansion is concentrated in Government as critical infrastructure designations broaden.
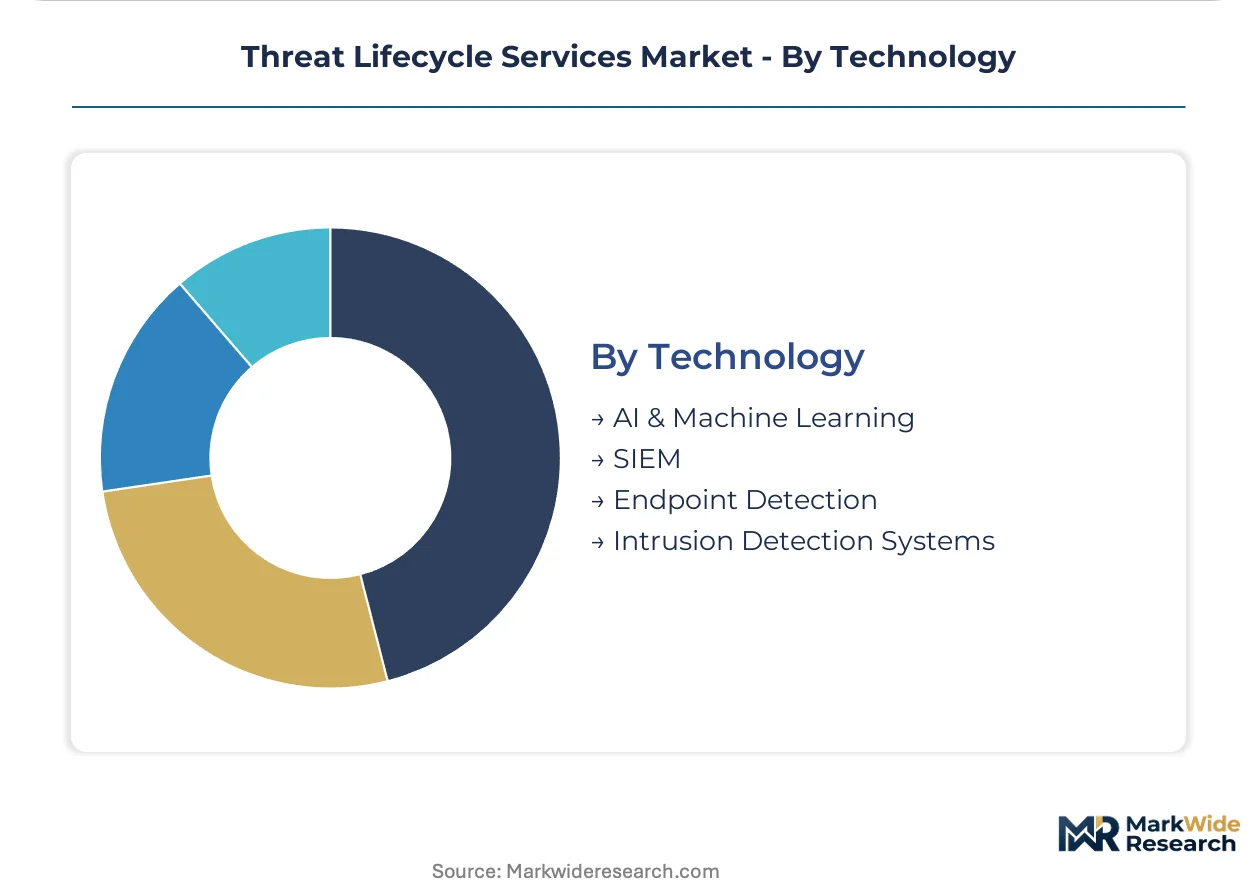
Technology:
Automation capability and integration breadth separate platforms that reduce analyst burden from those that amplify it.
- AI & Machine Learning:Automated alert triage, behavioral analytics, and false-positive reduction at scale. The EU AI Act's risk classification framework is mandating algorithmic transparency documentation before contract execution in German and French critical infrastructure.
- SIEM:Centralized log aggregation and correlation across security telemetry sources. Legacy deployments face replacement pressure as elastic data lakes displace fixed-capacity architectures.
- Endpoint Detection:Agent-based monitoring of laptops, servers, and mobile devices for malicious activity.
- Intrusion Detection Systems:Network-layer signature and anomaly detection for perimeter and east-west traffic.
Platform consolidation sits with SIEM. Gaining share fastest is AI & Machine Learning as vendors automate detection engineering and response orchestration.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The Washington D.C. metropolitan corridor anchors North American procurement of threat lifecycle services as federal agencies and defense contractors concentrate security operations near policy centers.
United States
Financial services firms in New York and technology companies in Silicon Valley are expanding managed detection contracts as SEC disclosure rules compress response timelines. The Securities and Exchange Commission mandates four-day material incident reporting for publicly traded firms. Chicago-based utilities are converting from hourly consulting to fixed-fee incident response retainers.
Germany
Critical infrastructure operators in the Ruhr industrial basin and Bavarian manufacturing corridors are procuring 24-hour monitoring services under EU NIS2 Directive obligations. The Federal Office for Information Security enforces supply-chain risk audits for energy and transport sectors. Frankfurt's financial district is demanding algorithmic transparency documentation before AI-powered security tool deployment.
Japan
Energy and transportation operators in Tokyo and Osaka are elevating procurement of localized incident response capabilities under METI critical infrastructure guidelines. The Ministry of Economy, Trade and Industry mandates sector-specific security standards for designated operators. Nagoya's automotive manufacturing cluster is integrating cloud-native threat hunting across hybrid production networks.
United Kingdom
London-based financial institutions and Edinburgh's asset management sector are expanding compliance monitoring services ahead of NIS2 transposition into UK law. The National Cyber Security Centre mandates incident reporting thresholds for critical national infrastructure. Manchester's growing technology corridor is adopting elastic data lake architectures for threat detection.
France
Healthcare operators in Paris and Lyon are demanding audit trails for machine-generated alerts under EU AI Act risk classification frameworks. The National Commission for Information Technology and Civil Liberties enforces algorithmic transparency for automated security decisions. Toulouse's aerospace and defense cluster is procuring managed services for export-controlled data environments.
Threat Lifecycle Services Market Competitive Landscape
The competitive structure tilts toward cloud-native specialists with native platform architectures. Consolidation pressure is intensifying as enterprise buyers favor integrated detection and response capabilities over point solutions. Three archetypes dominate: endpoint-centric platforms with managed service overlays, legacy technology conglomerates with incident response retainers, and network-security vendors bundling SOC automation. M&A activity targets detection engineering talent pools, while strategic partnerships address multi-telemetry integration complexity.
Within the cloud-native tier, CrowdStrike Holdings Inc. and Palo Alto Networks exemplify platform-first positioning, while IBM anchors enterprise trust through professional services depth. CrowdStrike's native cloud architecture captures managed detection contracts from regulated utilities seeking elastic scalability. Palo Alto Networks occupies a position in automated SOC workflows for mid-market buyers. IBM represents the legacy conglomerate archetype, leveraging X-Force incident response retainers and threat intelligence feeds to maintain enterprise relationships.
| Leading Market Players |
|---|
| CrowdStrike Holdings Inc. |
| SecureWorks |
| IBM |
| Cisco Systems Inc. |
| Palo Alto Networks |
| Fortinet Inc. |
| Google LLC |
| Symantec Corporation |
| Recorded Future Inc. |
| Others |
Value Network & Pricing Analysis
Financial services CISOs in New York and Frankfurt anchor pricing power for threat lifecycle services, converting procurement from hourly consulting to fixed-fee retainers with guaranteed response SLAs. This buyer concentration forces vendors to absorb talent scarcity costs while competing on outcome-based metrics rather than time-and-materials billing.
Pricing Analysis
Outcome-based pricing anchored to mean-time-to-detect and mean-time-to-respond metrics dominates enterprise contracts, with premium tiers commanding guarantees below four-hour response windows. Price differentiation hinges on responder certification density and AI-driven automation depth, with cloud-native platforms extracting margin advantages over legacy SIEM-dependent competitors. Pricing pressure stems from certified responder scarcity inflating delivery costs, while mid-market buyers lacking SOC staffing drive softness in automated monitoring tiers. Financial services firms under SEC disclosure rules exhibit lowest price sensitivity, accepting premium retainer structures to secure guaranteed capacity.
Supply Chain Analysis
Certified incident responder talent rests on concentrated training pipelines in the United States, United Kingdom, and Israel, with specialized forensics expertise concentrated among former intelligence community professionals. Service delivery draws from cloud infrastructure provisioned through hyperscaler data centers, proprietary threat intelligence feeds, and endpoint agent distribution networks. Single-source vulnerability sits with responder certification bodies controlling credential scarcity and pipeline velocity. Distribution runs through direct enterprise sales organizations and managed security service provider channel partnerships, with regulatory complexity favoring vertically integrated vendors over pure-play technology licensors.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Threat lifecycle services represent a consolidation play as regulatory compliance mandates compress procurement cycles and elevate scale requirements beyond mid-tier vendor capacity.
For Market Incumbents: To counter cloud-native platform entrants capturing managed detection contracts, incumbents must deepen responder certification pipelines through captive training academies and acquire specialized detection engineering boutiques to close talent gaps. Board-level accountability mandates under SEC and NIS2 frameworks favor vendors with proven incident response track records over point-solution specialists. For New Entrants and Emerging Players: Automated SOC workflow channels targeting mid-market manufacturers in Japan and Germany offer the most penetrable entry vector, with METI and NIS2 compliance gaps creating immediate demand for bundled endpoint protection and monitoring services. Partnering with regional systems integrators accelerates credibility establishment without building direct sales infrastructure. For Investors and Strategic Acquirers: The window for entry favors platforms with native cloud architecture and established responder benches, as talent scarcity and certification bottlenecks protect incumbent positions against pure-technology entrants. Detection engineering boutiques with vertical specialization in energy or healthcare compliance represent priority acquisition targets. Regulatory enforcement intensity across EU member states serves as the critical inflection signal for capacity expansion timing.| Strategic Initiative | Industry Significance |
|---|---|
| Responder Certification Pipeline Expansion | Captive training programs address scarcity constraining service delivery under NIS2 mandates. |
| AI-Driven Alert Triage Automation | Machine learning integration reduces analyst burden and improves mean-time-to-respond metrics for enterprise clients. |
| Vertical Specialization in Energy | Deep expertise in OT/IT convergence addresses critical infrastructure procurement under METI and SEC frameworks. |
| Cloud-Native Platform Migration | Elastic data lake architectures displace legacy SIEM infrastructure and compress replacement cycles. |
| Incident Response Retainer Consolidation | Fixed-fee structures with guaranteed SLAs displace hourly consulting as breach notification deadlines tighten. |
Research Methodology
Document review covered SEC cybersecurity disclosure filings, EU NIS2 implementation guidance, and METI critical infrastructure standards, complemented by interviews with CISOs at financial services firms, critical infrastructure operators, and managed security service providers. Secondary validation drew from hyperscaler security service announcements, threat intelligence platform disclosures, and certification body training statistics. Bottom-up service contract analysis and top-down regulatory impact modeling were triangulated to establish market sizing.
Cross-referencing historical managed security services adoption patterns against panel input from procurement officers and vendor executives shaped the analytical framework across the projection horizon. Segmentation dimensions modeled include service type, deployment architecture, end-user vertical, and underlying technology platform, with AI automation penetration and responder capacity constraints serving as key forecast inputs. CAGRs were derived from elasticity analysis of regulatory mandate timing and cloud migration velocity.
The model holds under sustained enforcement of SEC disclosure rules and NIS2 transposition timelines; deviation in regulatory delay or economic contraction affecting security budgets would shift service mix toward lower-cost automated tiers. A small set of triggers—certification body pipeline expansion, hyperscaler platform bundling strategies, and critical infrastructure designation expansion—warrants ongoing watch.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Critical Infrastructure Protection
Global Railway Platform Security Market
Critical Infrastructure Protection
Global Perimeter Protection Market
Critical Infrastructure Protection
Middle East Commercial Security Market
Critical Infrastructure Protection
Asia Pacific Tank Protection Market
Critical Infrastructure Protection
Tank Protection Market
Critical Infrastructure Protection
Counter Cyberterrorism Market
Critical Infrastructure Protection
UK Critical Infrastructure Protection Market
Critical Infrastructure Protection
Global High Integrity Pressure Protection System (HIPPS) Market
Critical Infrastructure Protection
Europe Tank Protection Market
Critical Infrastructure Protection
Tele Protection Market
Critical Infrastructure Protection
Global Threat Intelligence Platform Market
Critical Infrastructure Protection
Continuous Threat Exposure Management Market
Critical Infrastructure Protection
Middle East and Africa Pipeline Security Market
Critical Infrastructure Protection
Blast Resistant and Bulletproof Buildings Market
Critical Infrastructure Protection
Global Advanced Persistent Threat (APT) Protection Market
Critical Infrastructure Protection
Utilities Security Market