
 Cloud Security Gateway Market | 2026-2036
Cloud Security Gateway Market Size, Share, and Industry Trends Forecast 2026-2036
Cloud Security Gateway Market Analysis
ISO 27001 certification cycles are redrawing competitive boundaries in cloud security procurement. Palo Alto Networks leverages extensive firewall integration to sustain enterprise loyalty across hybrid environments. Zscaler anchors its position through cloud-native architecture that eliminates on-premise hardware dependencies. Check Point Software Technologies differentiates via unified threat prevention platforms that span SaaS, IaaS, and private cloud deployments.
A cloud security gateway functions as a policy enforcement point between enterprise networks and cloud service providers, inspecting encrypted traffic at line speed through TLS/SSL decryption while applying data loss prevention rules and access controls. The technology serves to centralize visibility and governance across dispersed cloud workloads without degrading application performance. Cloud-based deployment configurations now capture the fastest expansion as organizations abandon capital-intensive appliance models, while hybrid architectures retain stronghold status among regulated sectors requiring localized data residency. Threat detection services command premium pricing relative to employee training modules due to automated response capabilities and reduced mean-time-to-remediation.
The EU AI Act, GDPR, and NIS2 Directive collectively mandate auditable data flows and breach notification protocols that only certified gateway architectures can satisfy. HIPAA in the United States imposes comparable encryption and access logging standards on healthcare cloud migrations, while China's GB standards and MEE cybersecurity rules constrain foreign gateway vendors operating within domestic cloud ecosystems. Stakeholders must evaluate whether their gateway investments align with emerging cross-border data transfer restrictions before committing to multi-year platform contracts.
Market Dynamics
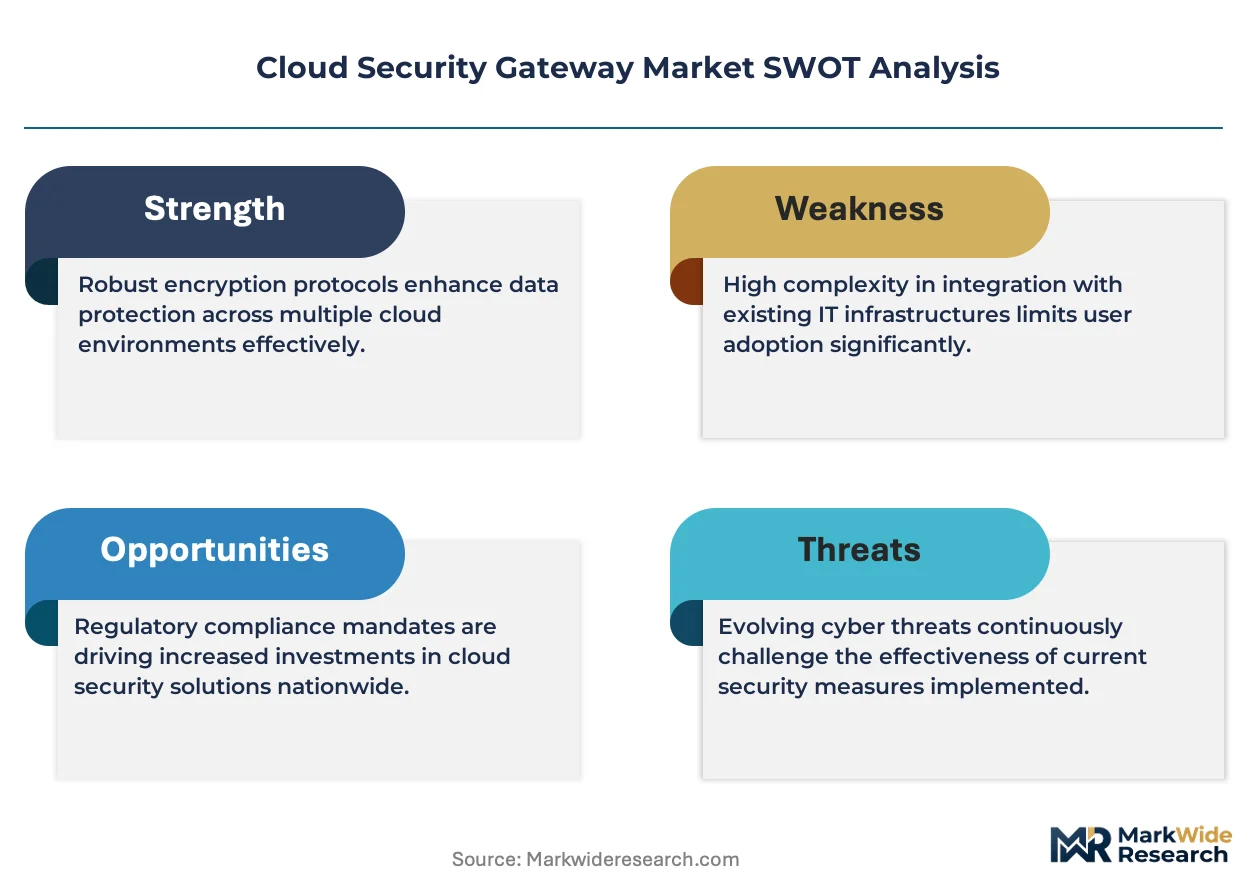
TLS/SSL decryption at line speed is compressing procurement cycles as financial services firms demand real-time policy enforcement without latency penalties. ISO 27001 certification timelines now gate vendor selection, favoring architectures that unify SaaS, IaaS, and private cloud governance under single audit trails.
Growth Catalysts
- EU AI Act compliance mandates:European enterprises must deploy auditable data flow architectures, accelerating gateway adoption in Germany, France, and the United Kingdom.
- Healthcare cloud migrations:HIPAA encryption and access logging standards in the United States require certified gateway solutions for sensitive workload protection.
- TLS/SSL inspection automation:Real-time encrypted traffic analysis eliminates performance trade-offs that previously slowed cloud adoption in regulated sectors.
Market Restraints
- Capital intensity of hybrid deployments:On-premise hardware requirements in regulated sectors drain IT budgets compared to pure cloud-native alternatives.
- China's GB standards and MEE rules:Foreign gateway vendors face operational constraints within domestic cloud ecosystems, limiting market access.
- Mean-time-to-remediation gaps:Automated threat response capabilities remain concentrated in premium service tiers, excluding mid-market buyers.
Strategic Opportunities
- Underpenetrated German manufacturing:Industrial IoT cloud migrations lack standardized gateway architectures, creating first-mover advantages for certified providers.
- NIS2 Directive tailwinds:Mandatory breach notification protocols across EU member states expand addressable market for unified threat prevention platforms.
- Edge-cloud convergence:Integration of zero-trust network access with 5G mobile edge computing opens new deployment configurations for distributed enterprises.
Industry Challenges
- Cross-border data transfer complexity:Emerging restrictions between EU, US, and Chinese jurisdictions complicate multi-year platform contract commitments.
- ISO 27001 certification timelines:Extended audit cycles delay vendor qualification, compressing implementation windows for time-sensitive cloud migrations.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cloud Security Gateway Market |
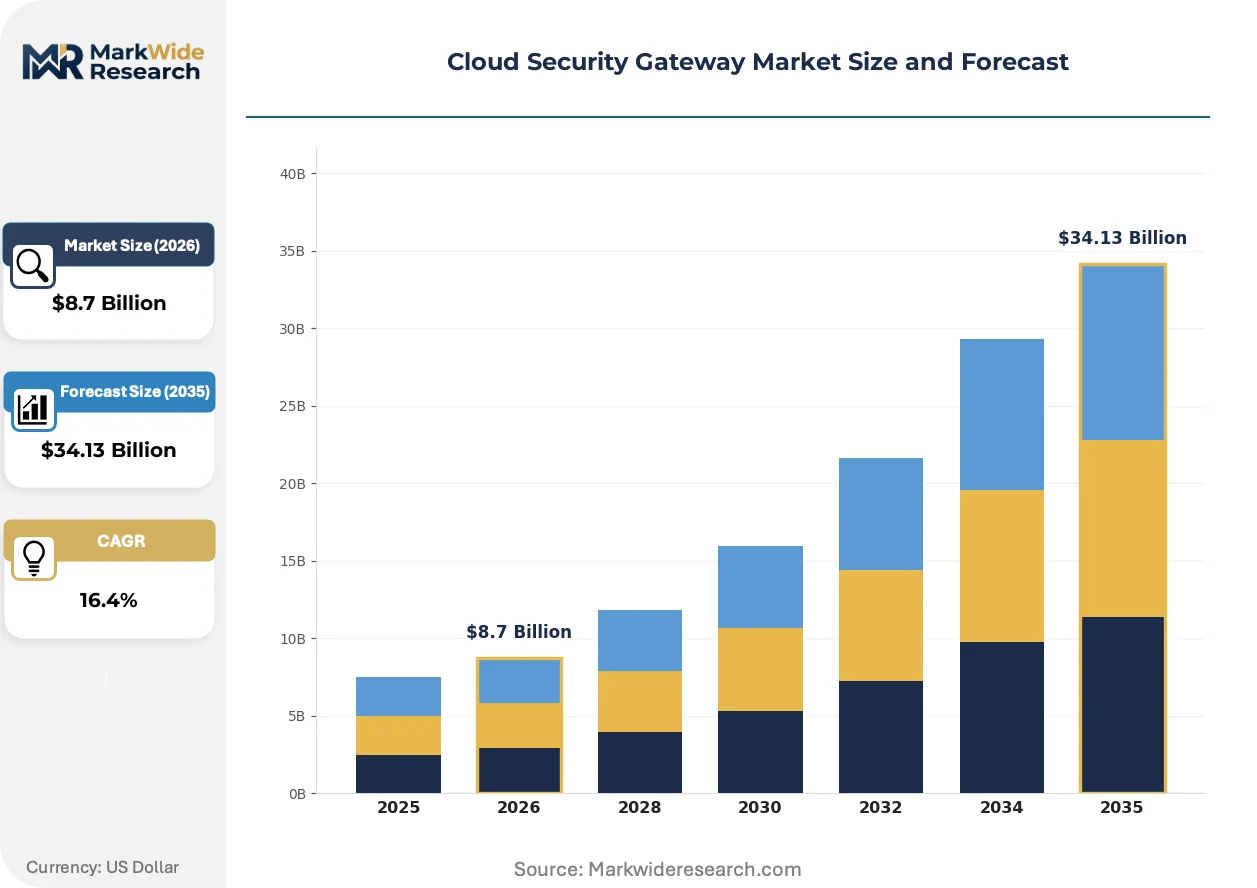
| Market Size in 2026 | $8.7 Billion |
| Market Size in 2035 | $34.13 Billion |
| CAGR (2026 – 2036) | 16.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premise, Cloud-Based, Hybrid, Multi-Cloud Service Type: Continuous Monitoring, Threat Detection, Incident Response, Employee Training End User: Healthcare, Finance, Education, Manufacturing Technology: Data Encryption, Firewall Protection, Malware Prevention, Access Control |
| Companies Covered | Fortinet, Cisco Systems, Palo Alto Networks, Check Point Software Technologies, Zscaler, Netskope, Forcepoint, McAfee, Microsoft Corporation, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cloud Security Gateway Market Emerging Trajectories
Cloud-native security architectures are compressing traditional appliance supply chains while regulatory mandates force convergence between data governance and access control technologies. Three distinct vectors are reshaping competitive positioning.
Hardware-based TLS/SSL decryption appliances is miniaturizing as software-defined alternatives embed directly into cloud service provider infrastructure. Financial services firms in London and Frankfurt are adopting these virtualized inspection engines to eliminate rack-space constraints. The technology is miniaturizing physical footprints while maintaining line-speed performance, collapsing the traditional three-tier procurement model into single-vendor cloud subscriptions.
GDPR's Article 44-49 cross-border transfer mechanisms are forcing architectural redesigns for any gateway handling EU personal data outside the bloc. Organizations must now demonstrate supplementary measures beyond standard contractual clauses, raising engineering requirements for encryption and access logging. Healthcare and banking verticals in Ireland and the Netherlands are responding by demanding sovereign cloud integrations that keep decryption keys within jurisdictional boundaries.
Consumption-based licensing is displacing perpetual appliance purchases as buyers prioritize operational expenditure alignment with actual traffic volumes. Managed security service providers in Singapore and Sydney are capturing this transition by bundling gateway capacity into broader cloud transformation contracts. Manufacturing conglomerates across Southeast Asia now treat security infrastructure as variable cost rather than capital commitment, compressing vendor sales cycles from quarters to weeks.
Cloud Security Gateway Market Segmentation
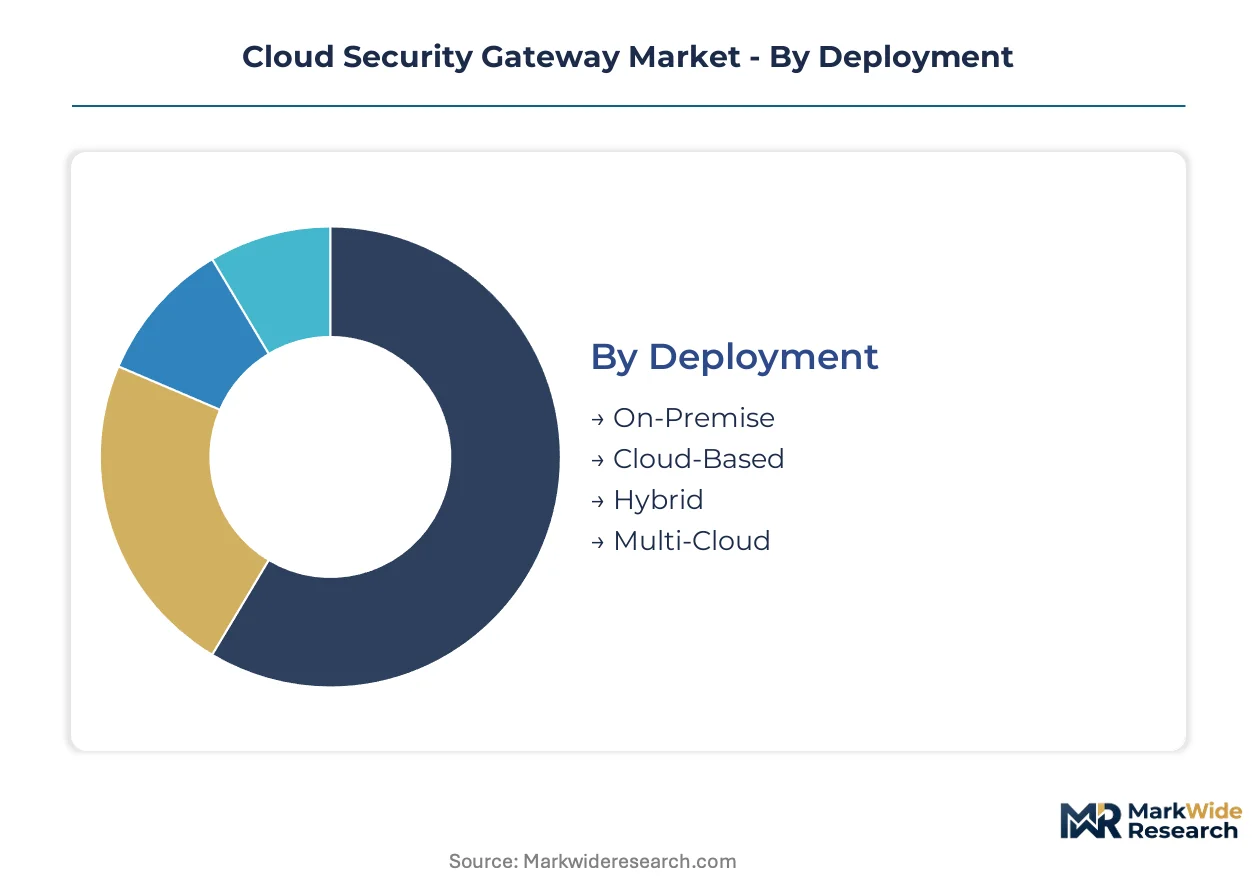
Deployment configurations determine capital commitment levels and compliance posture for cloud security gateway procurement. Service tier selection reflects organizational maturity in threat response automation. End-user verticals impose distinct regulatory constraints that reshape feature prioritization across vendor roadmaps.
Deployment:
Cloud-native architectures are displacing hardware-dependent alternatives fastest in mid-market financial services, while regulated healthcare and government buyers retain hybrid requirements for data sovereignty.
- Cloud-Based:Fully virtualized gateway stacks eliminate rack-space constraints and compress procurement cycles from quarters to weeks. Demand concentrates among Singapore and Sydney-based managed security service providers bundling capacity into broader transformation contracts, driven by operational expenditure alignment with actual traffic volumes.
- Hybrid:Split architectures maintain on-premise decryption appliances for sensitive workloads while cloud components handle routine traffic. German and French banking regulators mandate this configuration for audit trail continuity, though capital intensity drains IT budgets relative to pure cloud alternatives.
- On-Premise:Physical appliance deployments persist in Chinese domestic cloud ecosystems constrained by GB standards and MEE cybersecurity rules.
- Multi-Cloud:Unified policy enforcement across AWS, Azure, and Google Cloud environments addresses vendor lock-in concerns for large manufacturing conglomerates.
Cloud-based configurations gain share fastest; hybrid deployments retain revenue concentration among regulated verticals.
Service Type:
Automation depth separates premium tiers from commoditized offerings, with real-time response capabilities commanding pricing multiples over passive monitoring.
- Threat Detection:Machine-learning-powered inspection engines identify anomalous patterns in encrypted TLS/SSL traffic without decryption latency. London and Frankfurt financial services firms prioritize these capabilities for real-time policy enforcement, accepting premium pricing for reduced mean-time-to-remediation.
- Incident Response:Automated containment workflows isolate compromised endpoints and revoke compromised credentials through SOAR platform integration. Healthcare systems in the United States select this tier to satisfy HIPAA breach notification timelines, though mid-market buyers face exclusion from advanced automation features.
- Continuous Monitoring:Persistent visibility dashboards track data flow anomalies across SaaS and IaaS environments.
- Employee Training:Phishing simulation and security awareness modules address human-factor vulnerabilities.
Threat detection commands the steepest pricing premiums; employee training serves as the entry-level attachment for mid-market penetration.
End User:
Regulatory stringency varies dramatically across verticals, with HIPAA and EU AI Act compliance timelines compressing procurement windows for certified solutions.
- Finance:Capital markets firms and retail banks demand line-speed TLS/SSL decryption without latency penalties for high-frequency trading platforms. United Kingdom and German institutions lead adoption, driven by NIS2 Directive mandatory breach notification protocols and ECB operational resilience requirements.
- Healthcare:Hospital systems and payers migrating electronic health records to cloud infrastructure require encryption and access logging standards that only certified gateway architectures satisfy. United States providers face HIPAA enforcement actions for inadequate cloud security controls, accelerating replacement cycles.
- Manufacturing:Industrial IoT cloud migrations in German automotive and machinery sectors lack standardized gateway architectures.
- Education:University research institutions handling international student data navigate GDPR Article 44-49 cross-border transfer complexity.
Finance contributes the largest revenue pool; healthcare delivers the steepest expansion trajectory as cloud migration accelerates post-pandemic.
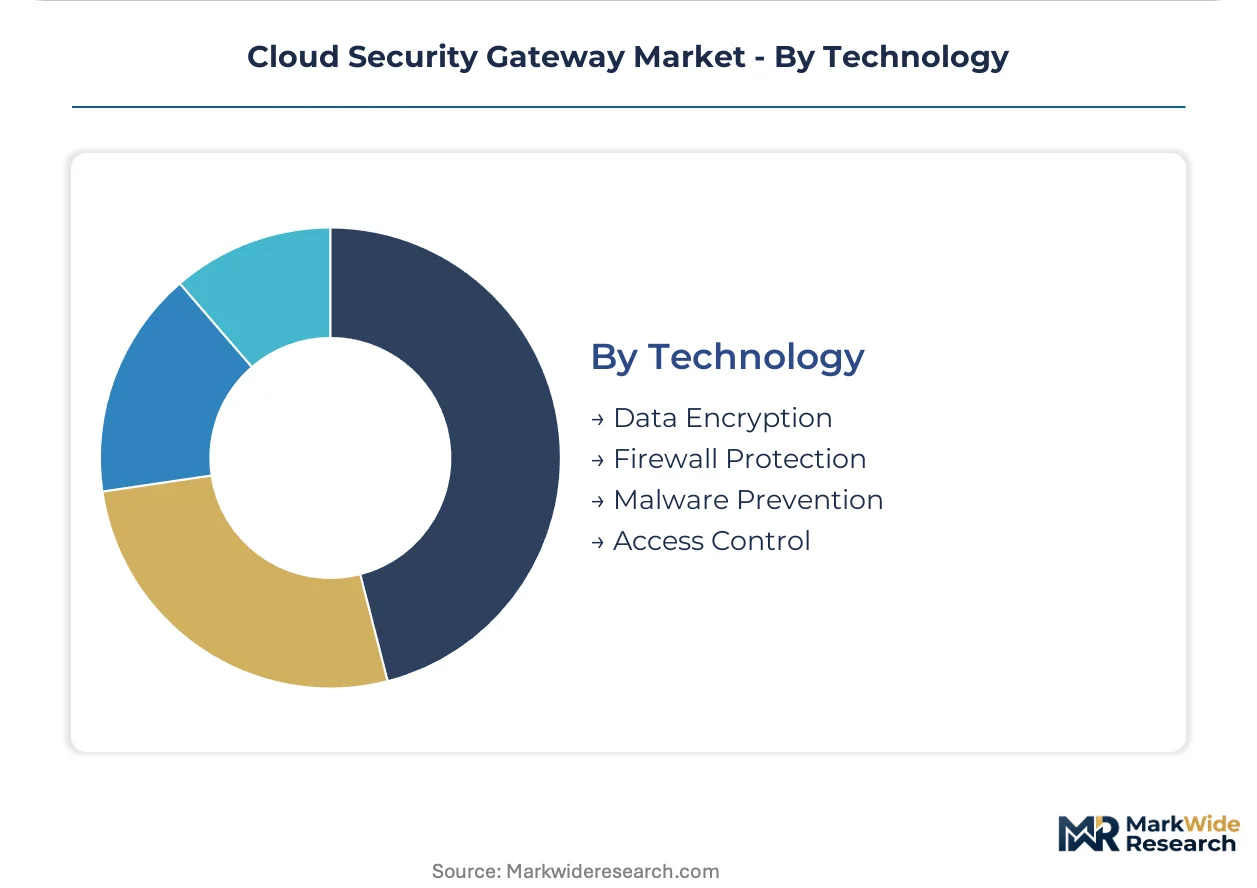
Technology:
Integration breadth determines competitive positioning, with vendors converging previously discrete security functions into unified policy enforcement points.
- Data Encryption:Sovereign cloud integrations keep decryption keys within jurisdictional boundaries for GDPR Article 44-49 compliance. Irish and Dutch healthcare and banking verticals demand these architectures, requiring engineering investment beyond standard contractual clause implementations.
- Access Control:Zero-trust network access integration with 5G mobile edge computing enables distributed enterprise security for manufacturing and logistics operations. Southeast Asian conglomerates treat this as variable infrastructure cost rather than capital commitment.
- Firewall Protection:Next-generation firewall capabilities embedded at cloud egress points replace standalone appliance stacks.
- Malware Prevention:Sandbox detonation and file reputation services inspect cloud-stored content before endpoint delivery.
Data encryption anchors compliance-driven procurement; access control expands fastest through edge-cloud convergence.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
EU AI Act compliance mandates are accelerating gateway procurement across European financial centers. German banking regulators enforce NIS2 Directive protocols that demand auditable data flow architectures. United States healthcare providers face HIPAA enforcement pressure for inadequate cloud security controls.
Germany
Frankfurt-based capital markets firms demand line-speed TLS/SSL decryption for high-frequency trading platforms. BaFin operational resilience requirements mandate hybrid gateway configurations with on-premise decryption appliances. Bavarian automotive conglomerates migrating industrial IoT workloads lack standardized security architectures.
United States
New York and Chicago financial institutions prioritize real-time policy enforcement without latency penalties. HIPAA encryption standards accelerate hospital system cloud migrations requiring certified gateway solutions. Pacific Northwest technology clusters drive consumption-based licensing adoption among mid-market enterprises.
United Kingdom
London financial services firms lead NIS2 Directive implementation for mandatory breach notification protocols. FCA operational resilience deadlines compress procurement cycles for unified threat prevention platforms. Scottish banking hubs demand sovereign cloud integrations keeping decryption keys within jurisdictional boundaries.
France
Paris-based retail banks and insurers navigate GDPR Article 44-49 cross-border transfer complexity. ANSSI certification requirements gate vendor selection for critical infrastructure protection. Lyon pharmaceutical clusters migrating research data to cloud infrastructure require localized data residency guarantees.
China
Shanghai and Beijing financial institutions operate within GB standards and MEE cybersecurity constraints that limit foreign gateway vendor access. Domestic cloud ecosystems favor physical appliance deployments over virtualized alternatives. Shenzhen technology manufacturing hubs drive edge-cloud convergence for 5G mobile security integration.
Cloud Security Gateway Market Vendor Landscape
Player mix skews toward network security incumbents with established firewall franchises and cloud-native specialists with zero hardware dependencies. Market structure concentrates around two dominant archetypes: appliance-anchored vendors leveraging installed base relationships and software-defined platforms eliminating rack-space requirements. Strategic differentiation centers on TLS/SSL inspection performance and regulatory certification velocity. Consolidation pressure intensifies as ISO 27001 audit timelines compress vendor qualification windows.
Within the network security incumbent tier, Palo Alto Networks and Check Point Software Technologies exemplify hybrid-cloud positioning that spans SaaS, IaaS, and private cloud deployments. Zscaler occupies a distinct cloud-native archetype through architecture eliminating on-premise hardware dependencies. Fortinet and Cisco Systems represent appliance-anchored scale players with extensive firewall integration sustaining enterprise loyalty. Netskope and Forcepoint sit within the data-centric protection segment addressing SaaS governance requirements. Microsoft Corporation leverages cloud infrastructure ownership to bundle gateway capabilities into broader enterprise subscriptions.
| Leading Market Players |
|---|
| Fortinet |
| Cisco Systems |
| Palo Alto Networks |
| Check Point Software Technologies |
| Zscaler |
| Netskope |
| Forcepoint |
| McAfee |
| Microsoft Corporation |
| Others |
Supply Flow & Price Mechanics
Ninety-day ISO 27001 certification cycles compress vendor qualification windows, concentrating pricing power with pre-certified suppliers while forcing uncertified competitors toward aggressive discounting to retain procurement conversations. This lead-time compression reshapes supply chain priorities, as buyers trade hardware flexibility for audit-ready architectures that accelerate cloud migration timelines.
Pricing Analysis
Certification level creates the primary spread between premium and standard tiers, with ISO 27001-accredited solutions commanding substantial premiums over uncertified alternatives. Three-tier pricing structure across premium, standard, and economy levels aligns with automation depth, where real-time threat response capabilities separate premium offerings from passive monitoring tiers. Cost compression in the mid-market intensifies because managed security service providers bundle gateway capacity into broader transformation contracts, eroding standalone pricing power. Healthcare systems and capital markets firms exhibit the least price sensitivity due to regulatory enforcement pressure, while mid-market manufacturing buyers drive the steepest discount negotiations.
Supply Chain Analysis
Port congestion on Asia-Pacific trade lanes elevates inbound logistics costs for hardware-dependent hybrid deployments, tilting procurement toward fully virtualized alternatives that eliminate physical appliance dependencies. Supply concentrates in the United States, Ireland, and Singapore for cloud-native software stacks, while on-premise decryption appliance manufacturing draws from Taiwan and South Korea for specialized silicon. Component dependencies span TLS/SSL acceleration chips, sovereign cloud infrastructure, and zero-trust network access modules. Single-source vulnerability in certified sovereign cloud integrations poses structural risk as GDPR Article 44-49 compliance demands jurisdictional key custody. Distribution runs through managed security service providers in Sydney and Singapore, with direct enterprise sales retaining dominance in regulated European banking sectors.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market functions as a defensive moat sustained by regulatory entrenchment, where ISO 27001 certification timelines and NIS2 Directive mandates create switching costs that cement incumbent positions across multi-year procurement cycles.
For Market Incumbents: Compound certification velocity advantages by accelerating audit-ready feature development for EU AI Act compliance, while extending hardware abstraction layers to capture mid-market buyers fleeing capital-intensive hybrid deployments. Deepen vertical integration into sovereign cloud infrastructure to defend margin position against pure software-defined entrants. Prioritize German and French banking relationships where BaFin and ACPR operational resilience requirements lock in long-term contract structures. For New Entrants and Emerging Players: Mid-market manufacturing in Bavaria and Baden-Württemberg represents the most penetrable white-space target, as industrial IoT cloud migrations lack standardized gateway architectures and incumbent sales cycles remain elongated. Target consumption-based licensing models that align with Southeast Asian conglomerates treating security infrastructure as variable cost. Pursue channel partnerships with Sydney and Singapore-based managed security service providers to bypass direct enterprise sales friction. For Investors and Strategic Acquirers: Carve-out targets emerge from network security incumbents with dormant cloud-native portfolios and stranded hardware appliance divisions. Long-term viability hinges on regulatory certification entrenchment rather than feature velocity, favoring assets with established ISO 27001 audit relationships over pure technology plays. Monitor NIS2 Directive implementation velocity across EU member states as the primary inflection indicator for contract renewal pricing power.| Strategic Initiative | Industry Significance |
|---|---|
| Sovereign Cloud Partnership | GDPR Article 44-49 compliance in Irish and Dutch banking verticals demands jurisdictional key custody architectures. |
| Zero-Trust Network Access Integration | 5G mobile edge computing convergence opens distributed enterprise security for Southeast Asian manufacturing conglomerates. |
| Managed Security Service Provider Channel Expansion | Sydney and Sydney-based MSSPs compress sales cycles from quarters to weeks through bundled transformation contracts. |
| ISO 27001 Certification Acceleration | BaFin and ECB operational resilience requirements gate vendor selection for Frankfurt capital markets procurement. |
| Hardware Abstraction Layer Development | Virtualized inspection engines eliminate rack-space constraints for London financial services firms adopting cloud-native stacks. |
Methodological Framework
A spread of perspectives from chief information security officers, cloud infrastructure architects, regulatory compliance leads, and managed security service provider executives converged on the working assumptions underlying this analysis. Primary fieldwork combined structured interviews with secondary validation against SEC filings, hyperscaler capex disclosures, EU regulatory implementation timelines, and hospital procurement databases. Bottom-up triangulation across deployment configuration volumes and top-down validation through regulatory mandate tracking anchored the quantitative framework.
Segmentation dimensions modeled span deployment architecture, service tier automation depth, end-user vertical regulatory stringency, and geographic compliance regime clustering across the projection horizon. CAGRs were derived through logistic adoption curve fitting for cloud-native displacement of hybrid configurations, cross-referenced with NIS2 Directive implementation schedules. Forecast inputs incorporated TLS/SSL inspection performance benchmarks, sovereign cloud integration pipeline visibility, and managed security service provider bundling penetration rates.
Forecasts assume regulatory continuity in EU AI Act, GDPR, and NIS2 Directive enforcement; material policy shifts would require re-modeling adoption velocity assumptions. Specific risk factors include cross-border data transfer restriction tightening, ISO 27001 audit timeline elongation, and China GB standards enforcement escalation against foreign vendors. Outcomes outside this envelope would require model recalibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Cloud Security Market
Cybersecurity
India Ransomware Protection Market
Cybersecurity
Cybersecurity Mesh Market
Cybersecurity
Network Traffic Analysis Solutions Market
Cybersecurity
Global Information Security Consulting Market
Cybersecurity
Bahrain Cybersecurity Market
Cybersecurity
Global Ddos Protection Market
Cybersecurity
Singapore Cybersecurity Market
Cybersecurity
Global Cyber Threat Intelligence Market
Cybersecurity
Argentina Cybersecurity Market
Cybersecurity
Content Delivery Network (CDN) Security Market
Cybersecurity
Portugal Cybersecurity Market
Cybersecurity
Global Content Disarm and Reconstruction Market
Cybersecurity
5G Security Market
Cybersecurity
V2X Cybersecurity Market
Cybersecurity
Cognitive Security Market