
 Cybersecurity Mesh Market | 2026-2036
Cybersecurity Mesh Market Size, Share, and Industry Trends Forecast 2026-2036
Cybersecurity Mesh Market Analytics
Enterprise buyer concentration around cloud-native infrastructure is recalibrating procurement priorities for decentralized security fabrics. Cisco Systems leverages extensive hardware-software integration to sustain channel dominance across hybrid environments. Palo Alto Networks anchors its position through AI-driven threat intelligence platforms that span identity and network layers. Fortinet competes aggressively on consolidated security stack pricing while extending its ASIC-powered appliance footprint.
Cybersecurity mesh denotes an architectural approach where individual security services coordinate through interoperable APIs to enforce policy across distributed assets, typically operating via identity-aware proxies and software-defined perimeters rather than fixed network boundaries. The architecture's primary purpose centers on eliminating implicit trust by verifying every access request against contextual identity, device posture, and behavioral signals before granting resource entry. Cloud-based deployment configurations capture expanding margin pools as enterprises abandon capital-intensive appliance refresh cycles in favor of consumption-based security service delivery. Identity management solutions lead solution-type revenue generation because privileged access remains the dominant lateral movement vector in documented breach patterns. Managed service models within the service model dimension attract fastest-growing demand as skills scarcity forces internal security teams toward co-managed detection and response partnerships.
NIST, ISO 27001, and the EU AI Act collectively reshape product certification requirements and cross-border data governance obligations for mesh architecture vendors. HIPAA and PCI-DSS add sector-specific compliance layers that filter which platform capabilities qualify for healthcare and finance procurement shortlists. Stakeholders must monitor how fragmentation between national encryption standards and identity federation protocols affects interoperability claims across vendor ecosystems.
Market Dynamics
Zero-trust architecture mandates from NIST are forcing enterprises to dismantle perimeter-based security models and reconstruct access control around continuous identity verification. This structural shift compresses procurement cycles for legacy firewall replacements while elevating API-first security vendors.
Growth Catalysts
- Federal zero-trust mandates:NIST SP 800-207 compels US government contractors to deploy identity-aware proxies and software-defined perimeters, creating immediate compliance-driven procurement.
- Healthcare data protection:HIPAA security rule enforcement drives hospitals toward decentralized access controls that segment electronic health records across cloud and edge environments.
- AI-powered threat detection:Machine learning models analyzing behavioral biometrics and device posture signals enable real-time anomaly blocking without fixed network boundaries.
Market Restraints
- Skills scarcity in identity architecture:Enterprise security teams lack personnel proficient in OAuth 2.0, SAML federation, and policy-as-code implementation, slowing deployment velocity.
- Interoperability friction:Fragmentation between vendor-specific APIs and proprietary policy engines forces costly integration middleware development.
- Regulatory encryption conflicts:Divergent national cryptography standards between the US, EU, and China complicate cross-border mesh deployments for multinational enterprises.
Strategic Opportunities
- Operational technology security:Manufacturing and energy sectors remain underpenetrated for identity-aware access controls protecting industrial control systems.
- EU AI Act compliance services:Automated risk classification and audit trail capabilities for high-risk AI systems create adjacent revenue streams for mesh vendors.
- Converged IT/OT platforms:Unified identity fabrics spanning enterprise IT and operational technology networks address convergence-driven attack surface expansion.
Industry Challenges
- Legacy directory integration:Active Directory and LDAP migration to cloud-native identity providers requires staged certificate rotation and application refactoring.
- Policy orchestration complexity:Distributed enforcement across hundreds of microservices demands consistent attribute-based access control definition and testing.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cybersecurity Mesh Market |
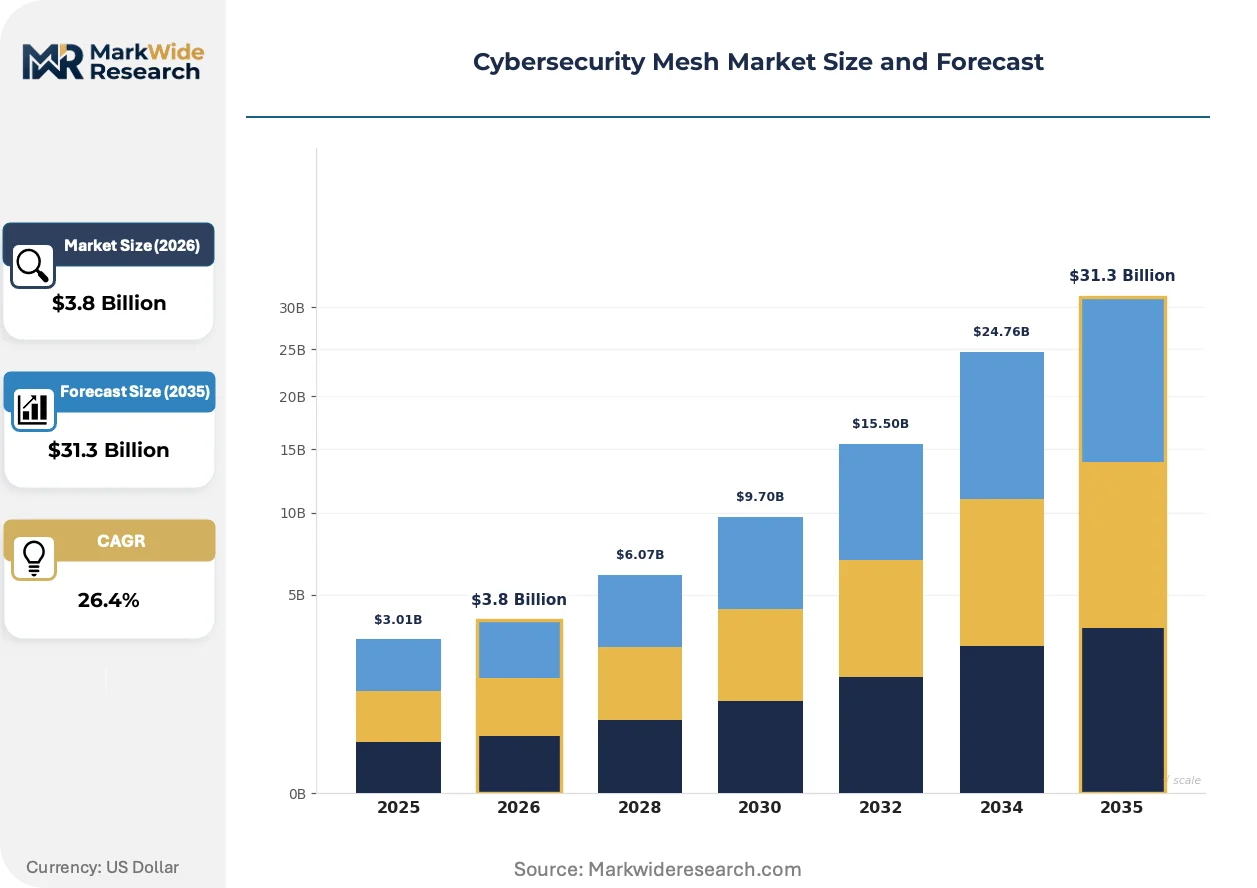
| Market Size in 2026 | $3.8 Billion |
| Market Size in 2035 | $31.3 Billion |
| CAGR (2026 – 2036) | 26.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premises, Cloud-Based, Hybrid, Distributed Solution Type: Identity Management, Network Security, Endpoint Security, Application Security End User: Government, Healthcare, Finance, Retail Service Model: Managed Services, Consulting, Training, Incident Response |
| Companies Covered | Cisco Systems, Palo Alto Networks, Fortinet, IBM, Microsoft, Check Point Software Technologies, Zscaler, CrowdStrike, Forcepoint, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cybersecurity Mesh Market Evolving Landscape
Security service orchestration is displacing monolithic platform consolidation as enterprises prioritize composable architectures. Vendors now compete on API interoperability rather than feature breadth alone.
Identity fabric technology is converging with confidential computing enclaves to enable zero-trust verification without exposing sensitive credentials to host operating systems. Financial services firms in the United States are piloting these integrations for high-value transaction authorization. This convergence is compressing the boundary between identity verification and hardware-rooted trust.
EU AI Act risk classification requirements are mandating automated audit trails and explainable access decisions for AI systems processing personal data. Mesh vendors must embed policy logging and model inference monitoring into their control planes. Healthcare and finance procurement committees in Germany and France now require these capabilities for vendor qualification.
Consumption-based security procurement is replacing perpetual license models as CFOs prioritize operational expenditure alignment with cloud migration timelines. Managed detection and response providers are capturing this transition through co-managed identity operations. This pattern concentrates in US and UK enterprises with mature cloud-native infrastructure programs.
Cybersecurity Mesh Market Segmentation
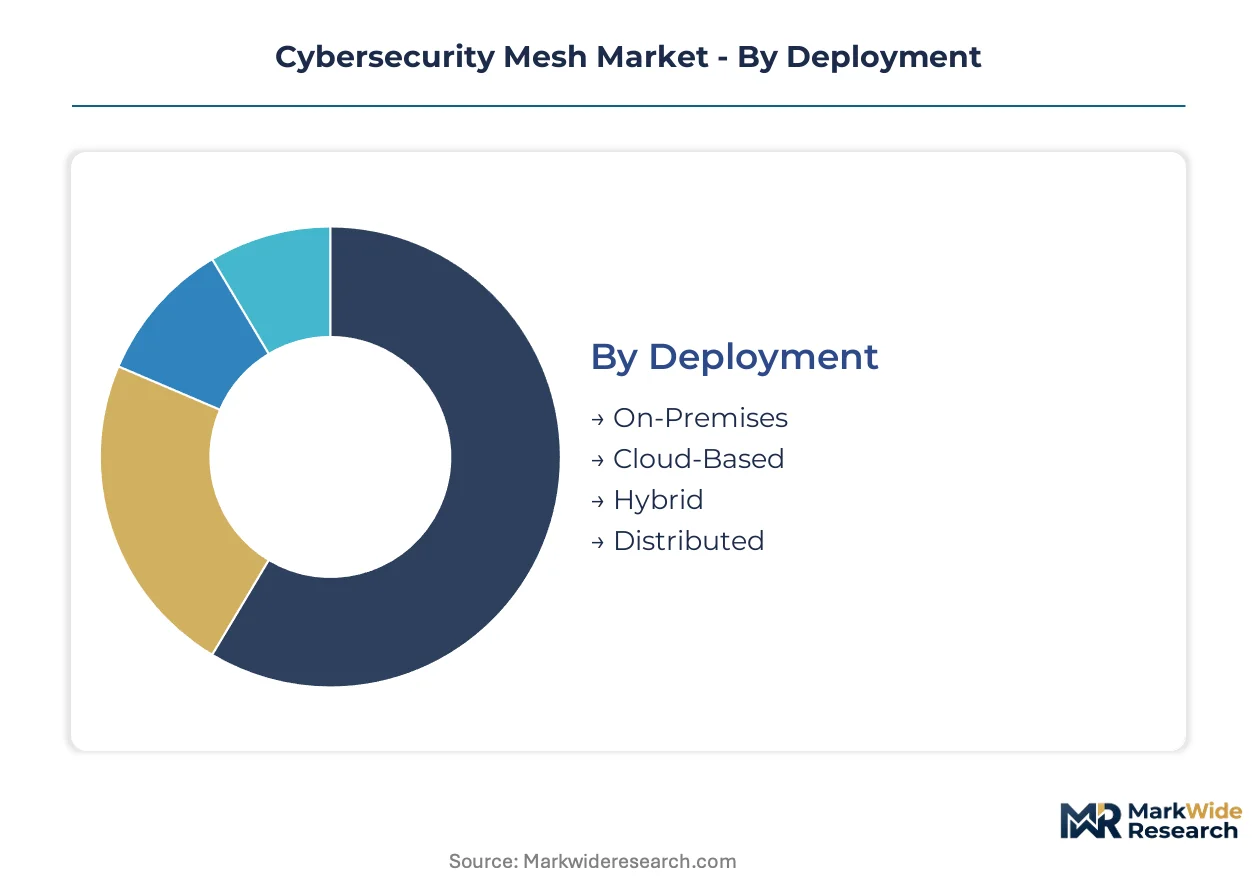
Cybersecurity mesh architectures require granular segmentation to match security service delivery with enterprise infrastructure maturity and compliance obligations. Deployment configurations and solution types determine integration complexity, while end-user verticals and service models shape vendor pricing power and contract duration.
Deployment:
Supply concentration among cloud hyperscalers is redistributing deployment economics toward consumption-based delivery models and away from capital-intensive appliance procurement.
- On-Premises:Hardware-anchored security stacks operating within enterprise data centers with dedicated appliance infrastructure. Demand concentrates in German and Japanese financial institutions subject to strict data residency mandates that prohibit cross-border credential processing.
- Cloud-Based:Fully managed security services delivered via SaaS consumption models with API-native policy orchestration. United States healthcare systems and federal contractors are migrating here fastest to satisfy HIPAA and NIST zero-trust mandates without infrastructure ownership.
- Hybrid:Split architectures maintaining sensitive workloads on-premises while extending policy enforcement to cloud assets.
- Distributed:Edge-deployed security nodes serving IoT and operational technology environments with localized decision-making.
Today's leader: Cloud-Based. Tomorrow's challenger: Distributed.
Solution Type:
Cost tier differentiation separates premium identity fabrics from commoditized endpoint agents, with API interoperability becoming the primary procurement filter.
- Identity Management:Centralized credential lifecycle platforms spanning authentication, authorization, and privileged access governance. United States federal agencies and Fortune 500 enterprises prioritize these investments to satisfy NIST SP 800-207 continuous verification requirements and compress breach response timelines.
- Network Security:Software-defined perimeters and microsegmentation controllers replacing legacy firewall boundaries. Finance and healthcare sectors in the United Kingdom and Singapore are deploying these fastest to segment cloud-native workloads without physical network reconfiguration.
- Endpoint Security:Device posture verification and behavioral monitoring agents deployed across workstations and mobile assets.
- Application Security:Runtime protection and API gateways embedded within microservice architectures.
Identity Management commands premium pricing. Application Security is climbing the fastest.
End User:
Application maturity varies sharply across verticals, with regulated industries demanding certified configurations that extend sales cycles but lock in multi-year contracts.
- Government:Federal, state, and municipal agencies with classified and unclassified network segmentation requirements. United States Department of Defense and civilian agencies are expanding fastest under executive zero-trust mandates with dedicated procurement vehicles.
- Healthcare:Hospital systems, payers, and pharmaceutical manufacturers protecting electronic health records and clinical trial data. German university hospitals and United States health systems are prioritizing decentralized access controls to satisfy GDPR and HIPAA enforcement.
- Finance:Banking, insurance, and capital markets firms with transaction integrity and fraud prevention obligations.
- Retail:E-commerce platforms and physical point-of-sale networks defending payment card data and customer PII.
Finance leads contract value. Healthcare offers the steepest expansion trajectory.
Service Model:
Customer type segmentation reveals a bifurcation between self-operating enterprises with internal security operations centers and skill-constrained organizations outsourcing detection and response.
- Managed Services:Co-managed or fully outsourced security operations with 24/7 threat monitoring and incident response. Mid-market enterprises in the United States and United Kingdom are adopting these fastest to address identity architecture skills scarcity without expanding headcount.
- Consulting:Architecture design, zero-trust transformation planning, and policy engineering engagements.
- Training:Certification programs and workforce development for identity and access management competencies.
- Incident Response:Retainer-based breach containment and forensic investigation services.
Managed Services dominates recurring revenue. Incident Response is gaining share fastest.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Cybersecurity talent clusters in the United States, Germany, United Kingdom, Japan, and Singapore are anchoring regional deployment velocity for mesh architectures. Each concentration shapes procurement patterns through distinct regulatory enforcement and infrastructure maturity.
United States
Federal zero-trust mandates and healthcare digitization drive procurement velocity. NIST SP 800-207 compels government contractors to deploy identity-aware proxies and software-defined perimeters. Boston's healthcare technology cluster sees hospital systems migrating electronic health records to decentralized access controls.
Germany
Strict data residency requirements and industrial automation security needs concentrate demand. BSI technical guidelines enforce encryption standards for critical infrastructure operators. Munich's automotive and manufacturing hub deploys identity fabrics protecting operational technology networks.
United Kingdom
Financial services modernization and cloud-native infrastructure expansion accelerate adoption. NCSC zero-trust principles guide banking sector procurement for transaction integrity. London's fintech cluster segments cloud workloads through microsegmentation controllers.
Japan
Critical infrastructure protection and manufacturing digitization shape market development. METI cybersecurity frameworks mandate continuous verification for industrial control systems. Nagoya's automotive manufacturing corridor implements identity-aware access for supplier networks.
Singapore
Smart nation initiatives and regional financial hub status concentrate investment. MAS technology risk management guidelines enforce resilient access controls for banking institutions. The island's data center cluster hosts multi-tenant mesh deployments for Southeast Asian enterprises.
Cybersecurity Mesh Market Competitive Landscape
Diversified conglomerates compete with focused pure-play specialists across the cybersecurity mesh landscape. The vendor base spans established networking hardware manufacturers, cloud-native security platforms, and endpoint protection specialists. Three archetypes dominate: hardware-integrated platform providers, API-first cloud security vendors, and AI-driven threat intelligence operators. Consolidation through strategic acquisitions and technology licensing partnerships reshapes competitive boundaries.
Among diversified technology conglomerates, Cisco Systems and IBM occupy positions spanning hardware-software integration and enterprise consulting. Palo Alto Networks exemplifies the cloud-native specialist archetype with AI-driven threat intelligence capabilities. These three anchors represent distinct strategic postures: infrastructure incumbency, services-led transformation, and born-in-the-cloud agility.
| Leading Market Players |
|---|
| Cisco Systems |
| Palo Alto Networks |
| Fortinet |
| IBM |
| Microsoft |
| Check Point Software Technologies |
| Zscaler |
| CrowdStrike |
| Forcepoint |
| Others |
Value Network & Pricing Analysis
Private-equity-rolled-up managed security service providers anchor supply concentration in the United States and United Kingdom, compressing pricing discipline through platform consolidation while feeding consumption-based SaaS economics that reward recurring revenue over perpetual license models.
Pricing Analysis
Bundled managed detection and response services command premium positioning against unbundled identity fabric components. Three-tier pricing structure across premium, standard, and economy levels separates full-stack zero-trust platforms from point-solution API gateways. Cost compression in the economy tier intensifies because hyperscaler marketplaces commoditize basic policy orchestration tools. Mid-market enterprises in healthcare and finance exhibit highest price sensitivity, while federal contractors accept premium pricing to satisfy NIST compliance mandates.
Supply Chain Analysis
Freight costs for hardware security modules and ASIC-powered appliances concentrate supply dependencies in Taiwan, South Korea, and the United States. Semiconductor fabrication for cryptographic processors draws from TSMC and Samsung foundry capacity, while cloud-native policy engines rest on AWS, Azure, and GCP infrastructure. Single-source vulnerability in advanced node chip production threatens appliance delivery timelines. Distribution runs through value-added resellers and hyperscaler marketplaces with direct enterprise procurement gaining share fastest.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Geographic arbitrage between United States federal compliance premiums and European data residency requirements creates margin capture opportunities for vendors with multi-sovereign deployment capabilities.
For Market Incumbents: To counter API-first cloud-native specialists eroding hardware-anchored market share, Cisco Systems and Palo Alto Networks must deepen backward integration into confidential computing enclaves while extending channel control through co-managed service partnerships that lock in multi-year federal procurement vehicles. For New Entrants and Emerging Players: Begin with operational technology security in German automotive manufacturing corridors and Japanese industrial control networks, where identity-aware access controls remain underpenetrated. A vertical-specific go-to-market anchored in IEC 62443 certification consulting bypasses direct competition with established IT security incumbents. For Investors and Strategic Acquirers: Valuations sit cheapest among managed security service providers with established SOC-2 Type II audit trails and federal contracting vehicles. Long-term viability hinges on recurring revenue concentration exceeding eighty percent and demonstrated cross-sell velocity into identity governance. Watch NIST SP 800-207 procurement deadline acceleration as the inflection signal for compliance-driven valuation expansion.| Strategic Initiative | Industry Significance |
|---|---|
| Zero-Trust Platform Integration | Unifies identity, network, and endpoint policy enforcement across hybrid cloud environments for federal contractors. |
| Confidential Computing Partnership | Embeds hardware-rooted trust into identity verification workflows for financial services transaction authorization. |
| OT Security Specialist Acquisition | Extends identity fabric coverage into industrial control systems serving German and Japanese manufacturing bases. |
| EU AI Act Compliance Module | Automates audit trail generation for high-risk AI systems processing personal data under French and German procurement rules. |
| Managed Detection and Response Scale-Up | Addresses identity architecture skills scarcity among United States mid-market enterprises through co-managed SOC partnerships. |
Research Methodology
Multiple input streams — chief information security officers at Fortune 500 enterprises, federal procurement officers, managed security service provider executives, and cloud platform engineering leads — were reconciled against SEC 10-K filings, hyperscaler capex disclosures, federal contract award databases, and NIST publication archives. Bottom-up deployment estimates across cloud, hybrid, and on-premises configurations were triangulated with top-down addressable market calculations derived from enterprise IT security budget allocations.
Historical spending patterns were cross-referenced against panel input from identity and access management practitioners to construct the projection framework. Segmentation dimensions modeled include deployment configuration, solution type, end-user vertical, and service model complexity tier. CAGRs were derived from weighted average growth assumptions across these segments, with specific adjustments for NIST mandate compliance deadlines and HIPAA enforcement intensity in United States healthcare systems.
Several conditions sit outside the modeled scope, including sovereign encryption standard fragmentation effects, unforeseen zero-day vulnerability cascades, and major hyperscaler service disruptions. Stakeholders should weight assumptions against their own operating context and monitor regulatory enforcement velocity for forecast revision triggers.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Cloud Authentication Market
Cybersecurity
Global Cloud Encryption Market
Cybersecurity
Micro Segmentation Technology Market
Cybersecurity
E-Mail Security Market
Cybersecurity
Israel Cybersecurity Market
Cybersecurity
Europe Cybersecurity Market
Cybersecurity
Cloud Security in Banking Market
Cybersecurity
Asia-Pacific Cloud DLP Market
Cybersecurity
China Cybersecurity Market
Cybersecurity
Global Patch Management Market
Cybersecurity
Finland Cybersecurity Market
Cybersecurity
Open RAN Security Market
Cybersecurity
Cloud-Based Email Security Market
Cybersecurity
Global Cloud Security Posture Management Market
Cybersecurity
Global Database Security Market
Cybersecurity
Threat Intelligence Security Market