
 Global Information Security Consulting Market | 2026-2036
Global Information Security Consulting Market Size, Share, and Industry Trends Forecast 2026-2036
Global Information Security Consulting Market Foresight
Subscription-based managed detection and response financing is fragmenting the competitive landscape by lowering capital barriers for mid-tier buyers. Deloitte leverages its audit-aligned risk methodology to anchor enterprise retainer relationships across Fortune 500 accounts. Wipro Limited competes through outcome-based pricing that ties consulting fees to measurable security posture improvements. Accenture differentiates via in-house threat intelligence platforms that extend traditional advisory into continuous monitoring services.
Information security consulting encompasses advisory services that assess, design, and implement protective controls for digital assets, typically delivered through frameworks mapping to ISO 27001, NIST CSF, or SOC 2 technical specifications. These engagements reduce residual cyber risk by translating control gaps into prioritized remediation roadmaps for CISO organizations. Risk assessment services dominate revenue contribution due to regulatory audit cycles and insurance underwriting requirements. Cloud security consulting represents the fastest-expanding technology segment as multicloud complexity outpaces in-house expertise at client organizations. Outcome-based engagement models are gaining share against time-and-material structures because procurement teams demand measurable security ROI.
The U.S. SEC cyber disclosure rules, EU NIS2 Directive, and India's CERT-In reporting mandates are collectively extending compliance advisory demand beyond traditional financial services into critical infrastructure operators. ISO 27001 certification requirements embedded in enterprise procurement clauses are reshaping market access for boutique consultancies lacking accredited audit partnerships. Stakeholders must monitor how AI-generated attack tooling compresses incident response windows and whether regulatory frameworks adapt fast enough to mandate autonomous detection standards.
Market Dynamics
Zero-trust architecture mandates are compressing advisory engagement cycles as financial institutions and critical infrastructure operators accelerate control implementation timelines. The EU AI Act and NIS2 Directive are tightening breach-notification windows, forcing procurement teams to prioritize consultancies with accredited audit partnerships and continuous monitoring capabilities.
Growth Catalysts
- Cloud Migration Complexity:Multicloud environments at healthcare and energy operators exceed in-house security expertise, driving demand for architecture assessment and control mapping services.
- SEC Cyber Disclosure Rules:US public companies must now report material cybersecurity incidents within four business days, expanding retainer relationships with incident response specialists.
- ISO 27001 Procurement Clauses:Enterprise vendor qualification requirements are embedding certification mandates into supply chain contracts, reshaping market access for boutique advisory firms.
Market Restraints
- Accreditation Concentration:ISO 27001 lead auditor certification capacity concentrates with a limited pool of accredited bodies, creating bottlenecks for consultancy scale-out.
- Technical Talent Scarcity:Shortages of professionals holding both cloud security architecture and regulatory compliance expertise constrain project delivery velocity.
- Insurance Underwriting Rigidity:Cyber insurance carriers are narrowing coverage terms for organizations lacking documented control frameworks, squeezing mid-market advisory budgets.
Strategic Opportunities
- India CERT-In Mandates:Reporting obligations for data breaches and security incidents are extending compliance advisory demand beyond traditional IT services into manufacturing and logistics.
- AI-Generated Attack Tooling:Autonomous threat detection requirements are converging with advisory services, creating white space for consultancies bundling threat intelligence with control design.
- Outcome-Based Pricing Models:Procurement teams in Germany and the United States are displacing time-and-material structures with contracts tying fees to measurable security posture improvements.
Industry Challenges
- Legacy System Integration:Industrial control environments at energy and utilities operators require specialized expertise to map modern zero-trust controls onto decades-old operational technology architectures.
- Skill Certification Velocity:The gap between emerging cloud security specializations and available training pathways delays consultant deployment on multicloud engagements.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Information Security Consulting Market |
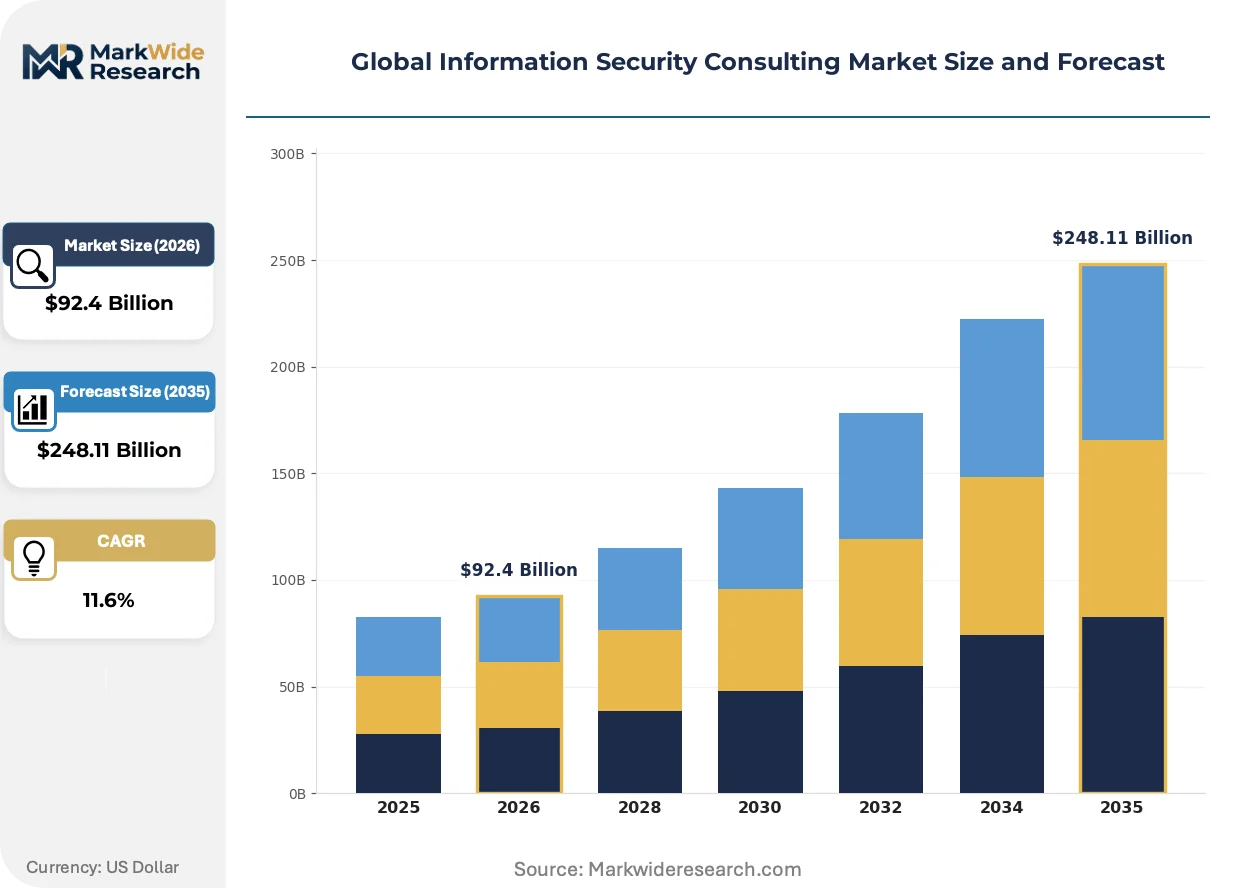
| Market Size in 2026 | $92.4 Billion |
| Market Size in 2035 | $248.11 Billion |
| CAGR (2026 – 2036) | 11.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Risk Assessment, Incident Response, Compliance Advisory, Penetration Testing, Security Architecture, Forensic Analysis Technology: Cloud Security, Endpoint Protection, Identity & Access Management, Network Security, Data Loss Prevention, Security Information & Event Management Client Type: Financial Institutions, Government Agencies, Telecommunication Providers, Manufacturing Firms, Educational Institutions, Energy Companies Engagement Model: Project-Based, Retainer, Outcome-Based, Time & Material, Staff Augmentation, Managed Services |
| Companies Covered | Deloitte, Ernst & Young, PwC, KPMG, Accenture, IBM, Atos, BAE Systems, Wipro Limited, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Information Security Consulting Market Shifts & Advancements
Security service delivery is virtualizing around continuous monitoring platforms, compressing the traditional gap between advisory assessment and operational control enforcement. Three converging developments are restructuring how protective capabilities reach end-user organizations.
Extended detection and response platforms are virtualizing the security operations center function, enabling mid-tier enterprises to access tier-one threat hunting without captive infrastructure. Healthcare systems and regional banks are adopting these cloud-native architectures fastest, displacing on-premise SIEM deployments. The technology is virtualizing consultant roles from periodic assessors into embedded control operators with persistent network visibility.
The EU AI Act is mandating risk classification and documentation for high-risk AI systems, extending security advisory scope into algorithmic governance and training data protection. Industrial manufacturers deploying predictive maintenance AI must now document cybersecurity controls alongside bias assessments. German automotive suppliers and French healthcare AI developers are engaging consultancies earliest to map existing ISO 27001 frameworks onto emerging AI-specific requirements.
Enterprise buyers are consolidating vendor relationships, preferring consultancies that bundle advisory, implementation, and managed detection under unified accountability. This concentration is displacing discrete project-based engagements, particularly at Fortune 500 accounts with complex multicloud footprints. The pattern is most visible in US financial services and German critical infrastructure, where procurement teams demand single-contract responsibility for security outcomes.
Global Information Security Consulting Market Segmentation
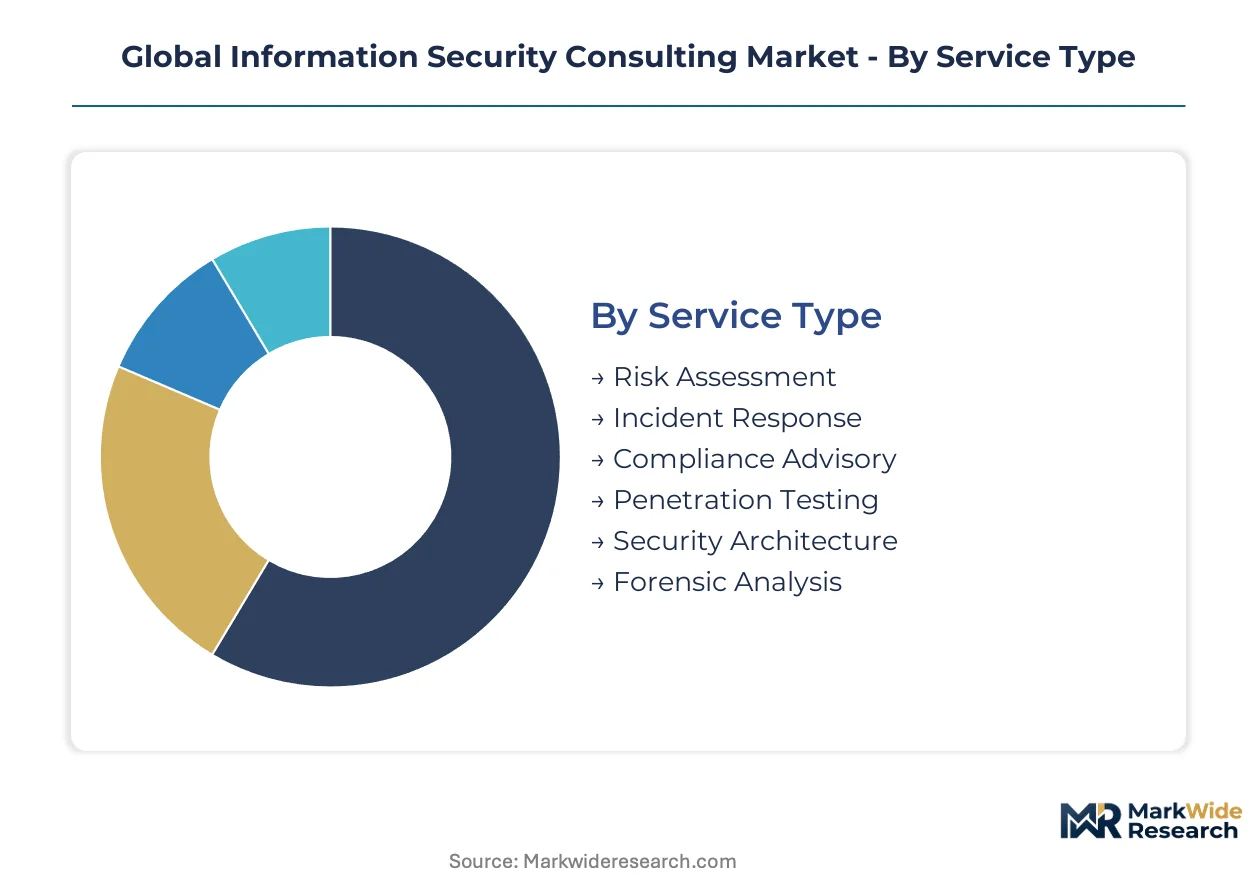
Segmentation in information security consulting reveals how procurement cycles and technical complexity fragment demand across service lines. Buyers select engagement structures based on regulatory pressure intensity and in-house capability gaps.
Service Type:
Risk assessment engagements turn over fastest due to annual audit cycles, while forensic analysis retains the longest sales cycles tied to post-breach litigation timelines.
- Risk Assessment:Systematic evaluation of control gaps against ISO 27001, NIST CSF, or SOC 2 frameworks. Financial institutions in the United States and Germany commission these most heavily as cyber insurance underwriters tighten documentation requirements.
- Incident Response:Retainer-based emergency containment and recovery services activated upon breach detection. SEC four-day disclosure mandates are compressing procurement decisions for US public companies seeking guaranteed response SLAs.
- Compliance Advisory:Regulatory mapping and remediation planning for EU NIS2 Directive and India CERT-In mandates.
- Penetration Testing:Simulated attack exercises validating control effectiveness across cloud and on-premise environments.
- Security Architecture:Zero-trust design and multicloud control implementation for healthcare and energy operators.
- Forensic Analysis:Post-incident evidence preservation and chain-of-custody documentation for legal proceedings.
Risk assessment anchors the volume base while incident response gains share at the steepest rate.
Technology:
Cost tiering separates commodity endpoint tools from premium cloud-native platforms requiring specialized architecture expertise.
- Cloud Security:Multicloud control assessment and configuration hardening across AWS, Azure, and GCP environments. Healthcare systems in the United States and manufacturing firms in Germany are expanding advisory budgets fastest as workload migration outpaces security team scaling.
- Identity & Access Management:Privileged access governance and zero-trust identity fabric design. Financial institutions commission these engagements most intensively as phishing campaigns targeting credentials intensify.
- Endpoint Protection:Device-level threat detection and response configuration for distributed workforces.
- Network Security:Segmentation design and perimeter defense modernization for operational technology environments.
- Data Loss Prevention:Sensitive data classification and exfiltration control implementation.
- Security Information & Event Management:Log aggregation and correlation rule development for security operations centers.
Cloud security commands premium pricing tiers while endpoint protection operates at volume scale with compressed margins.
Client Type:
Application intensity varies by sector exposure to regulated data and operational technology convergence.
- Financial Institutions:Comprehensive advisory spanning regulatory compliance, fraud prevention, and third-party risk management. Banks and insurers in the United States, Germany, and India are consolidating vendor relationships under unified accountability contracts.
- Government Agencies:Classified system accreditation and supply chain security assessment. Defense and civilian agencies commission these through extended procurement cycles with stringent personnel clearance requirements.
- Telecommunication Providers:Critical infrastructure protection and subscriber data governance for 5G network rollouts.
- Manufacturing Firms:Industrial control system security and predictive maintenance AI risk classification under EU AI Act.
- Educational Institutions:Student data protection and research cybersecurity for federally funded programs.
- Energy Companies:Operational technology segmentation and ransomware resilience for generation and distribution networks.
Financial institutions dominate current spending while energy companies are expanding advisory budgets most aggressively.
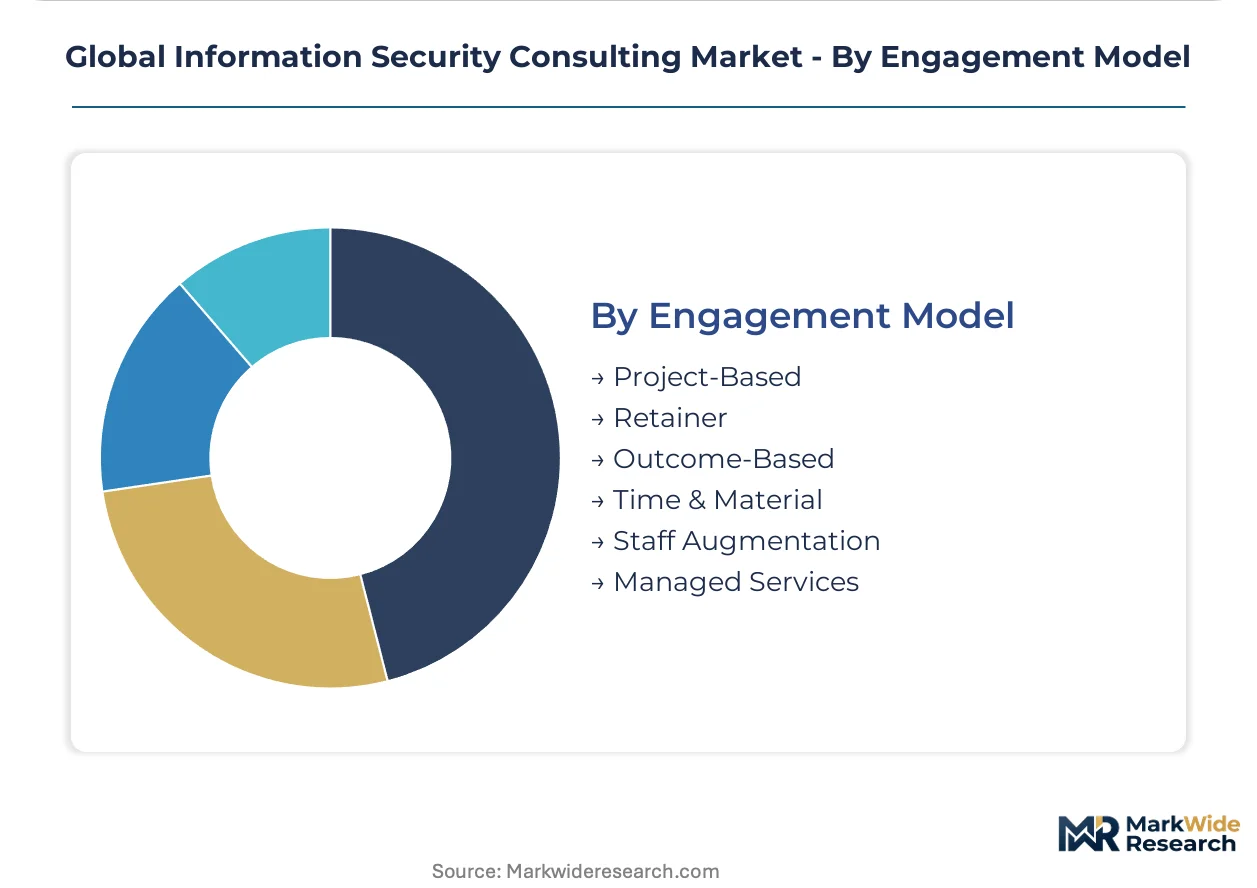
Engagement Model:
Maturity gradients separate legacy time-and-material structures from emerging outcome-based contracts with shared risk profiles.
- Retainer:Fixed-fee ongoing advisory with guaranteed response times and quarterly posture reviews. Fortune 500 accounts in US financial services and German critical infrastructure prefer this structure for multicloud complexity management.
- Outcome-Based:Fee structures tied to measurable security posture improvements or incident reduction metrics. Procurement teams in Germany and the United States are displacing hourly billing fastest as ROI documentation requirements tighten.
- Project-Based:Discrete scope engagements for specific assessments or implementations with defined deliverables.
- Time & Material:Hourly billing for advisory services with open-ended scope and duration.
- Staff Augmentation:Embedded consultant placement filling specific skill gaps in client security teams.
- Managed Services:Continuous monitoring and control operation outsourced to consultancy threat intelligence platforms.
Retainer relationships anchor revenue predictability while outcome-based contracts are climbing the fastest as procurement sophistication advances.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
SEC disclosure mandates, EU NIS2 Directive enforcement, and India's CERT-In reporting obligations are redrawing procurement priorities across financial services and critical infrastructure operators. Regulatory compression in the United States, Germany, and India concentrates advisory demand where cloud migration outpaces security team scaling.
United States
Financial institutions in New York and Chicago are expanding zero-trust architecture budgets as the SEC's four-day incident disclosure window forces retainer relationships with response specialists. HIPAA enforcement at HHS and state-level privacy laws in California and Virginia compound compliance complexity for healthcare systems. The Dallas-Fort Worth corridor anchors energy sector consulting as ransomware resilience mandates tighten for pipeline operators.
Germany
Automotive suppliers in Stuttgart and Munich are commissioning AI risk classification services under EU AI Act high-risk system documentation requirements. The NIS2 Directive's tightened breach-notification timelines are compressing procurement cycles for critical infrastructure operators in the Ruhr industrial basin. Frankfurt's financial services cluster is consolidating vendor relationships under unified accountability contracts for multicloud security.
India
Manufacturing firms in Maharashtra and Karnataka are extending compliance advisory demand beyond traditional IT services as CERT-In mandates reach logistics and industrial sectors. RBI cybersecurity guidelines for banks and SEBI disclosure requirements for market infrastructure institutions expand retainer relationships in Mumbai. Bangalore's technology corridor drives cloud security consulting as SaaS providers face enterprise procurement clauses demanding ISO 27001 certification.
United Kingdom
Financial services firms in London are navigating post-Brexit regulatory divergence between UK GDPR and EU data protection frameworks. The Financial Conduct Authority's operational resilience requirements are extending advisory demand into incident response planning for clearing houses and payment systems. The Manchester-Leeds corridor concentrates healthcare consulting as NHS trusts migrate patient records to cloud environments.
Japan
Automotive and electronics manufacturers in the Nagoya-Toyota industrial zone are aligning supply chain security with NIST CSF and ISO 27001 procurement requirements from US and European customers. METI's cybersecurity management guidelines for critical infrastructure are expanding advisory budgets at utilities and telecommunications operators. Tokyo's financial district anchors demand as regional banks consolidate security vendor relationships under outcome-based pricing structures.
Global Information Security Consulting Market Competitive Landscape
On the supply side, the industry is consolidating around three distinct capability tiers. The Big Four audit networks leverage existing risk methodology relationships to anchor enterprise retainer accounts. Technology integrators compete through in-house threat intelligence platforms that extend advisory into continuous monitoring. Boutique specialists survive by embedding deep expertise in regulated verticals where accreditation requirements create defensible niches. M&A activity concentrates among mid-tier firms seeking ISO 27001 lead auditor capacity, while strategic partnerships between consultancies and cloud hyperscalers accelerate multicloud implementation velocity.
Within the audit-aligned tier, Deloitte, Ernst & Young, and PwC exemplify the risk methodology approach that dominates Fortune 500 relationships. These firms occupy positions where existing financial audit relationships create natural pathways into cybersecurity advisory. Accenture and IBM represent the technology-integrator archetype, with in-house platforms enabling continuous service delivery beyond traditional project boundaries. Wipro Limited anchors the outcome-based pricing vector where procurement teams demand measurable security posture improvements rather than time-and-material billing.
| Leading Market Players |
|---|
| Deloitte |
| Ernst & Young |
| PwC |
| KPMG |
| Accenture |
| IBM |
| Atos |
| BAE Systems |
| Wipro Limited |
| Others |
Supply & Pricing Matrix
ISO 27001 lead auditor accreditation bottlenecks in the United States, Germany, and India determine both pricing tier spreads and supply chain shape, compressing margins for mid-tier consultancies while concentrating premium capture with Big Four networks and accredited boutique specialists.
Pricing Analysis
Certification level creates the primary spread between engagement tiers. Three-tier pricing structure across premium, standard, and economy levels dominates: Fortune 500 retainers with accredited audit partnerships command premium positioning, mid-market project-based engagements occupy standard tiers, and staff augmentation services compete at compressed margins. Price differentiation hinges on ISO 27001 lead auditor availability and threat intelligence platform ownership. Cost compression in the mid-tier is intensifying because insurance underwriters are narrowing coverage terms for organizations lacking documented control frameworks. Procurement teams at regional banks and healthcare systems demonstrate highest price sensitivity, while critical infrastructure operators in energy and telecommunications show lowest sensitivity due to regulatory penalty exposure.
Supply Chain Analysis
Tariff exposure between the United States and China dominates supply chain risk profiles for hardware-dependent security implementations. Talent concentration in the United States, India, and Germany feeds project delivery velocity, with Bangalore, Dallas-Fort Worth, and Frankfurt anchoring consultant deployment pipelines. Raw material dependencies span cloud infrastructure subscriptions, threat intelligence data feeds, and specialized training certifications. Single-source vulnerability concentrates with a limited pool of ISO 27001 accredited bodies creating certification bottlenecks. Distribution runs through direct enterprise sales forces for retainer relationships, while channel partnerships with cloud hyperscalers accelerate multicloud implementation velocity for project-based engagements.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
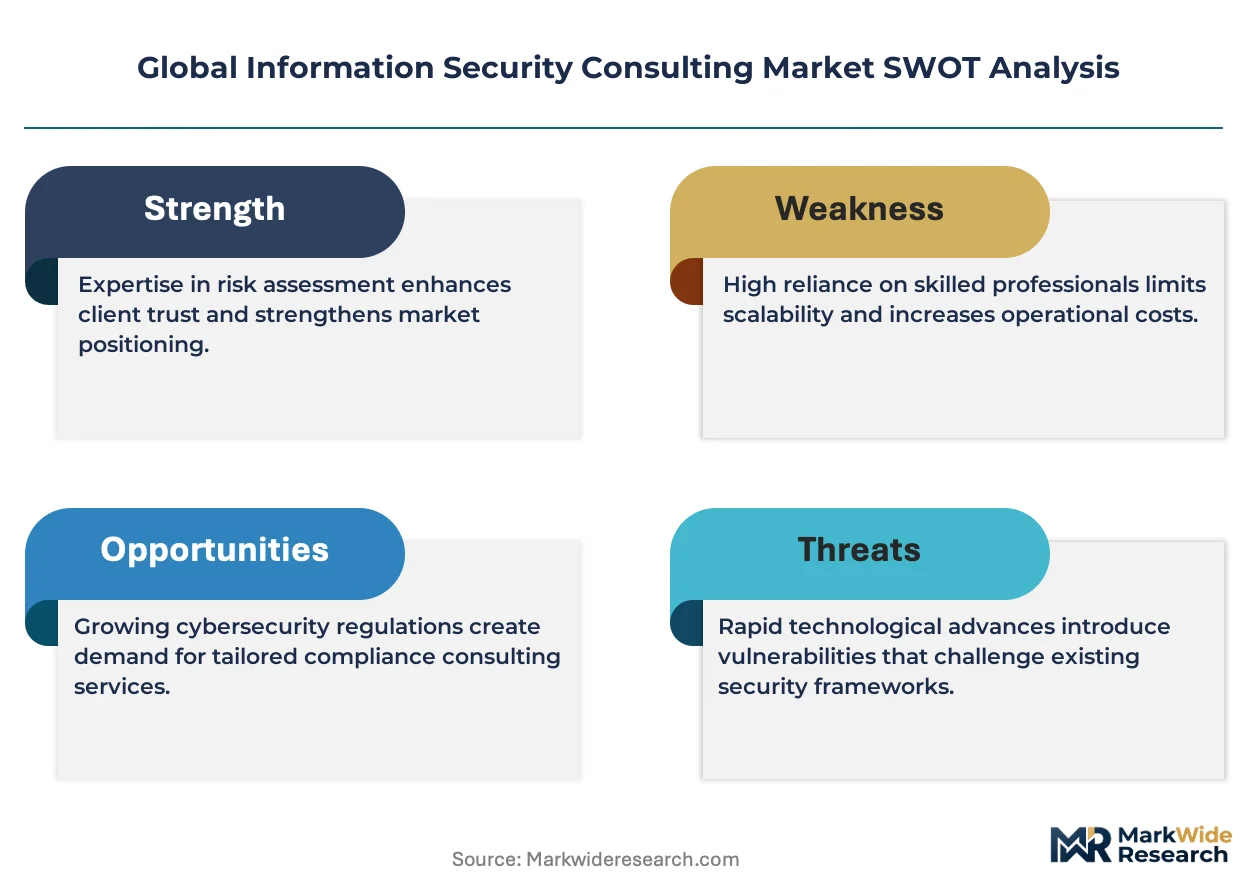
The market rewards consultancies that bridge cloud security architecture expertise with regulatory compliance credentials, yet the pipeline of professionals holding both skill sets remains structurally constrained.
For Market Incumbents: Pre-empt boutique acquisition opportunities to secure ISO 27001 lead auditor capacity before accreditation bottlenecks worsen. Consolidate threat intelligence platform investments to extend advisory into continuous monitoring services, displacing discrete project-based competitors. Vertical integration into managed detection and response capabilities defends retainer relationships against technology integrators. For New Entrants and Emerging Players: Mid-market manufacturing firms in Maharashtra and Karnataka under CERT-In mandate expansion represent the most penetrable entry point, bypassing saturated financial services competition. Outcome-based pricing contracts for measurable security posture improvements unlock procurement access in Germany and the United States. Channel partnerships with AWS, Azure, and GCP sales organizations provide accelerated customer acquisition velocity. For Investors and Strategic Acquirers: The market sits at a consolidation phase that favors accredited boutique specialists with vertical-specific expertise. Long-term viability rests on consultancies that bundle advisory, implementation, and managed services under unified accountability. Acquisition target archetype: ISO 27001-accredited firms in industrial control security or AI governance advisory. Signal to watch: regulatory frameworks mandating autonomous detection standards compressing incident response windows.| Strategic Initiative | Industry Significance |
|---|---|
| Threat Intelligence Platform Integration | Extends advisory into continuous monitoring, anchoring Fortune 500 retainer relationships against project-based competitors. |
| ISO 27001 Lead Auditor Capacity Acquisition | Resolves accreditation bottlenecks that constrain scale-out velocity and premium pricing capture. |
| Cloud Hyperscaler Partnership | Accelerates multicloud implementation pipelines through co-sell arrangements with AWS, Azure, and GCP field organizations. |
| Outcome-Based Pricing Structure | Aligns consultancy compensation with measurable security posture improvements demanded by German and US procurement teams. |
| AI Governance Advisory Capability | Captures EU AI Act compliance demand from automotive suppliers and healthcare AI developers in Germany and France. |
Research Methodology
A spread of perspectives from CISOs at financial institutions, procurement officers at critical infrastructure operators, cloud security architects, and ISO 27001 lead auditors converged on the working assumptions. Primary interviews combined with secondary validation from SEC disclosure filings, EU regulatory directive texts, CERT-In mandate documentation, and cloud hyperscaler partner program disclosures. Bottom-up service line sizing and top-down macroeconomic triangulation anchored volume and value estimates.
Demand-supply balance framing structured the analytical approach across the analysis window. Segmentation dimensions modeled include service type, technology category, client vertical, and engagement model maturity. CAGRs derived from regression analysis against cloud migration velocity and regulatory mandate implementation timelines. Industry-specific forecast inputs encompass multicloud complexity indices and cyber insurance underwriting requirement evolution.
Practitioners should monitor AI-generated attack tooling adoption rates and regulatory framework adaptation velocity for early signals of forecast revision. Continuous validation against operating reality is the recommended discipline.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Threat Intelligence Market
Cybersecurity
IoT Security Market
Cybersecurity
Belgium Cybersecurity Market
Cybersecurity
Malaysia Cybersecurity Market
Cybersecurity
Singapore Cybersecurity Market
Cybersecurity
Application Programming Interface Security Market
Cybersecurity
Middle East Cybersecurity Market
Cybersecurity
Multi-Cloud Data Protection Market
Cybersecurity
Middle East & Africa AI Cybersecurity Market
Cybersecurity
Artificial Intelligence in Cybersecurity Market
Cybersecurity
Next-Generation Firewall Market
Cybersecurity
Global Distributed Denial of Service (Ddos) Protection Market
Cybersecurity
Homomorphic Encryption Market
Cybersecurity
Russia Cybersecurity Market
Cybersecurity
Vietnam Cybersecurity Market
Cybersecurity
Europe Mobile Security Market