
 Portugal Cybersecurity Market | 2026-2036
Portugal Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Portugal Cybersecurity Market Analytics
Enterprise-grade security certification is bifurcating the Portugal Cybersecurity Market into premium and standard service tiers. Microsoft leverages its cloud-native security stack to dominate hybrid deployment contracts across Portuguese government agencies. S21sec anchors its position through deep specialization in managed security services tailored to Iberian regulatory requirements.
Portugal Cybersecurity encompasses hardware, software, and service-based protections engineered to safeguard digital assets against unauthorized access, data exfiltration, and operational disruption, with next-generation firewalls typically processing traffic at throughput rates exceeding 100 Gbps. Its primary commercial purpose centers on ensuring business continuity, regulatory compliance, and customer trust for organizations operating interconnected IT environments. Managed Security services capture the largest revenue pool as Portuguese enterprises outsource 24/7 threat monitoring to address persistent talent shortages. Cloud-Based deployment is expanding fastest as SMBs migrate from capital-intensive on-premises appliances to subscription models. The Finance end-user segment sustains premium pricing due to stringent European Central Bank supervisory expectations for operational resilience.
Portugal's national cybersecurity regulator, Centro Nacional de Cibersegurança, enforces mandatory incident reporting thresholds that directly shape procurement specifications for critical infrastructure operators. The EU NIS2 Directive and GDPR compliance frameworks compel healthcare and education sectors to upgrade encryption and intrusion detection capabilities beyond baseline standards. Stakeholders must weigh whether to build in-house Security Operations Centers or deepen reliance on Lisbon-based managed security providers as attack surface complexity outpaces internal staffing capacity.
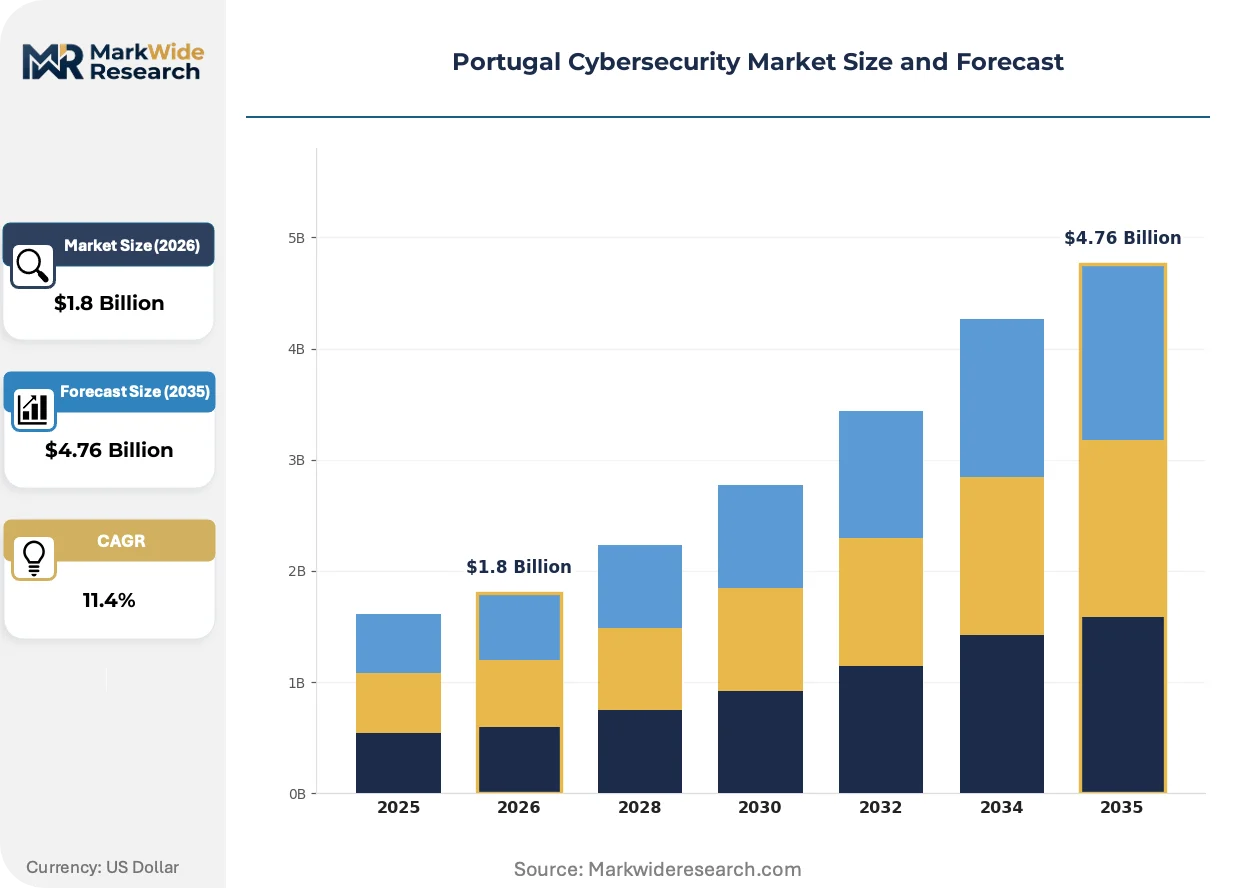
Market Dynamics
EU NIS2 Directive compliance deadlines are compressing procurement cycles across Portuguese critical infrastructure operators, forcing accelerated security stack overhauls ahead of mandatory incident reporting thresholds.
Growth Catalysts
- NIS2 Directive Mandates:The EU NIS2 Directive imposes strict incident reporting timelines on energy, transport, and healthcare operators in Portugal, compelling immediate security infrastructure investment.
- Zero-Trust Architecture Migration:Portuguese financial institutions are replacing perimeter-based defenses with zero-trust frameworks to satisfy European Central Bank operational resilience expectations.
- Lisbon Metropolitan Cluster:Public-private cybersecurity hubs in Lisbon concentrate national IT security spending and talent pipelines, creating localized demand density.
Market Restraints
- Specialized Talent Scarcity:Portugal produces fewer than 1,200 cybersecurity graduates annually, creating persistent staffing bottlenecks for Security Operations Center expansion.
- Cloud Migration Cost Burden:SMBs face prohibitive subscription stacking costs when migrating from depreciated on-premises appliances to multi-cloud security suites.
- Legacy System Interoperability:Decades-old SCADA and industrial control systems in Portuguese utilities resist API-native security overlay integration.
Strategic Opportunities
- Porto Technology Corridor Expansion:Secondary metropolitan zones outside Lisbon offer underpenetrated mid-market enterprise demand with lower competitive saturation.
- Healthcare Encryption Upgrades:GDPR Article 32 enforcement against Portuguese hospital networks creates immediate demand for end-to-end patient data encryption.
- AI-Augmented Threat Detection:Convergence of machine learning inference with edge-deployed sensors enables predictive threat hunting for manufacturing OT environments.
Industry Challenges
- Certification Timeline Compression:ISO/IEC 27001 and SOC 2 audit queues extend 8-14 months, delaying contract eligibility for time-sensitive government tenders.
- Multi-Vendor Stack Complexity:Enterprises integrating cloud-native, on-premises, and OT security tools face interoperability gaps requiring expensive custom middleware development.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Portugal Cybersecurity Market |
| Market Size in 2026 | $1.8 Billion |
| Market Size in 2035 | $4.76 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Consulting, Managed Security, Incident Response, Compliance Deployment Model: On-Premises, Cloud-Based, Hybrid, Virtual End User: Government, Healthcare, Finance, Education Solution: Firewall, Antivirus, Encryption, IDS |
| Companies Covered | Microsoft, Dell Technologies, Cisco Systems, S21sec, Noesis, Fortinet, IBM Corporation, NTT DATA, Palo Alto Networks, Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Portugal Cybersecurity Market Evolving Landscape
Security architecture in Portugal is pivoting from hardware-centric perimeter defense to software-defined, AI-augmented threat detection systems that compress detection-to-response intervals.
Extended Detection and Response platforms aggregate telemetry across endpoints, cloud workloads, and identity systems into unified analysis pipelines. Portuguese managed security providers are deploying these platforms for mid-market clients previously priced out of enterprise-grade monitoring. The technology is miniaturizing deployment footprints, enabling 24/7 coverage without dedicated Security Operations Center real estate.
The EU NIS2 Directive mandates 24-hour incident notification to Centro Nacional de Cibersegurança for critical infrastructure operators. Portuguese energy distributors and port authorities must reconfigure logging architectures to meet automated reporting specifications. Water utilities in the Alentejo region are prioritizing encrypted telemetry backbones to satisfy both NIS2 and GDPR Article 32 technical requirements.
Portuguese enterprises are consolidating vendor relationships to reduce integration overhead and contractual complexity. Single-pane security platforms displace point-solution procurement that characterized early cloud migration phases. This concentration is most visible among Lisbon-headquartered financial services firms seeking unified compliance reporting for European Central Bank supervisory reviews.
Portugal Cybersecurity Market Segmentation
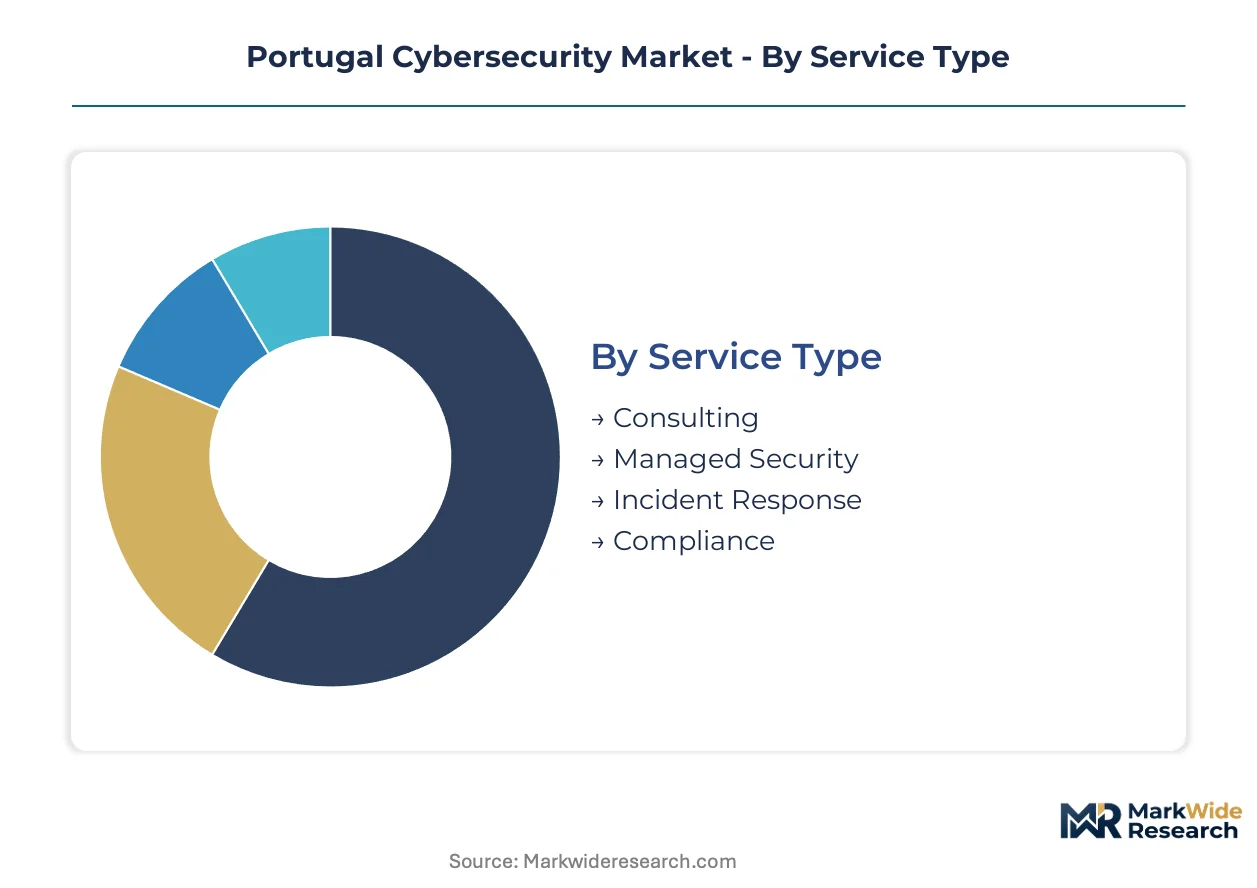
Segmentation in the Portugal Cybersecurity Market reveals how regulatory pressure and infrastructure maturity shape procurement patterns across service tiers, deployment architectures, and sector-specific compliance burdens. Distinct buyer profiles emerge between critical infrastructure operators facing NIS2 mandates and mid-market enterprises prioritizing cost-efficient threat coverage.
Service Type:
EU NIS2 Directive reporting thresholds differentiate service procurement, with mandatory 24-hour incident notification driving specialized demand for integrated response capabilities.
- Managed Security:Continuous threat monitoring and Security Operations Center functions delivered as subscription services. Portuguese banks and energy distributors in Lisbon's metropolitan corridor outsource 24/7 coverage to address persistent talent scarcity and satisfy European Central Bank operational resilience expectations.
- Consulting:Advisory services spanning risk assessment, architecture design, and compliance readiness. Healthcare networks in Porto engage consulting firms to map GDPR Article 32 encryption gaps ahead of regulatory audits.
- Incident Response:Retained breach containment and forensic investigation capabilities.
- Compliance:Audit preparation and certification support for ISO/IEC 27001 and SOC 2 frameworks.
Established volume favors Managed Security; emerging adoption favors Incident Response.
Deployment Model:
Cost tier differentiation separates capital-intensive infrastructure from operational expenditure models, with subscription economics reshaping mid-market procurement.
- Cloud-Based:Software-delivered security functions eliminating hardware lifecycle management. SMBs across Portugal's interior regions migrate from depreciated appliances to multi-cloud suites, though subscription stacking creates budget strain for organizations below 500 employees.
- Hybrid:Orchestrated controls spanning on-premises assets and cloud workloads. Finance sector institutions in Lisbon deploy hybrid architectures to maintain sovereign data custody while leveraging elastic compute for threat analytics.
- On-Premises:Appliance-based perimeter and internal network defenses.
- Virtual:Containerized security functions deployed on hyperconverged infrastructure.
Hybrid deployments dominate finance sector procurement; Cloud-Based solutions are gaining share fastest among regional healthcare providers.
End User:
Application intensity varies by sector exposure to supervisory scrutiny and operational disruption consequences.
- Finance:Banking, insurance, and capital markets institutions subject to European Central Bank operational resilience frameworks. Portuguese retail banks allocate premium budgets for zero-trust architecture migration and real-time payment system protection.
- Government:Central and municipal agencies managing citizen data and critical service delivery. The Centro Nacional de Cibersegurança procurement specifications shape security stack requirements for national infrastructure operators.
- Healthcare:Hospital networks and regional health authorities.
- Education:Universities and research institutions.
Finance sustains premium pricing; Healthcare shows steepest expansion trajectory as GDPR enforcement intensifies against patient data handlers.
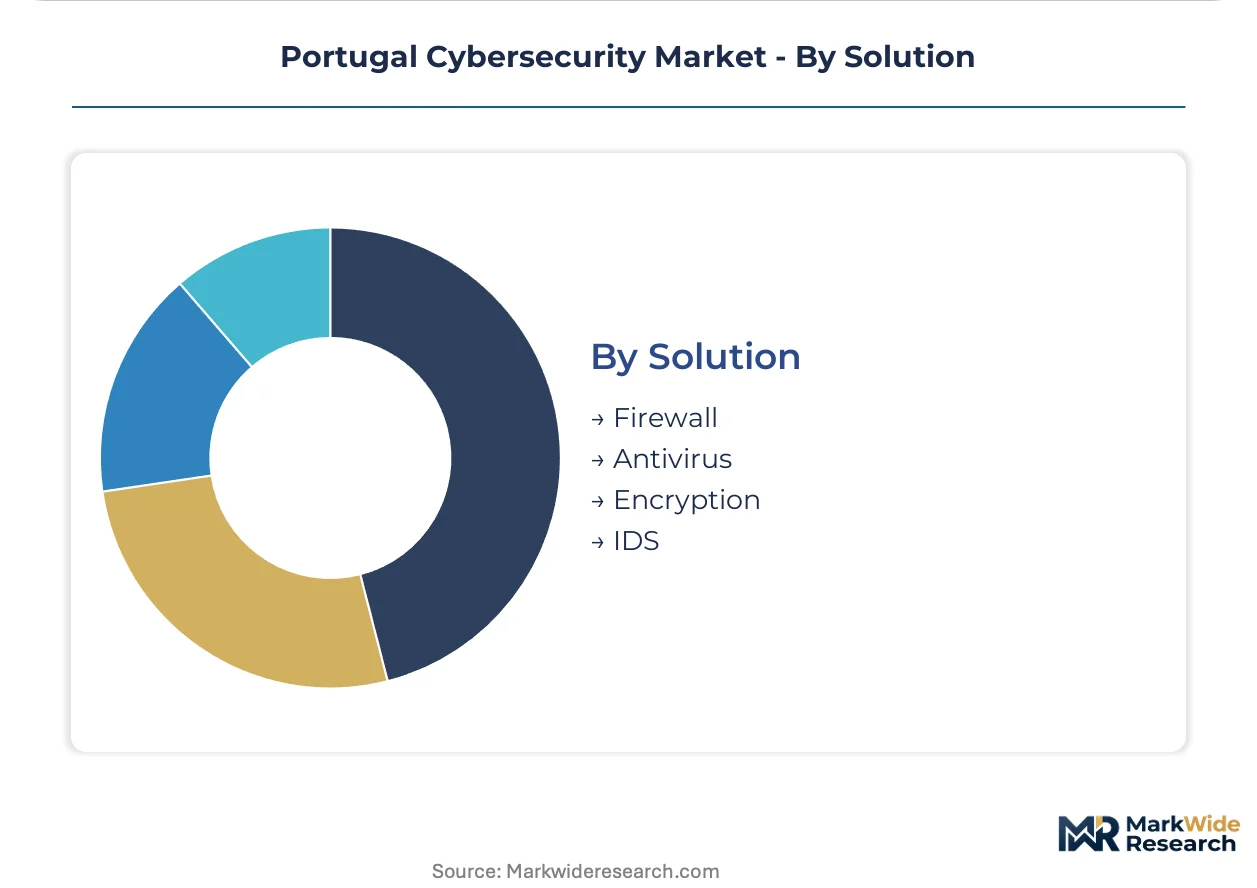
Solution:
Technology maturity curves separate established perimeter controls from emerging encryption and detection capabilities.
- Encryption:Data-at-rest and data-in-transit protection meeting GDPR Article 32 technical standards. Portuguese water utilities in Alentejo prioritize encrypted telemetry backbones to satisfy concurrent NIS2 and data protection requirements.
- Firewall:Next-generation perimeter controls processing traffic exceeding 100 Gbps throughput. Energy distributors maintain firewall refresh cycles to secure SCADA integration points.
- IDS:Signature and behavioral intrusion detection systems.
- Antivirus:Endpoint malware protection and remediation tools.
Firewall maintains installed base dominance; Encryption climbs the fastest as healthcare and utility sectors confront data protection audit exposure.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Cybersecurity service provision concentrates in Lisbon's metropolitan technology corridor, where public-private clusters aggregate national IT security spending and specialized talent pipelines. This concentration shapes procurement patterns across Portuguese sub-regions.
Lisbon Metropolitan Area
Financial institutions and government agencies drive premium-tier security demand, with European Central Bank operational resilience frameworks mandating zero-trust architecture investment. The Centro Nacional de Cibersegurança enforces NIS2 Directive compliance timelines for critical infrastructure operators headquartered in the capital. Lisbon's cybersecurity hubs host managed security service providers delivering 24/7 threat monitoring to address nationwide talent scarcity.
Porto Metropolitan Area
Healthcare networks and manufacturing operations generate mid-market demand for GDPR-compliant encryption and intrusion detection systems. Regional hospital authorities engage consulting firms to map Article 32 technical gaps ahead of regulatory audits. Porto's technology corridor offers underpenetrated enterprise demand with lower competitive saturation than Lisbon.
Alentejo Region
Water utilities and agricultural cooperatives prioritize encrypted telemetry backbones to satisfy concurrent NIS2 and data protection requirements. The national cybersecurity regulator's mandatory incident reporting thresholds shape procurement specifications for SCADA integration points. Distributed infrastructure operators in this sub-region outsource Security Operations Center functions to Lisbon-based providers.
Central Portugal
Industrial manufacturing and logistics operations require OT-specific threat detection for legacy control systems resistant to API-native security overlays. GDPR enforcement against regional data processors drives endpoint protection upgrades. Coimbra's university-industry partnerships feed specialized cybersecurity graduates into national talent pipelines.
Algarve Region
Tourism-dependent hospitality networks and municipal service operators face budget constraints when migrating from depreciated on-premises appliances to cloud-based security suites. The national cybersecurity regulator's procurement specifications influence security stack selection for critical service delivery. Regional IT spending concentrates in Faro's administrative and healthcare infrastructure.
Portugal Cybersecurity Market Competitive Landscape
Concentration sits with global technology conglomerates and Iberian-specialized managed security providers. The Portugal Cybersecurity Market exhibits tiered structure, with multinational cloud-native platforms dominating government and large-enterprise contracts while regional specialists capture mid-market compliance-driven demand. Two strategic archetypes predominate: horizontally integrated technology platforms delivering end-to-end security stacks, and vertically focused service providers with deep regulatory expertise. Competitive dynamics center on portfolio diversification into AI-augmented threat detection and strategic partnerships with national infrastructure operators.
Among global technology platforms, Microsoft and Cisco Systems exemplify the horizontally integrated archetype, leveraging cloud-native infrastructure to anchor hybrid deployment contracts across Portuguese government agencies. Dell Technologies occupies a position representing hardware-centric security appliance provision. Within the Iberian-specialized tier, S21sec anchors managed security service delivery tailored to regional regulatory requirements. These named entities represent competitive positioning patterns rather than exhaustive market coverage, with additional participants including Fortinet, IBM Corporation, NTT DATA, Palo Alto Networks, and Noesis occupying various positions across service type and deployment model specializations.
| Leading Market Players |
|---|
| Microsoft |
| Dell Technologies |
| Cisco Systems |
| S21sec |
| Noesis |
| Fortinet |
| IBM Corporation |
| NTT DATA |
| Palo Alto Networks |
| Others |
Value Network & Pricing Analysis
Scale economies in cloud-native security platform development concentrate procurement leverage among hyperscale providers, compressing price floors for mid-market managed security services while elevating premium tiers for NIS2-compliant critical infrastructure deployments. Lisbon's metropolitan technology corridor aggregates national IT security spending, creating localized supplier density that shapes regional pricing power and service tier differentiation across Portuguese sub-markets.
Pricing Analysis
The EU NIS2 Directive dictates the pricing tier structure across the Portugal Cybersecurity Market, separating premium managed security services for critical infrastructure operators from standardized SaaS offerings targeting mid-market enterprises. Three-tier pricing structure across premium, standard, and economy levels reflects certification grade differentiation, with ISO/IEC 27001 and SOC 2 compliance commanding substantial premiums over baseline threat monitoring subscriptions. Cost compression in the standard tier is intensifying because subscription stacking burdens SMBs migrating from depreciated on-premises appliances. Healthcare networks and regional utilities demonstrate highest price sensitivity, while finance sector institutions facing European Central Bank operational resilience mandates exhibit lowest sensitivity to premium-tier security expenditure.
Supply Chain Analysis
The United States and Ireland anchor cloud infrastructure supply for Portuguese cybersecurity deployments, with hyperscale data centers in Dublin and Frankfurt serving as primary compute backbones for Lisbon-based managed security providers. Taiwan and South Korea supply specialized semiconductor components for next-generation firewall appliances processing traffic exceeding 100 Gbps throughput. The supply chain draws from encryption module manufacturers in Germany and Israel, alongside threat intelligence feed aggregators headquartered in the United Kingdom and Netherlands. Single-source vulnerability in cloud-native platform dependencies creates concentrated exposure to hyperscale provider pricing and service continuity decisions. Distribution runs through Lisbon-headquartered value-added resellers and direct enterprise sales teams serving critical infrastructure operators in Porto and Alentejo regions.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The Portugal Cybersecurity Market represents an early-cycle expansion story, with NIS2 Directive compliance deadlines compressing procurement cycles and accelerating security stack overhauls across energy, transport, and healthcare operators ahead of mandatory incident reporting thresholds.
For Market Incumbents: Fortify managed security service delivery capabilities through AI-augmented threat detection platform deployment, addressing persistent talent scarcity that constrains 24/7 Security Operations Center expansion for Portuguese enterprises. Deepen vertical integration into Iberian regulatory compliance consulting, capturing GDPR Article 32 and NIS2 Directive audit preparation demand from healthcare networks in Porto. Certification investment in ISO/IEC 27001 and SOC 2 frameworks accelerates contract eligibility for time-sensitive government tenders where audit queues currently extend 8-14 months. For New Entrants and Emerging Players: Anchor in Porto's technology corridor, where healthcare networks and manufacturing operations generate underpenetrated mid-market demand with lower competitive saturation than Lisbon's concentrated cybersecurity hub. Target GDPR-compliant encryption and intrusion detection system deployment for regional hospital authorities mapping Article 32 technical gaps ahead of regulatory audits. A specialized go-to-market angle emphasizing OT-specific threat detection for legacy SCADA systems resistant to API-native security overlays differentiates against cloud-native generalists. For Investors and Strategic Acquirers: Mid-cycle technology positioning favors vertically focused service providers with deep regulatory expertise over horizontally integrated technology platforms facing margin compression in standardized SaaS tiers. Long-term viability over the next decade hinges on AI-augmented threat detection capability maturation and sustained NIS2 enforcement intensity across European critical infrastructure operators. Acquisition target archetypes include Iberian-specialized managed security providers with established Centro Nacional de Cibersegurança relationships and healthcare sector compliance track records. The signal to watch is European Central Bank operational resilience framework expansion beyond finance into payment system infrastructure, which would broaden premium-tier addressable market.| Strategic Initiative | Industry Significance |
|---|---|
| AI-Augmented Threat Detection Platform Launch | Compresses detection-to-response intervals for manufacturing OT environments facing legacy system interoperability constraints. |
| Strategic Partnership with National Infrastructure Operators | Secures multi-year managed security contracts with Portuguese energy distributors and port authorities under NIS2 mandates. |
| Acquisition of Specialist Compliance Firm | Accelerates ISO/IEC 27001 and SOC 2 certification throughput to capture government tender eligibility demand. |
| Geographic Expansion into Porto Technology Corridor | Captures underpenetrated healthcare and manufacturing demand with lower competitive saturation than Lisbon. |
| Platform Integration for Unified Compliance Reporting | Addresses European Central Bank supervisory review requirements for Lisbon-headquartered financial services firms. |
Research Methodology
Demand-side practitioners and supply-side operators were both consulted through structured primary interviews with CISOs at Portuguese retail banks, security architects at energy distributors, procurement officers at regional hospital networks, and technical directors at Lisbon-based managed security providers. Secondary validation drew from Centro Nacional de Cibersegurança incident reporting disclosures, European Central Bank operational resilience framework documentation, GDPR enforcement actions by Portuguese data protection authorities, and hyperscaler capex disclosures for cloud infrastructure deployment. Bottom-up and top-down triangulation reconciled service provider revenue estimates with end-user IT security budget allocations across finance, government, and healthcare verticals.
Across the analysis window, the forecasting framework modeled deployment model transitions from on-premises appliances to cloud-based and hybrid architectures, service type evolution from point solutions to integrated managed security platforms, and end-user segment growth differentiated by NIS2 Directive applicability and European Central Bank supervisory intensity. CAGRs were derived from regression analysis against regulatory deadline schedules, cloud migration penetration curves, and talent supply constraints limiting Security Operations Center expansion. Industry-specific forecast inputs included mandatory 24-hour incident notification compliance timelines and zero-trust architecture procurement acceleration among Portuguese financial institutions.
Decision-makers should treat outputs as directional under sustained NIS2 enforcement intensity and stable cloud infrastructure pricing assumptions; material deviation in regulatory timeline delays or hyperscale provider consolidation would warrant model refresh. Recalibration cycles align with material shifts in European Central Bank operational resilience framework scope and Centro Nacional de Cibersegurança procurement specification updates.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
SOC As a Service Market
Cybersecurity
Europe Zero Trust Security Market
Cybersecurity
Cybersecurity Mesh Market
Cybersecurity
Quantum Cryptography Market
Cybersecurity
Digital Forensics Market
Cybersecurity
Latin America IoT Security Market
Cybersecurity
Global Zero-Trust Security Market
Cybersecurity
Saas-Based IT Security Market
Cybersecurity
Botnet Detection Market
Cybersecurity
Cloud-Based Email Security Market
Cybersecurity
Digital Security Market
Cybersecurity
Global Network Forensics Market
Cybersecurity
Canada Ransomware Protection Market
Cybersecurity
India Ransomware Protection Market
Cybersecurity
Web Filtering Market
Cybersecurity
Cloud-Based Database Security Market