
 Certification Authority Market | 2026-2036
Certification Authority Market Size, Share, and Industry Trends Forecast 2026-2036
Certification Authority Market Outlook
Post-quantum cryptography migration is reshaping how certificate infrastructures are architected and deployed. DigiCert anchors the high-assurance segment through its FIPS 140-2 validated hardware security modules and government trust relationships. Sectigo competes aggressively on price and automation for mid-market cloud-native deployments. GlobalSign extends its European footprint with qualified trust services under eIDAS regulation.
A certification authority issues and manages digital certificates that bind cryptographic public keys to verified identities, operating through hierarchical trust chains with root certificates protected in hardware security modules maintaining FIPS 140-2 Level 3 or Common Criteria EAL4+ physical security. SSL/TLS certificates dominate transaction volume but face margin compression from Let's Encrypt and ACME protocol automation, while code signing certificates command premium pricing due to software supply chain security mandates from Microsoft and Apple. Cloud-based delivery models capture the fastest growth trajectory as DevOps teams integrate certificate provisioning into CI/CD pipelines, whereas on-premises hardware security module deployments persist in defense and central banking sectors where sovereign data control remains non-negotiable.
The EU eIDAS framework and GDPR impose strict qualified certificate standards for electronic signatures and identity verification, while the US NIST post-quantum cryptography standards and FERC critical infrastructure directives reshape procurement specifications for energy and financial sector trust anchors. China's SAMR and GB/T standards for commercial cryptography create parallel compliance pathways that fragment cross-border certificate interoperability. Stakeholders must monitor quantum computing timelines and regional sovereignty requirements to align trust infrastructure investments with evolving compliance perimeters.
Market Dynamics
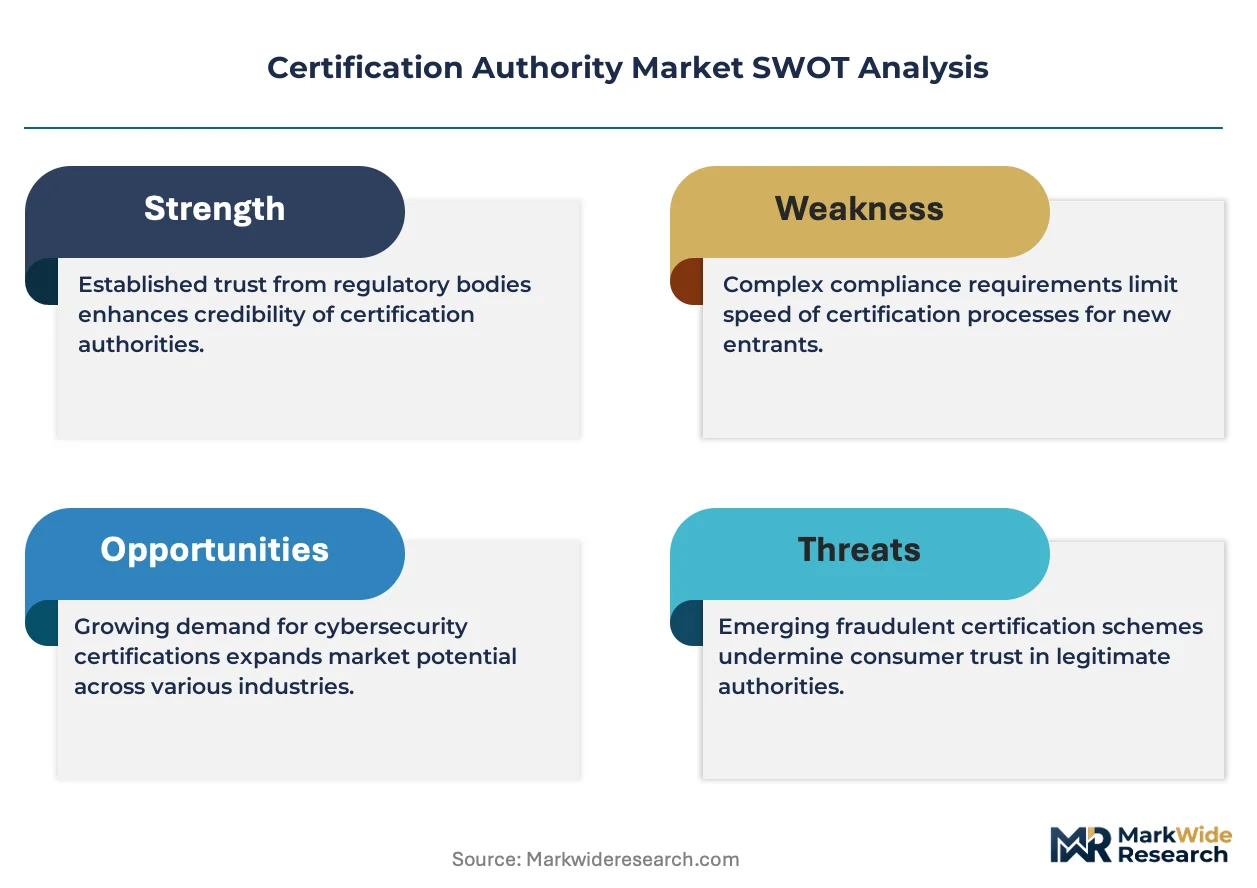
Post-quantum cryptography migration is compressing certificate replacement cycles and forcing infrastructure reinvestment across financial services, automotive, and defense sectors before quantum computers threaten existing RSA and ECC algorithms.
Growth Catalysts
- NIS2 Directive:The EU cybersecurity framework mandates qualified trust services and automated certificate lifecycle management for critical infrastructure operators across member states.
- Software supply chain security:Microsoft's code signing requirements and Apple's notarization mandates drive premium code signing certificate volumes for independent software vendors.
- Cloud workload automation:DevOps teams embed ACME protocol certificate provisioning into CI/CD pipelines, accelerating cloud-native PKI adoption.
Market Restraints
- Hardware security module costs:FIPS 140-2 Level 3 validated HSMs for root key protection require six-figure capital outlays that exclude smaller certification authorities.
- Let's Encrypt margin compression:Free domain-validated certificates automated through the ACME protocol commoditize basic SSL/TLS offerings.
- Fragmented sovereignty requirements:China's SAMR commercial cryptography rules and GB/T standards block foreign root certificates from domestic trust stores.
Strategic Opportunities
- Post-quantum algorithm integration:NIST's finalized ML-KEM and ML-DSA standards enable hybrid certificate offerings combining classical and quantum-resistant signatures.
- IoT device authentication:Manufacturing and automotive OEMs require high-volume, low-latency certificate issuance for connected vehicle and industrial sensor fleets.
- eIDAS qualified trust services:Remote qualified electronic signature demand creates specialized certificate provisioning for legal, healthcare, and government workflows.
Industry Challenges
- Cryptographic engineering talent scarcity:Post-quantum algorithm implementation requires specialized lattice-based cryptography expertise that outpaces academic pipeline output.
- Legacy system integration friction:Mainframe and embedded systems in banking and industrial control lack firmware update paths for new certificate formats.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Certification Authority Market |
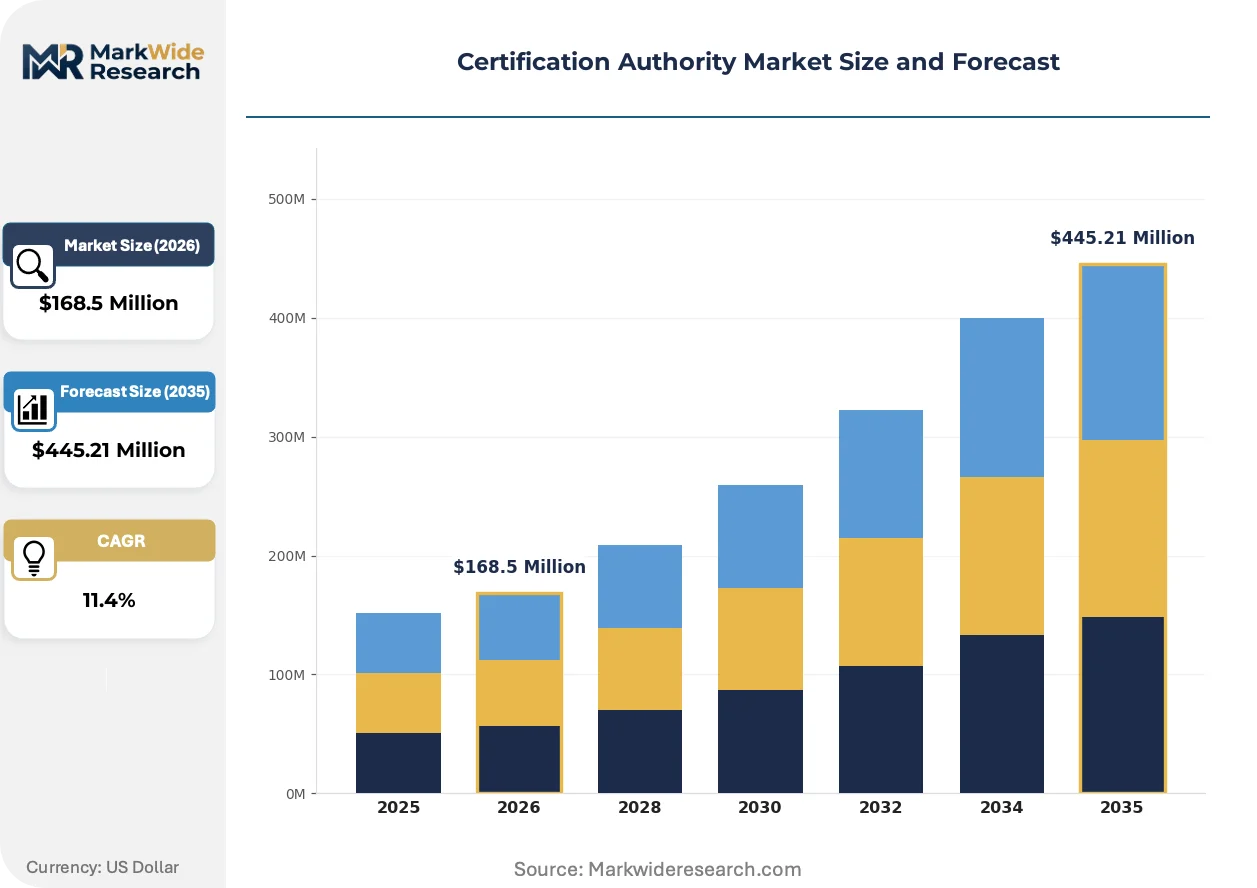
| Market Size in 2026 | $168.5 Million |
| Market Size in 2035 | $445.21 Million |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: SSL/TLS Certificates, Code Signing, Email Security, Document Signing Client Type: Enterprises, Government, Small Businesses, Non-Profits Delivery Model: Cloud-Based, On-Premises, Managed Services, Hybrid Compliance Standard: PCI DSS, HIPAA, GDPR, ISO 27001 |
| Companies Covered | GoDaddy, IdenTrust, DigiCert, Amazon Trust Services, Internet Security Research Group, Sectigo, Entrust, Certum, GlobalSign, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Certification Authority Market Strategic Shifts
Certificate infrastructure is pivoting from perimeter-based trust models to identity-centric zero trust architectures. Automation, quantum resistance, and sovereign data localization are reshaping procurement specifications.
Certificate lifecycle management is migrating from manual renewal workflows to fully automated orchestration platforms. Financial services institutions and cloud-native enterprises now demand API-first provisioning that embeds directly into infrastructure-as-code deployments. This shift compresses operational overhead and reduces certificate-related outages.
The EU AI Act and NIS2 Directive impose strict digital identity verification standards for high-risk AI systems and critical infrastructure operators. These frameworks mandate qualified certificates for electronic seals and authentication mechanisms. German automotive OEMs and French energy utilities are accelerating procurement of eIDAS-compliant trust services.
Certificate buying patterns now favor consumption-based pricing tied to actual issuance volumes rather than annual subscription tiers. Mid-market SaaS vendors and DevOps teams reject upfront capacity commitments. This preference shift concentrates demand in Germany, the Netherlands, and Nordic markets where cloud-native adoption rates exceed Southern European averages.
Certification Authority Market Segmentation
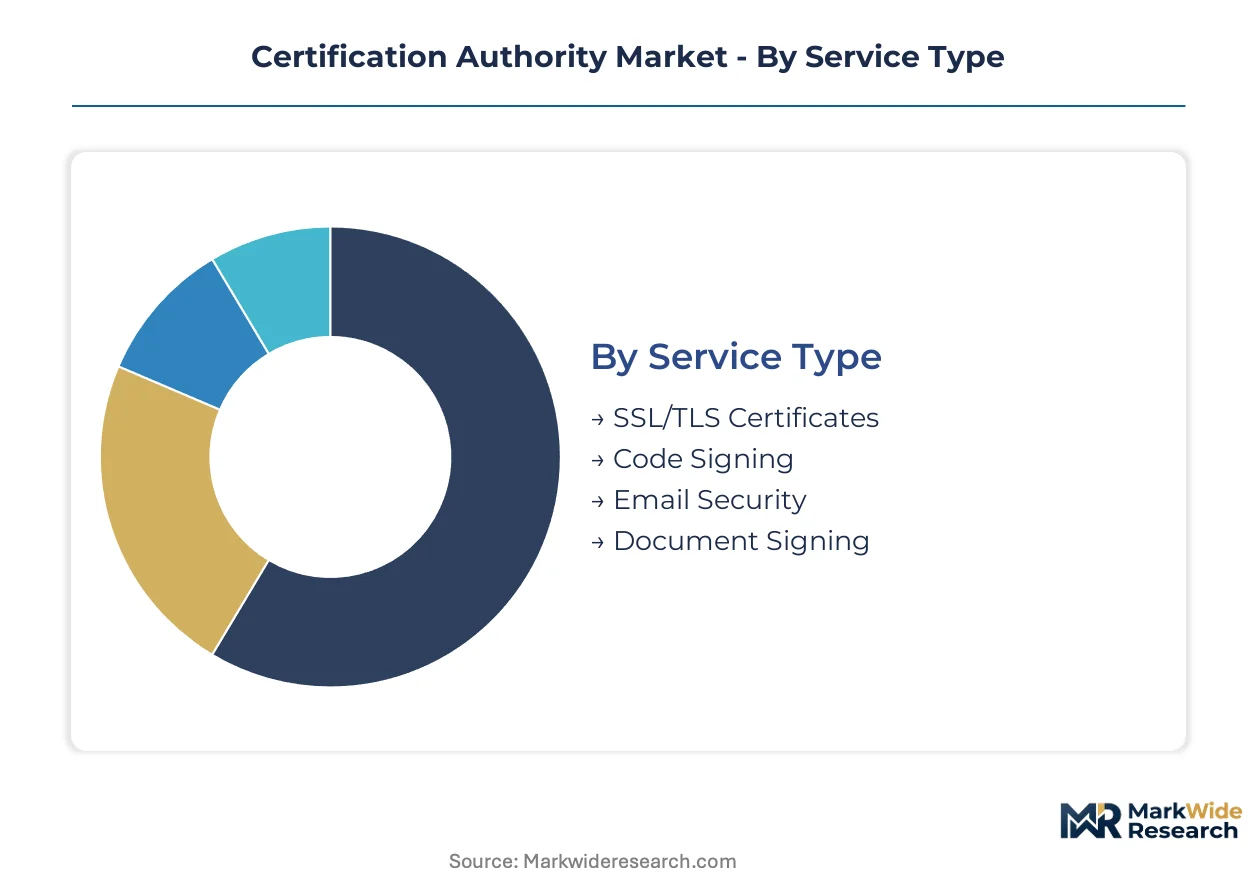
Certificate procurement patterns diverge sharply across organizational scale, technical use case, and sovereignty requirements. Understanding these fault lines exposes where automation investments concentrate and where margin compression strikes hardest.
Service Type:
SSL/TLS certificates anchor the highest transaction volumes through web encryption mandates, while code signing commands premium pricing due to software supply chain security enforcement.
- SSL/TLS Certificates:Domain-validated certificates face severe margin compression from Let's Encrypt's free ACME-automated issuance. Extended validation certificates retain pricing power among financial services institutions in Germany and the Netherlands where browser trust indicators still influence procurement.
- Code Signing:Microsoft's SmartScreen reputation requirements and Apple's notarization mandates force independent software vendors to purchase organization-validated certificates. German automotive OEMs and French defense contractors now require hardware token-based signing for firmware updates.
- Email Security:S/MIME certificates for encrypted corporate communications see concentrated demand from healthcare providers and legal firms under GDPR and professional confidentiality obligations.
- Document Signing:eIDAS-qualified certificates for remote electronic signatures attract procurement from Dutch notaries and Belgian government agencies digitizing administrative workflows.
The dominant share belongs to SSL/TLS certificates, while code signing is closing the gap fastest.
Client Type:
Procurement scale and compliance rigor separate enterprise deployments from automated small-business consumption.
- Enterprises:DevOps teams at cloud-native SaaS vendors embed certificate lifecycle management into CI/CD pipelines. German industrial conglomerates mandate post-quantum cryptography readiness assessments for supply chain partners.
- Government:Defense ministries and central banks require FIPS 140-2 Level 3 HSM-backed root key protection with sovereign data localization. France's ANSSI and Germany's BSI impose qualified trust service standards for federal procurement.
- Small Businesses:Automated domain-validated certificates through hosting providers and CDN platforms dominate. ACME protocol adoption eliminates manual renewal overhead for WordPress and e-commerce operators.
- Non-Profits:Educational institutions and open-source projects leverage discounted or donated certificate programs from commercial authorities seeking trust store placement.
Enterprises generate the highest absolute revenue, though small-business automation volumes are climbing the fastest.
Delivery Model:
Cloud-native architectures displace on-premises HSM deployments except where data sovereignty or air-gapped security requirements prevail.
- Cloud-Based:API-first provisioning platforms capture DevOps-centric demand at Nordic fintechs and Dutch scale-ups. Consumption-based pricing tied to actual issuance volumes replaces annual capacity commitments.
- On-Premises:Air-gapped root key ceremonies persist in Bundesbank payment infrastructure and French nuclear operator control systems. FIPS 140-2 validated HSM procurement requires six-figure capital outlays.
- Managed Services:Outsourced certificate lifecycle operations attract mid-market manufacturers lacking in-house cryptographic engineering expertise.
- Hybrid:Private root hierarchies with cloud-issued end-entity certificates balance sovereign control with operational flexibility for German automotive suppliers.
Cloud-based delivery holds the dominant position, while hybrid architectures are gaining share fastest among regulated industrial operators.
Compliance Standard:
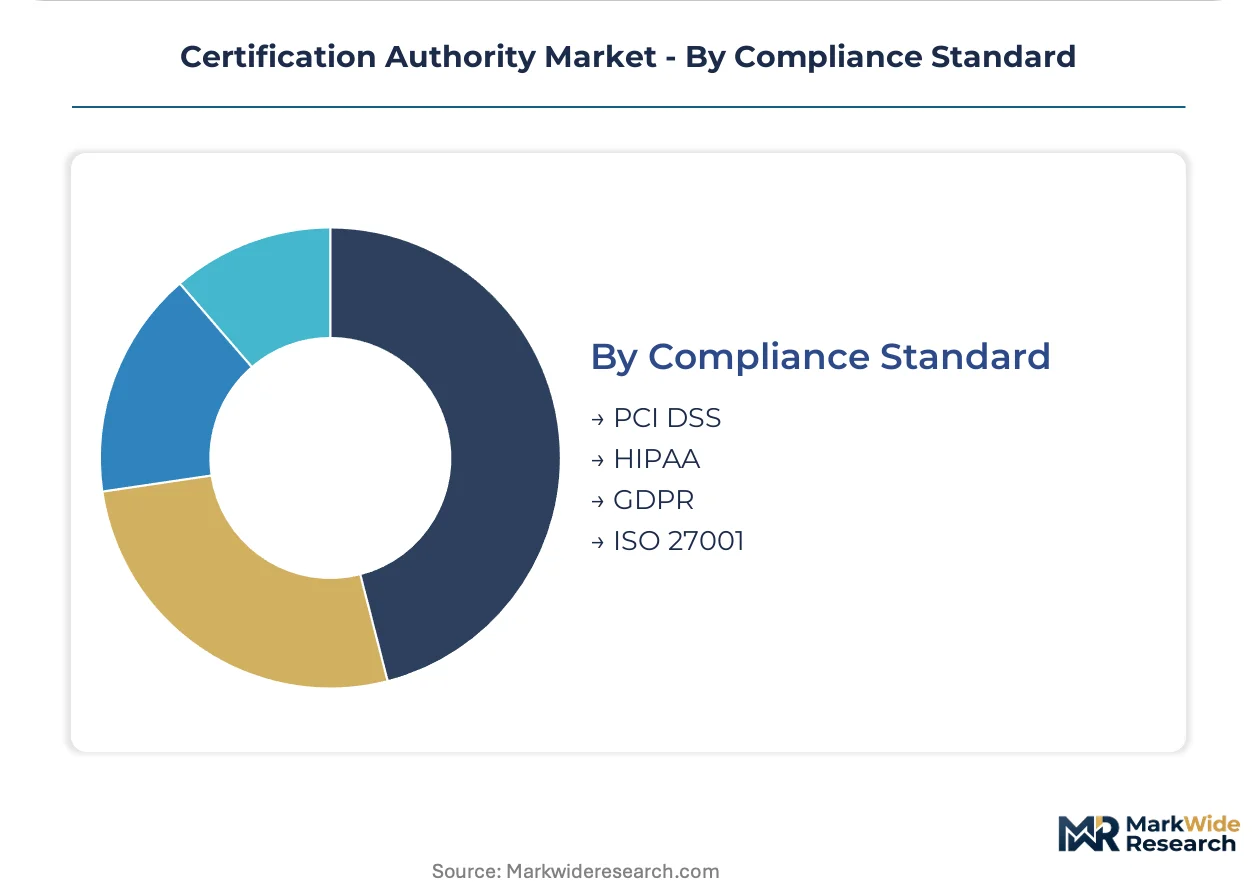
Regulatory frameworks fragment procurement specifications across sector-specific mandates and geographic enforcement regimes.
- PCI DSS:Payment card industry mandates drive annual certificate rotation and cipher suite compliance at German e-commerce platforms and Dutch payment processors.
- HIPAA:US healthcare encryption requirements influence certificate procurement for medical device manufacturers exporting to American hospital systems.
- GDPR:EU data protection law elevates qualified electronic signature demand for cross-border data processing agreements and breach notification workflows.
- ISO 27001:Information security management certification requires documented certificate lifecycle controls, favoring automated discovery and renewal platforms.
PCI DSS anchors the largest compliance-driven spend, while GDPR-qualified certificate requirements are expanding most quickly across legal and healthcare verticals.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
German trust service providers export qualified certificates to Dutch financial institutions and French healthcare networks under the eIDAS mutual recognition framework. This cross-border trade corridor anchors European digital identity infrastructure procurement.
United States
FERC critical infrastructure directives and NIST post-quantum cryptography standards drive certificate replacement cycles at energy sector operators. Federal procurement mandates FIPS 140-2 Level 3 HSM protection for root key ceremonies. Silicon Valley cloud providers and Washington DC defense contractors anchor high-assurance PKI demand.
Germany
Automotive OEMs mandate post-quantum cryptography readiness assessments across supply chain tiers. The BSI imposes qualified trust service standards for federal procurement and critical infrastructure. Munich and Stuttgart industrial clusters concentrate DevOps certificate automation deployments for connected vehicle platforms.
France
ANSSI cybersecurity certification requirements tighten digital identity specifications for nuclear operators and defense contractors. The EU AI Act imposes qualified certificate mandates for high-risk AI system authentication. Paris financial services firms and Lyon healthcare networks accelerate eIDAS-compliant electronic seal procurement.
Netherlands
Dutch payment processors and fintech scale-ups drive API-first certificate lifecycle management adoption. GDPR cross-border data processing agreements elevate qualified electronic signature demand. Amsterdam's cloud-native SaaS vendors reject annual capacity commitments in favor of consumption-based trust service pricing.
China
SAMR commercial cryptography rules and GB/T standards fragment cross-border certificate interoperability with foreign root stores. State-owned banks and telecommunications operators deploy domestic trust anchors under sovereign data localization mandates. Beijing and Shanghai technology corridors concentrate government-directed PKI infrastructure investment.
Certification Authority Market Competitive Environment
On the supply side, the industry is consolidating around three strategic tiers differentiated by assurance level and automation depth. FIPS-validated hardware security module operators anchor high-assurance procurement for defense and central banking sectors. Cloud-native API-first platforms capture mid-market DevOps demand through consumption-based pricing. Free ACME-automated authorities compress margins at the domain-validated base layer. Dominant competitive moves include post-quantum algorithm portfolio diversification and eIDAS qualified trust service geographic expansion.
Within the high-assurance tier, DigiCert and Entrust occupy positions defined by government trust relationships and FIPS 140-2 validated infrastructure. Sectigo sits within the cloud-native automation segment, exemplifying price-competitive mid-market positioning against free certificate alternatives. GlobalSign anchors European qualified trust service provision under eIDAS regulation.
| Leading Market Players |
|---|
| GoDaddy |
| IdenTrust |
| DigiCert |
| Amazon Trust Services |
| Internet Security Research Group |
| Sectigo |
| Entrust |
| Certum |
| GlobalSign |
| Others |
Value Chain & Pricing Dynamics
Overcapacity in domain-validated SSL/TLS issuance compresses margins across the certificate authority landscape, forcing suppliers toward premium code signing and qualified trust services where pricing power persists. German automotive OEMs and French defense contractors absorb higher costs for FIPS 140-2 Level 3 HSM-backed certificates, while automated cloud-native provisioning drives commoditization at the base tier.
Pricing Analysis
The pricing gap between classical RSA/ECC certificates and post-quantum hybrid offerings widens as NIST ML-KEM and ML-DSA standards mature, with early adopters paying premiums for cryptographic agility. Three-tier pricing structure across premium, standard, and economy levels separates extended validation certificates for financial services from domain-validated ACME-automated issuance and free Let's Encrypt alternatives. Cost compression in basic SSL/TLS is intensifying because hyperscaler cloud providers bundle certificates into infrastructure services. Small-business hosting customers exhibit highest price sensitivity, while central banks and defense ministries show near-zero elasticity for sovereign root key protection.
Supply Chain Analysis
Contract manufacturing concentration for FIPS 140-2 Level 3 validated hardware security modules rests on Thales, Entrust, and Utimaco production facilities in France, Germany, and the United States. Geographic supply concentration centers on European Union member states for eIDAS-qualified trust services, the United States for federal PKI infrastructure, and China for domestic commercial cryptography under SAMR rules. Raw material dependencies include tamper-resistant semiconductor substrates, cryptographic accelerators, and secure element chips. Single-source vulnerability in HSM firmware supply creates systemic risk for root key ceremonies. Distribution runs through direct enterprise sales for high-assurance deployments and API-first platforms for cloud-native consumption.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The certification authority market sits at a platform-economics inflection where API-first provisioning and ACME protocol standardization collapse switching costs, while eIDAS mutual recognition and post-quantum algorithm migration create new interoperability moats.
For Market Incumbents: Build regulatory-certification moats by accelerating eIDAS qualified trust service expansion into Dutch fintech and French healthcare networks. Anchor high-assurance positioning through FIPS 140-2 Level 4 HSM investments before NIST post-quantum mandates harden procurement specifications. DigiCert and Entrust face margin erosion from Sectigo's price-competitive automation unless they deepen vertical integration into managed certificate lifecycle services for DevOps pipelines. For New Entrants and Emerging Players: Mid-market SaaS vendors in the Netherlands and Nordic countries represent the most penetrable entry point, as these buyers reject annual capacity commitments and favor consumption-based API pricing. Post-quantum cryptography readiness assessments for German automotive supply chains offer specialized consulting attach. A go-to-market angle anchored in hybrid certificate offerings—combining classical and ML-DSA signatures—addresses immediate procurement anxiety without requiring full infrastructure replacement. For Investors and Strategic Acquirers: Capital-intensity ratios are inflecting upward across cloud-native certificate lifecycle management platforms as API infrastructure and multi-region redundancy requirements escalate. Long-term viability favors providers with established government trust relationships and eIDAS qualified status, as regulatory fragmentation raises barriers. Acquisition targets should demonstrate embedded DevOps workflows and post-quantum algorithm portfolios. The signal to watch is Bundesbank and ANSSI procurement timeline acceleration for quantum-resistant root hierarchies.| Strategic Initiative | Industry Significance |
|---|---|
| Post-Quantum Algorithm Integration | Hybrid ML-KEM and ML-DSA certificates address NIST standards and German automotive mandates. |
| eIDAS Geographic Expansion | Qualified trust service recognition unlocks Dutch payment processor and French healthcare procurement. |
| API-First Platform Development | ACME protocol embedding captures DevOps-centric demand at Nordic fintech scale-ups. |
| Managed Certificate Lifecycle Services | Outsourced operations attract mid-market manufacturers lacking cryptographic engineering depth. |
| HSM Infrastructure Upgrade | FIPS 140-2 Level 4 validation defends high-assurance positioning against Entrust and Thales. |
Study Parameters
Demand-side practitioners and supply-side operators were both consulted through structured primary interviews with PKI architects at German automotive OEMs, DevOps leads at Dutch fintechs, trust service managers at French defense contractors, and regulatory affairs specialists at eIDAS-supervised providers. Secondary validation drew from NIST post-quantum cryptography standard filings, EU eIDAS trusted list updates, BSI technical guidelines, ANSSI certification decisions, and FERC critical infrastructure directives. Bottom-up certificate issuance volume estimates and top-down market sizing were triangulated against hardware security module shipment data and cloud API call metrics.
Calibration against historical replacement cycles and regulatory compliance deadlines anchored the analytical framework across the projection horizon. Segmentation dimensions modeled include service type, client scale, delivery architecture, and compliance framework tier. CAGRs were derived from elasticity-adjusted adoption curves for post-quantum migration and automation penetration rates. Industry-specific forecast inputs incorporated EU AI Act implementation timelines and NIS2 Directive enforcement phase-ins.
Macroeconomic conditions sit as an overlay; deviation in central bank digital currency deployment schedules or quantum computing breakthrough timelines would shift the trajectory. Forecasts reflect documented assumptions regarding regulatory harmonization and cryptographic standard finalization. Quarterly review of BSI procurement bulletins and ANSSI certification queues is advised to detect inflection.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Global Visitor Management System Market
Security Software
Encryption Software Market
Security Software
Online Background Check Market
Security Software
Cloud Identity and Access Management Software Market
Security Software
Global Log Management Market
Security Software
User Provisioning Software Market
Security Software
Global Wireless Intrusion Prevention System Market
Security Software
Latin America Fraud Detection and Prevention Market
Security Software
Employee Surveillance and Monitoring Software Market
Security Software
Personal Data Recovery Software Market
Security Software
Website Monitoring Software Market
Security Software
Automotive Endpoint Authentication Market
Security Software
Enterprise Rights Management Solution Market
Security Software
Remote Access Management Market
Security Software
Global Data Masking Market
Security Software
Biometric POS Terminals Market