
 Cyber Deception Market | 2026-2036
Cyber Deception Market Size, Share, and Industry Trends Forecast 2026-2036
Cyber Deception Market Analysis
Static signature-based detection is shifting toward adaptive deception fabrics that dynamically spawn decoy assets, credentials, and data trails. CrowdStrike Holdings Inc. leverages cloud-native architecture to embed deception nodes directly within endpoint workloads. Illusive Networks Ltd. specializes in agentless credential and connection deceptions that map attacker lateral movement without production-system agents. Acalvio Technologies Inc. extends its platform through autonomous deception orchestration that spins up thousands of ephemeral honeytokens across hybrid infrastructure.
Cyber deception encompasses the deliberate deployment of fabricated digital assets, synthetic network segments, and bait credentials designed to detect, delay, and study unauthorized intrusions. Modern platforms integrate machine learning-driven decoy generation with automated incident response playbooks, achieving mean-time-to-detection reductions measured in minutes rather than months. Network deception solutions anchor the largest revenue pool today as enterprises retrofit existing VLAN architectures with fabric-based decoy deployment. Cloud-based delivery represents the fastest-expanding deployment mode, driven by managed security service providers seeking scalable multi-tenant deception operations without on-premises hardware overhead.
CMMC compliance requirements from the US Department of Defense reshape product standards by mandating deception capabilities as part of controlled unclassified information protection. The EU AI Act and NIS2 Directive impose algorithmic transparency and incident-reporting obligations on automated deception systems operating within European critical infrastructure. Stakeholders must monitor how emerging export-control frameworks treat deception-platform source code and threat-intelligence sharing mechanisms.
Market Dynamics
Zero-trust architecture mandates from the US Department of Defense are compressing enterprise deployment timelines and forcing security teams to replace static perimeter defenses with adaptive deception fabrics that spawn ephemeral decoy assets.
Growth Catalysts
- CMMC compliance deadlines:Defense contractors face mandatory deception capabilities for controlled unclassified information protection, accelerating procurement cycles across the federal supply chain.
- AI-generated synthetic environments:Machine learning-driven decoy generation cuts operational costs while extending attacker dwell-time metrics for threat intelligence collection.
- NATO member state procurement:European defense agencies are expanding active cyber defense operations through deception grid deployments.
Market Restraints
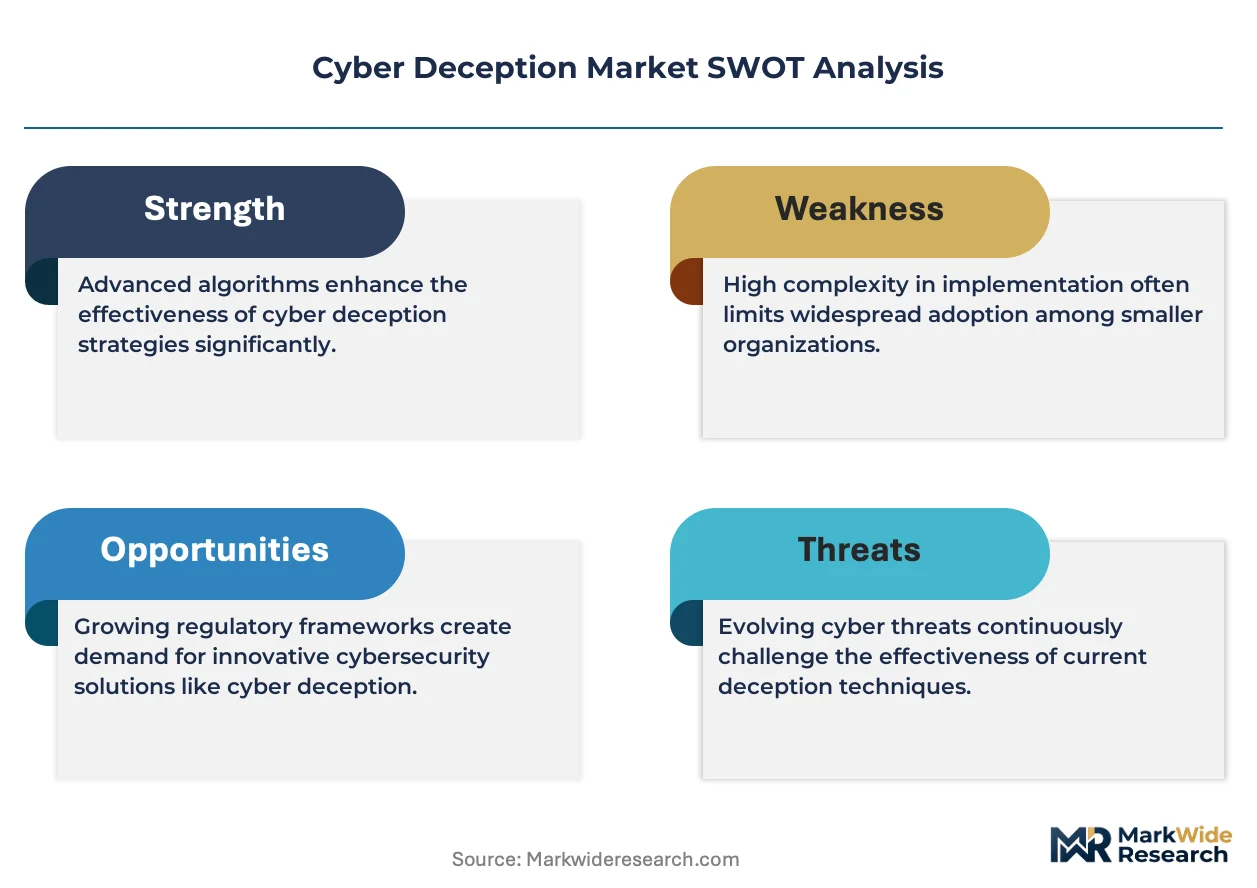
- Specialized talent scarcity:Shortage of adversary simulation engineers and deception architects limits enterprise scaling beyond pilot deployments.
- Integration friction with legacy SIEM:Established security information platforms lack native APIs for honeytoken telemetry ingestion.
- EU AI Act algorithmic transparency:Automated deception systems face explainability requirements that complicate machine learning model deployment.
Strategic Opportunities
- Managed deception services:Security service providers are building multi-tenant cloud platforms that eliminate on-premises hardware overhead for mid-market buyers.
- Operational technology convergence:Industrial control system operators seek deception fabrics that bridge IT-OT network boundaries.
- NIS2 Directive incident reporting:European critical infrastructure operators must deploy detection mechanisms that satisfy accelerated disclosure timelines.
Industry Challenges
- Attacker evasion techniques:Advanced persistent threat groups are developing fingerprinting methods to distinguish synthetic decoys from production assets.
- Cross-functional orchestration:Security teams struggle to align deception operations with incident response playbooks and threat hunting workflows.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cyber Deception Market |
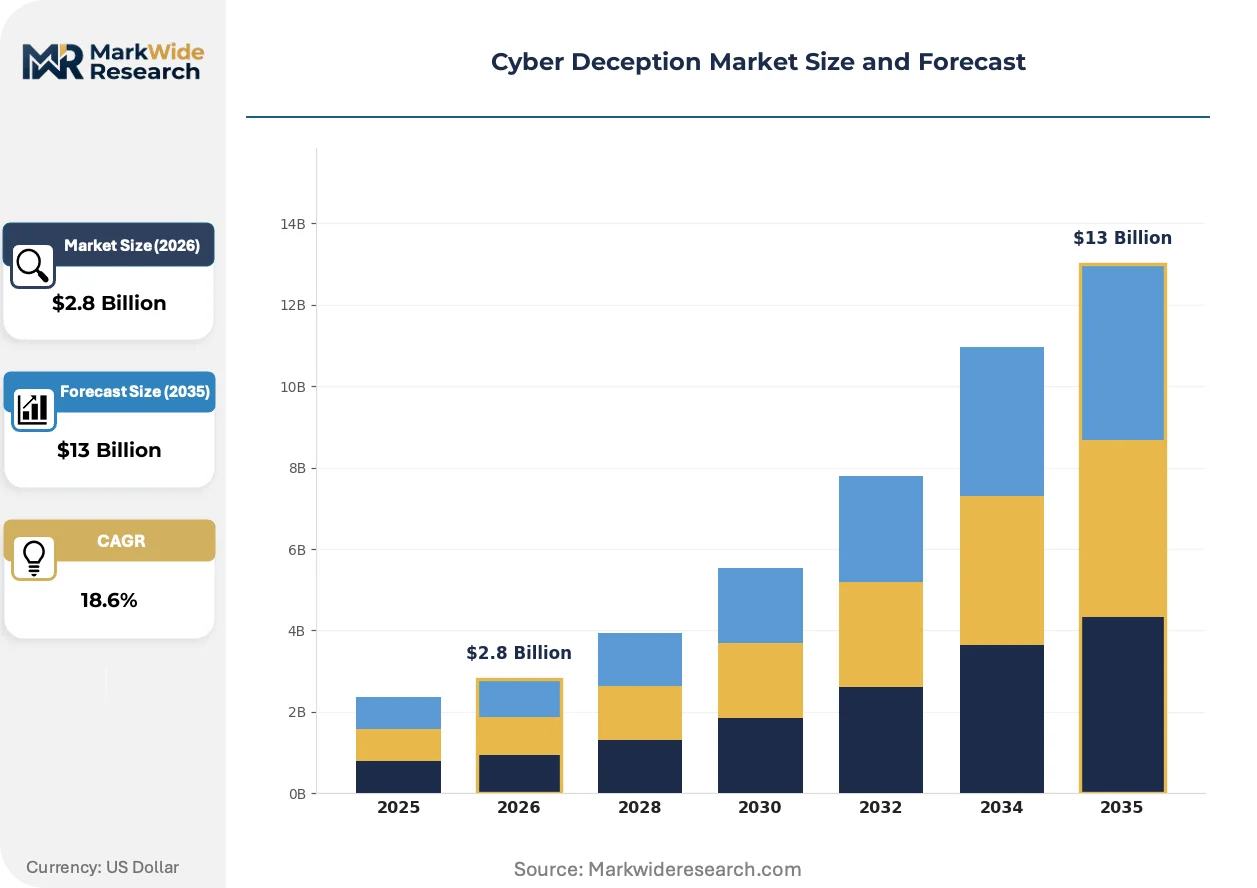
| Market Size in 2026 | $2.8 Billion |
| Market Size in 2035 | $13 Billion |
| CAGR (2026 – 2036) | 18.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution: Attack Simulation, Threat Intelligence, Security Orchestration, Network Deception End User: Financial Services, Government, Telecommunications, Healthcare Deployment: On-Premises, Cloud-Based, Hybrid, Managed Services Application: Fraud Detection, Threat Analysis, Incident Response, Vulnerability Management |
| Companies Covered | SentinelOne Inc., Akamai Technologies Inc., CrowdStrike Holdings Inc., Trend Micro Incorporated, Fortinet Inc., Rapid7 Inc., Illusive Networks Ltd., Acalvio Technologies Inc., Fidelis Cybersecurity LLC, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cyber Deception Market Emerging Trajectories
Agentless deployment architectures are displacing endpoint-heavy approaches, enabling security teams to map lateral movement without production system modifications. This shift is compressing time-to-value and expanding addressable markets.
Deception fabrics built on cloud-native microservices are decentralizing decoy orchestration across hybrid infrastructure. Financial services institutions are adopting these architectures fastest, spinning up thousands of ephemeral honeytokens that dissolve after detection events. The approach is decentralizing security operations center workflows and reducing mean-time-to-containment.
The EU AI Act imposes algorithmic transparency obligations on automated deception systems operating within European critical infrastructure. Industrial consequences include mandatory documentation of machine learning model decision pathways. Energy and telecommunications sectors are responding by demanding explainable decoy generation from platform vendors.
Security procurement is consolidating around integrated platforms that bundle deception with extended detection and response capabilities. Value-added resellers are displacing point-solution vendors as preferred channels. This consolidation is most visible in United States federal contracting, where CMMC compliance requirements favor full-stack security suites over standalone deception tools.
Cyber Deception Market Segmentation
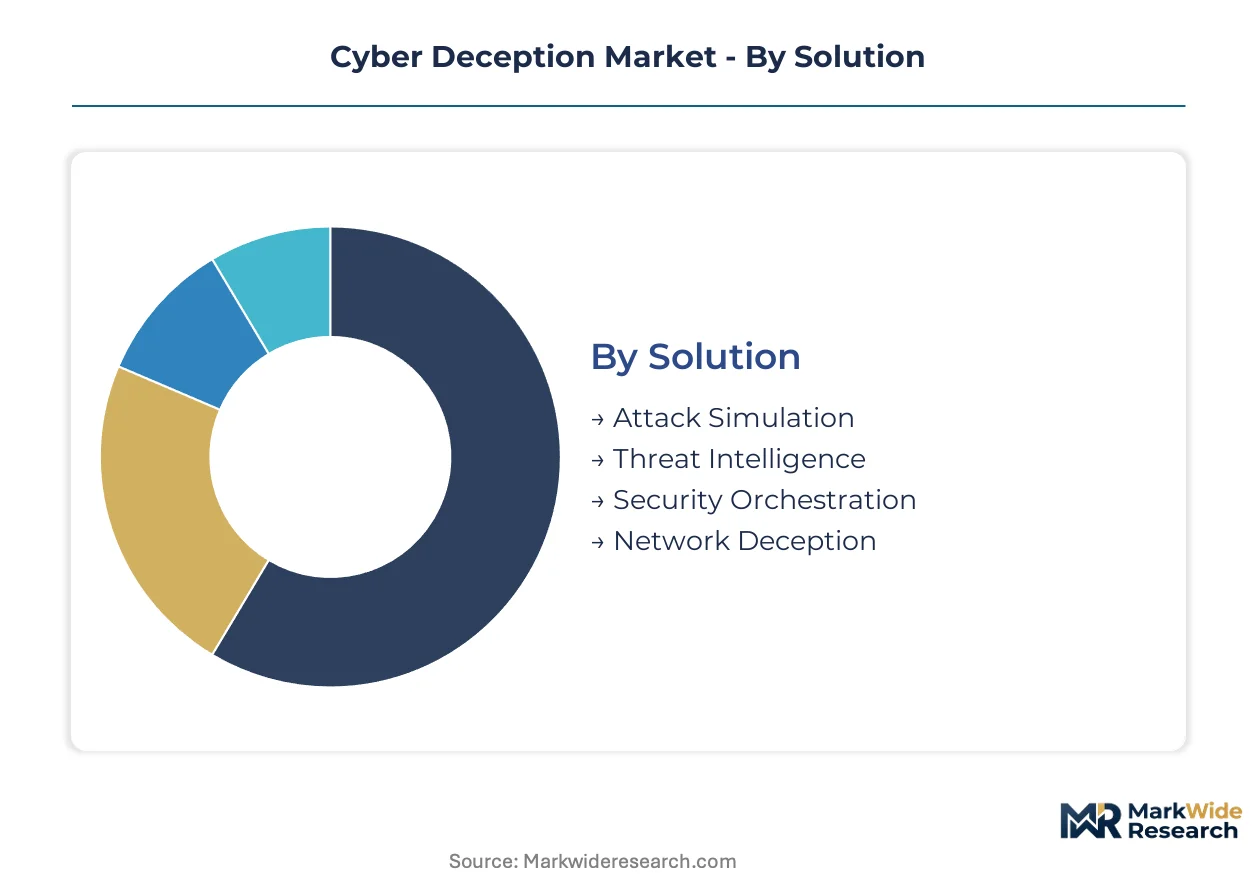
Segmentation in cyber deception reveals how procurement priorities diverge across compliance regimes and infrastructure maturity. Defense contractors prioritize CMMC-aligned solutions while commercial enterprises weigh cloud delivery against sovereign data requirements. Understanding these fault lines enables vendors to calibrate feature roadmaps and pricing architectures.
Solution:
CMMC mandates from the US Department of Defense primarily burden Network Deception and Attack Simulation deployments, requiring FedRAMP authorization and controlled unclassified information safeguards. Threat Intelligence and Security Orchestration face lighter certification loads but must still satisfy NIST 800-171 baseline controls.
- Network Deception:Fabric-based decoy deployment across VLAN architectures creates synthetic network segments that intercept lateral movement. Financial institutions in New York and London concentrate procurement here, driven by SWIFT network protection mandates and settlement system resilience requirements. The segment anchors current revenue concentration due to retrofit compatibility with existing switching infrastructure.
- Attack Simulation:Adversary emulation platforms automate breach-and-attack scenarios to validate detection coverage. NATO defense agencies and US federal contractors drive demand, compelled by continuous diagnostic and mitigation requirements under CMMC Level 2 and above. Vendors must maintain cleared personnel facilities for classified threat intelligence integration.
- Threat Intelligence:Deception-derived attacker telemetry feeds indicator enrichment and attribution workflows.
- Security Orchestration:Automated playbook execution coordinates decoy deployment with SIEM and SOAR platforms.
Leading the category by volume: Network Deception. Growing fastest: Attack Simulation.
End User:
Government and Financial Services segments command premium pricing tiers due to classified processing requirements and real-time transaction volume sensitivity. Healthcare and Telecommunications operate at lower cost thresholds but exhibit steeper adoption curves as regulatory deadlines compress.
- Financial Services:Real-time payment networks and custody operations deploy deception fabrics to isolate credential compromise before fund movement. Major banks in Singapore, Zurich, and Frankfurt prioritize agentless deployment to avoid latency in high-frequency trading environments. Regulatory pressure from the European Banking Authority and Monetary Authority of Singapore accelerates procurement cycles.
- Government:Defense and civilian agencies mandate deception capabilities for controlled unclassified information protection under CMMC and NIST frameworks. US federal contracting requirements now embed deception into security control baselines, forcing primes and subcontractors to demonstrate active cyber defense postures. Classified programs require air-gapped deployments with domestic supply chain provenance.
- Telecommunications:5G core network operators seek deception grids that protect signaling infrastructure without subscriber-visible latency.
- Healthcare:HIPAA-covered entities deploy credential deceptions to protect electronic health record systems from ransomware affiliates.
Dominant by procurement value: Financial Services. Expanding most quickly: Healthcare.
Deployment:
Cost-to-serve varies dramatically across delivery modes, with Managed Services capturing mid-market budgets and Hybrid deployments extracting maximum enterprise spend through professional services attachment.
- Cloud-Based:Multi-tenant SaaS platforms eliminate capital expenditure for deception infrastructure, enabling security service providers to deliver honeytoken orchestration at scale. Managed security service providers in Frankfurt, Sydney, and Toronto build regional instances to satisfy data residency requirements without on-premises hardware. The model compresses time-to-value from months to days.
- Managed Services:Fully outsourced deception operations include adversary simulation, threat hunting, and incident response integration. Mid-market enterprises in Manchester, Lyon, and Austin outsource deception architecture to avoid specialized hiring. Providers assume operational risk through outcome-based contracting structures.
- On-Premises:Air-gapped deployments satisfy classified and critical infrastructure environments with sovereign control requirements.
- Hybrid:Split orchestration across cloud control planes and on-premises decoy execution balances agility with compliance.
Widest addressable reach: Cloud-Based. Steepest margin expansion: Managed Services.
Application:
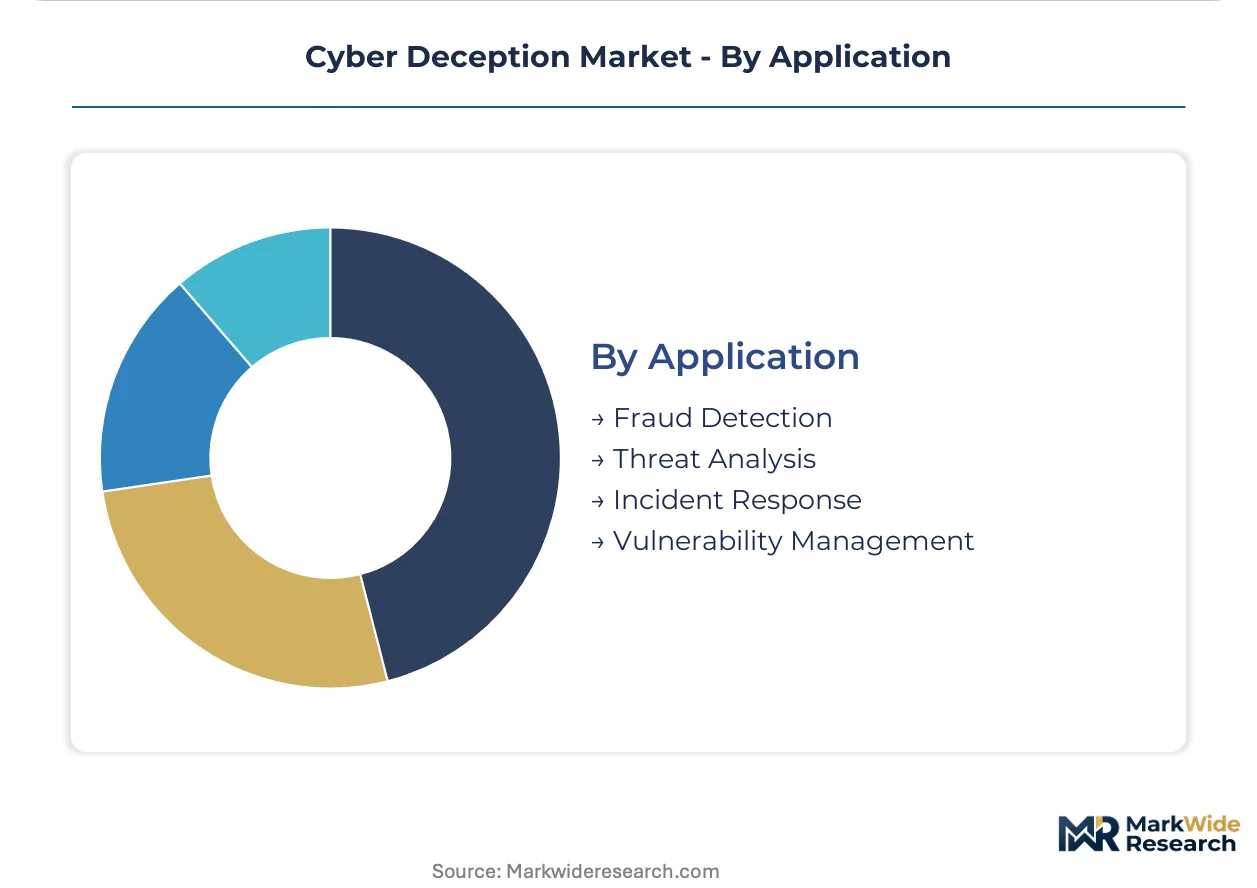
Incident Response and Threat Analysis applications mature earliest due to measurable dwell-time reduction metrics, while Fraud Detection and Vulnerability Management require longer validation cycles before procurement approval.
- Incident Response:Deception-triggered automation accelerates containment by isolating compromised segments before data exfiltration. Security operations centers in Chicago, Munich, and Tokyo measure mean-time-to-containment improvements in minutes rather than hours. The application justifies deception investment through quantified breach cost avoidance.
- Threat Analysis:Extended dwell-time in synthetic environments yields TTP documentation and attribution indicators for threat intelligence teams. Government cyber defense units in Tallinn, The Hague, and Ottawa prioritize this application for nation-state actor tracking. Machine learning models trained on deception telemetry improve production detection accuracy.
- Fraud Detection:Synthetic customer accounts and transaction patterns identify credential stuffing and synthetic identity schemes.
- Vulnerability Management:Deception-derived attacker path mapping prioritizes patching based on actual exploitation likelihood.
Highest deployment frequency: Incident Response. Gaining share fastest: Threat Analysis.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Defense procurement and financial regulatory pressure concentrate demand in the United States, Germany, United Kingdom, Japan, and Singapore, with each market exhibiting distinct compliance-driven deployment patterns.
United States
CMMC deadlines and zero-trust mandates compress deployment schedules across the federal supply chain. The Department of Defense requires deception capabilities for controlled unclassified information protection, forcing primes and subcontractors into accelerated procurement cycles. Security operations centers in Washington DC, San Antonio, and Seattle retrofit existing infrastructure with fabric-based decoy deployment.
Germany
NIS2 Directive incident-reporting obligations accelerate detection mechanism procurement for critical infrastructure operators. The EU AI Act imposes algorithmic transparency requirements on automated deception systems deployed in energy and telecommunications. Frankfurt and Munich host the densest concentration of managed security service providers building multi-tenant deception platforms.
United Kingdom
Financial services regulators in London mandate SWIFT network protection and settlement system resilience through synthetic network segments. The National Cyber Security Centre publishes active cyber defense guidance that elevates deception grid adoption across government and regulated industries. Edinburgh and Manchester emerge as secondary hubs for adversary simulation engineering talent.
Japan
METI cybersecurity frameworks for critical infrastructure emphasize IT-OT convergence, driving deception fabric deployment across industrial control systems. Tokyo and Osaka financial institutions prioritize agentless credential deception to avoid latency in high-frequency trading environments. The 2024 Olympics legacy accelerated public-private threat intelligence sharing mechanisms.
Singapore
The Monetary Authority of Singapore's technology risk management guidelines compel banking and payment network operators to deploy deception capabilities. The city-state's position as a regional cloud hub attracts managed deception service providers seeking Asia-Pacific data residency compliance. Cyber defense units in one-north and Changi Business Park integrate deception telemetry with regional threat hunting operations.
Cyber Deception Market Vendor Landscape
Platform consolidation dominates the current landscape as security vendors bundle deception with extended detection and response suites. The vendor base fragments across three tiers: cloud-native endpoint specialists, network fabric orchestrators, and managed security service providers. Two strategic archetypes have emerged: agentless credential deception architects and autonomous honeytoken orchestrators. M&A activity and strategic partnerships represent the dominant competitive vectors, with established platforms acquiring niche decoy-generation capabilities to fill portfolio gaps.
Within the cloud-native tier, CrowdStrike Holdings Inc. and SentinelOne Inc. exemplify endpoint-embedded deception architectures, while Illusive Networks Ltd. occupies a distinct position specializing in agentless lateral movement mapping. These three anchors demonstrate how geographic origin and corporate structure shape competitive positioning: US-based Inc. entities leverage federal contracting relationships, while Israeli Ltd. structures emphasize specialized engineering depth in credential deception.
| Leading Market Players |
|---|
| SentinelOne Inc. |
| Akamai Technologies Inc. |
| CrowdStrike Holdings Inc. |
| Trend Micro Incorporated |
| Fortinet Inc. |
| Rapid7 Inc. |
| Illusive Networks Ltd. |
| Acalvio Technologies Inc. |
| Fidelis Cybersecurity LLC |
| Others |
Supply Flow & Price Mechanics
US defense contractors concentrated under CMMC procurement mandates anchor pricing power with vendors holding FedRAMP authorization, compressing negotiation leverage and elevating subscription premiums for compliant deception fabrics. This buyer concentration feeds back into supply chain specialization, as vendors prioritize cleared personnel facilities and domestic engineering centers over cost-optimized offshore development.
Pricing Analysis
High-volume SaaS subscriptions for mid-market security service providers trade margin for scale, while low-volume air-gapped deployments for classified programs extract maximum value through professional services attachment. Price differentiation hinges on FedRAMP authorization tier and adversary simulation engineering depth, with cleared-facility vendors commanding substantial premiums over uncertified competitors. Cost compression in cloud-native delivery tiers is intensifying because hyperscaler infrastructure commoditizes basic honeytoken orchestration. Healthcare and telecommunications segments exhibit highest price sensitivity due to constrained security budgets, whereas defense primes demonstrate lowest sensitivity given compliance-driven procurement mandates.
Supply Chain Analysis
Single-source vulnerability sits with Israeli engineering talent pools specializing in agentless credential deception and adversary simulation methodologies. Software development concentrates in Israel, the United States, and India, with threat intelligence research anchored in Tallinn, The Hague, and Ottawa. Raw material dependencies include cloud compute capacity from hyperscalers, specialized machine learning training infrastructure, and cleared personnel for classified threat intelligence integration. Supply chain risk centers on export-control restrictions affecting deception-platform source code and cross-border threat-data sharing mechanisms. Distribution runs through value-added resellers displacing direct sales, particularly in US federal contracting channels where CMMC compliance requirements favor integrated security suites.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Adversary simulation engineering talent scarcity props pricing for vendors maintaining cleared personnel pipelines, creating supply-constrained conditions that favor incumbent consolidation over price competition.
For Market Incumbents: Anchor market position through backward integration into threat intelligence collection infrastructure and adversary simulation engineering academies. CrowdStrike Holdings Inc. and Illusive Networks Ltd. demonstrate how cleared-facility investments defend against emerging cloud-native entrants lacking federal contracting relationships. Certification maintenance in FedRAMP and CMMC alignment represents the critical lever for margin protection. For New Entrants and Emerging Players: NIS2 Directive in Germany opens a window for managed deception service providers targeting European critical infrastructure operators with accelerated incident-reporting obligations. Healthcare delivery organizations in Manchester, Lyon, and Austin present the most penetrable segment due to ransomware defense urgency and limited in-house security engineering. A channel partnership strategy with established managed security service providers offers the fastest path to revenue without direct enterprise sales infrastructure. For Investors and Strategic Acquirers: The window for entry favors specialist deception orchestration platforms with autonomous honeytoken generation capabilities. Long-term viability rests on machine learning model differentiation and integration depth with SIEM-SOAR ecosystems. The signal to watch is NATO member state procurement acceleration for active cyber defense grids, indicating sovereign demand inflection.| Strategic Initiative | Industry Significance |
|---|---|
| Autonomous Deception Orchestration | Acalvio Technologies Inc. demonstrates how ephemeral honeytoken scaling reduces operational overhead for hybrid infrastructure. |
| FedRAMP Authorization Investment | Defense contracting eligibility under CMMC mandates requires cleared personnel facilities and domestic supply chain provenance. |
| Agentless Architecture Development | Illusive Networks Ltd. proves credential deception without endpoint agents expands addressable markets in latency-sensitive trading environments. |
| Managed Security Service Partnership | Multi-tenant cloud platforms in Frankfurt and Sydney eliminate hardware overhead for mid-market buyers seeking rapid deployment. |
| Threat Intelligence Integration | Deception-derived telemetry feeds attribution workflows for government cyber defense units in Tallinn and Ottawa. |
Methodological Framework
Multi-period observation of CMMC procurement timelines, NATO defense agency deception grid deployments, and managed security service provider platform launches anchored the trend analysis, supplemented by interviews with deception architects, adversary simulation engineers, federal contracting officers, and critical infrastructure security directors. Secondary validation drew from Department of Defense budget justifications, EU NIS2 implementation guidance, SEC filings of publicly traded cybersecurity vendors, and hyperscaler infrastructure capex disclosures. Bottom-up segmentation modeling triangulated against top-down market sizing from defense procurement databases and enterprise security spending surveys.
Input-output matrices mapped deception solution adoption across deployment modes, end-user verticals, and application types throughout the forecast period. Segmentation dimensions modeled include solution category, organization size tier, infrastructure maturity level, and regional regulatory cluster. CAGRs were derived from deployment schedule compression analysis and procurement cycle acceleration indicators. Industry-specific forecast inputs encompassed CMMC compliance deadline phasing and EU AI Act algorithmic transparency implementation timelines.
The model assumes a particular technology adoption path; alternative pathways for AI-generated synthetic environments would alter the outlook if attacker evasion techniques outpace decoy realism improvements. Forecasts reflect assumptions regarding federal zero-trust mandate continuity and NATO collective defense spending trajectories. Outcomes are best read as a band of plausibility, not a single trajectory.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Global Content Disarm and Reconstruction Market
Cybersecurity
5G Security Market
Cybersecurity
Endpoint Protection Platforms (EPP) Market
Cybersecurity
Cybersecure Vehicle Control Unit Gateway Systems Market
Cybersecurity
Application Programming Interface Security Market
Cybersecurity
Global Cyber Security in Healthcare Market
Cybersecurity
LAMEA Deception Technology Market
Cybersecurity
Dark Web Intelligence Market
Cybersecurity
Thailand IT and Security Market
Cybersecurity
Germany Ransomware Protection Market
Cybersecurity
Cyber Security and Big Data Analytics Market
Cybersecurity
Global Cyber Threat Intelligence Market
Cybersecurity
Argentina Cybersecurity Market
Cybersecurity
Next-Generation Firewall Market
Cybersecurity
Europe SOC As a Service Market
Cybersecurity
Netherlands Cybersecurity Market