
 Artificial Intelligence-Based Cybersecurity Market | 2026-2036
Artificial Intelligence-Based Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Artificial Intelligence-Based Cybersecurity Market Outlook
GPU silicon is broadening cost-performance envelopes for neural inference at the network edge, displacing CPU-only architectures in high-throughput inspection nodes. Palo Alto Networks leverages its integrated platform strategy to anchor enterprise firewall-to-SASE transitions. CrowdStrike specializes in endpoint behavioral models that sustain recurring revenue density across mid-market accounts. Darktrace competes through self-learning topology mapping that occupies a distinct niche in anomaly detection for operational technology environments.
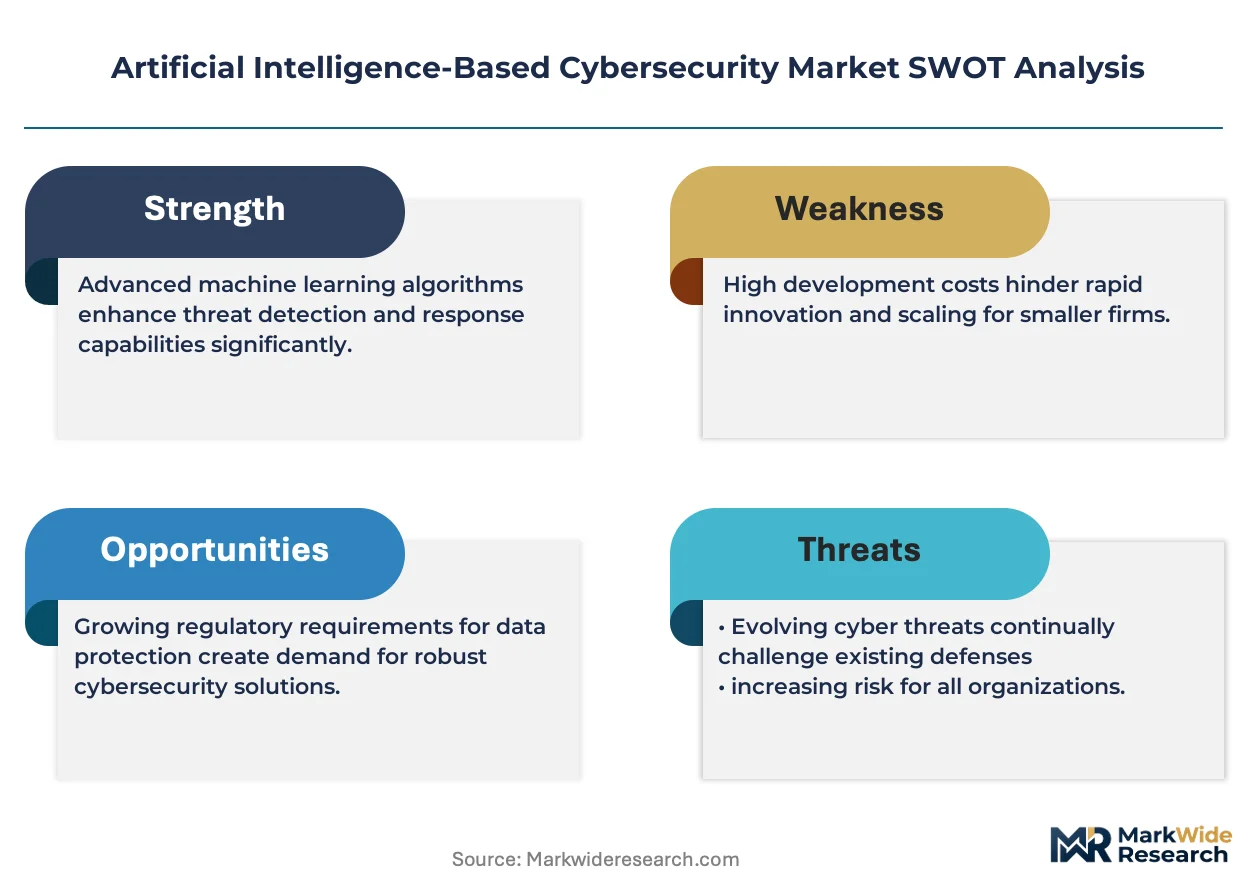
Artificial intelligence-based cybersecurity denotes systems that apply machine learning classifiers, deep neural networks, and statistical anomaly detection to identify, correlate, and autonomously respond to malicious activity across digital infrastructure at millisecond latency. These systems serve the primary commercial purpose of reducing mean-time-to-detect and mean-time-to-respond metrics below thresholds where human analysts alone become cost-prohibitive. Cloud Security now captures disproportionate R&D allocation as distributed workforces and multi-tenant architectures expand attack surfaces beyond traditional perimeter controls. Behavioral Analytics represents the fastest-growing technology segment because CISOs prioritize insider-threat and supply-chain compromise scenarios that signature-based tools miss consistently. Managed Service deployments are gaining share among enterprises lacking internal data-science benches to tune model drift and false-positive rates.
The EU AI Act classifies certain cybersecurity algorithms as high-risk systems, imposing conformity assessments that reshape vendor product roadmaps and go-to-market costs. In the United States, NIST's AI Risk Management Framework and SEC cyber disclosure rules compel publicly traded firms to document AI governance in incident response protocols. Stakeholders must monitor how divergent transatlantic compliance architectures affect cross-border SaaS delivery models and model-training data localization requirements.
Market Dynamics
GPU-accelerated neural inference at the network edge is compressing latency thresholds below human analyst response windows, forcing architectural decisions across enterprise security stacks.
Growth Catalysts
- Federal zero-trust mandates:United States government procurement cycles now require AI-native threat detection in critical infrastructure contracts, accelerating vendor certification timelines.
- Behavioral analytics priority:CISOs in financial services deploy machine learning classifiers to catch insider threats and supply-chain compromises that signature-based tools miss.
- Cloud security R&D concentration:Distributed workforces and multi-tenant architectures expand attack surfaces beyond traditional perimeter controls, pulling investment toward autonomous response systems.
Market Restraints
- Silicon supply concentration:Advanced GPU fabrication depends on Taiwan-based foundry capacity, creating single-point vulnerability for edge inference hardware procurement.
- EU AI Act compliance friction:Conformity assessments for high-risk cybersecurity algorithms add 12-18 month certification delays to European product launches.
- Model drift management costs:Enterprises lacking internal data-science benches face recurring service fees to tune false-positive rates and maintain classifier accuracy.
Strategic Opportunities
- Operational technology convergence:Self-learning topology mapping for industrial control systems addresses a white space where IT-centric vendors lack domain expertise.
- Managed service channel expansion:Mid-market accounts without security operations centers represent an underpenetrated buyer segment for outsourced AI-tuning services.
- NIS2 Directive tailwind:European critical infrastructure operators must deploy algorithmic accountability systems by 2024, creating mandated demand for compliant platforms.
Industry Challenges
- Adversarial ML expertise scarcity:Defensive teams lack practitioners trained to harden neural networks against poisoning attacks and evasion techniques.
- Cross-border data localization:Divergent transatlantic compliance architectures complicate SaaS delivery models and model-training data residency requirements.
- Legacy SIEM integration complexity:Enterprises with decade-old security information platforms face forklift upgrades to accommodate real-time inference pipelines.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Artificial Intelligence-Based Cybersecurity Market |
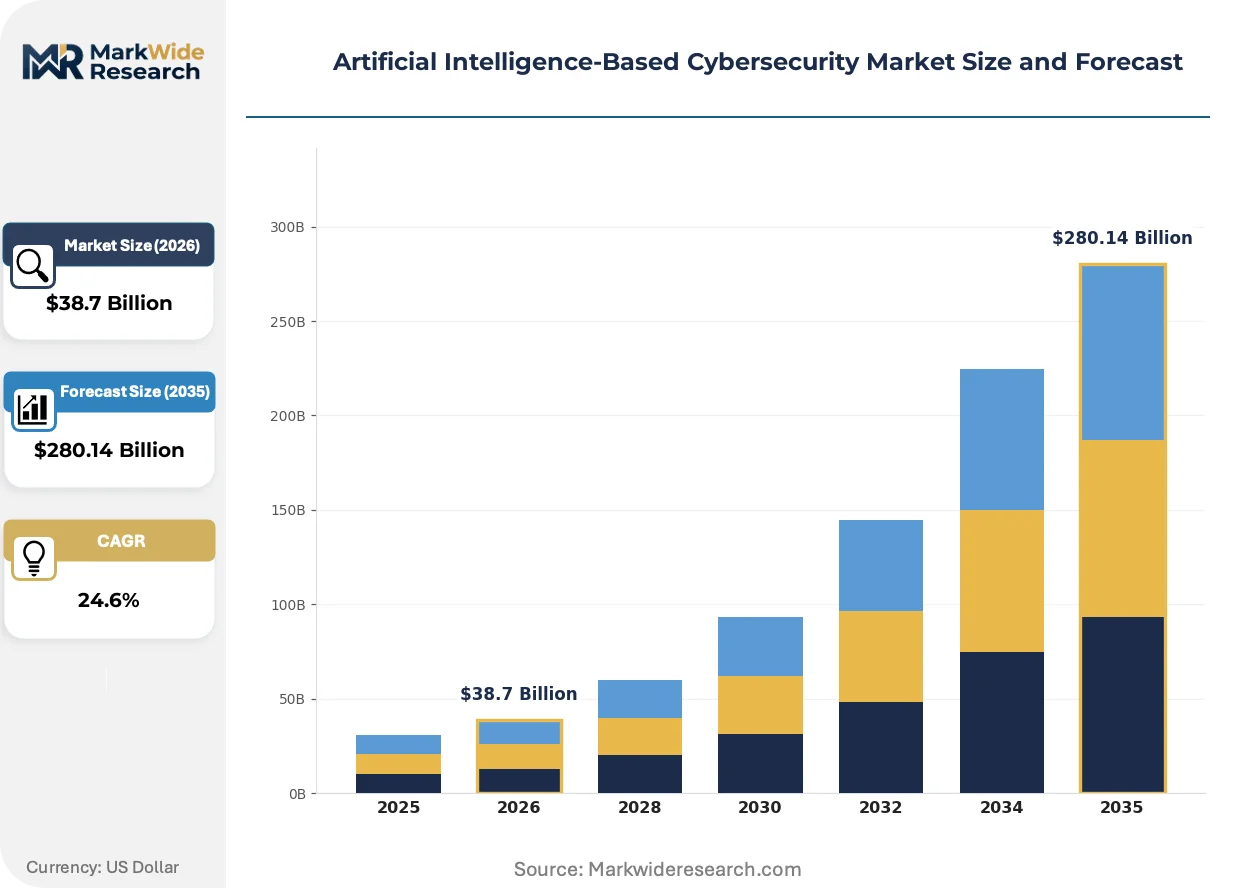
| Market Size in 2026 | $38.7 Billion |
| Market Size in 2035 | $280.14 Billion |
| CAGR (2026 – 2036) | 24.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Endpoint Security, Network Security, Application Security, Cloud Security Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Service End User: Enterprises, Government Agencies, Financial Institutions, Healthcare Organizations Technology: Machine Learning, Deep Learning, Behavioral Analytics, Threat Intelligence |
| Companies Covered | Check Point, Arctic Wolf, Palo Alto Networks, SentinelOne, Exabeam, CrowdStrike, Fortinet, Darktrace, Zscaler, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Artificial Intelligence-Based Cybersecurity Market Strategic Shifts
Security architecture is fragmenting into composable, API-driven components that buyers assemble rather than purchase as monolithic suites. This decomposition is redrawing vendor competitive boundaries.
Transformer-based large language models are modularizing security operations workflows by automating alert triage, incident documentation, and threat intelligence synthesis. Mid-market enterprises with lean security teams adopt these copilot interfaces fastest. The technology is modularizing tier-1 analyst functions into software-defined services that compress headcount requirements.
The EU AI Act imposes conformity assessments on cybersecurity algorithms classified as high-risk systems, forcing vendors to document training data provenance and model performance benchmarks. Product roadmaps now embed regulatory checkpoints earlier in development cycles. European critical infrastructure operators face the steepest compliance burden and are pre-qualifying vendors with established notified-body relationships.
Subscription-based managed detection and response is displacing perpetual-license endpoint protection among enterprises without internal data-science capabilities. Channel partners are building recurring revenue streams around model tuning and false-positive optimization. This shift is most visible in United States healthcare and financial services verticals where staffing constraints meet stringent breach-notification requirements.
Artificial Intelligence-Based Cybersecurity Market Segmentation
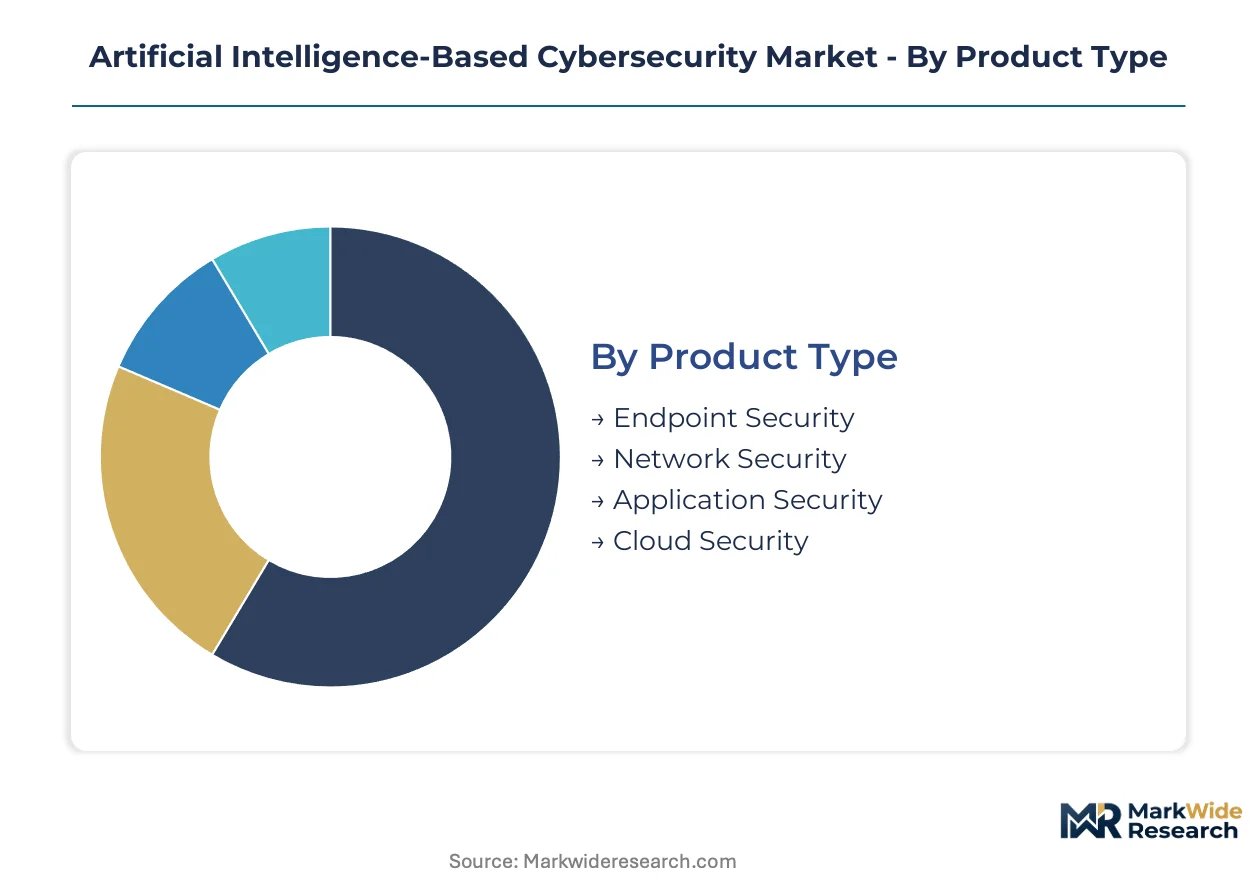
Segmentation in AI-based cybersecurity reveals how buyers prioritize autonomous response capabilities over legacy detection tools. Procurement patterns diverge sharply between organizations with internal data-science benches and those dependent on vendor-managed services.
Product Type:
Cloud Security commands premium pricing while Endpoint Security drives unit volume across mid-market accounts.
- Cloud Security:Autonomous workload protection for multi-tenant architectures and serverless compute environments. Financial institutions in the United States prioritize this segment to meet SEC cyber disclosure requirements for cloud-resident data.
- Endpoint Security:Behavioral classifiers deployed on laptops, mobile devices, and IoT endpoints to catch fileless malware and living-off-the-land techniques. Healthcare organizations lacking security operations centers favor managed deployments to offset staffing constraints.
- Network Security:GPU-accelerated deep packet inspection at network edges.
- Application Security:Runtime application self-protection for custom software portfolios.
Today's leader: Cloud Security. Tomorrow's challenger: Endpoint Security.
Deployment Model:
Managed Service offerings capture margin expansion opportunities while Cloud-Based deployments scale fastest among digital-native enterprises.
- Managed Service:Outsourced security operations where vendors tune model drift and false-positive rates on subscriber behalf. Mid-market accounts without internal data-science capabilities drive demand concentration in United States healthcare and financial services verticals.
- Cloud-Based:SaaS-delivered threat detection with API-native integration into existing security stacks. Technology firms and distributed workforces favor this model for rapid deployment without infrastructure procurement cycles.
- Hybrid:Split architectures retaining sensitive data processing on-premises.
- On-Premises:Air-gapped deployments for classified or regulated environments.
Managed Service claims the steepest expansion trajectory as skills scarcity persists.
End User:
Financial Institutions pay premium rates for real-time fraud detection while Government Agencies mandate compliance-certified procurement.
- Financial Institutions:Real-time transaction monitoring and anti-money laundering classifiers operating at millisecond latency. United States banks expand AI-driven threat detection budgets to counter authorized push payment fraud and synthetic identity schemes.
- Government Agencies:Classified workload protection with FedRAMP and zero-trust architecture mandates. Federal procurement cycles now require AI-native threat detection in critical infrastructure contracts.
- Enterprises:Cross-industry adoption spanning manufacturing to retail.
- Healthcare Organizations:HIPAA-aligned breach prevention for patient data repositories.
Financial Institutions dominate current spending. Government Agencies will accelerate fastest under NIS2-equivalent procurement rules.
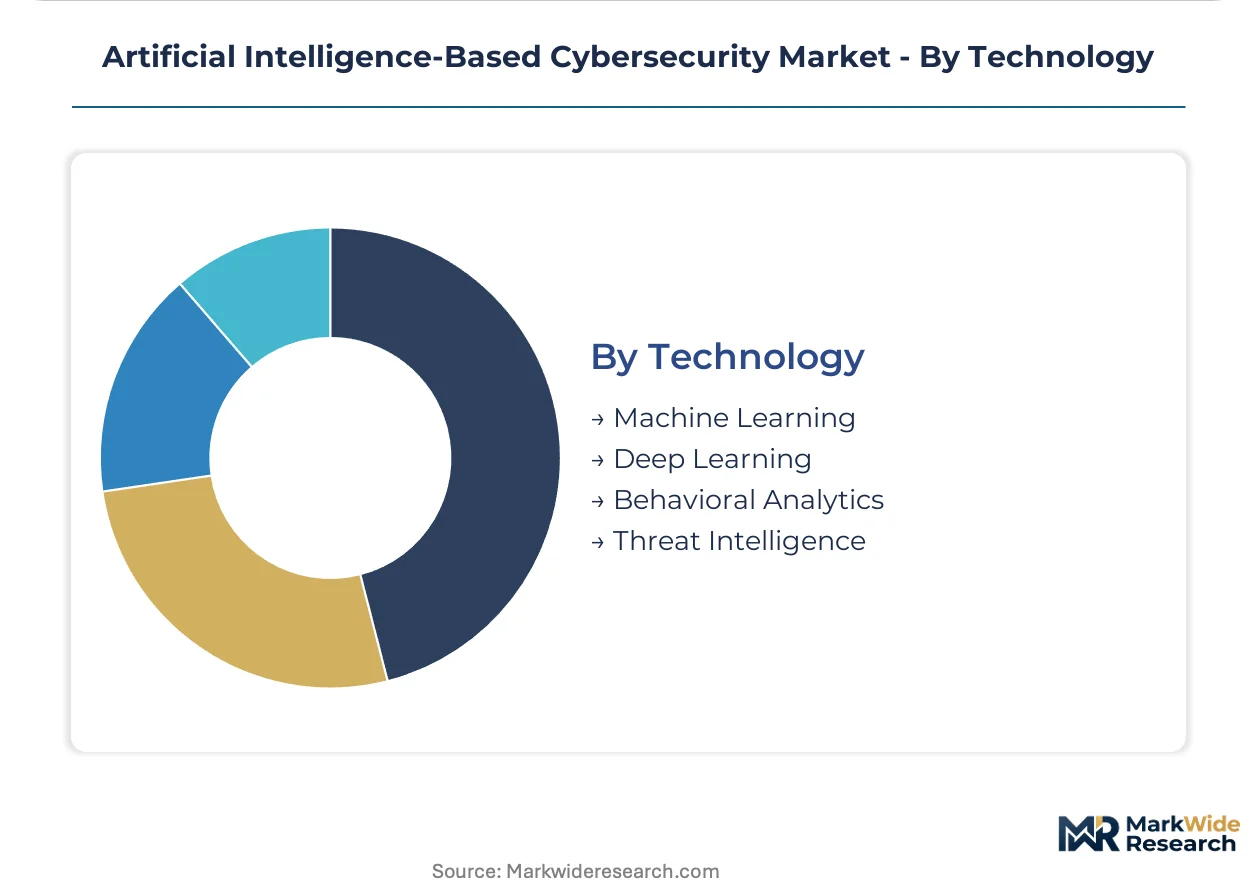
Technology:
Behavioral Analytics attracts R&D investment concentration while Machine Learning underpins baseline commercial deployments.
- Behavioral Analytics:Statistical anomaly detection identifying insider threats and supply-chain compromises that signature-based tools miss. CISOs prioritize this segment for operational technology environments where traditional indicators of compromise fail.
- Machine Learning:Supervised classifiers trained on labeled threat intelligence for known attack pattern recognition. Managed service providers leverage this technology for mid-market accounts requiring turnkey deployment without custom model development.
- Deep Learning:Neural architectures for unstructured data analysis and zero-day detection.
- Threat Intelligence:Curated indicator feeds and adversary tracking platforms.
Behavioral Analytics leads innovation pipelines. Deep Learning will challenge as GPU costs decline.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Silicon Valley's concentration of venture capital and security engineering talent anchors North American AI cybersecurity development. Federal procurement mandates and banking regulatory pressure generate concentrated demand in specific metropolitan clusters. National regulatory divergence creates distinct compliance architectures across major economies.
United States
Federal zero-trust architecture mandates and SEC cyber disclosure rules drive procurement concentration in Washington DC and New York financial corridors. NIST's AI Risk Management Framework compels documentation of algorithmic governance in incident response protocols. California's technology cluster generates disproportionate R&D investment in autonomous response systems.
Germany
Industrial control system vulnerability and automotive supply chain exposure generate demand for operational technology-specific solutions. The NIS2 Directive imposes algorithmic accountability requirements on critical infrastructure operators by 2024. Bavaria's manufacturing belt concentrates deployment of self-learning topology mapping for factory floor environments.
United Kingdom
Financial services regulatory pressure and Lloyd's cyber insurance requirements accelerate behavioral analytics adoption. The National Cyber Security Centre publishes AI security guidelines that shape vendor certification criteria. London's fintech corridor drives real-time fraud detection procurement at millisecond latency thresholds.
Japan
Manufacturing intellectual property protection and supply chain integrity concerns prioritize insider-threat detection capabilities. METI's cybersecurity framework emphasizes autonomous response for operational technology environments. The Kanto region's electronics cluster demands GPU-accelerated edge inference for high-throughput inspection nodes.
Singapore
Financial hub status and cross-border data flow governance generate demand for compliant SaaS security architectures. The Monetary Authority of Singapore's technology risk management guidelines mandate AI-native threat detection for digital banking licenses. The city-state's data center concentration attracts cloud security R&D investment from global vendors.
Artificial Intelligence-Based Cybersecurity Market Competitive Environment
Global majors compete with regional champions across platform integration versus specialized detection capabilities. The vendor base organizes into three tiers: integrated platform providers spanning firewall-to-SASE transitions, endpoint specialists sustaining recurring revenue through behavioral models, and anomaly detection pure-plays occupying industrial control niches. Strategic moves concentrate on M&A for data-science talent and API-native partnerships for security stack integration.
Within the integrated platform tier, Palo Alto Networks and Fortinet exemplify breadth-first strategies anchoring enterprise consolidation plays. CrowdStrike represents the endpoint-centric archetype with density-focused recurring revenue models. Darktrace occupies a distinct position in self-learning topology mapping for operational technology environments where IT-centric vendors lack domain expertise.
| Leading Market Players |
|---|
| Check Point |
| Arctic Wolf |
| Palo Alto Networks |
| SentinelOne |
| Exabeam |
| CrowdStrike |
| Fortinet |
| Darktrace |
| Zscaler |
| Others |
Value Chain & Pricing Dynamics
GPU silicon costs cascade through three-tier pricing structures across premium, standard, and economy levels, with Taiwan-foundry wafer prices dictating margin compression at the network edge before reaching federal procurement officers and mid-market CISOs.
Pricing Analysis
Input-cost pass-through from advanced semiconductor fabrication dominates vendor pricing strategies. Subscription-based SaaS tiers separate FedRAMP-authorized deployments from standard commercial licenses and economy managed service bundles. Pricing pressure stems from EU AI Act conformity assessment fees adding certification overhead to European launches. Government agencies demonstrate lowest price sensitivity due to zero-trust mandate compliance deadlines, while healthcare mid-market buyers negotiate aggressively on per-endpoint behavioral analytics licensing.
Supply Chain Analysis
Workforce availability constraints in Taiwan, South Korea, and the United States constrain advanced GPU packaging capacity for edge inference hardware. Supply chains draw from TSMC foundry output, HBM memory stacks, and specialized networking ASICs. Single-source vulnerability concentrates in Taiwan-based 3nm wafer production. Distribution runs through hyperscaler cloud marketplaces and certified federal procurement channels alongside traditional enterprise security VARs.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Geographic arbitrage between United States federal procurement premiums and EU compliance-cost absorption creates margin optimization opportunities for vendors with dual-certification capabilities.
For Market Incumbents: Deploy API-native platform consolidation to counter modular security stack fragmentation. Fortify FedRAMP authorization pipelines against emerging cloud-native challengers. Channel control through managed service partner certification programs defends recurring revenue density against behavioral analytics pure-plays.
For New Entrants and Emerging Players: Enter via operational technology self-learning topology mapping where IT-centric vendors lack industrial control domain expertise. Target German automotive supply chain operators under NIS2 Directive pressure. Go-to-market acceleration through notified-body pre-certification partnerships compresses European launch timelines.
For Investors and Strategic Acquirers: Consolidation pressure builds where adversarial ML expertise scarcity fragments defensive capability across mid-market portfolios. Five-to-ten year viability favors acquisition targets with established data-science benches and false-positive optimization IP. Watch GPU cost decline curves as inflection signal for deep learning segment displacement of behavioral analytics.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Palo Alto Networks anchors firewall-to-SASE transitions through unified threat intelligence fabric. |
| Acquisition of Specialist Firm | Adversarial ML talent scarcity drives rollup strategies for model-hardening capabilities. |
| Strategic Partnership | Hyperscaler marketplace listings accelerate federal procurement cycle compression. |
| Geographic Expansion | Notified-body relationships in Germany unlock NIS2-mandated critical infrastructure demand. |
| Product Launch | Transformer-based LLM copilot interfaces modularize tier-1 analyst functions for lean security teams. |
Study Parameters
Quantitative tracking and qualitative interviews ran in parallel throughout the study window, combining primary discussions with CISOs, federal procurement officers, managed service provider executives, and data-science team leads with secondary validation against SEC cyber disclosure filings, NIST AI Risk Management Framework documentation, FedRAMP authorization databases, and hyperscaler security marketplace transaction data. Bottom-up endpoint deployment estimates and top-down federal budget appropriations triangulated to segment-level outputs.
Segment-weighting approaches distributed value across cloud security, endpoint security, network security, and application security product types, further disaggregated by managed service, cloud-based, hybrid, and on-premises deployment models. Behavioral analytics, machine learning, deep learning, and threat intelligence technology segments carried distinct adoption curves across financial institutions, government agencies, enterprises, and healthcare organizations. CAGRs derived from procurement cycle velocity analysis and R&D concentration tracking, with GPU cost elasticity and regulatory checkpoint friction serving as industry-specific forecast modifiers.
The model holds under stable Taiwan-foundry capacity and linear EU AI Act enforcement; deviation in semiconductor export controls or notified-body processing delays would shift deployment timelines. Material deviation in named triggers warrants pause and re-evaluation.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Application Security Market
Cybersecurity
Global Information Security Consulting Market
Cybersecurity
France Cybersecurity Market
Cybersecurity
Global File Integrity Monitoring Market
Cybersecurity
Cyber Warfare Market
Cybersecurity
Romania Cybersecurity Market
Cybersecurity
Cloud-Based IDS IPS Market
Cybersecurity
Corporate Web Security Market
Cybersecurity
Cloud Siem Market
Cybersecurity
Global Network Security Policy Management Market
Cybersecurity
Argentina Cybersecurity Market
Cybersecurity
North America Digital Forensics Market
Cybersecurity
Application Programming Interface Security Market
Cybersecurity
Germany Ransomware Protection Market
Cybersecurity
Middle East Cybersecurity Market
Cybersecurity
Global Ransomware Protection Market