
 Greece Cybersecurity Market | 2026-2036
Greece Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Greece Cybersecurity Market Foresight
The Greek cybersecurity landscape is recalibrating around a widening gap between premium managed-detection services and commodity antivirus subscriptions. Palo Alto Networks leverages its next-generation firewall portfolio to anchor high-end enterprise accounts in Athens and Thessaloniki. Obrela Security Industries differentiates through native Security Operations Center capabilities that sustain long-term contracts with Greek banking groups. NVISO Greece competes on specialized penetration-testing services for EU-funded critical infrastructure projects.
Cybersecurity encompasses technologies, processes, and controls designed to protect systems, networks, and data from digital attacks, with firewalls operating at throughput rates exceeding 100 Gbps in enterprise deployments and encryption relying on AES-256 standards for data-at-rest protection. The solution dimension shows firewall and intrusion detection system spending outpacing antivirus as Greek organizations prioritize perimeter defense against advanced persistent threats. Cloud-based deployment is accelerating fastest among small and medium enterprises seeking to bypass capital-intensive on-premises infrastructure, while hybrid architectures dominate among financial institutions navigating NIS2 compliance timelines.
Greek cybersecurity procurement operates under the European Union's NIS2 Directive, which tightens incident-reporting windows to 24 hours and expands oversight to managed service providers, while the GDPR framework shapes data-breach notification obligations that drive demand for encryption and access-control solutions. The Hellenic Data Protection Authority enforces these standards through sector-specific audits of energy and telecommunications operators. Stakeholders must monitor how transposition of the EU Cyber Resilience Act into Greek national law will impose mandatory security-update obligations on connected device vendors serving the domestic market.
Market Dynamics
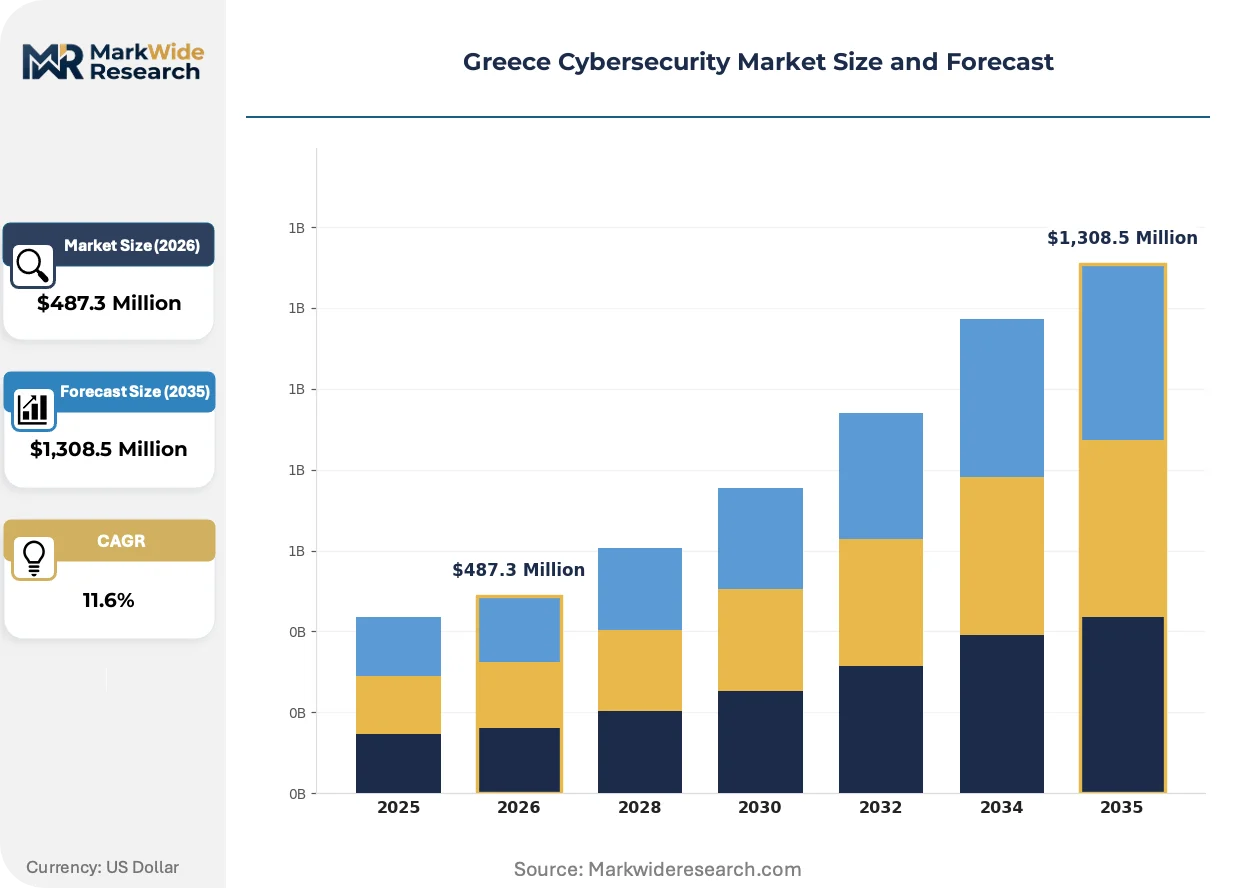
The Greek cybersecurity market is restructuring around NIS2 Directive compliance deadlines, with financial institutions and critical infrastructure operators accelerating procurement of managed detection and response services ahead of enforcement timelines.
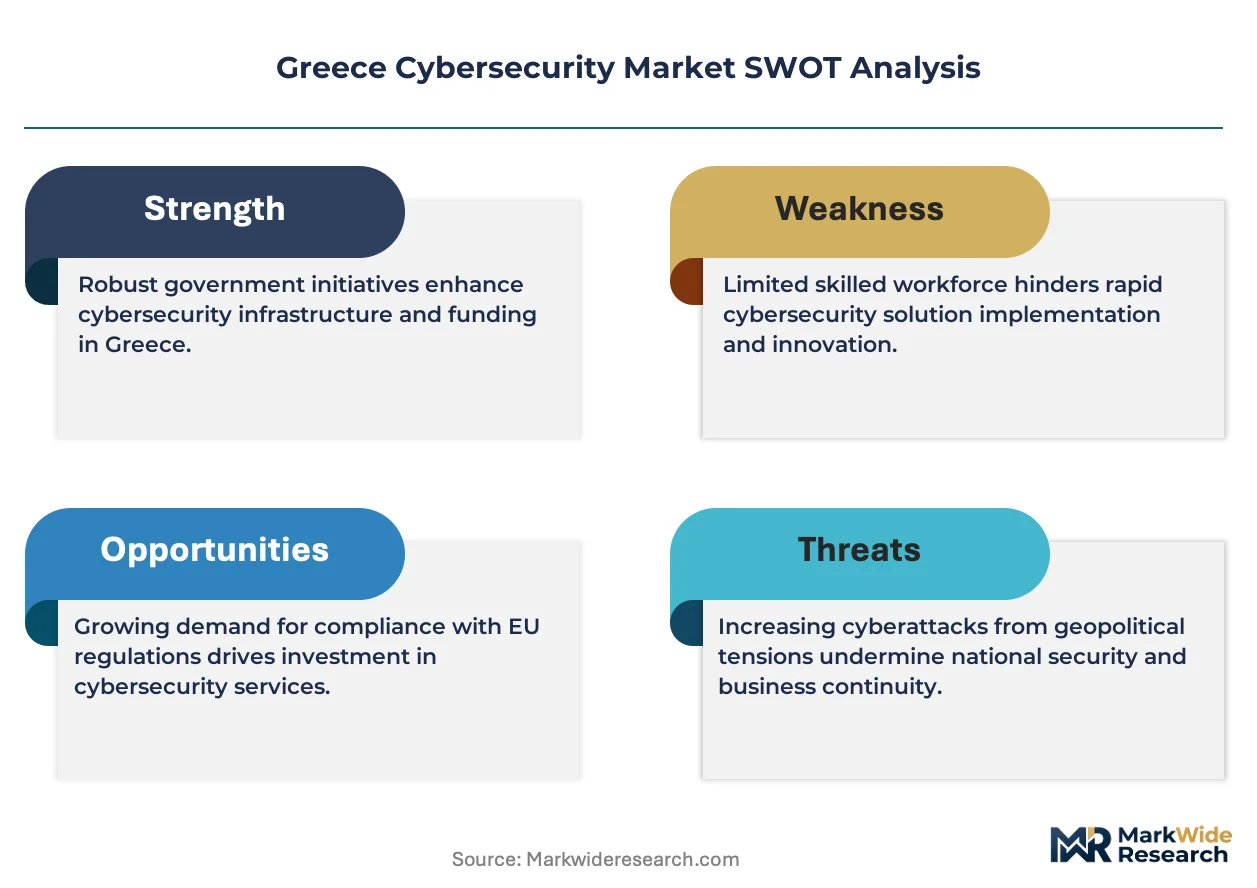
Growth Catalysts
- NIS2 Directive mandates:The European Union's expanded incident-reporting obligations and supply-chain security requirements are compelling Greek energy and telecommunications operators to upgrade monitoring infrastructure.
- Digital banking transformation:Greek retail and commercial banks are deploying next-generation firewalls and encryption layers to protect mobile payment platforms and open banking APIs.
- Athens critical infrastructure concentration:The clustering of government data centers and utility operators in the capital creates dense demand for on-premise security operations centers and specialized penetration-testing services.
Market Restraints
- Specialized talent scarcity:Greece produces insufficient certified security architects and incident response specialists relative to NIS2-driven hiring demand, inflating compensation costs.
- Cloud service provider concentration:Domestic small and medium enterprises rely heavily on three major hyperscale platforms for security-as-a-service, creating single-point-of-failure exposure.
- Legacy system interoperability:Public sector agencies maintain decades-old operational technology networks that resist modern endpoint detection and response agent deployment.
Strategic Opportunities
- Thessaloniki enterprise expansion:Northern Greece's second-largest city is attracting regional headquarters of multinational manufacturers seeking localized security operations center support.
- EU Cyber Resilience Act preparation:Greek systems integrators can capture pre-compliance consulting revenue by advising connected device importers on mandatory security update obligations.
- Zero-trust architecture convergence:The intersection of software-defined perimeter technology with identity and access management platforms opens integrated solution opportunities for domestic managed service providers.
Industry Challenges
- Certification timeline compression:Greek cybersecurity consultancies face capacity constraints delivering ISO/IEC 27001 and SOC 2 audit preparation services ahead of NIS2 transposition deadlines.
- Operational technology integration complexity:Industrial control system operators in Greek energy and water utilities struggle to segment legacy SCADA networks from IT environments without operational disruption.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Greece Cybersecurity Market |
| Market Size in 2026 | $487.3 Million |
| Market Size in 2035 | $1,308.5 Million |
| CAGR (2026 – 2036) | 11.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution: Firewall, Antivirus, Intrusion Detection System, Encryption End User: Government, Financial Institutions, Retailers, Healthcare Providers Deployment: Cloud-based, On-premises, Hybrid, Managed Services Industry Vertical: Telecommunications, Energy, Education, Transportation |
| Companies Covered | Palo Alto Networks, Inc., Microsoft Corporation, IBM Corporation, NVISO Greece, Obrela Security Industries, Cisco Systems, Inc., Check Point Software Technologies Ltd., Qualysec, Fortinet Inc., Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Greece Cybersecurity Market Shifts & Advancements
Extended detection and response platforms are displacing siloed point solutions across Greek enterprise security stacks, while regulatory pressure accelerates automation in compliance reporting workflows.
Cloud-native security information and event management architectures are expanding into mid-market manufacturing and logistics firms that previously relied on spreadsheet-based incident tracking. These organizations now demand API-first platforms that aggregate telemetry from Microsoft 365, Amazon Web Services, and on-premise Active Directory environments. The shift is expanding into managed service provider portfolios, compressing deployment timelines from quarters to weeks and enabling subscription revenue models that displace perpetual license arrangements.
The European Union's Cyber Resilience Act is mandating vulnerability disclosure programs and automatic security update capabilities for all connected devices sold in Greek retail and enterprise channels. Hardware importers and software distributors must now maintain product lifecycle documentation and incident response playbooks that satisfy national market surveillance authorities. Greek value-added resellers are responding by building technical compliance teams that bridge gap assessments and remediation engineering for device manufacturers lacking EU representation.
Greek CISOs are consolidating vendor relationships and demanding outcome-based service level agreements that specify mean-time-to-detect and mean-time-to-respond metrics rather than tool deployment counts. This procurement evolution is displacing multi-vendor best-of-breed strategies in favor of integrated platform contracts with single accountability. The pattern is most visible among Athens-based financial institutions navigating European Central Bank supervisory expectations for operational resilience.
Greece Cybersecurity Market Segmentation
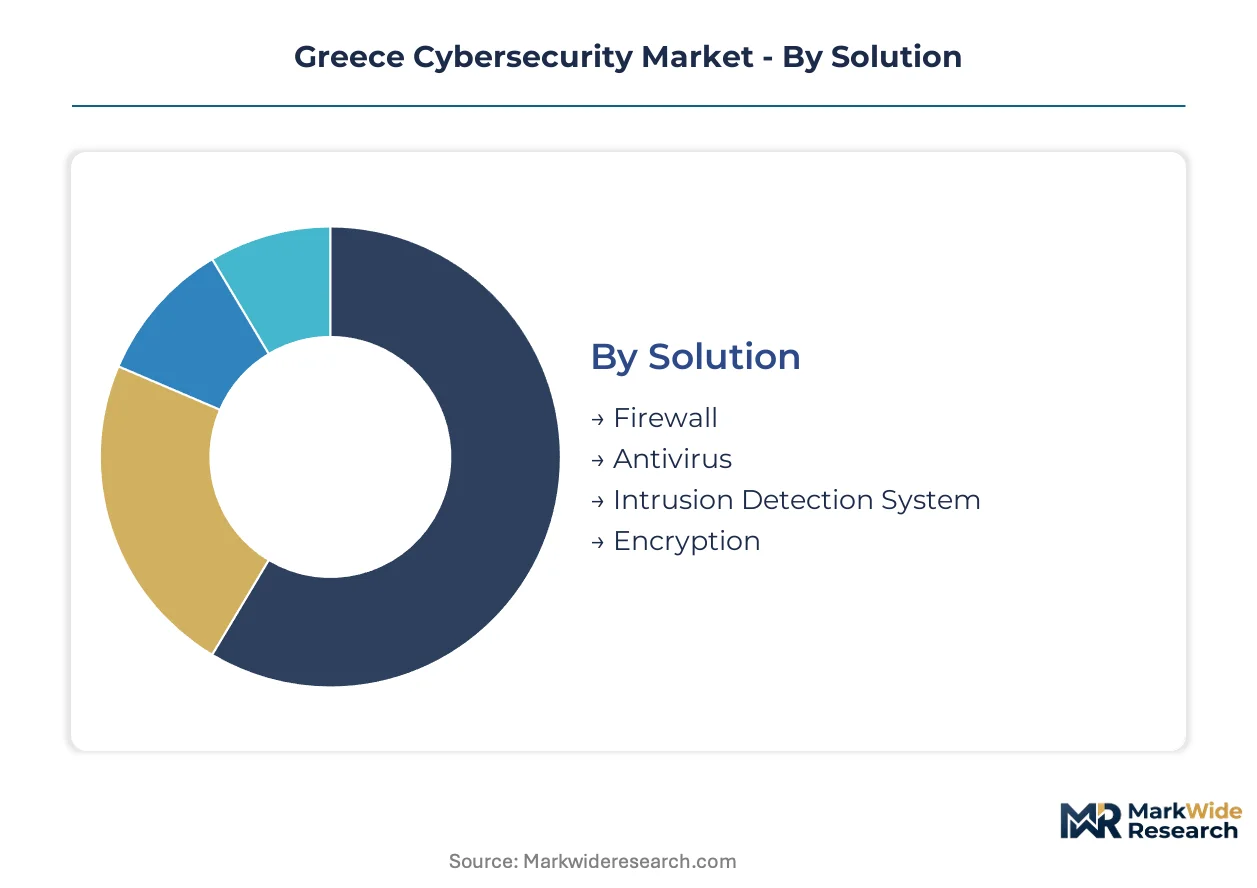
Greek cybersecurity procurement patterns diverge sharply across solution types and deployment models, with NIS2 Directive timelines forcing prioritization decisions that reshape budget allocation. Financial institutions and critical infrastructure operators drive premium segment growth while constrained public sector budgets compress mid-market alternatives.
Solution:
Certification requirements under the EU Cyber Resilience Act and Hellenic Data Protection Authority audits concentrate most heavily on firewall and encryption deployments, where ISO/IEC 27001 attestation is mandatory for government contracts.
- Firewall:Next-generation platforms with application-layer inspection and 100+ Gbps throughput anchor enterprise perimeter defense. Athens-based banking groups prioritize these for open banking API protection under European Central Bank supervisory pressure.
- Encryption:AES-256 implementations for data-at-rest and TLS 1.3 for data-in-transit dominate compliance-driven procurement. Healthcare providers and government data centers in Athens cluster demand here to satisfy GDPR breach-notification obligations.
- Intrusion Detection System:Network-based and host-based variants with behavioral analytics detect anomalous traffic patterns in SCADA environments.
- Antivirus:Signature-based endpoint protection faces displacement by extended detection and response platforms in enterprise accounts.
Leading the category by volume: Firewall. Expanding most quickly: Encryption.
End User:
Procurement scale and compliance urgency separate government and financial institution buyers from retail and healthcare segments operating under tighter margin constraints.
- Government:Central ministries and regional administrations deploy hybrid security operations centers with sovereign data residency requirements. NIS2 transposition deadlines accelerate Athens data center consolidation projects.
- Financial Institutions:Retail and commercial banks fund the largest managed detection and response contracts. Digital banking transformation and PSD2 open banking obligations drive next-generation firewall and identity platform spending.
- Retailers:E-commerce platforms and payment processors seek PCI-DSS compliant point-to-point encryption for cardholder data environments.
- Healthcare Providers:Hospital networks and diagnostic chains prioritize medical device security and patient record access controls under GDPR enforcement.
Dominant procurement volume: Financial Institutions. Steepest budget expansion trajectory: Government.
Deployment:
Capital availability and internal technical capacity determine whether Greek organizations absorb infrastructure costs directly or shift to operational expenditure models through managed service providers.
- Cloud-based:Subscription security-as-a-service enables small and medium enterprises to bypass capital-intensive hardware procurement. Manufacturing and logistics firms in Thessaloniki adopt API-first platforms aggregating Microsoft 365 and Amazon Web Services telemetry.
- Managed Services:Outsourced security operations centers deliver 24/7 monitoring without internal specialist recruitment. Greek banking groups favor these to address certified security architect scarcity while meeting NIS2 incident-response timelines.
- Hybrid:Financial institutions combine on-premise encryption appliances with cloud-native analytics to navigate compliance transitions.
- On-premises:Legacy data center operators and classified government facilities maintain air-gapped security stacks.
Highest adoption rate: Cloud-based. Fastest-growing contract value: Managed Services.
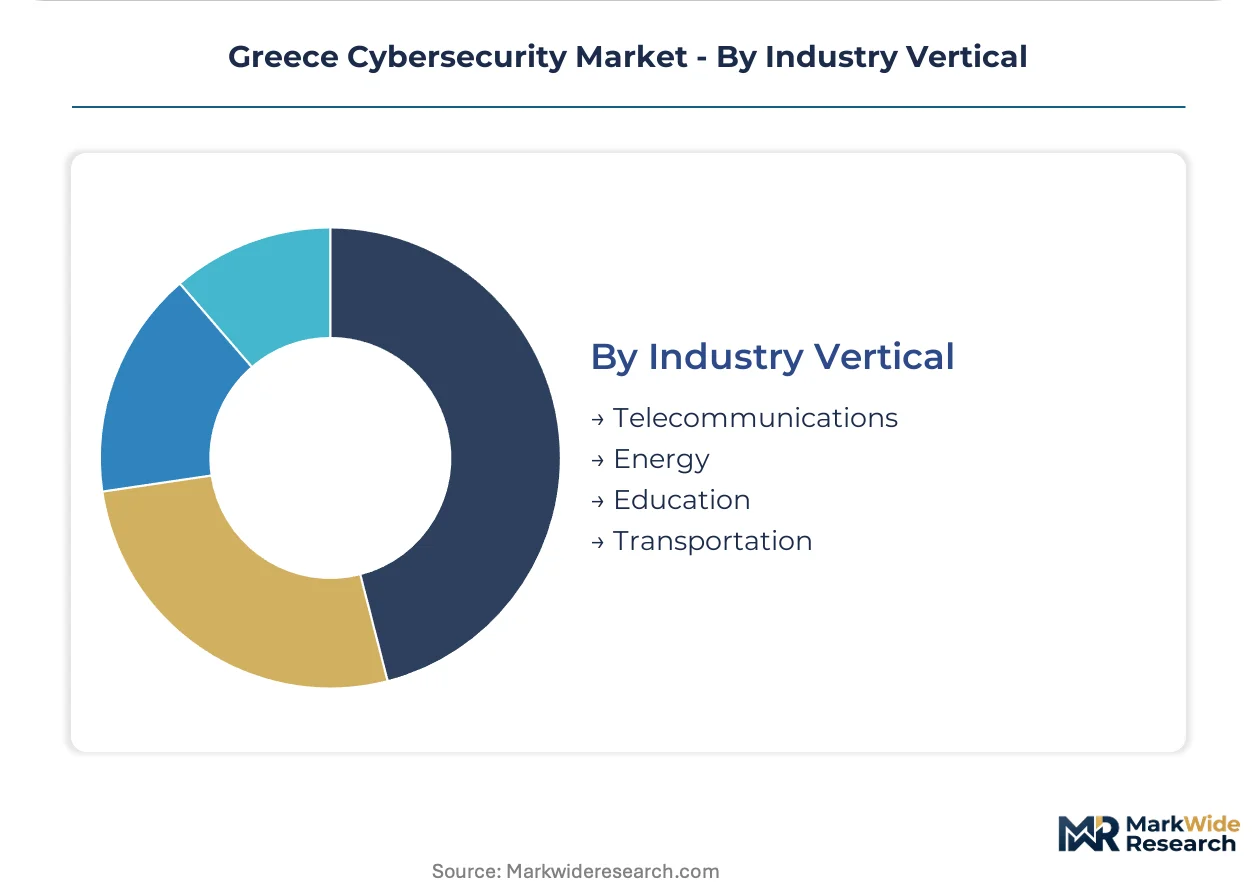
Industry Vertical:
Critical infrastructure designation under NIS2 elevates telecommunications and energy operators above education and transportation in security investment priority.
- Telecommunications:Mobile network operators and internet service providers face mandatory supply-chain security audits and 24-hour incident reporting windows. 5G core network segmentation drives zero-trust architecture adoption.
- Energy:Electricity transmission operators and natural gas distributors struggle to integrate modern endpoint detection with legacy SCADA systems. The Hellenic Data Protection Authority conducts sector-specific audits of operational technology security.
- Education:Universities and research institutions deploy identity and access management for distributed student and faculty populations.
- Transportation:Port authorities and airline operators implement perimeter defense for logistics management systems.
Top investment intensity: Telecommunications. Gaining regulatory attention fastest: Energy.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Athens concentrates Greek cybersecurity demand through its clustering of government data centers, banking headquarters, and critical infrastructure operators. The metropolitan area anchors national procurement patterns while regional disparities in technical talent and compliance urgency shape sub-national market development.
Attica Region
Attica hosts the Hellenic Data Protection Authority headquarters and European Central Bank-supervised financial institutions driving managed detection and response contracts. NIS2 Directive transposition deadlines accelerate security operations center consolidation in Athens data centers. Piraeus port authorities implement perimeter defense systems for logistics management platforms.
Central Macedonia
Thessaloniki attracts regional headquarters of multinational manufacturers seeking localized security operations center support beyond Athens congestion. Cloud-native security information and event management platforms expand among mid-market manufacturing firms in the Thermi technology zone. The city's universities produce certified security architects addressing national talent scarcity.
Peloponnese
Energy transmission operators in the Peloponnese struggle with legacy SCADA network segmentation under Hellenic Data Protection Authority operational technology audits. Electricity distribution utilities modernize monitoring infrastructure ahead of NIS2 enforcement timelines. The Patras industrial corridor sees incremental zero-trust architecture pilot programs.
Crete
Heraklion and Chania healthcare networks prioritize medical device security and patient record access controls under GDPR enforcement patterns. Hospital procurement concentrates on encryption solutions for diagnostic data environments. The island's tourism-dependent payment processors seek PCI-DSS compliant point-to-point encryption systems.
Greece Cybersecurity Market Competitive Landscape
Capital-heavy platform vendors compete with asset-light specialized service providers across the Greek cybersecurity landscape. The vendor base organizes around three strategic tiers: multinational platform enterprises with direct Athens presence, regional managed security service providers with native Security Operations Center capabilities, and boutique penetration-testing specialists serving EU-funded infrastructure projects. Dominant competitive moves include geographic expansion into Thessaloniki enterprise accounts and portfolio diversification toward zero-trust architecture integration.
Within the multinational platform tier, Palo Alto Networks and Microsoft Corporation occupy positions anchored by next-generation firewall and cloud-native security portfolios. Among regional specialists, Obrela Security Industries exemplifies the native Security Operations Center archetype sustaining long-term banking contracts, while NVISO Greece represents the compliance-focused penetration-testing segment serving critical infrastructure operators. These three anchors illustrate the competitive structure: global platforms compete on technology breadth, regional providers on service proximity, and specialists on regulatory expertise.
| Leading Market Players |
|---|
| Palo Alto Networks, Inc. |
| Microsoft Corporation |
| IBM Corporation |
| NVISO Greece |
| Obrela Security Industries |
| Cisco Systems, Inc. |
| Check Point Software Technologies Ltd. |
| Qualysec |
| Fortinet Inc. |
| Others |
Supply & Pricing Matrix
NIS2 Directive compliance deadlines gate both qualified supply and premium-tier pricing access, as Greek cybersecurity procurement increasingly demands certified managed detection and response providers with native Security Operations Center capabilities. Vendors lacking ISO/IEC 27001 attestation or documented incident-response playbooks find themselves excluded from government and financial institution contracts, compressing margins in the commoditized antivirus segment while enabling outcome-based pricing premiums for qualified suppliers.
Pricing Analysis
Outcome-based pricing anchors Greek enterprise cybersecurity contracts, with mean-time-to-detect and mean-time-to-respond metrics replacing tool-deployment counts in service level agreements. Three-tier pricing structure across premium, standard, and economy levels separates managed detection and response bundles from cloud-native security information and event management platforms and basic antivirus subscriptions. Pricing pressure stems from hyperscale platform concentration among small and medium enterprises seeking security-as-a-service alternatives. Retailers and healthcare providers exhibit highest price sensitivity, while Athens-based banking groups prioritize performance guarantees over unit cost.
Supply Chain Analysis
Regional distribution centers in Frankfurt, London, and Amsterdam anchor hardware appliance delivery to Greek data centers, with hub-and-spoke patterns routing next-generation firewalls and encryption appliances through Athens logistics corridors. Taiwan and the United States supply specialized semiconductor components for high-throughput security appliances, while Ireland and the Netherlands host cloud infrastructure serving Greek software-as-a-service deployments. Single-source vulnerability in certified security architect talent inflates implementation costs and extends deployment timelines. Distribution runs through authorized value-added resellers with technical compliance teams bridging gap assessments for device manufacturers.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Greek cybersecurity vendors face a vertical-integration race, with backward integration into native Security Operations Center capabilities emerging as the decisive lever for sustaining long-term banking contracts against multinational platform competition.
For Market Incumbents: Anchor market position through ISO/IEC 27001 certification investment and Security Operations Center capacity expansion in Thessaloniki. Defend against Palo Alto Networks and Microsoft platform consolidation by embedding outcome-based service level agreements with named mean-time-to-respond guarantees. Deepen upstream control over certified incident response specialist pipelines through university partnership programs addressing national talent scarcity. For New Entrants and Emerging Players: Enter via EU Cyber Resilience Act compliance consulting for connected device importers lacking Greek market representation. Target Peloponnese energy utilities struggling with legacy SCADA network segmentation as the most penetrable vertical outside Athens banking saturation. Pursue zero-trust architecture integration partnerships with domestic managed service providers seeking software-defined perimeter capabilities. For Investors and Strategic Acquirers: NIS2 enforcement timeline acceleration is the leading indicator that managed detection and response contract values will compress competitive returns for pure-play antivirus vendors. Position acquisition screening around regional specialists with native Security Operations Center capabilities and documented banking group relationships. Monitor Hellenic Data Protection Authority audit frequency as the signal for compliance-driven procurement inflection.| Strategic Initiative | Industry Significance |
|---|---|
| Security Operations Center Expansion | Thessaloniki facilities capture multinational manufacturing demand beyond Athens congestion. |
| Zero-Trust Architecture Integration | Software-defined perimeter platforms intersect with identity management for financial institutions. |
| EU Cyber Resilience Act Compliance Services | Technical compliance teams bridge gap assessments for device manufacturers without EU representation. |
| Certified Talent Pipeline Development | University partnerships address security architect scarcity inflating implementation costs. |
| Outcome-Based Service Level Agreements | Mean-time-to-detect metrics displace tool-deployment pricing in Athens banking procurement. |
Research Methodology
Trade association data, regulatory filings, and customs records anchored secondary inputs, combined with primary interviews across CISOs at Greek financial institutions, security operations center directors, Hellenic Data Protection Authority officials, value-added reseller technical leads, and critical infrastructure procurement officers. Hellenic Association of Enterprises and Industries sector reports, European Central Bank supervisory disclosures, EU NIS2 transposition documents, and hyperscaler capex filings supplied validation benchmarks. Bottom-up contract value aggregation and top-down regulatory impact modeling enabled triangulation.
Granularity-level framing applied solution-type and deployment-model dimensions at the vendor-contract level, with end-user and industry-vertical segmentation modeled at the organizational-budget-allocation tier. Compound annual growth rate derivation rested on NIS2 compliance deadline pacing and digital banking transformation capex schedules across the projection horizon. Cloud-native security information and event management adoption curves and managed detection and response contract renewal rates served as industry-specific forecast inputs.
Revisions become necessary when NIS2 transposition delays, hyperscale platform service disruptions, or EU Cyber Resilience Act enforcement scope changes materialize across the analysis window. Forecasts reflect assumptions regarding regulatory timeline adherence and certified talent supply elasticity. Periodic stress-testing of base assumptions is recommended.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Benelux Cybersecurity Market
Cybersecurity
DNS Firewall Market
Cybersecurity
Dark Web Intelligence Market
Cybersecurity
Mainframe Security Market
Cybersecurity
Next-Gen Firewall Market
Cybersecurity
Internet of Things (IoT) Security Market
Cybersecurity
Japan Cybersecurity Market
Cybersecurity
Global Breach and Attack Simulation Market
Cybersecurity
Next-Generation Firewall Market
Cybersecurity
Global Deep Packet Inspection (DPI) Market
Cybersecurity
Israel Cybersecurity Market
Cybersecurity
Global Ddos Protection Market
Cybersecurity
Colombia Cybersecurity Market
Cybersecurity
Endpoint Security Market
Cybersecurity
Vietnam Cybersecurity Market
Cybersecurity
Artificial Intelligence in Cybersecurity Market