
 Cloud Network Security Market | 2026-2036
Cloud Network Security Market Size, Share, and Industry Trends Forecast 2026-2036
Cloud Network Security Market Analysis
The gap between on-premises perimeter defense and cloud-native security architecture is narrowing as organizations abandon castle-and-moat models for identity-centric protection. Palo Alto Networks leverages integrated platform consolidation to anchor enterprise-grade secure access service edge deployments across hybrid environments. Fortinet sustains hardware-anchored differentiation through custom ASIC development that competes on throughput economics at scale. Zscaler dominates pure-cloud proxy architectures, occupying the broker position between users and SaaS applications without traditional network touchpoints.
Cloud network security encompasses the policies, controls, and technologies that protect data, applications, and infrastructure within cloud computing environments through encryption, microsegmentation, and continuous traffic inspection across distributed architectures. Its primary purpose is to enforce confidentiality, integrity, and availability guarantees while enabling elastic resource consumption without fixed perimeter dependency. Firewall solutions within the solution-type segment lead current revenue pools due to their position as mandatory compliance controls, though encryption is recording the fastest expansion as quantum-resistant algorithms and confidential computing mature. Hybrid cloud deployment models attract disproportionate investment because large enterprises maintain legacy data center obligations while scaling public cloud workloads, creating persistent demand for unified policy orchestration.
ISO 27017 cloud security standards, NIST SP 800-207 zero-trust architecture guidance, and FedRAMP authorization frameworks collectively elevate baseline product requirements and disqualify vendors lacking third-party attestation. The EU AI Act and GDPR cross-border data transfer rules add jurisdictional complexity that shapes multi-cloud routing decisions and residency-bound service procurement. Stakeholders must monitor how sovereign cloud mandates fragment previously global security stacks into geography-specific compliance layers.
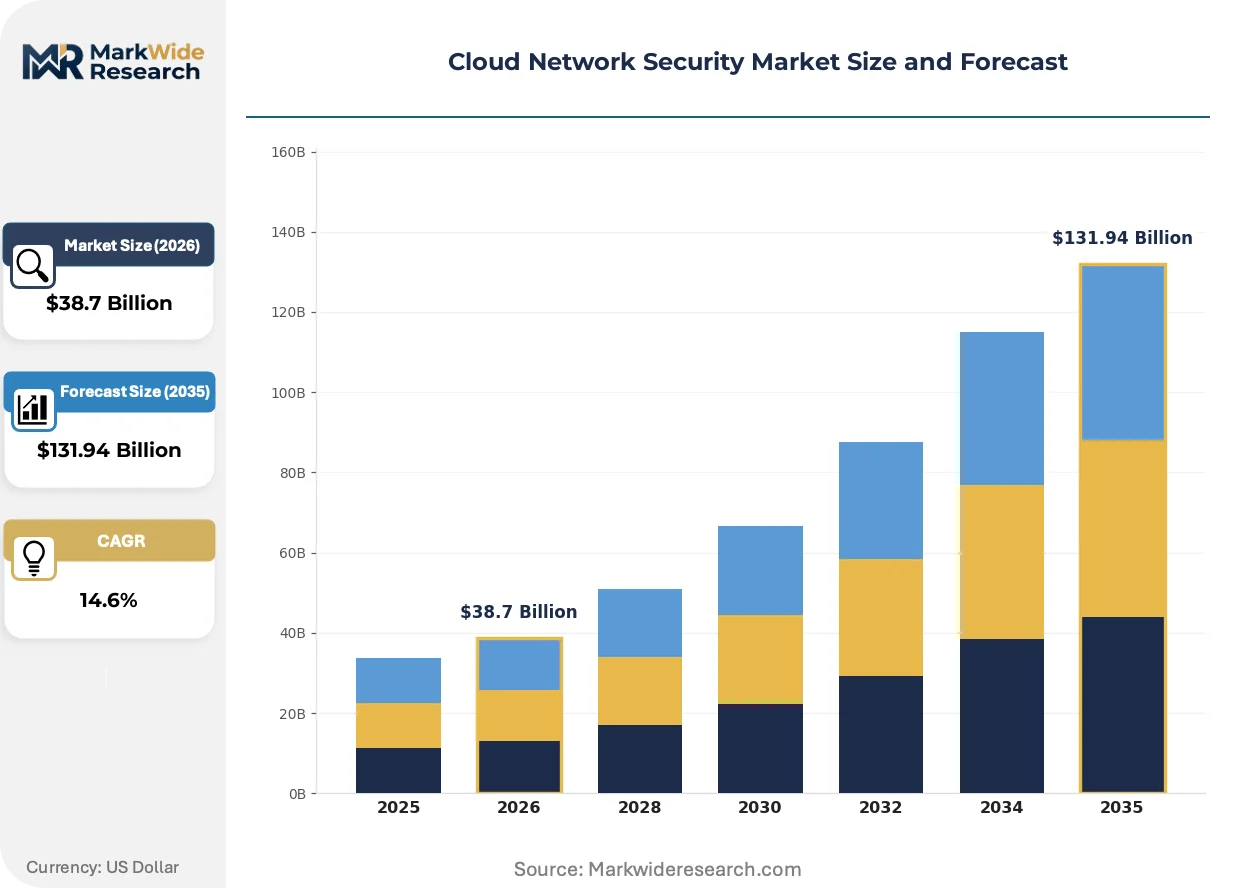
Market Dynamics
Zero-trust architecture mandates from federal agencies are dismantling perimeter-based security procurement, forcing vendors to reengineer product roadmaps around identity verification and continuous authentication rather than network location trust.
Growth Catalysts
- NIST SP 800-207:Federal agencies now require zero-trust compliance for cloud procurement, expanding addressable market for certified vendors serving government contractors and regulated industries.
- Confidential computing hardware:AMD SEV and Intel TDX deployments in financial services are normalizing memory encryption as a baseline requirement for sensitive workload migration.
- Manufacturing OT convergence:Industrial IoT gateways connecting operational technology to cloud analytics platforms create mandatory segmentation demand that legacy firewalls cannot satisfy.
Market Restraints
- Specialized engineering scarcity:Cloud-native security architects command compensation premiums that inflate implementation costs for mid-market enterprises by 40-60% versus traditional network administrators.
- FedRAMP authorization timelines:The 12-18 month certification cycle excludes emerging vendors from federal contracting opportunities regardless of technical capability.
- Homogeneous silicon dependence:Custom ASIC development for high-throughput inspection concentrates in Taiwan semiconductor foundries, exposing supply continuity risk.
Strategic Opportunities
- India data localization:RBI and CERT-In mandates for financial data residency are compelling multinational banks to deploy sovereign cloud security stacks distinct from global architectures.
- Post-quantum cryptography:NIST's standardized algorithms for 2024-2025 deployment create replacement cycle opportunity for encryption vendors with hybrid certificate management capabilities.
- Managed detection and response:Skills-starved mid-market enterprises are outsourcing 24/7 security operations to channel partners rather than building internal SOCs.
Industry Challenges
- Multi-cloud policy orchestration:Enterprises operating across AWS, Azure, and GCP struggle to maintain consistent microsegmentation rules without vendor-specific syntax translation layers.
- Detection engineering talent:The shortage of analysts capable of writing high-fidelity SIEM correlation rules forces vendors to pre-build content packs that commoditize differentiation.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cloud Network Security Market |
| Market Size in 2026 | $38.7 Billion |
| Market Size in 2035 | $131.94 Billion |
| CAGR (2026 – 2036) | 14.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Firewall, Intrusion Detection System, Antivirus, Encryption Deployment Model: Public Cloud, Private Cloud, Hybrid Cloud, Community Cloud End User: Small Enterprises, Large Enterprises, Government Agencies, Non-Profits Service Type: Managed Services, Professional Services, Consulting, Implementation |
| Companies Covered | Palo Alto Networks, Fortinet, Cisco Systems, Check Point Software Technologies, Microsoft Corporation, Netskope, Trend Micro, Zscaler, CrowdStrike, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cloud Network Security Market Emerging Trajectories
Security architecture is fragmenting from monolithic platforms into composable control planes that unify policy across heterogeneous cloud environments without requiring workload displacement.
Secure access service edge technology is hybridizing network security and wide-area networking into single-vendor stacks. Large enterprises with distributed manufacturing facilities are consolidating 10-15 point products into integrated SASE deployments over 18-24 month refresh cycles. This convergence is compressing standalone SD-WAN and firewall markets while elevating vendors with native zero-trust network access capabilities.
EU AI Act risk classification rules are mandating security documentation for high-risk AI systems processing personal data. Cloud providers serving European healthcare and financial institutions must now demonstrate algorithmic transparency and data lineage controls that exceed baseline ISO 27001 requirements. German automotive manufacturers are requiring Tier 1 suppliers to obtain third-party attestation of these controls before cloud-based quality analytics deployment.
Consumption-based licensing is displacing perpetual appliance purchases in enterprise procurement. CISOs at Fortune 500 industrials are negotiating elastic commit contracts that scale inspection capacity with cloud workload growth rather than pre-purchasing fixed throughput. This shift is most pronounced in North American financial services, where quarterly cloud spend variability of 30-40% makes capital-intensive hardware procurement economically irrational.
Cloud Network Security Market Segmentation
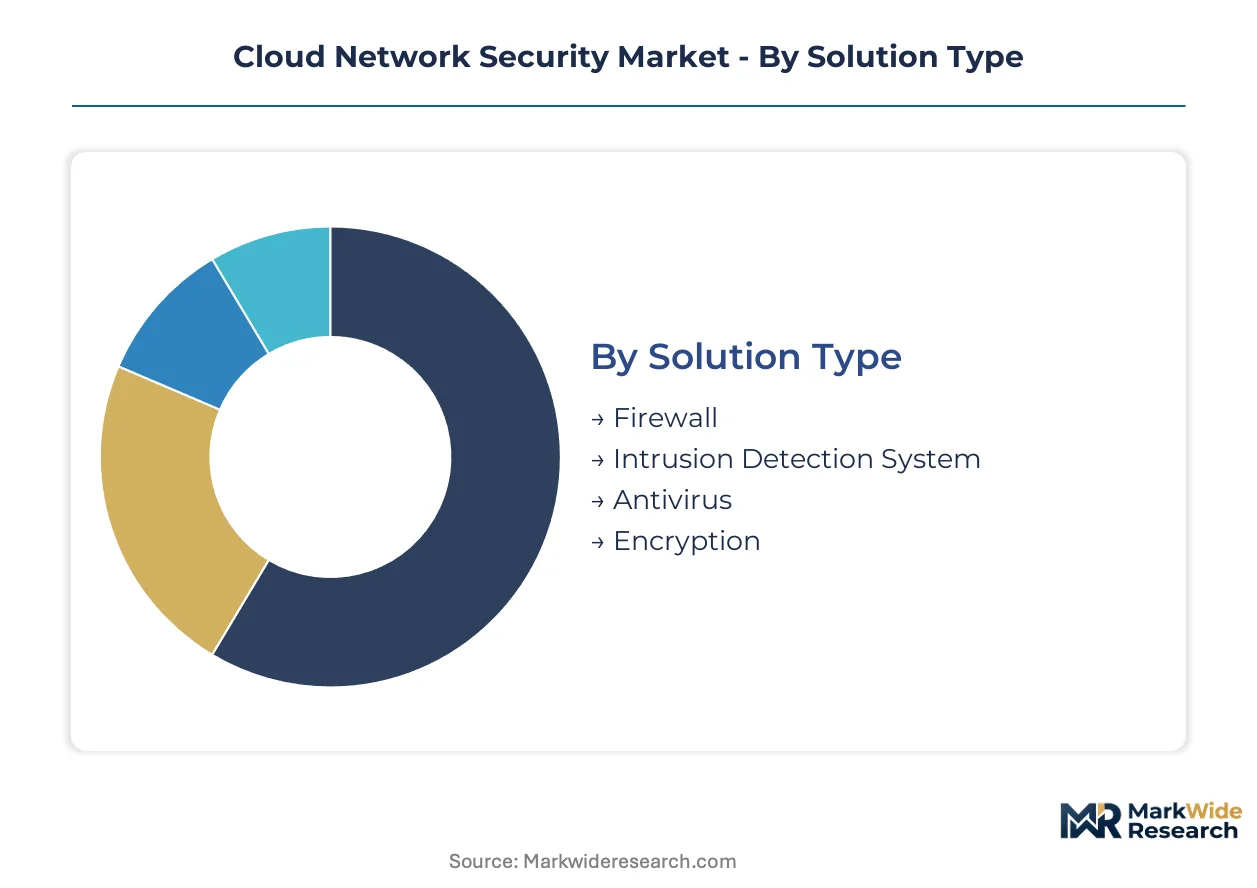
Cloud network security procurement patterns diverge sharply across organizational scale, infrastructure maturity, and compliance exposure. Segment boundaries determine vendor selection criteria, pricing architecture, and channel strategy.
Solution Type:
Security teams deploy distinct control layers based on workload sensitivity, regulatory minimums, and throughput requirements across distributed architectures.
- Firewall:Next-generation firewalls enforce stateful inspection and application-layer filtering at cloud network boundaries. Financial services firms in the United States deploy these as mandatory FedRAMP-authorized controls for federal contractor eligibility.
- Encryption:Data-at-rest and in-transit protection using AES-256 and emerging post-quantum algorithms. Confidential computing hardware from AMD and Intel is accelerating memory encryption adoption for sensitive workload migration in European banking.
- Intrusion Detection System:Signature and behavioral analysis engines monitoring east-west traffic for lateral movement indicators.
- Antivirus:Endpoint protection extended to cloud workloads through agentless scanning integration with hypervisor APIs.
Established volume favors Firewall; emerging adoption favors Encryption.
Deployment Model:
Infrastructure location decisions reflect data sovereignty obligations, legacy system interdependencies, and elasticity requirements.
- Hybrid Cloud:Unified policy orchestration spanning on-premises data centers and public cloud workloads. Large manufacturers in Germany maintain this architecture to connect operational technology gateways with cloud analytics while satisfying EU AI Act documentation requirements.
- Public Cloud:Native security controls and third-party marketplace solutions deployed within AWS, Azure, or GCP environments.
- Private Cloud:Dedicated infrastructure with single-tenant isolation for classified or highly regulated workloads.
- Community Cloud:Shared infrastructure serving specific industry verticals with common compliance profiles.
Procurement concentration tilts toward Hybrid Cloud for enterprise refresh cycles; Public Cloud captures net-new cloud-native deployments.
End User:
Organizational scale dictates security operations maturity, budget allocation flexibility, and tolerance for managed service dependency.
- Large Enterprises:Dedicated CISO organizations with 24/7 security operations centers and custom detection engineering capabilities. These buyers negotiate elastic commit contracts scaling inspection capacity with quarterly cloud spend variability.
- Government Agencies:Zero-trust architecture mandates under NIST SP 800-207 reshape procurement standards. United States federal contractors must demonstrate FedRAMP authorization regardless of technical differentiation.
- Small Enterprises:Skills-constrained organizations outsourcing security operations to managed detection and response providers rather than building internal SOCs.
- Non-Profits:Grant-funded security investments prioritizing compliance attestation for donor and beneficiary data protection.
Large Enterprises dominate current revenue pools; Government Agencies are forcing architectural standardization across supplier ecosystems.
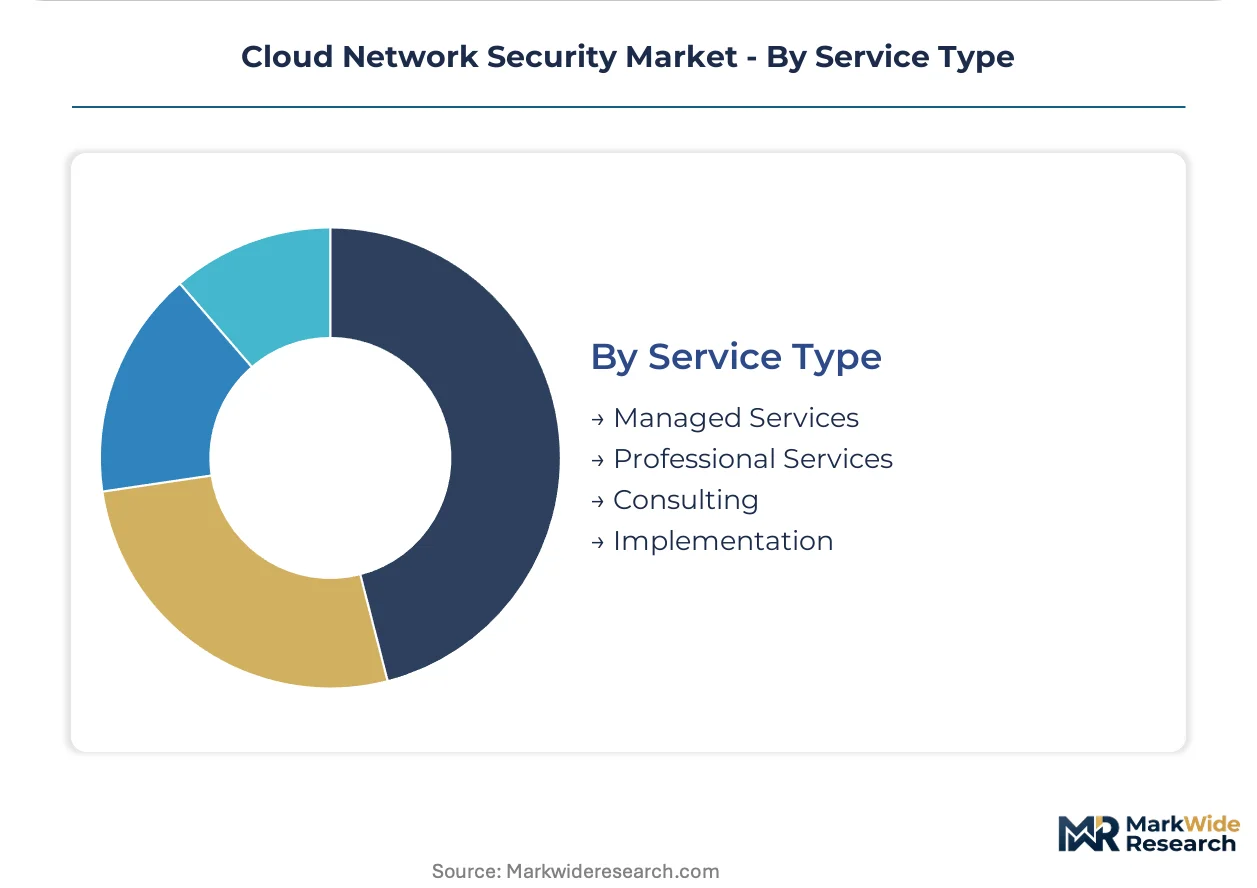
Service Type:
Delivery mechanism selection tracks internal capability gaps, urgency of deployment, and ongoing operational burden tolerance.
- Managed Services:24/7 monitoring, threat hunting, and incident response delivered through channel partners. Mid-market enterprises facing 40-60% implementation cost inflation for cloud-native security architects increasingly outsource security operations.
- Professional Services:Architecture design, migration planning, and integration engineering for complex multi-cloud environments.
- Consulting:Risk assessment, compliance gap analysis, and zero-trust transformation roadmapping.
- Implementation:Deployment engineering, policy configuration, and production cutover support.
Managed Services is expanding most quickly as skills scarcity persists; Professional Services retains premium pricing for transformation complexity.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Israeli cybersecurity firms export zero-trust architectures to United States federal contractors, while German automotive manufacturers demand EU AI Act-compliant cloud security attestation from Asian suppliers before cloud-based quality analytics deployment.
United States
Federal cloud migration mandates and FedRAMP authorization requirements drive procurement concentration among government contractors. NIST SP 800-207 zero-trust architecture guidance reshapes enterprise security roadmaps. The Washington DC-Baltimore corridor hosts defense contractors integrating confidential computing hardware for classified workload migration.
Germany
Automotive and industrial manufacturing sectors require Tier 1 suppliers to obtain third-party security attestation before cloud analytics deployment. EU AI Act risk classification rules mandate algorithmic transparency documentation. Bavaria's automotive cluster demands memory encryption standards for connected vehicle data processing.
India
RBI and CERT-IN data localization mandates compel multinational banks to deploy sovereign cloud security stacks distinct from global architectures. Financial services firms accelerate zero-trust adoption for digital payment infrastructure. Mumbai's banking district drives demand for FedRAMP-equivalent domestic certification frameworks.
Japan
Financial services and automotive sectors adopt confidential computing for sensitive workload protection. METI cybersecurity guidelines emphasize supply chain security for cloud service procurement. Tokyo's financial district implements hardware-anchored encryption for cross-border data transfer compliance.
United Kingdom
Post-Brexit data sovereignty rules reshape multi-cloud routing decisions for financial services. NCSC cloud security principles elevate baseline procurement requirements. London's fintech cluster drives demand for identity-centric protection replacing perimeter-based models.
Cloud Network Security Market Vendor Landscape
On the supply side, the industry is consolidating around integrated platform vendors capable of unifying network security and wide-area networking functions. Pure-cloud specialists compete against hardware-anchored incumbents on throughput economics and deployment flexibility. Three strategic archetypes dominate: integrated SASE platforms, hardware-optimized appliance vendors, and cloud-native proxy architectures. Competitive moves concentrate on strategic partnerships for managed detection and response capabilities and portfolio diversification into confidential computing integration.
Among platform consolidation leaders, Palo Alto Networks exemplifies the integrated SASE archetype through hybrid environment deployments, while Fortinet represents hardware-anchored differentiation through custom silicon development. Zscaler occupies the pure-cloud proxy position between users and SaaS applications without traditional network touchpoints.
| Leading Market Players |
|---|
| Palo Alto Networks |
| Fortinet |
| Cisco Systems |
| Check Point Software Technologies |
| Microsoft Corporation |
| Netskope |
| Trend Micro |
| Zscaler |
| CrowdStrike |
| Others |
Supply Flow & Price Mechanics
Taiwan semiconductor foundry concentration for custom ASIC development compresses margin spreads between hardware-anchored security platforms and software-native alternatives while forcing vendors into dual-sourcing commitments that reshape procurement tiering.
Pricing Analysis
Current-generation hardware-anchored firewalls command substantial premiums over prior-generation virtualized appliances and emerging confidential computing instances. Consumption-based licensing now dominates enterprise procurement, with elastic commit contracts scaling inspection capacity to cloud workload variability rather than fixed throughput purchases. Price differentiation rests on FedRAMP authorization tier and confidential computing hardware integration, with government contractors showing lowest price sensitivity due to compliance mandates while mid-market enterprises face acute cost pressure from cloud-native architect scarcity.
Supply Chain Analysis
Extended payment terms from hyperscaler cloud providers now finance upstream component procurement for security appliance vendors. Custom ASIC fabrication concentrates in Taiwan, South Korea, and the United States, with memory encryption hardware sourcing from AMD and Intel foundry networks. Supply chain risk centers on single-source vulnerability for advanced node semiconductor production. Distribution runs through channel partners delivering managed detection and response services to skills-constrained mid-market buyers.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Cloud network security procurement increasingly filters through organizations lacking internal zero-trust architecture expertise, elevating vendor certification portfolios and managed service capabilities above pure technical differentiation.
For Market Incumbents: Entrench platform consolidation advantages by deepening confidential computing hardware partnerships and securing FedRAMP High authorization ahead of federal contractor procurement waves. Prioritize channel control through managed detection and response provider certification programs to capture mid-market outsourcing demand. Counter emerging pure-cloud proxy architectures with hybrid deployment flexibility that accommodates legacy data center obligations. For New Entrants and Emerging Players: Build out sovereign cloud security stacks for India and EU data localization mandates where global incumbents face architectural retrofit costs. Target financial services mid-market segments in Mumbai and Frankfurt where compliance complexity exceeds internal security operations capacity. Lead with post-quantum cryptography hybrid certificate management as a differentiated entry wedge against established encryption vendors. For Investors and Strategic Acquirers: NIST's post-quantum cryptography standardization timeline reshapes the acquisition landscape toward encryption vendors with algorithmic transition capabilities. Position for five-to-ten year viability by targeting managed detection and response channel partners with established mid-market customer density rather than pure technology plays. Monitor FedRAMP authorization backlog clearance rates as the signal indicating federal market access velocity.| Strategic Initiative | Industry Significance |
|---|---|
| Confidential Computing Integration | AMD SEV and Intel TDX partnerships enable memory encryption for financial services workload migration. |
| FedRAMP Authorization Investment | Twelve-to-eighteen month certification cycles create defensive moats around federal contractor procurement pools. |
| Managed Detection and Response Partnership | Channel alliances capture mid-market outsourcing demand from skills-starred enterprise security teams. |
| Post-Quantum Cryptography Development | NIST algorithm standardization drives replacement cycles for certificate management infrastructure. |
| Sovereign Cloud Stack Localization | India RBI and EU GDPR mandates compel architectural divergence from global security platforms. |
Methodological Framework
Operator-level perspectives from CISOs, cloud infrastructure architects, federal procurement officers, and managed security service providers anchored the qualitative base. Primary interview findings triangulated against secondary sources including FedRAMP authorization databases, NIST cybersecurity framework documentation, hyperscaler capex disclosures, and customs records for security appliance trade flows. Bottom-up segment sizing across solution types, deployment models, and end-user categories validated against top-down macroeconomic anchoring.
Scenario-bracketing framed demand projections across the analysis window, with segmentation dimensions spanning solution type, deployment model, organization scale, and regional regulatory cluster. CAGRs derived from elasticity modeling of cloud workload growth against security control penetration rates. Forecast inputs incorporated federal zero-trust mandate implementation velocity and confidential computing hardware shipment trajectories.
The forecast holds incumbent behavior within observed patterns; aggressive platform consolidation moves by hardware-anchored vendors or pure-cloud specialists would shift outcomes. Macroeconomic contraction in cloud services spending, acceleration of sovereign cloud fragmentation, or breakthrough quantum computing advances would prompt forecast revision.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
India Network Security and Cyber Risk Management Market
Cybersecurity
Bahrain Cybersecurity Market
Cybersecurity
Spain Cybersecurity Market
Cybersecurity
Asia Pacific Data Exfiltration Market
Cybersecurity
Network Sandboxing Market
Cybersecurity
Global Digital Forensic Laboratory As a Service Market
Cybersecurity
Global Mobile Anti Malware Market
Cybersecurity
Global Information Security Consulting Market
Cybersecurity
Penetration Testing Market
Cybersecurity
Indonesia Cybersecurity Market
Cybersecurity
Network Edge Security Solutions Market
Cybersecurity
M2M Network Security Market
Cybersecurity
Cloud Workload Protection Market
Cybersecurity
Dark Web Intelligence Market
Cybersecurity
Australia Cybersecurity Market
Cybersecurity
North America Extended Detection and Response Market