
 North America Extended Detection and Response Market | 2026-2036
North America Extended Detection and Response Market Size, Share, and Industry Trends Forecast 2026-2036
North America Extended Detection and Response Market Insights
Security operations analyst talent is rotating toward cloud-native platforms, creating workforce gaps that vendors must address through automation. Palo Alto Networks leverages integrated platform consolidation to reduce alert fatigue for understaffed SOCs. Microsoft Corporation anchors enterprise uptake through native embedding within productivity suites. CrowdStrike Holdings differentiates via lightweight agent architecture that minimizes endpoint performance drag.
Extended Detection and Response unifies telemetry from endpoints, networks, cloud workloads, and identity systems into a correlated analytics layer for threat detection and automated response. The architecture ingests structured and unstructured security data through APIs, applies behavioral analytics to identify multi-stage attacks, and triggers orchestrated containment actions across the technology stack. Cloud deployment configurations are capturing the fastest expansion as organizations retire on-premises SIEM infrastructure. Endpoint Security solutions within the solution segment command the deepest margin pools due to persistent licensing attach rates. BFSI end users generate the most complex integration requirements, driving premium service tiers.
CISA directives, NIST SP 800-53 revisions, and SEC cybersecurity disclosure rules are collectively mandating faster mean-time-to-detect metrics and documented response playbooks across US critical infrastructure operators. Health Canada and the Canadian Centre for Cyber Security are aligning federal procurement standards with similar telemetry and reporting requirements. Stakeholders must evaluate vendor AI/ML transparency against emerging algorithmic accountability expectations before committing to multi-year platform contracts.
Market Dynamics
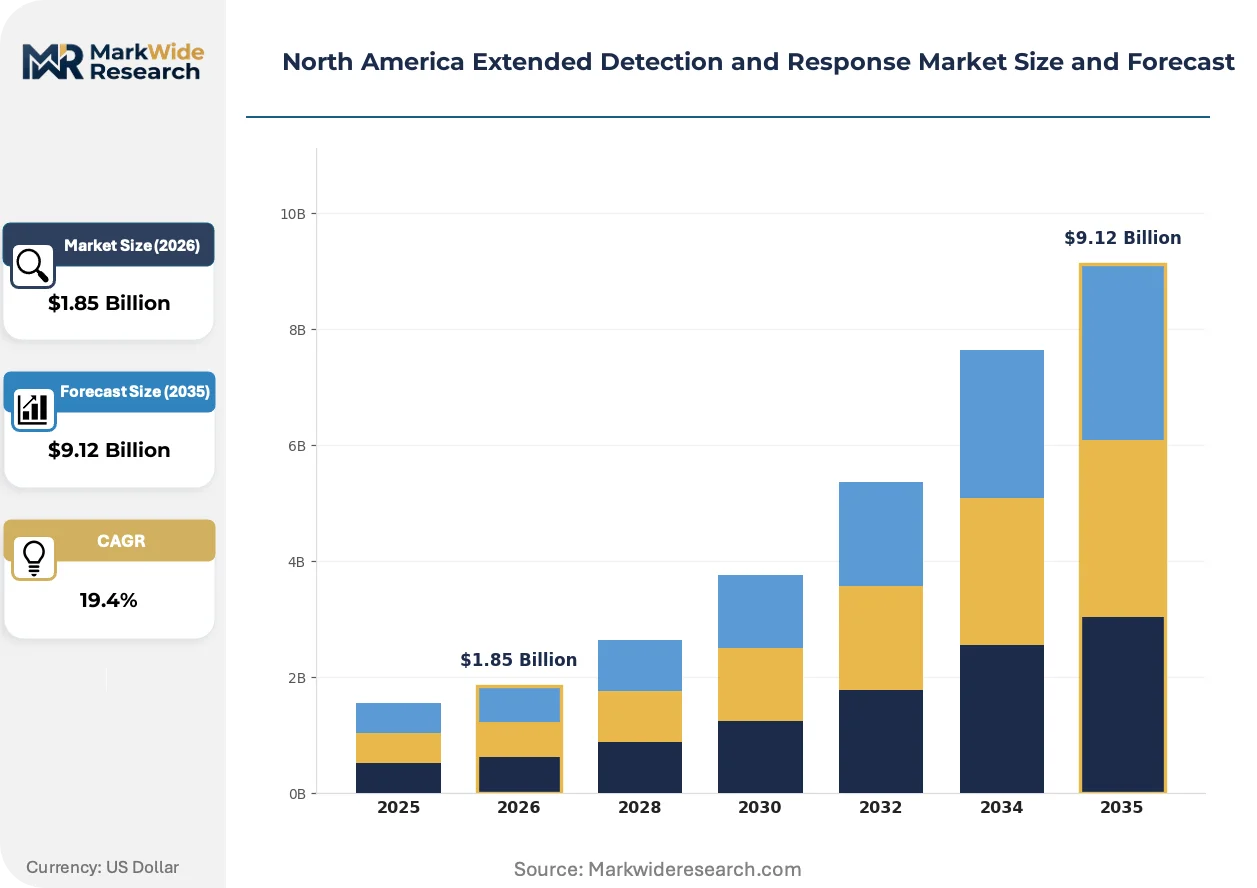
The North America Extended Detection and Response market is being reshaped by the forced retirement of on-premises SIEM infrastructure as CISA mandates and SEC disclosure rules accelerate cloud-native telemetry requirements across critical infrastructure operators.
Growth Catalysts
- SEC Cybersecurity Disclosure Rules:Publicly traded companies in the United States must now report material cybersecurity incidents within four business days, forcing investment in automated detection and response platforms that generate auditable telemetry.
- Healthcare digitization:Hospital systems and regional health networks are consolidating patient data onto cloud platforms, creating attack surfaces that XDR architectures unify across endpoints, identity systems, and medical IoT devices.
- Cloud workload expansion:Financial services firms migrating core banking systems to hybrid cloud configurations require correlated analytics across multi-cloud environments that legacy point solutions cannot provide.
Market Restraints
- Specialized analyst scarcity:The shortage of security operations analysts capable of interpreting AI-generated threat correlations limits deployment velocity for mid-market enterprises without managed security service provider support.
- Integration tax:Legacy endpoint detection and response investments in large enterprises create sunk-cost friction that delays full-platform XDR consolidation cycles.
- Data residency requirements:Canadian provincial privacy statutes and US state-level data localization mandates fragment cloud deployment architectures, complicating vendor platform standardization.
Strategic Opportunities
- Municipal and county government tier:Underpenetrated state and local government entities in the US Midwest and Canadian Prairie provinces represent greenfield deployment opportunities as federal cybersecurity grant programs expand.
- Operational technology convergence:XDR platforms that ingest industrial control system telemetry alongside IT security data capture premium pricing from energy and manufacturing verticals securing converged infrastructure.
- Health Canada alignment:Federal procurement standardization with NIST SP 800-53 creates vendor certification pathways that streamline multi-year hospital system contracts.
Industry Challenges
- Alert tuning complexity:Security operations centers struggle to calibrate machine-learning detection thresholds without generating false-positive volumes that erode analyst trust and response velocity.
- API standardization gaps:Inconsistent telemetry formats across network equipment vendors and cloud service providers force custom integration development that extends deployment timelines.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | North America Extended Detection and Response Market |
| Market Size in 2026 | $1.85 Billion |
| Market Size in 2035 | $9.12 Billion |
| CAGR (2026 – 2036) | 19.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-premises, Cloud, Hybrid, Managed Services Solution: Threat Intelligence, SIEM, Endpoint Security, Network Security End User: Healthcare, Retail, Manufacturing, BFSI Technology: Artificial Intelligence, Machine Learning, Automation, Analytics |
| Companies Covered | Palo Alto Networks, Microsoft Corporation, CrowdStrike Holdings, Cisco Systems, Trend Micro, SentinelOne, Broadcom, Sophos, Cybereason, Others |
| Regions Covered | North America: US, Canada, Mexico |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
North America Extended Detection and Response Market Trends and Innovations
Agentless telemetry collection and autonomous response orchestration are compressing the traditional managed detection and response service model, while regulatory pressure forces faster mean-time-to-detect metrics across regulated verticals.
Extended detection and response architecture is fragmenting the standalone endpoint security market by absorbing network detection, identity threat detection, and cloud workload protection into unified data lakes. Mid-market enterprises in the US Southeast are adopting these consolidated platforms fastest, displacing multi-vendor security stacks that require separate management consoles and correlation engines.
CISA's Secure by Design pledge and binding operational directives are mandating memory-safe programming practices and software bill of materials disclosure from vendors serving federal agencies. This regulatory pressure is filtering into commercial procurement requirements, with healthcare and financial services buyers now demanding vendor attestation of supply chain security practices before contract execution.
Subscription fatigue among security buyers is compressing vendor consolidation cycles, with procurement teams favoring platforms that consolidate multiple security functions under single licensing structures. Managed security service providers are responding by unbundling traditional co-managed detection and response offerings into modular tiers, with the most visible shift occurring among US regional banks seeking to reduce operational expenditure volatility.
North America Extended Detection and Response Market Segmentation
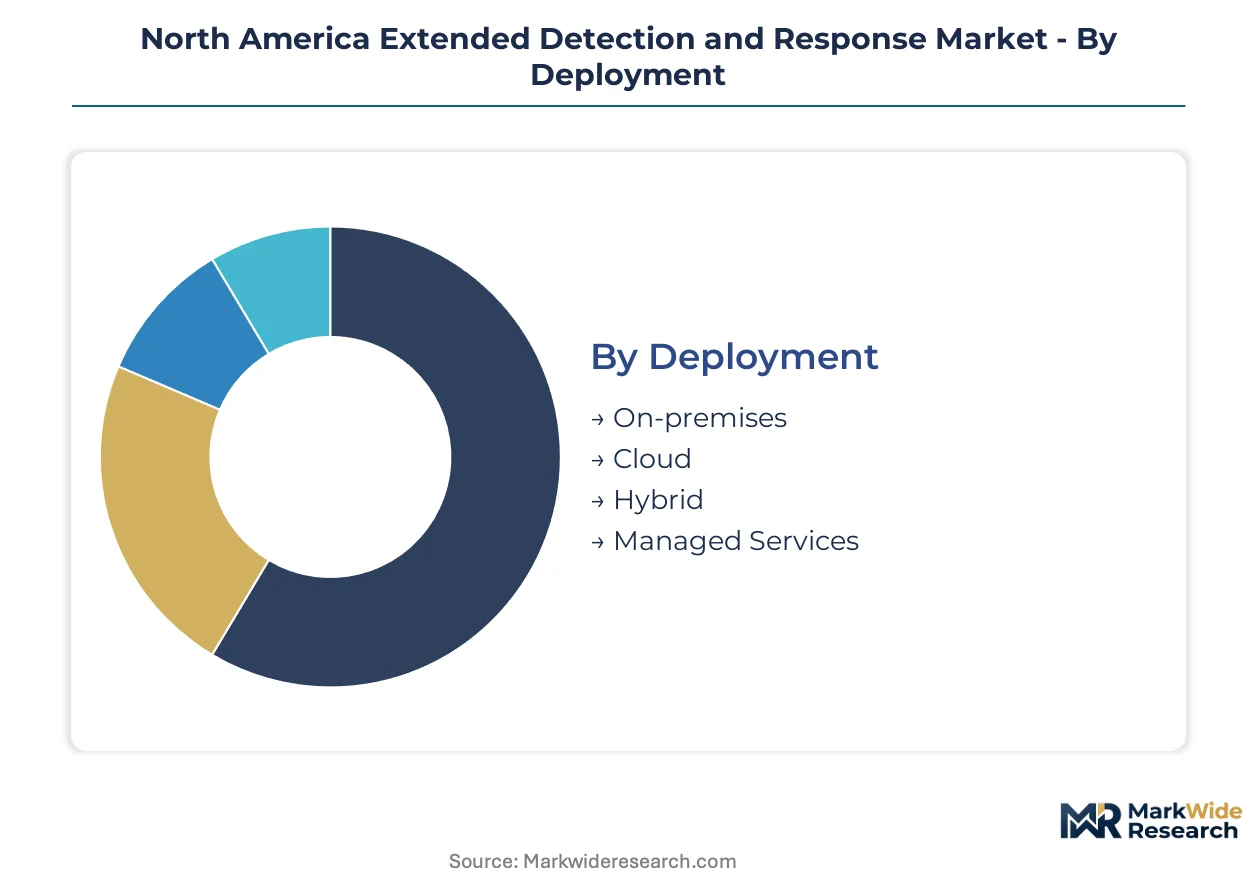
XDR deployment patterns reflect divergent regulatory timelines across US and Canadian jurisdictions. Cloud configurations accelerate where SEC disclosure mandates and CISA directives compress detection-to-reporting windows. Procurement teams segment investments by telemetry source density and cross-border data residency requirements.
Deployment:
Regulatory differentiation separates cloud-native mandates from legacy infrastructure grandfathering provisions.
- Cloud:Native SaaS architectures ingest endpoint, network, and identity telemetry through unified APIs without customer-managed infrastructure. US financial services corridors in New York and Chicago prioritize cloud deployments to satisfy four-day SEC incident disclosure windows.
- Hybrid:Split configurations retain sensitive workload processing on-premises while pushing analytics to cloud data lakes. Canadian provincial privacy statutes and US state data localization laws force hybrid architectures for healthcare systems spanning Ontario and Michigan.
- Managed Services:Third-party SOC operators assume detection engineering and response orchestration through multi-tenant platforms. Mid-market enterprises in the US Southeast and Canadian Prairie provinces adopt managed services to address analyst talent scarcity.
- On-premises:Customer-operated infrastructure persists in classified federal environments and isolated industrial control networks. Energy sector operators in Alberta and Texas maintain on-premises stacks for air-gapped operational technology segments.
Established volume favors On-premises; emerging adoption favors Cloud.
Solution:
Margin concentration tracks licensing attach rates and integration complexity across the technology stack.
- Endpoint Security:Lightweight agents deploy across workstations, servers, and mobile devices to capture process telemetry and behavioral indicators. Persistent licensing models generate recurring revenue depth; US healthcare networks anchor demand as medical device proliferation expands attack surfaces.
- SIEM:Security information and event management platforms aggregate structured logs from firewalls, identity systems, and cloud workloads. BFSI end users in Charlotte and Toronto drive premium tier uptake through complex multi-source correlation requirements.
- Threat Intelligence:External data feeds enrich internal telemetry with indicators of compromise and adversary attribution. Retail sector demand concentrates in Chicago and Montreal as payment card industry audits mandate threat landscape monitoring.
- Network Security:Deep packet inspection and flow analytics detect lateral movement across segmented infrastructure. Manufacturing verticals in Ohio and Quebec adopt network-centric XDR modules to secure converged IT-OT environments.
Recurring revenue depth concentrates in Endpoint Security; integration complexity premiums concentrate in SIEM.
End User:
Application-specific telemetry requirements shape vendor platform configuration and service tier design.
- BFSI:Banking, financial services, and insurance operators demand sub-minute detection thresholds for wire fraud and account takeover scenarios. The US Northeast corridor generates the most complex multi-cloud integration requirements.
- Healthcare:Hospital systems and regional health networks require HIPAA-aligned audit trails across electronic health record systems and connected medical devices. Health Canada procurement standardization accelerates platform certification cycles.
- Manufacturing:Discrete and process manufacturers secure converged IT-OT infrastructure where industrial control systems interface with enterprise networks. Ontario and Michigan manufacturing belts drive operational technology telemetry demand.
- Retail:Point-of-sale networks and e-commerce platforms require seasonal elasticity in detection capacity. US Southeast retail hubs prioritize managed service tiers to handle holiday transaction volume spikes.
Contract value concentration favors BFSI; federal certification velocity favors Healthcare.
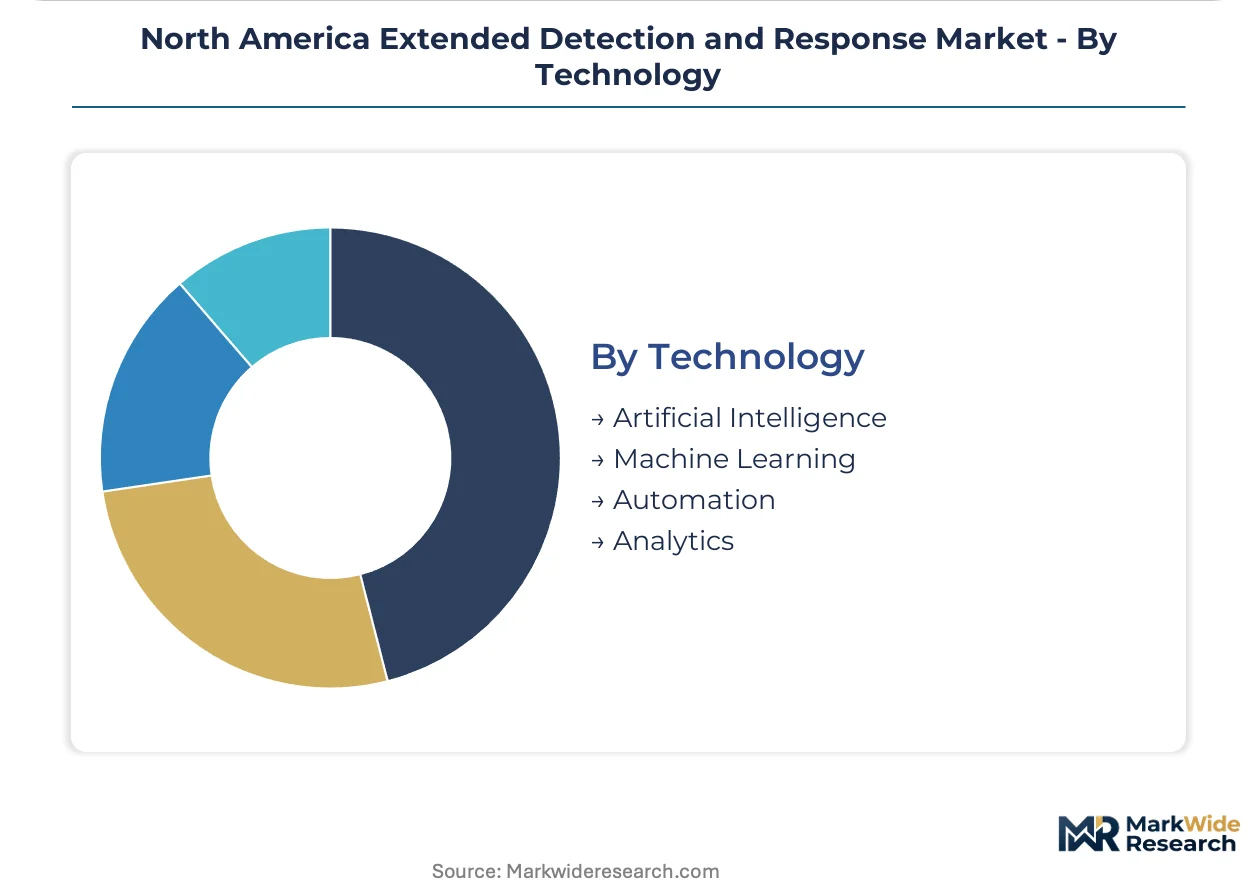
Technology:
Maturity gradients separate production-grade automation from experimental algorithmic layers.
- Automation:Orchestrated response playbooks execute containment actions across endpoints, firewalls, and identity systems without human intervention. CISA binding operational directives mandate documented automation for critical infrastructure operators.
- Artificial Intelligence:Deep learning models identify novel attack patterns through unsupervised training on historical incident data. SEC disclosure rule pressure accelerates AI investment for material incident classification.
- Machine Learning:Supervised classifiers score user and entity behavioral anomalies against baseline profiles. Alert tuning complexity limits deployment velocity in mid-market enterprises without dedicated data science resources.
- Analytics:Correlation engines and visualization layers translate raw telemetry into investigator-actionable narratives. Municipal government tier adoption in the US Midwest depends on simplified analytics interfaces for generalist IT staff.
Operational reliability favors Automation; capability differentiation favors Artificial Intelligence.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
United States organizations consume XDR primarily through cloud-native deployments to satisfy compressed SEC disclosure windows, while Canadian operators favor hybrid architectures shaped by provincial data residency statutes.
United States
Financial services corridors in New York, Chicago, and Charlotte drive cloud-first procurement as SEC four-day incident disclosure rules eliminate on-premises telemetry latency. CISA binding operational directives mandate documented automation playbooks for critical infrastructure operators. Healthcare networks across the Midwest and Southeast are consolidating endpoint agents to secure proliferating medical IoT devices.
Canada
Provincial privacy statutes in Ontario and Quebec fragment deployment architectures, forcing split configurations that retain sensitive health data on-premises while pushing analytics to cloud data lakes. Health Canada procurement standardization with NIST SP 800-53 accelerates vendor certification cycles for hospital systems. Energy operators in Alberta maintain air-gapped on-premises stacks for operational technology segments.
Mexico
Manufacturing clusters in Nuevo León and the Bajío Region generate demand for converged IT-OT XDR platforms as automotive and electronics producers digitize production lines. The national data protection authority imposes localization requirements on cross-border telemetry flows. Mexico City financial institutions are adopting managed security service tiers to address analyst talent scarcity without building captive SOCs.
North America Extended Detection and Response Market Competitive Landscape
A small set of integrated leaders sits above a broader specialist tier, with platform consolidation and managed service unbundling defining current competitive dynamics. The vendor landscape separates into three archetypes: native cloud platforms with embedded productivity suite distribution, lightweight endpoint specialists minimizing performance drag, and network-centric incumbents leveraging existing infrastructure relationships. Dominant competitive moves include strategic partnerships to fill telemetry gaps and portfolio diversification into adjacent identity threat detection modules.
Within the integrated platform tier, Palo Alto Networks and Microsoft Corporation exemplify divergent distribution strategies—one through security-focused platform consolidation, the other through native embedding within productivity suites. CrowdStrike Holdings occupies a position among endpoint-centric specialists, representing the lightweight agent architecture approach that minimizes resource consumption on deployed endpoints.
| Leading Market Players |
|---|
| Palo Alto Networks |
| Microsoft Corporation |
| CrowdStrike Holdings |
| Cisco Systems |
| Trend Micro |
| SentinelOne |
| Broadcom |
| Sophos |
| Cybereason |
| Others |
Pricing and Supply Chain Analysis
Cloud-native API architectures displacing legacy on-premises SIEM infrastructure simultaneously concentrate vendor development resources in US West Coast technology corridors and compress pricing premiums for traditional managed security service tiers. This substitution dynamic reshapes procurement economics as buyers trade capital expenditure for operational expenditure models.
Pricing Analysis
Multi-year subscription contracts dominate enterprise procurement, with three-tier pricing structure across premium, standard, and economy levels differentiating by telemetry source density and automation sophistication. Price differentiation tracks SOC staffing support tiers and cross-border data residency compliance modules. Pricing pressure stems from mid-market buyers consolidating multi-vendor stacks into single-platform licenses. Municipal government segments exhibit highest price sensitivity; BFSI operators in New York and Charlotte demonstrate lowest sensitivity due to regulatory penalty exposure.
Supply Chain Analysis
Specialized GPU clusters for AI model training in Taiwan and South Korea create chokepoint vulnerability for vendors developing autonomous threat detection capabilities. Cloud hyperscaler infrastructure draws from US, Ireland, and Singapore data center networks. Supply chain risk centers on single-source dependency for advanced behavioral analytics silicon. Distribution runs through direct enterprise sales teams and managed security service provider channel partnerships.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Incumbent XDR platforms face substitution pressure from native security modules embedded within productivity suites, requiring defensive repositioning around telemetry breadth and response automation depth.
For Market Incumbents: Consolidate platform capabilities through strategic acquisition of identity threat detection specialists and network detection vendors to close telemetry gaps. Deepen automation playbook libraries for CISA-mandated critical infrastructure operators. Prioritize Health Canada certification pathways to secure multi-year hospital system contracts against cloud-native competitors. For New Entrants and Emerging Players: Mid-market managed services whitespace in Canadian Prairie provinces and US Midwest municipal governments offers penetrable entry points where analyst talent scarcity prevents self-managed deployments. Target manufacturing verticals in Ohio and Quebec with converged IT-OT telemetry modules. Pursue co-development partnerships with regional managed security service providers to bypass direct enterprise sales infrastructure requirements. For Investors and Strategic Acquirers: The market sits at a platform consolidation phase that favors vendors with proven multi-tenant cloud architectures and federal certification velocity. Long-term viability over the coming decade rests on AI transparency compliance and supply chain security attestation capabilities. Monitor SEC enforcement patterns around four-day incident disclosure compliance as inflection indicator for automation premium pricing power.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies endpoint, network, and identity telemetry into correlated data lakes for SOCs. |
| Acquisition of Specialist Firm | Fills telemetry gaps in operational technology and medical IoT security domains. |
| Strategic Partnership | Aligns with managed security service providers to reach analyst-constrained mid-market buyers. |
| Product Launch | Introduces agentless telemetry collection to reduce deployment friction in healthcare networks. |
| Geographic Expansion | Establishes Canadian data residency zones to satisfy Ontario and Quebec provincial privacy statutes. |
Research Methodology
The analysis maps cloud-native SaaS platforms, hybrid deployment configurations, managed security services, and on-premises infrastructure segments, each validated through primary interviews with CISOs, SOC directors, healthcare IT security leads, and federal procurement officers. Secondary sources include CISA binding operational directives, SEC cybersecurity disclosure filings, Health Canada procurement standards, and vendor SEC 10-K security revenue disclosures. Bottom-up deployment volume estimates triangulate against top-down addressable market calculations.
Consistency checks validated volume and value outputs against hyperscaler security revenue disclosures and managed security service provider contract announcement patterns. The analytical framework models deployment mode, organization size tier, vertical regulatory intensity, and cross-border data residency requirements across the projection horizon. CAGRs derive from segment-specific adoption curves calibrated to regulatory mandate timelines. Forecast inputs include SOC analyst hiring data from US Bureau of Labor Statistics and Canadian cybersecurity workforce surveys.
Forecasts assume regulatory continuity in SEC disclosure regimes and CISA directive enforcement; material policy shifts would require re-modeling adoption velocity assumptions. Practitioners should keep alternative scenarios live as Health Canada procurement standardization and provincial data localization statute evolution reshape vendor certification requirements.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Colombia Cybersecurity Market
Cybersecurity
Global Network Security Policy Management Market
Cybersecurity
Cyber Security and Big Data Analytics Market
Cybersecurity
Denmark Cybersecurity Market
Cybersecurity
Global Internet Security Market
Cybersecurity
Global Digital Forensic Laboratory As a Service Market
Cybersecurity
Data Diode Solution Market
Cybersecurity
Secure Socket Layer (SSL) Certification Market
Cybersecurity
India Ransomware Protection Market
Cybersecurity
Virtualization Security Tools Market
Cybersecurity
Next-Generation Firewall Market
Cybersecurity
Global Ddos Protection Market
Cybersecurity
Cloud Application Security Market
Cybersecurity
Open RAN Security Market
Cybersecurity
Europe Cloud DLP Market
Cybersecurity
Post-Quantum Cryptography Market