
 Germany Cybersecurity Market | 2026-2036
Germany Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Germany Cybersecurity Market Foresight
German cybersecurity talent pipelines is restructuring as domestic universities expand specialized degree programs and federal vocational retraining initiatives accelerate. T-Systems leverages its sovereign cloud infrastructure to anchor public-sector contracts across federal and state administrations. Secunet Security Networks specializes in high-assurance encryption products for classified government networks. Rohde & Schwarz Cybersecurity dominates electromagnetic spectrum security and hardware-based trust modules for defense applications.
Cybersecurity encompasses the technologies, processes, and practices designed to protect networks, devices, programs, and data from attack, damage, or unauthorized access, with encryption standards such as AES-256 and TLS 1.3 forming core technical safeguards. Its primary purpose is ensuring confidentiality, integrity, and availability of digital assets across enterprise and governmental operations. Cloud-based deployment models capture accelerating enterprise migration momentum as German mid-caps abandon legacy on-premises maintenance burdens. Endpoint security solutions sustain premium pricing power due to persistent remote-work attack surface expansion. Managed services segments attract mid-market buyers seeking outsourced Security Operations Center capabilities without captive specialist hiring.
The Federal Office for Information Security (BSI) mandates baseline protection standards for critical infrastructure under the IT Security Act, while EU NIS2 transposition tightens supply-chain security obligations across member states. Germany's implementation of the EU Cyber Resilience Act imposes conformity requirements on hardware and software products with digital elements. Stakeholders must monitor BSI certification evolution and NIS2 enforcement timelines to align product roadmaps with compliance-driven procurement criteria.
Market Dynamics
Zero-trust architecture mandates from the EU NIS2 Directive are compressing procurement cycles across German critical infrastructure, forcing operators to restructure vendor relationships around continuous verification rather than perimeter defense.
Growth Catalysts
- Connected vehicle security mandates:German automotive OEMs must harden supply chains against over-the-air intrusion, expanding encryption procurement across Tier-1 and Tier-2 networks.
- BSI baseline protection standards:The Federal Office for Information Security mandates systematic risk management for energy, transport, and healthcare operators, creating recurring compliance expenditure.
- Munich-Stuttgart corridor concentration:Defense-tech clusters and enterprise headquarters in Bavaria generate dense demand for high-assurance security services and sovereign cloud infrastructure.
Market Restraints
- Specialized talent scarcity:Zero-trust architecture implementation requires certified security architects, whose supply trails demand across German federal states by substantial margins.
- Hardware trust module costs:Electromagnetic spectrum security and hardware-based encryption modules carry premium input costs that mid-market buyers struggle to absorb.
- NIS2 transposition friction:Supply-chain security obligations create vendor audit burdens that slow procurement velocity for complex multi-tier contracts.
Strategic Opportunities
- EU Cyber Resilience Act conformity:Hardware and software products with digital elements face new certification requirements, opening assessment and advisory service revenue streams.
- Managed SOC outsourcing:Mid-market enterprises seek external Security Operations Center capabilities without captive specialist hiring, favoring subscription-based delivery models.
- Quantum-resistant cryptography migration:Federal agencies are piloting post-quantum encryption standards, creating early-mover positioning for domestic certification authorities.
Industry Challenges
- Legacy system integration complexity:Industrial control systems in manufacturing and energy sectors resist seamless zero-trust overlay without operational disruption.
- BSI certification timeline compression:Product roadmaps must align with evolving federal certification criteria that lack predictable release schedules.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Germany Cybersecurity Market |
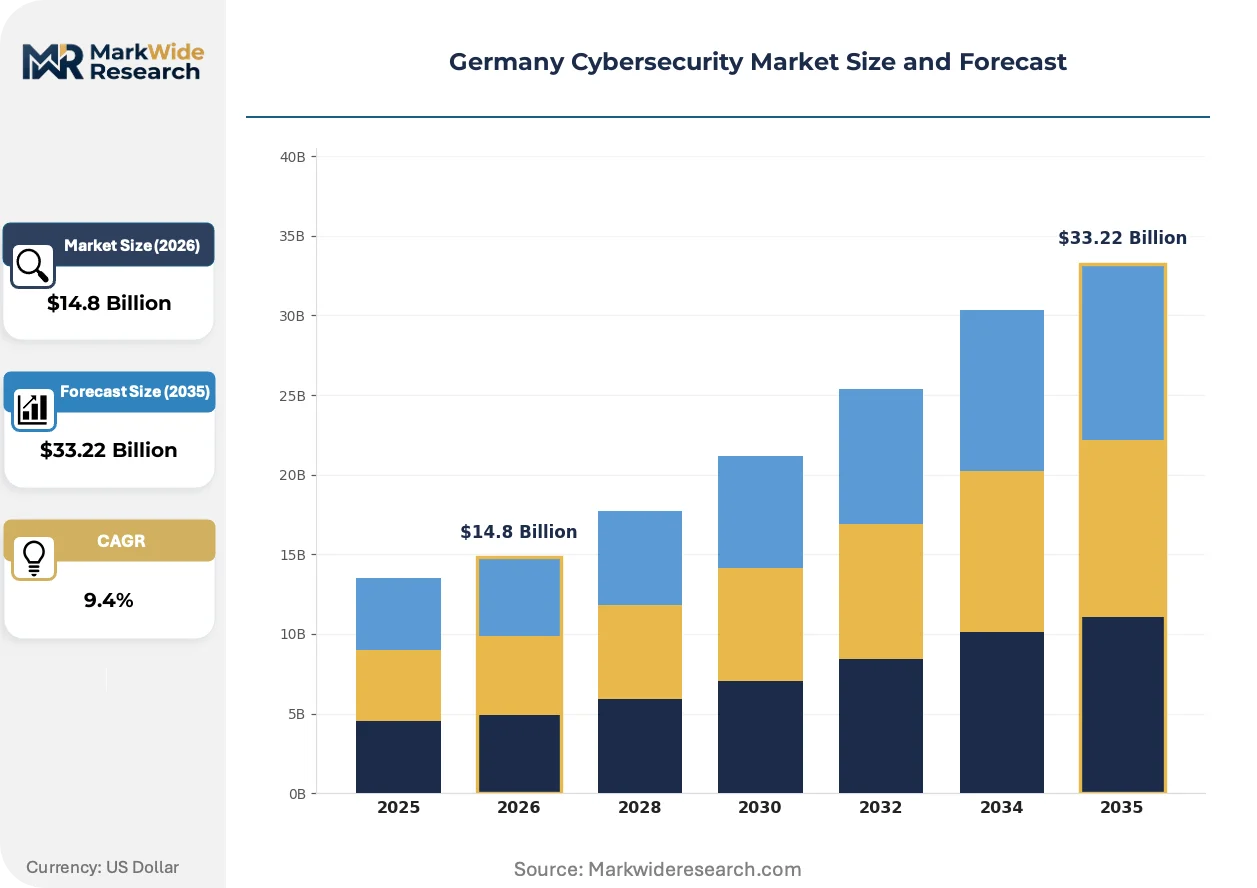
| Market Size in 2026 | $14.8 Billion |
| Market Size in 2035 | $33.22 Billion |
| CAGR (2026 – 2036) | 9.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Firewall, Antivirus Software, Intrusion Detection System, Encryption Tools Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Services End User: Government, Financial Services, Healthcare, Manufacturing Application Area: Network Security, Endpoint Security, Application Security, Cloud Security |
| Companies Covered | T-Systems, Infodas, Factosecure, IBM Security Germany, Atos Germany Cybersecurity, Secunet Security Networks, G DATA CyberDefense, Cisco Security Germany, Rohde & Schwarz Cybersecurity, Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Germany Cybersecurity Market Shifts & Advancements
Secure access service edge frameworks are restructuring how German enterprises deploy network security, collapsing distinct point solutions into unified cloud-native architectures. This convergence is compressing vendor consolidation cycles and redrawing competitive boundaries.
Confidential computing technology is decentralizing data protection by processing sensitive workloads in hardware-isolated enclaves. Automotive manufacturers in Stuttgart are adopting these trusted execution environments for connected vehicle telemetry. The approach is decentralizing security architecture away from centralized data centers toward distributed edge processing nodes.
The EU Cyber Resilience Act imposes conformity assessment requirements on all hardware and software products with digital elements sold in member states. German industrial automation vendors must redesign development pipelines to embed security-by-design documentation. Machinery and component manufacturers face the steepest compliance adaptation curves.
Mid-cap enterprises are abandoning perpetual license models for consumption-based security service contracts. Value-added resellers and systems integrators in North Rhine-Westphalia are capturing recurring revenue through bundled threat detection and response offerings. The Mittelstand manufacturing segment exhibits the fastest behavioral transition toward outsourced security operations.
Germany Cybersecurity Market Segmentation
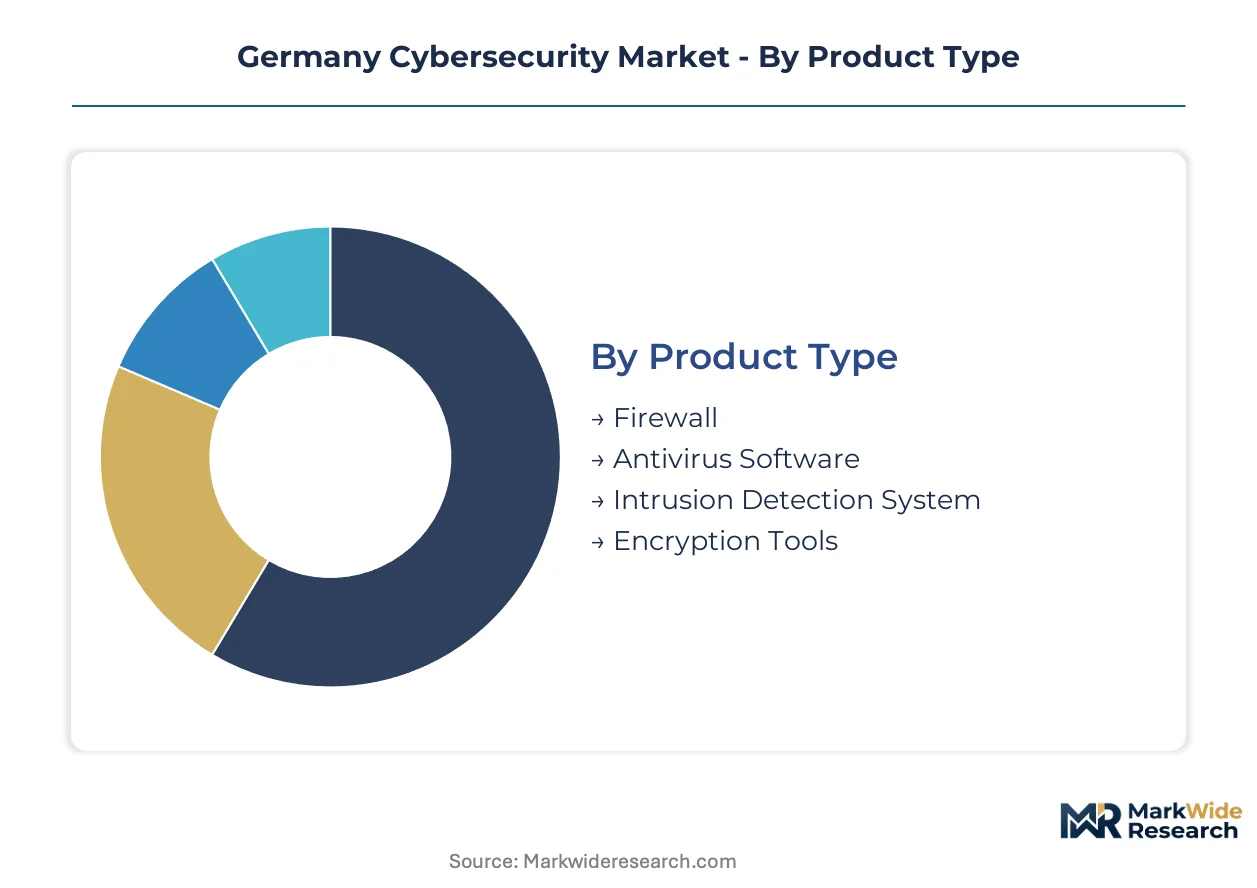
German cybersecurity procurement patterns diverge sharply across product architectures and operational contexts. The NIS2 Directive's risk-tiering requirements are forcing buyers to match specific technical controls to criticality classifications rather than adopting uniform protection stacks.
Product Type:
Standardized perimeter tools dominate volume procurement, while encryption modules command premium customization cycles aligned to federal certification timelines.
- Firewall:Next-generation platforms integrate deep packet inspection with application-layer visibility. Munich-Stuttgart corridor manufacturers deploy these at OT-IT convergence points to segment industrial control networks from enterprise systems.
- Encryption Tools:Hardware security modules and quantum-resistant algorithms anchor classified government networks. BSI certification mandates stretch procurement cycles but lock in multi-year replacement schedules across federal agencies.
- Antivirus Software:Endpoint detection and response platforms displace signature-based scanning across Mittelstand manufacturing networks.
- Intrusion Detection System:Network behavior analytics tools monitor east-west traffic flows in containerized cloud environments.
Most installed capacity flows through Firewall segments. Expansion is steepest in Encryption Tools.
Deployment Model:
Cost tier stratification separates sovereign infrastructure investments from consumption-based service contracts.
- Cloud-Based:Elastic compute architectures enable rapid security stack scaling without capital expenditure commitment. Bavarian automotive suppliers favor this model for connected vehicle telemetry processing to avoid captive data center maintenance.
- Managed Services:External Security Operations Center capabilities deliver 24/7 threat monitoring without specialist hiring burdens. North Rhine-Westphalia mid-caps exhibit the fastest behavioral transition toward subscription-based security operations.
- On-Premises:Air-gapped installations persist in defense and classified research facilities with data sovereignty requirements.
- Hybrid:Split architectures maintain sensitive workloads locally while bursting analytics to sovereign cloud instances.
Cloud-Based deployments carry the largest current installed base. Managed Services is gaining share fastest.
End User:
Application maturity varies dramatically across vertical risk exposure and regulatory scrutiny intensity.
- Government:Federal and state administrations mandate BSI-certified components with hardware-based trust anchors. Procurement concentrates through T-Systems sovereign cloud frameworks and Secunet high-assurance encryption.
- Financial Services:BaFin supervision drives continuous authentication and transaction monitoring investments across Frankfurt banking clusters.
- Healthcare:Patient data protection requirements accelerate endpoint hardening for clinical IoT device fleets.
- Manufacturing:Industrial control system segmentation dominates security expenditure in Baden-Württemberg automotive supply chains.
Government vertical absorbs the deepest compliance-driven investment. Healthcare is expanding most quickly.
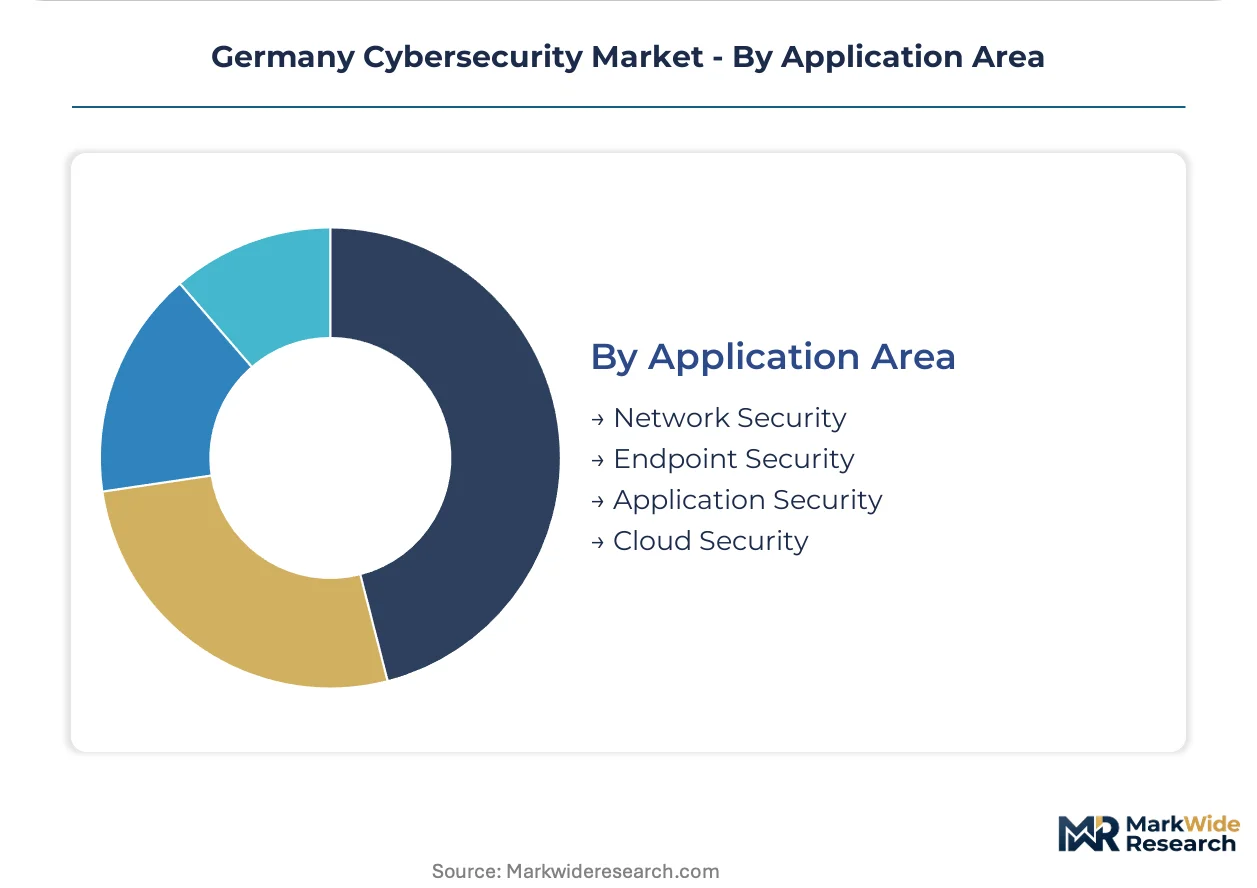
Application Area:
Supply concentration in defense-tech clusters shapes regional demand patterns for high-assurance implementations.
- Network Security:Zero-trust architecture mandates compress procurement cycles across critical infrastructure operators. Secure access service edge frameworks collapse point solutions into unified cloud-native stacks.
- Endpoint Security:Remote-work attack surface expansion sustains premium pricing for device-level protection platforms. Stuttgart automotive manufacturers prioritize these for engineering workstation fleets.
- Cloud Security:Shared responsibility model confusion drives demand for configuration management and workload protection tools.
- Application Security:DevSecOps pipeline integration requirements reshape software development practices in industrial automation vendors.
Network Security commands the largest installed capacity. Cloud Security shows the steepest expansion trajectory.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Compliance cost differentials across German federal states are redirecting cybersecurity procurement toward jurisdictions with streamlined BSI certification pathways. Bavaria and Baden-Württemberg absorb the deepest investment due to defense-tech clustering, while North Rhine-Westphalia captures mid-market outsourcing demand.
Bavaria
BSI baseline protection mandates drive sovereign cloud procurement across Munich federal and state administrations. The IT Security Act requires systematic risk management for energy and transport operators, compressing vendor selection timelines. The Munich-Stuttgart corridor concentrates defense-tech headquarters and high-assurance encryption specialists serving classified networks.
North Rhine-Westphalia
Mid-cap manufacturers abandon perpetual licenses for consumption-based security contracts across the Mittelstand manufacturing segment. EU NIS2 transposition tightens supply-chain security obligations for industrial automation vendors. Value-added resellers in Cologne-Düsseldorf capture recurring revenue through bundled threat detection and response offerings.
Baden-Württemberg
Connected vehicle security mandates from automotive OEMs expand encryption procurement across Tier-1 and Tier-2 supplier networks. The EU Cyber Resilience Act imposes conformity requirements on hardware and software products with digital elements. Stuttgart manufacturers adopt confidential computing for trusted execution environments in connected vehicle telemetry processing.
Hesse
BaFin supervision drives continuous authentication investments across Frankfurt banking clusters. Financial services operators mandate hardware-based trust anchors for transaction monitoring systems. The Rhine-Main metropolitan area concentrates IT security consultancies serving regulated financial institutions.
Berlin-Brandenburg
Federal vocational retraining initiatives accelerate certified security architect supply for zero-trust implementation demand. Start-up ecosystem density attracts venture capital for quantum-resistant cryptography pilots. The capital region hosts BSI headquarters and federal cybersecurity policy coordination.
Germany Cybersecurity Market Competitive Landscape
Bavaria-based sovereign infrastructure providers anchor the high-assurance tier; North Rhine-Westphalia mid-market specialists hold the managed services segment. Market structure consolidates around three archetypes: federal cloud contractors, automotive supply-chain security vendors, and mid-cap outsourcing providers. M&A activity concentrates on zero-trust capability acquisition; strategic partnerships dominate sovereign cloud framework participation.
Within the federal contractor tier, T-Systems and Secunet Security Networks exemplify high-assurance positioning. Rohde & Schwarz Cybersecurity occupies a specialized niche in electromagnetic spectrum security. These three entities represent distinct competitive vectors: sovereign cloud infrastructure, classified network encryption, and hardware-based trust modules for defense applications.
| Leading Market Players |
|---|
| T-Systems |
| Infodas |
| Factosecure |
| IBM Security Germany |
| Atos Germany Cybersecurity |
| Secunet Security Networks |
| G DATA CyberDefense |
| Cisco Security Germany |
| Rohde & Schwarz Cybersecurity |
| Others |
Supply & Pricing Matrix
Certified security architect scarcity across Bavaria and Baden-Württemberg widens labor-cost differentials between sovereign-cloud providers and mid-market managed services vendors, compressing pricing-tier spreads at the lower end while sustaining premium tiers for BSI-certified implementations.
Pricing Analysis
Distributor margins on hardware security modules compress as direct-to-OEM procurement channels expand for automotive Tier-1 suppliers. Subscription-based SaaS tiers dominate endpoint security delivery, with price differentiation anchored in certification grade and volume scale. Pricing pressure stems from mid-market buyers abandoning perpetual licenses for consumption-based contracts. Mittelstand manufacturers exhibit highest price sensitivity; federal agencies demonstrate lowest.
Supply Chain Analysis
Workforce availability constraints in Munich-Stuttgart corridor manufacturing nodes tether component sourcing to Taiwan semiconductor foundries and Netherlands lithography equipment. Hardware trust modules draw from specialized German fabrication, while encryption software development centers on Berlin-Brandenburg. Single-source vulnerability in advanced node semiconductors poses structural risk. Distribution runs through value-added resellers bundling threat detection with implementation services.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Germany's cybersecurity market functions as a geographic-arbitrage play between Bavaria's high-assurance federal contracting premiums and North Rhine-Westphalia's mid-market outsourcing cost efficiencies, with NIS2 compliance timelines widening the regulatory-cost differential.
For Market Incumbents: Acquire zero-trust architecture capabilities to counter cloud-native challenger erosion in the Mittelstand segment. Deepen BSI certification pipelines ahead of NIS2 enforcement timelines. Anchor sovereign cloud infrastructure investments in Munich federal procurement corridors.
For New Entrants and Emerging Players: Quantum-resistant cryptography pilots offer technology-first positioning against established encryption vendors. White-space concentrates in mid-market managed SOC outsourcing across Cologne-Düsseldorf industrial clusters. Go-to-market leverage: consumption-based pricing without captive specialist hiring burdens.
For Investors and Strategic Acquirers: Defense contractors are the most active acquirer in this space, consolidating electromagnetic spectrum security and hardware trust module specialists. Long-term viability favors vertically integrated platforms spanning sovereign infrastructure to endpoint protection. Watch NIS2 transposition velocity as inflection indicator for compliance-driven procurement acceleration.
| Strategic Initiative | Industry Significance |
|---|---|
| Zero-Trust Architecture Acquisition | Consolidates continuous verification capabilities against perimeter-defense legacy vendors. |
| BSI Certification Pipeline Expansion | Aligns product roadmaps with federal procurement criteria under IT Security Act mandates. |
| Managed SOC Platform Launch | Captures recurring revenue from mid-market buyers avoiding captive security hiring. |
| Quantum-Resistant Cryptography Pilot | Positions early-mover advantage for federal agency post-quantum encryption standards. |
| Sovereign Cloud Infrastructure Partnership | Anchors public-sector contracts through T-Systems federal framework participation. |
Research Methodology
Direct dialogue with CISOs at automotive OEMs, federal procurement officers, managed security service providers, and BSI certification specialists grounded qualitative findings in operational reality. Secondary validation drew from BSI technical guidelines, EU NIS2 directive texts, federal IT Security Act documentation, and Bavarian economic development cluster reports. Bottom-up segment sizing triangulated against top-down macroeconomic anchors.
Bottom-up modeling aggregated individual product-category trajectories across deployment models and end-user verticals; top-down constraints applied GDP-correlated IT spending elasticities. Segmentation dimensions spanned product architecture, deployment model, end-user vertical, and regional compliance intensity. CAGRs derived from fitted trend extrapolation with scenario-weighted adjustments for regulatory enforcement timelines and technology substitution curves.
Forecast confidence holds firmest in the near-window; longer-horizon outcomes carry greater sensitivity to NIS2 transposition delays, quantum computing breakthrough timelines, and federal certification schedule shifts. Forecasts reflect documented assumptions on compliance adoption rates and technology migration patterns. Material deviation in BSI enforcement velocity or post-quantum standardization warrants pause and re-evaluation.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Cloud-Based Email Security Market
Cybersecurity
Sweden Cybersecurity Market
Cybersecurity
Europe Mobile Security Market
Cybersecurity
Cloud-Based Database Security Market
Cybersecurity
Canada Ransomware Protection Market
Cybersecurity
Cybersecurity Mesh Market
Cybersecurity
Africa Cybersecurity Market
Cybersecurity
Cloud DLP Market
Cybersecurity
Application Security Market
Cybersecurity
Mobile Encryption Market
Cybersecurity
Micro-Segmentation Solutions Market
Cybersecurity
Retail Cybersecurity Market
Cybersecurity
Application-Level Encryption Market
Cybersecurity
Global Healthcare IoT Security Market
Cybersecurity
Global Ddos Protection Market
Cybersecurity
Belgium Cybersecurity Market