
 Prescriptive Security Market | 2026-2036
Prescriptive Security Market Size, Share, and Industry Trends Forecast 2026-2036
Prescriptive Security Market Analysis
EU AI Act enforcement is expanding the cost-of-entry calculus for prescriptive security vendors selling into European critical infrastructure. IBM leverages its Watson cybersecurity platform to anchor hybrid cloud security deployments across regulated industries. Cisco Systems dominates network-layer prescriptive analytics through its integrated threat intelligence architecture. Splunk competes on real-time log correlation and automated response orchestration for enterprise security operations centers.
Prescriptive security denotes systems that apply artificial intelligence, machine learning, and behavioral analytics to anticipate threats, automate response protocols, and recommend preventive actions before incidents materialize. These platforms process streaming telemetry from endpoints, networks, and cloud environments to generate prioritized remediation directives with associated confidence scores and business impact weightings. Cloud Security solutions within the solution type dimension lead current spending as distributed workforces expand attack surfaces across multi-tenant environments. Managed Security Services within the service type category represents the fastest-growing margin pool, driven by skills shortages that push enterprises toward outsourced security operations with embedded prescriptive capabilities.
FDA oversight of connected medical devices, FCC rules on telecommunications infrastructure resilience, and SEC cyber disclosure mandates collectively shape product certification requirements and liability frameworks for prescriptive security vendors. HIPAA security rule enforcement is accelerating healthcare provider investment in automated threat prediction and response systems. Stakeholders must monitor how converging regulatory timelines for AI accountability and critical infrastructure protection reshape procurement criteria and vendor qualification standards across end-user segments.
Market Dynamics
The EU AI Act enforcement timeline is compressing vendor qualification windows and forcing rapid architecture redesigns for automated security decision systems across European critical infrastructure operators.
Growth Catalysts
- EU AI Act compliance mandates:Financial institutions in Germany and France accelerate procurement of auditable prescriptive analytics platforms to meet algorithmic accountability requirements before enforcement deadlines.
- Healthcare automation:HIPAA security rule enforcement drives hospital systems toward automated threat prediction systems that reduce manual security operations center workload.
- Critical infrastructure protection:Industrial operators integrate predictive threat models into SCADA and OT environments, creating demand for specialized prescriptive security modules.
Market Restraints
- Skills scarcity premium:Shortages of machine learning security engineers inflate implementation costs and extend deployment timelines for complex behavioral analytics platforms.
- Algorithmic liability uncertainty:Ambiguous fault allocation for automated security decisions under EU product liability frameworks chills vendor willingness to offer performance guarantees.
- Legacy system incompatibility:Aging SIEM architectures in established enterprises resist API-based integration with modern prescriptive analytics engines.
Strategic Opportunities
- Managed security services expansion:Skills gaps push mid-market enterprises toward outsourced security operations with embedded prescriptive capabilities, creating recurring revenue pools.
- Medical device security:FDA oversight of connected devices opens specialized vertical for prescriptive platforms that predict exploitation of hospital IoT endpoints.
- Convergence of XDR and SOAR:Extended detection and response platforms merging with security orchestration tools create architectural openings for unified prescriptive engines.
Industry Challenges
- Certification timeline compression:Vendors must achieve CE marking under MDR and EU AI Act conformity assessments simultaneously, straining regulatory affairs capacity.
- False positive management:Behavioral analytics systems generate alert volumes that overwhelm security operations center analysts, degrading trust in automated recommendations.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Prescriptive Security Market |
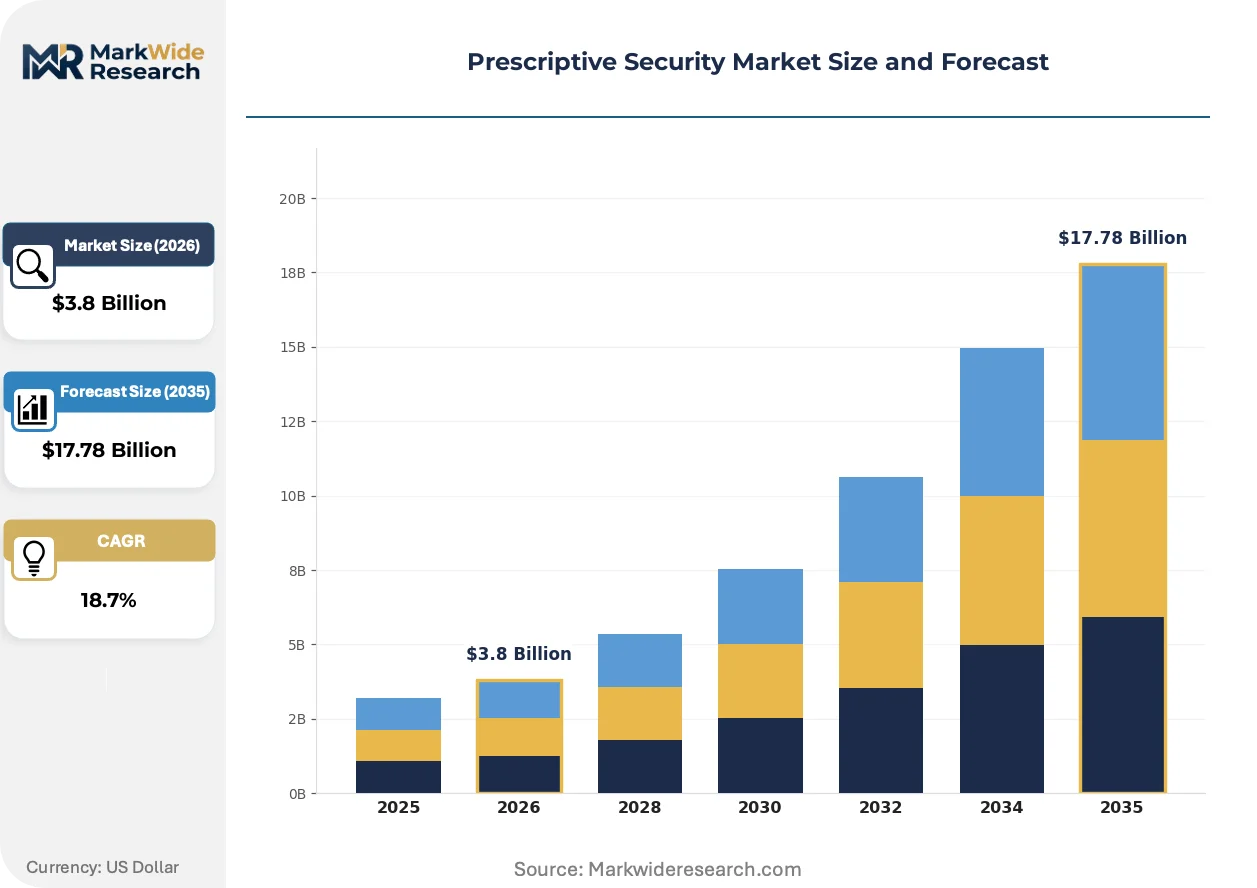
| Market Size in 2026 | $3.8 Billion |
| Market Size in 2035 | $17.78 Billion |
| CAGR (2026 – 2036) | 18.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Endpoint Protection, Network Security, Cloud Security, Application Security Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Service End User: Healthcare Providers, Educational Institutions, Government Agencies, Enterprises Service Type: Consulting, Integration, Managed Security Services, Support Services |
| Companies Covered | IBM, Cisco Systems, Hexagon, NEC Corporation, SAS Institute, Nice Systems, Splunk, ATOS, ESRI, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Prescriptive Security Market Emerging Trajectories
Artificial intelligence architectures are shifting from descriptive dashboards toward autonomous response generation, compressing the human-in-the-loop interval from hours to seconds across threat detection workflows.
Behavioral biometrics fused with network telemetry is expanding into financial services authentication flows. Large banks deploy continuous identity verification that analyzes keystroke dynamics and mouse patterns alongside transaction context. This convergence is compressing fraud detection latency from batch overnight processing to real-time intervention at payment authorization gates.
The EU AI Act risk classification system imposes documentation and human oversight requirements on high-risk automated security systems. Vendors must maintain technical files demonstrating algorithmic robustness, accuracy, and bias mitigation. Financial services and healthcare providers in Germany, France, and the Netherlands are demanding pre-certified platforms to accelerate their own compliance timelines.
Enterprise buyers are consolidating vendor relationships and demanding prescriptive capabilities bundled within existing cybersecurity contracts rather than procuring standalone point solutions. Security operations centers prefer platforms that ingest telemetry from their incumbent endpoint and network tools. This preference shift favors vendors with open API architectures and pre-built integrations over specialized best-of-breed players.
Prescriptive Security Market Segmentation
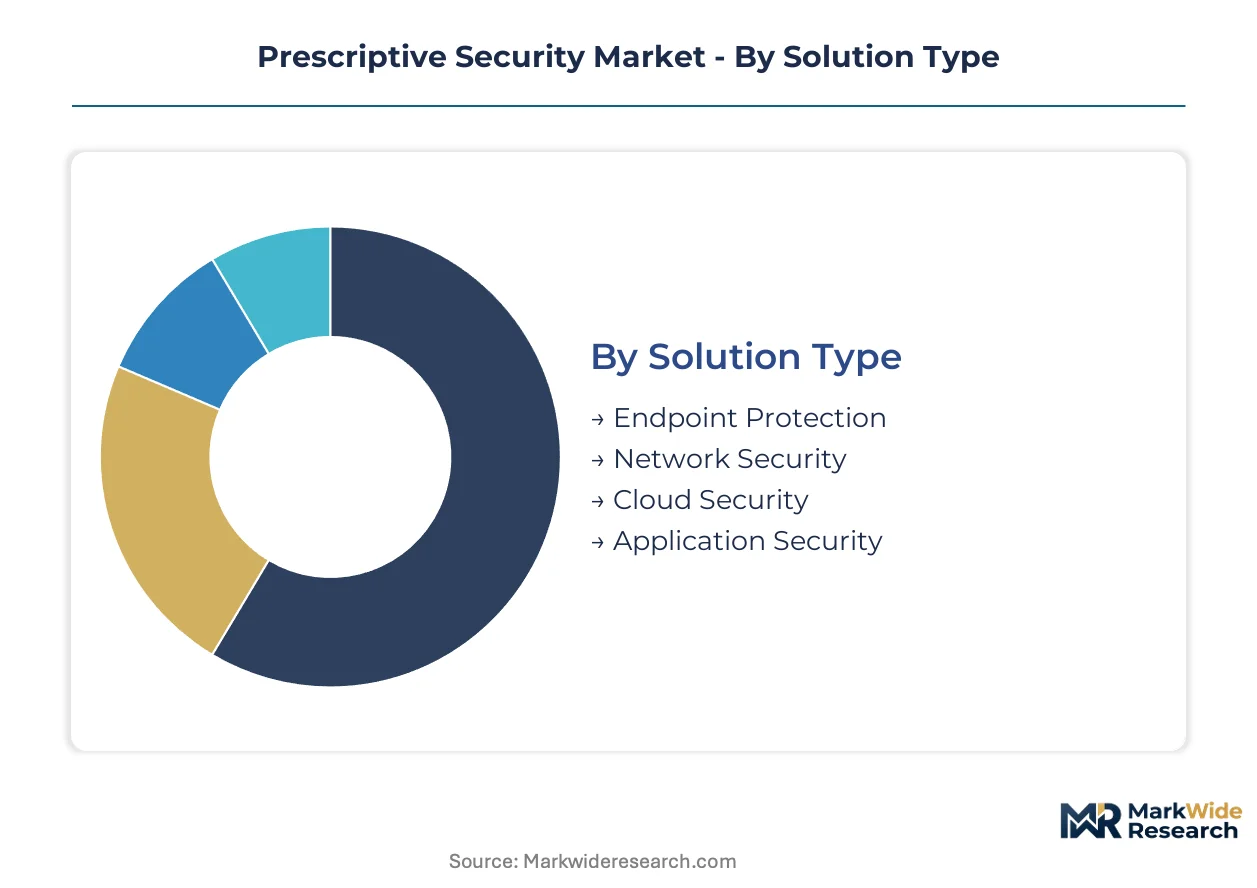
Prescriptive security vendors configure product architectures around four intersecting dimensions. Solution type determines core technology investment, while deployment model shapes recurring revenue mechanics and customer acquisition costs across regulated industries.
Solution Type:
Supply concentration in cloud-native architectures is pulling development resources away from endpoint-centric platforms toward distributed telemetry engines.
- Cloud Security:Platforms ingest multi-tenant telemetry across AWS, Azure, and GCP environments to generate automated remediation playbooks for misconfigurations and lateral movement. German automotive suppliers and French financial institutions are prioritizing these deployments to satisfy EU AI Act documentation requirements for high-risk automated decision systems.
- Network Security:Systems apply behavioral analytics to east-west traffic flows in software-defined perimeters, correlating NetFlow data with threat intelligence feeds. Demand clusters among telecommunications operators in the Netherlands and energy grid operators in Spain seeking predictive models for OT-IT convergence risks.
- Endpoint Protection:Agents deploy machine learning models locally for offline inference on device behavior.
- Application Security:Runtime application self-protection tools embed prescriptive logic directly into software execution paths.
Cloud Security absorbs the bulk of installed capacity; Network Security is expanding most quickly.
Deployment Model:
Cost tier stratification separates enterprise buyers with captive security operations centers from mid-market organizations outsourcing to managed service providers.
- Managed Service:Providers deliver prescriptive capabilities as embedded features within security operations center-as-a-service offerings, absorbing talent scarcity costs. Healthcare systems in Germany and manufacturing conglomerates in Italy are migrating to this model to bypass internal hiring bottlenecks for machine learning security engineers.
- Hybrid:Architectures split inference workloads between on-premises appliances for latency-sensitive OT environments and cloud backends for model training. Critical infrastructure operators in France and Belgium favor this approach to satisfy data residency requirements while accessing scalable compute.
- Cloud-Based:Fully SaaS-delivered platforms eliminate capital expenditure for endpoint agents.
- On-Premises:Air-gapped deployments serve classified government facilities and defense contractors.
Hybrid deployments carry the highest average contract values; Managed Service is gaining share fastest.
End User:
Application intensity varies sharply across verticals, with regulatory enforcement timelines dictating procurement urgency more than breach history.
- Healthcare Providers:Hospital systems deploy prescriptive platforms to automate HIPAA security rule compliance and predict exploitation of connected medical devices. FDA oversight of device cybersecurity is accelerating investment among integrated delivery networks in Germany and university medical centers in France.
- Government Agencies:National cybersecurity authorities mandate prescriptive analytics for critical infrastructure protection frameworks. German BSI certification requirements and French ANSSI procurement guidelines are standardizing algorithmic accountability documentation across public sector deployments.
- Enterprises:Fortune 500 manufacturers and retailers integrate prescriptive engines into existing SIEM investments.
- Educational Institutions:Universities with research hospital affiliations adopt healthcare-grade platforms for shared infrastructure.
Healthcare Providers command the deepest solution customization; Government Agencies are climbing the fastest on compliance-driven procurement cycles.
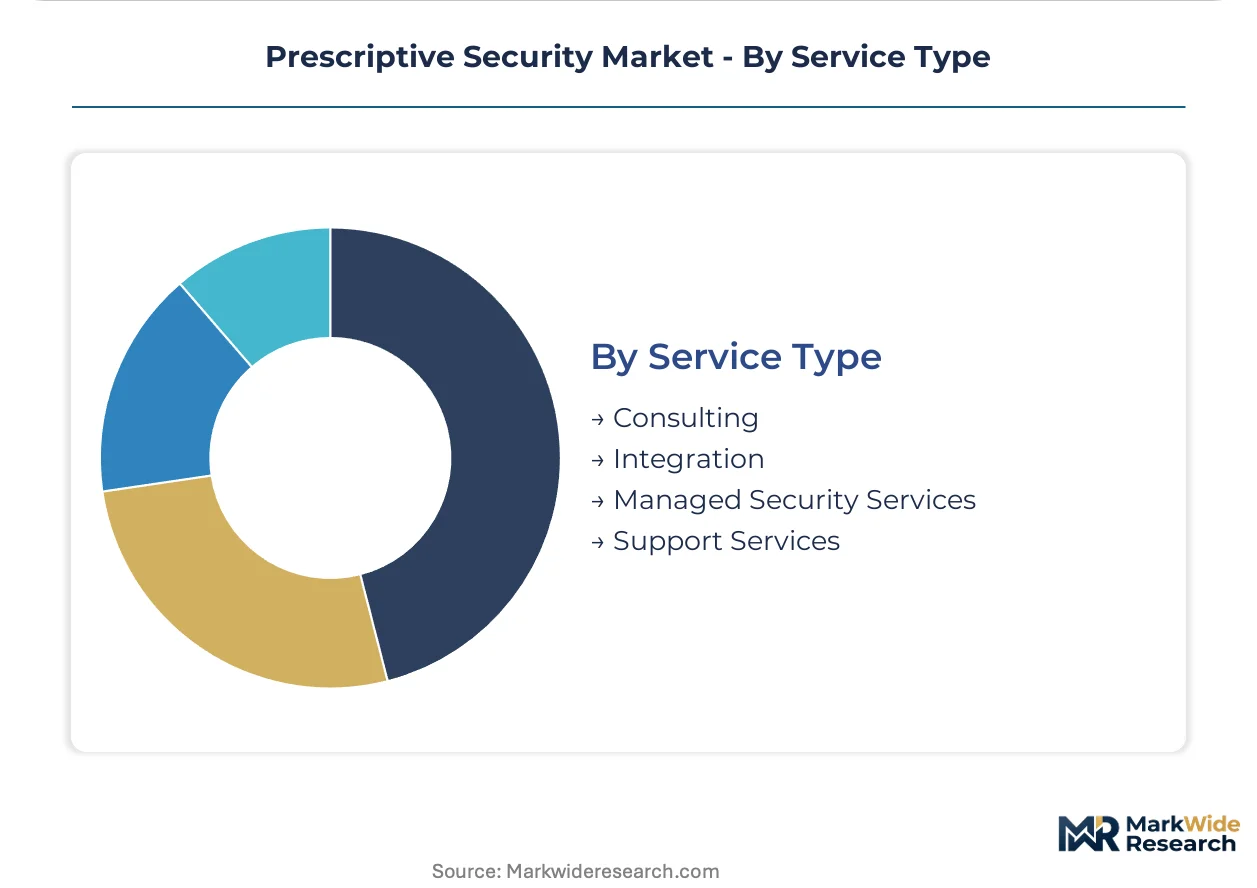
Service Type:
Margin structures favor recurring engagements over project-based delivery, with vendor capabilities converging toward outcome-based pricing models.
- Managed Security Services:Providers guarantee mean-time-to-containment metrics through prescriptive automation, aligning fees with operational outcomes. Skills shortages across Germany, France, and the Netherlands are compressing sales cycles for these engagements as enterprises abandon internal build strategies.
- Integration:Professional services embed prescriptive engines into heterogeneous tool stacks, resolving API incompatibility between legacy SIEM architectures and modern behavioral analytics platforms. System integrators in Germany and Belgium are building specialized practices around EU AI Act conformity assessment support.
- Consulting:Advisory engagements focus on algorithmic risk governance and bias mitigation documentation.
- Support Services:Tiered maintenance contracts cover model retraining and threat intelligence feed updates.
Managed Security Services captures the dominant share of recurring revenue; Integration services are expanding most quickly on retrofit demand.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Financial institutions in Germany and France are accelerating procurement of auditable prescriptive analytics platforms ahead of EU AI Act enforcement deadlines. Healthcare systems across Western Europe are automating HIPAA security rule compliance to reduce manual security operations center workload. Industrial operators in Belgium and the Netherlands are integrating predictive threat models into SCADA and OT environments.
Germany
Automotive suppliers and financial institutions dominate demand for cloud-native prescriptive security platforms. The BSI certification requirements mandate algorithmic accountability documentation for public sector deployments. Frankfurt's banking cluster and Munich's industrial corridor are prioritizing hybrid deployments that satisfy data residency requirements while accessing scalable cloud compute.
France
Energy grid operators and telecommunications providers are deploying network-layer behavioral analytics for OT-IT convergence risks. ANSSI procurement guidelines standardize prescriptive security requirements across critical infrastructure protection frameworks. The Paris-Saclay research cluster and Lyon manufacturing belt are driving integration of predictive models into legacy SIEM architectures.
United States
Fortune 500 manufacturers and integrated delivery networks are consolidating vendor relationships around bundled prescriptive capabilities. FDA oversight of connected medical devices and SEC cyber disclosure mandates shape product certification requirements and liability frameworks. The Boston healthcare corridor and Silicon Valley enterprise technology clusters are demanding platforms with open API architectures.
United Kingdom
Financial services firms are deploying continuous identity verification systems that analyze behavioral biometrics alongside transaction context. The national cybersecurity authority mandates prescriptive analytics for critical national infrastructure protection. London's fintech cluster and Cambridge research institutions are compressing fraud detection latency from batch processing to real-time intervention.
Netherlands
Telecommunications operators and port logistics companies are applying predictive models to east-west traffic flows in software-defined perimeters. Skills shortages are compressing sales cycles for managed security services as enterprises abandon internal build strategies. The Rotterdam port complex and Amsterdam financial district are migrating toward outsourced security operations with embedded prescriptive capabilities.
Prescriptive Security Market Vendor Landscape
United States producers anchor the scale-driven tier; European specialists hold the compliance-certified segment. The vendor base separates between consolidated platform providers with hybrid cloud security deployments and fragmented best-of-breed players with narrow behavioral analytics specializations. Three archetypes dominate: integrated technology conglomerates with cybersecurity divisions, pure-play analytics software vendors, and managed security service providers with embedded automation. Competitive moves concentrate on strategic partnerships for API interoperability and portfolio diversification into medical device security verticals.
Within the integrated platform tier, IBM and Cisco Systems exemplify archetypes of technology conglomerates leveraging existing enterprise relationships. Splunk occupies a position among pure-play analytics specialists competing on real-time log correlation capabilities. These three companies represent the dominant competitive anchors across the prescriptive security landscape, each sitting within distinct strategic positioning vectors.
| Leading Market Players |
|---|
| IBM |
| Cisco Systems |
| Hexagon |
| NEC Corporation |
| SAS Institute |
| Nice Systems |
| Splunk |
| ATOS |
| ESRI |
| Others |
Supply Flow & Price Mechanics
Horizontal integration into managed security service provider networks anchors pricing power for prescriptive security vendors across European critical infrastructure markets. This consolidation pattern concentrates procurement leverage among German automotive suppliers and French financial institutions while compressing margins for standalone platform vendors lacking embedded service delivery capabilities.
Pricing Analysis
Volume concentrates in subscription-based SaaS tiers while margin pools shift toward outcome-based managed service contracts. Three-tier pricing structure across enterprise-grade, mid-market, and entry-level configurations reflects certification complexity under EU AI Act documentation requirements. Pricing pressure stems from skills scarcity premiums inflating implementation costs for behavioral analytics deployments. Mid-market enterprises exhibit highest price sensitivity as they abandon internal security operations center builds in favor of outsourced alternatives.
Supply Chain Analysis
Specialized GPU hardware supply rests on Taiwanese semiconductor foundries and South Korean memory manufacturers for model training infrastructure. Cloud compute capacity draws from hyperscaler data centers across Germany, Ireland, and the Netherlands to satisfy EU data residency mandates. Single-source vulnerability concentrates in NVIDIA accelerator supply chains for real-time inference workloads. Distribution runs through certified system integrators in Germany and Belgium who bundle prescriptive engines with EU AI Act conformity assessment services.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The prescriptive security market sits at a technology-transition inflection where autonomous response generation displaces human-in-the-loop security operations center workflows. Machine learning inference at the network edge is replacing centralized SIEM correlation architectures across regulated European industries.
For Market Incumbents: Anchor hybrid cloud security deployments through existing enterprise relationships to defend against pure-play analytics specialists. Prioritize API interoperability investments that ingest telemetry from incumbent endpoint and network tools already deployed in Fortune 500 manufacturing environments. Certification capacity expansion under BSI and ANSSI frameworks creates defensive moats against emerging entrants lacking regulatory affairs scale.
For New Entrants and Emerging Players: Mid-market healthcare systems in Italy and Spain represent the most penetrable buyer archetype as skills shortages compress sales cycles for outsourced security operations. Target medical device security verticals where FDA oversight creates specialized demand for predictive exploitation models. Position through managed service provider channel partnerships rather than direct enterprise sales to bypass incumbent vendor consolidation preferences.
For Investors and Strategic Acquirers: Exit pathways concentrate in platform acquisitions by technology conglomerates seeking cybersecurity division expansion. Five-to-ten year viability favors vendors with pre-certified EU AI Act compliance documentation and established managed security service revenue streams. Watch algorithmic liability framework clarifications under European product liability directives as the critical inflection signal for performance guarantee willingness and valuation multiples.
| Strategic Initiative | Industry Significance |
|---|---|
| EU AI Act Pre-Certification Investment | Accelerates procurement timelines for German financial institutions and French healthcare providers facing enforcement deadlines. |
| Managed Security Service Provider Partnership | Captures mid-market enterprises abandoning internal security operations center builds due to machine learning engineer scarcity. |
| Medical Device Security Vertical Expansion | Opens specialized revenue pools through FDA-mandated predictive exploitation models for hospital IoT endpoints. |
| API Interoperability Architecture Development | Enables telemetry ingestion from incumbent endpoint and network tools preferred by consolidating enterprise buyers. |
| Hybrid Deployment Capability Buildout | Satisfies French and Belgian data residency requirements while accessing scalable cloud compute for model training. |
Methodological Framework
Independent corroboration across chief information security officers, managed security service provider executives, and EU regulatory affairs specialists underwrites the qualitative findings in this study. Primary interviews with hospital system procurement directors and industrial control system engineers combined with secondary validation from SEC cyber disclosure filings, BSI certification databases, and ANSSI procurement guidelines established demand-side patterns. Bottom-up deployment estimates triangulated against top-down vendor revenue assessments across the analysis window.
Comparable-period anchoring to historical security operations center automation adoption curves shaped the projection methodology for autonomous response generation penetration. Segmentation modeling incorporated solution type, deployment model, end-user vertical, and service type dimensions alongside regulatory compliance tier as an industry-specific stratifier. CAGRs derived from fitted adoption curves reflecting EU AI Act enforcement timeline compression and healthcare HIPAA automation mandates.
Revisions become necessary when algorithmic liability frameworks clarify fault allocation for automated security decisions or when hyperscaler cloud capacity constraints disrupt model training infrastructure supply. Forecasts reflect documented assumptions about regulatory enforcement adherence and skills shortage persistence. A small set of named triggers warrants ongoing watch: EU AI Act conformity assessment capacity bottlenecks, FDA medical device cybersecurity rulemakings, and critical infrastructure protection framework expansions beyond current member state coverage.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security and Surveillance
Lawful Interception Market
Security and Surveillance
Smart Security in Healthcare Market
Security and Surveillance
Door and Window Alarm Market
Security and Surveillance
Destructible Security Labels Market
Security and Surveillance
Global Threat Intelligence Management Market
Security and Surveillance
Maritime Security Market
Security and Surveillance
Global Security Advisory Services Market
Security and Surveillance
Global X-Ray Security Scanner Market
Security and Surveillance
5G-Enhanced Surveillance Market
Security and Surveillance
Middle East Manned Security Services Market
Security and Surveillance
Global Manned Security Service Market
Security and Surveillance
Europe Rockfall Radar Market
Security and Surveillance
Security Analytics Market
Security and Surveillance
Full Body Scanner Market
Security and Surveillance
India Electronic Security Market
Security and Surveillance
North America Security Screening Market