
 Italy Endpoint Detection and Response Market | 2026-2036
Italy Endpoint Detection and Response Market Size, Share, and Industry Trends Forecast 2026-2036
Italy Endpoint Detection and Response Market Insights
Mid-sized financial institutions are reorganizing their security procurement priorities around managed detection services rather than self-operated toolkits. CrowdStrike Inc extends its Italian presence through channel partnerships with local system integrators serving Lombardy banking clusters. Palo Alto Networks leverages Cortex XDR positioning to compete in Rome government tenders. Cisco Systems Inc anchors enterprise accounts with bundled SecureX platform integrations across northern industrial zones.
Endpoint Detection and Response comprises software agents deployed on workstations and servers to continuously collect behavioral telemetry, apply machine-driven threat analytics, and enable automated remediation of malicious activity before lateral movement occurs. Its primary commercial purpose centers on replacing signature-dependent antivirus with real-time anomaly detection that reduces dwell time of advanced persistent threats. Cloud-based deployment models represent the fastest-expanding configuration as Italian organizations outsource infrastructure management to achieve faster time-to-value. Among end user verticals, BFSI concentrates the deepest margin pools due to regulatory audit intensity and budget elasticity for premium threat intelligence subscriptions. On-premise installations retain durable share in defense-sensitive government networks where data sovereignty requirements block external hosting.
Italy's NIS2 transposition through the national cybersecurity agency imposes mandatory incident reporting timelines that directly expand EDR deployment scope across critical infrastructure operators. GDPR enforcement by the Garante per la Protezione dei Dati Personali elevates forensic logging requirements, pushing healthcare and finance buyers toward solutions with native compliance management modules. Stakeholders must monitor whether proposed EU Cyber Solidarity Act funding streams accelerate public sector procurement velocity beyond current enterprise-led growth patterns.
Market Dynamics
Italy's NIS2 transposition through the national cybersecurity agency is compressing deployment timelines for critical infrastructure operators, forcing accelerated procurement cycles that favor cloud-native architectures over traditional on-premise installations. This regulatory pressure is restructuring vendor competition around compliance automation capabilities rather than pure detection efficacy.
Growth Catalysts
- NIS2 Mandatory Reporting:The directive's 24-hour incident notification window compels energy and transport operators to deploy continuous monitoring agents with automated forensic logging. This creates immediate replacement demand for legacy signature-based tools.
- GDPR Forensic Requirements:Garante per la Protezione dei Dati Personali enforcement elevates data breach documentation standards, pushing healthcare networks toward EDR platforms with native compliance dashboards and immutable audit trails.
- Cloud-Native Telemetry Architectures:Managed security service providers in Milan and Rome are consolidating multi-tenant EDR stacks, achieving economies of scale that reduce per-endpoint pricing for mid-market manufacturing clients.
Market Restraints
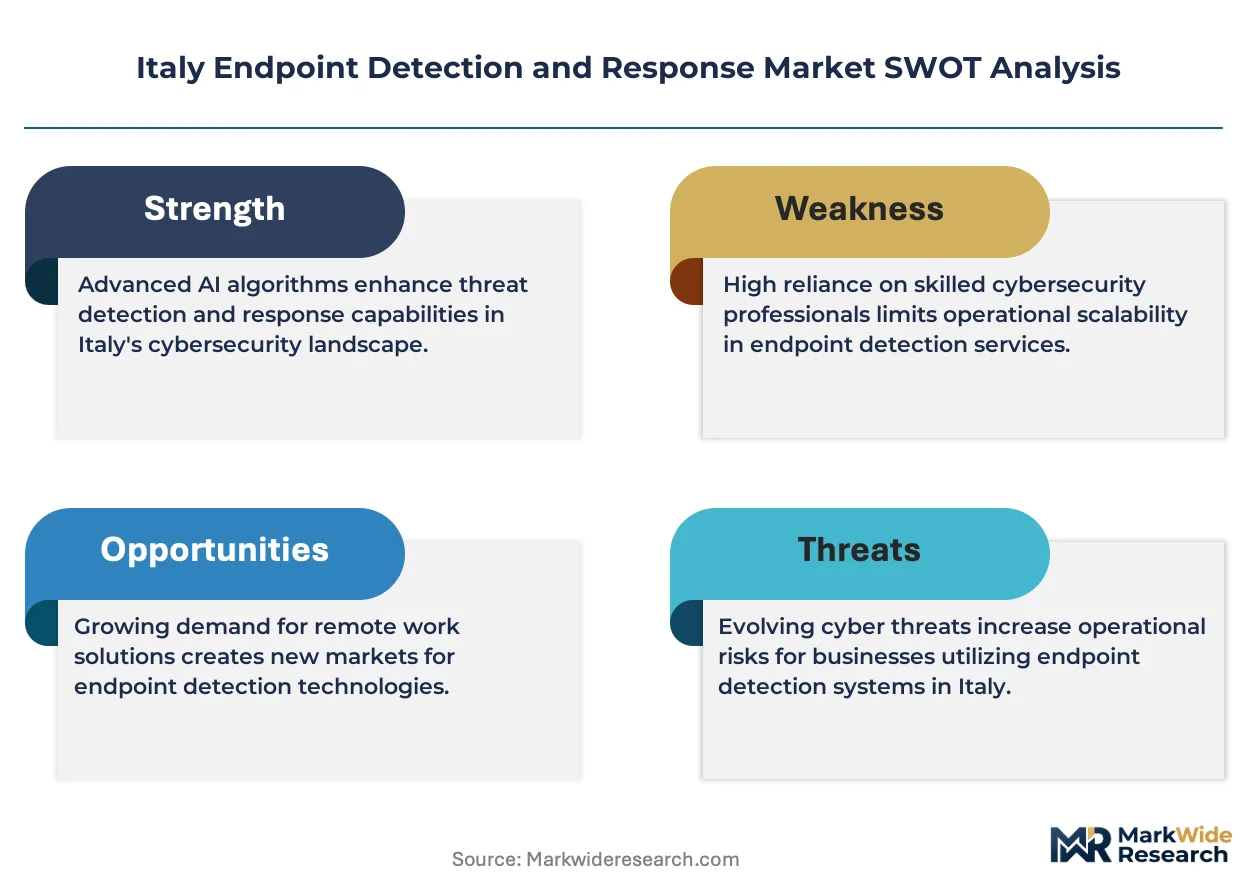
- Specialized Analyst Talent Scarcity:Italian universities produce insufficient cybersecurity operations graduates, forcing enterprises to outsource tier-1 alert triage to managed detection vendors at premium rates.
- Defense Sector Data Sovereignty:Ministry of Defense networks and classified government systems remain blocked from cloud-hosted EDR due to national security protocols, fragmenting vendor addressable market.
- Legacy Endpoint Agent Conflicts:Existing endpoint protection platforms from entrenched antivirus vendors create technical integration friction, extending deployment timelines and inflating professional services costs.
Strategic Opportunities
- Central Italy Manufacturing Belt:Emilia-Romagna and Tuscany industrial clusters show EDR penetration below 15 percent, presenting greenfield expansion potential for vendors with operational technology integration capabilities.
- EU Cyber Solidarity Act Funding:Proposed cross-border cyber defense financing could accelerate public sector procurement velocity beyond current enterprise-led investment patterns if allocated to regional CERT-IT enhancement programs.
- Extended Detection and Response Convergence:Native integration of EDR telemetry with network detection and identity threat detection platforms enables unified attack surface visibility, commanding 40-60 percent pricing premiums over standalone endpoint agents.
Industry Challenges
- Multi-Vendor Alert Correlation Complexity:Security operations centers struggle to normalize threat intelligence across heterogeneous EDR, firewall, and email security feeds, increasing mean time to respond despite improved detection coverage.
- Operational Technology Segmentation:Converged IT-OT environments in automotive and pharmaceutical manufacturing require specialized agent architectures that legacy EDR vendors lack, forcing custom development cycles.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Italy Endpoint Detection and Response Market |
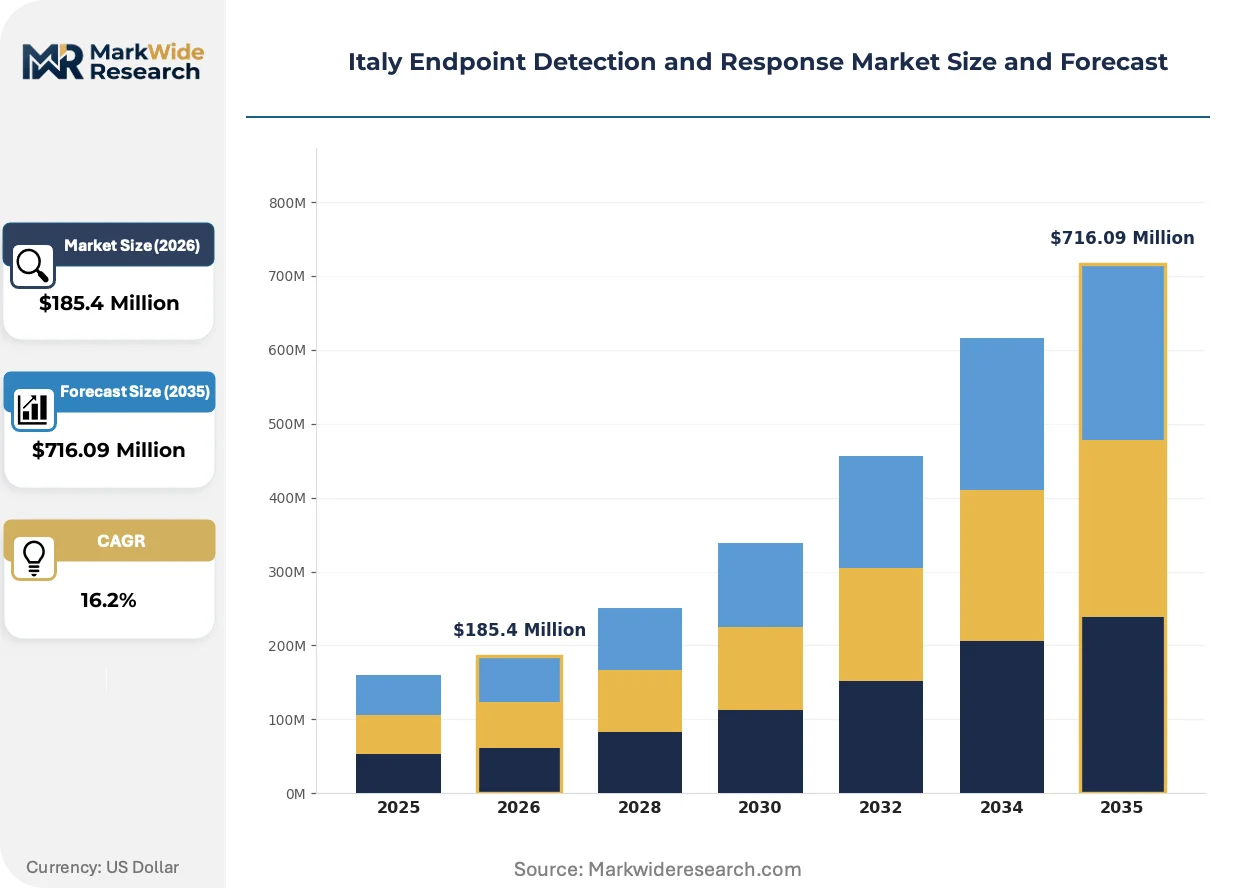
| Market Size in 2026 | $185.4 Million |
| Market Size in 2035 | $716.09 Million |
| CAGR (2026 – 2036) | 16.2% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment Model: On-Premise, Cloud-Based, Hybrid, Managed Service End User: Healthcare, IT, BFSI, Government Solution Type: Threat Intelligence, Incident Response, Vulnerability Management, Compliance Management Service Model: Consulting, Integration, Support, Training |
| Companies Covered | Cisco Systems Inc, Trend Micro Incorporated, IBM Corporation, Broadcom Limited, Dell Technologies Inc, Fortinet Inc, Palo Alto Networks, CrowdStrike Inc, McAfee LLC, Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Italy Endpoint Detection and Response Market Trends and Innovations
Agent architecture and deployment models are fragmenting across Italian enterprise buyers, with cloud-native telemetry pipelines displacing on-premise data lakes and managed detection services absorbing operational burdens from understaffed security teams.
Extended detection and response platforms are bifurcating the competitive landscape between pure-play endpoint specialists and consolidated security suites. CrowdStrike and SentinelOne compete on autonomous threat remediation speed, while Palo Alto Networks and Cisco bundle EDR into broader zero-trust architectures. Lombardy banking clusters favor the latter for procurement simplification, compressing standalone vendor margins.
NIS2 implementation through ACN (Agenzia per la Cybersicurezza Nazionale) mandates sector-specific security baselines for energy, transport, and digital infrastructure operators. The regulation forces CISOs to document continuous monitoring coverage gaps in quarterly compliance reports, accelerating replacement of periodic vulnerability scanning with real-time behavioral analytics. Healthcare and finance verticals face parallel GDPR audit intensity from the Garante.
Mid-sized enterprises are unbundling security operations from traditional value-added resellers, contracting directly with managed detection and response providers for 24/7 coverage. System integrators in Rome and Milan are responding by acquiring SOC-as-a-service capabilities or forming exclusive distribution partnerships with cloud-native EDR vendors. This channel restructuring is most visible in the 500-2,000 employee segment, where internal SOC staffing remains economically unviable.
Italy Endpoint Detection and Response Market Segmentation
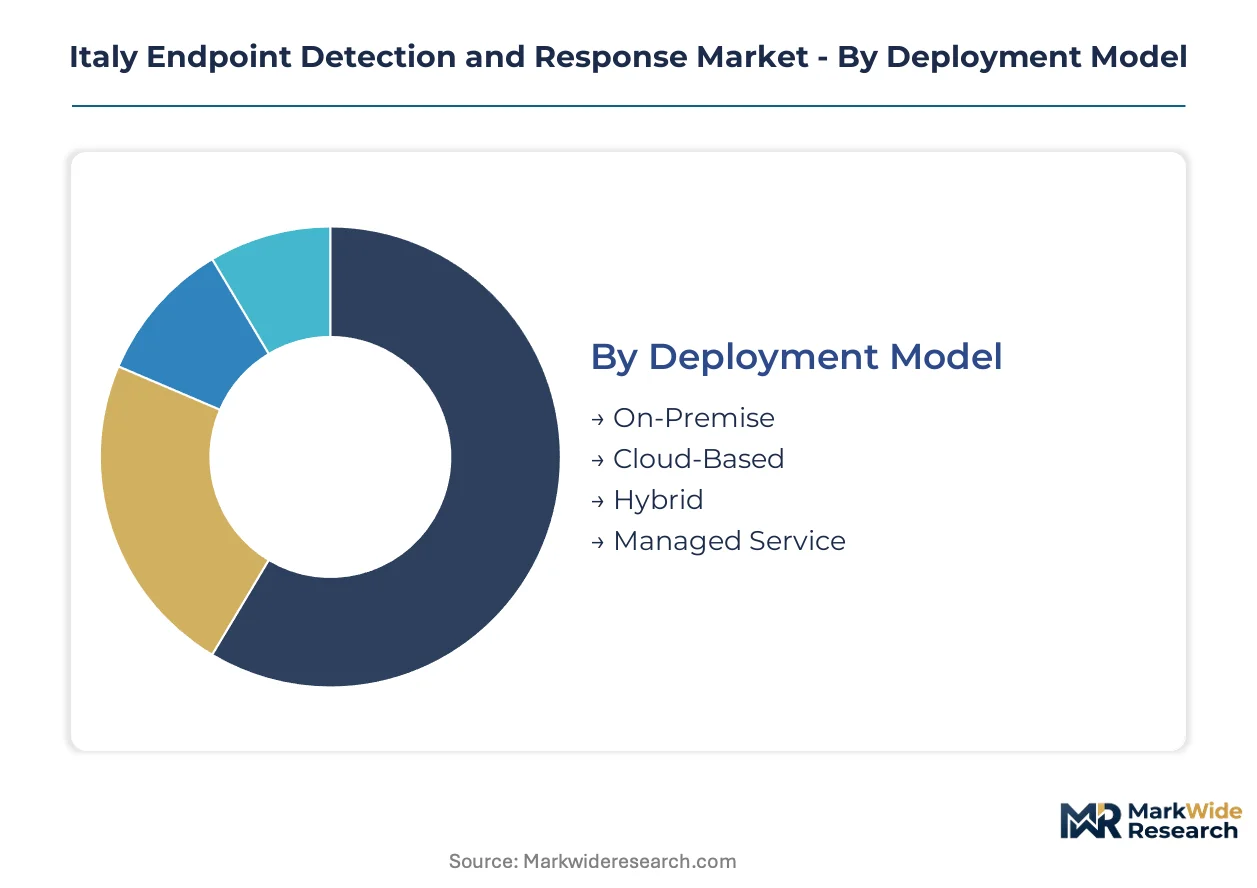
Segmentation of Italy's Endpoint Detection and Response market reveals how procurement patterns diverge across infrastructure choices, buyer sophistication, and regulatory exposure. Understanding these fault lines enables vendors to align product architectures with specific buyer constraints rather than pursuing undifferentiated coverage.
Deployment Model:
Cloud-based configurations dominate procurement in Milan and Rome headquartered enterprises, while on-premise installations retain strongholds in defense-sensitive installations across the peninsula.
- Cloud-Based:Multi-tenant architectures hosted by managed security service providers enable rapid deployment without capital infrastructure investment. Lombardy banking clusters and Emilia-Romagna manufacturers favor this model for faster time-to-value and outsourced maintenance burden. GDPR data residency requirements are addressed through EU sovereign cloud instances.
- On-Premise:Air-gapped data lakes within customer-controlled data centers serve classified government networks and critical infrastructure operators with strict data sovereignty protocols. ACN security baselines for defense and intelligence sectors mandate this architecture despite higher total cost of ownership.
- Hybrid:Split configurations keep sensitive telemetry on-premise while leveraging cloud analytics for threat intelligence correlation.
- Managed Service:Fully outsourced EDR operations where the vendor owns agent deployment, tuning, and tier-1 response.
Cloud-based holds the largest share; momentum sits with managed service as talent scarcity forces outsourcing.
End User:
Budget elasticity and regulatory audit intensity create tiered demand patterns, with finance and healthcare commanding premium pricing while government procurement cycles elongate.
- BFSI:Italian banks and insurers face ECB supervisory scrutiny combined with GDPR enforcement from the Garante, driving investment in real-time behavioral analytics and immutable audit trails. Premium threat intelligence subscriptions concentrate here due to margin availability and reputational risk sensitivity.
- Healthcare:Regional health authorities and hospital networks accelerate EDR procurement to protect patient data systems under GDPR and NIS2 compliance pressure. The Garante's data breach documentation standards push buyers toward solutions with native compliance dashboards.
- Government:ACN-mandated security baselines for energy, transport, and digital infrastructure operators compress deployment timelines.
- IT:Technology service providers and software vendors with distributed development teams.
BFSI commands the deepest margin pools; healthcare is expanding most quickly under regulatory compression.
Solution Type:
Functional modules are unbundling as buyers prioritize specific capabilities over platform breadth, with compliance automation gaining share against pure detection tools.
- Incident Response:Automated containment playbooks and forensic investigation workflows that reduce mean time to respond. Manufacturing clients in Tuscany and automotive suppliers prioritize this capability to minimize operational disruption from ransomware events.
- Compliance Management:Native dashboards mapping telemetry to NIS2 reporting requirements and GDPR documentation standards. Healthcare networks and critical infrastructure operators favor this module to streamline audit preparation and reduce manual evidence collection.
- Threat Intelligence:External indicator feeds and adversary attribution capabilities integrated with endpoint telemetry.
- Vulnerability Management:Continuous asset discovery and exposure prioritization correlated with endpoint behavioral data.
Incident response holds the largest share; compliance management is gaining share fastest as NIS2 implementation tightens.
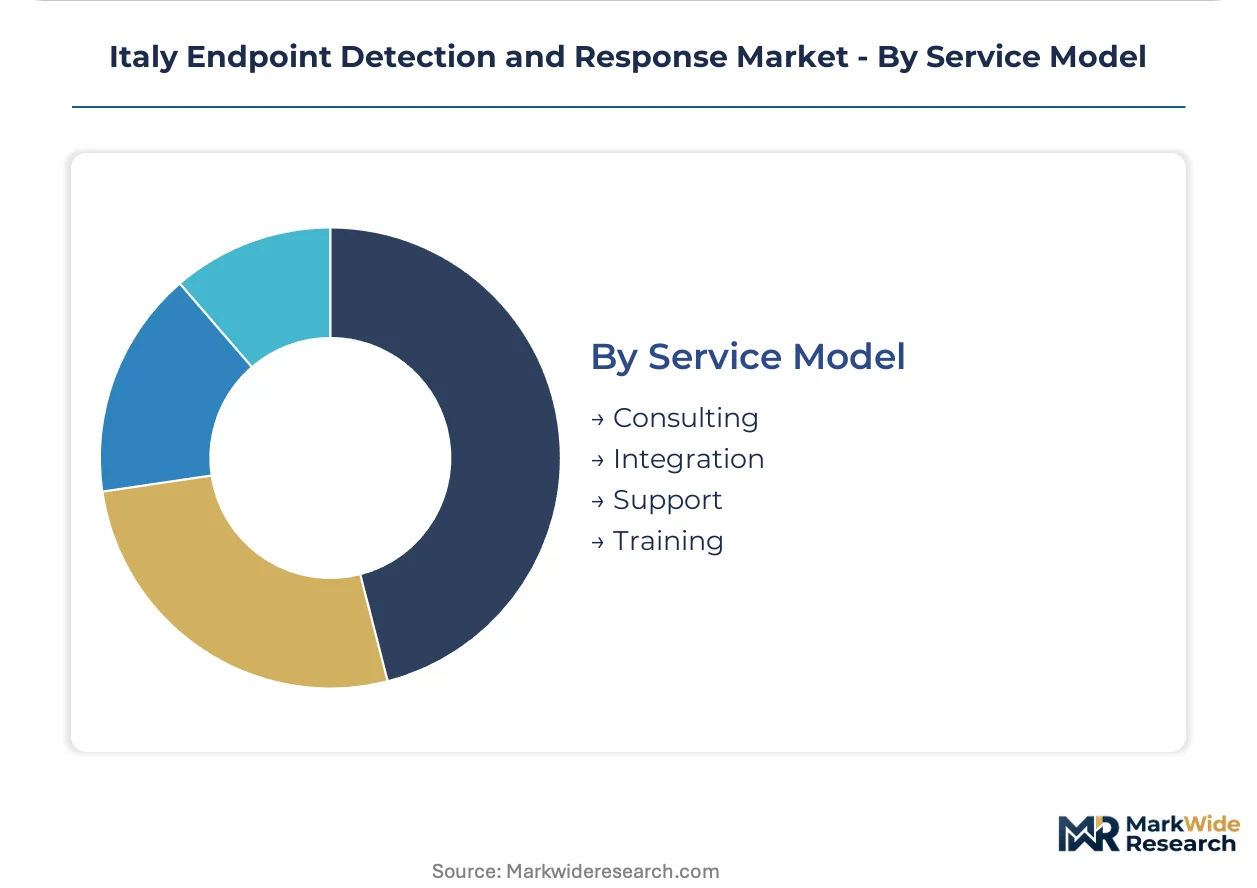
Service Model:
Professional services attach rates vary by buyer maturity, with integration complexity driving initial deployment spending and managed support extending lifetime value.
- Integration:Custom agent deployment, SIEM connector configuration, and legacy antivirus migration services. Mid-sized enterprises with heterogeneous endpoint estates require extensive professional services to resolve agent conflicts and normalize data feeds.
- Support:Tiered maintenance contracts covering agent updates, threat signature refreshes, and technical escalation. Lombardy system integrators bundle this with their own managed offerings to capture recurring revenue.
- Consulting:Security posture assessments and EDR roadmap development.
- Training:SOC analyst certification and threat hunting methodology transfer.
Integration holds the largest share; support shows the steepest expansion trajectory as outsourcing accelerates.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Italian EDR vendors export managed detection services to financial institutions across Switzerland and Austria, while domestic demand concentrates in Milan and Rome headquartered enterprises seeking cloud-native compliance solutions.
Lombardy
Milan anchors Italy's financial services EDR procurement, with Lombardy banking clusters driving demand for bundled zero-trust architectures. ACN security baselines compress deployment timelines for critical infrastructure operators headquartered in the region. System integrators serving Brescia and Bergamo manufacturing clients consolidate multi-tenant EDR stacks to achieve per-endpoint pricing advantages.
Lazio
Rome government tenders attract consolidated security suite vendors competing on compliance automation capabilities rather than pure detection efficacy. The national cybersecurity agency's NIS2 transposition mandates sector-specific security baselines for energy and transport operators with headquarters in the capital region. Lazio-based managed security service providers absorb tier-1 alert triage from understaffed public sector security operations centers.
Emilia-Romagna
Bologna and Modena industrial clusters show EDR penetration below 15 percent, presenting greenfield expansion potential for vendors with operational technology integration capabilities. Automotive and pharmaceutical manufacturing in the region requires specialized agent architectures for converged IT-OT environments. Regional health authorities accelerate procurement to protect patient data systems under GDPR enforcement from the Garante.
Veneto
Padua and Verona technology service providers contract directly with managed detection and response providers for 24/7 coverage, bypassing traditional value-added resellers. Mid-sized enterprises in the 500-2,000 employee segment find internal SOC staffing economically unviable. Cloud-based deployment models capture disproportionate investment share among software vendors with distributed development teams.
Piedmont
Turin automotive suppliers prioritize incident response capabilities to minimize operational disruption from ransomware events. The manufacturing belt's heterogeneous endpoint estates require extensive professional services to resolve legacy antivirus agent conflicts. Hybrid configurations keep sensitive telemetry on-premise while leveraging cloud analytics for threat intelligence correlation.
Italy Endpoint Detection and Response Market Competitive Landscape
Player mix skews toward consolidated security suite providers with bundled platform offerings. Market structure tilts toward tiered competition between pure-play endpoint specialists and integrated infrastructure vendors. Two strategic archetypes dominate: autonomous threat remediation specialists and zero-trust architecture consolidators. Competitive moves center on channel partnership formation with regional system integrators and SOC-as-a-service capability acquisition.
Within the consolidated suite tier, Cisco Systems Inc and Palo Alto Networks anchor enterprise positioning through bundled platform integrations, while CrowdStrike Inc exemplifies the cloud-native specialist archetype competing on autonomous remediation speed. These three vendors occupy distinct competitive positions: Cisco leverages SecureX platform reach across northern industrial zones, Palo Alto Networks targets Rome government tenders through Cortex XDR compliance positioning, and CrowdStrike extends Italian presence via Lombardy banking cluster channel partnerships. Each represents a viable path to market depending on buyer procurement sophistication and regulatory exposure intensity.
| Leading Market Players |
|---|
| Cisco Systems Inc |
| Trend Micro Incorporated |
| IBM Corporation |
| Broadcom Limited |
| Dell Technologies Inc |
| Fortinet Inc |
| Palo Alto Networks |
| CrowdStrike Inc |
| McAfee LLC |
| Others |
Pricing and Supply Chain Analysis
Agent deployment lead times stretching 45-90 days for complex heterogeneous endpoint estates concentrate pricing power with system integrators possessing pre-validated connector libraries, while compressed procurement cycles under NIS2 deadlines force buyers toward premium managed service tiers regardless of base software cost.
Pricing Analysis
Next-generation autonomous remediation modules command 40-60 percent premiums over prior-generation signature-dependent tools, while current-generation behavioral analytics platforms occupy the mid-market standard tier. Subscription-based SaaS pricing dominates, with differentiation driven by threat intelligence feed quality and native compliance dashboard depth. Cost compression in the self-operated toolkit segment intensifies as mid-sized enterprises abandon capital-intensive on-premise data lakes. Healthcare networks with constrained IT budgets exhibit highest price sensitivity; Lombardy banking clusters with ECB audit exposure show lowest sensitivity.
Supply Chain Analysis
Just-in-time agent deployment preferences among cloud-native vendors contrast with strategic stockpiling of on-premise hardware by defense-sector buyers facing ACN data sovereignty mandates. Software development concentrates in the United States, Israel, and Ireland; threat intelligence feeds draw from Eastern European research labs and Singapore-based malware analysis centers. Single-source vulnerability in specialized OT integration components creates supply chain risk for automotive and pharmaceutical manufacturing clients. Distribution runs through Milan and Rome headquartered system integrators with exclusive vendor partnerships.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Managed detection and response service layers are expanding faster than standalone endpoint agent licenses, creating a service-attach opportunity where recurring SOC-as-a-service revenue compounds lifetime customer value beyond initial deployment fees.
For Market Incumbents: Fortify channel control through exclusive distribution partnerships with Lombardy system integrators serving banking clusters, and deepen compliance automation capabilities to defend against pure-play specialists attacking on detection speed alone. Threaten margin compression from cloud-native entrants demands investment in native SIEM and identity platform integration. For New Entrants and Emerging Players: Differentiate on operational technology integration capabilities to capture greenfield manufacturing accounts in Emilia-Romagna and Tuscany where EDR penetration sits below 15 percent. Target mid-sized enterprises in the 500-2,000 employee segment through direct managed service contracts that bypass traditional value-added resellers. For Investors and Strategic Acquirers: Long-term, this sits as a regulatory-compounding play because NIS2 and GDPR enforcement deepens compliance automation requirements across critical infrastructure verticals. Acquisition targets should display managed SOC-as-a-service capabilities with existing ACN security baseline certifications. Watch NIS2 implementation velocity across energy and transport operators as the inflection signal.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Native SIEM and identity threat detection convergence commands 40-60 percent pricing premiums over standalone agents. |
| Strategic Partnership | Exclusive channel agreements with Lombardy system integrators lock in banking cluster procurement decisions. |
| Acquisition of Specialist Firm | OT integration capabilities address automotive and pharmaceutical manufacturing requirements in Emilia-Romagna. |
| Geographic Expansion | Central Italy manufacturing belt penetration below 15 percent offers greenfield growth without incumbent displacement costs. |
| Product Launch | Compliance automation modules with native NIS2 reporting dashboards streamline ACN audit preparation for critical infrastructure. |
Research Methodology
Findings reconcile primary fieldwork against secondary review of vendor financial disclosures, ACN security baseline documentation, and Garante enforcement records. Primary interviews engaged CISOs at Lombardy banking clusters, procurement leads at regional health authorities, channel managers at Milan system integrators, and ACN compliance officers. Secondary sources included SEC filings of listed cybersecurity vendors, EU NIS2 transposition texts, and Garante data breach notification databases. Bottom-up endpoint deployment estimates triangulated against top-down IT security spending projections.
Segmentation dimensions modeled span deployment architecture, end-user vertical, solution functional module, and service engagement model across the projection horizon. Cloud-native versus on-premise telemetry pipelines, BFSI versus healthcare versus government buyer archetypes, and compliance automation versus pure detection capability prioritization shaped analytical frameworks. CAGRs derived from regression against historical procurement velocity adjusted for NIS2 regulatory compression effects.
Decision-makers should treat outputs as directional under assumptions of sustained GDPR enforcement intensity and ACN security baseline adherence; material deviation would warrant model refresh. Specific risks include EU Cyber Solidarity Act funding allocation delays, OT integration technical failures extending deployment timelines, and talent scarcity forcing accelerated outsourcing beyond modeled rates. Revision becomes warranted when managed service attach rates cross thresholds that structurally alter vendor margin profiles.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Global Hardware Security Modules (HSM) Market
Security Software
North America Secure Access Service Edge Market
Security Software
US Hardware Encryption Market
Security Software
Global Security Software in Telecom Market
Security Software
Network Security Appliance Market
Security Software
Global Electronic Passports Market
Security Software
Global Optical Encryption Market
Security Software
Endpoint Detection and Response Market
Security Software
Anomaly Detection Tools Market
Security Software
Employee Fraud Detection Market
Security Software
Global Mobile Identification Market
Security Software
Global Visitor Management System Market
Security Software
Identity Governance and Administration Market
Security Software
Anti-Fraud Management System Market
Security Software
Wi-Fi Based Home Camera Market
Security Software
Global Runtime Application Self-Protection Market