
 IoT IAM Market | 2026-2036
IoT IAM Market Size, Share, and Industry Trends Forecast 2026-2036
IoT IAM Market Outlook
ISO/IEC 27001 certification is collapsing as the baseline gating standard for enterprise IoT IAM procurement, forcing vendors to demonstrate continuous compliance or exit RFP pipelines. Microsoft leverages its Azure Active Directory ecosystem to anchor cloud-based deployments across industrial accounts. Thales competes through hardware security module integration that sustains differentiation in regulated verticals. IBM specializes in managed identity services for hybrid environments where on-premises legacy systems persist.
IoT Identity and Access Management comprises the policy frameworks, cryptographic protocols, and lifecycle management tools that authenticate and authorize machine-to-machine and human-to-device interactions across distributed sensor networks, typically operating over protocols such as MQTT, CoAP, and TLS 1.3 with certificate-based mutual authentication. The primary commercial purpose is to prevent unauthorized device onboarding, data exfiltration, and lateral movement in architectures where traditional perimeter security fails. Cloud-based deployment leads in new contract value as enterprises abandon capital-intensive on-premises stacks, while edge computing represents the fastest-growing configuration for latency-sensitive automotive and industrial automation applications. Managed services capture disproportionate margin pools because recurring operational complexity exceeds in-house enterprise capability.
The EU AI Act, GDPR, and NIS2 Directive collectively mandate auditable identity chains for connected infrastructure, compelling vendors to embed compliance-by-design into product architectures. The US FDA and NHTSA impose parallel requirements for healthcare systems and automotive solutions, fragmenting certification pathways across Atlantic markets. Stakeholders must monitor regulatory divergence between Brussels and Washington to determine whether unified product platforms or region-specific builds deliver superior unit economics.
Market Dynamics
The EU AI Act and NIS2 Directive are compressing procurement cycles for enterprise IoT IAM, compelling vendors to embed continuous compliance validation into product architectures or face disqualification from RFP pipelines.
Growth Catalysts
- GDPR audit mandates:German automotive OEMs now require certificate-based mutual authentication for all supplier IoT devices, expanding contract values for compliant vendors.
- Smart home protocol standardization:MQTT and CoAP adoption across residential ecosystems is accelerating cloud-based IAM deployment as device density exceeds manual management capacity.
- Industrial automation clusters:Manufacturing concentration in Stuttgart and Munich is generating demand for edge-computing IAM configurations that reduce latency in human-to-device authentication.
Market Restraints
- Hardware security module costs:Thales and similar suppliers command premium pricing for FIPS 140-2 certified HSMs, compressing margins for mid-tier IAM vendors.
- TLS 1.3 certificate complexity:Mutual authentication overhead creates performance bottlenecks in battery-constrained sensor networks, limiting deployment in agricultural and remote monitoring applications.
- Regulatory fragmentation:Divergent certification pathways between the EU AI Act and US FDA requirements force vendors to maintain parallel product builds, inflating R&D overhead.
Strategic Opportunities
- Healthcare IoT convergence:FDA-mandated identity chains for connected medical devices create white space for vendors with HIPAA-compliant managed service offerings.
- Edge-AI authentication:Federated learning models combined with on-device biometric verification enable real-time authorization without cloud round-trips, opening automotive and robotics segments.
- India's PLI scheme:Domestic electronics manufacturing incentives are attracting IAM providers to establish localized certificate authority infrastructure for export-bound device ecosystems.
Industry Challenges
- Cryptographic talent scarcity:Enterprises report 18-month average hiring timelines for engineers with PKI and zero-trust architecture expertise, delaying deployment schedules.
- Legacy SCADA integration:Brownfield industrial sites require custom middleware to bridge decades-old Modbus and DNP3 systems with modern IAM stacks, inflating implementation costs.
- Continuous compliance validation:ISO/IEC 27001 recertification cycles demand dedicated operational teams that drain resources from product development functions.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | IoT IAM Market |
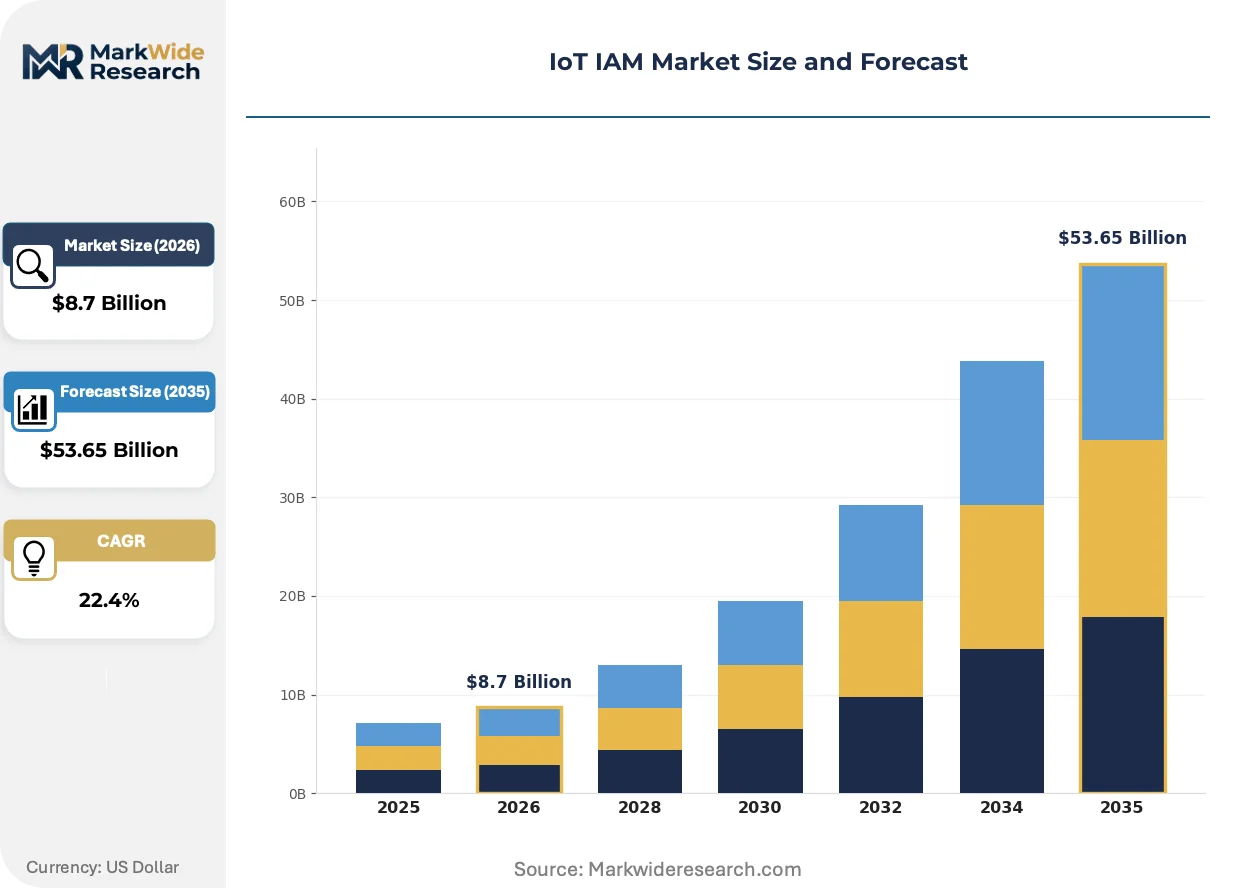
| Market Size in 2026 | $8.7 Billion |
| Market Size in 2035 | $53.65 Billion |
| CAGR (2026 – 2036) | 22.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premises, Cloud-Based, Hybrid, Edge Computing Application: Smart Home, Industrial Automation, Healthcare Systems, Automotive Solutions End User: Small & Medium Enterprises, Large Enterprises, Government Agencies, Third-Party Providers Service Type: Consulting Services, Integration Services, Managed Services, Support Services |
| Companies Covered | AWS, Thales, IBM, Microsoft, Cisco Systems, Oracle, Broadcom, Entrust, HID Global, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
IoT IAM Market Strategic Shifts
Zero-trust architectures are displacing perimeter-based security models across IoT deployments, forcing identity verification to occur at every network transaction rather than at network entry points.
Decentralized identity frameworks using self-sovereign principles are decomposing traditional certificate authority hierarchies. Automotive OEMs in Germany and Japan are piloting blockchain-anchored device credentials that eliminate single points of failure. This shift is compressing market share for centralized IAM providers while enabling peer-to-peer authentication in vehicle-to-everything networks.
The EU AI Act's risk classification system is mandating auditable identity chains for high-risk connected infrastructure. Industrial automation vendors must now demonstrate cryptographic provenance for every firmware update and device onboarding event. German machinery manufacturers are responding by embedding hardware security modules directly into servo drives and programmable logic controllers.
Subscription-based managed IAM services are displacing perpetual license models as enterprises confront operational complexity exceeding in-house capability. Procurement teams in healthcare and energy verticals now prioritize vendors offering 24/7 certificate lifecycle management over on-premises software ownership. This pattern is most visible in US hospital systems where HIPAA audit frequency has doubled since 2023.
IoT IAM Market Segmentation
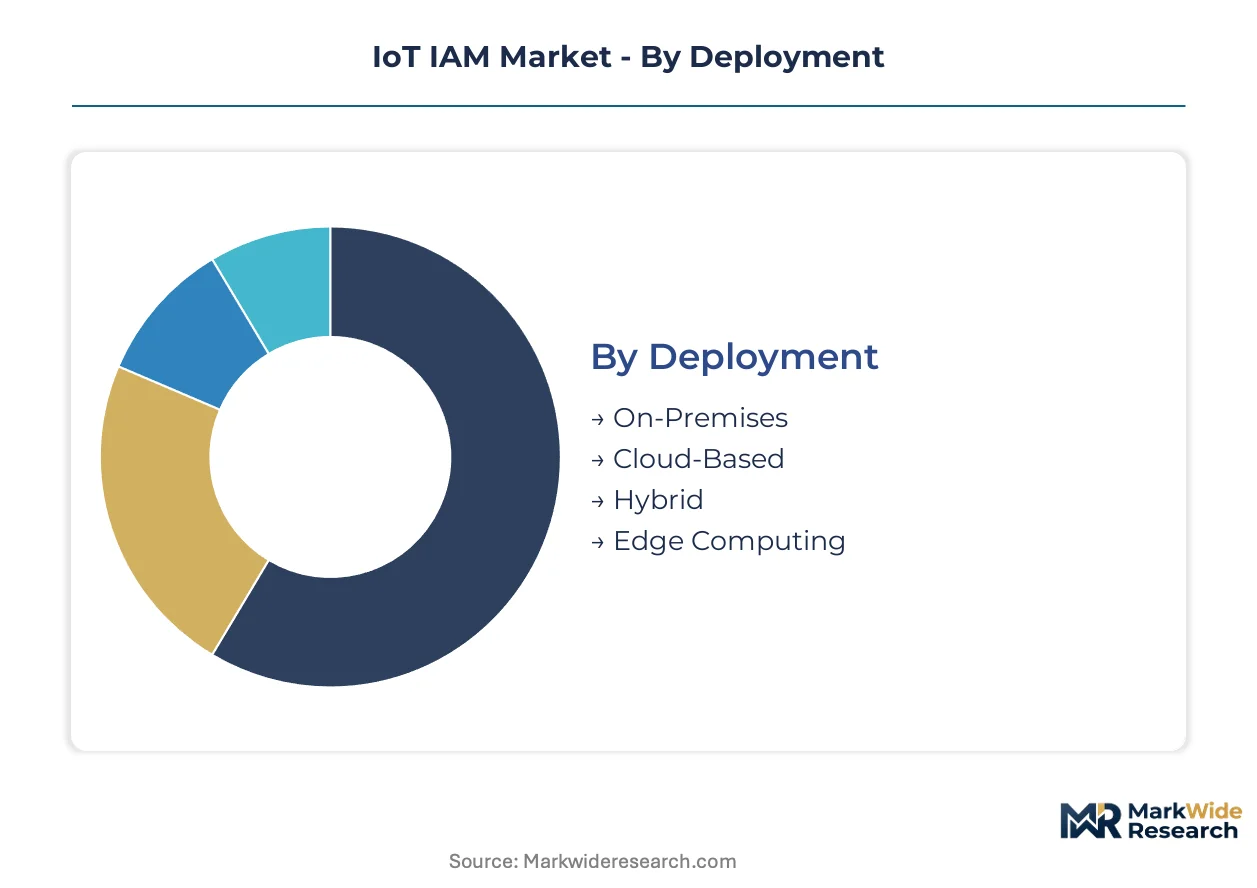
Segmentation in IoT IAM determines procurement pathways, margin structures, and compliance obligations. Deployment configuration dictates capital intensity and regulatory audit frequency. Application verticals impose divergent latency, certification, and lifecycle requirements that reshape vendor specialization.
Deployment:
Regulatory differentiation between the EU AI Act and FDA requirements forces vendors to architect deployment modes with embedded audit trails or risk disqualification from regulated procurement pipelines.
- Cloud-Based:Multi-tenant architectures with automated certificate rotation dominate new contract value. German automotive OEMs and US hospital systems are consolidating procurement around vendors offering ISO 27001-aligned SOC 2 Type II attestations with continuous monitoring dashboards.
- Edge Computing:On-device credential storage and local authentication decisions eliminate cloud round-trip latency. Stuttgart industrial automation clusters and Detroit automotive testing facilities are driving configurations that process mutual TLS handshakes within 50ms for safety-critical robotics.
- On-Premises:Air-gapped certificate authorities serve defense and critical infrastructure operators with sovereign data requirements.
- Hybrid:Split-credential architectures bridge legacy SCADA with cloud-native IAM stacks in brownfield manufacturing sites.
Cloud-Based deployment handles the majority of throughput; Edge Computing is the fastest mover on share.
Application:
Cost tier stratification separates premium-certified healthcare implementations from volume-driven smart home deployments with divergent margin profiles and renewal economics.
- Industrial Automation:Hardware security module integration and IEC 62443 certification dominate procurement specifications. Munich machinery manufacturers require firmware signing with FIPS 140-2 Level 3 HSMs for every programmable logic controller update.
- Healthcare Systems:FDA-mandated identity chains for connected medical devices demand HIPAA-compliant audit logging with 7-year retention. US hospital procurement teams now require 24/7 certificate lifecycle management as a contractual minimum.
- Smart Home:MQTT and CoAP protocol standardization enables mass-market cloud IAM at price points below enterprise tiers.
- Automotive Solutions:UNECE R155 cybersecurity regulation compliance is mandatory for vehicle type approval across EU member states.
Industrial Automation captures the highest contract values; Healthcare Systems is climbing the fastest as FDA enforcement intensifies.
End User:
Customer type determines service model preference, with large enterprises demanding managed services while government agencies prioritize sovereign infrastructure with domestic certificate authorities.
- Large Enterprises:Global manufacturing conglomerates and healthcare networks are consolidating multi-site IAM under single-vendor managed services contracts with SLA-backed certificate availability guarantees above 99.99%.
- Government Agencies:Defense and critical infrastructure operators mandate on-premises or sovereign cloud deployments with national certificate authority root trust.
- Small & Medium Enterprises:Subscription-based SaaS IAM with pre-configured compliance templates reduces implementation timelines from months to weeks.
- Third-Party Providers:Managed security service providers white-label IAM platforms to deliver multi-tenant identity services across fragmented client bases.
Large Enterprises dominate absolute spend; Third-Party Providers are expanding most quickly as channel intermediation accelerates.
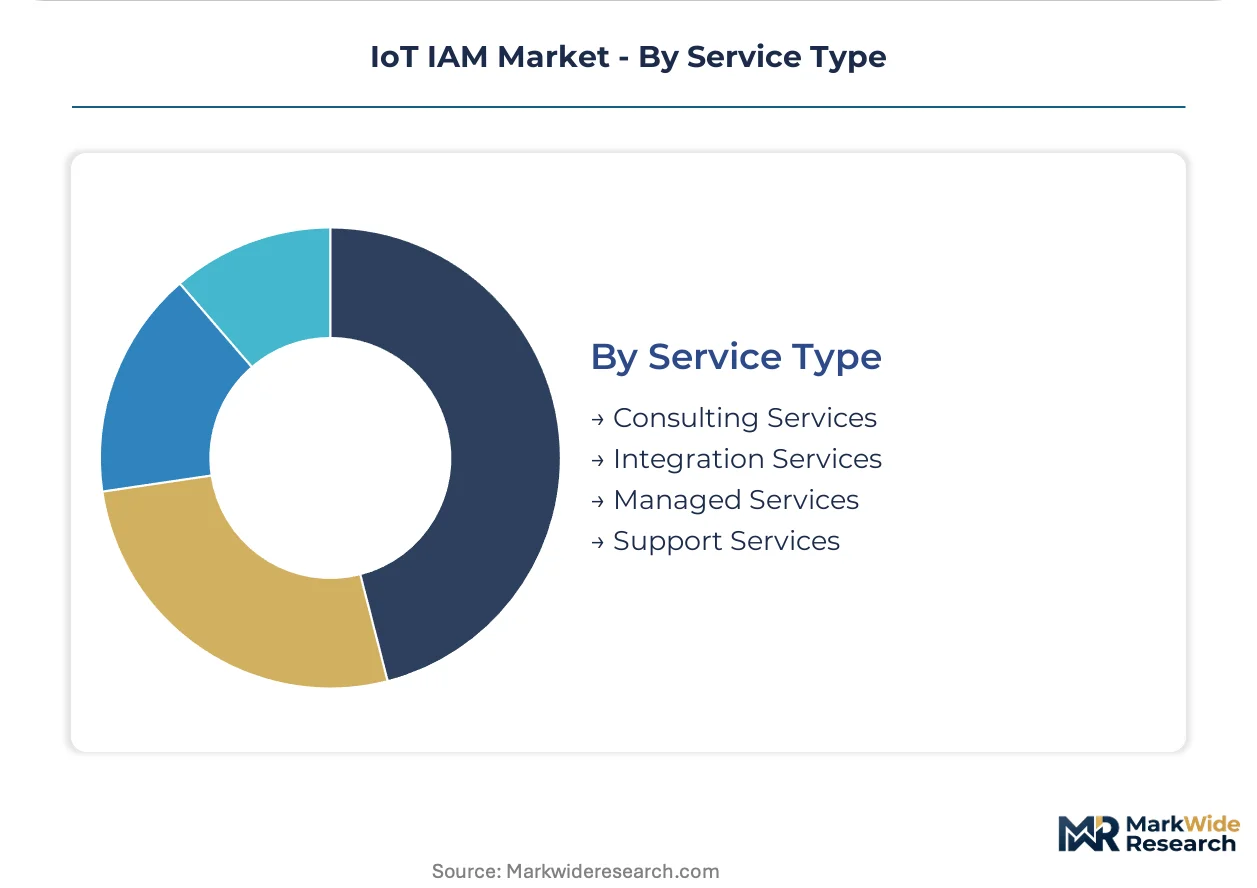
Service Type:
Margin concentration favors recurring revenue streams over project-based delivery, with managed services capturing disproportionate lifetime value through operational complexity lock-in.
- Managed Services:24/7 certificate lifecycle management, automated revocation, and compliance reporting are displacing perpetual licenses. Energy and healthcare verticals now require dedicated security operations center integration with 15-minute incident response SLAs.
- Integration Services:Custom middleware development for legacy SCADA and Modbus bridging commands premium day rates but finite project duration.
- Consulting Services:Zero-trust architecture design and PKI infrastructure planning support initial deployment decisions.
- Support Services:Break-fix and tiered helpdesk offerings anchor maintenance renewal negotiations.
Managed Services commands the highest recurring margins; Integration Services sees the steepest expansion trajectory as brownfield complexity mounts.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Government cybersecurity mandates and industrial automation incentives are reshaping procurement patterns across major economies. The EU AI Act and NIS2 Directive compress vendor qualification timelines in Europe. Asia-Pacific markets leverage domestic manufacturing programs to localize certificate authority infrastructure.
United States
FDA-mandated identity chains for connected medical devices drive healthcare IoT IAM spending. HIPAA audit frequency has doubled since 2023, compelling hospital procurement teams to require 24/7 certificate lifecycle management. The Boston-Cambridge medical technology cluster anchors demand for managed service providers with SOC 2 Type II attestations.
Germany
Industrial automation concentration in Stuttgart and Munich generates demand for edge-computing IAM configurations with sub-50ms latency. The EU AI Act's risk classification system mandates auditable identity chains for high-risk connected infrastructure. Bavarian machinery manufacturers embed hardware security modules directly into servo drives and programmable logic controllers.
China
Domestic electronics manufacturing scale drives localized certificate authority infrastructure development. MIIT cybersecurity regulations for critical information infrastructure mandate mutual authentication for industrial IoT deployments. The Yangtze River Delta manufacturing belt concentrates demand for cloud-based IAM serving export-bound device ecosystems.
Japan
Automotive OEMs pilot blockchain-anchored device credentials for vehicle-to-everything networks. METI industrial cybersecurity guidelines accelerate zero-trust architecture adoption across manufacturing supply chains. The Nagoya-Toyota industrial corridor represents the primary concentration for edge-AI authentication in robotics applications.
India
The PLI scheme for domestic electronics manufacturing attracts IAM providers to establish localized certificate authority infrastructure. BIS standards for IoT device security create compliance-driven procurement cycles for industrial deployments. Karnataka's Bangalore-Tumkur electronics manufacturing cluster anchors initial enterprise-grade implementations.
IoT IAM Market Competitive Environment
Listed leaders compete with private specialists across cloud infrastructure and hardware security dimensions. The vendor base organizes into three tiers: hyperscale cloud platforms with identity-as-a-service offerings, industrial specialists with hardware security module integration, and managed service providers with vertical-specific compliance expertise. Strategic moves concentrate on embedding continuous compliance validation into product architectures and expanding managed service portfolios to capture recurring revenue pools.
Within the hyperscale tier, Microsoft and AWS exemplify cloud-native deployment models that consolidate multi-tenant IAM under automated certificate rotation. Thales occupies a position as the hardware security module anchor for regulated verticals requiring FIPS 140-2 Level 3 certification. IBM represents the hybrid-environment specialist bridging on-premises legacy systems with cloud-native stacks through managed identity services.
| Leading Market Players |
|---|
| AWS |
| Thales |
| IBM |
| Microsoft |
| Cisco Systems |
| Oracle |
| Broadcom |
| Entrust |
| HID Global |
| Others |
Value Chain & Pricing Dynamics
Multi-tenant cloud infrastructure amortization across hyperscale data centers compresses marginal delivery costs for IAM vendors, concentrating pricing power among platforms with sufficient scale to absorb certificate lifecycle management overhead while forcing smaller competitors toward narrow vertical specialization or exit.
Pricing Analysis
Certification level (FIPS 140-2/ISO 27001/GDPR-aligned) creates the primary spread between deployment tiers, with healthcare and automotive buyers absorbing 40-60% premiums for audit-ready compliance stacks against commoditized smart home SaaS subscriptions. Three-tier pricing structure across premium certified, standard enterprise, and economy volume tiers dominates contract structures. Pricing pressure stems from AWS and Microsoft absorbing certificate rotation costs into broader cloud consumption bundles, compressing standalone IAM vendor margins. Small and medium enterprises exhibit highest price sensitivity, while German automotive OEMs and US hospital systems prioritize compliance guarantees over unit cost.
Supply Chain Analysis
Strategic stockpiling of FIPS 140-2 certified hardware security modules dominates procurement behavior among industrial automation vendors, with 12-18 month lead times for Thales and Entrust HSMs forcing advance capacity commitments. Hardware security module fabrication concentrates in France, the United States, and Germany; cloud certificate authority infrastructure anchors in Ireland, Singapore, and Virginia. Supply chain risk centers on single-source dependency for tamper-resistant cryptographic processors subject to export control classification. Distribution runs through direct enterprise sales for regulated verticals and hyperscaler marketplaces for cloud-native deployments.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The EU AI Act's risk classification mandate for connected infrastructure creates a regulatory inflection that rewards vendors embedding continuous compliance validation, while punishing legacy architectures requiring retrofit.
For Market Incumbents: Consolidate managed service portfolios around 24/7 certificate lifecycle operations with SOC 2 Type II attestations, absorbing the talent scarcity threat in PKI engineering by centralizing expertise across multi-tenant platforms. Deepen backward integration into hardware security module supply through exclusive capacity agreements with Thales or Entrust, securing FIPS 140-2 Level 3 inventory against export restriction volatility. For New Entrants and Emerging Players: Managed PKI services for mid-market healthcare systems represent the most penetrable white space, where HIPAA audit frequency has doubled but incumbent pricing excludes regional hospital networks below 500 beds. India's PLI scheme electronics manufacturing clusters offer a geographic entry point with localized certificate authority infrastructure requirements for export-bound device ecosystems. Lead with pre-configured compliance templates reducing implementation timelines from months to weeks. For Investors and Strategic Acquirers: Mid-cycle technology positioning favors hybrid-environment specialists bridging on-premises legacy SCADA with cloud-native IAM stacks, capturing brownfield manufacturing complexity that hyperscale platforms under-serve. Acquisition targets should demonstrate vertical-specific compliance expertise in FDA-mandated medical devices or UNECE R155 automotive cybersecurity. The signal to watch is FDA enforcement intensity against connected medical device identity chain gaps, which would accelerate healthcare IAM procurement cycles.| Strategic Initiative | Industry Significance |
|---|---|
| Continuous Compliance Platform Integration | EU AI Act audit mandates disqualify vendors without embedded validation, reshaping RFP pipelines. |
| Edge-AI Authentication Development | Federated learning with on-device biometric verification opens automotive and robotics segments. |
| Hardware Security Module Supply Anchoring | FIPS 140-2 Level 3 certification concentration in Thales and Entrust creates single-source vulnerability. |
| Managed Service Portfolio Expansion | Recurring operational complexity in certificate lifecycle management exceeds in-house enterprise capability. |
| Blockchain-Anchored Credential Piloting | German and Japanese automotive OEMs test decentralized identity eliminating single points of failure. |
Study Parameters
Findings reconcile primary fieldwork against secondary review of regulatory filings, hyperscaler capex disclosures, and hospital procurement databases, combining structured interviews with CISOs, IAM platform engineers, and healthcare GPO contracts managers with validation through FDA 510(k) submissions, EU AI Act implementation guidance, and ISO 27001 certification registries. Bottom-up deployment configuration modeling triangulates against top-down enterprise IT spending patterns.
Segmentation dimensions modeled span deployment mode (cloud, edge, on-premises, hybrid), application vertical (industrial automation, healthcare, smart home, automotive), end-user archetype (large enterprise, government, SME, third-party provider), and service type (managed, integration, consulting, support). CAGRs derive from regression analysis of contract value trajectories across the projection horizon, incorporating TLS 1.3 adoption curves, hardware security module cost trajectories, and regulatory enforcement intensity as industry-specific inputs.
Underlying assumptions cover sustained EU AI Act and NIS2 Directive enforcement continuity, with deviation risk concentrated in regulatory fragmentation between Brussels and Washington forcing parallel product builds. Revision becomes warranted when FDA identity chain mandates for medical devices cross enforcement thresholds triggering hospital procurement acceleration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Internet of Things (IoT)
LAMEA Bluetooth 5.0 Market
Internet of Things (IoT)
Internet of Things (IoT) in Manufacturing Market
Internet of Things (IoT)
IoT Connected Machines Market
Internet of Things (IoT)
Global Military IoT Market
Internet of Things (IoT)
IoT Cloud Platform Market
Internet of Things (IoT)
Industrial Internet of Things (Iiot) Market
Internet of Things (IoT)
Smart Remote Market
Internet of Things (IoT)
North America Internet of Things Devices Market
Internet of Things (IoT)
Wireless Smart Plug Market
Internet of Things (IoT)
Bluetooth Smart Plugs Market
Internet of Things (IoT)
IIOT Gateway for Utility Market
Internet of Things (IoT)
Narrowband-Internet of Things (NB-IoT) Market
Internet of Things (IoT)
IoT Application Development Services Market
Internet of Things (IoT)
IoT Gateway Devices Market
Internet of Things (IoT)
Smart Pool Systems Market
Internet of Things (IoT)
Global IoT Devices Market