
 North America Software Defined Perimeter Market | 2026-2036
North America Software Defined Perimeter Market Size, Share, and Industry Trends Forecast 2026-2036
North America Software Defined Perimeter Market Analytics
Modular SDP bundling is decoupling network security from hardware-centric procurement cycles. Palo Alto Networks leverages cloud-native delivery to sustain recurring revenue streams across federal and commercial accounts. Cisco Systems anchors its position through deep integration with existing enterprise switching infrastructure, while Fortinet competes aggressively on price-performance metrics in mid-market deployments.
A Software Defined Perimeter is a security architecture that dynamically creates one-to-one network connections between users and resources, employing micro-segmentation and identity verification before any access is granted. The framework replaces traditional perimeter-based defenses with policy-driven, encrypted tunnels that authenticate both device and user posture in real time. Cloud deployment configurations now capture the fastest expansion trajectory as organizations retire on-premises VPN concentrators. Zero Trust technology leads solution positioning, though managed service wrappers around hybrid deployments are emerging as the stickiest margin pool for channel partners.
CISA zero-trust directives and OMB memoranda M-22-09 are reshaping federal procurement requirements across the United States, Canada, and Mexico. NIST SP 800-207 provides the technical baseline that vendors must satisfy for government eligibility, while state-level privacy frameworks in California and Texas add compliance layers for multi-jurisdictional operators. Stakeholders must track how FedRAMP authorization timelines and cross-border data localization rules in Canadian provincial jurisdictions alter vendor qualification costs and deployment architectures.
Market Dynamics
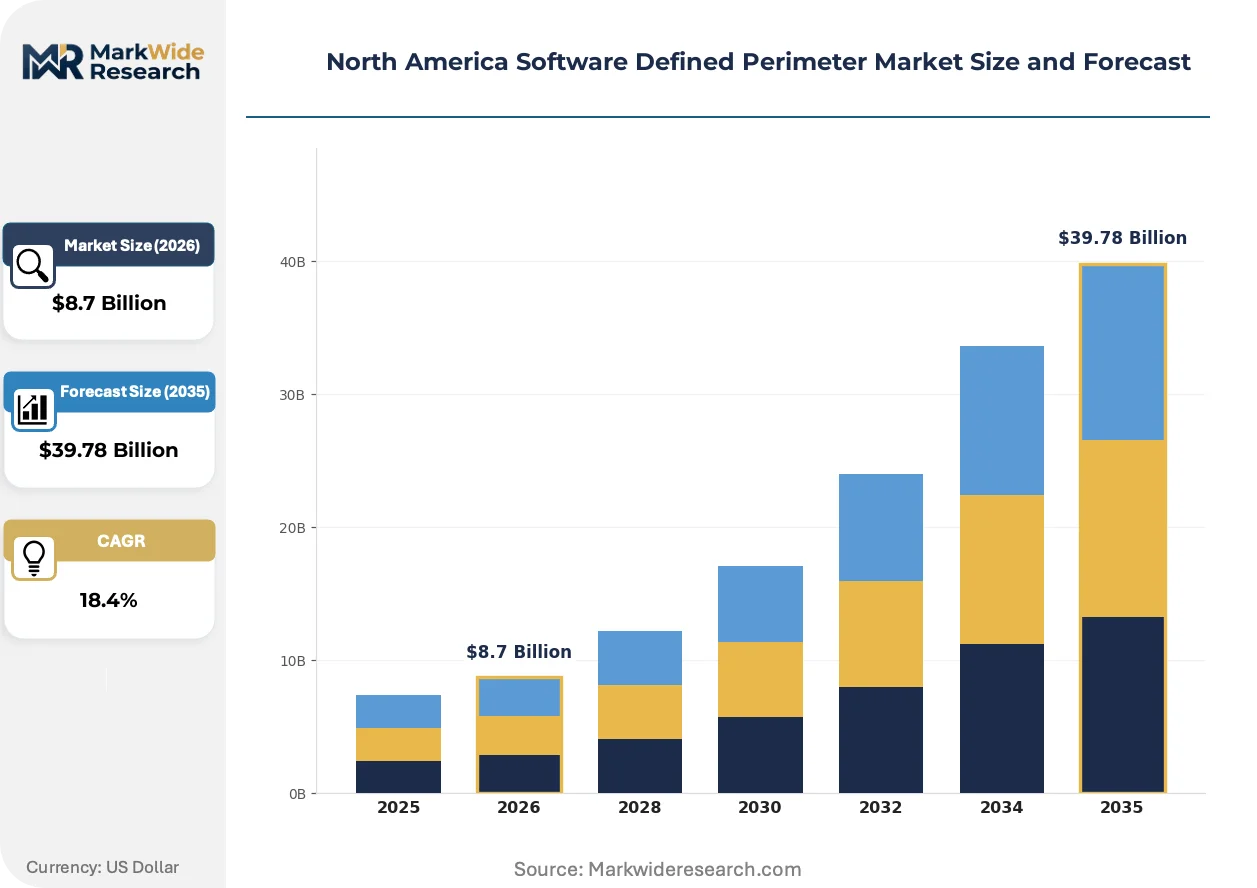
Zero-trust mandates from CISA and OMB are compressing federal procurement cycles and forcing identity-centric access architectures into defense, financial services, and critical infrastructure operators across the United States, Canada, and Mexico.
Growth Catalysts
- OMB Memorandum M-22-09:Federal agencies must achieve zero-trust architecture by fiscal year 2024, creating immediate demand for SDP solutions that replace legacy VPN infrastructure.
- Micro-segmentation:Healthcare and energy sector operators deploy SDP frameworks to isolate critical workloads and contain lateral movement during ransomware incidents.
- California CCPA and CPRA:State-level privacy mandates drive financial institutions and technology firms toward identity-verified access models that demonstrate data governance compliance.
Market Restraints
- FedRAMP authorization timelines:Vendor qualification periods extending 12-18 months delay market entry for emerging SDP providers seeking federal contracts.
- Legacy identity provider concentration:Deep integration dependencies with established directory services create switching friction and prolong hybrid deployment phases.
- Cross-border data localization:Canadian provincial regulations and Mexican data sovereignty requirements fragment cloud architecture standardization for multi-national deployments.
Strategic Opportunities
- Managed security service providers:Channel partners bundle SDP with SOC-as-a-service offerings, capturing recurring revenue from mid-market enterprises lacking internal zero-trance expertise.
- Operational technology convergence:SDP architectures extend into industrial control systems, securing remote access to SCADA and distributed energy resources without traditional network perimeter exposure.
- Texas and Virginia state procurement:Sub-federal government entities accelerate zero-trust adoption with simplified acquisition vehicles that bypass federal authorization complexity.
Industry Challenges
- Zero-trust architecture expertise:Shortage of engineers proficient in NIST SP 800-207 implementation creates deployment bottlenecks and quality variation across integrator networks.
- Certificate lifecycle management:Device posture verification at scale demands automated PKI infrastructure that many organizations lack, forcing manual intervention and access latency.
- Multi-cloud policy orchestration:Consistent access control across AWS GovCloud, Azure Government, and private data centers requires abstraction layers that increase architectural complexity.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | North America Software Defined Perimeter Market |
| Market Size in 2026 | $8.7 Billion |
| Market Size in 2035 | $39.78 Billion |
| CAGR (2026 – 2036) | 18.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premises, Cloud, Hybrid, Managed Service Solution: Access Control, Threat Detection, Identity Management, Policy Enforcement End User: Healthcare, Education, Financial Services, Government Technology: Zero Trust, VPN, Multi-Factor Authentication, Encryption |
| Companies Covered | Palo Alto Networks, Inc., Cisco Systems, Inc., Fortinet, Inc., Zscaler, Inc., Check Point Software Technologies Ltd., Akamai Technologies, Inc., Broadcom Inc., Verizon, Inc., Intel Corporation, Others |
| Regions Covered | North America: US, Canada, Mexico |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
North America Software Defined Perimeter Market Evolving Landscape
Identity-centric security architectures are displacing hardware-bound perimeter defenses, with cloud-native delivery models and continuous authentication protocols redefining how organizations provision and monitor network access across distributed workforces and operational environments.
Software-defined perimeter platforms are decentralizing trust enforcement from centralized VPN concentrators to distributed policy decision points embedded at the application layer. Defense contractors and classified program offices adopt these architectures fastest, driven by CMMC 2.0 compliance deadlines. The shift is compressing hardware procurement cycles and redirecting capital toward subscription-based access orchestration.
CISA zero-trust maturity model directives and NIST SP 800-207 implementation guidance are reshaping vendor qualification requirements for federal contracts. Commercial enterprises in regulated sectors mirror these standards to preempt cyber insurance exclusions and demonstrate security posture to boards. Financial services firms in New York and Chicago align SDP deployments with NYDFS cybersecurity regulations and FFIEC examination priorities.
Security procurement is consolidating around outcome-based service contracts that bundle SDP technology with continuous monitoring and threat response. Mid-market enterprises displace point-product purchasing through managed security service providers offering guaranteed uptime and breach containment SLAs. This pattern concentrates most visibly in Texas energy sector and California technology verticals where internal security team scale lags threat environment complexity.
North America Software Defined Perimeter Market Segmentation
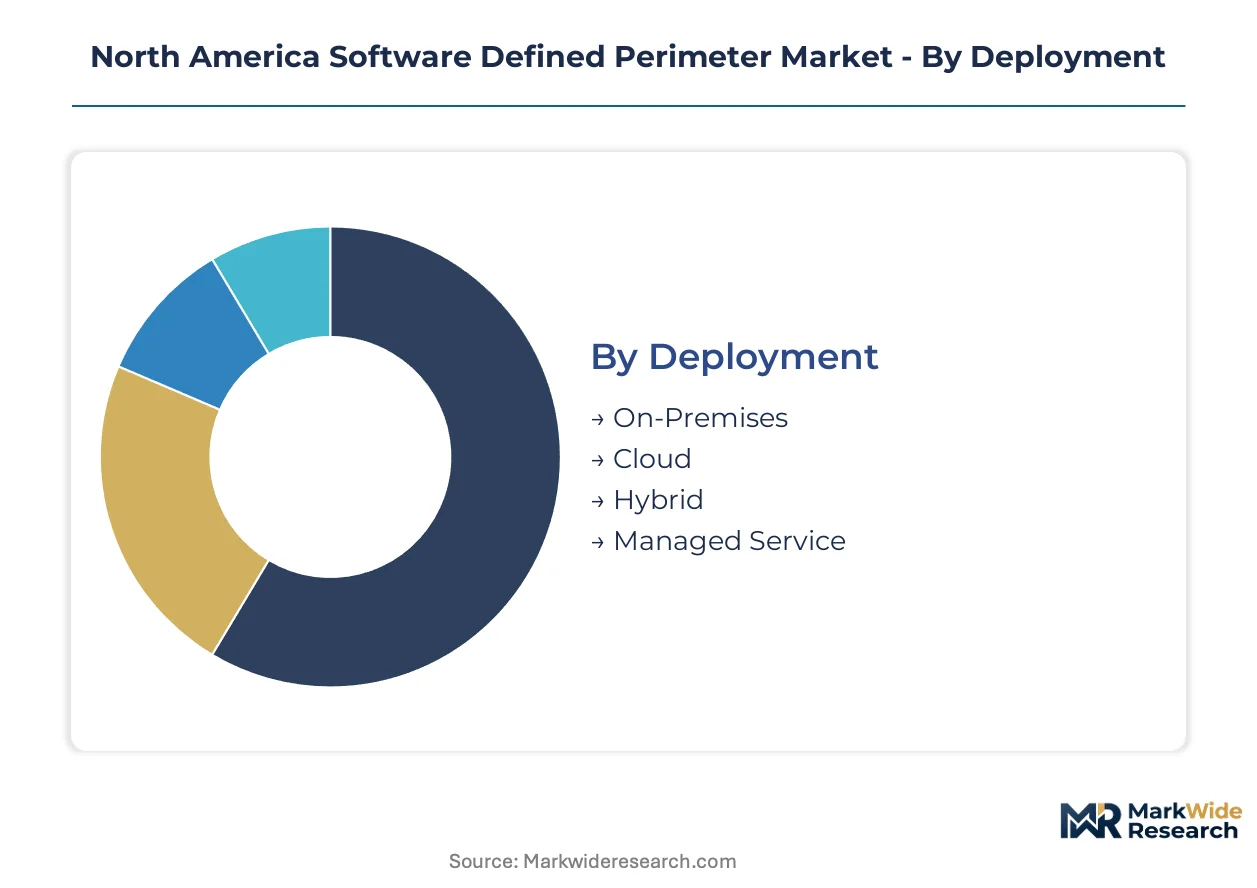
SDP segmentation reveals how procurement priorities diverge across infrastructure maturity levels and compliance postures. Organizations map deployment models to existing identity investments, while technology choices reflect zero-trust readiness and legacy system constraints.
Deployment:
Standardization dominates at the infrastructure layer, though customization intensity rises with regulatory complexity and data sovereignty requirements.
- Cloud:Cloud-native delivery eliminates hardware procurement cycles and enables elastic capacity for seasonal workload spikes. Federal agencies in Virginia and Texas prioritize FedRAMP-authorized cloud configurations to satisfy OMB M-22-09 mandates without capital expenditure.
- Managed Service:Third-party operation transfers certificate lifecycle management and policy orchestration to specialized providers. Mid-market financial institutions in California adopt managed wrappers to address NIST SP 800-207 compliance gaps without internal zero-trust engineering depth.
- On-Premises:Air-gapped installations serve classified program offices and defense contractors with CMMC 2.0 obligations.
- Hybrid:Split architectures accommodate legacy mainframe connectivity while modernizing user-facing access layers.
Leading the category by volume: Cloud. Growing fastest: Managed Service.
Solution:
Functional modules align with customer security operations maturity, from basic access gating through automated threat response integration.
- Access Control:Dynamic tunnel creation based on device posture and user identity replaces static network segmentation. Healthcare systems in Texas deploy access control modules to isolate electronic health record environments from guest and vendor networks.
- Identity Management:Continuous authentication chains bind user verification to resource requests throughout session lifecycles. State government entities in California integrate identity management with CCPA data governance workflows to demonstrate access auditability.
- Threat Detection:Behavioral analytics identify anomalous access patterns for automated policy adjustment.
- Policy Enforcement:Distributed decision points execute access rules at application edges rather than network perimeters.
Identity Management claims the largest revenue share. Access Control shows the steepest expansion trajectory as organizations retire VPN concentrators.
End User:
Sector-specific compliance regimes reshape solution packaging, with federal procurement vehicles setting technical baselines that commercial regulated industries mirror.
- Government:CISA zero-trust maturity model compliance drives standardized deployment architectures across civilian and defense agencies. Federal contracts in Virginia concentrate procurement among vendors with active FedRAMP authorizations and NIST SP 800-207 implementation experience.
- Financial Services:NYDFS cybersecurity regulations and FFIEC examination priorities mandate identity-verified access models. Banking operators in New York and Chicago deploy SDP frameworks to preempt cyber insurance exclusions and satisfy board risk oversight requirements.
- Healthcare:HIPAA security rule enforcement and ransomware containment priorities accelerate micro-segmentation adoption.
- Education:Distributed campus networks and research collaboration requirements create demand for scalable remote access without perimeter appliance proliferation.
Government verticals dominate current procurement volume. Healthcare is climbing the fastest as ransomware incident frequency forces workload isolation investments.
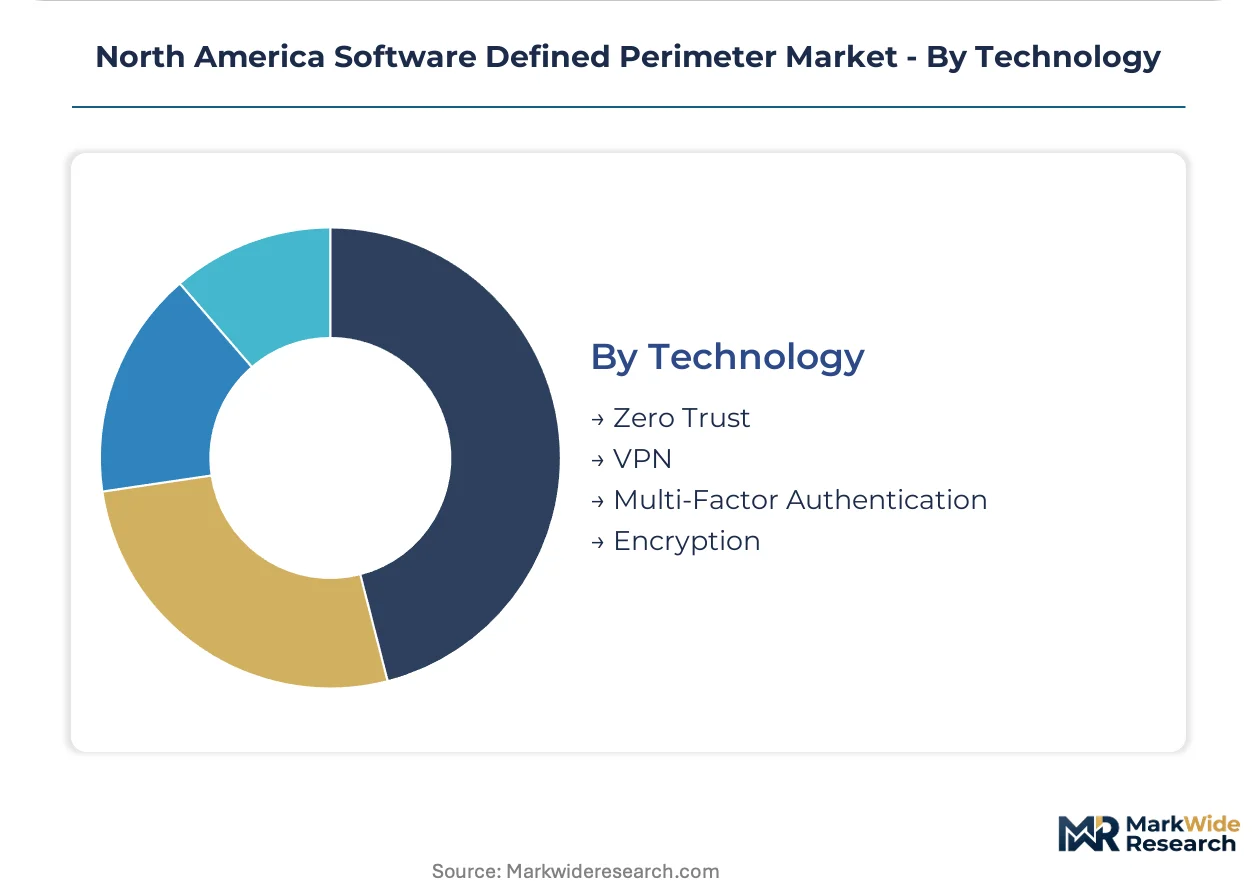
Technology:
Architectural choices reflect migration stage from perimeter-based trust models to continuous verification frameworks.
- Zero Trust:Identity-centric security architecture eliminates implicit trust based on network location and verifies every access request. Defense contractors across California, Texas, and Virginia accelerate zero-trust adoption ahead of CMMC 2.0 assessment deadlines.
- Multi-Factor Authentication:Step-up authentication chains bind possession and inherence factors to high-risk resource access. Financial services firms in Chicago integrate MFA with real-time transaction risk scoring to satisfy FFIEC authentication guidance.
- VPN:Legacy tunnel protocols persist in hybrid deployments during phased migration periods.
- Encryption:Certificate-based transport security underlies all SDP communications regardless of overlay technology.
Zero Trust technology anchors the largest deployment base. Multi-Factor Authentication is gaining share fastest as organizations harden access workflows against credential compromise.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The United States generates the dominant share of SDP consumption across North America, while Canada and Mexico exhibit concentrated demand in specific verticals. Procurement patterns diverge sharply between federal-mandated zero-trust deployments and commercial sector risk management priorities.
United States
Civilian and defense agencies drive volume through CISA zero-trust maturity model compliance deadlines. OMB Memorandum M-22-09 mandates federal architecture transformation by fiscal year 2024. Virginia's concentration of defense contractors and Texas energy sector operators anchor the fastest procurement cycles.
California
Technology firms and financial institutions deploy identity-verified access models to satisfy CCPA and CPRA data governance requirements. State privacy mandates create compliance-driven procurement distinct from federal security directives. The San Francisco Bay Area and Los Angeles metropolitan clusters concentrate vendor qualification activity for cloud-native SDP configurations.
Texas
Energy sector operators and state government entities accelerate zero-trust adoption through simplified acquisition vehicles. Critical infrastructure protection priorities and ransomware containment drive micro-segmentation investments. Dallas-Fort Worth and Houston anchor deployment concentration for operational technology convergence.
Canada
Federal agencies mirror NIST SP 800-207 implementation guidance while navigating provincial data localization requirements. Cross-border data sovereignty rules fragment cloud architecture standardization for multi-national deployments. Ontario and Quebec concentrate procurement among vendors with Health Canada and PMRA-aligned security frameworks.
Mexico
Financial services and manufacturing verticals adopt SDP frameworks to secure cross-border supply chain connectivity. National data sovereignty requirements shape deployment architecture decisions for international operators. Mexico City metropolitan area and Nuevo León industrial corridor anchor commercial sector adoption.
North America Software Defined Perimeter Market Competitive Landscape
The competitive structure tilts toward platform-centric incumbents with established federal authorization pathways. Three archetypes dominate: cloud-native specialists with subscription delivery models, infrastructure incumbents leveraging switching integration, and telecommunications carriers bundling SDP with managed security services. Consolidation pressure intensifies through strategic partnerships and technology licensing arrangements rather than capacity expansion.
Within the platform-centric tier, Palo Alto Networks and Cisco Systems occupy positions reflecting divergent go-to-market strategies. Zscaler represents the cloud-native delivery archetype with recurring revenue concentration. Fortinet exemplifies price-performance positioning in mid-market verticals. These three anchors illustrate how vendor qualification timelines and FedRAMP authorization status create structural barriers for emerging competitors.
| Leading Market Players |
|---|
| Palo Alto Networks, Inc. |
| Cisco Systems, Inc. |
| Fortinet, Inc. |
| Zscaler, Inc. |
| Check Point Software Technologies Ltd. |
| Akamai Technologies, Inc. |
| Broadcom Inc. |
| Verizon, Inc. |
| Intel Corporation |
| Others |
Value Network & Pricing Analysis
CISA zero-trust maturity model compliance gates both qualified supply and premium-tier pricing access, as FedRAMP authorization timelines stretch 12-18 months and concentrate procurement among pre-cleared vendors. This regulatory bottleneck compresses hardware-centric margins while elevating subscription-based cloud-native delivery premiums across federal and commercial accounts.
Pricing Analysis
Margin tightening in mid-market deployments reflects aggressive price-performance positioning by infrastructure incumbents competing against cloud-native specialists. Subscription-based SaaS pricing dominates federal and enterprise tiers, while managed service wrappers capture stickiest recurring revenue. Price differentiation hinges on FedRAMP authorization status and NIST SP 800-207 implementation depth. Cost-down pressure on on-premises configurations accelerates as agencies retire VPN concentrators for elastic cloud capacity. State government entities in Texas and Virginia show highest price sensitivity, while defense contractors with CMMC 2.0 deadlines accept premium tiers for accelerated deployment.
Supply Chain Analysis
Engineer shortages in California, Texas, and Virginia constrain zero-trust architecture implementation capacity and extend project timelines. Software development concentrates in the United States, with cloud infrastructure sourcing from domestic FedRAMP-authorized regions and Canadian data centers for provincial localization compliance. Raw material dependencies center on cryptographic hardware modules, commercial cloud compute, and specialized identity verification silicon. Single-source vulnerability in FedRAMP authorization consulting creates bottlenecks for emerging vendors. Distribution runs through channel partners bundling SDP with SOC-as-a-service offerings, particularly in mid-market energy and healthcare verticals.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
FedRAMP authorization backlog creates supply-constrained vendor qualification, propping pricing premiums for pre-cleared providers across federal procurement cycles.
For Market Incumbents: Lock in federal channel control by deepening integration with existing enterprise switching infrastructure and accelerating CMMC 2.0-aligned certification investments. Consolidate position through exclusive managed security service partnerships that bundle SDP with continuous monitoring SLAs, neutralizing cloud-native entrants lacking authorization depth. For New Entrants and Emerging Players: Launch via Texas and Virginia state procurement vehicles that bypass federal authorization complexity, targeting energy sector operational technology convergence with simplified acquisition paths. Penetrate mid-market healthcare micro-segmentation demand where internal zero-trust engineering gaps create managed service attachment opportunities. For Investors and Strategic Acquirers: FedRAMP authorization timeline compression is the leading indicator that vendor qualification scarcity will concentrate M&A premiums among pre-cleared assets. Long-term viability centers on platform-centric recurring revenue models with federal sticky-ness. Target acquisition archetype: cloud-native specialists with active authorization status and NIST SP 800-207 implementation track records. Watch CISA zero-trust maturity model enforcement acceleration as inflection signal.| Strategic Initiative | Industry Significance |
|---|---|
| FedRAMP Authorization Acceleration | Compresses 12-18 month qualification timelines to capture federal procurement windows ahead of OMB M-22-09 deadlines. |
| Managed Security Service Bundling | Captures recurring revenue from mid-market enterprises lacking internal zero-trust engineering depth in Texas energy and California healthcare. |
| Operational Technology Convergence | Extends SDP architectures into industrial control systems securing remote SCADA access without traditional perimeter exposure. |
| State Procurement Vehicle Expansion | Bypasses federal authorization complexity through simplified acquisition paths in Texas and Virginia sub-federal entities. |
| Certificate Lifecycle Automation | Addresses PKI infrastructure gaps that force manual intervention and access latency at device posture verification scale. |
Research Methodology
SEC filings, hyperscaler capex disclosures, and federal procurement databases formed the secondary backbone, cross-referenced with primary interviews across CISOs, federal IT procurement officers, zero-trust integration specialists, and channel partners. Bottom-up and top-down triangulation validated deployment model splits and vertical adoption curves, with particular attention to FedRAMP authorization status and NIST SP 800-207 implementation maturity.
Bottom-up modeling anchored volume estimates to named federal agency zero-trust mandates and state-level privacy compliance deadlines, while top-down cross-checks applied macro spending ratios across defense, financial services, and critical infrastructure operators. Segmentation dimensions spanned deployment configuration, solution module, end-user vertical, and technology architecture across the projection horizon. CAGR derivation incorporated OMB M-22-09 fiscal year deadlines and CMMC 2.0 assessment timelines as demand pull factors.
Regulatory enforcement delays, FedRAMP authorization timeline extensions, and cross-border data localization rule changes are the dominant revision risks. Forecasts reflect assumptions around CISA zero-trust maturity model adoption velocity and cloud infrastructure capacity expansion. Material deviation in named triggers warrants pause and re-evaluation.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Operational Technology Security Market
Cybersecurity
Web Application Firewall Market
Cybersecurity
Cloud-Based Email Security Market
Cybersecurity
South Korea Cybersecurity Market
Cybersecurity
Finland Cybersecurity Market
Cybersecurity
Poland Cybersecurity Market
Cybersecurity
Global Mobile Data Protection Market
Cybersecurity
North America Data Exfiltration Market
Cybersecurity
Bahrain Cybersecurity Market
Cybersecurity
Enterprise Mobility Security Market
Cybersecurity
Deception Technology Market
Cybersecurity
Micro-Segmentation Solutions Market
Cybersecurity
Middle East Cybersecurity Market
Cybersecurity
Cybersecurity Mesh Market
Cybersecurity
Global Mobile Anti Malware Market
Cybersecurity
Global Dynamic Data Masking Market