
 SOC As a Service Market | 2026-2036
SOC As a Service Market Size, Share, and Industry Trends Forecast 2026-2036
SOC As a Service Market Intelligence
The shift to subscription-based, asset-light delivery models is tilting the competitive landscape away from capital-intensive, on-premise security infrastructure. This change favors providers with scalable cloud architectures and operational efficiencies. Palo Alto Networks leverages its cloud-native platform to offer flexible solutions for diverse client sizes. In contrast, IBM sustains its market position through integrated security services targeting large, complex enterprise environments that require extensive customization and support.
SOC as a Service provides outsourced cybersecurity operations, delivering 24/7 network monitoring, threat intelligence analysis, and log management through a subscription model. Its primary purpose is to give organizations access to expert security personnel and advanced tools without the overhead of an in-house SOC. Within solution offerings, threat detection and incident response form the core of most service agreements. Large enterprises continue to dominate consumption, but demand from small and medium enterprises is accelerating due to the model's cost-effectiveness.
Regulatory frameworks are a significant catalyst for market adoption. Europe's GDPR imposes strict data breach notification requirements, while the US HIPAA standard mandates robust security controls for protected health information, both driving demand for continuous monitoring services. Providers must now decide whether to specialize in specific compliance verticals or build broad, multi-regulation capabilities to serve a diverse client base.
Market Dynamics
The convergence of stringent data protection regulations and the escalating sophistication of cyber threats forms the central structural force shaping the SOC as a Service market. Mandates like Europe's GDPR and the US HIPAA framework create non-negotiable requirements for continuous monitoring.
Growth Catalysts
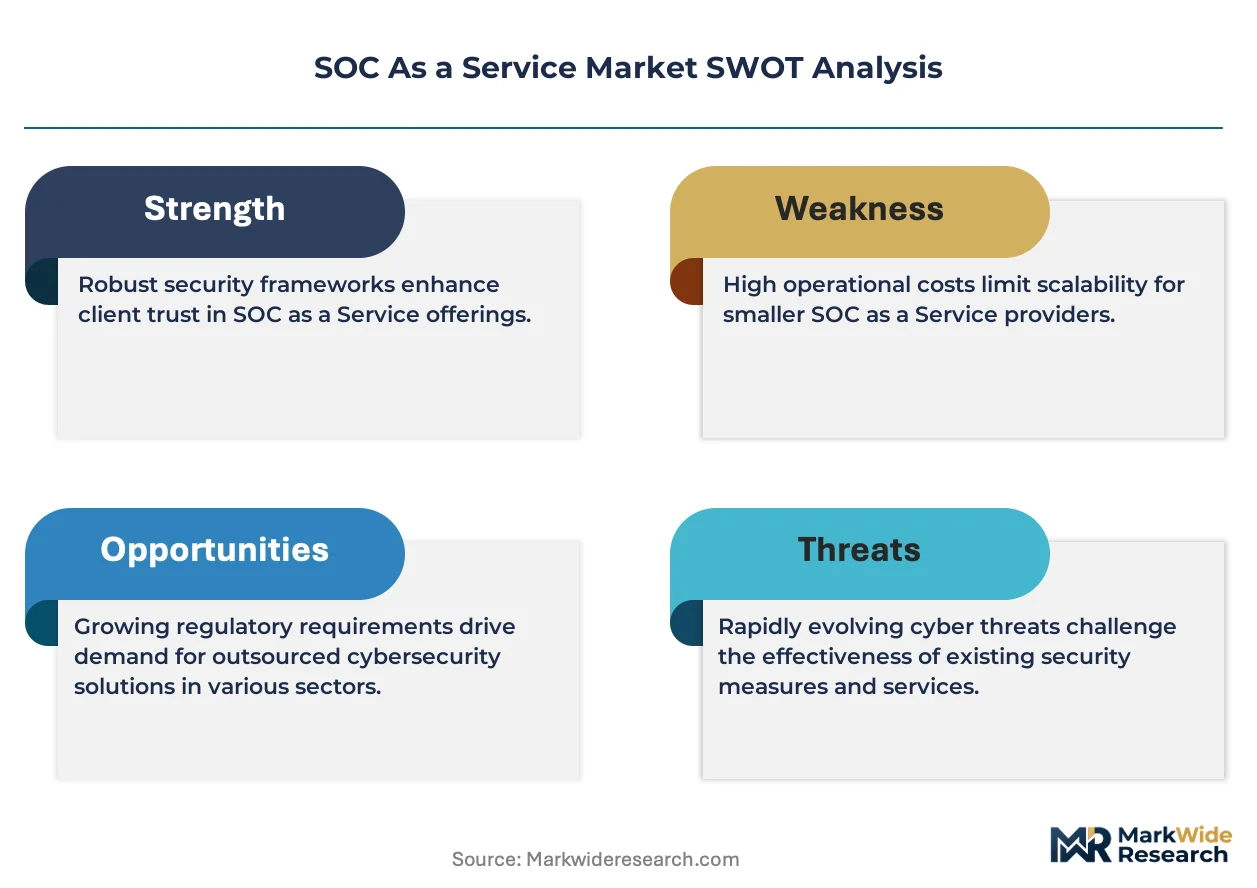
- Regulatory Compliance Mandates:Strict data breach notification rules under frameworks like Europe’s GDPR compel organizations to implement 24/7 monitoring capabilities, directly stimulating demand for outsourced security operations to ensure timely detection and reporting.
- Financial Sector Adoption:The banking and financial services industry is a primary adopter, leveraging SOC as a Service to secure sensitive customer financial data, protect against fraud, and comply with sector-specific cybersecurity regulations.
- Rising Threat Complexity:The proliferation of advanced persistent threats and complex ransomware attacks makes establishing and maintaining an effective in-house security operations center prohibitively expensive for many small and medium-sized enterprises.
Market Restraints
- High Service Costs:The premium cost associated with 24/7 expert monitoring and advanced security tooling can be a significant barrier for smaller businesses with limited cybersecurity budgets, restricting broader market penetration.
- Legacy System Integration:Providers face considerable difficulty integrating their modern, cloud-native platforms with the complex and often outdated legacy IT infrastructure prevalent in many large enterprises, causing implementation delays.
- Trust and Data Privacy Concerns:Handing over access to sensitive internal network data and logs to a third-party provider creates inherent concerns about data confidentiality and control, acting as a restraint for risk-averse organizations.
Strategic Opportunities
- Operational Technology Security:Extending services to secure Operational Technology (OT) and Industrial Control Systems (ICS) in the manufacturing, energy, and utilities sectors represents a significant growth vector as these environments become more connected.
- Expansion in Southeast Asia:Rapid digitalization within the e-commerce and fintech sectors across countries like Indonesia and Vietnam creates untapped demand for cybersecurity services where local expertise is scarce.
- Data Sovereignty Solutions:The rise of data residency laws in nations such as India and Brazil presents an opportunity for providers to establish in-country SOCs that help clients meet local data storage and processing requirements.
Industry Challenges
- Cybersecurity Talent Shortage:A persistent global shortage of skilled security analysts, threat hunters, and incident responders makes it difficult for service providers to scale their operations while maintaining a high quality of service.
- Alert Fatigue Management:A major operational hurdle is effectively managing the high volume of security alerts generated by disparate tools, which can lead to analyst burnout and the risk of missing genuine threats among the noise.
- Multi-Regulation Compliance:Providers serving a global clientele face the challenge of maintaining deep expertise and audit-readiness across an expanding array of international and industry-specific regulations, such as PCI DSS and ISO 27001.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | SOC As a Service Market |
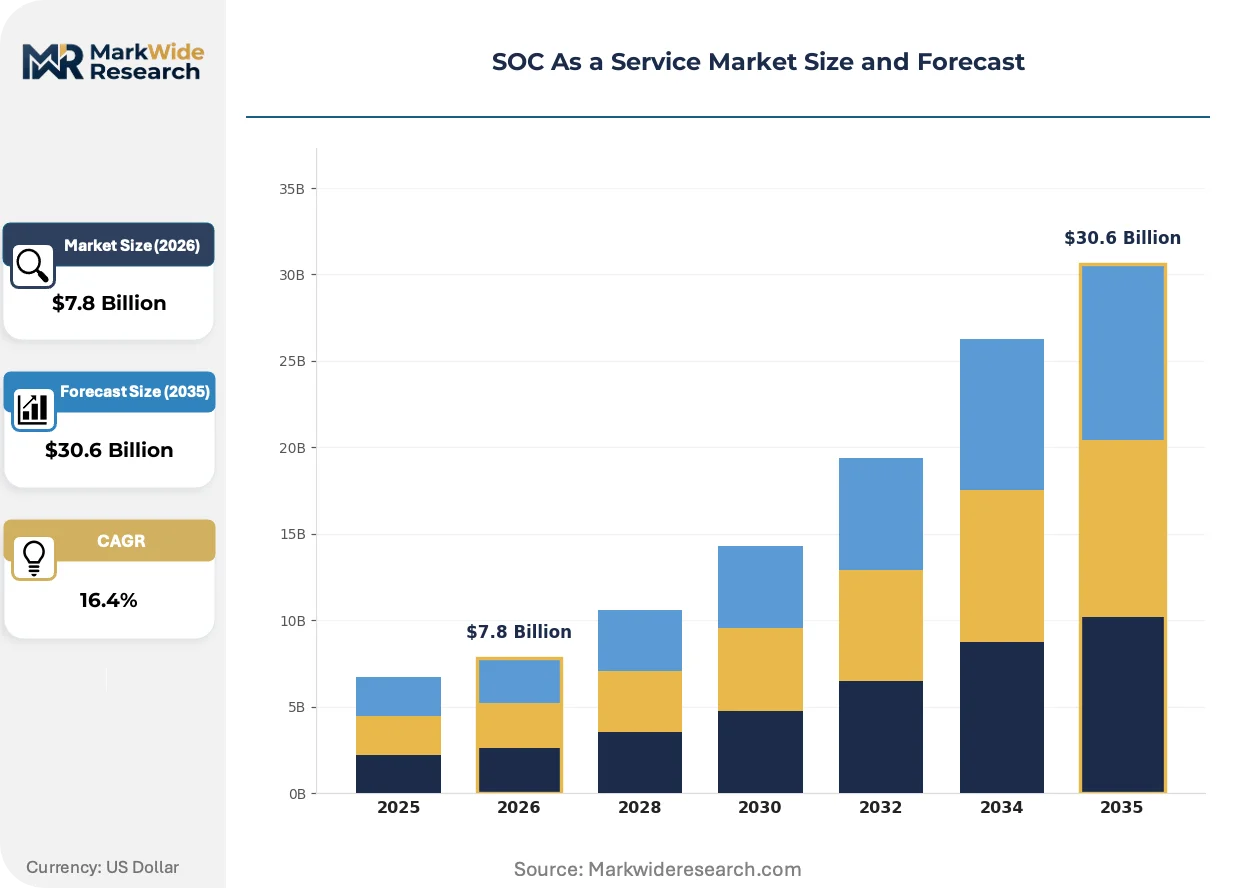
| Market Size in 2026 | $7.8 Billion |
| Market Size in 2035 | $30.6 Billion |
| CAGR (2026 – 2036) | 16.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment Model: Cloud-Based, On-Premise, Hybrid, Managed Service Solution Offering: Threat Detection, Incident Response, Vulnerability Management, Compliance Monitoring, Security Analytics Application Area: Financial Institutions, Telecommunications, Government Agencies, Retail Chains, Energy Providers End User Type: Large Enterprises, Small & Medium Enterprises, Managed Security Service Providers, IT Consultancies |
| Companies Covered | IBM, AT&T Cybersecurity, Arctic Wolf Networks, Palo Alto Networks, Cisco Systems, Check Point Software Technologies, Fortinet, Verizon, Cloudflare, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
SOC As a Service Market Strategic Shifts & Innovations
Automation and artificial intelligence are fundamentally altering the delivery of security operations, shifting the focus from reactive alert monitoring toward proactive, intelligence-driven threat hunting. This evolution is enabling providers to offer more effective and efficient protection against emerging cyber threats.
Extended Detection and Response (XDR) platforms integrate security telemetry from endpoints, cloud workloads, and network infrastructure. Large enterprises are increasingly adopting XDR to achieve a unified view of their security posture and break down data silos between security tools. This technology is hybridizing the traditional SOC model by enabling a collaborative environment where a provider's outsourced experts and a client's internal IT team can analyze threats using a common data platform.
Europe's Digital Operational Resilience Act (DORA) establishes strict requirements for ICT risk management and incident reporting across the financial sector. This directive forces financial entities to demonstrate robust capabilities for withstanding and recovering from significant cyber disruptions. The financial services segment is most impacted, increasing its reliance on SOCaaS providers that can deliver DORA-specific compliance validation, threat intelligence, and resilience testing services.
A co-managed delivery model is gaining significant traction, challenging the fully outsourced "black box" approach. This collaborative framework allows an organization’s internal security team to work directly with the provider’s analysts, sharing context and responsibilities. This consumption pattern is particularly evident in the technology and healthcare sectors in the United States, where organizations seek to retain visibility and control while augmenting their internal capabilities.
SOC As a Service Market Segmentation
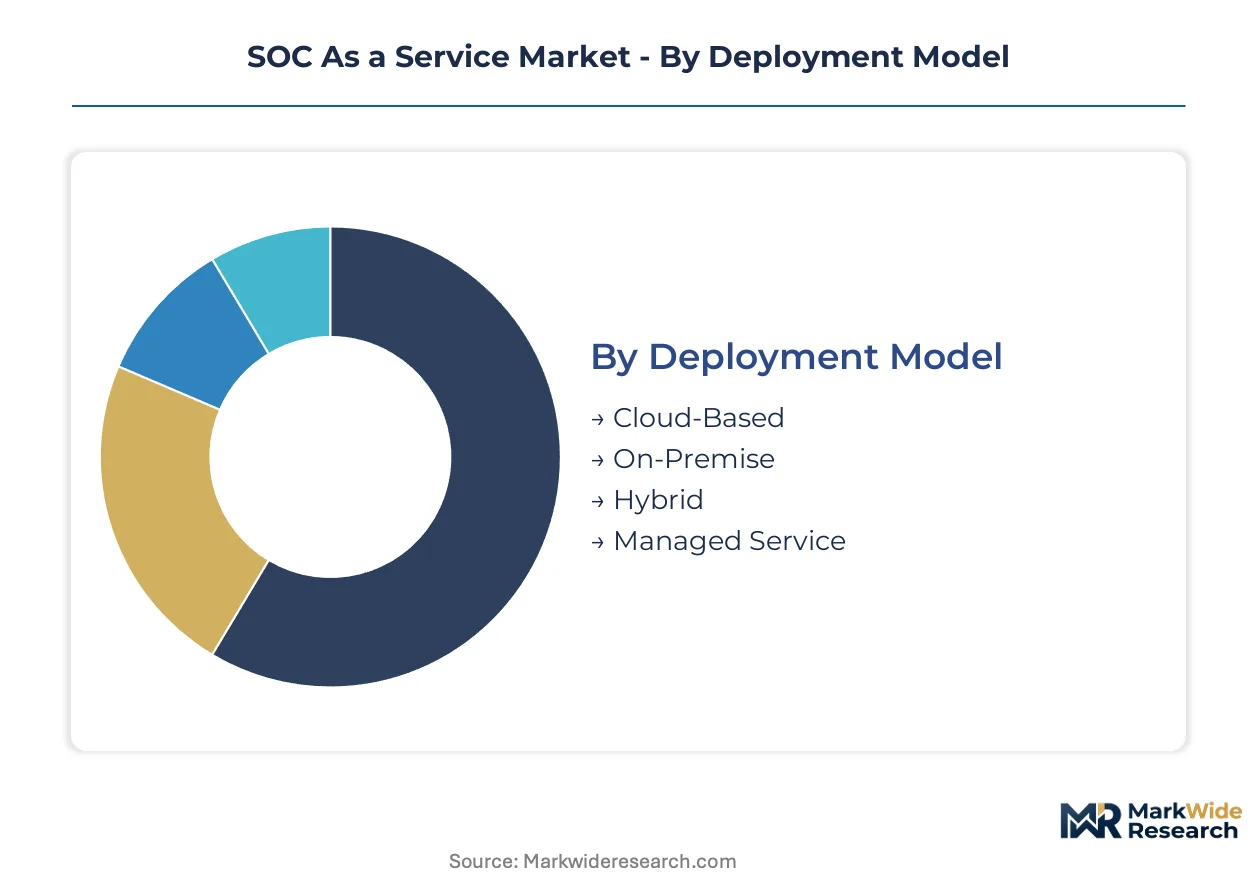
The SOC as a Service market's functional differentiation allows providers to address diverse client requirements and operational models. Understanding these segments helps tailor service delivery to specific deployment preferences, threat landscapes, and organizational sizes. This granular view illuminates where demand concentrates and how specialized offerings gain traction.
Deployment Model:
The spectrum of deployment models reflects varying client comfort levels with external infrastructure and internal resource availability.
- Cloud-Based:This model delivers security operations entirely through a provider's cloud infrastructure, offering scalability and reduced client overhead. Demand is high in industries prioritizing agility and cost efficiency, like technology startups and digital-native businesses in Germany.
- On-Premise:Security operations are conducted using hardware and software located within the client's own data centers.
- Hybrid:This approach combines elements of both cloud-based and on-premise security solutions, allowing organizations to maintain control over sensitive data while leveraging cloud scalability. Large enterprises in the United States often adopt hybrid models to balance compliance needs with operational flexibility.
- Managed Service:Providers fully manage the client's security infrastructure, often integrating with existing systems.
The dominant share belongs to Cloud-Based deployments, while Hybrid solutions are closing the gap fastest.
Solution Offering:
Solution offerings categorize the core security functions that clients seek to outsource, reflecting specific operational needs.
- Threat Detection:This service continuously monitors network traffic, endpoints, and logs to identify malicious activities and anomalies using advanced analytics. Financial institutions in London rely on robust threat detection to protect against sophisticated cyber fraud and data breaches.
- Incident Response:Providers offer rapid containment, eradication, and recovery services following a security breach, minimizing damage and downtime. Organizations in the healthcare sector, particularly in the US, prioritize incident response to meet HIPAA data breach notification requirements.
- Vulnerability Management:This involves identifying, assessing, and remediating security weaknesses in systems and applications.
- Compliance Monitoring:Services ensure adherence to regulatory standards like GDPR and HIPAA through continuous auditing and reporting.
- Security Analytics:Advanced analytics tools process vast amounts of security data to uncover hidden threats and improve overall security posture.
Threat Detection holds the largest segment, with Incident Response solutions expanding most quickly.
Application Area:
Application areas define the specific industries leveraging SOC as a Service, each presenting unique security challenges and regulatory environments.
- Financial Institutions:Banks, investment firms, and insurance companies utilize SOC as a Service to protect sensitive customer data, prevent fraud, and comply with strict regulations like DORA in Europe. Demand is particularly strong across major financial hubs.
- Telecommunications:Telecom companies secure vast network infrastructures and customer data against sophisticated cyberattacks.
- Government Agencies:Public sector entities outsource security operations to defend critical infrastructure and classified information from state-sponsored threats. Agencies in the United States and Germany increasingly adopt these services to bolster national cybersecurity defenses.
- Retail Chains:These businesses protect point-of-sale systems, customer payment information, and e-commerce platforms.
- Energy Providers:Utilities and power grids secure operational technology and critical infrastructure from cyber-physical attacks.
Financial Institutions command a significant share, while Government Agencies are rapidly climbing in adoption.
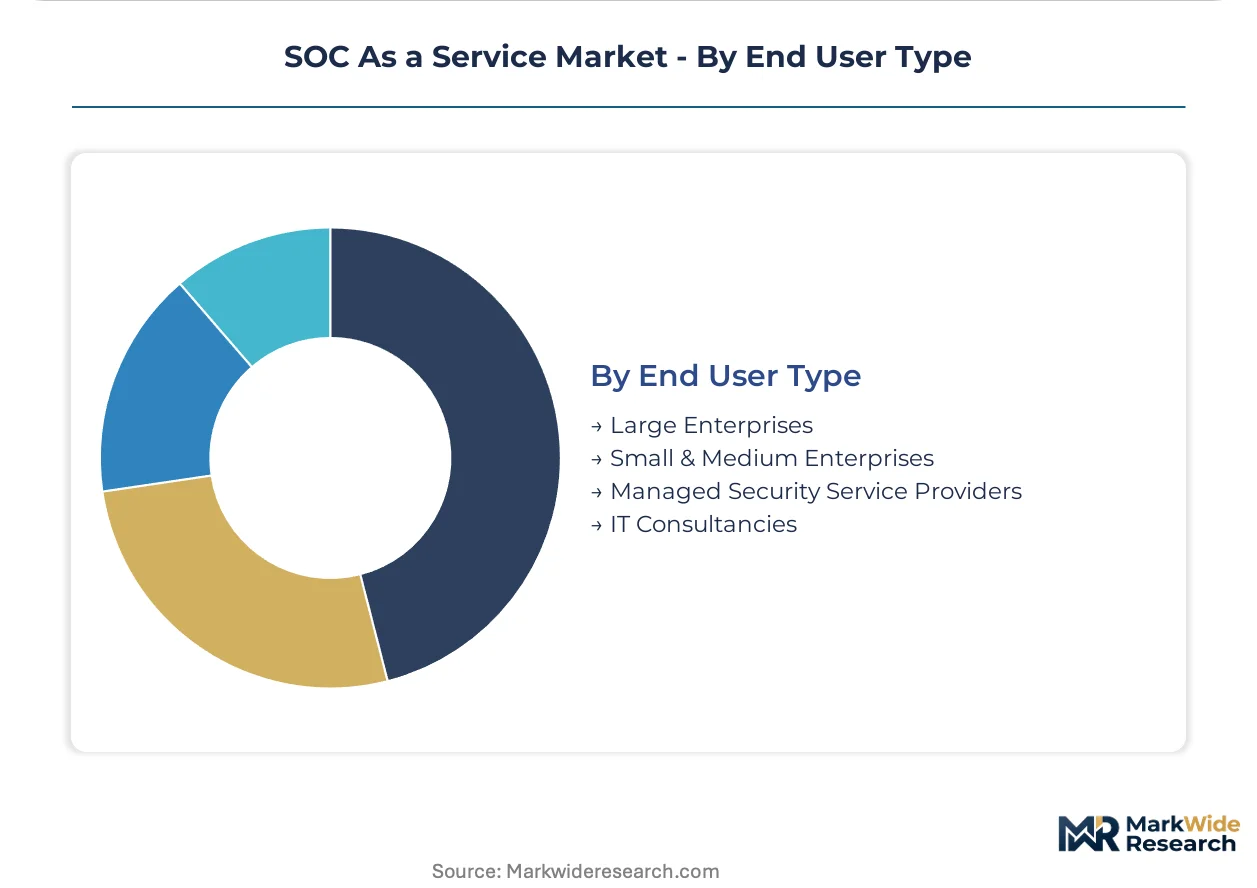
End User Type:
End user types highlight the organizational scale and operational models that drive adoption of outsourced security operations.
- Large Enterprises:These organizations possess extensive IT infrastructure and complex threat landscapes, often requiring customized security solutions and 24/7 monitoring. Companies in the US and Europe frequently outsource to manage the scale of their security needs and reduce operational costs.
- Small & Medium Enterprises:SMEs leverage SOC as a Service to access expert security capabilities and advanced tools without the prohibitive costs of an in-house security operations center. This segment is expanding quickly, particularly in developing digital economies.
- Managed Security Service Providers:MSSPs often white-label SOC as a Service to augment their own offerings to clients.
- IT Consultancies:These firms integrate SOC as a Service into broader IT strategy and implementation projects for their clients.
Large Enterprises constitute the primary customer base, with Small & Medium Enterprises demonstrating the steepest expansion trajectory.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The SOC as a Service market sees significant adoption where organizations prioritize data security and regulatory adherence. Large enterprises, particularly within the financial sector, drive substantial demand for outsourced security operations. This consumption pattern is evident across digitally mature economies and rapidly expanding digital markets.
United States
United States organizations seek advanced threat detection and incident response capabilities to protect sensitive customer data. The US HIPAA framework mandates robust security controls for protected health information, compelling continuous monitoring. Major financial hubs like New York City leverage SOC as a Service to protect against sophisticated cyber fraud and data breaches.
Germany
Germany's large enterprises are increasingly outsourcing security operations to manage complex threat landscapes. Europe's GDPR imposes strict data breach notification requirements on German businesses, stimulating demand for 24/7 monitoring. Industrial powerhouses in Bavaria are increasingly adopting cloud-based solutions for operational agility and compliance.
United Kingdom
Financial institutions in the United Kingdom are primary adopters, leveraging SOC as a Service to secure sensitive customer data and prevent fraud. Europe's Digital Operational Resilience Act (DORA) establishes strict ICT risk management for UK financial entities. London's financial district relies on robust threat detection to secure vast amounts of customer financial data.
Indonesia
Rapid digitalization within the e-commerce and fintech sectors in Indonesia creates untapped demand for cybersecurity services. Local data residency laws are emerging, presenting opportunities for providers to establish in-country SOCs. Jakarta's burgeoning tech startup ecosystem seeks cost-effective cybersecurity solutions to secure their digital assets.
Vietnam
Vietnam's expanding fintech sector and rapid digitalization drive the need for advanced cybersecurity services. Government initiatives promote digital transformation, increasing the imperative for secure infrastructure. Ho Chi Minh City's tech sector accelerates demand for outsourced security operations, particularly among small and medium enterprises.
SOC As a Service Market Key Industry Players
Channel-controlling players compete with product-specialist players in the SOC as a Service market, which exhibits a tiered structure. The market sees a mix of large integrated security providers and specialized cloud-native companies. Strategic archetypes include comprehensive service integrators, platform-centric innovators, and niche compliance specialists. Dominant competitive moves involve strategic partnerships to expand service portfolios and M&A activities to acquire advanced threat intelligence capabilities.
Within the comprehensive service integrator archetype, IBM exemplifies a provider sustaining its market position through integrated security services for large, complex enterprise environments. Palo Alto Networks, conversely, represents a platform-centric innovator, leveraging its cloud-native architecture to offer flexible solutions for diverse client sizes. Arctic Wolf Networks occupies a position among specialized providers focusing on managed detection and response, catering to organizations seeking expert security personnel without the full overhead of an in-house SOC. These companies collectively anchor the market's capabilities across different client needs and operational scales.
| Leading Market Players |
|---|
| IBM |
| AT&T Cybersecurity |
| Arctic Wolf Networks |
| Palo Alto Networks |
| Cisco Systems |
| Check Point Software Technologies |
| Fortinet |
| Verizon |
| Cloudflare |
Cost & Logistics Intelligence
Data sovereignty regulations, necessitating in-country data processing, directly determine both pricing tier spreads for compliant services and the geographic shape of the SOC as a Service supply chain.
Pricing Analysis
Cost-plus contract patterns, often indexed to the number of monitored assets or security events, establish baseline service charges for SOC as a Service. Price differentiation stems from customization levels for specific client environments and the volume scale of security operations required. Pricing pressure stems from the increasing commoditization of basic monitoring services, particularly for smaller organizations. Small and Medium Enterprises are most price-sensitive, while large enterprises prioritize comprehensive coverage and advanced capabilities over marginal cost savings.
Supply Chain Analysis
The upstream supply of highly skilled cybersecurity personnel and advanced threat intelligence feeds primarily originates from talent hubs in the United States, Europe, and India. Key raw material dependencies include cloud infrastructure services from major providers and specialized security software licenses. A structural risk is the persistent global cybersecurity talent shortage, which drives up operational costs for providers. Distribution runs through direct sales teams for large enterprises and through partnerships with Managed Security Service Providers for broader market reach.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The SOC as a Service market presents a significant service-attach opportunity, with advanced threat intelligence subscriptions expanding faster than basic monitoring packages.
For Market Incumbents: Insulate core revenue streams by investing in proprietary AI-driven automation for alert fatigue management, reducing reliance on manual processes. Consolidate market share by acquiring specialized providers focused on niche compliance verticals like Europe's DORA. This defends against commoditization of basic services and evolving regulatory threats.
For New Entrants and Emerging Players: Pursue specific compliance-driven segments, such as healthcare organizations needing HIPAA-specific monitoring or financial entities requiring DORA validation. The most penetrable segment is Small & Medium Enterprises in rapidly digitalizing economies like Southeast Asia. A strong go-to-market angle involves offering cost-effective co-managed SOC models that augment existing internal IT teams.
For Investors and Strategic Acquirers: The market sits at a growth phase that favors platform-centric innovators with scalable cloud architectures and strong automation capabilities. Long-term viability over the next decade depends on providers' ability to integrate advanced AI for threat hunting. Acquisition targets should include specialized providers in Operational Technology security or multi-regulation compliance. A signal to watch is increasing M&A activity for AI/ML-driven threat intelligence platforms.
| Strategic Initiative | Industry Significance |
|---|---|
| AI-Driven Threat Hunting | Enhances detection capabilities against sophisticated cyber threats, improving service efficacy for clients. |
| DORA Compliance Specialization | Addresses strict ICT risk management requirements for financial institutions, securing a high-value segment. |
| Operational Technology Security Expansion | Extends service offerings to critical infrastructure, tapping into a growing and underserved market. |
| Co-Managed SOC Model Development | Attracts organizations seeking shared security responsibilities, increasing market penetration and client retention. |
| Southeast Asia Market Entry | Captures demand from rapidly digitalizing economies with nascent cybersecurity infrastructure. |
Research Approach
Initial hypotheses were tested against primary input from CIOs, CSOs, security operations managers, and MSSP executives, and refined through iterative feedback loops. This approach combined in-depth primary interviews with rigorous secondary validation, drawing insights from SEC filings, cybersecurity vendor reports, and industry regulatory guidelines such as GDPR and HIPAA. Bottom-up and top-down triangulation ensured robust data consistency.
Demand-supply-balance framing informed the forecast framework, projecting market trajectories across the analysis window. The model segmented the market by deployment model, solution offering, application area, end user type, and geographic region. Compound Annual Growth Rates were derived from historical data trends and projected adoption rates, incorporating forecast inputs like cyberattack frequency and regulatory enforcement actions.
Sensitivities concentrate around rapid technological shifts in cyber defense, unforeseen regulatory changes, and major global economic downturns. Forecasts reflect assumptions documented through extensive primary and secondary research. Cross-checking against national cybersecurity agency reports is advised before commitment-grade decisions.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Portugal Cybersecurity Market
Cybersecurity
Cloud Security in Banking Market
Cybersecurity
Global Distributed Denial of Service (Ddos) Protection Market
Cybersecurity
Homomorphic Encryption Market
Cybersecurity
DNS Firewall Market
Cybersecurity
Micro-Segmentation Solutions Market
Cybersecurity
Latin America IoT Security Market
Cybersecurity
Middle East and Africa Cybersecurity Market
Cybersecurity
Application Programming Interface Security Market
Cybersecurity
Africa Cybersecurity Market
Cybersecurity
Cloud DLP Market
Cybersecurity
Network Edge Security Solutions Market
Cybersecurity
Information Security Products and Services Market
Cybersecurity
Multi-Cloud Data Protection Market
Cybersecurity
Global File Integrity Monitoring Market
Cybersecurity
Russia Cybersecurity Market