
 Global Security Policy Management Market | 2026-2036
Global Security Policy Management Market Size, Share, and Industry Trends Forecast 2026-2036
Global Security Policy Management Market Foresight
The shift from siloed, single-vendor security stacks toward multi-source, best-of-breed policy orchestration is realigning procurement patterns across enterprise security teams. Cisco Systems leverages its network hardware dominance to embed policy management directly into routing infrastructure. IBM Corporation anchors its position through hybrid cloud integration services that unify on-premises and cloud policy enforcement. Tufin Software Technologies specializes in firewall-agnostic workflow automation that reduces rule-set complexity across heterogeneous environments.
Global Security Policy Management encompasses the centralized creation, enforcement, auditing, and optimization of security rules across firewalls, cloud workloads, and identity systems, typically operating through continuous configuration validation with sub-minute policy propagation latency. Its primary purpose is to eliminate rule conflicts, close shadow access paths, and maintain compliance posture without manual spreadsheet review. Cloud-Based deployment now captures the fastest expansion as organizations retire legacy firewall management appliances. Policy Compliance solutions command the deepest margin pools because audit-ready documentation reduces regulatory penalty exposure. Hybrid deployments sustain steady traction among banks and telecom operators with strict data residency requirements.
The Federal Risk and Authorization Management Program in the United States and the EU Cybersecurity Act shape product certification requirements, forcing vendors to achieve common criteria evaluation before selling into government channels. ISO 27001 and NIST SP 800-53 further harden baseline controls, elevating demand for automated evidence collection and continuous control monitoring. Stakeholders must weigh whether to consolidate around platform-native policy engines or maintain interoperability across independent specialists as attack surfaces fragment across SaaS, edge, and operational technology domains.
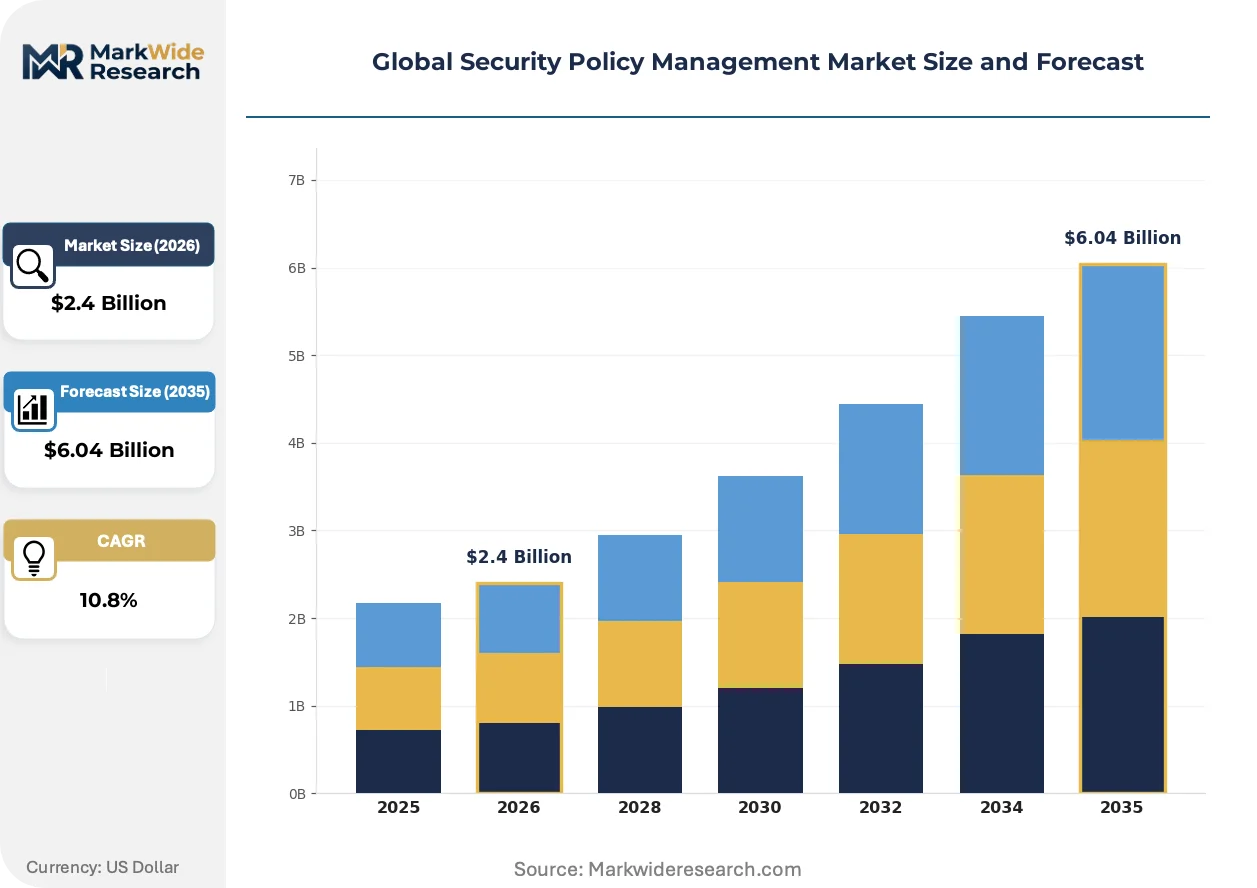
Market Dynamics
Multi-cloud fragmentation is forcing security teams to abandon siloed firewall consoles in favor of centralized policy orchestration platforms that span AWS, Azure, and private data centers.
Growth Catalysts
- EU AI Act algorithmic transparency mandates:Financial institutions in Germany and France must document automated security decision-making, driving automated evidence collection tooling.
- Critical infrastructure modernization:Japan's METI cybersecurity frameworks for energy and telecom sectors mandate continuous configuration validation across operational technology networks.
- Zero-trust network architecture:US federal agencies under NIST SP 800-207 guidance are replacing perimeter-based firewall rules with identity-centric microsegmentation policies.
Market Restraints
- Specialized engineering talent scarcity:Shortage of professionals fluent in both firewall rule optimization and cloud-native policy-as-code languages limits deployment velocity.
- Legacy appliance sunk costs:Enterprises with five-year depreciation cycles on hardware firewalls delay cloud migration despite operational inefficiencies.
- Cross-border data residency conflicts:GDPR Article 44 restrictions on EU personal data transfers complicate unified policy management for multinational banks.
Strategic Opportunities
- Operational technology convergence:Manufacturing and energy facilities in India require unified IT/OT policy management as ICS networks connect to enterprise systems.
- API-first security orchestration:DevSecOps teams in Brazil and Mexico are adopting policy-as-code workflows that integrate with CI/CD pipelines.
- Automated compliance documentation:ISO 27001 certification bodies are accepting machine-generated evidence trails, reducing audit preparation labor for mid-market enterprises.
Industry Challenges
- Firewall rule-set technical debt:Decades of accumulated access rules create shadow paths that automated discovery tools struggle to map completely.
- Multi-vendor syntax fragmentation:Each network equipment manufacturer uses proprietary policy languages, forcing translation layers that introduce propagation errors.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Security Policy Management Market |
| Market Size in 2026 | $2.4 Billion |
| Market Size in 2035 | $6.04 Billion |
| CAGR (2026 – 2036) | 10.8% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Policy Compliance, Risk Assessment, Threat Intelligence, Incident Response, Access Control Deployment Model: Cloud-Based, On-Premises, Hybrid, Managed Services End User: IT Departments, Financial Institutions, Telecommunication Providers, Government Agencies, Educational Institutions Channel Type: Direct Sales, Value-Added Resellers, System Integrators, Online Marketplaces |
| Companies Covered | Cisco Systems, IBM Corporation, Check Point Software Technologies, Juniper Networks, Fortinet, FireMon, Tufin Software Technologies, McAfee, Forcepoint, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Security Policy Management Market Shifts & Advancements
Security policy management is pivoting from reactive rule editing to predictive posture optimization, with artificial intelligence and continuous validation pipelines compressing remediation cycles from weeks to minutes.
Graph-based policy modeling engines are unifying firewall, cloud security group, and identity access rules into single relationship maps. Large US healthcare systems are deploying these engines to visualize lateral movement paths across hybrid environments. This unifying capability is collapsing the distinction between network and identity policy administration, forcing vendors to acquire complementary capabilities or partner deeply.
The EU Cybersecurity Act's common criteria certification scheme is mandating formal verification for security products sold into government channels. Vendors must submit policy management platforms for evaluation against standardized assurance levels before procurement eligibility. German federal agencies and French defense contractors are now filtering RFP responses based on certified evaluation status, elevating compliance documentation to a competitive differentiator.
Enterprise buyers are consolidating vendor relationships around platform-native policy engines rather than maintaining standalone firewall management specialists. CISOs at US financial services firms are retiring point solutions in favor of integrated suites from primary network or cloud security providers. This preference shift is visible most acutely in the Fortune 500 segment, where procurement teams prioritize vendor reduction over best-of-breed functional depth.
Global Security Policy Management Market Segmentation
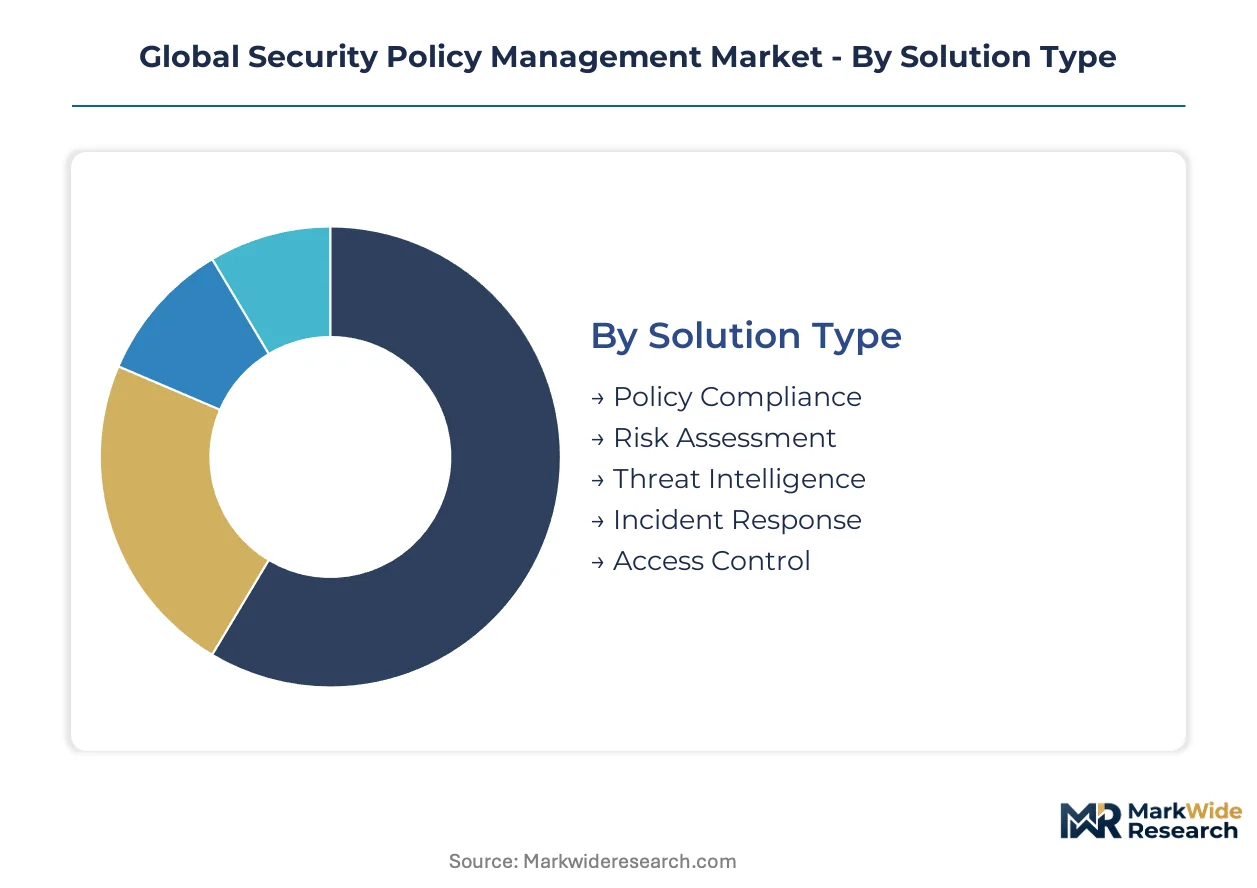
Security policy management vendors configure product roadmaps around distinct operational contexts. Deployment constraints, regulatory exposure, and procurement channels each reshape feature prioritization and pricing architecture across supplier portfolios.
Solution Type:
Supply concentration tilts toward audit-ready documentation tools as regulatory penalties escalate across financial services and healthcare.
- Policy Compliance:Automated evidence collection engines map firewall rules against NIST SP 800-53 and ISO 27001 control frameworks. German banks under BaFin supervision and US federal contractors facing FedRAMP audits drive demand for continuous control monitoring with machine-generated documentation trails.
- Risk Assessment:Quantitative scoring algorithms prioritize rule-set remediation based on exposure severity and blast radius calculations. Japanese energy utilities aligning with METI cybersecurity frameworks require operational technology risk quantification that spans IT and ICS network boundaries.
- Threat Intelligence:External indicator ingestion correlates observed attack patterns against policy configuration gaps.
- Incident Response:Automated policy quarantine workflows isolate compromised assets without manual firewall rule editing.
- Access Control:Identity-centric microsegmentation replaces perimeter-based network policies in zero-trust architectures.
Policy Compliance absorbs the bulk of installed capacity; Risk Assessment is expanding most quickly.
Deployment Model:
Cost tier differentiation separates subscription-based cloud offerings from capital-intensive appliance deployments with multi-year depreciation cycles.
- Cloud-Based:API-native policy orchestration platforms provision through AWS Marketplace and Azure Private Offers. DevSecOps teams in Brazil and Mexico adopt policy-as-code workflows that integrate with CI/CD pipelines, eliminating manual change windows.
- Hybrid:Split-policy architectures enforce data residency for EU personal data under GDPR Article 44 while centralizing management planes. French defense contractors and German federal agencies mandate common criteria certification for on-premises components.
- On-Premises:Air-gapped deployments serve classified networks with no external connectivity.
- Managed Services:Outsourced policy administration offloads rule optimization to specialized security operations centers.
Hybrid deployments retain the largest active footprint; Cloud-Based offerings are climbing the fastest.
End User:
Application-specific requirements fragment product positioning across verticals with divergent audit frequencies and data classification regimes.
- Financial Institutions:Algorithmic transparency mandates under the EU AI Act require automated documentation of security decision-making logic. German and French banks invest in evidence collection tooling that satisfies both prudential regulators and data protection authorities.
- Government Agencies:FedRAMP authorization and common criteria evaluation filter vendor eligibility before procurement. US federal zero-trust mandates under NIST SP 800-207 accelerate identity-centric microsegmentation deployments.
- IT Departments:Enterprise security teams consolidate point solutions around platform-native policy engines.
- Telecommunication Providers:Critical infrastructure designation triggers continuous configuration validation requirements.
- Educational Institutions:Budget-constrained procurement favors multi-tenant cloud solutions with volume-based academic pricing.
Financial Institutions command the deepest investment per seat; Government Agencies are gaining share fastest.
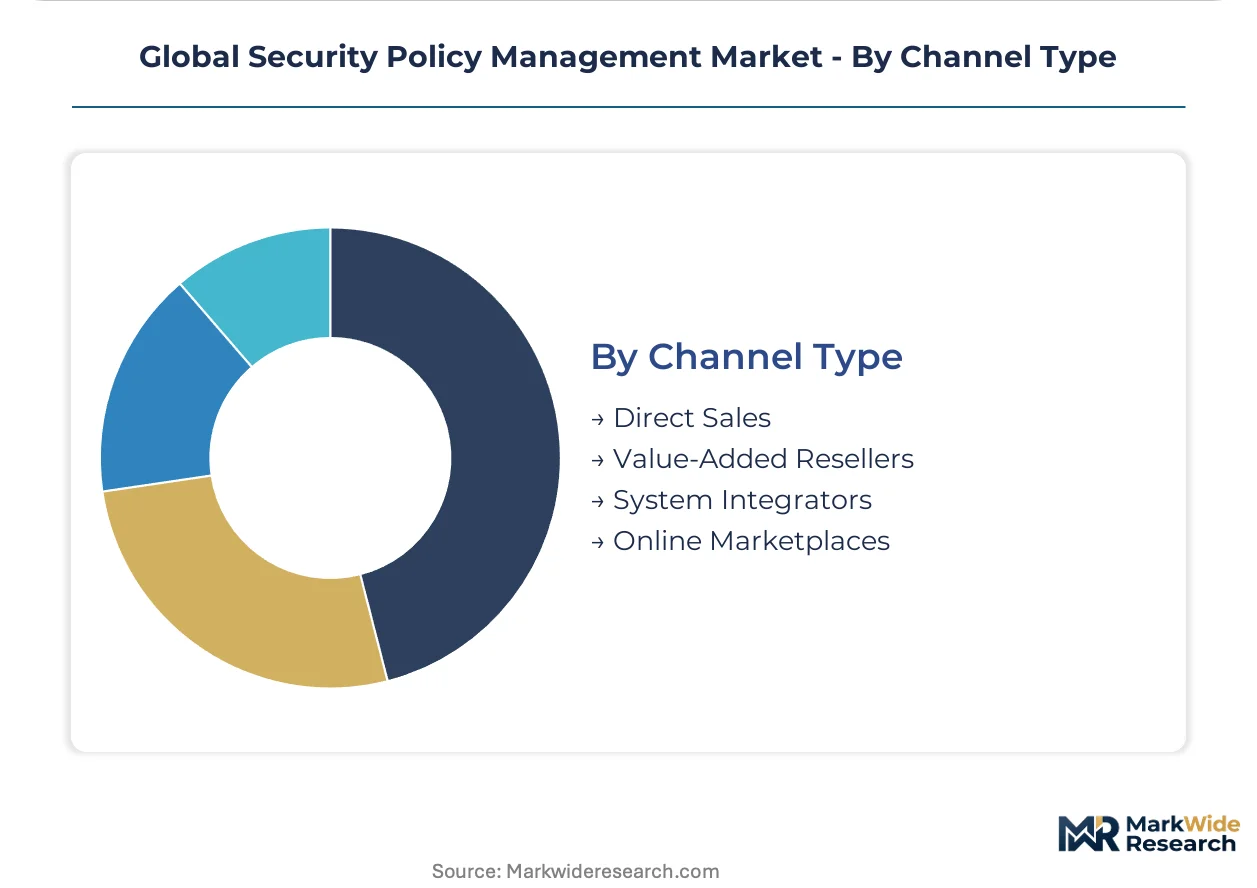
Channel Type:
Customer type and deal complexity determine route-to-market economics, with enterprise accounts demanding high-touch engagement.
- Direct Sales:Vendor field organizations handle Fortune 500 deployments with custom integration requirements and executive sponsorship programs. US healthcare systems and Japanese automotive manufacturers negotiate enterprise license agreements with dedicated customer success resources.
- System Integrators:Accenture and Deloitte deployment teams embed policy management into broader digital transformation engagements. Complex multi-cloud migrations across AWS, Azure, and private data centers require professional services coordination.
- Value-Added Resellers:Regional specialists provide first-line support for mid-market accounts with standardized requirements.
- Online Marketplaces:Self-service procurement through cloud marketplaces serves developer-led evaluations and departmental purchases.
Direct Sales captures the majority of contract value; System Integrators are expanding most quickly.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Silicon Valley's cybersecurity talent density anchors North American policy management innovation, while Frankfurt's financial regulatory gravity pulls European compliance tooling investment toward Germany.
United States
Federal zero-trust mandates under NIST SP 800-207 and FedRAMP authorization requirements drive procurement from Washington DC-area defense contractors and healthcare systems. The Department of Defense's CMMC framework accelerates continuous control monitoring adoption among aerospace suppliers in Virginia and Maryland clusters.
Germany
BaFin's prudential supervision and the EU AI Act's algorithmic transparency requirements compel Frankfurt and Munich-based banks to automate security decision documentation. Industrial manufacturers in Baden-Württemberg deploy unified IT/OT policy management as factory networks converge with enterprise systems.
Japan
METI cybersecurity frameworks for energy and telecom sectors mandate continuous configuration validation across operational technology networks. Tokyo and Osaka financial institutions modernize legacy firewall infrastructure while maintaining strict data residency for domestic payment systems.
France
ANSSI's critical infrastructure designation and the EU Cybersecurity Act's common criteria certification filter vendor eligibility for Paris-based defense contractors. Cloud policy orchestration platforms gain traction among Lyon pharmaceutical manufacturers navigating GDPR Article 44 transfer restrictions.
India
SEBI's cybersecurity guidelines for capital markets and RBI's data localization requirements push Mumbai and Bangalore financial institutions toward hybrid policy architectures. Manufacturing facilities in Gujarat and Tamil Nadu require unified IT/OT policy management as industrial control systems connect to enterprise networks.
Global Security Policy Management Market Competitive Landscape
Global majors compete with regional champions across certification depth and cloud-native integration capabilities. The vendor base organizes around three tiers: network hardware incumbents embedding policy engines into routing infrastructure, standalone firewall-agnostic specialists, and cloud-native orchestration platforms. Strategic moves concentrate on common criteria certification achievement for government channel eligibility and API-first architecture development for DevSecOps pipeline integration.
Within the network-embedded tier, Cisco Systems exemplifies hardware-anchored policy distribution, while IBM Corporation occupies a position bridging hybrid cloud management services. Tufin Software Technologies represents the standalone specialist archetype focused on heterogeneous environment workflow automation. These three anchors illustrate the strategic choice confronting enterprise buyers between platform consolidation and best-of-breed interoperability.
| Leading Market Players |
|---|
| Cisco Systems |
| IBM Corporation |
| Check Point Software Technologies |
| Juniper Networks |
| Fortinet |
| FireMon |
| Tufin Software Technologies |
| McAfee |
| Forcepoint |
| Others |
Supply & Pricing Matrix
Firewall rule optimization specialists concentrated in Israel and the United States command wage premiums that widen pricing spreads between premium managed-service bundles and stripped-down software licenses. Labor-cost differentials between Tel Aviv engineering hubs and Eastern European delivery centers translate directly into three-tier pricing structures that separate white-glove policy administration from self-service cloud offerings.
Pricing Analysis
Warranty and service bundling separates premium offerings from entry tiers, with continuous configuration validation and sub-minute policy propagation guarantees commanding substantial premiums over basic rule-editing tools. Three-tier pricing structure across premium, standard, and economy levels reflects certification depth—common criteria evaluation for government channels, ISO 27001 mapping for financial services, and unbundled SaaS for mid-market enterprises. Cost compression in the economy tier intensifies as open-source policy-as-code frameworks mature, reducing willingness-to-pay among DevSecOps teams. Government agencies and defense contractors exhibit the lowest price sensitivity due to procurement security requirements, while educational institutions and mid-market manufacturers drive hardest bargain.
Supply Chain Analysis
Direct-to-enterprise channels handle Fortune 500 deployments with custom integration requirements, while cloud marketplaces serve developer-led evaluations through AWS Marketplace and Azure Private Offers. Software development concentrates in Israel, the United States, and India, with policy engine R&D anchored in Tel Aviv cybersecurity clusters and Bangalore cloud-native engineering centers. The supply chain draws from specialized talent pools in network security engineering, cloud architecture, and compliance documentation. Single-source vulnerability around common criteria certification laboratories creates bottleneck risk for vendors seeking government channel eligibility. Distribution runs through value-added resellers for mid-market accounts and system integrators for complex multi-cloud transformations.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Consolidation pressure is intensifying as platform-native policy engines from network hardware incumbents displace standalone firewall management specialists, forcing weaker players toward acquisition or exit.
For Market Incumbents: Anchor market position through hybrid cloud integration investments that unify on-premises and cloud policy enforcement across AWS, Azure, and private data centers. Acquire API-first orchestration capabilities to capture DevSecOps pipeline integration opportunities in Brazil and Mexico. Common criteria certification maintenance represents essential defensive spend as German federal agencies and French defense contractors filter RFP responses based on certified evaluation status. For New Entrants and Emerging Players: Launch via cloud-native API-first architectures targeting mid-market enterprises with policy-as-code workflows that integrate with CI/CD pipelines. Manufacturing and energy facilities in India present the most penetrable white-space opportunity, requiring unified IT/OT policy management as industrial control systems connect to enterprise networks. Partner with regional system integrators to overcome entrenched vendor relationships in financial services and government verticals. For Investors and Strategic Acquirers: Re-rating potential sits with standalone firewall-agnostic specialists given platform consolidation tailwinds and enterprise buyer preference shifts toward integrated suites. Long-term viability favors vendors with proven common criteria certification achievement and demonstrated DevSecOps pipeline integration. Monitor FedRAMP authorization timelines and EU Cybersecurity Act evaluation completion rates as inflection indicators for government channel access and revenue acceleration.| Strategic Initiative | Industry Significance |
|---|---|
| Common Criteria Certification Achievement | Unlocks procurement eligibility for German federal agencies and French defense contractors under EU Cybersecurity Act mandates. |
| API-First Platform Integration | Captures DevSecOps adoption in Brazil and Mexico through CI/CD pipeline embedding and policy-as-code workflows. |
| Hybrid Cloud Orchestration Expansion | Addresses data residency requirements for EU personal data under GDPR Article 44 while centralizing management planes. |
| IT/OT Convergence Capability Buildout | Targets manufacturing and energy facilities in India and Japan as operational technology networks connect to enterprise systems. |
| Strategic Partnership with System Integrators | Accelerates complex multi-cloud deployments across AWS, Azure, and private data centers through Accenture and Deloitte channels. |
Research Methodology
Independent corroboration across CISO interviews, channel partner assessments, and regulatory filing analysis underwrites the qualitative findings in this study. Primary fieldwork engaged firewall administrators, cloud security architects, compliance officers, and procurement leads at financial institutions, government agencies, and critical infrastructure operators across the United States, Germany, Japan, France, and India. Secondary validation drew from FedRAMP authorization databases, EU Cybersecurity Act certification registries, NIST SP 800-53 control mappings, and ISO 27001 audit documentation. Bottom-up installed base estimates triangulate against top-down addressable market calculations derived from enterprise security spend benchmarks.
Rate-of-change decomposition separates volume expansion from value migration across the projection horizon. Segmentation dimensions modeled include deployment architecture, solution type, end-user vertical, and channel structure, with additional granularity on regulatory exposure tier and integration complexity. CAGRs were synthesized from historical adoption curves, policy refresh cycle analysis, and compliance mandate enforcement timelines. Forecast inputs incorporate zero-trust architecture migration pace, operational technology convergence rates, and algorithmic transparency documentation requirements under the EU AI Act.
The model assumes a particular technology adoption path; alternative pathways for cloud-native policy-as-code would alter the outlook if open-source frameworks achieve enterprise-grade feature parity faster than projected. Practitioners should monitor FedRAMP authorization queue lengths, common criteria evaluation backlog durations, and DevSecOps toolchain standardization signals for early indicators of vendor competitive position shifts.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security and Surveillance
India Perimeter Intrusion Detection and Prevention Market
Security and Surveillance
Global Contraband Detector Market
Security and Surveillance
Shock Sensor Market
Security and Surveillance
Latin America Electronics Security Market
Security and Surveillance
Anti-Piracy Protection Market
Security and Surveillance
Ballistic Protection Scanners Market
Security and Surveillance
Explosive Trace Detection Market
Security and Surveillance
Middle East Manned Security Services Market
Security and Surveillance
Smart Security Market
Security and Surveillance
Global Intrusion Detection System Market
Security and Surveillance
Face Smart Lockers Market
Security and Surveillance
Radar Security Market
Security and Surveillance
Manned Guarding Services Market
Security and Surveillance
Asia-Pacific Security Services Market
Security and Surveillance
Commercial Security Market
Security and Surveillance
Riot Control System Market