
 Global Artificial Intelligence in Security Market | 2026-2036
Global Artificial Intelligence in Security Market Size, Share, and Industry Trends Forecast 2026-2036
Global Artificial Intelligence in Security Market Foresight
The acute shortage of cybersecurity professionals with machine learning expertise is collapsing project timelines across enterprise deployments. IBM Corporation leverages its Watson security division to anchor hybrid cloud threat intelligence offerings. Palo Alto Networks competes through Cortex XSIAM, specializing in autonomous security operations center orchestration. CrowdStrike Holdings dominates endpoint protection with AI-native Falcon platform architecture that extends real-time detection capabilities.
Artificial intelligence in security encompasses neural network-based systems that process multimodal data streams—network traffic, video feeds, behavioral biometrics, and log files—at inference latencies below 50 milliseconds to identify, classify, and respond to threats without human intervention. The technology serves critical infrastructure operators, commercial enterprises, and government entities seeking to reduce mean-time-to-detect below the current industry baseline of 280 days. Threat detection solutions capture the largest revenue share as ransomware volume strains legacy signature-based defenses. Edge computing deployments represent the fastest-expanding configuration, driven by latency requirements for autonomous vehicle networks and smart city surveillance. Government agencies form the most concentrated end-user segment, with procurement cycles tied to national critical infrastructure protection mandates.
The U.S. NIST AI Risk Management Framework and the EU AI Act establish divergent compliance baselines that fragment product development roadmaps for vendors seeking transatlantic market access. China's NMPA and GB standards for algorithmic security auditing create additional certification layers for biometric and predictive policing applications. The U.S. SEC's cybersecurity disclosure rules and the EU's GDPR Article 32 obligations on automated processing further tighten liability frameworks for AI security providers. Stakeholders must monitor regulatory fragmentation between Washington, Brussels, and Beijing as the primary determinant of product architecture investments and geographic go-to-market sequencing.
Market Dynamics
The EU AI Act's risk-based classification system for biometric surveillance is fragmenting vendor compliance roadmaps and forcing architectural redesigns for transatlantic market access.
Growth Catalysts
- Critical Infrastructure Mandates:Government agencies in the United States, China, and Germany are expanding procurement of autonomous threat detection systems tied to national infrastructure protection programs.
- EU AI Act Compliance Deadlines:The regulation's tiered obligations for high-risk AI applications are accelerating enterprise replacement of legacy signature-based defenses with neural network architectures.
- Edge Computing Latency Requirements:Autonomous vehicle networks and smart city surveillance operators are demanding inference capabilities below 50 milliseconds, pulling AI security deployments toward distributed architectures.
Market Restraints
- Regulatory Fragmentation Costs:Divergent compliance baselines between the U.S. NIST AI Risk Management Framework and EU AI Act are duplicating product certification expenses for vendors seeking multi-jurisdictional approval.
- Specialized Talent Scarcity:The acute shortage of cybersecurity professionals with machine learning expertise is collapsing implementation timelines and inflating project labor costs across enterprise deployments.
- GPU Supply Concentration:Inference hardware dependencies on concentrated semiconductor foundry capacity in Taiwan and South Korea create procurement vulnerability for security AI training pipelines.
Strategic Opportunities
- Operational Technology Convergence:Industrial control system operators in Germany and the United States are integrating AI security with SCADA anomaly detection, creating unified cyber-physical protection platforms.
- Federated Learning Architectures:Privacy-preserving model training across distributed endpoints without centralizing sensitive data is opening sovereign AI security capabilities for government clients with data localization requirements.
- India's Digital Public Infrastructure:The country's expanding critical infrastructure digitization and domestic AI capability investments are creating procurement openings for biometric and network security vendors.
Industry Challenges
- Mean-Time-to-Detect Compression:Enterprise security teams struggle to reduce detection latency below the current 280-day industry baseline while managing alert fatigue from high-volume AI-generated threat signals.
- Cross-Border Data Governance:Conflicting GDPR Article 32 obligations on automated processing and China's GB standards for algorithmic auditing complicate cloud-native security service delivery.
- Adversarial Attack Surface Expansion:Neural network-based detection systems face escalating poisoning and evasion attacks requiring continuous model retraining and validation infrastructure.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Artificial Intelligence in Security Market |
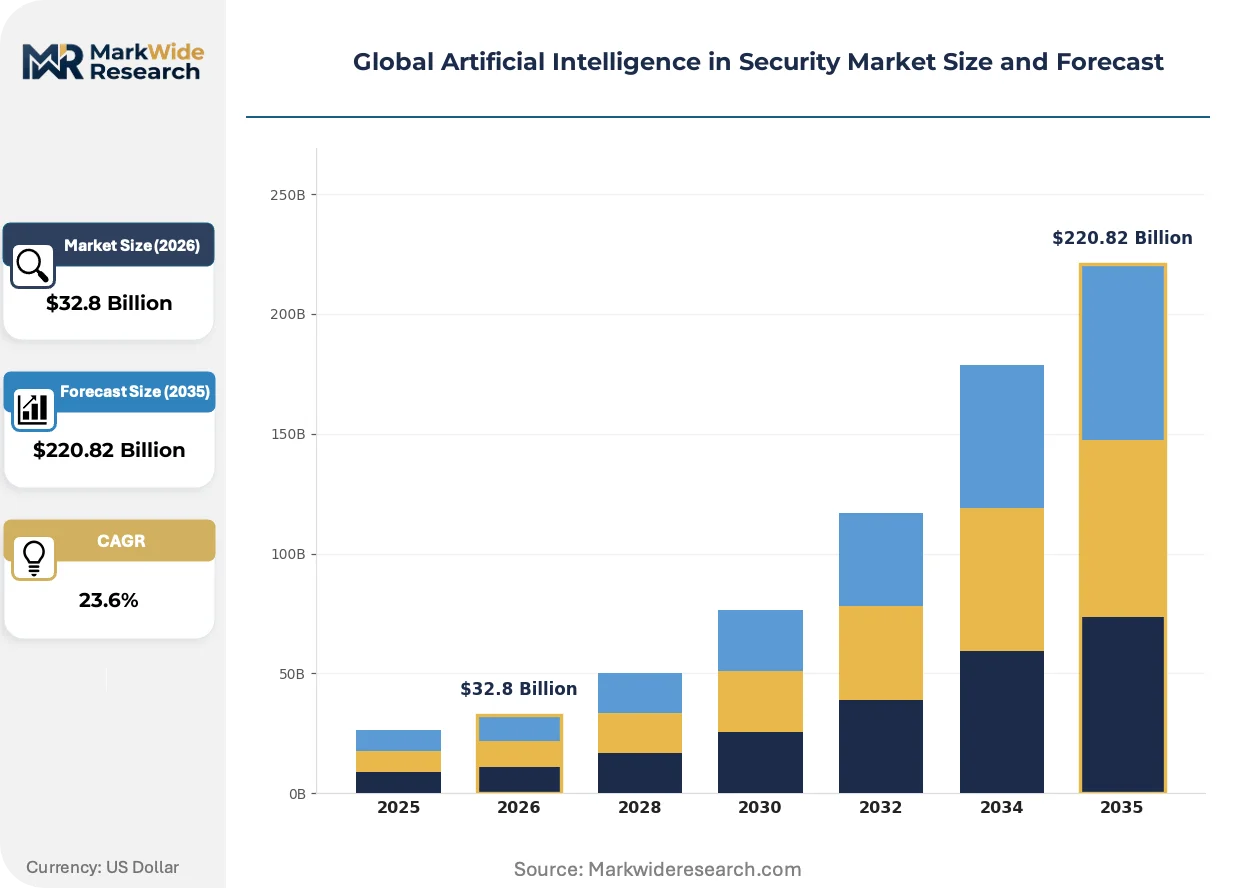
| Market Size in 2026 | $32.8 Billion |
| Market Size in 2035 | $220.82 Billion |
| CAGR (2026 – 2036) | 23.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution/Offering: Facial Recognition, Behavior Analysis, Threat Detection, Access Control, Fraud Prevention Deployment: Cloud-Based, On-Premise, Hybrid, Edge Computing Application: Cybersecurity, Public Safety, Retail Theft Prevention, Border Security, Asset Protection End User: Government Agencies, Financial Institutions, E-Commerce, Transportation Authorities |
| Companies Covered | IBM Corporation, Palo Alto Networks, CrowdStrike Holdings, Microsoft Corporation, Cisco Systems, Fortinet, Darktrace, SentinelOne, Google, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Artificial Intelligence in Security Market Shifts & Advancements
Neural network inference architectures are fragmenting into specialized configurations optimized for distinct latency, accuracy, and sovereignty requirements across government and commercial deployments.
Transformer-based large language models for security log analysis are bifurcating vendor competitive positioning. Financial institutions and managed security service providers are deploying these systems for autonomous threat hunting and incident narrative generation. The technology is compressing analyst investigation cycles while creating divergence between vendors offering cloud-dependent versus air-gapped deployment options.
The EU AI Act's prohibition on real-time biometric identification in public spaces is reshaping product roadmaps for European market entry. Vendors must now architect systems with explicit human-in-the-loop decision gates for high-risk use cases. European critical infrastructure operators are prioritizing explainable AI capabilities to satisfy audit trail requirements, favoring vendors with interpretable model architectures over black-box alternatives.
Security procurement is consolidating around integrated platform contracts rather than point-solution accumulation. Chief information security officers in United States healthcare and German manufacturing verticals are displacing multi-vendor endpoint, network, and identity stacks with unified AI-native security fabrics. This consolidation is most visible in enterprise segments with mature security operations centers seeking reduced vendor management overhead.
Global Artificial Intelligence in Security Market Segmentation
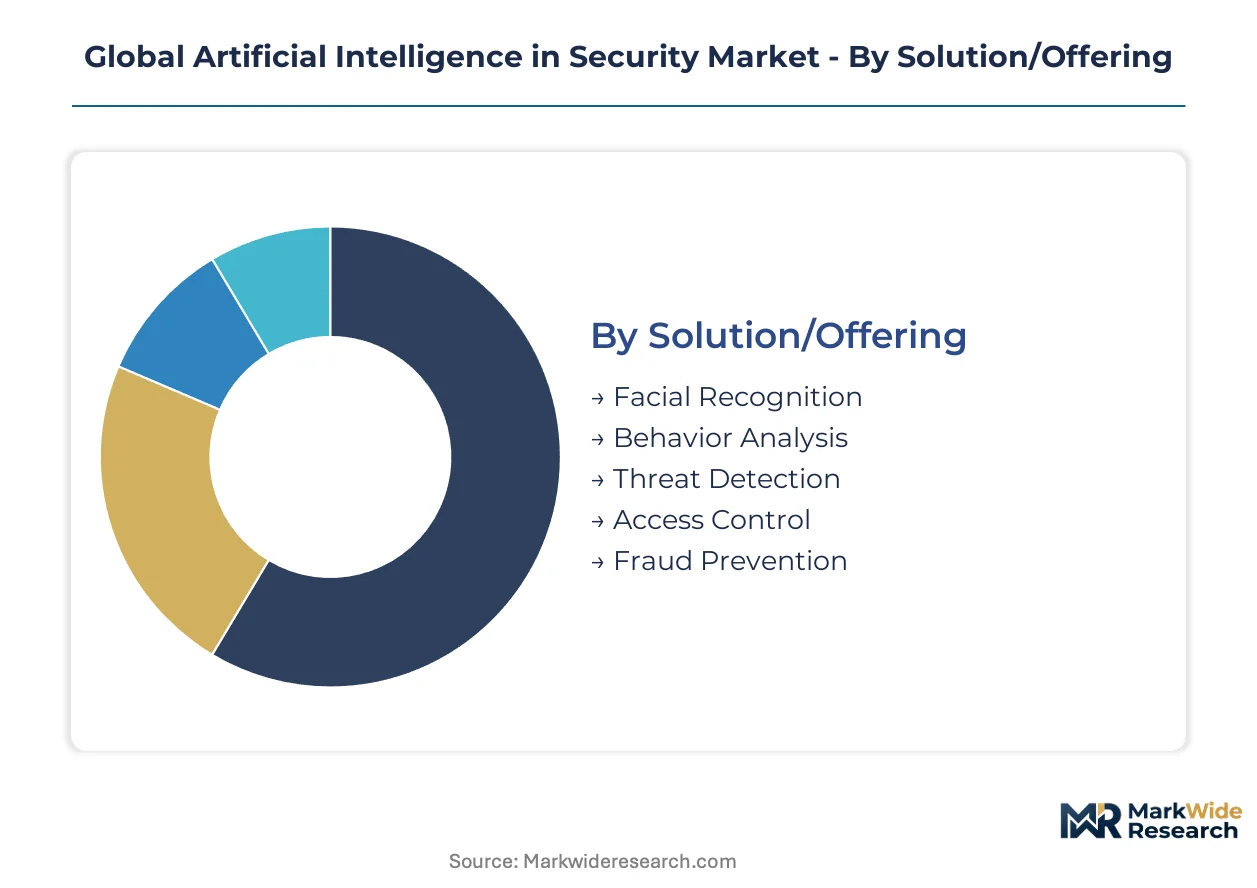
AI security deployments fragment across distinct technical architectures and operational contexts. Procurement patterns diverge sharply between sovereign government programs and commercial cloud-native implementations. Understanding these segment boundaries clarifies vendor positioning and compliance obligations across jurisdictions.
Solution/Offering:
Geographic demand concentration varies significantly across solution types, with biometric applications facing stricter localization requirements than network-centric offerings.
- Threat Detection:Neural network-based systems process multimodal data streams—network traffic, behavioral biometrics, and log files—at inference latencies below 50 milliseconds. Government agencies in the United States and Germany are expanding procurement of autonomous systems tied to national infrastructure protection mandates, compressing mean-time-to-detect below the 280-day industry baseline.
- Fraud Prevention:Financial institutions deploy real-time transaction monitoring using transformer architectures for pattern recognition across payment networks. Banks in the United States and China are replacing legacy rule-based systems with machine learning models to address synthetic identity fraud and authorized push payment scams.
- Facial Recognition:Biometric identification systems for access control and surveillance applications.
- Behavior Analysis:Anomaly detection for insider threat identification and user entity behavior analytics.
- Access Control:AI-enhanced physical and logical access management with continuous authentication.
Threat Detection commands the established base. The steepest expansion runs through Fraud Prevention.
Deployment:
Cost tier stratification separates premium sovereign deployments from standardized commercial cloud offerings, with latency requirements driving architectural decisions.
- Edge Computing:Distributed inference nodes process data locally to meet sub-50 millisecond latency requirements for autonomous vehicle networks and smart city surveillance. Operators in Germany and China are prioritizing edge architectures to satisfy data sovereignty mandates while enabling real-time response capabilities.
- Cloud-Based:Centralized model training and inference delivery through hyperscale infrastructure. Managed security service providers in the United States favor cloud deployment for threat intelligence federation across distributed enterprise clients, though GDPR Article 32 obligations complicate cross-border data flows for European operations.
- On-Premise:Air-gapped installations for classified government environments and critical infrastructure operators with strict data localization requirements.
- Hybrid:Split architectures combining edge inference with cloud-based model updates and analytics.
Cloud-Based deployments hold the dominant installed base. Edge Computing is climbing the fastest as latency-sensitive applications multiply.
Application:
Customer maturity and procurement sophistication vary dramatically across use cases, from regulated critical infrastructure to commercial loss prevention.
- Cybersecurity:AI-native security operations center platforms for endpoint, network, and identity protection. Financial institutions and healthcare providers in the United States are consolidating multi-vendor stacks into unified AI fabrics to reduce vendor management overhead and improve detection coherence.
- Public Safety:Real-time video analytics for crowd monitoring and emergency response coordination. Municipal operators in China and Germany face divergent compliance obligations under the EU AI Act's biometric surveillance restrictions versus domestic algorithmic auditing standards.
- Border Security:Multi-biometric identification and risk scoring for immigration and customs enforcement.
- Retail Theft Prevention:Computer vision systems for inventory protection and organized retail crime detection.
- Asset Protection:Physical security AI for critical infrastructure, data centers, and corporate facilities.
Cybersecurity applications anchor current revenue. Public Safety is gaining share fastest as urban surveillance investments accelerate.
End User:
Procurement authority and budget scale create distinct vendor engagement models across government and commercial segments.
- Government Agencies:National security and critical infrastructure protection programs with sovereign capability requirements. Agencies in the United States, China, and Germany are building domestic AI security supply chains, mandating local model training and algorithmic transparency for high-risk applications.
- Financial Institutions:Banks, insurers, and payment processors deploying fraud prevention and anti-money laundering systems. Institutions face tightening liability frameworks from the U.S. SEC's cybersecurity disclosure rules and the EU's GDPR Article 32 automated processing obligations.
- Transportation Authorities:Aviation, rail, and autonomous vehicle operators requiring sub-50 millisecond inference for safety-critical systems.
- E-Commerce:Online marketplaces and digital payment platforms deploying transaction monitoring and seller verification.
Government Agencies represent the most concentrated demand pool. Financial Institutions are expanding most quickly as regulatory pressure intensifies.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The SEC anchors the United States regulatory framework for AI security disclosure, while the EU AI Act and China's NMPA establish parallel compliance baselines that fragment vendor certification requirements across transatlantic and Asia-Pacific deployments.
United States
Financial institutions and critical infrastructure operators drive autonomous threat detection procurement under SEC cybersecurity disclosure rules and NIST AI Risk Management Framework mandates. The Department of Homeland Security coordinates national infrastructure protection programs requiring sub-50 millisecond inference capabilities. Silicon Valley clusters anchor cloud-native security development, while Washington DC metro defense contractors build sovereign AI capabilities for classified environments.
Germany
Industrial control system operators integrate AI security with SCADA anomaly detection under EU AI Act high-risk system obligations and BSI federal security standards. Bavaria's automotive manufacturing corridor demands edge-computing architectures for autonomous vehicle networks. Frankfurt's financial hub deploys real-time fraud prevention systems compliant with GDPR Article 32 automated processing requirements.
China
Government agencies mandate domestic algorithmic auditing under NMPA and GB standards for biometric surveillance applications. Smart city surveillance operators in Shenzhen and Shanghai prioritize edge inference nodes satisfying data sovereignty requirements. Beijing's AI security clusters focus on predictive policing and public safety video analytics for municipal deployment.
India
Digital public infrastructure expansion creates procurement openings for biometric and network security vendors under RBI financial sector guidelines and MeitY domestic capability incentives. Bangalore's technology corridor hosts AI security development centers serving government and enterprise clients. Mumbai's financial institutions deploy machine learning fraud prevention replacing legacy rule-based systems.
United Kingdom
Financial services regulators enforce operational resilience requirements accelerating AI-native security operations center consolidation. London's cybersecurity clusters specialize in managed security service provider platforms federating threat intelligence across European clients. The National Cyber Security Centre mandates algorithmic transparency standards for critical national infrastructure protection contracts.
Global Artificial Intelligence in Security Market Competitive Landscape
A small set of integrated leaders sits above a broader specialist tier, with platform consolidation displacing point-solution accumulation across enterprise security procurement. The vendor base separates into three archetypes: cloud-native platform providers, endpoint protection specialists, and autonomous security operations center orchestrators. Strategic moves concentrate on M&A for threat intelligence data assets and federated learning architecture development to satisfy data localization mandates.
Within the integrated platform tier, IBM Corporation and Palo Alto Networks exemplify hybrid-cloud threat intelligence positioning, while CrowdStrike Holdings anchors endpoint-native AI detection capabilities. Microsoft Corporation occupies a position spanning cloud infrastructure and security service delivery. These entities represent divergent architectural bets between centralized cloud inference and distributed edge deployment models competing for government and financial institution contracts.
| Leading Market Players |
|---|
| IBM Corporation |
| Palo Alto Networks |
| CrowdStrike Holdings |
| Microsoft Corporation |
| Cisco Systems |
| Fortinet |
| Darktrace |
| SentinelOne |
| Others |
Supply & Pricing Matrix
GPU cluster utilization rates above 85 percent at Taiwan Semiconductor Manufacturing and Samsung Foundry create scale economies that compress inference-hardware unit costs while concentrating supply-side bargaining power among hyperscale cloud providers. This density dynamic establishes price floors for sovereign AI security deployments that cannot match volume commitments, forcing government procurement toward longer-term reservation contracts.
Pricing Analysis
United States-Germany price spreads exceed 40 percent for equivalent edge-computing inference nodes due to EU AI Act compliance certification costs and localized model-training requirements. Three-tier pricing structure across premium sovereign, standard enterprise, and economy commercial levels separates vendors by data-residency guarantees and algorithmic-audit documentation depth. Pricing pressure stems from NVIDIA H100 supply constraints and concentrated foundry capacity, compressing margins for mid-tier security-AI vendors lacking direct silicon allocation. Financial institutions exhibit lowest price sensitivity, prioritizing sub-50 millisecond latency guarantees over per-unit cost, while municipal smart-city operators in India and Southeast Asia drive hardest bargain negotiations.
Supply Chain Analysis
Inventory lead times for AI training accelerators now extend 26-40 weeks, forcing security-AI vendors to pre-position hardware six months ahead of deployment commitments. Taiwan, South Korea, and the United States anchor foundry supply for advanced-node GPUs and AI-specific ASICs, with Netherlands-based ASML equipment dependencies creating single-source vulnerability at the lithography layer. Raw material exposure centers on high-purity silicon wafers, palladium for advanced packaging, and cobalt-free battery chemistries for edge-node power resilience. Distribution runs through hyperscale cloud marketplaces for commercial deployments, while sovereign programs demand direct OEM relationships with air-gapped logistics protocols.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Platform economics now govern competitive outcomes as security procurement consolidates around unified AI-native fabrics rather than point-solution accumulation, with interoperability standards and federated learning architectures determining ecosystem lock-in intensity.
For Market Incumbents: Consolidate threat-intelligence data assets through targeted acquisition of specialist behavioral-biometric vendors and edge-inference optimization shops. Deepen backward integration into GPU reservation contracts with foundry partners to secure allocation priority against cloud-hyperscaler competition. Reinforce platform stickiness by embedding EU AI Act compliance automation as a native service layer, reducing customer audit-preparation labor. For New Entrants and Emerging Players: Federated-learning deployment expertise represents the most under-served capability layer where incumbents lack architectural flexibility for data-localization mandates. Target India's digital public infrastructure expansion and Germany's industrial-control-system convergence as penetration points with lower incumbent saturation. Lead with sovereign-AI consulting and air-gapped implementation services rather than competing head-to-head on core detection algorithms. For Investors and Strategic Acquirers: Mid-cycle technology positioning favors specialists with proven edge-inference optimization and regulatory-automation tooling over horizontal platform aspirants. Acquisition candidates should demonstrate deployed production instances with government certification trajectories already initiated. Watch for EU AI Act enforcement precedent as the inflection signal that separates compliant architectures from stranded legacy investments.| Strategic Initiative | Industry Significance |
|---|---|
| Acquisition of Specialist Behavioral-Biometric Vendor | Consolidates differentiated training data assets for insider-threat detection under unified platform governance. |
| Federated Learning Architecture Development | Enables sovereign-AI deployments for government clients with strict data-localization mandates under GDPR Article 32. |
| EU AI Act Compliance Automation Layer | Reduces customer audit-preparation labor while creating switching costs through embedded regulatory-workflow integration. |
| GPU Reservation Contract with Foundry Partner | Secures inference-hardware allocation priority against cloud-hyperscaler competition during supply-constrained periods. |
| Edge-Inference Optimization for Sub-50ms Latency | Unlocks autonomous-vehicle and smart-city procurement segments with hard real-time requirements. |
Research Methodology
Demand-side practitioners and supply-side operators were both consulted through structured primary interviews with chief information security officers at financial institutions, government procurement officers for critical infrastructure programs, AI-security engineering leads at platform vendors, and managed security service provider executives. Secondary validation drew from SEC cybersecurity disclosure filings, EU AI Act implementation guidance documents, NIST AI Risk Management Framework technical standards, and hyperscaler capital expenditure disclosures for AI infrastructure buildouts. Bottom-up deployment estimates triangulated against top-down market sizing across solution type, deployment architecture, and end-user segment dimensions.
Across the analysis window, value projections integrated neural-network inference demand curves, regulatory-compliance cost escalators, and edge-computing hardware deployment trajectories. Segmentation modeling captured solution type, deployment architecture, application vertical, and end-user category with geographic regulatory-cluster overlays. CAGRs derived from historical adoption-pattern extrapolation adjusted for policy-mandated replacement cycles and sovereign-capability investment programs. Forecast inputs included foundry capacity-expansion announcements, government AI-security procurement budget authorizations, and adversarial-attack-surface evolution assumptions.
Forecasts assume regulatory continuity in Washington, Brussels, and Beijing compliance regimes; material policy shifts would require re-modeling of vendor certification timelines and geographic market-access sequencing. Outputs are directional rather than point-estimates.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Artificial Intelligence (AI)
Global Artificial Intelligence in E-Commerce Market
Artificial Intelligence (AI)
Global Computer Assisted Coding Market
Artificial Intelligence (AI)
Artificial Intelligence (AI) in Sports Market
Artificial Intelligence (AI)
Affective Computing Market
Artificial Intelligence (AI)
US Voice Recognition Market
Artificial Intelligence (AI)
Voice User Interface Market
Artificial Intelligence (AI)
Global Artificial Intelligence (AI) in Drug Discovery Market
Artificial Intelligence (AI)
Industrial AI Software Market
Artificial Intelligence (AI)
Artificial Intelligence HPC Cloud Market
Artificial Intelligence (AI)
Cloud Artificial Intelligence Market
Artificial Intelligence (AI)
Cognitive Computing Market
Artificial Intelligence (AI)
Federated Learning Market
Artificial Intelligence (AI)
Emotion AI Software Market
Artificial Intelligence (AI)
Cognitive Collaboration Market
Artificial Intelligence (AI)
Enterprise Generative AI Market
Artificial Intelligence (AI)
Edge AI Software Market