
 Europe Security Assurance Market | 2026-2036
Europe Security Assurance Market Size, Share, and Industry Trends Forecast 2026-2036
Europe Security Assurance Market Insights
The capability gap between capital-heavy platform vendors and point-solution providers is collapsing as cloud delivery models lower infrastructure barriers. Thales leverages its defense-grade certification pedigree to anchor premium positioning in government and aerospace verticals. Darktrace competes through autonomous-response AI that sustains recurring revenue without proportional headcount growth. Bitdefender extends its consumer antivirus brand into enterprise security assurance, occupying a mid-market tier that balances price sensitivity with compliance coverage.
Europe security assurance encompasses continuous validation, threat emulation, and compliance attestation services that verify organizational resilience against cyber incidents across hybrid IT estates. Technical implementations integrate automated breach-and-attack simulation, security control effectiveness measurement, and evidence-based risk scoring mapped to frameworks such as ISO 27001 and the EU Cybersecurity Certification Scheme. Cloud security assurance commands the largest current revenue pool as multi-cloud complexity outpaces native provider tooling. Application security segments register the fastest expansion as DevSecOps pipelines embed runtime verification into software delivery. Managed services for security assurance extract superior margins where clients outsource both technology operation and regulatory evidence production to specialized providers.
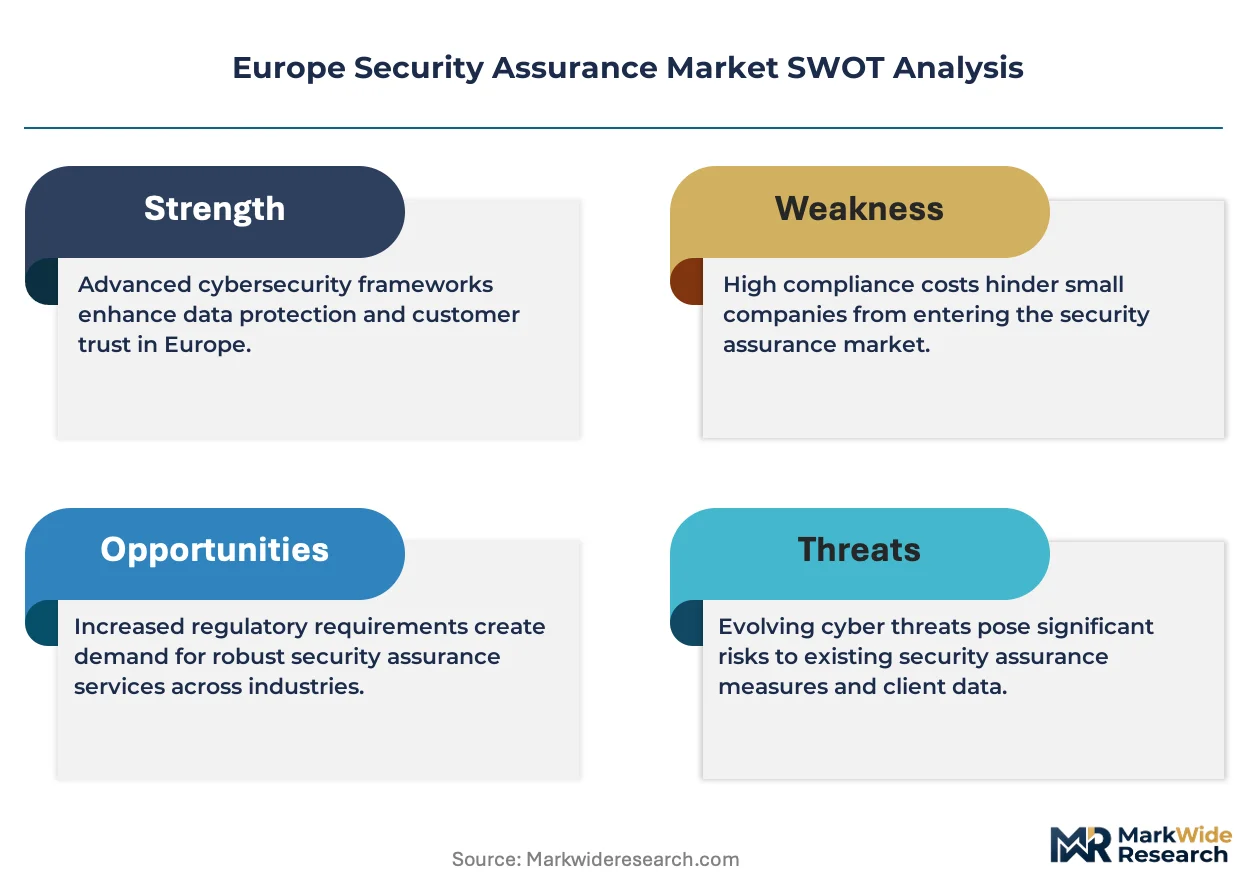
ENISA coordinates EU-wide certification schemes that shape product eligibility for public procurement and critical infrastructure supply chains. The NIS2 Directive compels member state regulators to enforce baseline security measures across expanded entity categories, directly stimulating demand for independent assurance validation. GDPR Article 32 obligations on technical and organizational measures reinforce processor accountability requirements that security assurance contracts document. Stakeholders must monitor how the EU Cyber Resilience Act extends assurance obligations to software and connected device manufacturers, reshaping addressable market boundaries beyond traditional enterprise IT.
Market Dynamics
The EU NIS2 Directive is compressing procurement cycles for security assurance services as essential and important entities face hard compliance deadlines with escalating penalty frameworks.
Growth Catalysts
- NIS2 enforcement timelines:Member state regulators must transpose the directive by October 2024, compelling critical infrastructure operators to procure continuous validation platforms ahead of audit windows.
- Financial services:Banks and insurers across Germany, France, and the Netherlands are mandating independent security attestation for third-party risk management under DORA convergence pressures.
- Cloud-native architectures:Multi-cloud complexity is outpacing native provider security tooling, forcing enterprises to externalize assurance functions to specialized vendors.
Market Restraints
- Certification backlog:ENISA's EU Cybersecurity Certification Scheme maintains limited accredited labs, creating 12-18 month queues for high-assurance product evaluations.
- Talent scarcity:The shortage of auditors qualified under ISO 27001 Lead Implementer standards constrains service delivery velocity for mid-tier consultancies.
- Input cost volatility:GPU-intensive breach simulation workloads face pricing pressure from cloud compute spot market fluctuations, compressing managed service margins.
Strategic Opportunities
- Eastern European expansion:Poland and Romania present underpenetrated demand as NIS2 expands entity categories to include regional logistics and digital infrastructure providers.
- DevSecOps convergence:Runtime application security testing integrated into CI/CD pipelines represents white space distinct from legacy perimeter-focused assurance.
- EU Cyber Resilience Act:Hardware and IoT manufacturers will require mandatory security attestation, extending addressable market boundaries beyond enterprise software.
Industry Challenges
- Skills fragmentation:The gap between cloud security architects and regulatory compliance specialists forces vendors to maintain dual-track hiring, inflating delivery costs.
- Integration friction:Legacy SIEM deployments resist API-native telemetry ingestion, requiring custom engineering that delays time-to-value for continuous validation deployments.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Europe Security Assurance Market |
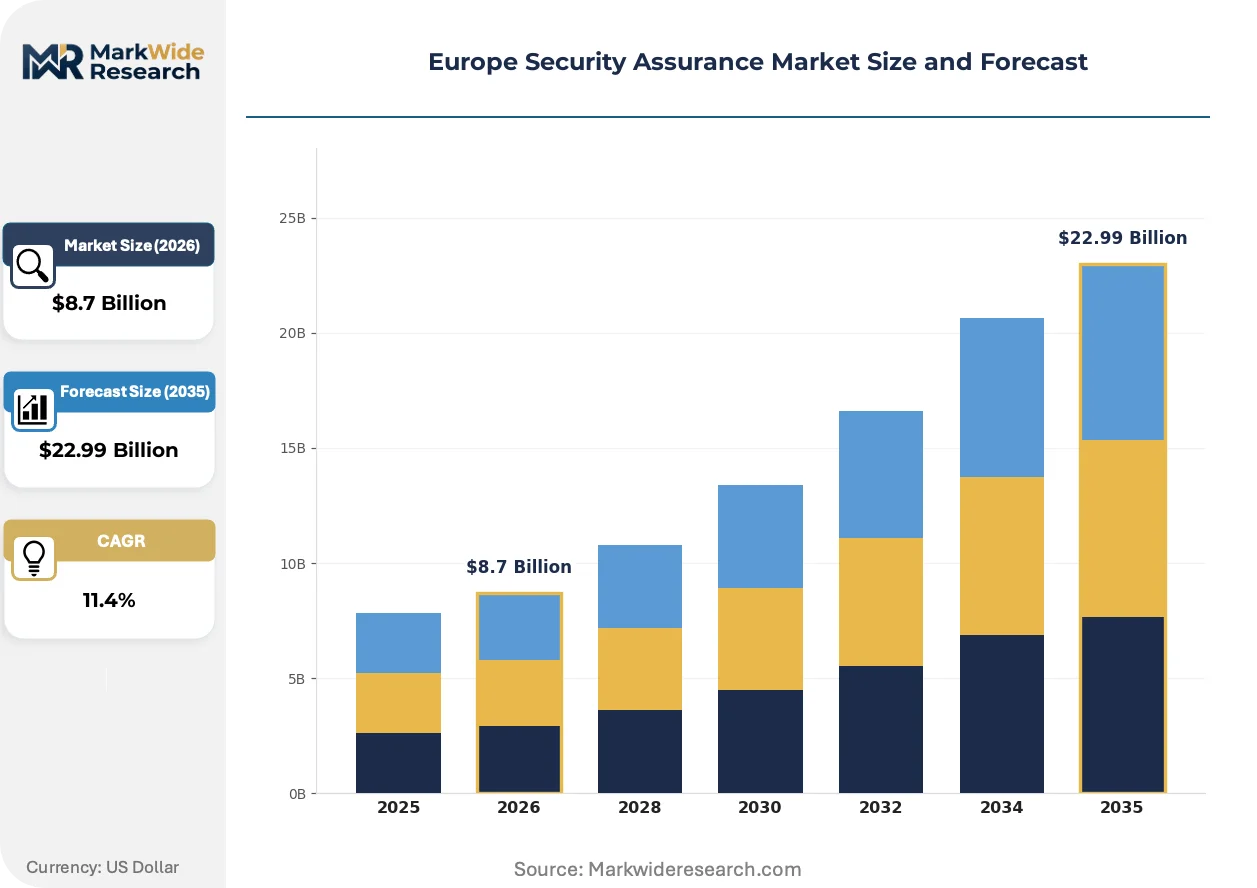
| Market Size in 2026 | $8.7 Billion |
| Market Size in 2035 | $22.99 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Cloud Security, Application Security, Endpoint Security, Network Security End User: Government, BFSI, Healthcare, Retail Service Type: Managed Services, Consulting, Training, Support Deployment: On-Premises, Hybrid, Public Cloud, Private Cloud |
| Companies Covered | Thales, Atos, Darktrace, Bitdefender, Accenture, BAE Systems, Sophos, WithSecure, NCC Group, Others |
| Regions Covered | Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Europe Security Assurance Market Trends and Innovations
Automated security control validation is displacing point-in-time penetration testing as the default procurement model for regulated industries, compressing the traditional assurance services value chain.
Breach-and-attack simulation technology is decomposing the market for manual red-team exercises. Financial services institutions in Frankfurt and Amsterdam are deploying autonomous threat emulation at weekly cadences. The technology is compressing pricing for traditional consulting engagements while expanding total addressable spend through continuous licensing models.
The EU Cyber Resilience Act imposes mandatory security update obligations and vulnerability disclosure requirements on connected device manufacturers. Industrial IoT producers in Germany face the heaviest compliance burdens as the regulation captures operational technology previously outside cybersecurity frameworks. ENISA is coordinating harmonized standards that will determine product eligibility for public procurement across member states.
Chief information security officers are consolidating vendor relationships around platforms that generate audit-ready evidence artifacts. Mid-market enterprises in Spain and Italy are abandoning multi-vendor point solutions for integrated assurance suites that automate ISO 27001 and NIS2 documentation. This preference shift favors vendors with pre-mapped control frameworks over specialized testing boutiques.
Europe Security Assurance Market Segmentation
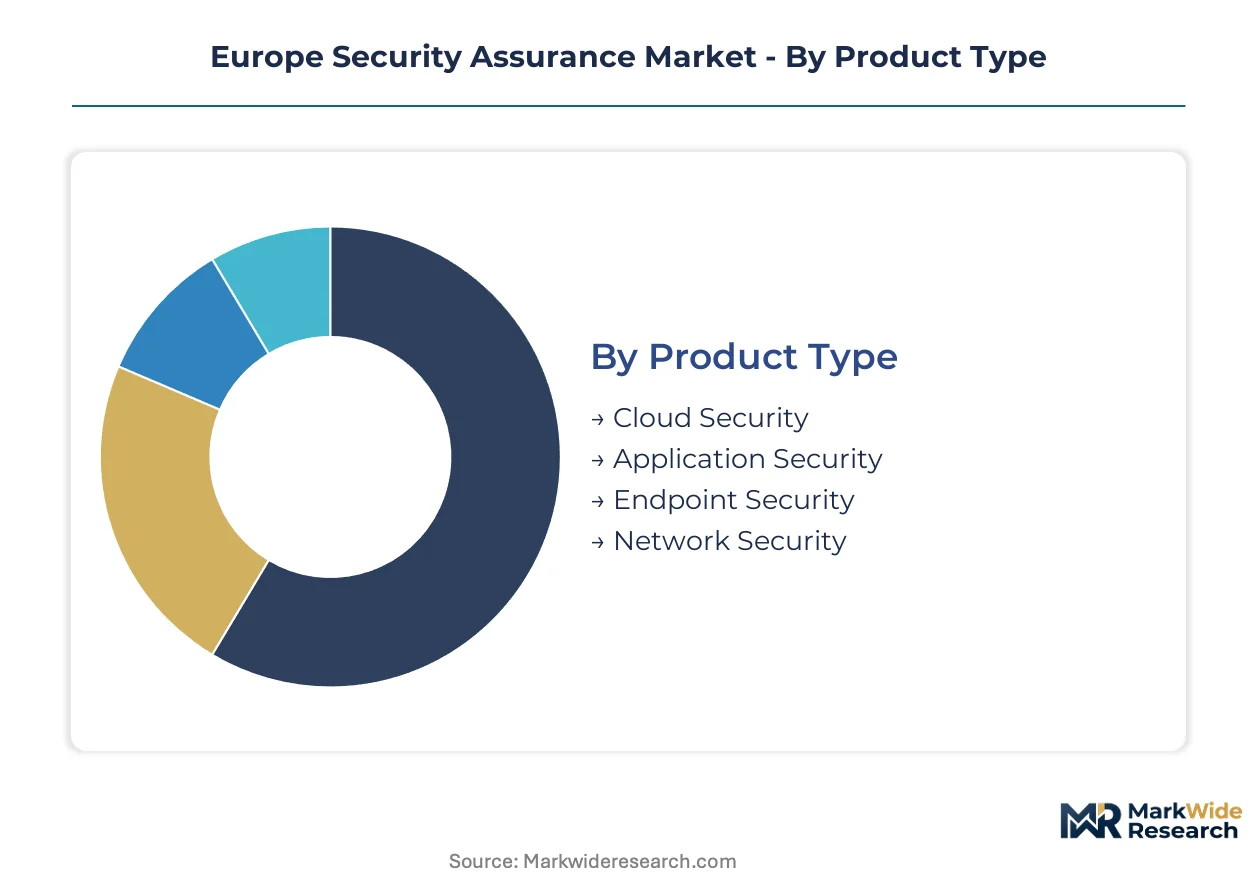
Security assurance procurement patterns diverge sharply across deployment models and service types, with compliance mandates reshaping how European organizations prioritize spending across the technology stack.
Product Type:
Cloud security offerings face intensifying substitution pressure from native provider tooling, while application security segments demonstrate stickier differentiation through DevSecOps integration.
- Cloud Security:Continuous validation platforms for multi-cloud estates dominate current procurement volumes. German automotive and French aerospace manufacturers drive demand as hybrid infrastructure complexity outstrips AWS, Azure, and GCP native security capabilities.
- Application Security:Runtime testing and software composition analysis embed directly into CI/CD pipelines. Dutch fintech clusters and Spanish telecom operators prioritize these tools to satisfy DORA and NIS2 software supply chain requirements.
- Endpoint Security:Device attestation and zero-trust verification tools.
- Network Security:Segmentation validation and microsegmentation assurance platforms.
Cloud security retains volume leadership; application security holds the steepest expansion curve.
End User:
Cost-tier segmentation reveals government buyers anchoring premium pricing while retail compresses margins through standardized procurement frameworks.
- Government:Defense-grade certification requirements and classified infrastructure mandates create insurmountable entry barriers. ENISA-coordinated schemes and national security clearances limit vendor eligibility across German federal systems and Scandinavian defense procurement.
- BFSI:Banks and insurers under DORA convergence pressures demand independent attestation for third-party risk management. Frankfurt and Amsterdam financial centers concentrate procurement of continuous validation platforms ahead of regulatory deadlines.
- Healthcare:GDPR Article 32 technical measure documentation and patient data processor accountability.
- Retail:PCI-DSS compliance automation and e-commerce transaction security verification.
Government segments command premium pricing tiers; BFSI demonstrates the most aggressive procurement acceleration.
Service Type:
Margin structures vary dramatically, with managed services extracting superior returns where clients outsource both technology operation and regulatory evidence production.
- Managed Services:Outsourced continuous monitoring and audit-ready documentation generation. Mid-market enterprises in Italy and Poland favor these arrangements to address ISO 27001 and NIS2 obligations without internal security operations center investment.
- Consulting:Gap assessments, control framework mapping, and remediation roadmapping. German industrial operators and Belgian logistics providers engage these services to interpret NIS2 entity classification and baseline security measure requirements.
- Training:Auditor certification programs and security awareness curriculum delivery.
- Support:Technical assistance and incident response retainer arrangements.
Managed services capture the highest margin expansion; consulting maintains the broadest geographic penetration.
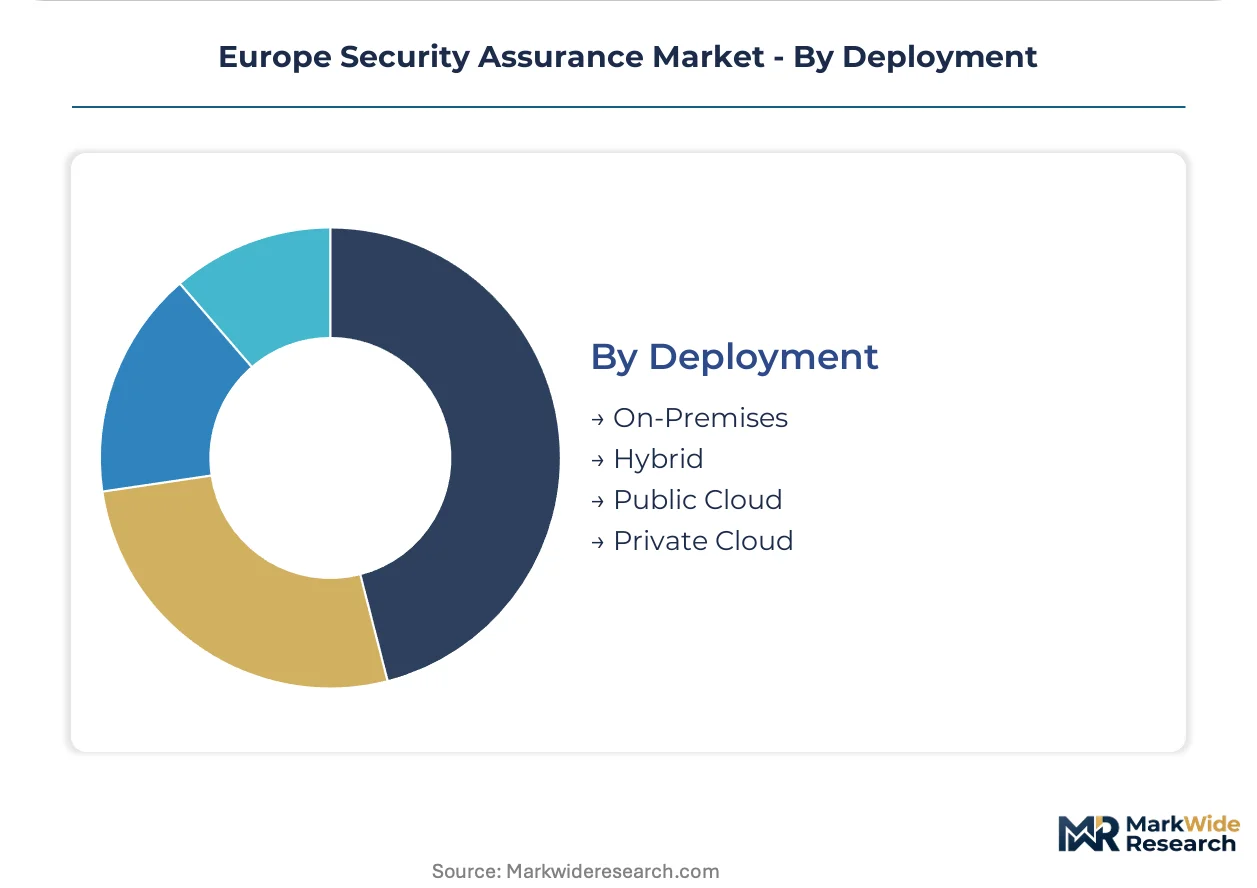
Deployment:
Maturity gradients separate established on-premises installations from cloud-native architectures, with hybrid deployments commanding transitional investment.
- On-Premises:Air-gapped validation platforms for classified and critical infrastructure environments. German energy operators and French nuclear facilities maintain these deployments to satisfy national security and operational technology isolation requirements.
- Hybrid:Split architectures accommodating regulated data residency alongside cloud scalability. UK financial services and Nordic healthcare providers prefer this model to reconcile GDPR localization with SaaS delivery economics.
- Public Cloud:Fully externalized assurance platforms leveraging provider infrastructure.
- Private Cloud:Dedicated tenant environments for single-organization use.
Hybrid deployment retains the largest active project pipeline; public cloud demonstrates the most rapid adoption velocity among new implementations.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
German industrial operators consume security assurance as embedded operational technology protection, whereas French and Dutch buyers prioritize financial services attestation and cloud-native validation respectively.
Germany
Automotive manufacturers and energy grid operators drive procurement of air-gapped validation platforms for operational technology isolation. The national implementation of NIS2 through the KRITIS umbrella tightens baseline security mandates for critical infrastructure. Industrial clusters in Bavaria and Baden-Württemberg embed continuous control verification into manufacturing execution systems.
France
Aerospace and defense contractors anchor demand for defense-grade certification and classified infrastructure assurance. ANSSI coordinates national security clearances that limit vendor eligibility across federal procurement channels. The Paris-Saclay cybersecurity cluster concentrates R&D investment in autonomous threat detection systems.
Netherlands
Amsterdam's fintech ecosystem accelerates adoption of continuous validation platforms for DORA convergence deadlines. The Dutch Authority for the Financial Markets enforces third-party risk management attestation requirements. Rotterdam port logistics operators procure supply chain security assurance for NIS2-expanded entity categories.
United Kingdom
Financial services institutions in the City of London mandate independent security attestation for operational resilience compliance. The Prudential Regulation Authority and Financial Conduct Authority jointly supervise DORA-aligned assurance frameworks. Edinburgh and Manchester health trusts deploy hybrid cloud validation to reconcile GDPR localization with SaaS economics.
Poland
Regional logistics providers and digital infrastructure operators represent underpenetrated demand as NIS2 expands entity classifications. The national cybersecurity authority implements EU certification scheme transposition with accelerated audit timelines. Warsaw and Krakow technology parks attract managed security service providers addressing mid-market ISO 27001 obligations.
Europe Security Assurance Market Competitive Landscape
A small set of integrated leaders sits above a broader specialist tier that competes on vertical-specific certification depth. Defense contractors and systems integrators occupy the upper tier through security clearance requirements that block generalist entry. Pure-play cybersecurity vendors and managed service specialists populate the broader tier beneath. Competitive moves center on strategic partnerships for certification lab access and portfolio diversification into adjacent compliance automation.
Within the integrated platform tier, Thales and BAE Systems exemplify defense-grade positioning anchored by national security clearances. Darktrace occupies a distinct autonomous-response archetype that sustains recurring revenue without proportional headcount expansion. Accenture represents the consulting-led convergence model that bundles technology deployment with regulatory evidence production.
| Leading Market Players |
|---|
| Thales |
| Atos |
| Darktrace |
| Bitdefender |
| Accenture |
| BAE Systems |
| Sophos |
| WithSecure |
| NCC Group |
| Others |
Pricing and Supply Chain Analysis
Cloud-native delivery models substituting for on-premises infrastructure are redrawing supply geography toward Ireland and the Netherlands while compressing pricing premiums previously commanded by hardware-dependent vendors. This substitution simultaneously erodes legacy margin structures and concentrates procurement leverage among hyperscale buyers.
Pricing Analysis
Managed service retainers and multi-year subscription renewals drive lifetime value across customer relationships. Three-tier pricing structure across premium, standard, and economy levels separates defense-grade certified platforms from mid-market compliance suites and basic validation tools. Price differentiation rests on ENISA certification tier and audit-ready documentation depth. Cost compression in the mid-market tier is intensifying because GPU-intensive breach simulation workloads face cloud compute spot market volatility. Retail and mid-market enterprises in Southern Europe exhibit the highest price sensitivity, while government buyers in Germany and France anchor premium tiers through security clearance requirements.
Supply Chain Analysis
Just-in-time provisioning of cloud compute instances dominates inventory strategy, though strategic stockpiling of GPU capacity is emerging among specialized breach simulation providers. Technology development concentrates in the United Kingdom, Germany, and Israel, with talent pipelines feeding from university cybersecurity programs in these jurisdictions. Component dependencies include specialized AI accelerators, ENISA-accredited certification lab access, and ISO 27001 Lead Implementer qualified auditors. Single-source vulnerability in GPU supply from NVIDIA and AMD creates concentration risk for autonomous threat emulation vendors. Distribution runs through direct enterprise sales teams, hyperscaler marketplaces, and systems integrators with national security clearances.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Buyer power is consolidating around integrated platform vendors as mid-market enterprises abandon multi-vendor point solutions for unified assurance suites.
For Market Incumbents: Shield recurring revenue streams by deepening integration with ENISA certification schemes and acquiring specialized DevSecOps testing boutiques before autonomous-response AI vendors extend into application security. Certification investment in the EU Cybersecurity Certification Scheme represents the critical defensive lever against emerging cloud-native entrants. For New Entrants and Emerging Players: Lead with runtime application security testing for Polish and Romanian logistics operators facing NIS2-expanded compliance deadlines. Eastern European mid-market enterprises present the most penetrable geography. Partner with regional systems integrators possessing existing ISO 27001 implementation relationships to bypass direct sales buildout costs. For Investors and Strategic Acquirers: Secondary-cycle assets sit with PE-backed managed security service providers in the United Kingdom and Germany holding government contracts with renewal visibility. Five-to-ten year viability hinges on DORA and NIS2 enforcement durability rather than discretionary security spending. Watch ENISA lab accreditation expansion timelines as the inflection signal for valuation multiples.| Strategic Initiative | Industry Significance |
|---|---|
| ENISA Certification Investment | Defense-grade accreditation unlocks German federal and aerospace procurement channels. |
| DevSecOps Platform Integration | Runtime testing embedded in CI/CD pipelines captures Dutch fintech and Spanish telecom demand. |
| Managed Service Expansion | Outsourced continuous monitoring addresses ISO 27001 gaps for Italian and Polish mid-market buyers. |
| Eastern European Geographic Expansion | NIS2 entity category expansion creates first-mover advantage in underpenetrated logistics markets. |
| Strategic Partnership with Systems Integrators | Channel access through Accenture and Atos accelerates deployment in regulated BFSI verticals. |
Research Methodology
Two parallel data streams informed the analysis: structured interviews with CISOs, IT procurement officers, ENISA certification lab directors, and managed security service delivery heads; and secondary validation through ENISA scheme documentation, NIS2 transposition progress reports, DORA regulatory technical standards, and hyperscaler security assurance capex disclosures. Primary fieldwork combined with bottom-up and top-down triangulation across vendor revenue disclosures and end-user procurement patterns.
Across the analysis window, volume and value outputs reflect modeled segmentation across deployment model, organization size tier, vertical industry, compliance framework complexity, and regional regulatory cluster. CAGRs derive from regression analysis of historical procurement velocity against enforcement timeline proximity. Forecast inputs incorporate ENISA accreditation capacity expansion and NIS2 penalty framework severity assumptions.
The analysis sits within stated boundaries; outcomes outside sustained regulatory enforcement or accelerated EU Cyber Resilience Act implementation would require recalibration. Forecasts reflect documented assumptions regarding member state transposition timelines and certification lab queue durations. Revision becomes warranted when ENISA accreditation backlog crosses eighteen-month thresholds.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security and Surveillance
Multi-Layer Security Market
Security and Surveillance
Swimming Pool Alarm Market
Security and Surveillance
Smart Home Security Market
Security and Surveillance
Global Traveler Security Services Market
Security and Surveillance
Global School and Campus Security Market
Security and Surveillance
Manned Guarding Services Market
Security and Surveillance
Narcotics Scanner Market
Security and Surveillance
Threat Detection Systems Market
Security and Surveillance
Specialized Threat Analysis and Protection Market
Security and Surveillance
Security System Integrators Market
Security and Surveillance
Night Vision Scopes Market
Security and Surveillance
Middle East and Africa Cargo and Vehicle Screening Market
Security and Surveillance
Cargo and Vehicle Screening Market
Security and Surveillance
Door and Window Alarm Market
Security and Surveillance
Middle East and Africa Cargo Inspection Market
Security and Surveillance
Air Cargo Security Equipment Market