
 Global SSH Terminal Market | 2026-2036
Global SSH Terminal Market Size, Share, and Industry Trends Forecast 2026-2036
Global SSH Terminal Market Foresight
Subscription-based licensing and managed service bundles are reconfiguring competitive entry barriers for SSH terminal vendors. SSH Communications Security Corp. leverages its proprietary protocol extensions to anchor enterprise-grade key management offerings. Bitvise Limited competes through deep Windows integration and granular access controls for regulated environments. VanDyke Software, Inc. specializes in cross-platform terminal emulation with FIPS-validated cryptography for federal contractors.
An SSH terminal is a software client that implements the Secure Shell protocol to establish encrypted command-line sessions over TCP/IP, typically operating on port 22 with support for public-key authentication and AES-256-GCM cipher suites. Its primary purpose is to enable administrators and developers to execute remote commands, transfer files, and manage network infrastructure without exposing credentials or payload data to interception. Cloud-based deployment leads solution type adoption as enterprises retire on-premises bastion hosts in favor of identity-aware proxy architectures. Secure Shell Client and Key Management segments capture concentrated margin pools where FIPS 140-2 compliance and hardware security module integration differentiate pricing tiers. Terminal Emulator solutions sustain steady demand from legacy mainframe and industrial control system environments.
FCC guidelines for critical infrastructure communications, EU NIS2 Directive requirements for entity security, and NIST SP 800-53 controls for federal information systems collectively mandate encrypted administrative access with auditable session recording. These frameworks shape procurement specifications and disqualify non-compliant vendors from government and financial services contracts. Stakeholders must monitor evolving post-quantum cryptography standards from NIST to determine when algorithm migration investments become compulsory rather than precautionary.
Market Dynamics
Zero-trust security mandates from NIST and EU cybersecurity frameworks are forcing wholesale protocol upgrades across enterprise infrastructure, compressing replacement cycles for legacy terminal emulators and elevating FIPS-validated cryptography from optional to procurement-critical.
Growth Catalysts
- NIST SP 800-53 Controls:Federal agencies must deploy encrypted administrative access with auditable session recording, disqualifying non-compliant vendors from government contracts and expanding the addressable market for certified solutions.
- Cloud Service Provider Expansion:Amazon Web Services, Microsoft Azure, and Google Cloud Platform are retiring on-premises bastion hosts in favor of identity-aware proxy architectures, creating pull-through demand for cloud-native SSH clients.
- Industrial Control System Hardening:Power utilities and manufacturing operators in Germany and Japan are replacing telnet and unencrypted serial consoles with AES-256-GCM protected terminal access to meet critical infrastructure protection standards.
Market Restraints
- Post-Quantum Cryptography Uncertainty:NIST's ongoing algorithm standardization timeline creates investment paralysis, as enterprises delay hardware security module upgrades until compulsory migration paths crystallize.
- Open Source Substitution:OpenSSH and community-maintained clients satisfy price-sensitive segments in emerging markets, compressing pricing power for commercial vendors in standardized deployment scenarios.
- Skill Concentration Geography:Deep expertise in hardware security module integration and FIPS 140-2 validation concentrates in the United States and Germany, creating talent bottlenecks for vendors seeking rapid certification.
Strategic Opportunities
- EU NIS2 Directive Compliance:The 2024 enforcement window mandates entity-level security for critical infrastructure operators across all twenty-seven member states, opening a regulatory tailwind for managed SSH service bundles.
- Quantum-Safe Key Management:Lattice-based cryptography integration with existing hardware security modules represents a technology convergence opportunity for first-movers offering algorithm agility.
- India Data Center Buildout:Hyperscaler facility construction in Mumbai and Hyderabad is outpacing local security tooling maturity, creating white space for cloud-native terminal access solutions with rupee-denominated pricing.
Industry Challenges
- FIPS 140-2 Validation Timeline:The CMVP certification process spans eighteen to twenty-four months, creating competitive lag for vendors responding to sudden procurement mandates.
- Legacy Mainframe Integration:Financial services institutions in Japan and Germany maintain decades-old IBM z/OS and Siemens BS2000 environments, requiring costly custom terminal emulation layers that fragment engineering resources.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global SSH Terminal Market |
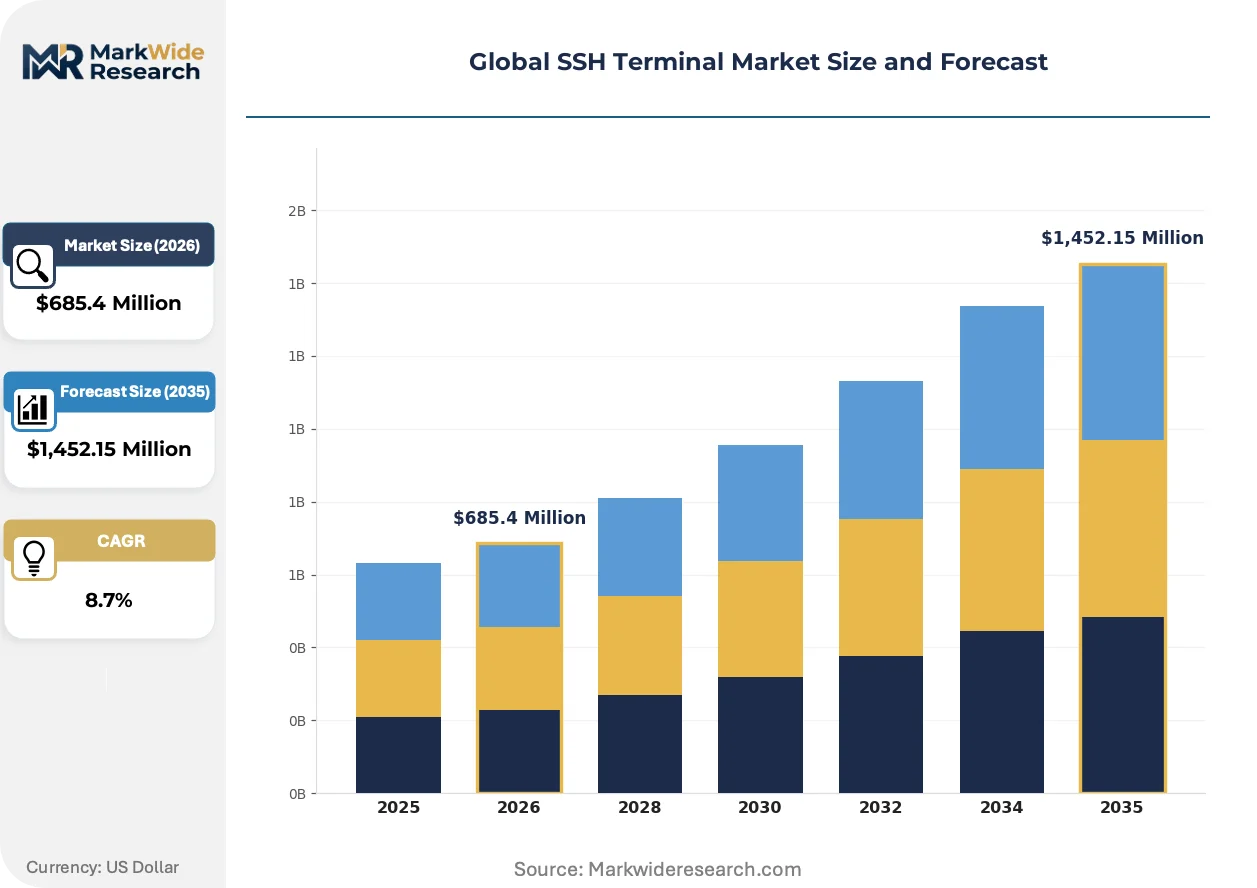
| Market Size in 2026 | $685.4 Million |
| Market Size in 2035 | $1,452.15 Million |
| CAGR (2026 – 2036) | 8.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: Cloud-based, On-premises, Hybrid, Managed Services Solution Type: Secure Shell Client, Terminal Emulator, Gateway, Key Management, Compliance Management Use Case: Network Management, Remote Access, Secure File Transfer, System Administration, Application Development End User Industry: Telecommunications, Financial Services, Manufacturing, Government Agencies, Educational Institutions |
| Companies Covered | SecureCRT, Bitvise Limited, Xshell, VanDyke Software, Inc., SSH Communications Security Corp., OpenSSH, Poderosa, FileZilla, MobaXterm, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global SSH Terminal Market Shifts & Advancements
Certificate-based authentication architectures are displacing password and static key methods, reshaping how enterprises provision, rotate, and audit credentials across distributed infrastructure teams.
Short-lived certificate authorities integrated with identity providers like Okta and Azure Active Directory are rendering obsolete the practice of distributing long-lived SSH private keys to developers and administrators. Fortune 500 technology teams are adopting this pattern at scale, with certificate lifespans compressed to hours rather than years. The structural consequence is collapsing incident response surface area, as compromised credentials automatically expire before lateral movement completes.
REACH and the EU AI Act are extending cybersecurity due diligence requirements to vendors of AI-assisted code generation tools, which increasingly embed SSH client libraries. Industrial consequence includes mandatory software bill of materials disclosure for terminal emulator components. European financial services procurement teams are now rejecting vendors unable to demonstrate transitive dependency vulnerability scanning.
Consumption-based licensing for terminal access sessions is displacing perpetual seat licenses in enterprise agreements, particularly among cloud-native software vendors with variable infrastructure team sizing. Channel disruption concentrates in value-added resellers historically dependent on upfront license margins. This pattern is most visible in United States technology sector procurement, where quarterly headcount fluctuations make fixed licensing economically unattractive.
Global SSH Terminal Market Segmentation
Segmentation in the SSH terminal market reveals how procurement priorities diverge across infrastructure maturity levels and regulatory exposure. Buyers in regulated industries prioritize FIPS-validated key management and audit-grade session recording, while cloud-native enterprises favor API-driven deployment models with consumption-based economics.
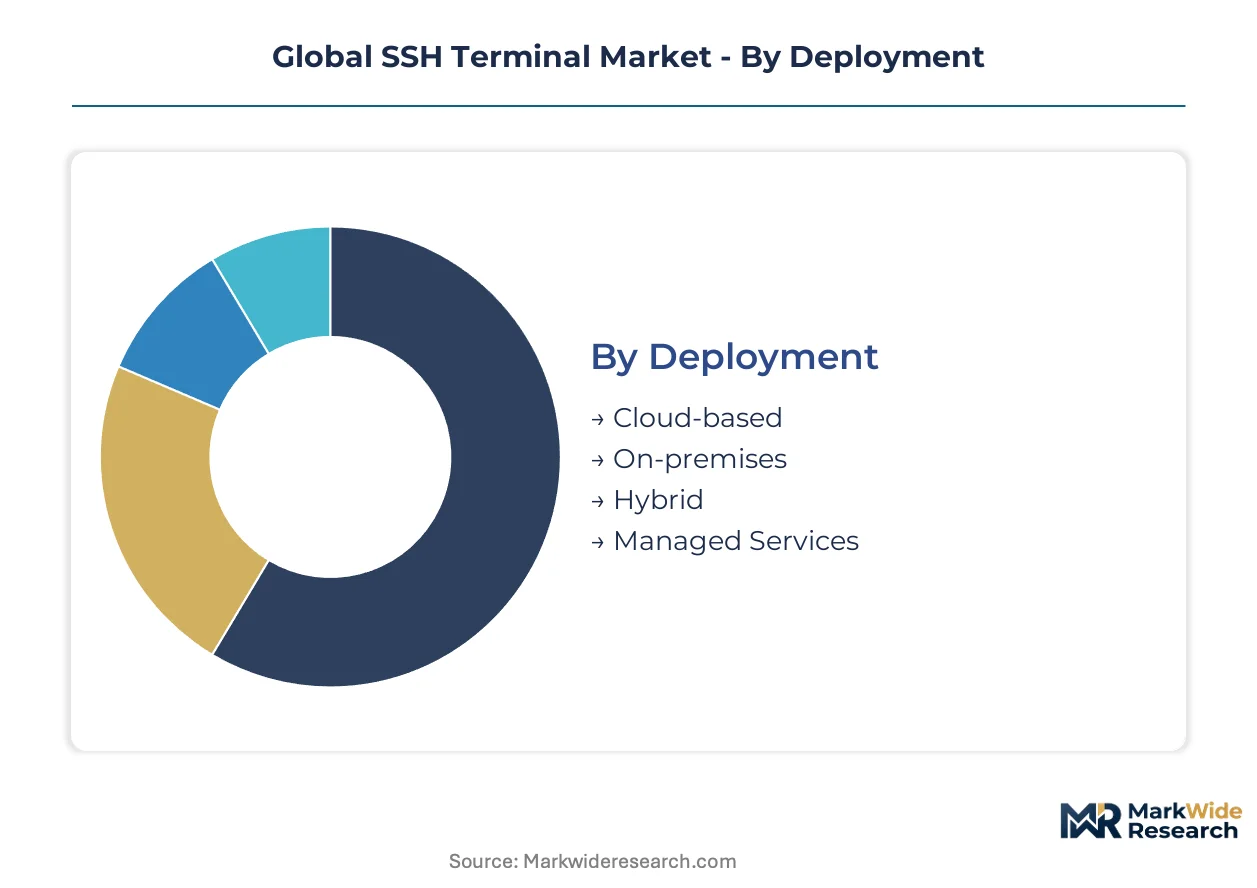
Deployment:
Mature self-hosted installations coexist with emerging identity-aware proxy architectures as enterprises navigate hybrid infrastructure transitions.
- Cloud-based:Identity-aware proxy architectures eliminate bastion hosts through just-in-time access provisioning. Demand concentrates among United States SaaS vendors replacing static SSH keys with short-lived certificates issued via Okta and Azure Active Directory integrations.
- On-premises:Air-gapped installations in classified facilities and critical infrastructure sites mandate local control over cryptographic material. German power utilities and Japanese manufacturing operators favor this model to satisfy national cybersecurity frameworks requiring domestic data residency.
- Hybrid:Split architectures route sensitive operations through on-premises hardware security modules while delegating development access to cloud gateways.
- Managed Services:Outsourced key lifecycle and session monitoring appeals to mid-market enterprises lacking internal cryptographic expertise.
Cloud-based deployments retain volume leadership; managed services holds the steepest expansion curve.
Solution Type:
Margin concentration follows certification intensity, with validated cryptography commanding premium pricing against commodity client software.
- Secure Shell Client:Software implementing SSH protocol versions 2.0 with AES-256-GCM cipher suites and public-key authentication. Financial services procurement in the United States and Germany disqualifies non-FIPS 140-2 validated clients from trading floor and payment system access.
- Key Management:Hardware security module integration and automated rotation workflows for enterprise-scale credential governance. Demand concentrates in federal contractor environments where NIST SP 800-53 mandates auditable key lifecycle controls.
- Terminal Emulator:Cross-platform emulation of legacy mainframe protocols including IBM 3270 and DEC VT-series for industrial control environments.
- Gateway:Centralized access brokers enforcing policy-based routing and session recording for compliance documentation.
- Compliance Management:Automated audit trail generation and regulatory mapping for EU NIS2 Directive and FCC critical infrastructure mandates.
Key Management captures the highest margin tier; Secure Shell Client maintains the broadest installed base.
Use Case:
Application context determines feature prioritization, with automation pipelines requiring API fidelity and human access emphasizing session auditability.
- Network Management:Real-time configuration of routers, switches, and firewalls through automated playbooks and interactive CLI sessions. Telecommunications operators in Japan prioritize this use case for 5G infrastructure orchestration.
- Secure File Transfer:SFTP and SCP implementations replacing unencrypted FTP in healthcare and financial document exchange. German banks drive demand for transfer solutions with end-to-end encryption and non-repudiation logging.
- Remote Access:Just-in-time developer and administrator connectivity to production environments.
- System Administration:Routine server maintenance and patch management across heterogeneous operating system fleets.
- Application Development:CI/CD pipeline integration for build server access and container orchestration control.
Network Management anchors current procurement volumes; Secure File Transfer is climbing fastest as compliance deadlines approach.
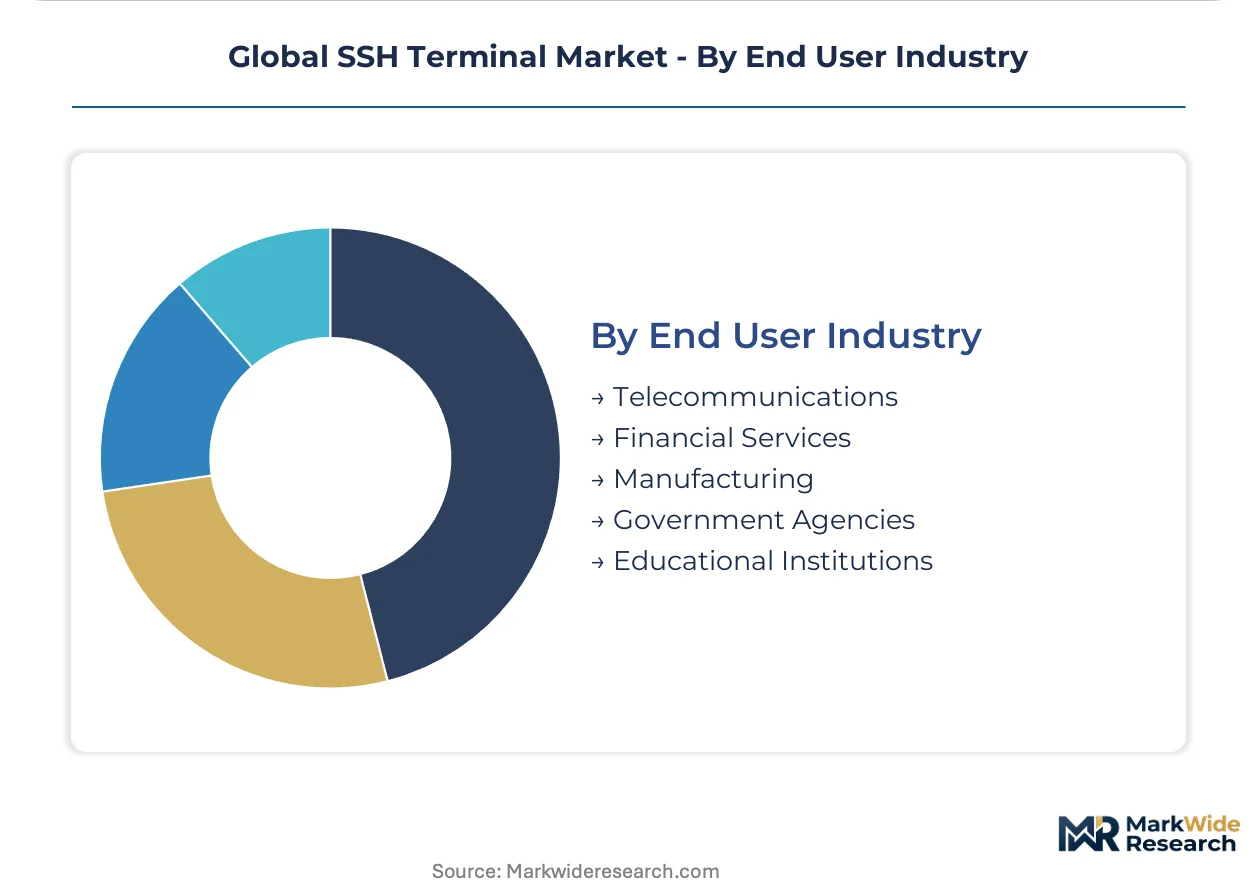
End User Industry:
Regulatory pressure intensity varies sharply across sectors, with critical infrastructure designations accelerating replacement cycles.
- Financial Services:Trading infrastructure, payment processing, and core banking systems requiring sub-millisecond latency with cryptographic assurance. United States and German institutions lead procurement of FIPS-validated terminals for SWIFT and Fedwire connectivity.
- Government Agencies:Classified and unclassified administrative networks subject to NIST controls and national security directives. Federal contractors in the United States face mandatory session recording and multi-factor authentication requirements.
- Telecommunications:Network element management and subscriber data access across distributed infrastructure.
- Manufacturing:Industrial control system access and supply chain integration for smart factory deployments.
- Educational Institutions:Research computing and campus IT administration with limited security staffing.
Financial Services dominates current spending; Government Agencies is expanding most quickly under zero-trust mandates.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Export flows from United States and German vendors dominate the SSH terminal trade balance, while import dependency characterizes emerging data center markets in India and Southeast Asia. Net exporters leverage FIPS validation and EU cybersecurity certifications as non-tariff trade advantages. Importing jurisdictions prioritize cloud-native procurement to bypass domestic capability gaps.
United States
Federal cloud migration and zero-trust architecture mandates drive procurement volume. NIST SP 800-53 controls disqualify non-validated vendors from government contracts. Northern Virginia data center clusters absorb identity-aware proxy solutions at scale.
Germany
Industrial control system hardening in power and manufacturing sectors accelerates terminal replacement cycles. EU NIS2 Directive enforcement from 2024 mandates entity-level security for critical infrastructure operators. Frankfurt and Munich host concentrated demand for hardware security module-integrated key management.
Japan
Financial services institutions modernize legacy mainframe access infrastructure while 5G telecommunications operators expand remote network element management. METI cybersecurity frameworks require encrypted administrative access for critical infrastructure. Tokyo and Osaka financial districts prioritize FIPS-validated terminal emulation.
India
Hyperscaler facility construction in Mumbai and Hyderabad outpaces local security tooling maturity, creating import demand for cloud-native solutions. RBI guidelines for payment system operators mandate encrypted administrative access with audit trails. Domestic vendors struggle to match FIPS 140-2 validation timelines.
United Kingdom
Post-Brexit regulatory divergence creates procurement complexity for vendors serving both UK and EU financial services clients. Financial Conduct Authority operational resilience requirements mandate auditable session recording for trading infrastructure. London's fintech cluster drives consumption-based licensing adoption.
Global SSH Terminal Market Competitive Landscape
Platform integrators command the system tier; component specialists sit upstream in the SSH terminal market structure. The vendor base separates into three functional layers: protocol originators with proprietary extensions, cross-platform terminal emulation specialists, and open-source community maintainers. Consolidation pressure concentrates in the middle tier, where Windows-centric vendors face displacement from cloud-native alternatives. Dominant competitive moves include strategic partnerships with identity providers and geographic expansion through managed service bundles.
Within the protocol originator tier, SSH Communications Security Corp. and VanDyke Software, Inc. exemplify divergent specialization strategies. Bitvise Limited occupies a position bridging deep operating system integration with regulated environment access controls. These three anchors represent distinct competitive archetypes: proprietary protocol leverage, cross-platform federal compliance, and granular policy enforcement.
| Leading Market Players |
|---|
| SecureCRT |
| Bitvise Limited |
| Xshell |
| VanDyke Software, Inc. |
| SSH Communications Security Corp. |
| OpenSSH |
| Poderosa |
| FileZilla |
| MobaXterm |
| Others |
Supply & Pricing Matrix
Trans-Pacific fiber routes between Los Angeles and Tokyo transmit cryptographic validation certificates and FIPS 140-2 documentation, with freight cost volatility amplifying margin compression for United States vendors serving Japanese financial services clients while reinforcing price premiums for hardware security module-integrated solutions.
Pricing Analysis
Industrial OEM buyers anchor three-tier pricing structure across premium, standard, and economy levels. Premium tiers command certification-grade premiums for FIPS 140-2 validated clients with hardware security module integration, while standard tiers compete on Windows-native deployment speed. Cost compression in economy tiers intensifies because OpenSSH community editions satisfy price-sensitive emerging market procurement. Government agencies and federal contractors exhibit least price sensitivity due to NIST mandate compliance requirements.
Supply Chain Analysis
Tariff exposure between United States and China dominates supply chain risk assessment for hardware security module components. Manufacturing concentrates in Taiwan, Germany, and United States for cryptographic processor fabrication. Component sourcing draws from specialized semiconductor foundries, tamper-resistant enclosure fabricators, and entropy source module suppliers. Single-source vulnerability persists for FIPS-validated cryptographic accelerators. Distribution runs through value-added resellers with federal contracting credentials and direct enterprise licensing portals.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Regulatory entrenchment creates durable defensive moats in the SSH terminal market, as FIPS 140-2 validation timelines spanning eighteen to twenty-four months erect structural barriers against fast-follower competition.
For Market Incumbents: Build certification moats through accelerated CMVP pipeline investments and exclusive hardware security module partnerships. Threat from cloud-native identity-aware proxy architectures demands pre-emptive API integration with Okta and Azure Active Directory. Channel control through federal reseller certification programs locks out unqualified competitors from government procurement. For New Entrants and Emerging Players: Establish a beachhead in India's hyperscaler data center buildout where FIPS validation gaps create white space for cloud-native solutions. Consumption-based licensing models penetrate mid-market enterprises with variable infrastructure team sizing. Go-to-market angle centers on rupee-denominated pricing and managed service bundles bypassing domestic certification bottlenecks. For Investors and Strategic Acquirers: Mid-cycle technology positioning favors protocol originators with proprietary extensions over commodity terminal emulation vendors. Long-term viability rests on post-quantum cryptography readiness and algorithm agility investments. Acquisition target archetype: cross-platform specialists with federal contractor installed base but lagging certificate-based authentication capabilities. Signal to watch: NIST post-quantum algorithm standardization announcement triggering compulsory migration investment cycles.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Native embedding with Okta and Azure Active Directory collapses credential provisioning friction for enterprise developers. |
| Geographic Expansion | Managed service bundles with rupee-denominated pricing capture India's hyperscaler facility construction wave. |
| Regulatory Certification Investment | FIPS 140-2 validation unlocks United States federal and German critical infrastructure procurement channels. |
| Strategic Partnership | Hardware security module vendor alliances differentiate key management offerings from commodity OpenSSH deployments. |
| Acquisition of Specialist Firm | Legacy mainframe emulation capabilities address Japanese financial services modernization requirements. |
Research Methodology
Findings reconcile primary fieldwork against secondary review of SEC filings, hyperscaler capex disclosures, NIST validation databases, and EU cybersecurity framework documentation. Interviews with chief information security officers, federal procurement officers, platform engineers, and hardware security module integration specialists inform demand-side validation. Top-down market sizing from infrastructure spend data triangulates against bottom-up vendor revenue aggregation across deployment models and solution types.
Forecast inputs span cloud migration velocity, zero-trust mandate enforcement timelines, and post-quantum cryptography standardization progress. Segmentation models capture deployment architecture, solution certification intensity, end-use industry regulatory exposure, and geographic adoption patterns. CAGRs derive from infrastructure investment trajectories and replacement cycle compression under compliance deadlines.
Sensitivities concentrate around NIST post-quantum algorithm finalization schedules and EU NIS2 Directive enforcement consistency. Forecasts reflect assumptions regarding hyperscaler bastion host retirement timelines and federal cloud migration pace. Material shifts in CMVP certification processing duration or export control restrictions on cryptographic components would require updated calibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
SSL VPN Market
Cybersecurity
Thailand IT and Security Market
Cybersecurity
Wireless Network Security Market
Cybersecurity
Global Virtualization Security Market
Cybersecurity
Global Database Encryption Market
Cybersecurity
North America Cyber Security Market
Cybersecurity
Web Application Firewall Market
Cybersecurity
Data Diode Solution Market
Cybersecurity
Thailand Cybersecurity Market
Cybersecurity
Global Cyber Data Security Market
Cybersecurity
Post-Quantum Cryptography Market
Cybersecurity
Finland Cybersecurity Market
Cybersecurity
ASEAN Cyber Security Market
Cybersecurity
Cloud-Based Email Security Market
Cybersecurity
Europe Cloud DLP Market
Cybersecurity
Indonesia Cybersecurity Market