
 South Korea Cybersecurity Market | 2026-2036
South Korea Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
South Korea Cybersecurity Market Analytics
Single-source dependency on foreign security vendors is decoupling as Korean enterprises diversify procurement. AhnLab anchors domestic endpoint protection with deep localization. SK Shieldus leverages its telecom heritage to dominate managed security services. Samsung SDS extends its IT systems integration strength into cloud security platforms for chaebol affiliates.
South Korea cybersecurity encompasses hardware, software, and services that protect digital infrastructure through threat detection, encryption protocols, and access control mechanisms operating at network perimeters and within cloud-native architectures. Its primary purpose is to ensure continuity of operations for critical systems across finance, government, and telecommunications sectors. Network security retains the largest installed base among solution types, though cloud security captures the fastest expansion as Korean enterprises migrate workloads. Within deployment models, hybrid architectures sustain the steepest growth curve as regulated industries balance data sovereignty requirements with scalability needs.
KISA, the national cybersecurity agency, mandates incident reporting standards that reshape enterprise security budgeting cycles. The Personal Information Protection Commission enforces data localization rules that constrain cross-border cloud deployments. MFDS guidelines for medical device cybersecurity add compliance layers to healthcare procurement. Stakeholders must weigh regulatory fragmentation against the operational efficiency of unified security platforms.
Market Dynamics
Hybrid cloud migration by Korean financial institutions is compressing traditional network security procurement cycles while amplifying demand for integrated cloud-native protection platforms that satisfy KISA incident reporting mandates.
Growth Catalysts
- Personal Information Protection Act amendments:Tighter data localization rules force enterprise cloud architecture redesigns, expanding compliance-driven security spending across banking and healthcare sectors.
- Medical device connectivity:MFDS cybersecurity guidelines for connected healthcare equipment create mandatory procurement layers for hospitals and device manufacturers.
- Zero-trust architecture:Government and defense sector mandates accelerate adoption of identity-centric security models replacing perimeter-based defenses.
Market Restraints
- Foreign vendor dependency:Critical infrastructure operators rely on overseas cloud security platforms, exposing procurement to supply chain disruption and sovereign data access conflicts.
- Specialized talent scarcity:Domestic universities produce insufficient cloud security engineers, inflating personnel costs for managed security service providers.
- Legacy system inertia:Manufacturing and public sector agencies operate decades-old SCADA and mainframe systems resistant to modern endpoint detection integration.
Strategic Opportunities
- Sejong smart city infrastructure:National pilot programs for urban digital twins create demand for integrated IoT security platforms at municipal scale.
- 5G private networks:Industrial manufacturers deploying campus-wide 5G for automation require edge-native security orchestration absent from current product portfolios.
- Security-as-a-service bundling:Telecom operators can capture enterprise accounts by embedding cybersecurity into connectivity contracts, displacing standalone vendor relationships.
Industry Challenges
- Cross-functional security operations:Enterprises struggle to align IT security teams with OT engineering groups in critical manufacturing facilities, delaying unified threat response protocols.
- Certification timeline compression:Rapid regulatory updates from KISA and the Personal Information Protection Commission outpace vendor product certification cycles, freezing procurement decisions.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | South Korea Cybersecurity Market |
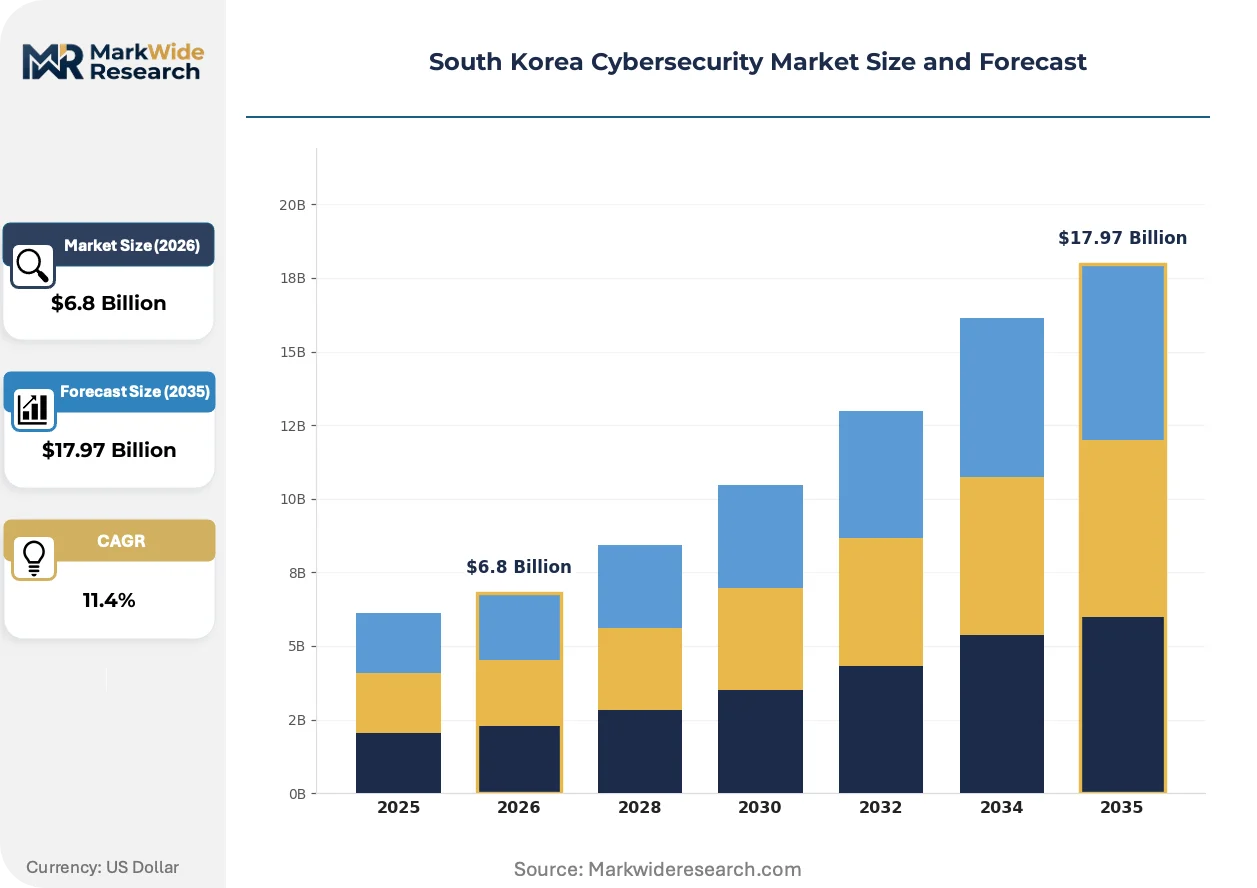
| Market Size in 2026 | $6.8 Billion |
| Market Size in 2035 | $17.97 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Network Security, Application Security, Endpoint Security, Cloud Security Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Security Industry Vertical: BFSI, Healthcare, Telecommunications, Government End User Type: Small Enterprises, Medium Enterprises, Large Enterprises, Public Sector |
| Companies Covered | Palo Alto Networks, Microsoft, AhnLab, Fortinet, Check Point Software Technologies, SK Shieldus, Cisco Systems, CrowdStrike, Samsung SDS, Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
South Korea Cybersecurity Market Evolving Landscape
Artificial intelligence is reshaping threat detection architectures across Korean enterprises, compressing response times while introducing new supply chain dependencies for specialized semiconductor hardware.
Extended detection and response platforms are absorbing the fastest investment concentration among mid-market enterprises. These systems consolidate endpoint, network, and cloud telemetry into unified analyst workflows. Security operations centers at major banks and insurers are absorbing these platforms to reduce mean-time-to-containment below four hours.
KISA's mandatory incident reporting standards are forcing architectural transparency across critical infrastructure operators. The regulation requires automated breach notification within seventy-two hours, compelling security stack interoperability investments. Financial services institutions are absorbing compliance costs by consolidating vendor relationships around platforms with native reporting APIs.
Subscription-based security consumption is displacing perpetual license procurement among Seoul-area enterprises. Chief information security officers prefer operational expenditure models that align costs with headcount fluctuations. This preference is compressing upfront revenue for hardware-centric vendors while expanding recurring revenue pools for cloud-native platform providers.
South Korea Cybersecurity Market Segmentation
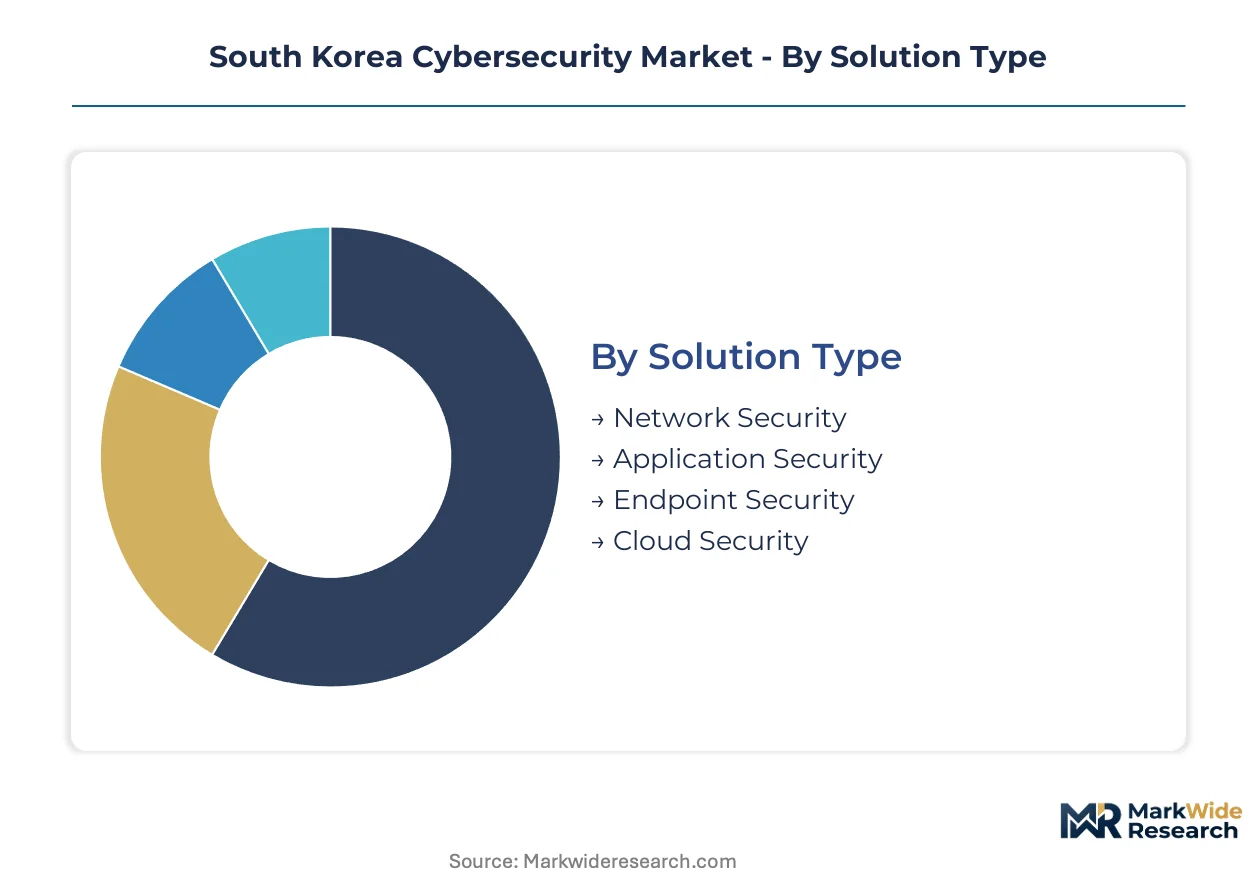
South Korea's cybersecurity procurement patterns diverge sharply across solution architectures and buyer profiles. KISA compliance mandates and chaebol IT modernization cycles create distinct demand clusters that reward specialized positioning over generic platform plays.
Solution Type:
Network security commands the largest installed base while cloud security absorbs the fastest premium pricing, reflecting Korea's hybrid infrastructure transition.
- Network Security:Firewalls, intrusion detection systems, and VPN infrastructure protect perimeter traffic across financial and telecommunications backbones. Demand concentrates among Seoul-based banks modernizing legacy MPLS networks for KISA incident reporting compliance.
- Cloud Security:Native workload protection, container security, and cloud access security brokers secure multi-tenant environments. Korean financial institutions migrating to hybrid architectures drive procurement as PIPA amendments tighten data localization requirements.
- Endpoint Security:EDR platforms and device control agents monitor laptops, servers, and mobile devices for anomalous behavior patterns.
- Application Security:SAST/DAST tools and runtime application self-protection secure software development pipelines for fintech and gaming companies.
Today's leader: Network Security. Tomorrow's challenger: Cloud Security.
Deployment Model:
Cost tiering separates capital-intensive on-premises installations from operational expenditure cloud models, with hybrid architectures capturing mid-market budget flexibility.
- Hybrid:Split workloads across private data centers and public cloud instances with unified policy orchestration. Manufacturing conglomerates and regional banks favor this model to satisfy data sovereignty rules while accessing scalable compute.
- Managed Security:Outsourced SOC operations, threat hunting, and incident response delivered as subscription services. SK Shieldus and telecom-affiliated providers dominate as talent scarcity inflates in-house security team costs.
- Cloud-Based:Fully SaaS-delivered security controls with zero local infrastructure footprint.
- On-Premises:Hardware appliances and perpetual software licenses deployed within customer data centers.
Managed Security claims the steepest expansion trajectory as Korean enterprises confront specialized analyst shortages.
Industry Vertical:
Application maturity varies: BFSI leads security sophistication while healthcare lags due to fragmented provider IT consolidation.
- BFSI:Multi-layered defenses spanning fraud detection, transaction monitoring, and regulatory reporting infrastructure. KB Financial Group and Shinhan Bank drive zero-trust architecture investments following Financial Services Commission guidance.
- Government:Classified network segmentation, critical infrastructure protection, and national cyber defense coordination. KISA mandates reshape procurement cycles for central agencies and municipal operators.
- Telecommunications:5G core network security, subscriber data protection, and edge computing safeguards.
- Healthcare:Medical device cybersecurity, patient record encryption, and telemedicine platform hardening under MFDS guidelines.
BFSI maintains procurement volume leadership. Healthcare represents the fastest-climbing vertical as hospital digitization accelerates.
End User Type:
Customer scale determines solution complexity: large enterprises demand integrated platforms while smaller buyers prioritize managed service simplicity.
- Large Enterprises:Custom security architectures with dedicated SOCs, threat intelligence feeds, and vendor consolidation programs. Samsung affiliates and Hyundai Motor Group operate captive security operations with dedicated engineering teams.
- Public Sector:Standardized procurement through KISA framework contracts with emphasis on domestic vendor preference and audit compliance.
- Medium Enterprises:Pre-configured security bundles with limited customization and shared SOC resources.
- Small Enterprises:Basic endpoint protection and email security through reseller channels.
Large Enterprises anchor current spending. Medium Enterprises gain share fastest as cloud delivery reduces deployment barriers.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Seoul Capital Area concentrates the majority of South Korea's cybersecurity procurement activity, hosting headquarters of major financial institutions and technology conglomerates that drive enterprise security spending. Metropolitan density here accelerates vendor-client relationships and shortens sales cycles for complex security implementations.
Seoul Capital Area
Financial services institutions and chaebol headquarters generate concentrated demand for zero-trust architectures and cloud-native protection platforms. KISA incident reporting mandates reshape procurement cycles for banks and insurers headquartered in Seoul's Yeouido and Gangnam districts. Samsung SDS and SK Shieldus maintain significant operations here, serving affiliated enterprises with integrated security services.
Busan-Ulsan
Port logistics operators and heavy manufacturing conglomerates require industrial control system security and OT-IT convergence solutions. The Korea Internet and Security Agency extends regional compliance enforcement to maritime critical infrastructure operators. Hyundai Heavy Industries and shipping companies in Busan Port drive specialized demand for supply chain cybersecurity and vessel communication protection.
Daejeon-Sejong
Government agencies and research institutes anchor public sector security procurement, with KISA headquarters directly influencing framework contract standards. The Personal Information Protection Commission maintains offices in Sejong, accelerating regulatory interpretation and enforcement timelines. National pilot programs for smart city infrastructure create demand for municipal-scale IoT security platforms.
Daegu-Gyeongbuk
Medical device manufacturers and regional healthcare networks confront MFDS cybersecurity guidelines for connected equipment. Daegu Catholic University Medical Center and affiliated hospitals drive procurement for patient record encryption and telemedicine platform hardening. The region's electronics manufacturing base generates demand for semiconductor supply chain security and intellectual property protection.
Gwangju-Honam
Renewable energy installations and agricultural technology deployments create emerging demand for distributed infrastructure protection. Regional banks and credit unions modernize legacy systems under Financial Services Commission guidance, expanding managed security service consumption. Gwangju Institute of Science and Technology contributes specialized cybersecurity research talent to the domestic labor pool.
South Korea Cybersecurity Market Competitive Landscape
Established producers occupy the standard tier; emerging entrants pursue cloud-native specialization and AI-driven threat detection. The market structures around three distinct maturity levels: global platform vendors with localized operations, domestic champions leveraging regulatory familiarity, and telecom-affiliated service providers capitalizing on infrastructure integration. Strategic archetypes include endpoint protection specialists, managed security service operators, and systems integrators extending into cloud security platforms. Competitive moves concentrate on vendor consolidation programs by large enterprises and subscription-based service bundling by telecom operators.
Within the domestic champion tier, AhnLab anchors endpoint protection with deep localization advantages, while SK Shieldus exemplifies telecom heritage conversion into managed security dominance. Samsung SDS occupies a position extending IT systems integration strength into cloud security platforms for affiliated enterprises. Palo Alto Networks and CrowdStrike represent global platform vendors establishing localized compliance capabilities. The competitive dynamic pits foreign technology depth against domestic regulatory fluency and chaebol relationship networks.
| Leading Market Players |
|---|
| Palo Alto Networks |
| Microsoft |
| AhnLab |
| Fortinet |
| Check Point Software Technologies |
| SK Shieldus |
| Cisco Systems |
| CrowdStrike |
| Samsung SDS |
| Others |
Value Network & Pricing Analysis
KISA's mandatory incident reporting standards gate qualified supply access for foreign security vendors while compressing premium-tier pricing power for domestic champions. Compliance certification timelines reshape procurement negotiations as enterprises prioritize platforms with native reporting APIs over uncertified alternatives.
Pricing Analysis
Input-cost pass-through from specialized semiconductor hardware for AI-driven threat detection is reshaping subscription pricing across cloud-native security platforms. Three-tier pricing structure across premium, standard, and economy levels separates SOC-as-a-service bundles from standalone endpoint agents and basic firewall appliances. Pricing pressure stems from telecom operators embedding security into connectivity contracts, forcing standalone vendors toward bundled service models. Small enterprises exhibit highest price sensitivity, while large financial institutions absorb premium tiers for integrated zero-trust architectures.
Supply Chain Analysis
Domestic-content mandates under KISA framework contracts are reshaping sourcing patterns for critical infrastructure operators. Hardware components draw from Taiwan, the United States, and domestic Korean foundries for specialized security appliances. Software dependencies rest on cloud infrastructure from hyperscalers with Seoul-region data centers. Single-source vulnerability concentrates in foreign-sourced AI training chips for threat detection engines. Distribution runs through systems integrators and telecom-affiliated service providers rather than direct vendor relationships.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
South Korea's cybersecurity market compounds steadily as regulatory compliance mandates perpetually refresh enterprise replacement cycles. KISA's evolving incident reporting standards ensure sustained procurement velocity regardless of macroeconomic conditions.
For Market Incumbents: Lock in chaebol relationships through integrated cloud security platforms that span IT and OT environments. Defend against emerging AI-native entrants by deepening localization advantages in KISA certification pathways. Prioritize managed security service bundling to capture operational expenditure shifts away from perpetual licenses. For New Entrants and Emerging Players: Launch via managed security service partnerships with regional banks outside Seoul Capital Area. White-space targets include 5G private network security for industrial manufacturers and medical device cybersecurity under MFDS guidelines. Penetrate through vertical-specific compliance solutions rather than generic platform plays. For Investors and Strategic Acquirers: Roll-up economics work for specialized cloud security boutiques because KISA certification scarcity creates artificial supply constraints. Long-term viability centers on platforms with native API architectures for automated incident reporting. Target acquisition archetypes include endpoint detection specialists with existing Financial Services Commission relationships. Watch for inflection when MFDS expands cybersecurity guidelines beyond medical devices into hospital IT systems.| Strategic Initiative | Industry Significance |
|---|---|
| Zero-Trust Platform Integration | Consolidates identity-centric security models replacing perimeter defenses across KB Financial Group infrastructure. |
| Managed Security Service Expansion | Captures enterprise accounts through telecom-embedded cybersecurity bundles displacing standalone vendor relationships. |
| AI-Driven Threat Detection Investment | Compresses mean-time-to-containment below four hours for Seoul-based bank security operations centers. |
| Cloud-Native Security Acquisition | Extends IT systems integration strength into hybrid workload protection for Samsung affiliate networks. |
| Regional Bank Partnership Program | Penetrates medium enterprise segment as cloud delivery reduces deployment barriers outside capital area. |
Research Methodology
Direct dialogue with chief information security officers, KISA compliance officers, managed security service providers, and financial services IT procurement leads grounded qualitative findings. Secondary validation drew from KISA incident reporting databases, Financial Services Commission guidance documents, MFDS cybersecurity guidelines, and hyperscaler Seoul-region infrastructure disclosures. Bottom-up segment sizing triangulated against top-down regulatory spending mandates.
Market size and growth trajectory outputs reflect convergent estimation across solution type, deployment model, industry vertical, and end user scale dimensions. CAGRs derive from regression analysis of historical procurement patterns against regulatory compliance cycle timing. Forecast inputs incorporate PIPA amendment implementation timelines, MFDS guideline expansion scope, and 5G private network deployment schedules for industrial automation.
Forecast precision tightens around the base case; tail outcomes carry wider variance under accelerated regulatory update schedules or geopolitical disruption of foreign vendor supply chains. Forecasts reflect documented assumptions regarding compliance cost absorption rates and enterprise cloud migration velocity. Within these boundaries, the analytical envelope holds.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Global Network Security Policy Management Market
Cybersecurity
Italy Cybersecurity Market
Cybersecurity
Global Managed Detection and Response (MDR) Market
Cybersecurity
Israel Cybersecurity Market
Cybersecurity
Cloud Workload Protection Market
Cybersecurity
Web Filtering Market
Cybersecurity
Global File Integrity Monitoring Market
Cybersecurity
Global Cyber Data Security Market
Cybersecurity
Russia Cybersecurity Market
Cybersecurity
India Cybersecurity Market
Cybersecurity
Europe Software Defined Perimeter Market
Cybersecurity
Deception Technology Market
Cybersecurity
ASEAN Cyber Security Market
Cybersecurity
Global Data Exfiltration Market
Cybersecurity
Artificial Intelligence in Cybersecurity Market
Cybersecurity
Global Online Fraud Detection and Prevention Market