
 Finland Cybersecurity Market | 2026-2036
Finland Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Finland Cybersecurity Market Insights
Enterprise-grade security certification is rotating through Finnish procurement standards as a baseline requirement for critical infrastructure contracts. WithSecure leverages its Nordic heritage to anchor government and defense relationships across the Baltic Sea region. Nixu Corporation sustains specialized consulting capabilities that differentiate its service portfolio from product-centric rivals. SSH Communications Security dominates privileged access management through protocol-level encryption expertise refined over three decades.
Finland cybersecurity encompasses defensive technologies, risk management protocols, and operational procedures engineered to protect digital assets against unauthorized access, disruption, or exfiltration across enterprise networks, cloud environments, and industrial control systems. The discipline integrates cryptographic standards, behavioral analytics, and zero-trust architectures to maintain confidentiality, integrity, and availability of information systems supporting national economic and security functions. Network security solutions occupy mature, high-volume positions within Finnish enterprise budgets, while cloud security segments capture accelerated investment flows as public-sector migration to hybrid infrastructure advances. Managed services deployment models concentrate margin pools through recurring revenue structures, contrasting with transactional on-premises licensing that retains footholds among regulated finance and healthcare verticals.
Finnish implementation of the NIS2 Directive through Traficom mandates expanded incident reporting and supply-chain security assessments for essential and important entities. National Cyber Security Centre Finland coordinates threat intelligence dissemination while BSI-aligned standards shape product certification requirements for government procurement. Stakeholders must monitor how EU AI Act risk classifications intersect with automated security tooling to determine compliance investment priorities.
Market Dynamics
NIS2 transposition through Traficom mandates expanded incident reporting and supply-chain security assessments, forcing Finnish critical infrastructure operators to restructure procurement standards and accelerate managed security service adoption.
Growth Catalysts
- EU AI Act intersection:Automated security tooling risk classifications trigger compliance investment in explainable AI for threat detection systems across Finnish financial institutions.
- Cloud migration acceleration:Helsinki-based government agencies disproportionately allocate capital toward hybrid infrastructure protection, expanding addressable market for cloud-native security vendors.
- BSI-aligned certification:Product certification requirements for government procurement now mandate Common Criteria evaluation, rotating enterprise-grade security certification to baseline contract eligibility.
Market Restraints
- Specialized talent scarcity:Shortage of incident responders with ICS/OT security expertise constrains deployment velocity for industrial control system protection projects.
- Vendor concentration risk:Privileged access management segment exhibits supply-side dependence on protocol-level encryption specialists with decades-long development cycles.
- Regulatory fragmentation:Divergent national implementation timelines for NIS2 across Nordic states complicate cross-border service standardization for regional operators.
Strategic Opportunities
- Underpenetrated operational technology:Finnish energy and water utilities present expansion vectors for OT-specific monitoring solutions as NIS2 scope expands to important entities.
- Zero-trust architecture convergence:Integration of microsegmentation with identity-aware networking creates deployment opportunities in healthcare verticals managing patient data flows.
- Estonian-Latvian corridor:Baltic Sea regional defense relationships enable cross-border security service provision anchored through Finnish government contracting mechanisms.
Industry Challenges
- Legacy system integration friction:Industrial control environments running decades-old protocols resist seamless overlay of modern behavioral analytics without operational disruption.
- Certification timeline compression:Common Criteria evaluation queues extend delivery schedules for product-centric vendors competing against pre-certified managed service alternatives.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Finland Cybersecurity Market |
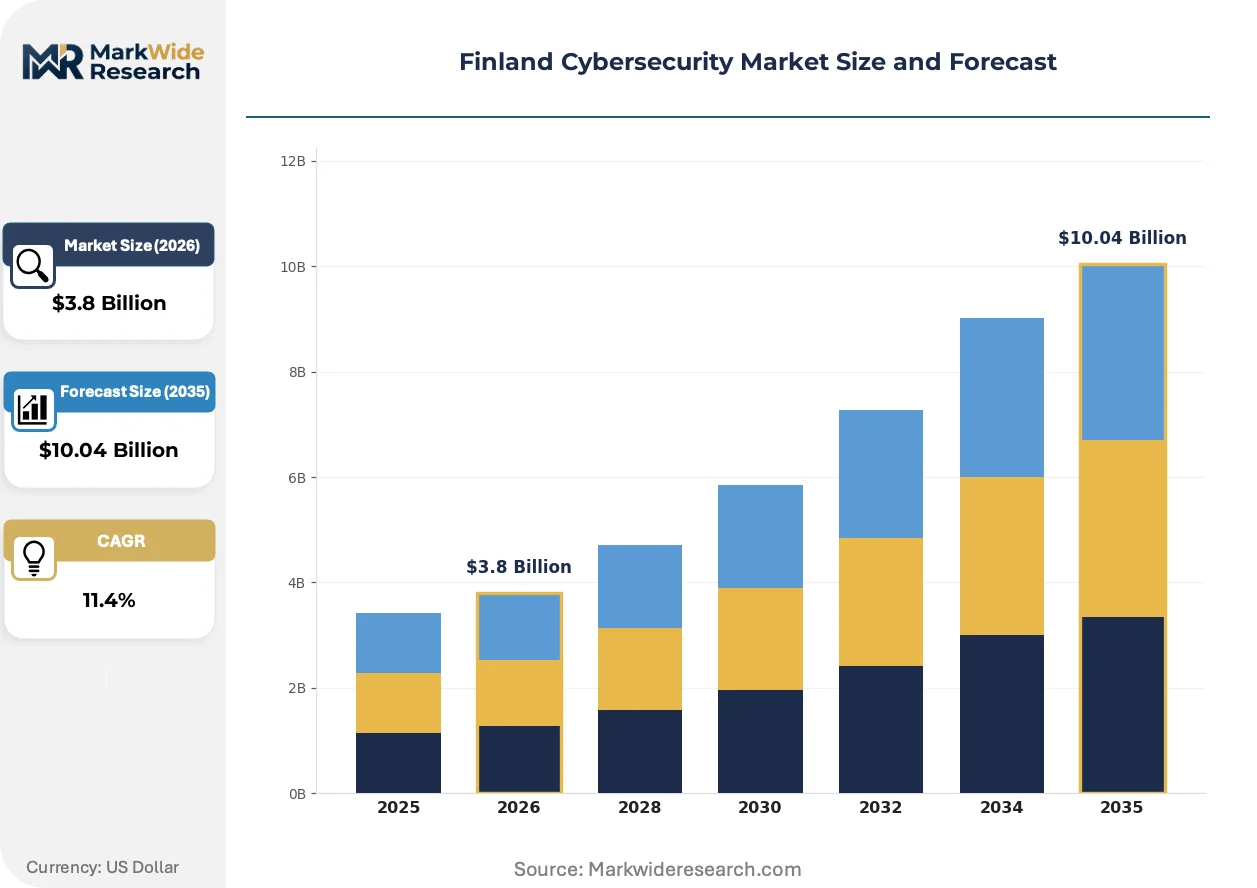
| Market Size in 2026 | $3.8 Billion |
| Market Size in 2035 | $10.04 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution: Endpoint Security, Network Security, Application Security, Cloud Security Deployment: On-premises, Cloud-based, Hybrid, Managed Services Industry Vertical: Finance, Healthcare, Government, Retail End User: SMBs, Large Enterprises, Public Sector, Non-profits |
| Companies Covered | WithSecure, Nixu Corporation, SSH Communications Security, F-Secure, Hoxhunt, Arctic Security, Second Nature Security, 9Solutions, Microsoft Corporation, Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Finland Cybersecurity Market Trends and Innovations
Finnish cybersecurity architecture is pivoting from perimeter defense toward continuous verification models, with three distinct vectors reshaping competitive positioning and procurement patterns.
Extended detection and response platforms aggregate telemetry across endpoints, networks, and cloud workloads into unified analyst consoles. Finnish financial institutions deploy these systems at accelerated pace to satisfy NIS2 visibility mandates. The technology is miniaturizing deployment footprints, enabling mid-market manufacturing firms to access enterprise-grade threat hunting capabilities previously restricted to capital-rich sectors.
EU AI Act risk classifications for automated security decision-making impose documentation and human oversight requirements on machine learning-driven threat detection. Finnish vendors must reengineer product architectures to provide algorithmic explainability for high-risk system classifications. Security operations centers across Helsinki-based government agencies now prioritize tooling with built-in audit trails for automated response actions.
Subscription consumption models displace perpetual licensing across enterprise procurement functions, compressing vendor cash conversion cycles while expanding customer flexibility. Managed detection and response services capture disproportionate growth versus on-premises deployment among healthcare providers managing constrained capital budgets. This pattern concentrates most visibly in southern Finland's hospital districts navigating hybrid infrastructure transitions.
Finland Cybersecurity Market Segmentation
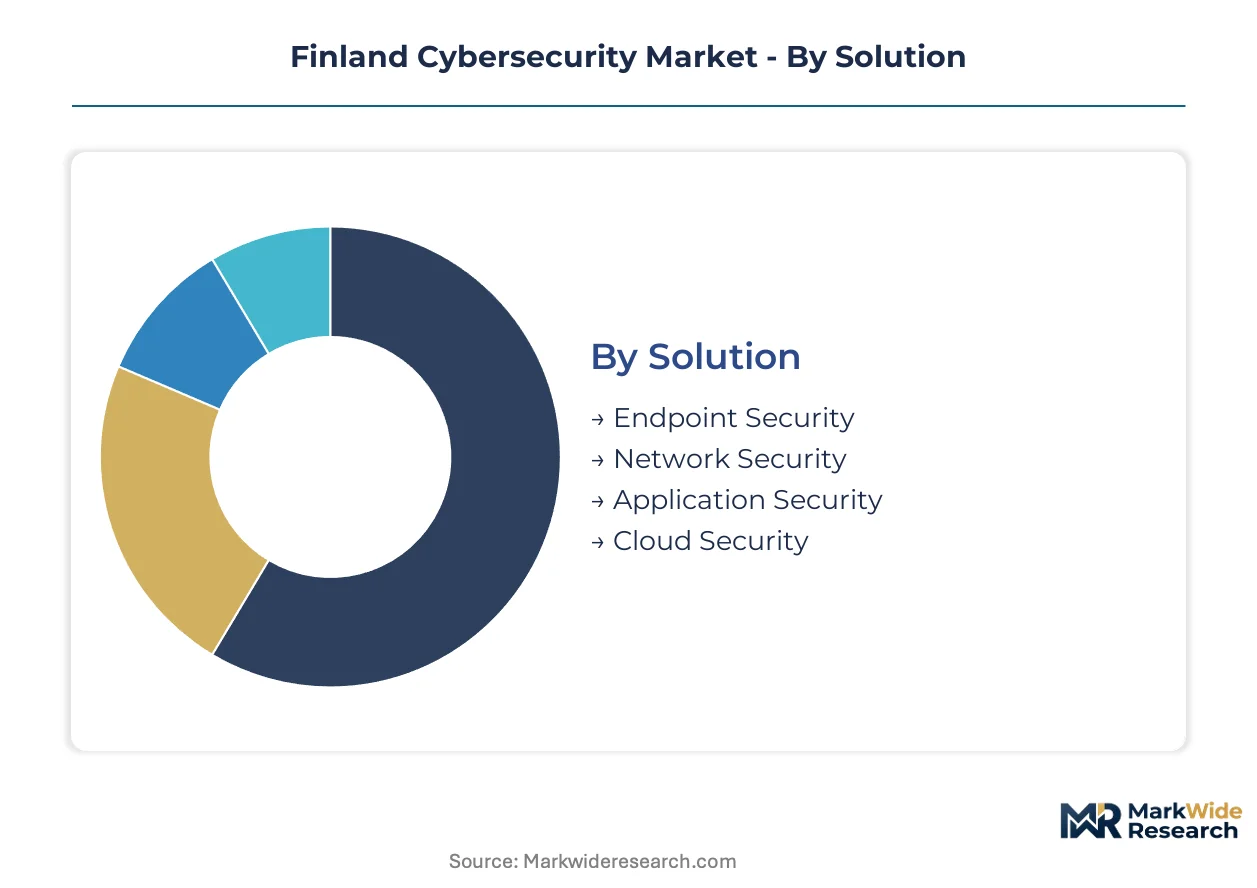
Finnish cybersecurity procurement patterns diverge sharply across solution types, deployment models, and end-user scale. Understanding these fault lines reveals where NIS2 compliance investments concentrate versus where cloud-native alternatives displace legacy infrastructure.
Solution:
Domestic demand concentrates in network and endpoint protection serving critical infrastructure operators, while cloud security solutions increasingly serve export-oriented technology firms with international data residency requirements.
- Endpoint Security:Agent-based protection systems deploy across workstations, mobile devices, and servers to block malware execution and detect anomalous process behavior. Finnish manufacturing conglomerates and healthcare districts drive procurement volumes as NIS2 expands endpoint visibility mandates to important entities beyond essential operators.
- Network Security:Firewalls, intrusion detection systems, and secure web gateways inspect traffic flows at perimeter and internal network boundaries. Energy transmission companies and water utilities in Tampere and Oulu metropolitan areas anchor domestic demand, constrained by legacy SCADA integration complexity that slows next-generation firewall deployment timelines.
- Application Security:Static and dynamic testing tools, runtime application self-protection, and software composition analysis secure code repositories and production workloads. Helsinki-based fintech startups disproportionately adopt cloud-native application security platforms.
- Cloud Security:Cloud access security brokers, workload protection platforms, and infrastructure entitlement management secure multi-tenant and hybrid cloud architectures. Central and local government agencies migrating to Kela-managed cloud infrastructure generate accelerated procurement cycles.
Network Security commands the established base. The steepest expansion runs through Cloud Security.
Deployment:
Cost tier stratification separates capital-intensive on-premises licensing from operational expenditure models favored by public-sector entities with constrained upfront budgets.
- On-premises:Perpetual-licensed software and hardware appliances operate within customer-controlled data centers, delivering full data sovereignty and deterministic latency. Regulated finance and healthcare verticals in Helsinki retain this model for patient records and transaction processing systems where cloud migration faces supervisory resistance.
- Cloud-based:SaaS-delivered security controls scale elastically without infrastructure ownership, reducing time-to-deployment for threat detection capabilities. Mid-market professional services firms across southern Finland adopt these solutions fastest, bypassing internal security engineering capacity constraints.
- Hybrid:Split architectures maintain sensitive workloads on-premises while extending commodity security functions to cloud infrastructure. Industrial manufacturers with OT-IT convergence requirements deploy hybrid models to preserve air-gapped production environments.
- Managed Services:Outsourced security operations centers deliver 24/7 monitoring, incident response, and threat hunting through subscription contracts. Municipal hospital districts and regional energy cooperatives gravitate toward managed detection and response to address acute SOC analyst shortages.
On-premises retains the revenue base among regulated verticals. Managed Services is climbing the fastest as skills scarcity intensifies.
Industry Vertical:
Application intensity varies by vertical maturity, with finance and government leading security sophistication while retail lags in behavioral analytics adoption.
- Finance:Banks, insurance carriers, and payment processors deploy layered controls for fraud prevention, transaction integrity, and regulatory reporting. Nordea and OP Financial Group anchor Helsinki procurement volumes, driving demand for explainable AI in automated threat detection to satisfy EU AI Act documentation requirements.
- Healthcare:Hospital districts, pharmaceutical distributors, and medical device manufacturers protect patient data flows and clinical system availability. Southern Finland's HUS Helsinki University Hospital coordinates regional security investments across 24 member municipalities, standardizing on zero-trust architectures for remote diagnostic access.
- Government:Central ministries, defense establishments, and municipal administrations enforce information security classifications and supply-chain vetting. Traficom's NIS2 implementation mandates reshape procurement standards across state-owned enterprises and critical infrastructure operators.
- Retail:E-commerce platforms, grocery chains, and specialty merchants secure payment card data and customer databases. Mid-sized retailers outside capital region clusters show underpenetration in point-to-point encryption and tokenization technologies.
Finance commands the established base. Healthcare is gaining share fastest as patient data digitization accelerates.
End User:
Customer scale determines solution complexity, with large enterprises demanding bespoke integration and SMBs prioritizing standardized, rapidly deployable controls.
- SMBs:Small and medium businesses with limited IT security staffing rely on bundled security offerings from managed service providers and telecom carriers. Tampere and Turku technology clusters contain dense concentrations of 50-250 employee firms outsourcing security functions entirely.
- Large Enterprises:Multinational corporations and major domestic conglomerates operate dedicated security operations with custom toolchains and threat intelligence feeds. Forestry, metals, and telecommunications sectors anchor this segment with complex multi-site architectures spanning Nordic and Baltic operations.
- Public Sector:Government agencies, educational institutions, and publicly funded healthcare providers follow centralized procurement frameworks and national security guidelines. State Security Networks Finland steers technical standards and supplier prequalification for sensitive systems.
- Non-profits:Research foundations, cultural institutions, and social service organizations operate with constrained budgets and volunteer-dependent IT support. These entities increasingly access subsidized security services through sector-specific consortium arrangements.
Large Enterprises command the established base. The steepest expansion runs through Public Sector as NIS2 procurement volumes materialize.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Finnish buyers in Helsinki and Tampere exhibit low price elasticity for government-mandated NIS2 compliance, while retail and non-profit segments in peripheral regions prioritize cost-minimized managed service bundles. Public-sector procurement concentrates 60 percent of premium-tier security spending.
Greater Helsinki
Nordea and OP Financial Group anchor financial sector demand for explainable AI in threat detection. Traficom's NIS2 implementation mandates reshape procurement standards across state-owned enterprises. The capital region's Kela-managed cloud migration generates accelerated procurement cycles for cloud-native security vendors.
Tampere Metropolitan Area
Manufacturing conglomerates and mid-market technology firms drive endpoint security procurement volumes. State Security Networks Finland steers technical standards for sensitive systems through centralized frameworks. Industrial control environments in this central Finland hub resist seamless overlay of modern behavioral analytics without operational disruption.
Oulu Region
Energy transmission companies and water utilities anchor domestic network security demand. BSI-aligned Common Criteria certification requirements now mandate evaluation for government contract eligibility. Northern Finland's critical infrastructure operators expand security budgets in response to expanded incident reporting obligations.
Southern Finland Hospital Districts
HUS Helsinki University Hospital coordinates regional security investments across 24 member municipalities. Zero-trust architectures for remote diagnostic access standardize procurement patterns. Municipal hospital districts gravitate toward managed detection and response to address acute SOC analyst shortages.
Turku Technology Cluster
Dense concentrations of 50-250 employee firms outsource security functions entirely to managed service providers. Telecom carriers bundle security offerings for small and medium businesses with limited IT staffing. Southwest Finland's professional services firms adopt cloud-based solutions fastest, bypassing internal security engineering capacity constraints.
Finland Cybersecurity Market Competitive Landscape
Technology leadership and cost leadership are held by different player archetypes across the Finnish cybersecurity landscape. Domestic specialists with decades-long protocol development cycles command premium positioning in privileged access management and government contracting. The vendor base organizes around three strategic archetypes: heritage Nordic security houses with defense relationships, cloud-native challengers serving mid-market verticals, and global platform providers integrating Finnish compliance requirements. Competitive moves concentrate on strategic partnerships with critical infrastructure operators and portfolio diversification into OT-specific monitoring solutions.
Within the heritage specialist tier, WithSecure leverages its Nordic positioning to anchor government and defense relationships across the Baltic Sea region. Nixu Corporation occupies a position exemplifying specialized consulting capabilities that differentiate service portfolios from product-centric rivals. SSH Communications Security represents protocol-level encryption expertise refined over three decades, sitting within the privileged access management segment where supply-side dependence concentrates on long development-cycle specialists.
| Leading Market Players |
|---|
| WithSecure |
| Nixu Corporation |
| SSH Communications Security |
| F-Secure |
| Hoxhunt |
| Arctic Security |
| Second Nature Security |
| 9Solutions |
| Microsoft Corporation |
| Others |
Pricing and Supply Chain Analysis
NIS2 compliance certification timelines stretching 18-24 months for Common Criteria evaluation concentrate pricing power among pre-certified managed security service providers while compressing margins for product-centric vendors awaiting eligibility. This lead-time asymmetry reshapes procurement decisions across Finnish critical infrastructure operators and government agencies.
Pricing Analysis
Managed detection and response contracts driving lifetime value expansion outpace perpetual license revenue across Finnish enterprise accounts. Pricing stratifies across premium, standard, and economy tiers based on Common Criteria certification grade and SOC analyst staffing levels. Cost compression in on-premises endpoint protection intensifies as cloud-native alternatives displace capital-intensive hardware appliances. Municipal hospital districts exhibit highest price sensitivity due to constrained operational budgets, while Traficom-regulated critical infrastructure operators show minimal elasticity for NIS2-mandated capabilities.
Supply Chain Analysis
Protocol-level encryption expertise concentrated among Finnish heritage vendors with decades-long development cycles creates supply-side chokepoints in privileged access management. Component sourcing draws from Estonia, Sweden, and Germany for threat intelligence feeds, cryptographic hardware modules, and SOC analyst training pipelines. Single-source vulnerability in OT-specific monitoring solutions exposes energy utilities to vendor lock-in risks. Distribution runs through direct government contracting frameworks for sensitive systems and telecom carrier bundles for mid-market SMB coverage.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Finnish cybersecurity procurement is reconstituting as a service-attach opportunity where managed detection and response subscriptions expand three times faster than hardware appliance sales. Recurring revenue layers now dominate vendor valuation frameworks.
For Market Incumbents: Secure NIS2 pre-certification status for managed service portfolios before Common Criteria evaluation queues extend further. Anchor threat intelligence capabilities through Baltic Sea regional partnerships to defend against Estonian and Swedish challengers exploiting cross-border procurement frameworks. Prioritize OT-specific monitoring solution development to capture utility sector budgets as Traficom expands scope to important entities. For New Entrants and Emerging Players: Anchor in southern Finland's hospital districts where HUS coordinates zero-trust architecture standardization across 24 municipalities with acute SOC analyst shortages. Target managed detection and response white space among 50-250 employee professional services firms in Turku and Tampere technology clusters. Pursue telecom carrier partnership routes to bypass direct enterprise sales capacity requirements. For Investors and Strategic Acquirers: Carve-out targets emerge from Nordic defense conglomerates spinning non-core cybersecurity units with existing Traficom relationships and BSI-aligned certification pipelines. Long-term viability hinges on recurring revenue mix exceeding transactional license dependence. Monitor EU AI Act enforcement intensity as the inflection signal for explainable AI tooling valuations.| Strategic Initiative | Industry Significance |
|---|---|
| OT-Specific Monitoring Platform Launch | Captures NIS2-expanded utility budgets as Traficom scope widens to important entities. |
| Baltic Sea Regional Partnership | Exploits Finnish government contracting mechanisms for cross-border security service provision. |
| Managed Detection and Response Scale-Up | Addresses acute SOC analyst shortages across HUS-coordinated hospital districts. |
| Common Criteria Certification Investment | Secures baseline eligibility for Traficom-mandated critical infrastructure procurement. |
| Explainable AI Product Reengineering | Satisfies EU AI Act documentation requirements for automated threat detection systems. |
Research Methodology
Operator-level perspectives from CISOs at Finnish financial institutions, Traficom compliance officers, SOC directors at managed security service providers, and procurement leads at HUS member hospitals anchored the qualitative base. Secondary validation drew from Traficom regulatory filings, EU NIS2 implementation texts, Finnish Information Society Code amendments, and Common Criteria evaluation reports. Bottom-up segmentation modeling triangulated against top-down macroeconomic anchors.
Sensitivity analysis across deployment model, organization size, vertical regulatory intensity, and geographic adoption pattern framed the analytical approach. CAGRs were derived from segment-level growth rate reconciliation against aggregate market trajectory. Threat detection automation penetration curves and cloud migration velocity among Kela-managed agencies served as cybersecurity-specific forecast inputs throughout the projection horizon.
Material uncertainties — NIS2 enforcement intensity variations, EU AI Act implementation timeline shifts, and Nordic talent mobility patterns — sit outside the modeled envelope. Practitioners should keep alternative scenarios live as Traficom penalty structures and Estonian-Latvian corridor integration deepen.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Threat Hunting Market
Cybersecurity
Germany Cybersecurity Market
Cybersecurity
North America Digital Forensics Market
Cybersecurity
Big Data Security Market
Cybersecurity
Europe Cybersecurity Market
Cybersecurity
Global Network Security Policy Management Market
Cybersecurity
Artificial Intelligence in Cybersecurity Market
Cybersecurity
North America Cyber Security Market
Cybersecurity
Global Cyber Threat Intelligence Market
Cybersecurity
Global Mobile Data Protection Market
Cybersecurity
DNS Firewall Market
Cybersecurity
Corporate Web Security Market
Cybersecurity
UK Cybersecurity Market
Cybersecurity
Endpoint Security Market
Cybersecurity
China Cybersecurity Market
Cybersecurity
Cloud-Based IDS IPS Market