
 Software Repository Market | 2026-2036
Software Repository Market Size, Share, and Industry Trends Forecast 2026-2036
Software Repository Market Insights
Enterprise DevOps teams are reorganizing software repository procurement around supply chain security and compliance automation. GitHub leverages its massive developer network to anchor platform ecosystems. JFrog Ltd. differentiates through binary artifact management that extends across the full software lifecycle. Sonatype Inc. specializes in open-source governance, competing on vulnerability detection depth rather than repository scale alone.
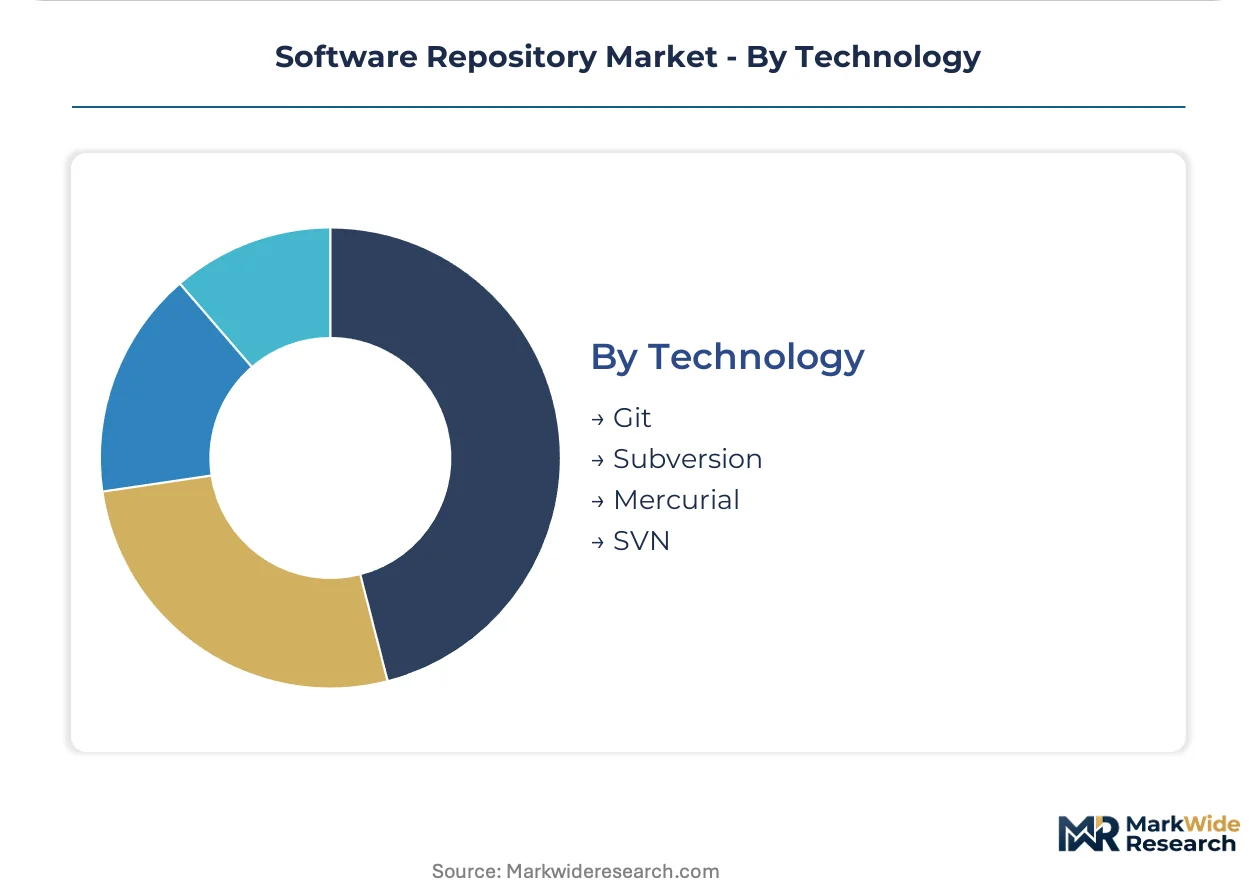
Software repositories are centralized storage systems for code, binaries, and dependencies that enforce version control through cryptographic commit hashes and distributed consensus protocols. Their primary purpose is enabling collaborative development while maintaining immutable audit trails of every code change. Public cloud deployment now leads in new customer acquisition, though hybrid cloud configurations capture the highest-margin enterprise contracts where data residency requirements apply. Dependency management services represent the fastest-growing segment as organizations confront transitive vulnerability exposure in open-source supply chains. Git-based version control dominates technology adoption, while Subversion persists in regulated industries requiring centralized administrative oversight.
FDA software validation guidelines, EU Cybersecurity Act certification requirements, and NIST Secure Software Development Framework standards collectively shape product roadmaps and procurement criteria across the market. These frameworks force repository vendors to embed attestations, SBOM generation, and cryptographic provenance verification as core platform capabilities. Stakeholders must monitor whether emerging sovereign cloud mandates fragment repository interoperability or consolidate platform selection around compliance-certified providers.
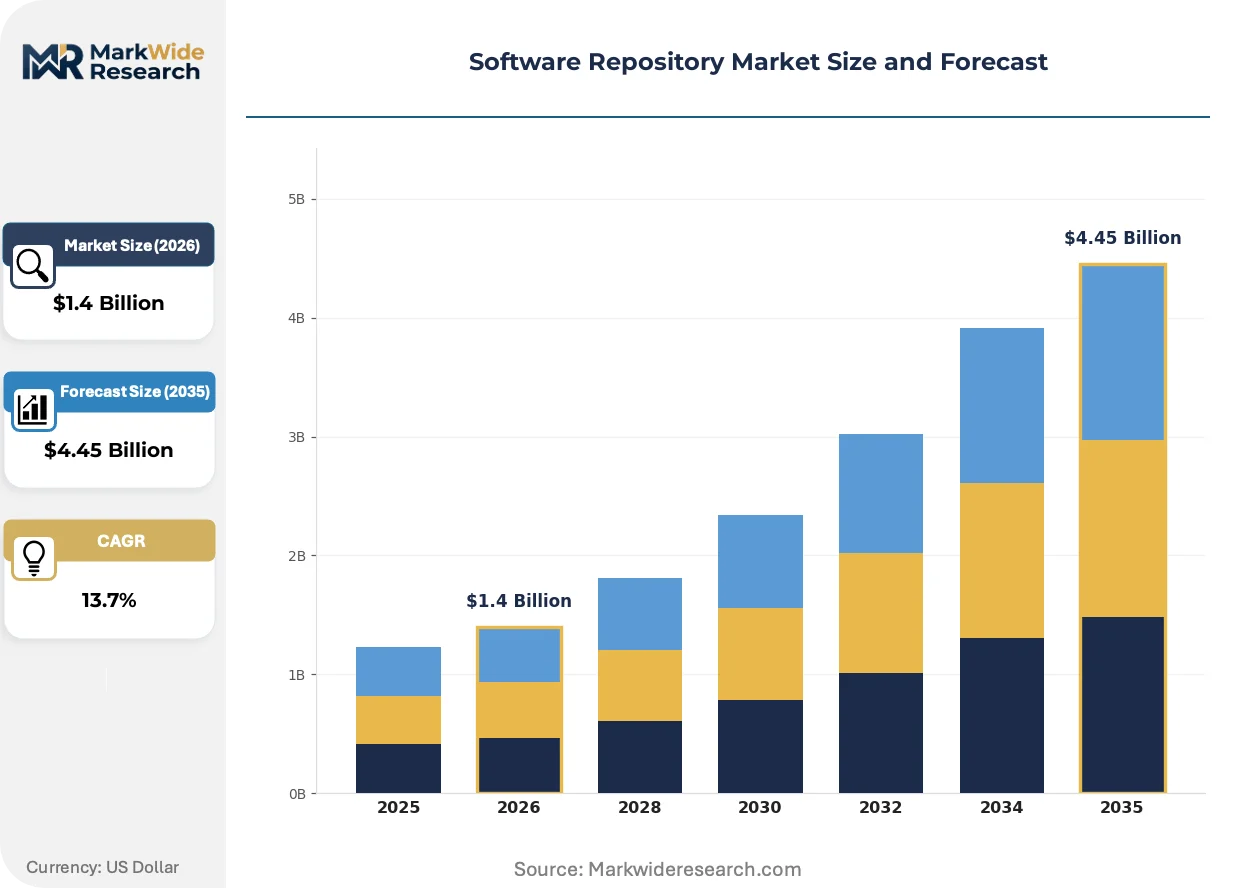
Market Dynamics
Enterprise DevOps procurement is pivoting toward supply chain security attestation as the primary selection criterion, forcing repository vendors to embed cryptographic provenance verification and SBOM generation as core platform capabilities rather than premium add-ons.
Growth Catalysts
- NIST Secure Software Development Framework:US federal procurement mandates now require attestation of secure development practices, creating compulsory upgrade cycles for repository infrastructure across government contractors and their supply chains.
- Transitive dependency vulnerability exposure:High-profile supply chain compromises have elevated automated dependency scanning from optional feature to procurement prerequisite, accelerating replacement of legacy version control systems.
- India's software export sector:Regulatory pressure from EU and US clients on Indian development service providers is driving rapid adoption of compliance-certified repository platforms with embedded governance tooling.
Market Restraints
- Cloud concentration risk:Dominance of hyperscaler-hosted repository services creates single-point-of-failure exposure and limits negotiating leverage for enterprise procurement teams.
- Legacy Subversion technical debt:Regulated industries in Germany and Japan face prohibitive migration costs from centralized version control systems due to embedded compliance workflows and validated tooling chains.
- EU Cybersecurity Act certification delays:Extended timelines for Common Criteria evaluation of repository platforms slow procurement in European financial services and healthcare sectors.
Strategic Opportunities
- Sovereign cloud mandates:Germany's Gaia-X initiative and India's data localization requirements are creating demand for regionally hosted repository instances with full cryptographic isolation from global infrastructure.
- Binary artifact lifecycle management:Extension of repository platforms from source code to container images, firmware binaries, and ML model artifacts opens adjacent revenue pools in IoT and edge computing deployments.
- GitOps operational convergence:Tightening integration between version control and infrastructure-as-code workflows is positioning repository platforms as control planes for entire cloud-native technology stacks.
Industry Challenges
- Attestation engineering talent scarcity:Shortage of professionals capable of implementing cryptographic provenance chains and reproducible build systems limits vendor delivery capacity.
- Legacy mainframe integration complexity:Financial institutions in the United States face years-long projects to bridge modern Git-based workflows with COBOL codebases and proprietary change management systems.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Software Repository Market |
| Market Size in 2026 | $1.4 Billion |
| Market Size in 2035 | $4.45 Billion |
| CAGR (2026 – 2036) | 13.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment Model: Public Cloud, Private Cloud, Hybrid Cloud, On-Premises Service Type: Version Control, CI/CD Integration, Dependency Management, Code Review Target User: Individual Developers, Small Teams, Enterprises, Open Source Projects Technology: Git, Subversion, Mercurial, SVN |
| Companies Covered | JFrog Ltd., Sonatype Inc., GitHub, GitLab Inc., Cloudsmith, Artifactory, Nexus Repository, Synopsys Inc., Snyk Ltd., Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Software Repository Market Trends and Innovations
Repository platform architecture is fragmenting between hyperscale cloud-native services and sovereign-hosted instances, with regulatory jurisdiction replacing technical feature parity as the primary vendor selection axis.
Software Bill of Materials (SBOM) generation is bifurcating repository platform roadmaps. Vendors must now support both SPDX and CycloneDX formats for export to regulatory auditors. Automotive and medical device manufacturers in Germany and the United States are mandating SBOM ingestion at procurement gates. This capability compression is eroding differentiation between specialized supply chain security tools and general-purpose repository platforms.
The EU Cybersecurity Act's certification framework for ICT products is reshaping European procurement criteria. Repository vendors must now complete Common Criteria evaluation or CE marking under delegated acts to access public sector and critical infrastructure contracts. French and German healthcare IT departments are prioritizing pre-certified platforms, compressing sales cycles for compliant vendors while excluding uncertified competitors.
Enterprise sourcing of repository services is consolidating through platform engineering teams rather than decentralized developer choice. Centralized procurement functions in US technology and financial services firms are mandating single-vendor standards to reduce supply chain audit surface area. This buyer concentration is visible most acutely in Fortune 500 enterprises with mature DevSecOps programs, where vendor consolidation clauses now accompany security attestation requirements.
Software Repository Market Segmentation

Repository platform purchasing splits sharply between compliance-heavy enterprise contracts and high-velocity developer self-serve adoption. Vendors must architect pricing and feature tiers that bridge these divergent buying centers without fragmenting their engineering investment.
Deployment Model:
Hybrid cloud deployments command premium pricing through data residency guarantees, while public cloud volumes subsidize platform R&D across all tiers.
- Public Cloud:Fully managed SaaS instances with automatic scaling and zero infrastructure overhead. US technology firms and Indian software exporters drive volume here, prioritizing immediate provisioning over compliance customization.
- Hybrid Cloud:Split architectures keeping sensitive workloads on-premises while leveraging cloud compute for CI/CD pipelines. German automotive manufacturers and US healthcare IT departments pay substantial premiums for this configuration to satisfy FDA validation requirements and EU data sovereignty mandates.
- Private Cloud:Dedicated single-tenant deployments within customer-controlled infrastructure. Financial institutions in Switzerland and defense contractors across NATO member states require this isolation for classified and protected data categories.
- On-Premises:Self-hosted installations with full source code audit rights. Japanese manufacturing conglomerates and legacy German industrial firms maintain these deployments due to embedded compliance workflows dating to Subversion-era tooling chains.
The dominant share belongs to Public Cloud, while Hybrid Cloud is closing the gap fastest as regulatory pressure intensifies across transatlantic supply chains.
Service Type:
Dependency management services now capture disproportionate expansion as transitive vulnerability exposure dominates procurement conversations.
- Dependency Management:Automated scanning and remediation of open-source package vulnerabilities with SBOM generation. Automotive and medical device manufacturers in Germany and the United States mandate this capability at procurement gates, accelerating replacement of standalone security tools.
- Version Control:Distributed source code management with cryptographic commit verification and immutable audit trails. Git-based implementations dominate new customer acquisition, though Subversion persists in regulated Japanese and German industries requiring centralized administrative oversight.
- CI/CD Integration:Native pipeline orchestration connecting repository events to build, test, and deployment automation. This capability is consolidating into core platform offerings rather than remaining a third-party extension market.
- Code Review:Structured collaboration workflows with mandatory approval gates and compliance attestation logging. Enterprise DevSecOps teams in US financial services treat this as non-negotiable infrastructure for SOX and SEC audit trails.
Version Control retains the largest installed base, though Dependency Management is expanding most quickly as supply chain security attestation becomes compulsory.
Target User:
Enterprise procurement concentrates vendor revenue while individual developer adoption determines platform ecosystem vitality and long-term retention economics.
- Enterprises:Centralized purchasing with mandatory security attestation, SBOM export requirements, and vendor consolidation clauses. Fortune 500 technology and financial services firms in the United States now mandate single-vendor standards across development organizations exceeding ten thousand engineers.
- Individual Developers:Free-tier or low-cost personal subscriptions driving platform familiarity and future enterprise conversion. This segment anchors GitHub's network effects through public repository visibility and social coding features.
- Small Teams:Growth-stage startups and departmental units with limited procurement bureaucracy but increasing compliance pressure from enterprise customers. Indian software service providers in this tier are rapidly upgrading to compliance-certified platforms under client contractual obligations.
- Open Source Projects:Foundation-hosted and community-maintained codebases with specific governance and contribution licensing requirements. These projects function as marketing infrastructure and talent pipeline for commercial platform vendors.
Enterprises generate the dominant revenue share, while Small Teams are climbing the fastest as regulatory pressure cascades down supply chain tiers.
Technology:
Technology choice now correlates more strongly with regulatory jurisdiction and migration cost tolerance than with functional capability differentiation.
- Git:Distributed version control with cryptographic content-addressable storage and branch-based workflow flexibility. This technology anchors virtually all new platform development and cloud-native tooling ecosystems.
- Subversion:Centralized version control with path-based access control and linear revision numbering. German pharmaceutical manufacturers and Japanese automotive suppliers maintain these systems due to validated tooling chains and FDA submission history.
- Mercurial:Distributed alternative with simpler command structure and extensible Python-based architecture. Niche adoption persists in specific scientific computing and academic research communities.
- SVN:Abbreviated reference to Subversion systems in legacy documentation and procurement systems, functionally identical to the Subversion segment above.
Git holds overwhelming dominance in new deployments, though Subversion maintains defensive positions in regulated industries where migration costs exceed platform licensing savings.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Enterprise procurement teams in the United States, Germany, and India are driving platform investment decisions, with regulatory pressure on software provenance and open-source governance reshaping vendor selection criteria across these three demand centers.
United States
Federal contractors and Fortune 500 technology firms are mandating NIST Secure Software Development Framework compliance for repository infrastructure. FDA software validation guidelines force medical device manufacturers to maintain immutable audit trails. The San Francisco Bay Area and Seattle technology corridors anchor domestic platform R&D and early-adopter deployment.
Germany
Automotive OEMs and pharmaceutical manufacturers are prioritizing EU Cybersecurity Act certification for repository platforms accessing public sector contracts. Gaia-X sovereign cloud initiatives are creating demand for regionally hosted instances with cryptographic isolation. Munich and Stuttgart industrial clusters are upgrading validated tooling chains from legacy Subversion systems.
India
Software export service providers face contractual pressure from EU and US clients to adopt compliance-certified platforms with embedded governance tooling. Data localization requirements under RBI and SEBI guidelines are accelerating private cloud and sovereign-hosted deployments. Bangalore and Hyderabad technology hubs are consolidating vendor standards across development organizations exceeding five thousand engineers.
Japan
Automotive suppliers and financial institutions maintain centralized version control systems due to embedded compliance workflows and METI-validated tooling chains. Migration costs from Subversion-era infrastructure exceed platform licensing savings for regulated manufacturers. Tokyo and Nagoya industrial corridors represent defensive positions for legacy repository architectures.
United Kingdom
Financial services firms in London are mandating single-vendor repository standards to reduce supply chain audit surface area under FCA operational resilience requirements. GitOps operational convergence is positioning repository platforms as control planes for cloud-native technology stacks. The London-Southeast corridor concentrates enterprise procurement decision-making for European headquarters operations.
Software Repository Market Competitive Landscape
Player mix skews toward platform-integrated specialists with supply chain security depth. Consolidation pressure is intensifying as enterprise procurement teams mandate single-vendor standards across development organizations. Three strategic archetypes dominate: hyperscale cloud-native platforms, binary artifact lifecycle specialists, and open-source governance purists. Competitive moves center on embedding cryptographic provenance verification as core capability and extending repository scope from source code to container images and ML model artifacts.
Within the platform-integrated tier, GitHub and GitLab Inc. exemplify developer-network effects and DevSecOps convergence strategies respectively. JFrog Ltd. occupies a distinct position as a binary artifact management specialist extending across full software lifecycles. Sonatype Inc. represents the governance-purist archetype, competing on vulnerability detection depth rather than repository scale alone.
| Leading Market Players |
|---|
| JFrog Ltd. |
| Sonatype Inc. |
| GitHub |
| GitLab Inc. |
| Cloudsmith |
| Artifactory |
| Nexus Repository |
| Synopsys Inc. |
| Snyk Ltd. |
| Others |
Pricing and Supply Chain Analysis
Hyperscale cloud infrastructure utilization rates above eighty percent compress marginal hosting costs for repository platform vendors, concentrating supply-side power among AWS, Azure, and Google Cloud while anchoring SaaS price floors at levels that exclude smaller regional competitors from profitable participation.
Pricing Analysis
Cost-plus contracts with hyperscaler indexation dominate enterprise repository procurement, with annual escalators tied to compute and storage commodity benchmarks. Pricing stratifies across premium compliance-certified tiers, standard multi-tenant SaaS, and economy self-hosted licenses, with differentiation driven by FedRAMP authorization depth and EU Cybersecurity Act pre-certification status. Cost compression in the standard tier is intensifying because Indian software exporters are consolidating vendor standards under client contractual pressure. Individual developers and small teams exhibit highest price sensitivity, while Fortune 500 financial services firms prioritize attestation depth over per-seat licensing costs.
Supply Chain Analysis
Port congestion at Shanghai and Rotterdam has elevated inbound logistics costs for on-premises appliance deliveries to German automotive manufacturers and Japanese pharmaceutical firms. Supply concentrates in the United States for hyperscale cloud infrastructure, Germany for sovereign-hosted Gaia-X compliant instances, and India for development service provider tooling. Raw material dependencies include cryptographic hardware security modules, specialized SSD storage arrays, and high-bandwidth network equipment. Single-source vulnerability runs through Intel and AMD processor supply for validated server configurations. Distribution runs through direct enterprise sales teams for contracts exceeding ten thousand seats, with channel partners handling mid-market penetration.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The software repository market is experiencing high-growth disruption as NIST Secure Software Development Framework mandates transform procurement from developer preference to centralized compliance infrastructure.
For Market Incumbents: Compound platform stickiness by embedding SBOM generation and cryptographic attestation as core capabilities rather than premium modules, neutralizing Sonatype's governance-purist positioning. Defend against GitLab's DevSecOps convergence threat by accelerating binary artifact lifecycle extensions into container images and ML model repositories. Priority lever rests on FedRAMP and EU Cybersecurity Act certification maintenance to preserve public sector access. For New Entrants and Emerging Players: EU Cybersecurity Act fast-track certification creates immediate procurement eligibility for French and German healthcare IT departments currently excluded from uncertified platforms. Target sovereign cloud mandates in Germany's Gaia-X initiative and India's data localization requirements as the most penetrable white-space, where global hyperscaler infrastructure faces regulatory displacement. Go-to-market angle centers on pre-certified regional instances with cryptographic isolation guarantees. For Investors and Strategic Acquirers: Recurring-revenue conversion is highest among binary artifact management specialists with multi-year enterprise contracts and embedded compliance workflows. Long-term viability favors vendors with demonstrated FedRAMP authorization history and proven migration tooling from legacy Subversion systems. Acquisition target archetype: mid-tier compliance-certified platforms with established German automotive or US healthcare customer bases. Signal to watch is consolidation clause penetration in Fortune 500 procurement templates as indicator of vendor concentration inflection.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Embedding SBOM generation and attestation tooling consolidates DevSecOps spend into single-vendor relationships. |
| Geographic Expansion | Sovereign cloud instances in Germany and India satisfy Gaia-X and RBI data localization mandates. |
| Acquisition of Specialist Firm | Binary artifact lifecycle capabilities extend repository scope beyond source code to container images. |
| Strategic Partnership | FedRAMP authorization sponsorship accelerates public sector procurement eligibility for emerging platforms. |
| Product Launch | ML model artifact repositories capture adjacent revenue in edge computing and IoT firmware deployments. |
Research Methodology
A standing panel of DevOps platform engineers, enterprise IT procurement officers, compliance auditors, and channel integration specialists provided ongoing calibration across the research cycle. Primary interviews with CTOs at Fortune 500 technology and financial services firms, alongside platform engineering leads at Indian software exporters, were triangulated against secondary validation from SEC filings, hyperscaler capex disclosures, EU Cybersecurity Act certification databases, and NIST guidance documents. Bottom-up deployment model sizing was cross-checked against top-down enterprise software spend analysis.
Consistency checks validated volume and value outputs against external benchmarks including hyperscaler revenue disclosures and compliance certification timelines. The analytical framework modeled deployment model, organization size, vertical industry, integration complexity, and regional adoption pattern across the projection horizon. CAGRs were derived from segmented growth rate analysis weighted by procurement pipeline visibility. Industry-specific forecast inputs included NIST SSDF mandate implementation timelines and EU Cybersecurity Act delegated act publication schedules.
Underlying assumptions cover sustained regulatory pressure on software provenance, stable hyperscaler infrastructure pricing, and gradual Subversion-to-Git migration velocity, with deviation risk concentrated in sovereign cloud mandate fragmentation and attestation engineering talent scarcity. Outcomes outside this envelope would require model recalibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Software & Services
AI Sales Assistant Software Market
Software & Services
Mobile Speech Recognition Software Market
Software & Services
Global Printing Software Market
Software & Services
Shift Planning Software Market
Software & Services
Global Offshore Software Development Market
Software & Services
Petcare Software Market
Software & Services
Equipment Management Software Market
Software & Services
Test Management Software Market
Software & Services
Legal Practice Management Software Market
Software & Services
Multivariate Testing Software Market
Software & Services
Global Affiliate Software Market
Software & Services
Resonator Design Software Market
Software & Services
Global Webinar Software Market
Software & Services
Emotion Recognition and Sentiment Analysis Software Market
Software & Services
Creative Software Market
Software & Services
Global Embedded Hypervisor Software Market