
 Portable Storage Device Control Software Market | 2026-2036
Portable Storage Device Control Software Market Size, Share, and Industry Trends Forecast 2026-2036
Portable Storage Device Control Software Market Analytics
Modular bundling of encryption with access management and remote wipe capabilities is rebalancing procurement patterns toward integrated suites rather than point solutions. ManageEngine Device Control Plus leverages its channel density across Asia-Pacific to sustain enterprise uptake. Trellix Endpoint DLP anchors its positioning through native integration with broader endpoint security stacks. Symantec Endpoint DLP dominates brand recognition in regulated verticals where compliance mandates drive purchasing authority.
Portable storage device control software governs the connection, authorization, encryption, and data flow of USB drives, external disks, and removable media through policy enforcement agents installed on endpoint operating systems. The software intercepts device insertion events, applies granular read-write-execute permissions, and logs file transfer activity for forensic audit trails. Encryption software and access management tools together capture the deepest margin pools, as buyers prioritize cryptographic key lifecycle management over passive monitoring. Cloud-based deployment is expanding fastest among mid-market enterprises seeking reduced on-premises infrastructure burden, though on-premises retains preference in defense and classified government environments where air-gapped networks remain mandatory.
FDA 21 CFR Part 11 requirements for electronic records in healthcare, HIPAA Security Rule provisions for endpoint access controls, and GDPR Article 32 mandates for personal data processing security collectively shape product certification requirements and buyer due diligence checklists. ISO 27001 alignment has become a baseline procurement filter, with auditors verifying removable media controls during certification surveillance visits. Stakeholders must monitor the divergence between cloud-native policy orchestration and legacy agent architectures as organizations hybridize their endpoint fleets.
Market Dynamics
GDPR enforcement and HIPAA audit frequency are compressing procurement cycles as healthcare and financial services buyers demand pre-certified endpoint control suites rather than building compliance stacks internally.
Growth Catalysts
- HIPAA Security Rule audits:US healthcare providers accelerate endpoint control deployments to satisfy OCR enforcement timelines and avoid penalty tiers.
- USB-C universal connectivity:Standardized physical interfaces simplify agent-based policy enforcement across heterogeneous device fleets.
- Patient data mobility:German and UK hospital networks expand removable media governance to secure diagnostic image transfers between facilities.
Market Restraints
- Agent compatibility overhead:Legacy Windows 7/8 endpoints in industrial manufacturing require separate policy engine builds, fragmenting R&D resources.
- Cloud dependency skepticism:Defense contractors and classified government facilities in the United States mandate air-gapped networks, excluding SaaS-native vendors.
- Encryption key escrow complexity:Multi-jurisdictional data residency rules force redundant key management infrastructure, elevating total cost of ownership.
Strategic Opportunities
- Zero Trust architecture mandates:US federal agencies under OMB guidance require continuous device verification, opening replacement cycles for passive monitoring tools.
- Medical device OEM integration:Embedded policy agents in diagnostic equipment address FDA 21 CFR Part 11 audit requirements at the point of manufacture.
- Managed security service providers:Mid-market enterprises in the United Kingdom outsource policy orchestration to MSSPs, creating recurring revenue attach rates.
Industry Challenges
- Firmware-level bypass techniques:Advanced persistent threat actors exploit USB controller vulnerabilities that sit below operating-system agents, requiring hardware-rooted trust implementations.
- Cross-platform policy consistency:macOS and Linux endpoint growth in creative and engineering verticals forces vendors to replicate Windows-native feature parity.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Portable Storage Device Control Software Market |
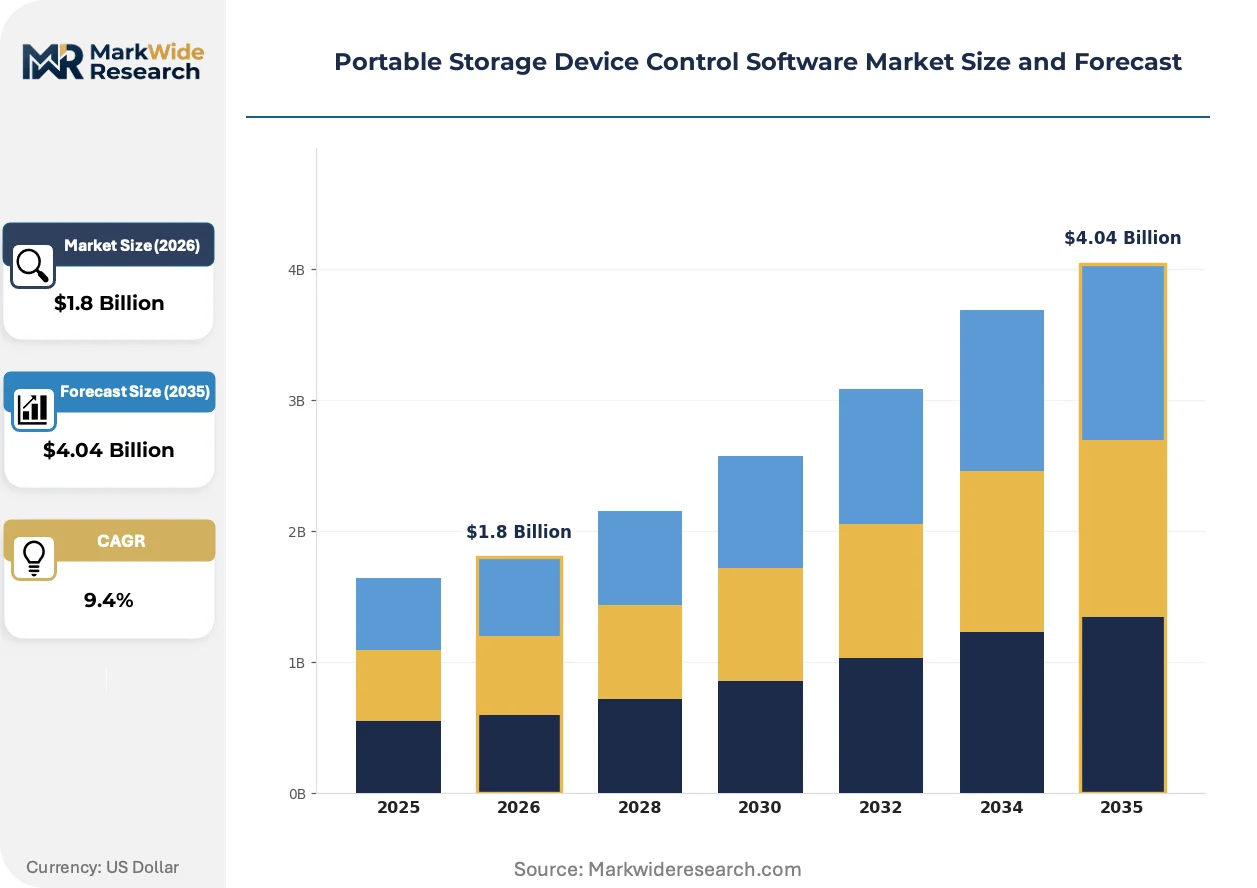
| Market Size in 2026 | $1.8 Billion |
| Market Size in 2035 | $4.04 Billion |
| CAGR (2026 – 2036) | 9.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
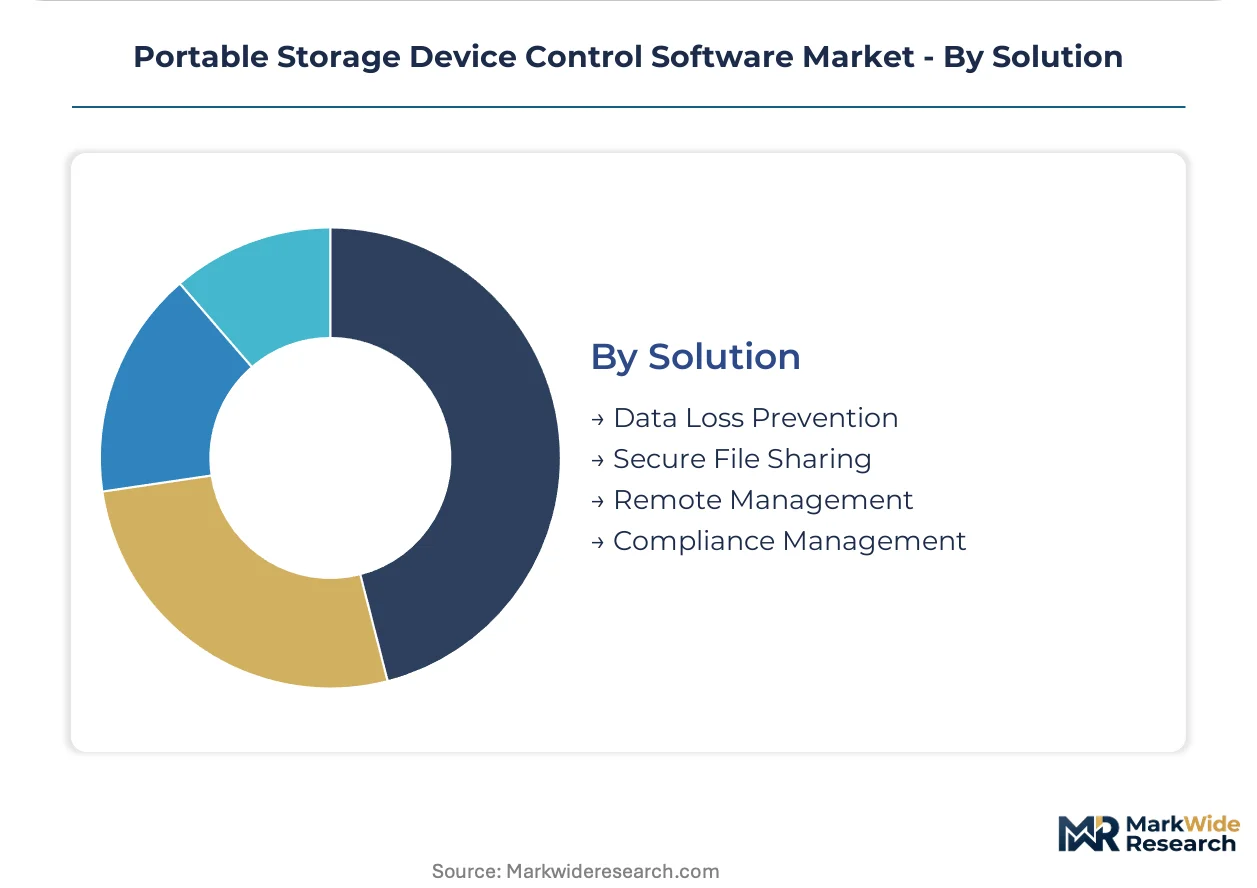
| Segmentation | Product Type: Encryption Software, Backup Solutions, Access Management Tools, Monitoring Systems Deployment: On-Premises, Cloud-Based, Hybrid, Local Network End User: Enterprises, Government Agencies, Educational Institutions, Healthcare Providers Solution: Data Loss Prevention, Secure File Sharing, Remote Management, Compliance Management |
| Companies Covered | Netwrix Endpoint Protector, ManageEngine Device Control Plus, DeviceLock, SafeticaONE, Trellix Endpoint DLP, Symantec Endpoint DLP, DriveLock, AccessPatrol, GFI EndPointSecurity, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Portable Storage Device Control Software Market Evolving Landscape
Endpoint security architecture is converging data loss prevention, encryption, and access governance into unified control planes, collapsing the procurement distinction between adjacent software categories.
Cloud-native policy orchestration is modularizing deployment topologies for portable storage control software. Healthcare IT departments in Germany adopt containerized agents that separate policy logic from endpoint footprint. This modularity compresses upgrade cycles and enables feature toggling without full redeployment.
GDPR Article 32 enforcement is mandating cryptographic key lifecycle management as a baseline procurement filter. European data protection authorities audit removable media controls during certification surveillance, forcing vendors to document key escrow procedures. Financial services buyers in the United Kingdom now require ISO 27001 alignment as a table-stakes qualification.
Subscription pricing models are displacing perpetual licenses across mid-market accounts. Managed service providers in the United States bundle endpoint control with broader security operations center offerings. Healthcare networks prefer consumption-based billing that scales with device fleet volatility rather than upfront capital commitment.
Portable Storage Device Control Software Market Segmentation
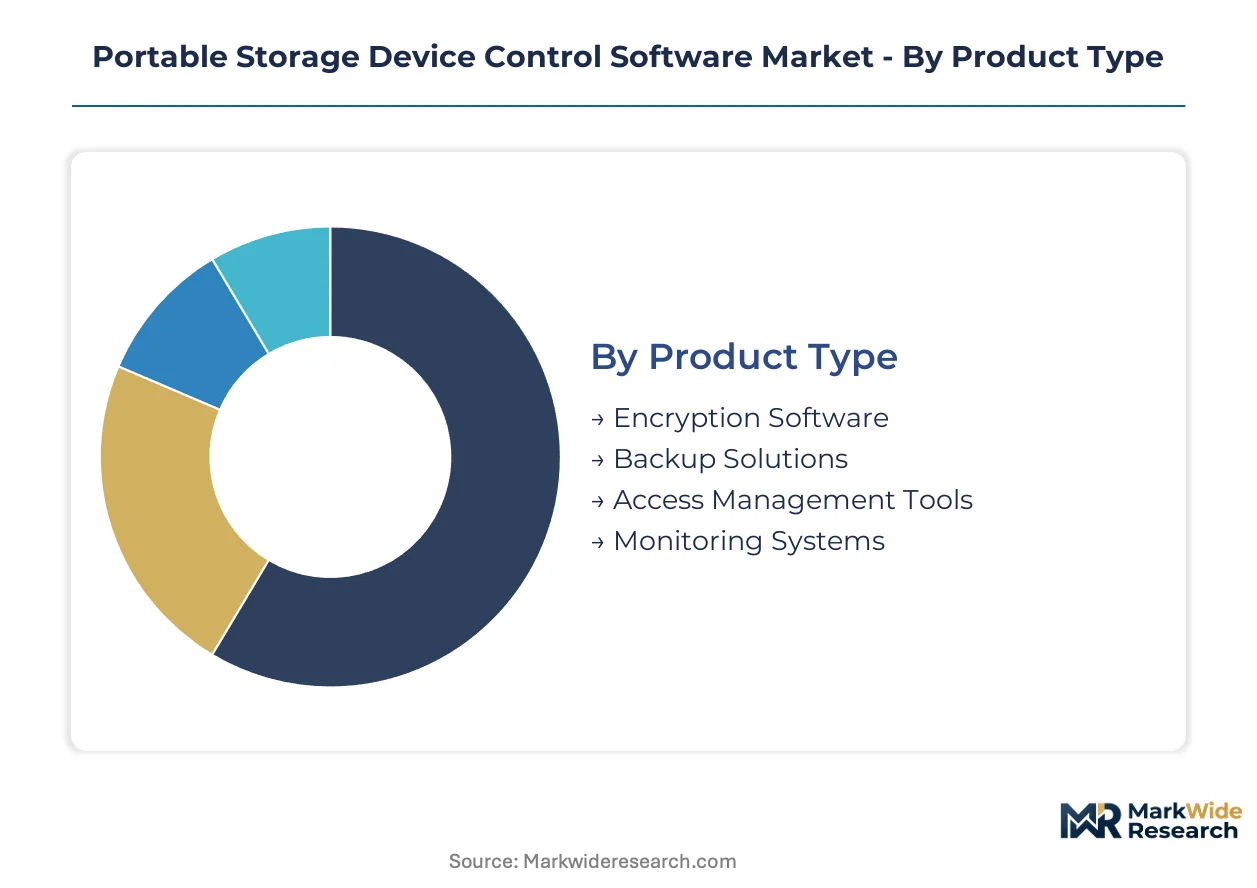
Segmentation reveals how procurement priorities diverge across deployment architectures and compliance mandates. Buyers in regulated verticals prioritize integrated suites over point solutions, while mid-market accounts favor consumption-based cloud models. Understanding these fault lines clarifies where vendors must anchor R&D investment versus channel partnerships.
Product Type:
Upgrade cycles accelerate where legacy encryption meets modern key lifecycle requirements, forcing replacement of certificate-based systems with hardware security module integration.
- Encryption Software:Cryptographic engines now embed AES-256 with FIPS 140-2 validation as baseline. German automotive suppliers and UK financial services firms drive demand for key escrow capabilities that satisfy GDPR Article 32 audit requirements.
- Access Management Tools:Policy engines enforce granular read-write-execute permissions at the USB controller level. United States healthcare networks under OCR enforcement timelines prioritize these tools over passive monitoring to demonstrate HIPAA Security Rule compliance.
- Backup Solutions:Removable media backup with immutable snapshots serves air-gapped defense facilities in the United States.
- Monitoring Systems:Forensic logging agents capture file transfer telemetry for ISO 27001 certification audits.
Volume placements concentrate in Encryption Software; the faster expansion belongs to Access Management Tools.
Deployment:
Cost tier stratification separates capital-intensive on-premises builds from operational expenditure models favored by budget-constrained mid-market buyers.
- Cloud-Based:Containerized policy orchestration eliminates endpoint agent bloat through microservice architectures. United Kingdom NHS trusts and German hospital networks adopt these deployments to reduce infrastructure overhead while maintaining GDPR-compliant audit trails.
- On-Premises:Air-gapped policy servers serve classified government facilities and defense contractors where network isolation is mandatory. United States Department of Defense sites require hardware-rooted trust implementations that SaaS architectures cannot satisfy.
- Hybrid:Split architectures route sensitive operations to local policy engines while offloading analytics to cloud substrates.
- Local Network:Segment-isolated deployments persist in industrial manufacturing where legacy Windows 7 endpoints resist cloud agent compatibility.
Cloud-Based deployments gain share fastest in commercial accounts; On-Premises retains dominance in classified and critical infrastructure environments.
End User:
Application-specific compliance deadlines compress procurement timelines differently across verticals, with healthcare and government facing the most rigid enforcement windows.
- Healthcare Providers:Patient data mobility requirements drive removable media governance for diagnostic image transfers between facilities. FDA 21 CFR Part 11 requirements for electronic records mandate embedded policy agents at the point of diagnostic equipment manufacture.
- Government Agencies:Zero Trust architecture mandates under United States OMB guidance require continuous device verification, opening replacement cycles for passive monitoring tools. Federal procurement now prioritizes FIPS-validated encryption with hardware security module integration.
- Enterprises:Mid-market manufacturing and professional services accounts outsource policy orchestration to managed security service providers.
- Educational Institutions:Research universities balance open data sharing norms against export control restrictions on sensitive technical data.
Healthcare Providers anchor near-term volume; Government Agencies represent the steepest expansion trajectory as Zero Trust mandates propagate through federal procurement.
Solution:
Margin concentration follows integration depth, with unified platforms capturing premium pricing over standalone modules.
- Data Loss Prevention:Unified control planes now collapse the distinction between endpoint DLP and removable media encryption, enabling single-pane policy orchestration across heterogeneous device fleets. United States financial services buyers under SEC cybersecurity guidance prioritize these integrated stacks.
- Compliance Management:Pre-certified suites with documented ISO 27001 alignment and GDPR Article 32 key escrow procedures command procurement preference in European regulated verticals. United Kingdom auditors verify removable media controls during certification surveillance visits.
- Secure File Sharing:Encrypted collaboration portals replace ungoverned consumer file sync services in enterprise accounts.
- Remote Management:Over-the-air policy updates serve distributed workforces and field service organizations.
Data Loss Prevention dominates current procurement volume; Compliance Management is climbing the fastest as certification requirements harden across European and North American regulated sectors.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Software development concentrates in the United States and Germany while deployment demand spreads across healthcare networks in the United Kingdom and government facilities in multiple jurisdictions. Consumption patterns diverge between cloud-ready commercial accounts and air-gapped classified environments.
United States
Defense contractors and healthcare systems drive procurement volume. HIPAA Security Rule enforcement by OCR compresses deployment timelines for endpoint control suites. Federal Zero Trust mandates under OMB guidance accelerate replacement cycles across civilian agencies and the Department of Defense.
Germany
Automotive suppliers and hospital networks prioritize GDPR-compliant key escrow capabilities. German data protection authorities audit removable media controls during certification surveillance. Munich and Stuttgart industrial clusters embed policy agents in diagnostic equipment manufacturing workflows.
United Kingdom
NHS trusts adopt containerized cloud deployments to reduce infrastructure overhead. ISO 27001 alignment serves as a baseline procurement filter across financial services in the City of London. Mid-market enterprises outsource policy orchestration to managed security service providers in Greater Manchester and Edinburgh.
Japan
Manufacturing conglomerates balance legacy Windows endpoints with modern device fleet governance. METI cybersecurity guidelines shape procurement specifications for critical infrastructure operators. Tokyo and Osaka enterprise clusters favor hybrid deployment architectures splitting sensitive operations from cloud analytics.
India
IT services exporters and pharmaceutical manufacturers expand endpoint control deployments for client compliance requirements. The country's national data protection framework elevates audit scrutiny for removable media handling. Bangalore and Hyderabad technology corridors drive cloud-native policy orchestration adoption among mid-market accounts.
Portable Storage Device Control Software Market Competitive Landscape
Diversified conglomerates compete with focused pure-play specialists across the portable storage device control software landscape. The vendor base spans endpoint security suites with native DLP integration and standalone device control modules. Three archetypes dominate: platform-anchored security stacks, modular endpoint specialists, and compliance-centric regional players. M&A activity concentrates on encryption key management capabilities while strategic partnerships target managed service provider channels.
Within the platform-anchored tier, Symantec Endpoint DLP and Trellix Endpoint DLP exemplify security stack integration strategies. ManageEngine Device Control Plus occupies a position among modular specialists with channel density across Asia-Pacific. These three represent divergent approaches to policy orchestration architecture and geographic reach.
| Leading Market Players |
|---|
| Netwrix Endpoint Protector |
| ManageEngine Device Control Plus |
| DeviceLock |
| SafeticaONE |
| Trellix Endpoint DLP |
| Symantec Endpoint DLP |
| DriveLock |
| AccessPatrol |
| GFI EndPointSecurity |
| Others |
Value Network & Pricing Analysis
Cybersecurity engineering talent concentration in the United States and Germany widens pricing-tier spreads between premium FIPS-validated suites and standard cloud-native offerings, as labor-cost differentials in cryptographic development feed into margin structures across deployment models.
Pricing Analysis
Margin tightening in mid-market SaaS tiers reflects channel partner commission compression and subscription billing infrastructure costs. Three-tier pricing structure across premium FIPS-validated, standard ISO-aligned, and economy cloud-native levels separates buyers by compliance mandate stringency. Pricing pressure stems from managed security service providers bundling endpoint control into broader SOC offerings at compressed attach rates. Healthcare networks under OCR enforcement timelines exhibit lowest price sensitivity; budget-constrained educational institutions demonstrate highest.
Supply Chain Analysis
Regional distribution centers in the United States, Germany, and United Kingdom anchor hub-and-spoke delivery of hardware security modules and policy orchestration appliances. Software development draws from cryptographic engineering clusters in California, Bavaria, and Tel Aviv, while cloud infrastructure rests on hyperscaler data center networks in Virginia, Frankfurt, and London. Single-source vulnerability in FIPS 140-2 validation laboratories creates certification bottlenecks. Distribution runs through value-added resellers and managed service providers rather than direct enterprise sales.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
GDPR Article 32 enforcement and HIPAA audit frequency are compressing procurement timelines toward pre-certified suites, forcing point-solution vendors toward acquisition or exit.
For Market Incumbents:Acquire encryption key management specialists to close hardware security module integration gaps. Consolidate channel partnerships with managed security service providers in the United Kingdom and Germany to lock out emerging cloud-native entrants. FIPS 140-2 validation backlog poses immediate threat; ISO 27001 alignment investment serves as defensive moat.
For New Entrants and Emerging Players:Cloud-native policy orchestration via containerized microservices offers lowest-friction entry path. Target mid-market pharmaceutical manufacturers in India and Southeast Asia with outsourced compliance management bundles. Partner with regional system integrators in Bangalore and Hyderabad to bypass direct enterprise sales infrastructure.
For Investors and Strategic Acquirers:Re-rating potential sits with modular endpoint specialists possessing Asia-Pacific channel density given Zero Trust mandate propagation through United States federal procurement. Long-term viability favors vendors with hybrid deployment architectures spanning cloud-native and air-gapped capabilities. Watch for inflection when Department of Defense CMMC certification requirements harden procurement filters.
| Strategic Initiative | Industry Significance |
|---|---|
| Acquisition of Specialist Firm | Key management vendors with FIPS 140-2 validation expertise command premium multiples under federal procurement pressure. |
| Platform Integration | Native embedding of device control agents within broader endpoint security stacks collapses procurement distinction between DLP and encryption categories. |
| Strategic Partnership | Managed security service provider alliances in Greater Manchester and Edinburgh unlock recurring revenue attach rates among NHS trusts. |
| Product Launch | Containerized policy agents addressing FDA 21 CFR Part 11 requirements capture diagnostic equipment OEM integration opportunities. |
| Geographic Expansion | Channel density investments across Asia-Pacific manufacturing corridors serve IT services exporters facing client compliance mandates. |
Research Methodology
Multi-period observation of HIPAA audit frequency, GDPR enforcement actions, and federal Zero Trust procurement timelines anchored the trend analysis, supplemented by interviews with CISOs at United States healthcare systems, data protection officers at German automotive suppliers, and procurement leads at United Kingdom NHS trusts. Secondary validation drew from FDA 21 CFR Part 11 guidance documents, OCR enforcement bulletins, EU data protection authority certification registers, and hyperscaler security compliance disclosures. Bottom-up deployment estimates triangulated against top-down endpoint security market sizing.
Input-output matrices modeled relationships between regulatory enforcement intensity, compliance certification requirements, and procurement cycle compression across the projection horizon. Segmentation dimensions spanned deployment architecture, solution integration depth, end-user vertical, and regional regulatory framework. CAGRs derived from fitted trend extrapolation with enforcement schedule overlays. Industry-specific inputs included Department of Defense CMMC rollout pacing and European data protection authority staffing levels.
The model holds under steady regulatory enforcement trajectories; deviation in federal procurement acceleration or data protection authority resource constraints would shift replacement cycle assumptions. Forecasts reflect documented base-case assumptions regarding HIPAA audit frequency and GDPR Article 32 interpretation consistency. Periodic stress-testing of base assumptions is recommended.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Data Storage
China Solid-State Drive Market
Data Storage
Serial EEPROM Market
Data Storage
Storage Class Memory Market
Data Storage
NOR Flash Market
Data Storage
Storage and Management Market
Data Storage
Ceph Storage Solutions Market
Data Storage
Electrochromic Storage Devices Market
Data Storage
Solid State Array Market
Data Storage
Optical Disk Market
Data Storage
Archival Grade Blu-Ray Discs Market
Data Storage
OTG Pen Drive Market
Data Storage
Blu-Ray Drive Market
Data Storage
SAS Hard Disk Drives Market
Data Storage
Wi-Fi SD Cards Market
Data Storage
Zoned Flash Market
Data Storage
Middle East and Africa Data Storage Market