
 North America Cyber Security Market | 2026-2036
North America Cyber Security Market Size, Share, and Industry Trends Forecast 2026-2036
North America Cyber Security Market Outlook
Artificial intelligence is expanding its role as a substitute for signature-based detection in endpoint protection, reducing reliance on static threat databases. Palo Alto Networks leverages machine-driven prevention to dominate enterprise firewall consolidation. CrowdStrike Holdings sustains cloud-native endpoint leadership through behavioral AI models. Fortinet anchors mid-market expansion with integrated networking-security convergence.
North America cyber security encompasses hardware, software, and services engineered to protect digital infrastructure from unauthorized access, disruption, or data exfiltration through encryption protocols, intrusion detection algorithms, and continuous monitoring architectures. Its primary purpose is preserving confidentiality, integrity, and availability across enterprise and government information systems. Cloud deployment models are capturing the fastest expansion as organizations migrate workloads away from on-premises data centers. Managed security services concentrate margin pools through recurring revenue structures and specialized threat-hunting expertise. Consulting services within the service-type dimension remain structurally constrained by talent scarcity despite rising breach-response demand.
The National Institute of Standards and Technology shapes product standards through its Cybersecurity Framework, while state regulators in California and New York enforce sector-specific mandates through CCPA and DFS 23 NYCRR 500. The SEC's disclosure rules for material cybersecurity incidents are forcing publicly traded entities to expand governance budgets and accelerate incident-response preparedness. Stakeholders must monitor how federal cloud-security authorization programs reshape vendor qualification barriers and procurement concentration.
Market Dynamics
Zero-trust architecture mandates are compressing procurement cycles across federal agencies and Fortune 500 enterprises, forcing vendors to reengineer product roadmaps around continuous verification rather than perimeter defense. This structural pivot favors cloud-native platforms over legacy appliance stacks.
Growth Catalysts
- NIST Cybersecurity Framework 2.0:Federal contractors must demonstrate compliance to maintain eligibility, expanding addressable demand for certified security services.
- SEC Cybersecurity Disclosure Rules:Publicly traded firms face accelerated incident-response timelines, driving board-level governance spending and external advisory retainers.
- Cloud workload migration:Enterprises shifting from on-premises data centers require containerized security orchestration, lifting demand for API-first protection platforms.
Market Restraints
- Specialized talent scarcity:Shortages of cloud security architects and threat-hunting analysts inflate service delivery costs and extend implementation timelines.
- Legacy infrastructure drag:Hybrid environments complicate unified policy enforcement, fragmenting security stacks and elevating operational overhead.
- State regulatory fragmentation:Divergent breach-notification timelines between California CCPA and New York DFS 23 NYCRR 500 multiply compliance program complexity.
Strategic Opportunities
- Operational technology convergence:Manufacturing and energy facilities are extending zero-trust principles to industrial control systems, opening new endpoint categories.
- Managed detection and response:Mid-market firms lacking in-house security operations centers represent an underpenetrated segment for subscription-based threat-hunting services.
- Quantum-resistant cryptography:NIST's post-quantum algorithm standards are creating upgrade cycles across government and financial services encryption infrastructure.
Industry Challenges
- Alert fatigue and false-positive rates:Security operations teams face burnout from noisy detection systems, degrading mean-time-to-response metrics.
- Multi-cloud policy orchestration:Enterprises struggle to maintain consistent access controls across AWS, Azure, and Google Cloud environments without vendor lock-in.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | North America Cyber Security Market |
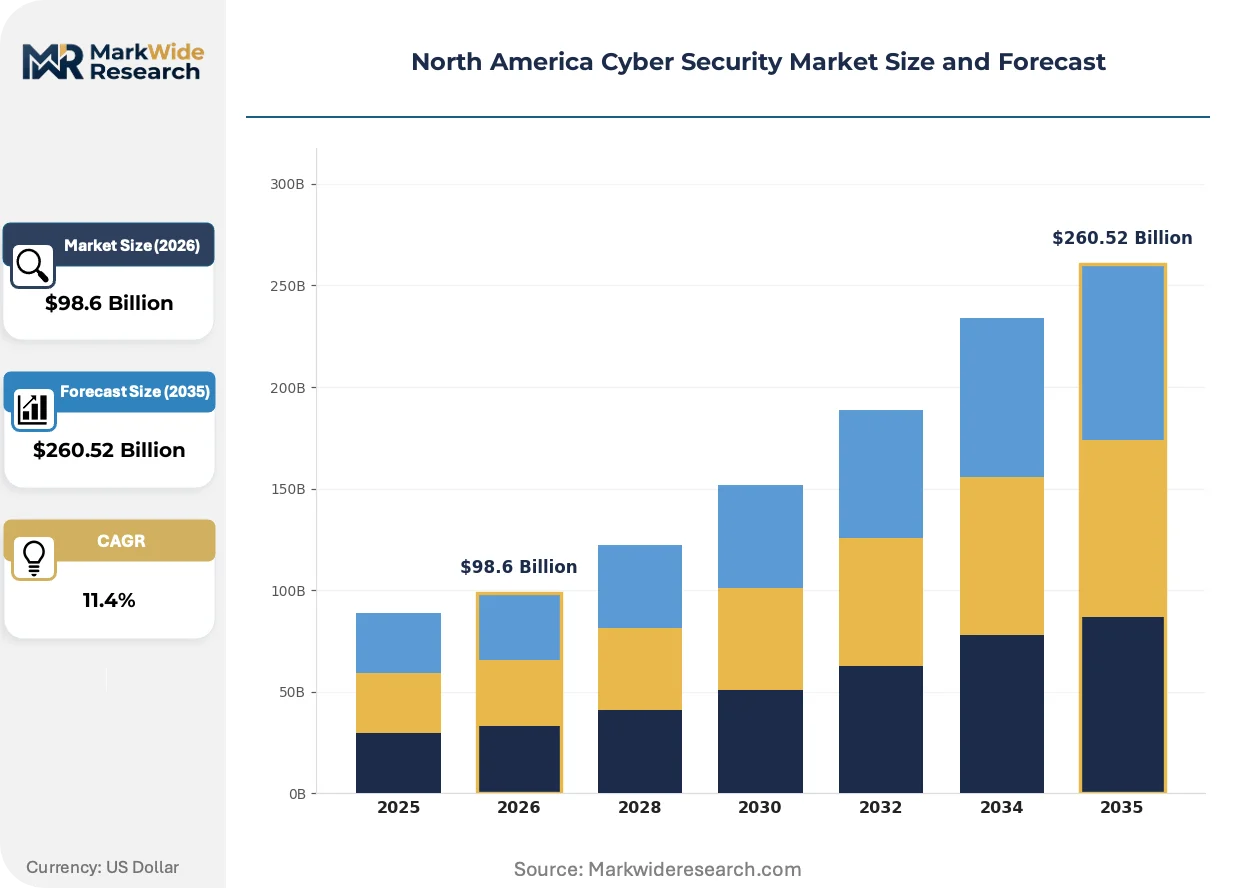
| Market Size in 2026 | $98.6 Billion |
| Market Size in 2035 | $260.52 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution: Firewall, IDS, IPS, Antivirus Deployment Model: On-Premises, Cloud, Hybrid, Managed Service End User: Government, BFSI, Healthcare, Retail Service Type: Consulting, System Integration, Support, Training |
| Companies Covered | Palo Alto Networks, Inc., Fortinet, Inc., CrowdStrike Holdings, Inc., Cisco Systems, Inc., Check Point Software Technologies Ltd., IBM Corporation, Broadcom, Inc., Proofpoint, Inc., McAfee, LLC, Others |
| Regions Covered | North America: US, Canada, Mexico |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
North America Cyber Security Market Strategic Shifts
Security architecture is fragmenting into composable microservices, enabling buyers to assemble protection layers rather than purchasing monolithic suites. This decomposition is redistributing value capture across the stack.
Extended detection and response platforms are modularizing security operations by unifying telemetry from endpoints, networks, and cloud workloads into single-pane analysis. Large healthcare systems and financial institutions are consolidating vendor relationships around these integrated consoles. The shift is compressing standalone endpoint security margins while elevating data lake and analytics layer valuations.
The SEC's cybersecurity disclosure mandates are forcing material incident reporting within four business days, compelling publicly traded entities to pre-position forensic capabilities and legal response frameworks. General counsels and audit committees are expanding direct oversight of security program maturity. This regulatory pressure is most acute in the energy and critical infrastructure sectors, where operational technology breaches carry amplified reputational and liability exposure.
Security service procurement is fragmenting between retained managed security service providers and on-demand incident-response boutiques, with buyers unbundling prevention, detection, and response functions. Channel partners are repositioning as orchestration advisors rather than product resellers. This bifurcation is most visible in the United States mid-market, where constrained internal security headcounts drive reliance on external expertise for specialized functions.
North America Cyber Security Market Segmentation
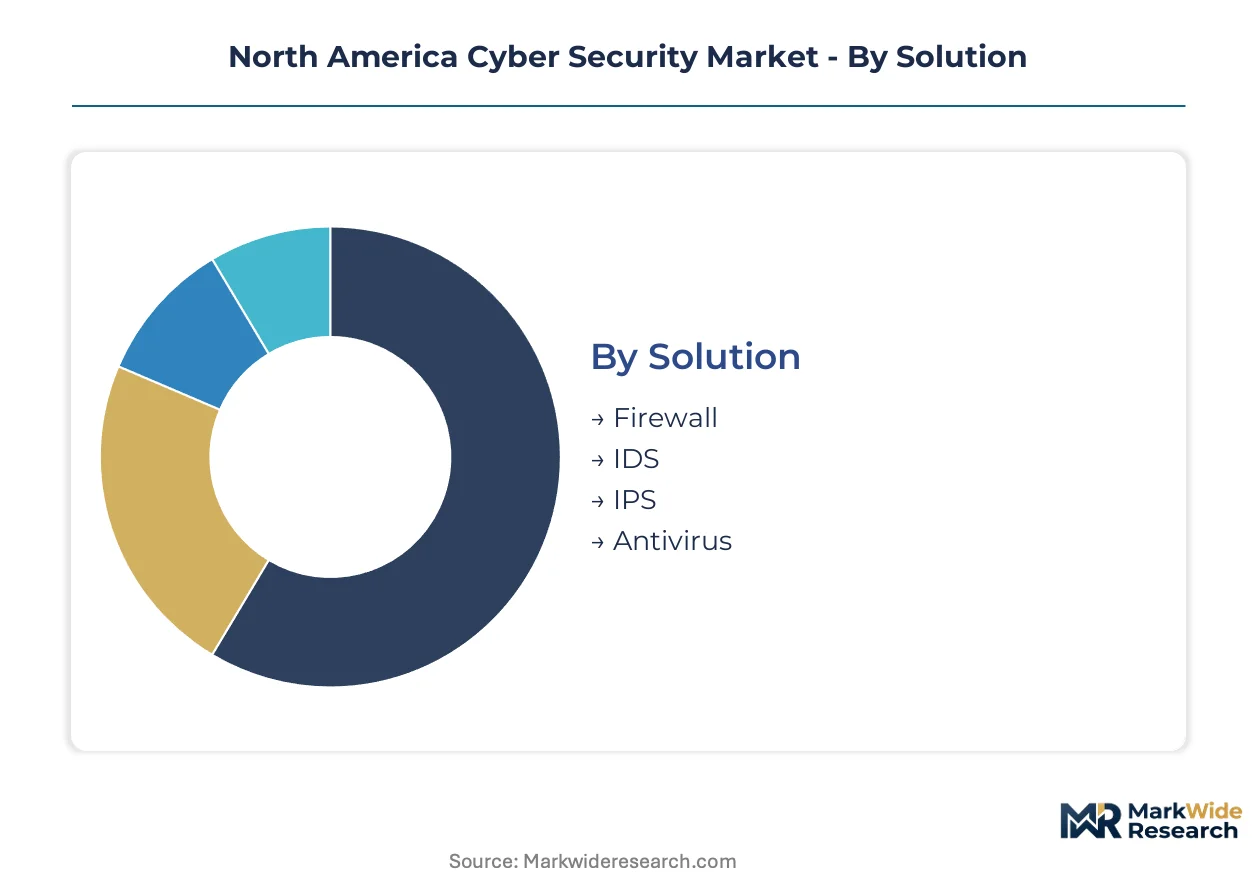
Security procurement patterns in North America diverge sharply by organizational maturity, with federal agencies and Fortune 500 enterprises driving premium solution demand while mid-market buyers prioritize managed consumption models. Understanding these segment boundaries reveals where vendor roadmaps must pivot between appliance-centric and cloud-native architectures.
Solution:
Firewall and IDS solutions concentrate manufacturing capacity among three dominant hardware suppliers, while IPS and antivirus segments fragment across dozens of specialized vendors with limited pricing power.
- Firewall:Next-generation appliances integrate deep packet inspection with application-layer visibility. Demand clusters in United States federal agencies modernizing perimeter defenses under zero-trust mandates, constrained by lengthy FedRAMP authorization cycles.
- IDS:Network-based intrusion detection systems analyze traffic patterns against behavioral baselines. Financial services firms in New York and California deploy these most aggressively, driven by DFS 23 NYCRR 500 and CCPA audit requirements.
- IPS:Inline prevention systems block malicious payloads in real-time. Healthcare networks prioritize these for HIPAA-protected environments.
- Antivirus:Endpoint protection platforms leverage machine learning for fileless attack detection. State and local governments represent the largest remaining on-premises deployment base.
Today's leader: Firewall. Tomorrow's challenger: IDS.
Deployment Model:
Cost tier stratification separates buyers with capital budgets for infrastructure ownership from those preferring operational expenditure models with embedded expertise.
- Cloud:API-first security services orchestrate protection across distributed workloads without hardware footprint. United States enterprises migrating from colocation facilities represent the steepest expansion trajectory, though multi-cloud policy consistency remains unresolved.
- Managed Service:Third-party security operations centers deliver 24/7 monitoring through subscription contracts. Mid-market manufacturers across the Midwest and Southeast adopt these fastest, lacking internal SOC headcount.
- Hybrid:Split architectures maintain sensitive workloads on-premises while extending cloud-native tools to edge environments. Energy sector critical infrastructure operators favor this model for operational technology segmentation.
- On-Premises:Appliance-based deployments persist in classified government networks and defense industrial base facilities with air-gapped requirements.
Cloud deployments are gaining share fastest. On-premises retains defensive moats in regulated enclaves.
End User:
Application-driven purchasing patterns separate threat-model sophistication, with BFSI and government buyers demanding predictive analytics while retail prioritizes compliance checkboxes.
- BFSI:Banking and insurance institutions deploy the most layered security stacks, combining zero-trust networking with quantum-resistant cryptography preparation. New York and California regulatory pressure accelerates refresh cycles.
- Government:Federal, state, and municipal entities bind procurement to NIST Cybersecurity Framework compliance. United States defense contractors face CMMC certification deadlines reshaping vendor qualification.
- Healthcare:Hospital systems and payers balance HIPAA security rules against clinical workflow friction. Large integrated delivery networks consolidate vendors around EDR platforms.
- Retail:Merchants and payment processors prioritize PCI-DSS compliance automation. E-commerce platforms drive cloud-native adoption fastest among this group.
BFSI commands premium pricing. Healthcare represents the most underpenetrated advanced-analytics opportunity.
Service Type:
Margin structure varies dramatically by talent intensity, with consulting and system integration capturing value from scarcity while support and training commoditize.
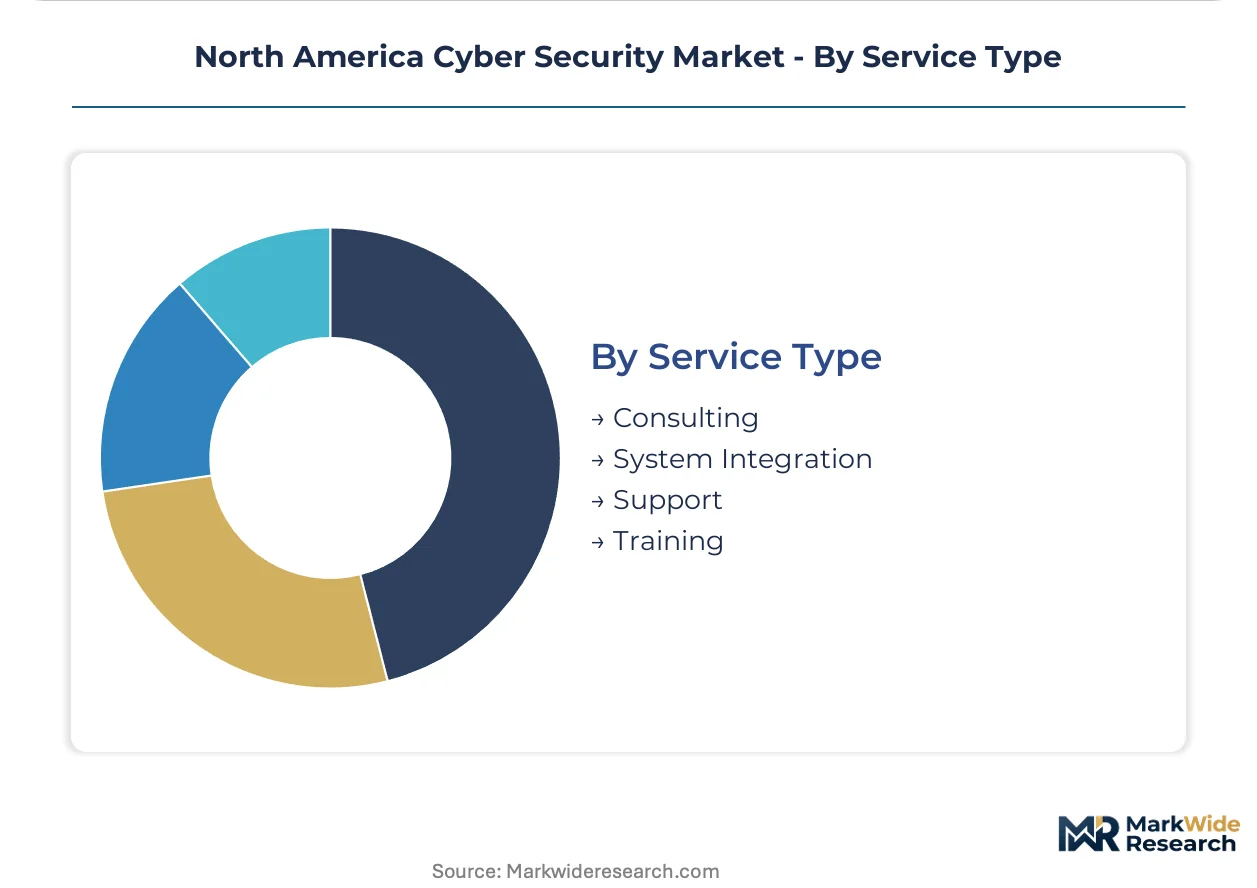
- Consulting:Advisory services assess security program maturity against NIST CSF 2.0 and SEC disclosure readiness. Boutique firms with former CISO practitioners command retainers above $500 hourly in major metropolitan markets.
- System Integration:Professional services deploy and configure multi-vendor security architectures. Large healthcare systems and federal integrators drive the most complex engagement scopes.
- Support:Technical maintenance contracts ensure patch management and availability SLAs. Hardware vendors bundle these to sustain recurring revenue.
- Training:Certification programs address the chronic shortage of cloud security architects. Community colleges and workforce development boards in Texas and California expand capacity fastest.
Consulting captures margin from talent scarcity. Training faces commoditization from self-service platforms.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Silicon Valley anchors North American cyber security demand through its concentration of cloud infrastructure providers and venture-backed security startups. Federal procurement mandates and state-level privacy regulations are reshaping vendor qualification requirements across the continent. Three national markets exhibit distinct procurement patterns driven by regulatory frameworks and industrial base composition.
United States
Defense contractors and financial institutions in Virginia and New York drive zero-trust architecture deployments. SEC cybersecurity disclosure rules mandate four-day incident reporting timelines for publicly traded firms. California's CCPA enforcement has spawned specialized compliance advisory practices in San Francisco and Los Angeles.
Canada
Toronto's financial services sector and Vancouver's cloud infrastructure operators anchor enterprise security spending. Health Canada coordinates with the Canadian Centre for Cyber Security on critical infrastructure protection standards. Ontario and Quebec host the majority of federal government security procurement contracts.
Mexico
Manufacturing facilities in Nuevo León and Baja California are extending operational technology security to industrial control systems. The national data protection authority enforces breach notification requirements for cross-border data flows. Mexico City concentrates banking sector security investments.
North America Cyber Security Market Competitive Environment
Platform consolidation dominates the current landscape as vendors bundle networking, endpoint, and cloud security into unified suites. The market structure concentrates among three large platform providers with integrated portfolios, while dozens of point-solution specialists compete on narrow functional domains. Two strategic archetypes have emerged: cloud-native platform builders and legacy appliance modernizers. M&A activity and strategic partnerships represent the dominant competitive moves, with incumbents acquiring behavioral analytics and identity verification capabilities.
Within the cloud-native platform tier, CrowdStrike Holdings, Inc. exemplifies endpoint-centric expansion into identity protection and log management. Palo Alto Networks, Inc. anchors the network-security convergence archetype through its integrated firewall and cloud access security broker positioning. Fortinet, Inc. occupies the mid-market consolidation position, representing the integrated networking-security appliance approach.
| Leading Market Players |
|---|
| Palo Alto Networks, Inc. |
| Fortinet, Inc. |
| CrowdStrike Holdings, Inc. |
| Cisco Systems, Inc. |
| Check Point Software Technologies Ltd. |
| IBM Corporation |
| Broadcom, Inc. |
| Proofpoint, Inc. |
| McAfee, LLC |
| Others |
Value Chain & Pricing Dynamics
Federal contractors under CMMC certification deadlines concentrate procurement authority among defense industrial base buyers, anchoring North American cyber security pricing around FedRAMP-authorized SaaS tiers with embedded compliance premiums.
Pricing Analysis
Input-cost pass-through from cloud infrastructure providers shapes subscription pricing across managed detection and response platforms. Three-tier pricing structure across premium, standard, and economy levels separates FedRAMP-authorized federal offerings from mid-market SaaS bundles and self-managed open-source alternatives. Pricing pressure stems from hyperscaler marketplace listings compressing standalone vendor margins. Mid-market manufacturers exhibit highest price sensitivity, while BFSI institutions prioritize certification tier over unit cost.
Supply Chain Analysis
Single-source vulnerability sits with Taiwan-based semiconductor foundries supplying custom ASICs for next-generation firewalls and hardware security modules. Component sourcing draws from Malaysia for circuit board assembly, Mexico for edge appliance final assembly, and domestic United States facilities for classified government configurations. Raw material dependencies include rare earth elements for magnetics, high-purity silicon for chips, and specialized alloys for tamper-resistant enclosures. Tariff exposure on Chinese-manufactured networking components elevates landed costs for mid-tier hardware vendors. Distribution runs through value-added resellers with security specialization certifications, direct hyperscaler marketplace procurement, and federal systems integrators holding blanket purchase agreements.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
North American cyber security margins are expanding through cloud-native delivery models that eliminate hardware fulfillment costs while capturing recurring revenue premiums from compliance-embedded service tiers.
For Market Incumbents: Extend platform consolidation into identity governance and operational technology security to counter modular best-of-breed challengers. Deepen backward integration into threat intelligence data lakes to differentiate analytics layers from commodity detection engines. Strengthen channel control through exclusive certification programs for managed security service partners serving federal contractor segments.
For New Entrants and Emerging Players: Launch via embedded security partnerships with vertical SaaS providers targeting healthcare and manufacturing operational technology environments. White-space concentration sits with mid-market energy facilities extending zero-trust segmentation to industrial control networks. Go-to-market leverage rests on API-first architectures that integrate into existing security operations center workflows without rip-and-replace displacement.
For Investors and Strategic Acquirers: Platform consolidation specialists are the most active acquirer in this space, seeking behavioral analytics and identity verification capabilities to fill portfolio gaps. Long-term viability favors vendors with demonstrated FedRAMP authorization velocity and recurring revenue concentration above eighty percent. Acquisition target archetype: cloud-native endpoint specialists with healthcare or energy vertical penetration. Signal to watch: NIST post-quantum cryptography standard adoption rates forcing infrastructure refresh cycles.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifying endpoint, network, and cloud telemetry compresses vendor consolidation timelines for Fortune 500 CISOs. |
| FedRAMP Authorization Acceleration | Fast-tracking federal cloud certification opens defense contractor procurement channels under CMMC deadlines. |
| Operational Technology Security Expansion | Extending zero-trust principles to industrial control systems captures manufacturing and energy facility budgets. |
| Managed Detection and Response Scale-Up | Building subscription-based SOC capabilities addresses mid-market talent scarcity with embedded expertise. |
| Post-Quantum Cryptography Readiness | Pre-positioning NIST algorithm-compliant encryption infrastructure secures financial services upgrade cycles. |
Study Parameters
Quantitative tracking and qualitative interviews ran in parallel throughout the study window, combining primary discussions with CISOs at healthcare systems and financial institutions, federal procurement officers, channel partners with security specializations, and cloud infrastructure architects with secondary validation against SEC cybersecurity disclosure filings, FedRAMP authorization databases, NIST framework implementation guidance, and state regulatory breach notification records. Bottom-up sizing of solution segments triangulated against top-down spending estimates from federal IT budget justifications and enterprise security expenditure surveys.
Comparable historical periods anchored the projection framework across the analysis window, with segmentation modeling spanning solution type, deployment architecture, end-user vertical, and service delivery mode. CAGRs derived from fitted growth curves adjusted for regulatory inflection points and technology substitution patterns. Forecast inputs included cloud workload migration velocities, zero-trust mandate implementation timelines, and managed security service penetration rates by organization size tier.
Forecast precision tightens around the base case; tail outcomes carry wider variance under accelerated quantum computing breakthroughs or federal procurement freeze scenarios. Forecasts reflect documented assumptions about regulatory enforcement continuity and hyperscaler pricing stability. Outcomes are best read as a band of plausibility, not a single trajectory.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Threat Intelligence Security Market
Cybersecurity
Cloud Workload Protection Market
Cybersecurity
Global Cyber Security in Healthcare Market
Cybersecurity
Israel Cybersecurity Market
Cybersecurity
Portugal Cybersecurity Market
Cybersecurity
Cloud-Based Database Security Market
Cybersecurity
DNS Security Market
Cybersecurity
Internet of Things (IoT) Security Market
Cybersecurity
North America Software Defined Perimeter Market
Cybersecurity
Global File Integrity Monitoring Market
Cybersecurity
Global Cyber Situational Awareness Market
Cybersecurity
SD-WAN Security Market
Cybersecurity
Global Content Disarm and Reconstruction Market
Cybersecurity
Turkey Cybersecurity Market
Cybersecurity
Cloud Firewalls Market
Cybersecurity
UK Cybersecurity Market