
 Europe SOC As a Service Market | 2026-2036
Europe SOC As a Service Market Size, Share, and Industry Trends Forecast 2026-2036
Europe SOC As a Service Market Insights
ISO 27001 certification is bifurcating the European vendor landscape into accredited providers and aspirants. Thales leverages its defense-grade security clearances to dominate government and aerospace contracts across France and neighboring states. Atos sustains broad geographic coverage through managed security centers in multiple European capitals, competing on response-time guarantees.
Europe SOC As a Service delivers continuous threat monitoring, incident detection, and response coordination through cloud-connected analyst teams operating on sub-15-minute SLA thresholds. Its primary purpose is to replace capital-intensive in-house security operations with subscription-based expertise accessible to organizations lacking dedicated cyber personnel. Managed Detection and Response commands the largest revenue share as enterprises prioritize real-time threat containment over retrospective intelligence reports. Cloud-Based deployment is expanding fastest among mid-market buyers seeking elastic capacity without fixed infrastructure commitments.
The EU NIS2 Directive, GDPR data-breach notification rules, and CE marking under the Cybersecurity Act collectively mandate demonstrable security operations for critical infrastructure operators and data processors. EMA guidelines for pharmaceutical supply chain integrity and EBA outsourcing standards for financial institutions further channel compliance spending toward certified SOC providers. Stakeholders must weigh vendor accreditation depth against specialization in industry-specific threat actor profiles when selecting long-term partners.
Market Dynamics
The EU NIS2 Directive is compelling mid-market enterprises across France, Germany, and the Netherlands to abandon capital-intensive in-house security operations in favor of subscription-based external monitoring. This regulatory pressure is restructuring competitive positioning around ISO 27001 accreditation depth and sub-15-minute response SLAs.
Growth Catalysts
- EU NIS2 Directive:Critical infrastructure operators in energy, transport, and healthcare sectors must now demonstrate continuous threat monitoring capabilities, driving mandatory outsourcing to certified providers.
- Connected vehicle fleets:German automotive manufacturers are expanding reliance on external SOCs to monitor real-time telemetry from millions of sensor-equipped vehicles.
- GDPR breach notification rules:Data processors face 72-hour disclosure deadlines that internal teams struggle to meet, accelerating demand for 24/7 analyst coverage.
Market Restraints
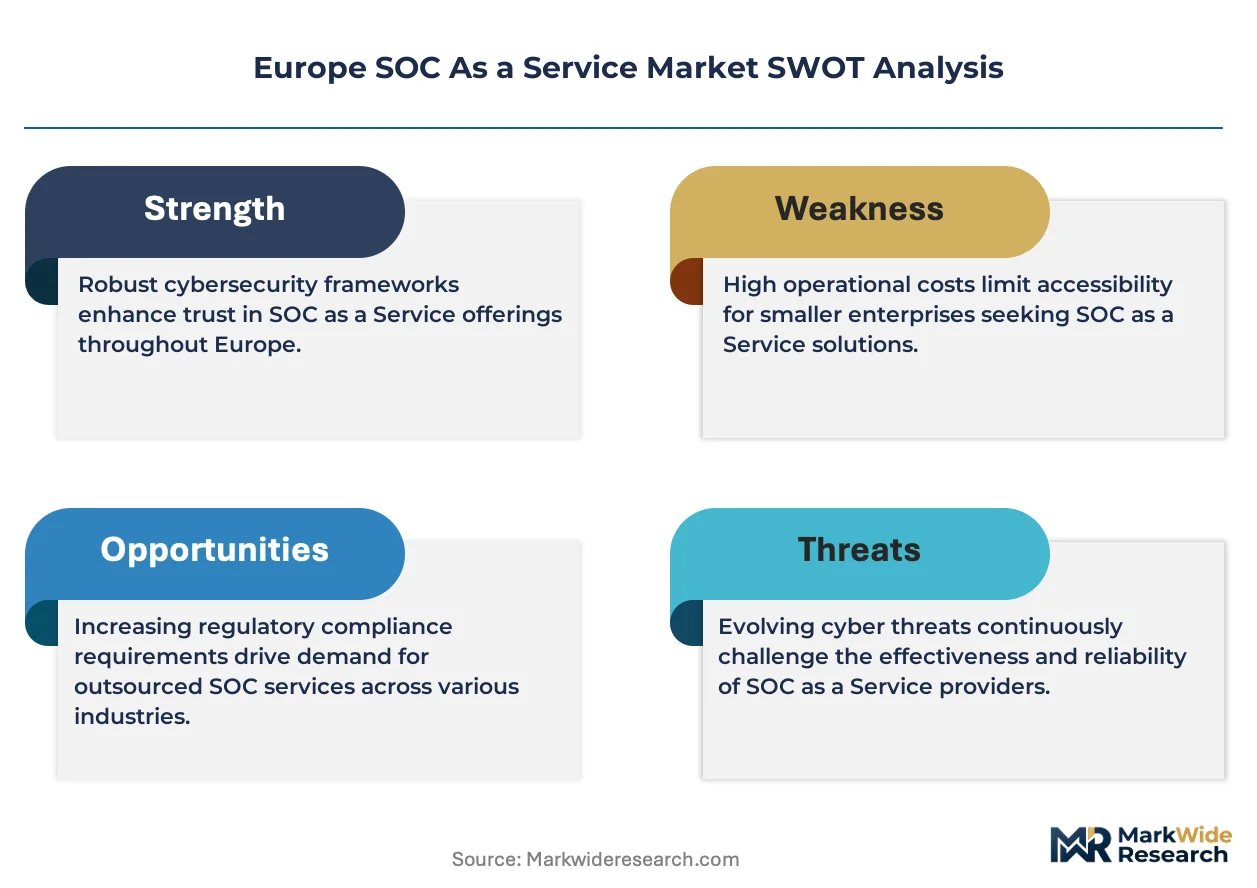
- ISO 27001 certification scarcity:The bifurcated vendor landscape limits buyer choice to a narrow pool of accredited providers, constraining price competition.
- Skilled analyst concentration:Certified security professionals cluster in Paris, Munich, and London, creating regional supply bottlenecks for remote delivery.
- Cloud dependency risks:Mid-market buyers' reliance on hyperscale infrastructure introduces concentration vulnerabilities when primary regions experience outages.
Strategic Opportunities
- Poland and Czech Republic:Underpenetrated Central European markets lack native SOC-as-a-service providers, creating first-mover openings for accredited vendors.
- EBA outsourcing standards:Financial institutions seeking compliance with European Banking Authority guidelines represent a channel for specialized MDR contracts.
- AI-augmented threat detection:Convergence of machine learning with human analyst workflows enables tier-1 automation that reduces per-incident labor costs.
Industry Challenges
- SOC 2 Type II audit timelines:The 6-12 month certification window delays market entry for emerging providers competing for enterprise contracts.
- Legacy SIEM integration:Enterprises with decade-old security information systems face complex data pipeline reconstruction when migrating to cloud-native platforms.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Europe SOC As a Service Market |
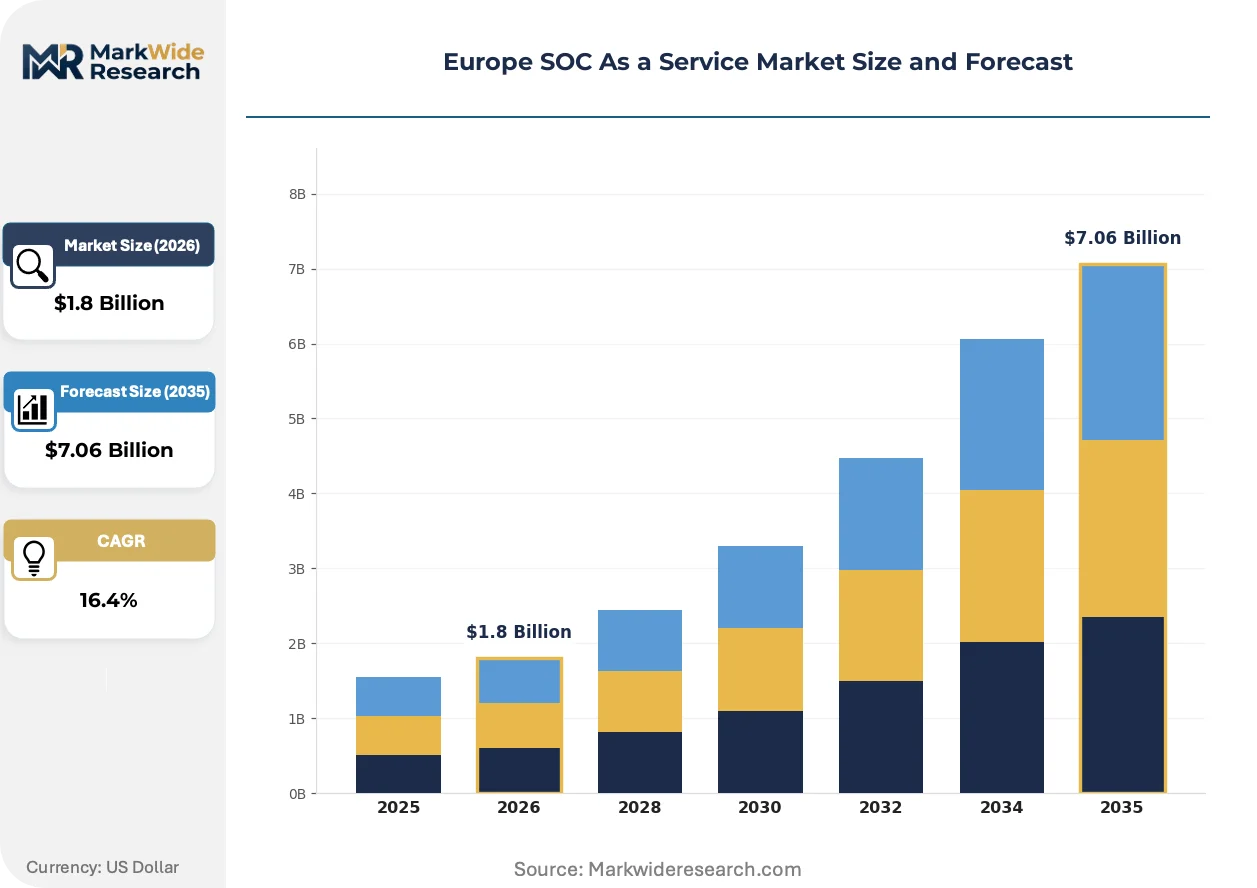
| Market Size in 2026 | $1.8 Billion |
| Market Size in 2035 | $7.06 Billion |
| CAGR (2026 – 2036) | 16.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Managed Detection & Response, Threat Intelligence, Incident Response, Compliance Management Deployment: Cloud-Based, On-Premises, Hybrid, Federated End User: Small Enterprises, Medium Enterprises, Large Enterprises, Government Agencies Industry Vertical: Finance, Healthcare, Retail, Telecommunications |
| Companies Covered | Thales, Atos, Orange Cyberdefense, Fortinet, Secureworks, IBM, Connectwise, BT Group, Accenture, Others |
| Regions Covered | Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Europe SOC As a Service Market Trends and Innovations
Artificial intelligence is fragmenting traditional analyst workflows across European SOC operations. Automation is compressing tier-1 alert triage while elevating human expertise toward strategic threat hunting. This shift is reshaping staffing models and service pricing structures.
Extended detection and response platforms are fragmenting the managed security services market. XDR consolidates endpoint, network, and cloud telemetry into unified analyst consoles. Mid-market buyers in France and Germany are adopting these integrated stacks faster than multi-vendor alternatives. The technology is fragmenting pure-play MDR contracts into platform-plus-service bundles.
The EU AI Act introduces mandatory risk classification for automated decision systems used in security operations. Providers deploying machine learning for threat scoring must now document training data provenance and human oversight protocols. Critical infrastructure operators in energy and healthcare are demanding pre-certified AI components to accelerate their own compliance timelines.
Subscription fatigue is altering procurement patterns among European mid-market enterprises. Buyers are consolidating vendor relationships and demanding outcome-based pricing tied to mean-time-to-containment metrics. This behavior is most pronounced in the Netherlands, where CFO scrutiny of recurring technology spend has intensified since 2023.
Europe SOC As a Service Market Segmentation
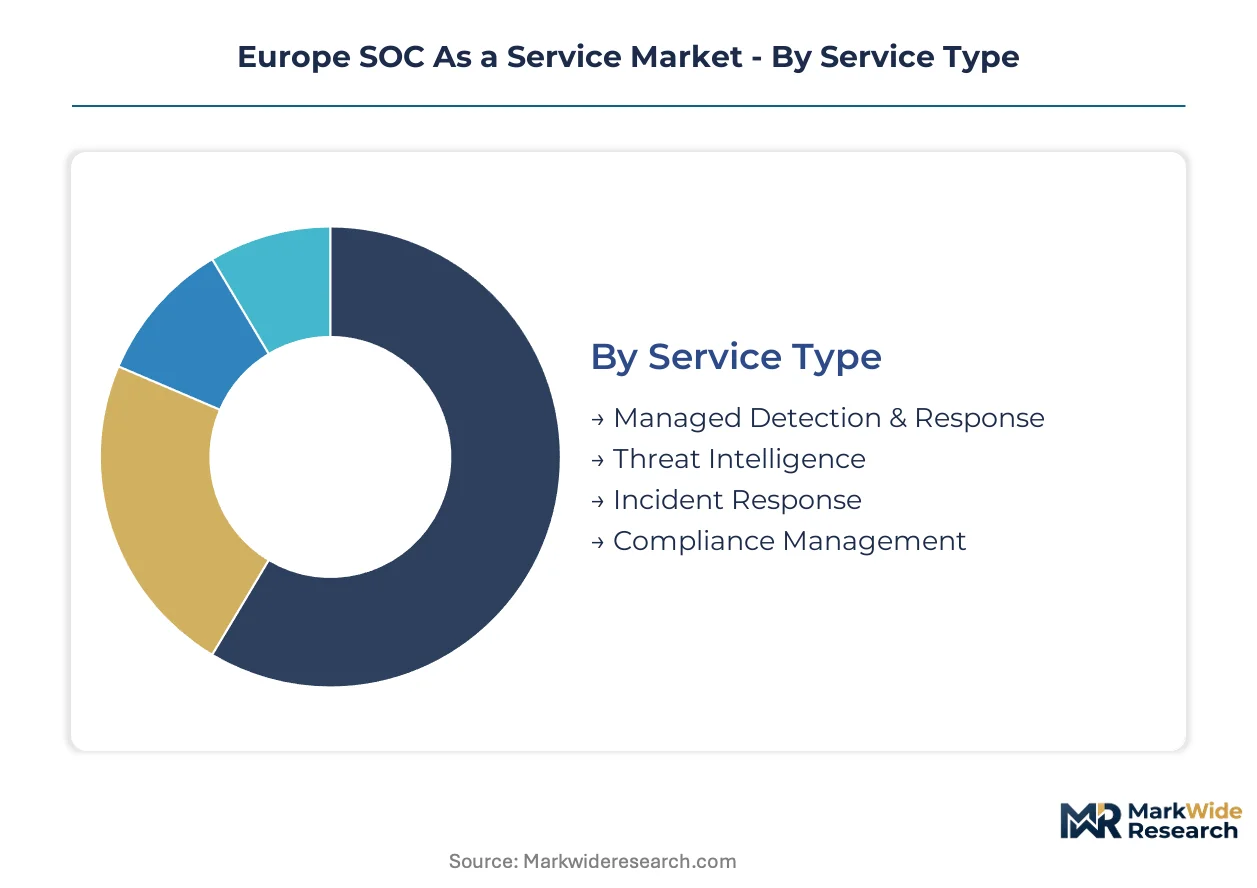
Segmentation in the Europe SOC As a Service Market reveals how regulatory mandates and operational constraints reshape procurement priorities across service tiers, infrastructure models, and buyer profiles. Understanding these divides enables vendors to align certification depth, response architectures, and pricing structures with specific compliance burdens and threat exposure levels.
Service Type:
GDPR breach notification rules and EU NIS2 Directive mandates create divergent compliance obligations that push buyers toward specialized service tiers with documented audit trails and guaranteed response windows.
- Managed Detection & Response:Real-time threat containment combining automated alert correlation with human analyst intervention for endpoint, network, and cloud telemetry. German automotive manufacturers and French energy operators prioritize MDR contracts with sub-15-minute SLAs to satisfy critical infrastructure monitoring requirements under NIS2.
- Threat Intelligence:Curated feeds of adversary tactics, infrastructure indicators, and sector-specific attack patterns delivered through structured formats. Demand concentrates among Dutch financial institutions seeking predictive visibility into regional threat actor campaigns targeting SEPA payment corridors.
- Incident Response:Retained or on-demand forensic investigation and containment services activated post-breach. Retainers are expanding fastest among mid-market healthcare providers in Belgium and Austria facing 72-hour GDPR disclosure deadlines.
- Compliance Management:Continuous control monitoring, evidence collection, and audit preparation for ISO 27001, SOC 2 Type II, and sector-specific frameworks. Adoption is accelerating among pharmaceutical suppliers aligning with EMA supply chain integrity guidelines.
Managed Detection & Response handles the majority of throughput; Compliance Management is expanding most quickly on share as NIS2 implementation deadlines approach.
Deployment:
Cost tier differentiation separates elastic subscription models from capital-intensive fixed infrastructure, with mid-market buyers gravitating toward hybrid architectures that balance control with operational expenditure limits.
- Cloud-Based:Fully managed multi-tenant platforms with elastic compute scaling and centralized analyst teams. French and German mid-market enterprises favor this model to avoid data center commitments while meeting GDPR data residency requirements through EU-only processing zones.
- On-Premises:Dedicated hardware and software stacks deployed within client facilities with remote analyst access. Defense contractors and classified government facilities in Italy and Spain require air-gapped deployments with security-cleared personnel.
- Hybrid:Split architectures combining on-premises collectors with cloud-based analytics and storage. Polish and Czech critical infrastructure operators adopt hybrid models to retain sensitive telemetry locally while leveraging centralized threat intelligence.
- Federated:Distributed SOC architectures linking multiple regional nodes under unified command with data sovereignty controls. Multinational banking groups use federated deployments to satisfy EBA outsourcing standards while maintaining jurisdictional separation of transaction data.
Cloud-Based deployment captures the highest volume of new contracts; Federated models are climbing the fastest as cross-border operators seek unified visibility with local compliance.
End User:
Organizational scale determines internal security team depth, with smaller entities outsourcing entirely while larger buyers seek co-managed arrangements that augment rather than replace in-house capabilities.
- Small Enterprises:Organizations with limited or no dedicated security personnel purchasing fully outsourced monitoring and response. GDPR exposure drives demand among professional services firms in Portugal and Ireland with concentrated client data liabilities.
- Medium Enterprises:Buyers with nascent security functions seeking tier-1 automation and escalation pathways. Dutch manufacturing and logistics companies represent the densest concentration as NIS2 expands coverage to previously exempt sectors.
- Large Enterprises:Sophisticated buyers with established SOCs purchasing specialized threat hunting, digital forensics, or overflow capacity. German automotive and aerospace manufacturers integrate external MDR with connected vehicle security operations.
- Government Agencies:National and regional authorities requiring security-cleared personnel, classified threat feeds, and sovereign data processing. French defense and interior ministries mandate defense-grade accreditation unavailable from commercial providers.
Medium Enterprises generate the steepest expansion trajectory as NIS2 compliance deadlines force security investments from previously underinvested sectors; Government Agencies maintain the most stringent vendor qualification barriers.
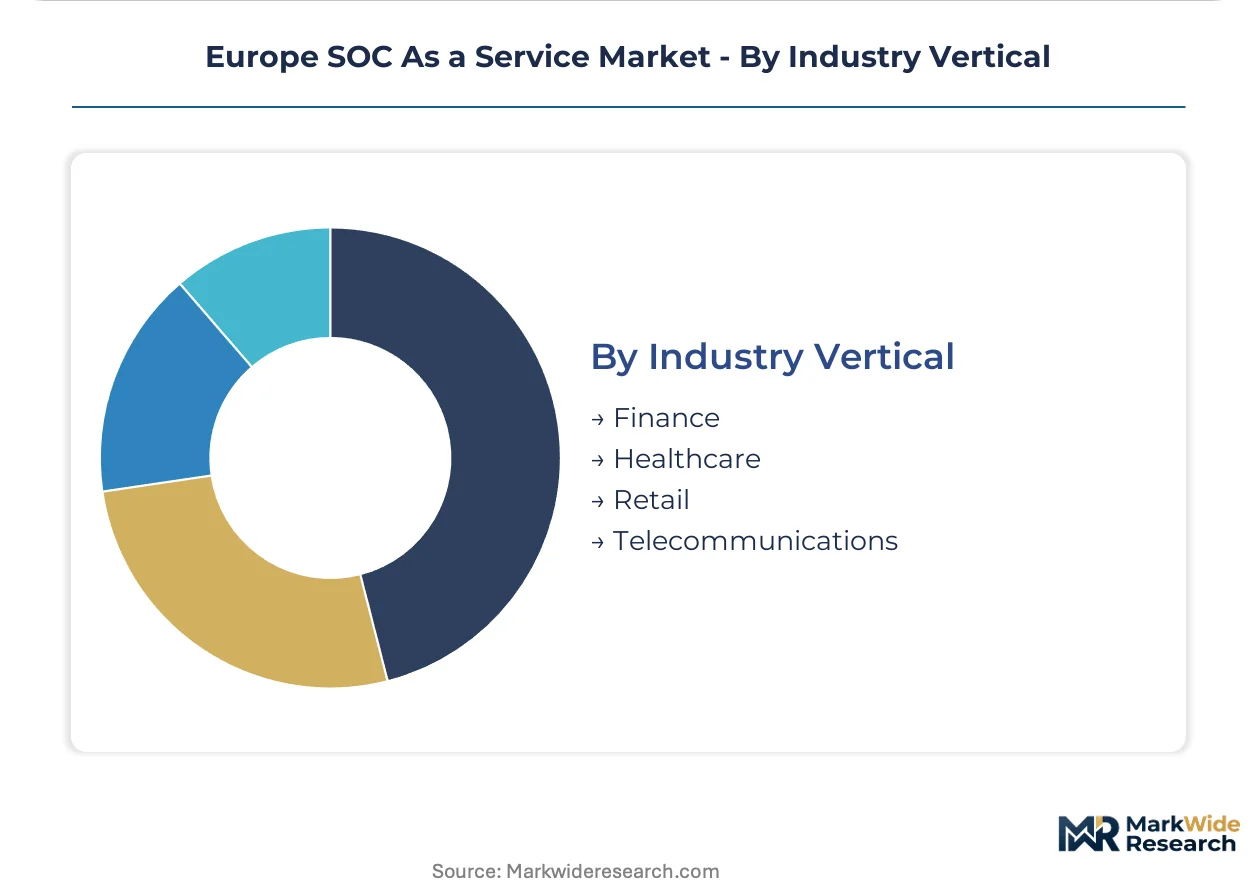
Industry Vertical:
Vertical-specific threat actor targeting and regulatory density create distinct service requirements, with financial and healthcare buyers prioritizing real-time containment while retail and telecommunications emphasize scale and cost efficiency.
- Finance:Banks, insurers, and payment processors facing EBA outsourcing standards and PSD2 security requirements. Scandinavian and Benelux institutions lead adoption of AI-augmented transaction monitoring with integrated SOC workflows.
- Healthcare:Hospitals, pharmaceutical manufacturers, and medical device companies subject to GDPR health data protections and EMA supply chain rules. German university hospitals and French regional health authorities drive demand for 24/7 coverage with clinical system expertise.
- Retail:E-commerce platforms and physical chains with seasonal transaction volatility and point-of-sale exposure. UK and Nordic retailers prioritize elastic capacity for peak trading periods with payment card industry compliance automation.
- Telecommunications:Network operators designated as critical infrastructure under NIS2 with mandatory incident reporting to national regulators. Italian and Spanish mobile operators invest in federated SOCs to monitor 5G network slices and IoT connectivity platforms.
Finance commands the largest contract values per seat; Healthcare is gaining share fastest as ransomware campaigns intensify targeting of clinical delivery organizations.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The Amsterdam Internet Exchange anchors northwest European data traffic routing, underwriting the Netherlands' centrality in cloud-delivered security operations. Frankfurt's DE-CIX and London's LINX create complementary infrastructure nodes that channel SOC service delivery across the continent.
Germany
Automotive telemetry monitoring from connected vehicle fleets drives external SOC procurement at BMW, Mercedes-Benz, and Volkswagen operations. The KBA transportation authority mandates cybersecurity management systems under UNECE R155 regulations for type-approved vehicles. Munich and Stuttgart host dense concentrations of ISO 27001-accredited providers serving manufacturing supply chains.
France
ANSSI national cybersecurity agency directives compel critical infrastructure operators in energy and defense sectors toward certified SOC frameworks. The EU NIS2 Directive transposition through French implementing legislation creates binding monitoring obligations for healthcare and transport entities. Paris concentrates defense-grade security clearances unavailable from commercial providers elsewhere.
United Kingdom
NCSC Cyber Assessment Framework requirements push NHS trusts and utilities toward 24/7 threat detection subscriptions. The UK GDPR retains breach notification deadlines that internal security teams struggle to satisfy without external analyst coverage. London's financial services cluster generates specialized demand for EBA-aligned outsourcing contracts.
Netherlands
Rotterdam port authority digitization and Schiphol airport critical infrastructure designation trigger mandatory SOC procurement under national NIS2 implementation. The Dutch Authority for Digital Infrastructure enforces continuous monitoring standards for designated operators. Eindhoven's high-tech systems sector concentrates mid-market buyers consolidating vendor relationships amid subscription fatigue.
Poland
Underpenetrated Central European markets lack native SOC-as-a-service providers, creating first-mover openings for accredited vendors crossing from Germany. The Polish NIS2 implementation timeline lags Western counterparts by 12-18 months, compressing procurement windows. Warsaw and Krakow emerging technology clusters show accelerating demand as GDPR enforcement intensifies.
Europe SOC As a Service Market Competitive Landscape
Listed leaders compete with private specialists across accreditation depth and response-time guarantees. The vendor landscape bifurcates sharply between ISO 27001-certified incumbents and aspirants awaiting SOC 2 Type II completion. Defense-grade clearances, hyperscale cloud partnerships, and automotive sector specialization constitute three dominant archetypes. Consolidation pressure manifests through M&A targeting regional boutiques and strategic partnerships bridging capability gaps.
Within the defense-accredited tier, Thales and Atos exemplify contrasting geographic strategies. Thales leverages its Paris headquarters and security-cleared workforce to anchor government and aerospace contracts requiring national sovereignty controls. Atos sustains broad coverage through distributed delivery centers across multiple European capitals, competing on sub-15-minute SLA guarantees. Orange Cyberdefense occupies a position between these models, combining telecom infrastructure ownership with managed security service scale.
| Leading Market Players |
|---|
| Thales |
| Atos |
| Orange Cyberdefense |
| Fortinet |
| Secureworks |
| IBM |
| Connectwise |
| BT Group |
| Accenture |
| Others |
Pricing and Supply Chain Analysis
Capacity utilization at multi-tenant cloud security platforms in Frankfurt and Paris shapes both supply concentration and subscription price floors. Scale economies from centralized analyst pools allow accredited providers to undercut in-house SOC costs while ISO 27001 certification scarcity preserves premium tiers for defense-cleared vendors.
Pricing Analysis
Certification level creates the primary spread between service tiers, with ISO 27001-accredited providers commanding substantial premiums over aspirants awaiting SOC 2 Type II completion. Three-tier pricing structure separates defense-grade sovereign offerings from commercial multi-tenant platforms and basic alert-only monitoring. Cost compression in the mid-market tier is intensifying because hyperscale cloud partnerships enable providers to absorb infrastructure scaling without proportional labor additions. Small enterprises with GDPR exposure demonstrate highest price sensitivity, while government agencies accept premium pricing for security-cleared personnel unavailable through commercial channels.
Supply Chain Analysis
Just-in-time talent deployment dominates European SOC operations, with providers maintaining floating analyst pools rather than fixed bench capacity to match elastic client demand. Human capital concentrates in France, Germany, and the United Kingdom, where certified security professionals cluster around national cybersecurity agencies and defense contractors. Technology infrastructure draws from hyperscale cloud regions in Ireland, the Netherlands, and Germany, creating single-source vulnerability when primary zones experience outages. Distribution runs through direct enterprise sales for large contracts and managed security service provider channels for mid-market penetration.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Platform economics are restructuring competitive advantage around XDR integration and API interoperability, as buyers consolidate vendor relationships to reduce subscription complexity. Ecosystem convergence between endpoint telemetry, cloud workload protection, and network monitoring is displacing point-solution contracts.
For Market Incumbents: Secure defense-grade accreditation moats by expanding security-cleared workforce pipelines in France and Germany before NIS2 implementation deadlines tighten. Deepen vertical integration into automotive telemetry analytics to capture connected vehicle monitoring contracts at BMW, Mercedes-Benz, and Volkswagen operations. Channel control through hyperscale cloud partnerships represents the critical lever against emerging AI-native entrants.
For New Entrants and Emerging Players: Lead with AI-augmented tier-1 automation to undercut incumbent labor costs and capture mid-market buyers facing subscription fatigue in the Netherlands. Poland and Czech Republic present the most penetrable geography, where native SOC-as-a-service providers remain absent and GDPR enforcement is accelerating demand. A compliance-first go-to-market emphasizing pre-certified AI components for EU AI Act readiness differentiates against established vendors with legacy workflow architectures.
For Investors and Strategic Acquirers: Mid-cycle technology positioning favors platform-plus-service bundles over pure-play managed detection contracts, as XDR consolidation fragments traditional MDR pricing models. Acquisition targets should demonstrate federated deployment capabilities for multinational banking compliance with EBA outsourcing standards. The signal to watch is NIS2 transposition timelines in Central European states, where compressed procurement windows will favor accredited entrants with pre-built delivery infrastructure.
| Strategic Initiative | Industry Significance |
|---|---|
| XDR Platform Integration | Unifies endpoint, network, and cloud telemetry for French and German mid-market buyers consolidating vendor stacks. |
| Defense-Grade Accreditation Investment | Captures ANSSI-mandated contracts for French energy and defense critical infrastructure operators. |
| AI-Augmented Tier-1 Automation | Reduces per-incident labor costs to compete for subscription-fatigued Dutch manufacturing and logistics buyers. |
| Central European Geographic Expansion | Establishes first-mover position in Poland and Czech Republic before NIS2 implementation accelerates demand. |
| Automotive Telemetry Specialization | Addresses KBA-mandated UNECE R155 cybersecurity management requirements for German connected vehicle fleets. |
Research Methodology
A standing panel of CISOs at German automotive manufacturers, French energy operators, Dutch financial institutions, and Belgian healthcare providers provided ongoing calibration across the study period. Primary interviews with SOC procurement officers, managed security service vendor executives, and national cybersecurity agency representatives combined with secondary validation from ENISA threat landscape reports, national NIS2 implementation guidance documents, and EBA outsourcing standard technical specifications. Bottom-up contract value aggregation and top-down market sizing triangulated against hyperscaler security revenue disclosures anchored volume estimates.
Consistency checks against external benchmarks validated output plausibility before finalization. The analytical framework modeled service type, deployment architecture, organization scale, and industry vertical dimensions across the projection horizon. CAGRs derived from segment-level growth rate differentials applied to base-year market values. Forecast inputs incorporated NIS2 compliance deadline phasing, connected vehicle fleet expansion trajectories, and AI-augmented automation adoption curves.
Forecasts assume regulatory continuity in EU NIS2 Directive implementation, GDPR enforcement intensity, and EBA outsourcing standard applicability; material policy shifts would require re-modeling. Outputs are directional rather than point-estimates.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Germany Cybersecurity Market
Cybersecurity
Canada Cybersecurity Market
Cybersecurity
SOC As a Service Market
Cybersecurity
Cyber Security and Big Data Analytics Market
Cybersecurity
Japan Cybersecurity Market
Cybersecurity
Norway Cybersecurity Market
Cybersecurity
Kuwait Cybersecurity Market
Cybersecurity
Asia Pacific IoT Security Market
Cybersecurity
Cloud Endpoint Protection Market
Cybersecurity
Virtualization Security Tools Market
Cybersecurity
Colombia Cybersecurity Market
Cybersecurity
North America Data Exfiltration Market
Cybersecurity
Global Cloud Encryption Market
Cybersecurity
North America Cyber Security Market
Cybersecurity
Data Security Market
Cybersecurity
Global API Security Market