
 HSM-As-A-Service Market | 2026-2036
HSM-As-A-Service Market Size, Share, and Industry Trends Forecast 2026-2036
HSM-As-A-Service Market Foresight
Germany is reconfiguring its data sovereignty infrastructure through domestic cloud HSM deployments tied to GDPR Article 32 encryption requirements. Thales leverages its European Common Criteria certifications to anchor high-assurance workloads for German automotive and banking clients. Utimaco competes through specialized hardware roots-of-trust manufactured at its Aachen facility, while Fortanix extends confidential computing integrations that abstract HSM functions into software-defined environments.
Hardware Security Module as a Service delivers FIPS 140-2 Level 3 or Common Criteria EAL4+ certified cryptographic processing through subscription-based cloud APIs, enabling organizations to generate, store, and manage keys without owning physical appliances. Cloud-based service type dominates current revenue as hyperscalers embed HSM APIs into managed key services, though hybrid deployments are capturing the fastest growth as regulated enterprises straddle on-premise legacy systems with cloud burst capacity. Finance vertical leads absolute spending due to PCI DSS and SWIFT CSP mandates, while government segments concentrate margin pools through classified workload certifications.
NIST in the United States, BSI in Germany, and ETSI in Europe collectively shape product standards through quantum-resistant algorithm transition timelines and Common Criteria evaluation schemas. PCI Security Standards Council requirements enforce HSM-backed key protection for cardholder data environments, creating non-negotiable procurement triggers. Stakeholders must monitor which certification bodies first mandate quantum-safe key encapsulation mechanisms, as this will determine competitive reordering among providers and customer migration urgency.
Market Dynamics
Post-quantum cryptography migration timelines are compressing procurement cycles across financial services and government sectors, forcing organizations to replace legacy key management infrastructure before cryptographic obsolescence renders current protections vulnerable.
Growth Catalysts
- NIST Post-Quantum Standards:Federal agencies and contractors face binding mandates to transition to quantum-resistant algorithms, triggering systematic HSM procurement across classified and unclassified systems.
- Payment Tokenization:PCI DSS 4.0 requirements for HSM-backed key protection in cardholder data environments create non-negotiable demand spikes among acquiring banks and payment processors.
- Confidential Computing Integration:Cloud providers are embedding HSM functions within trusted execution environments, enabling regulated enterprises to burst cryptographic workloads without physical appliance ownership.
Market Restraints
- Certification Bottlenecks:Common Criteria EAL4+ and FIPS 140-2 Level 3 evaluations require 12-18 month validation cycles, constraining product release velocity and feature iteration.
- Supply Concentration:Semiconductor fabrication for tamper-resistant hardware roots-of-trust concentrates among a limited set of European and Asian foundries, exposing procurement to geopolitical friction.
- Skills Scarcity:Cryptographic engineering and secure hardware design expertise pools remain shallow relative to deployment demand, inflating implementation costs and timeline risk.
Strategic Opportunities
- Edge Computing Expansion:Industrial IoT and autonomous vehicle manufacturers require distributed HSM capabilities for device attestation and secure firmware signing at manufacturing scale.
- EU Digital Identity Framework:eIDAS 2.0 mandates for qualified electronic signatures and wallet-based identity credentials will drive sovereign cloud HSM deployments across member states.
- Hybrid Architecture Adoption:Regulated enterprises are splitting key custody between on-premise hardware and cloud HSM services, creating managed orchestration service opportunities.
Industry Challenges
- Legacy System Integration:Mainframe-based financial infrastructure lacks native API compatibility with cloud HSM services, requiring costly middleware development and testing.
- Key Ceremony Complexity:Distributed key generation and multi-party computation protocols demand specialized operational procedures that most IT organizations lack mature playbooks to execute.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | HSM-As-A-Service Market |
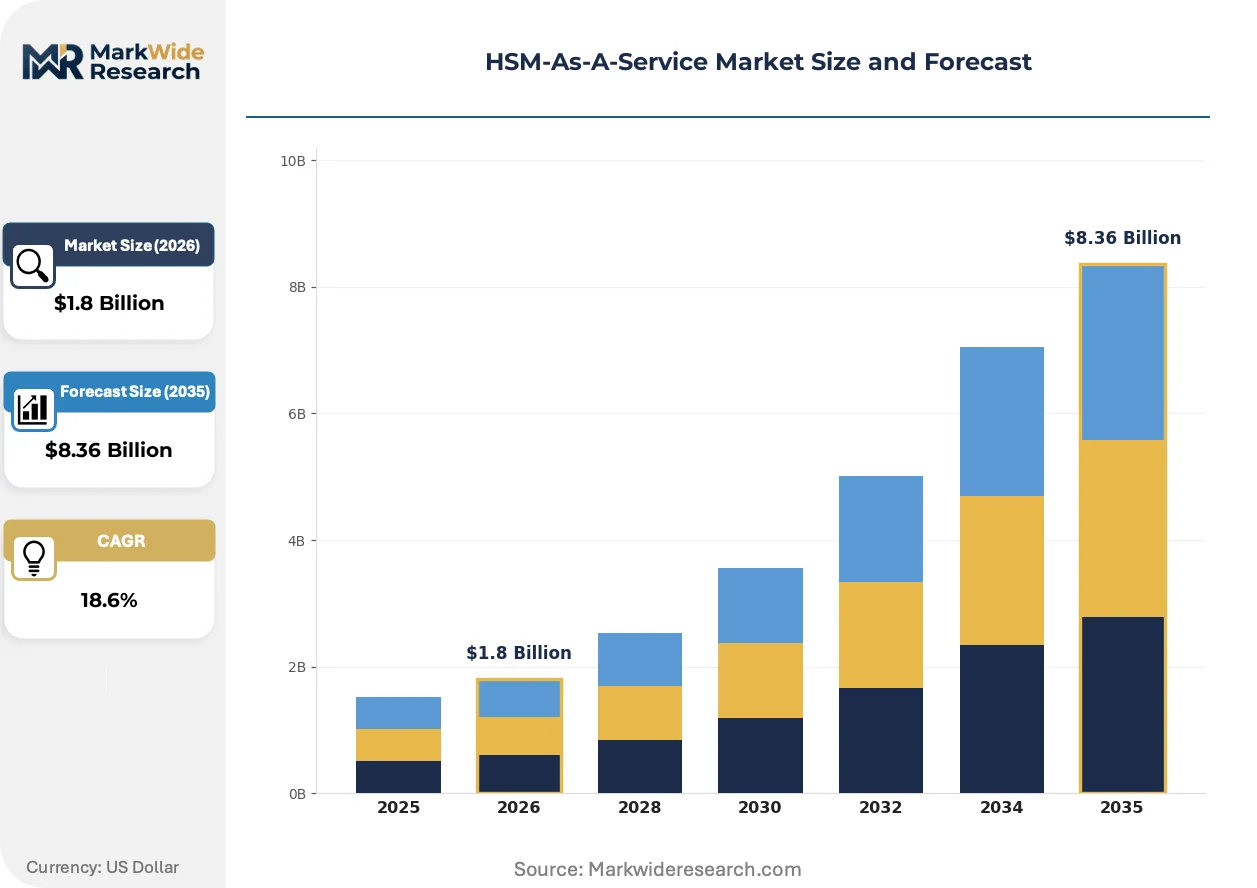
| Market Size in 2026 | $1.8 Billion |
| Market Size in 2035 | $8.36 Billion |
| CAGR (2026 – 2036) | 18.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Cloud-based, On-premise, Hybrid, Managed Industry Vertical: Finance, Healthcare, Government, Retail Deployment Model: Public Cloud, Private Cloud, Multi-Cloud, Hybrid Cloud Client Type: Small Enterprises, Mid-sized Businesses, Large Corporations, Startups |
| Companies Covered | Thales, Amazon Web Services, Microsoft, IBM, Entrust, Utimaco, Fortanix, Futurex, Atos, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
HSM-As-A-Service Market Shifts & Advancements
Three distinct vectors are restructuring how cryptographic assurance is delivered: algorithmic transitions, service model abstractions, and procurement pattern shifts. Each trend carries implications for vendor capability requirements and customer implementation roadmaps.
Confidential computing architectures are migrating from experimental deployments to production-grade key management platforms. Hyperscale cloud providers now offer HSM-backed trusted execution environments that isolate cryptographic operations from host operating systems. Financial institutions in Germany and Japan are adopting these services for payment HSM workloads that previously required dedicated physical appliances.
ETSI quantum-safe cryptography specifications are mandating crypto-agility requirements for telecommunications and critical infrastructure operators across Europe. Network equipment manufacturers must demonstrate algorithm substitution capabilities before procurement authorization. BSI in Germany has accelerated evaluation timelines for products supporting CRYSTALS-Kyber and CRYSTALS-Dilithium implementations.
Subscription-based consumption models are displacing perpetual license structures for cryptographic services. Enterprise buyers prefer operational expenditure treatment for HSM capacity that scales with transaction volume rather than peak-provisioned hardware. This pattern concentrates among mid-market financial services firms in the United States seeking PCI DSS compliance without capital-intensive infrastructure commitments.
HSM-As-A-Service Market Segmentation
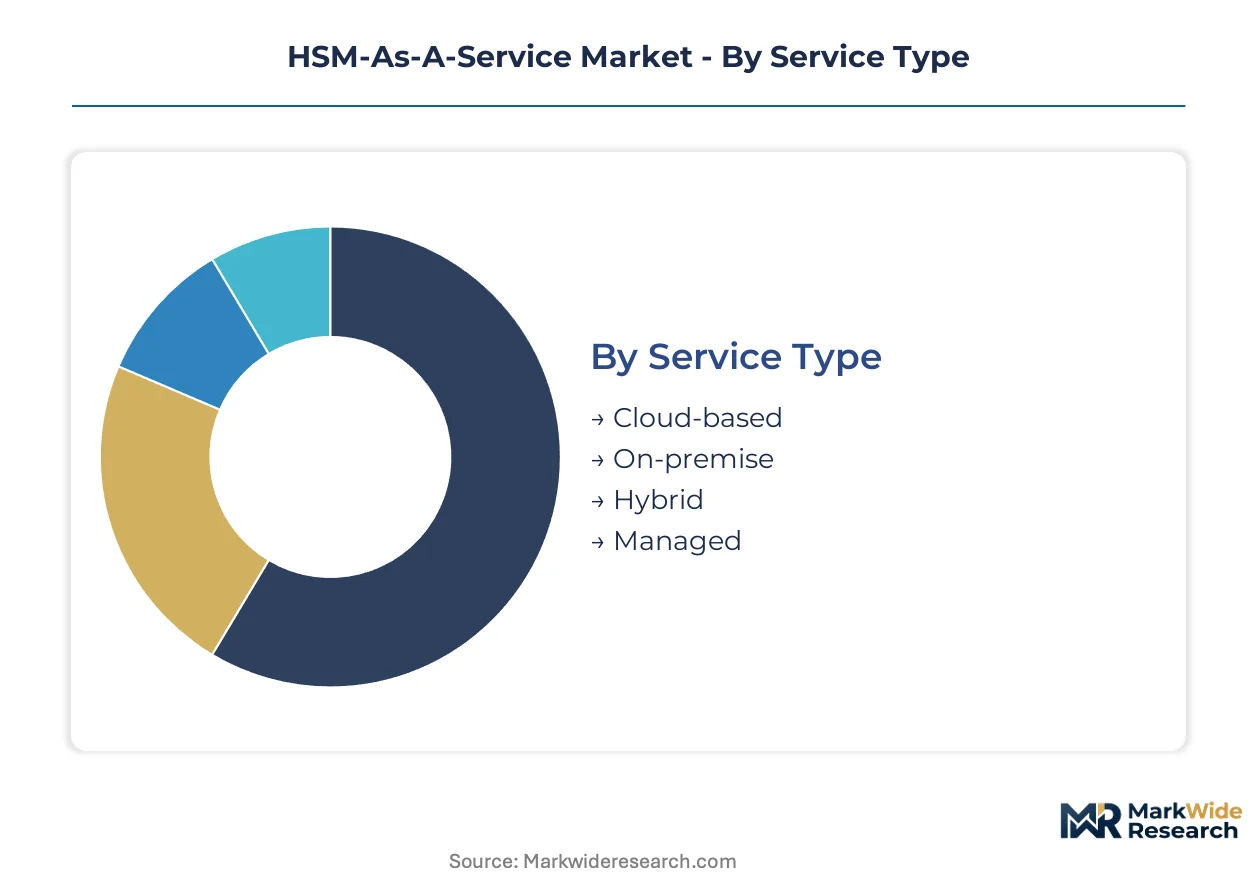
Segmentation in the HSM-As-A-Service market reveals distinct procurement rhythms across service architectures and buyer profiles. Cloud-native deployments refresh on 12-18 month cycles tied to hyperscaler roadmap updates, while on-premise hardware commitments extend 5-7 years. Understanding these cadences enables vendors to align certification investments with customer replacement windows.
Service Type:
Cycle times vary dramatically: cloud-based services turn over fastest as API versions iterate quarterly, while on-premise deployments lock in for hardware lifecycles. Hybrid models sit in the middle with 2-3 year refresh triggers.
- Cloud-based:FIPS 140-2 Level 3 certified cryptographic APIs delivered through hyperscaler marketplaces enable elastic key management without physical infrastructure. German automotive suppliers and Japanese payment processors concentrate procurement here, driven by PCI DSS 4.0 deadlines that compress migration timelines. Subscription billing aligns operational expenditure with transaction volume fluctuations.
- Hybrid:Split custody architectures anchor root keys in on-premise hardware while bursting operational keys to cloud HSM pools. United States regional banks with mainframe cores favor this model to preserve legacy investments while adding cloud agility for digital wallet launches.
- On-premise:Dedicated appliance deployments for classified government workloads requiring physical control over tamper-evident hardware modules.
- Managed:Fully outsourced key ceremonies and operational maintenance for organizations lacking cryptographic engineering benches.
Cloud-based anchors the volume base while hybrid gains share at the steepest rate.
Industry Vertical:
Margin concentration follows regulatory intensity rather than absolute spend, with government segments commanding premium pricing for classified certifications despite smaller volumes.
- Finance:PCI DSS mandates and SWIFT CSP requirements create non-negotiable procurement triggers for acquiring banks, card networks, and payment processors. Tokenization workloads for contactless payments dominate transaction volume, with United States processors leading absolute spending.
- Government:Federal agencies and defense contractors require Common Criteria EAL4+ or higher for classified systems, concentrating margin pools despite constrained volumes. NIST post-quantum migration timelines accelerate replacement cycles across civilian and intelligence community infrastructure.
- Healthcare:HIPAA encryption requirements and digital identity verification for patient portals drive adoption among hospital networks and health information exchanges.
- Retail:Point-of-sale tokenization and loyalty program fraud prevention motivate mid-market merchant acquirers seeking compliance without capital-intensive hardware.
Finance contributes the largest absolute revenue while government captures the highest margin per transaction.
Deployment Model:
Architectural choices reflect data sovereignty requirements and latency sensitivity, with multi-cloud strategies emerging as risk mitigation against vendor lock-in.
- Public Cloud:Shared HSM pools across hyperscaler availability zones deliver economies of scale for standardized cryptographic operations. United States fintech startups and mid-market payment processors cluster here, prioritizing speed-to-market over dedicated infrastructure.
- Private Cloud:Single-tenant HSM instances isolated within customer-controlled virtual networks. German automotive OEMs and Japanese banking consortiums mandate this architecture for GDPR Article 32 and domestic data localization requirements.
- Multi-Cloud:Orchestrated key management spanning AWS, Azure, and GCP deployments to prevent single-provider dependency. Enterprise buyers with geographic distribution requirements favor this model for resilience engineering.
- Hybrid Cloud:Coordinated on-premise and cloud HSM estates with unified policy enforcement. Regulated enterprises in the United States undergoing phased cloud migration adopt this transitional architecture.
Public cloud dominates transaction volume while multi-cloud deployments expand most quickly among risk-conscious enterprises.
Client Type:
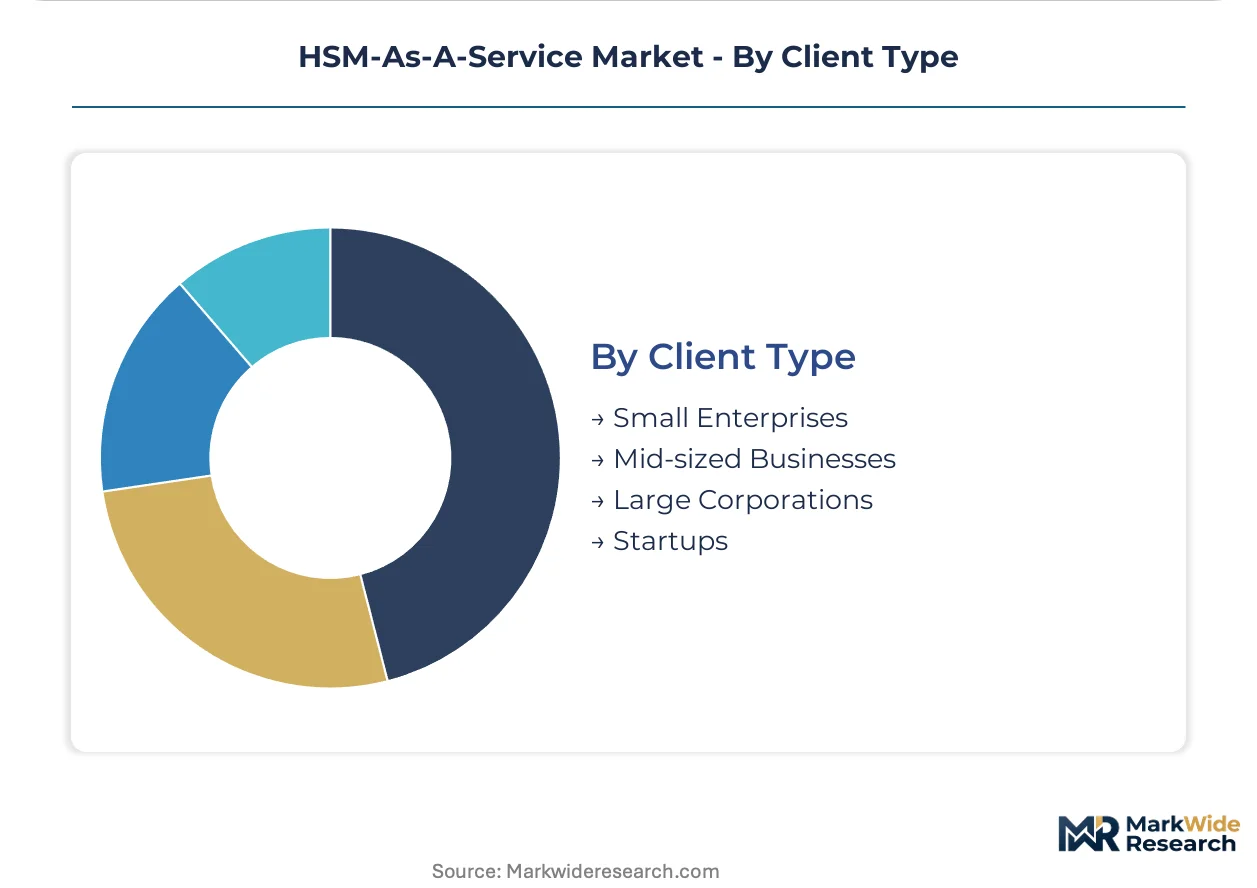
Procurement sophistication scales with organizational maturity, from API-first startups to governance-heavy multinationals with established key ceremony protocols.
- Large Corporations:Dedicated procurement teams negotiate enterprise agreements spanning multiple business units and geographic regions. United States multinational banks and German automotive groups drive standardization around Thales and Utimaco certification portfolios.
- Mid-sized Businesses:Compliance-driven buyers seeking PCI DSS or HIPAA coverage without dedicated cryptographic staff. United States regional banks and healthcare networks concentrate here, favoring managed service wrappers around cloud HSM APIs.
- Small Enterprises:Developer-centric adoption through marketplace integrations and pay-per-use billing. Payment facilitators and SaaS vendors embed HSM functions via REST APIs without operational overhead.
- Startups:Venture-backed fintechs prioritizing speed over customization, often defaulting to hyperscaler native key management services.
Large corporations anchor committed revenue while mid-sized businesses generate the steepest expansion trajectory as compliance deadlines broaden the addressable market.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The Frankfurt-Cologne railway corridor anchors Germany's data sovereignty infrastructure, channeling encrypted financial traffic between the ECB and Bundesbank. This fiber backbone underwrites European HSM procurement gravity.
United States
Federal cloud migration and NIST post-quantum mandates drive procurement across civilian and defense agencies. The SEC enforces cryptographic controls for financial market infrastructure. Northern Virginia's hyperscaler concentration hosts the bulk of FedRAMP-authorized HSM deployments for classified workloads.
Germany
Automotive OEMs and Landesbanken require GDPR Article 32 compliant key management with domestic data residency. BSI accelerates Common Criteria evaluations for quantum-safe implementations. The Aachen-Düsseldorf corridor concentrates hardware manufacturing for tamper-resistant security modules serving EU institutions.
Japan
Payment processors face Bank of Japan deadlines for SWIFT CSP compliance and contactless tokenization. METI guidelines mandate crypto-agility for critical infrastructure operators. Tokyo's financial district hosts concentrated cloud HSM deployments for yen-denominated clearing systems.
United Kingdom
Open Banking regulations and digital identity frameworks compel retail banks to modernize key management. The Financial Conduct Authority inspects HSM-backed authentication for payment initiation services. London's fintech cluster consumes managed HSM services through hyperscaler marketplaces.
India
RBI mandates hardware security modules for card networks and payment aggregators under tokenization guidelines. The Digital Personal Data Protection Act imposes encryption standards on data fiduciaries. Mumbai's banking headquarters and Bangalore's SaaS exporters drive cloud HSM adoption for UPI scale.
HSM-As-A-Service Market Competitive Landscape
Platform integrators command the system tier; component specialists sit upstream supplying certified hardware roots-of-trust. The market structures around three layers: hyperscale cloud providers operating shared HSM pools, security hardware manufacturers with Common Criteria certifications, and managed service wrappers bridging legacy infrastructure. Consolidation pressures concentrate among hardware specialists as cloud abstraction commoditizes lower-layer functions. Dominant competitive moves include strategic partnerships between cloud platforms and certified hardware vendors, plus geographic expansion through local data residency certifications.
Among European security hardware specialists, Thales and Utimaco occupy positions anchored by Common Criteria EAL4+ portfolios and domestic manufacturing footprints. Thales represents the integrated systems archetype with defense-sector lineage, while Utimaco exemplifies focused hardware specialization through its Aachen production facility. Fortanix sits within the software-defined tier, abstracting HSM functions into confidential computing environments without dedicated appliance ownership. These three anchors illustrate the competitive spectrum from physical tamper-resistance to cloud-native cryptographic services.
| Leading Market Players |
|---|
| Thales |
| Amazon Web Services |
| Microsoft |
| IBM |
| Entrust |
| Utimaco |
| Fortanix |
| Futurex |
| Atos |
| Others |
Supply & Pricing Matrix
Undercapacity at European Common Criteria evaluation laboratories is elongating certification queues to 14-18 months, compressing vendor margins and forcing buyers toward premium expedited service tiers. This utilization bottleneck simultaneously inflates upfront certification costs and concentrates pricing power among the three laboratories with EAL4+ quantum-safe evaluation authority.
Pricing Analysis
Volume-discount tiering structures separate enterprise-scale commitments exceeding 10 million annual API calls from mid-market bands at 1-10 million calls and developer tiers below 1 million. Certification grade drives the steepest price differentiation, with FIPS 140-2 Level 3 services commanding 40-60% premiums over Level 2 equivalents. Cost compression in the mid-market tier is intensifying because hyperscalers are bundling HSM functions into broader key management suites. Large multinational banks exhibit the lowest price sensitivity due to non-negotiable compliance mandates, while SaaS payment facilitators face acute margin pressure from per-transaction billing exposure.
Supply Chain Analysis
Tariff exposure between the United States and China dominates supply chain risk planning for tamper-resistant hardware modules, with BIS export controls on advanced semiconductor manufacturing equipment disrupting second-source strategies. Hardware root-of-trust fabrication concentrates in Germany, Taiwan, and South Korea, drawing from specialized silicon-on-insulator wafers, tamper-detection mesh sensors, and epoxy potting compounds with controlled thermal expansion coefficients. Single-source vulnerability persists for EAL6+ rated secure microcontrollers used in government deployments. Distribution runs through certified value-added resellers with Common Criteria audit authority rather than direct hyperscaler channels for high-assurance workloads.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The HSM-as-a-Service market rewards organizations that can marshal scarce cryptographic engineering talent and maintain synchronized certification portfolios across multiple national evaluation schemes. The gap between demand for post-quantum migration services and available implementation expertise is widening fastest in the mid-market financial segment.
For Market Incumbents: Harden certification moats by accelerating CRYSTALS-Kyber and CRYSTALS-Dilithium evaluations ahead of competitor filings, particularly at BSI and NIAP. Anchor cloud partnerships with exclusive hardware root-of-trust supply agreements that freeze out emerging software-defined entrants from physical tamper-resistance claims. Vertical integration into confidential computing silicon design at the foundry level protects margin structures against hyperscaler commoditization pressure. For New Entrants and Emerging Players: Pursue managed HSM orchestration services for United States regional banks stranded between mainframe legacy and cloud burst requirements, where incumbent hardware vendors lack API-native delivery capabilities. Target the EU Digital Identity Framework pre-certification window before eIDAS 2.0 mandates harden procurement around established Common Criteria portfolios. Lead with zero-trust key ceremony automation that eliminates the skills bottleneck blocking mid-market adoption. For Investors and Strategic Acquirers: Recurring-revenue conversion is highest among hardware-rooted vendors with multi-year government maintenance contracts and cloud-API subscription overlays. Long-term viability hinges on crypto-agility architecture that can absorb algorithm substitutions without hardware replacement cycles. Acquisition focus should center on European specialists with BSI evaluation momentum and domestic manufacturing footprints. The signal to watch is which national regulators first mandate quantum-safe key encapsulation for critical infrastructure, as this will trigger sudden procurement acceleration and vendor reordering.| Strategic Initiative | Industry Significance |
|---|---|
| Common Criteria EAL4+ Pre-Certification | BSI acceleration for CRYSTALS-Kyber implementations captures German automotive and banking procurement windows ahead of competitors. |
| Confidential Computing Integration | Embedding HSM functions within trusted execution environments isolates cryptographic operations from host infrastructure at hyperscale. |
| Hybrid Architecture Orchestration | Unified policy enforcement across on-premise hardware and cloud HSM estates preserves legacy investments while enabling digital wallet agility. |
| Post-Quantum Migration Services | Systematic algorithm transition consulting addresses NIST mandate compliance before cryptographic obsolescence renders current protections vulnerable. |
| EU Digital Identity Framework Alignment | eIDAS 2.0 qualified electronic signature pre-certification positions vendors for sovereign cloud HSM deployments across member states. |
Research Methodology
A standing panel of chief information security officers at Tier 1 banks, cloud platform engineering leads, Common Criteria evaluation laboratory directors, and payment network cryptography specialists provided ongoing calibration against operating reality. Primary fieldwork combined structured interviews with secondary validation against FIPS 140-2 validation certificates, Common Criteria evaluation reports, PCI SSC qualified security assessor filings, and hyperscaler service documentation. Bottom-up transaction volume estimates from payment processor deployments triangulated against top-down regulatory mandate timelines across the United States, Germany, and Japan.
Scenario bracketing around NIST post-quantum standard finalization dates and PCI DSS 4.0 enforcement windows bounded the projection range. Segmentation dimensions modeled include service architecture, industry vertical, deployment model, and client procurement sophistication tier. CAGRs derived from regression against historical cloud HSM adoption curves in financial services, adjusted for compliance deadline acceleration effects. Industry-specific inputs encompassed SWIFT CSP audit frequency data and Bundesbank payment infrastructure modernization schedules.
Sensitivities concentrate around Common Criteria evaluation timeline slippage, semiconductor fabrication capacity constraints for secure elements, and geopolitical friction affecting hardware root-of-trust supply continuity. Forecasts reflect assumptions regarding regulatory mandate adherence rates and cloud migration velocity among regulated enterprises. Continuous validation against operating reality is the recommended discipline.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Software & Services
Global Application Platform Market
Software & Services
Global Qualitative Data Analysis Software Market
Software & Services
Application Virtualization Market
Software & Services
Supply Chain Visibility (SCV) Software Market
Software & Services
Global Award Management Software Market
Software & Services
Global Childcare Management Software Market
Software & Services
Global MSP Software Market
Software & Services
United Kingdom HR Payroll Software Market
Software & Services
Global Automotive Software Market
Software & Services
Exploration and Production Accounting System Software Market
Software & Services
Family Office Software Solutions Market
Software & Services
Pure Play Software Testing Market
Software & Services
Global Product Information Management (PIM) Software Market
Software & Services
Courier Software Market
Software & Services
Middleware Market
Software & Services
House Cleaning App Market