
 Global Version Control Systems Market | 2026-2036
Global Version Control Systems Market Size, Share, and Industry Trends Forecast 2026-2036
Global Version Control Systems Market Foresight
GDPR Article 32 is consolidating compliance burdens around software provenance and change-tracking documentation across European enterprises. Microsoft Corporation leverages its Azure DevOps ecosystem to anchor hybrid deployment pipelines for regulated clients. GitLab differentiates through built-in security scanning and compliance dashboards that navigate FedRAMP authorization requirements in the United States.
Version control systems manage iterative modifications to digital assets through delta encoding, branching algorithms, and cryptographic commit hashing to preserve complete audit trails of source-code evolution. These systems enable concurrent engineering workflows, rollback capabilities, and forensic accountability across distributed development teams. Cloud-based deployment leads solution architecture as enterprises abandon self-hosted infrastructure maintenance, while distributed version control dominates solution type adoption due to Git's decentralized branching model and offline commit capabilities. The financial services end user industry generates concentrated margin pools from compliance-intensive contract values.
The U.S. SEC, EU EMA, and Japan's METI each enforce traceability standards that elevate version control from developer convenience to regulatory infrastructure. FDA 21 CFR Part 11 in the United States and EU MDR technical documentation requirements in Europe explicitly mandate timestamped, immutable change records that only enterprise-grade version control platforms can satisfy. Stakeholders must evaluate whether their current repository architecture can withstand forthcoming AI-generated code attribution rules from multiple national regulators.
Market Dynamics
Regulatory mandates for immutable audit trails are compressing procurement cycles as financial services and healthcare enterprises replace legacy source-code repositories with compliant Git-based infrastructure before enforcement deadlines.
Growth Catalysts
- FDA 21 CFR Part 11:Pharmaceutical manufacturers in the United States must maintain timestamped, unalterable change records for software used in medical device production, forcing enterprise VCS upgrades.
- AI-generated code attribution:National regulators across multiple jurisdictions are drafting rules requiring provenance tracking for machine-authored commits, expanding platform feature requirements.
- Financial services:SEC audit-trail mandates for algorithmic trading systems are driving contract values for compliant repository hosting among investment banks and hedge funds.
Market Restraints
- Cloud concentration risk:Three hyperscale providers control the majority of SOC 2 attested repository hosting, creating single-point-of-failure exposure for regulated enterprises.
- Legacy Perforce migration costs:Aerospace and defense contractors face seven-figure re-platforming expenses to convert monolithic codebases to distributed version control architectures.
- EU GDPR Article 32 friction:Cross-border data residency requirements for source-code repositories complicate multi-national deployment strategies and inflate compliance overhead.
Strategic Opportunities
- India's PLI scheme for electronics manufacturing:Contract electronics manufacturers building for export markets require FedRAMP-equivalent documentation systems, opening demand for authorized VCS platforms.
- SBOM (Software Bill of Materials) mandates:The US executive order on supply chain security is creating embedded compliance modules as a new revenue stream for repository vendors.
- Edge development convergence:GitOps workflows for Kubernetes-orchestrated IoT firmware updates are merging version control with deployment automation in industrial automation settings.
Industry Challenges
- Git-native security expertise scarcity:Enterprise security teams lack personnel trained in cryptographic commit signing and supply chain attack vectors specific to distributed repositories.
- FedRAMP authorization timelines:Cloud-based VCS providers face 12-18 month certification cycles that delay entry into federal contracting channels.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Version Control Systems Market |
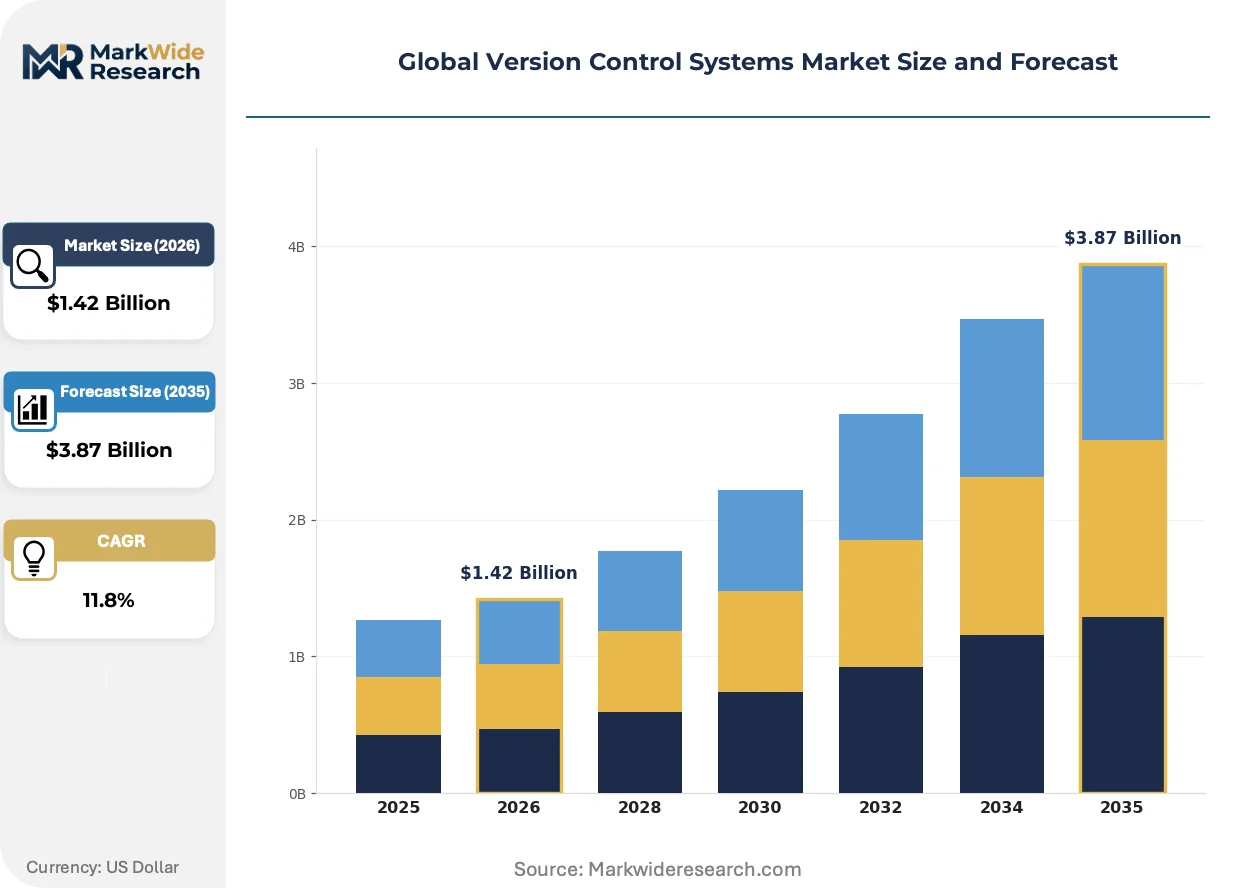
| Market Size in 2026 | $1.42 Billion |
| Market Size in 2035 | $3.87 Billion |
| CAGR (2026 – 2036) | 11.8% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: Cloud-Based, On-Premise, Hybrid, Hosted, Managed, Virtual Solution Type: Centralized Version Control, Distributed Version Control, Lock-Based, Snapshot, Transaction-Based Use Case: Software Development, Content Management, Configuration Management, Documentation Tracking, Code Review, Collaboration End User Industry: IT & Telecom, Media & Entertainment, Government Agencies, Education Sector, Financial Services, Research & Development |
| Companies Covered | Microsoft Corporation, IBM Corporation, Perforce Software, GitHub, GitLab, Apache Software Foundation, Canonical, Broadcom, Micro Focus, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Version Control Systems Market Shifts & Advancements
Immutable infrastructure patterns are merging version control with runtime deployment, collapsing the boundary between source-code management and production system state. This convergence is reshaping platform architecture and procurement criteria simultaneously.
GitOps operational models are decentralizing the relationship between repository commits and live system configuration. Platform engineering teams at SaaS providers are adopting this pattern to eliminate configuration drift, with the technology compressing incident response times by treating infrastructure as versioned artifacts. The structural consequence is that VCS platforms must now integrate with Kubernetes orchestration layers to remain competitive.
EU AI Act documentation requirements are mandating versioned model cards and training-data provenance for high-risk artificial intelligence systems. Medical device and credit-scoring algorithm developers must maintain immutable records of model evolution, with the regulation forcing repository vendors to expand metadata capabilities. German automotive manufacturers and French healthcare AI specialists are prioritizing platforms with built-in ML pipeline tracking.
Consumption patterns among mid-market software vendors are rotating toward usage-based repository pricing that scales with CI/CD pipeline execution minutes rather than seat licenses. This shift is displacing traditional per-developer subscription models, with the change most visible among Series B and C funded startups in Israel and Singapore that prioritize variable cost structures aligned with release frequency.
Global Version Control Systems Market Segmentation
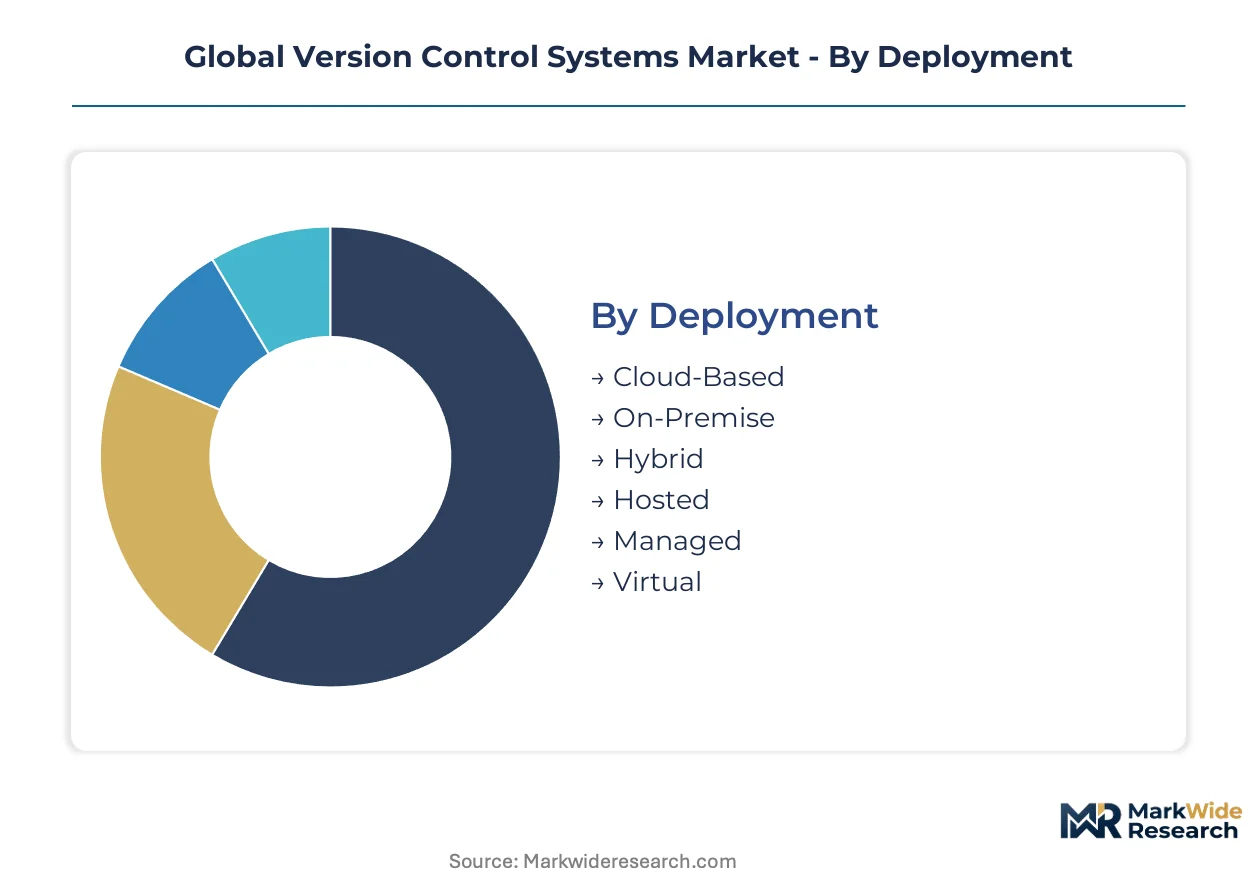
Version control platforms serve radically different operational contexts depending on deployment architecture, control model, and regulatory exposure. Procurement committees evaluate segments through integration depth, compliance surface area, and total cost of ownership rather than feature checklists alone.
Deployment:
Standalone deployments isolate version control from broader DevOps pipelines, while embedded configurations merge repository management with CI/CD orchestration, security scanning, and policy enforcement layers.
- Cloud-Based:Multi-tenant SaaS architectures with SOC 2 and FedRAMP attestation dominate procurement at financial services firms in the United States and Germany. The SEC's audit-trail mandates for algorithmic trading systems compress sales cycles for compliant cloud repositories.
- On-Premise:Self-managed infrastructure in air-gapped data centers persists at defense contractors and classified research facilities. Japan's METI cybersecurity guidelines for critical infrastructure operators sustain demand despite higher operational overhead.
- Hybrid:Split configurations keep sensitive codebases on-premise while routing collaboration workflows through cloud gateways. India's contract electronics manufacturers building for export markets favor this model under PLI scheme documentation requirements.
- Hosted:Single-tenant cloud instances managed by vendor operations teams reduce internal DevOps burden. French healthcare AI developers select hosted options to satisfy EU AI Act model-card versioning mandates without building compliance infrastructure.
- Managed:Fully outsourced repository administration including patching, backup, and access provisioning. Mid-market software vendors in Singapore and Israel adopt managed services to redirect engineering headcount toward product development.
- Virtual:Containerized deployment on private Kubernetes clusters with elastic scaling. German automotive manufacturers deploying GitOps for industrial IoT firmware updates drive specialized demand here.
Cloud-Based deployments lead volumes today; Hybrid configurations are gaining share fastest as regulated enterprises seek compartmentalized risk exposure.
Solution Type:
Architectural philosophy determines branching complexity, offline capability, and merge conflict resolution—factors that shape team productivity and repository scalability.
- Distributed Version Control:Git's decentralized model enables offline commits, lightweight branching, and cryptographic provenance tracking. The FDA's 21 CFR Part 11 requirements for unalterable change records accelerate enterprise Git migrations in United States pharmaceutical manufacturing.
- Centralized Version Control:Single-source-of-truth architectures with file-level locking suit binary asset management. Legacy installations at aerospace contractors face seven-figure re-platforming costs as talent pools shift toward Git-native expertise.
- Lock-Based:Exclusive checkout mechanisms prevent concurrent modification conflicts on large binary files. Game development studios in South Korea and Canada maintain lock-based workflows for uncompressed art assets and cinematic sequences.
- Snapshot:Full-repository state captures at commit time rather than delta encoding. Financial services stress-testing environments in Switzerland and the United Kingdom use snapshot systems for instant environment reproduction.
- Transaction-Based:ACID-compliant commit sequences guaranteeing atomic state transitions. High-frequency trading system developers in Chicago and London select transaction-based platforms for deterministic rollback capabilities.
Distributed Version Control dominates commercial adoption; Transaction-Based systems show the steepest expansion trajectory among algorithmic trading infrastructure teams.
Use Case:
Functional application determines metadata requirements, access pattern intensity, and integration surface area with adjacent enterprise systems.
- Software Development:Source-code versioning with branch protection, pull request workflows, and CI/CD triggers. Israel's cybersecurity startup cluster generates concentrated demand for repository platforms with embedded SAST and DAST scanning.
- Configuration Management:Infrastructure-as-code versioning for Kubernetes manifests, Terraform modules, and policy definitions. GitOps adoption at SaaS providers in Sweden and the Netherlands collapses incident response times by treating live system state as versioned artifacts.
- Code Review:Structured annotation, approval gates, and merge quality enforcement. India's software export houses deploy dedicated code review instances to satisfy client SLA documentation requirements.
- Documentation Tracking:Versioned technical writing, API specifications, and compliance artifacts. EU MDR technical documentation mandates in Germany and France drive pharmaceutical manufacturers toward documentation-native repository features.
- Content Management:Binary asset versioning for marketing materials, design files, and multimedia. Media conglomerates in Brazil and Mexico manage localized content variants through repository branching strategies.
- Collaboration:Real-time co-editing, comment threading, and notification routing. Remote-first development teams in Portugal and Poland prioritize collaboration modules to replace synchronous standup dependencies.
Software Development anchors revenue concentration; Configuration Management is climbing the fastest as platform engineering teams consolidate tooling stacks.
End User Industry:
Regulatory exposure and software intensity create divergent willingness-to-pay profiles across vertical markets.
- Financial Services:Investment banks, hedge funds, and insurance carriers with algorithmic trading and risk system development. The SEC's forthcoming AI-generated code attribution rules expand platform feature requirements for United States and United Kingdom institutions.
- IT & Telecom:Cloud service providers, network equipment manufacturers, and telecommunications operators. South Korean chaebol electronics groups and Finnish telecom infrastructure vendors drive volume through multi-thousand seat deployments.
- Government Agencies:Defense, civilian, and intelligence applications with classified handling requirements. FedRAMP authorization timelines of 12-18 months filter vendor eligibility for United States federal contracts.
- Research & Development:Academic institutions, national laboratories, and corporate innovation centers. CERN's distributed computing infrastructure and Japan's RIKEN research network sustain specialized repository customization demand.
- Media & Entertainment:Streaming platforms, game studios, and production houses managing large binary assets. Vancouver and Montreal post-production clusters require lock-based versioning for uncompressed video sequences.
- Education Sector:University computer science departments and vocational training programs. Massive open online course platforms in India and Indonesia generate seat-license volume with limited customization requirements.
IT & Telecom captures the largest seat-count deployments; Financial Services commands the highest contract values per seat through compliance-intensive procurement.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The version control systems industry traces its commercial origins to the United States, where early distributed computing research at Bell Labs and subsequent open-source movements established the foundational protocols that now dominate enterprise software development workflows worldwide.
United States
Financial services firms in New York and Chicago drive premium contract values for FedRAMP-authorized repository platforms. SEC audit-trail mandates for algorithmic trading systems compress procurement timelines at investment banks and hedge funds. Silicon Valley's SaaS provider cluster accelerates GitOps adoption for Kubernetes-orchestrated infrastructure management.
Germany
Automotive manufacturers in Stuttgart and Munich require version control platforms with embedded ML pipeline tracking for EU AI Act compliance. The country's national automotive regulator enforces strict documentation standards for autonomous driving software provenance. Bavaria's industrial automation sector merges repository management with edge deployment workflows for IoT firmware updates.
India
Contract electronics manufacturers in Karnataka and Tamil Nadu seek FedRAMP-equivalent documentation systems under the PLI scheme for export markets. The country's national electronics regulator mandates traceability infrastructure for semiconductor assembly operations. Hyderabad's cybersecurity startup cluster generates concentrated demand for repository platforms with integrated SAST and DAST scanning capabilities.
Japan
Pharmaceutical manufacturers in Tokyo and Osaka upgrade to Git-based infrastructure to satisfy PMDA timestamped record requirements for medical device software. METI cybersecurity guidelines for critical infrastructure operators sustain on-premise deployment demand despite higher operational overhead. Nagoya's automotive electronics suppliers integrate version control with deterministic rollback capabilities for safety-critical systems.
United Kingdom
Investment banks in the City of London prepare for forthcoming AI-generated code attribution rules from national regulators. The Financial Conduct Authority's operational resilience requirements elevate repository architecture to regulatory infrastructure status. Cambridge's research technology corridor sustains specialized demand for repository customization in academic and national laboratory settings.
Global Version Control Systems Market Competitive Landscape
The competitive structure tilts toward hyperscale cloud providers with compliance attestation capabilities. Three dominant platforms control the majority of SOC 2 attested repository hosting, creating concentrated supply-side dynamics. Strategic archetypes include vertically integrated DevOps suite vendors, standalone repository specialists with security differentiation, and open-source foundation-backed community editions. Dominant competitive moves encompass strategic partnerships with Kubernetes orchestration providers and portfolio diversification into embedded SBOM compliance modules.
Within the hyperscale-integrated tier, Microsoft Corporation exemplifies the vertically integrated DevOps suite archetype through its Azure ecosystem anchoring. GitLab occupies a position representing the standalone specialist path with built-in security scanning capabilities. Perforce Software exemplifies the legacy migration challenge archetype serving aerospace and defense contractors with monolithic codebase requirements.
| Leading Market Players |
|---|
| Microsoft Corporation |
| IBM Corporation |
| Perforce Software |
| GitHub |
| GitLab |
| Apache Software Foundation |
| Canonical |
| Broadcom |
| Micro Focus |
| Others |
Supply & Pricing Matrix
Financial services procurement committees at investment banks and hedge funds concentrate demand for FedRAMP-authorized cloud repositories, anchoring premium subscription tiers that scale with compliance attestation levels rather than seat counts alone.
Pricing Analysis
Three-tier pricing structure across premium, standard, and economy levels dominates commercial procurement. Premium tiers command substantial markups for SOC 2 Type II and FedRAMP authorization, while standard tiers serve mid-market vendors with basic audit-trail capabilities. Cost compression in economy tiers is intensifying because hyperscale providers bundle repository services with broader cloud commitments. Financial services buyers show the least price sensitivity due to regulatory mandate pressure, whereas education sector procurement exhibits the highest elasticity.
Supply Chain Analysis
FedRAMP and ISO 27001 certification gating restricts viable infrastructure suppliers to a narrow tier of hyperscale cloud operators. Primary compute capacity concentrates in the United States, Germany, and Ireland, with secondary redundancy nodes in Singapore and Japan. Platform development draws from cryptographic engineering talent pools, open-source Git protocol maintenance, and Kubernetes orchestration expertise. Single-source vulnerability in cloud substrate provisioning creates systemic exposure for regulated enterprises. Distribution runs through direct enterprise sales teams and hyperscaler marketplace integrations.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Margin expansion trajectories in version control systems rest on compliance module upselling and managed service tier penetration, with automation reducing per-customer operational overhead as the primary cost-down driver.
For Market Incumbents: Deploy embedded security scanning modules as a defensive perimeter against standalone DevSecOps specialists. Incumbents should deepen upstream control over Kubernetes orchestration layers to lock in GitOps workflow dependencies. FedRAMP authorization maintenance creates switching costs that protect contract renewals from emerging cloud-native competitors. For New Entrants and Emerging Players: The pricing gap between premium FedRAMP-authorized tiers and economy self-hosted alternatives creates entry space for mid-market hybrid deployment specialists. New entrants should prioritize India's PLI scheme documentation requirements as the most penetrable geography, targeting contract electronics manufacturers with FedRAMP-equivalent compliance without full federal authorization overhead. A channel partnership strategy with systems integrators accelerates credential transfer. For Investors and Strategic Acquirers: Hyperscale cloud providers are the most active acquirer in this space, seeking to fill DevOps suite gaps through repository platform consolidation. Long-term viability hinges on AI-generated code attribution feature readiness as regulatory mandates materialize. Acquisition targets should demonstrate embedded SBOM generation capabilities and active ML pipeline tracking development. The signal to watch is FDA draft guidance on machine-authored commit provenance.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Merging version control with Kubernetes orchestration layers collapses toolchain fragmentation for GitOps adopters. |
| Strategic Partnership | Alliances with hyperscale cloud providers accelerate FedRAMP authorization timelines for repository vendors. |
| Acquisition of Specialist Firm | Consolidating embedded security scanning capabilities defends against standalone DevSecOps competitors. |
| Geographic Expansion | Establishing India operations captures PLI scheme demand from contract electronics manufacturers. |
| Product Launch | SBOM compliance modules address US executive order supply chain security mandates for federal contractors. |
Research Methodology
Direct dialogue with platform engineering directors, enterprise security architects, federal procurement officers, and DevOps tooling specialists grounded qualitative findings. Secondary validation drew from SEC regulatory filings, FedRAMP authorization databases, hyperscaler capex disclosures, and EU AI Act implementation guidance. Bottom-up deployment model sizing and top-down regulatory mandate impact assessment were cross-triangulated for convergence.
Segment-level value outputs across the projection horizon reflect deployment architecture, solution type, and end-user industry stratification. The analytical framework modeled cloud-based, on-premise, hybrid, hosted, managed, and virtual deployment configurations alongside distributed, centralized, lock-based, snapshot, and transaction-based control philosophies. CAGRs were derived from regulatory enforcement timeline alignment and enterprise migration pattern velocity, with AI-generated code attribution rule development and SBOM mandate expansion as key scenario inputs.
Caveats apply where FedRAMP authorization timeline delays, EU GDPR Article 32 cross-border enforcement shifts, or AI attribution rule finalization could materially shift the outlook. Forecasts embed assumptions around compliance deadline adherence and hyperscaler pricing discipline. A model refresh is warranted upon material change in SEC algorithmic trading audit-trail enforcement intensity.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Software & Services
Attendance Management Software Market
Software & Services
Point Cloud Processing Software Market
Software & Services
Over the Air (OTA) Updates Market
Software & Services
Chromatography Data System (CDS) Software Market
Software & Services
Fiber Simulation Software Market
Software & Services
User Interface Software Market
Software & Services
Webcasting Software Market
Software & Services
Global Retail Execution Software Market
Software & Services
Simulation Software Market
Software & Services
Information Technology Service Management (ITSM) Market
Software & Services
Feedback Management Software Market
Software & Services
Global Nosql Software Market
Software & Services
Balance Sheet Management Software Market
Software & Services
Global Document Control Software Market
Software & Services
Automotive Operating Systems Market
Software & Services
App Building Software Market