
 Global Zero-Trust Security Market | 2026-2036
Global Zero-Trust Security Market Size, Share, and Industry Trends Forecast 2026-2036
Global Zero-Trust Security Market Foresight
The zero-trust security market is pivoting on a widening capability gap between integrated platform suites and point-product vendors. Palo Alto Networks leverages its Prisma SASE consolidation to anchor enterprise contracts spanning identity, network, and endpoint controls. Zscaler competes through cloud-native proxy architecture that eliminates on-premises hardware dependencies. CrowdStrike differentiates via endpoint telemetry that feeds real-time risk scoring into conditional access engines.
Zero-trust security denotes an architectural framework requiring continuous verification of every user, device, and transaction regardless of network location, typically enforced through software-defined perimeters, micro-segmentation policies, and identity-aware proxies operating at sub-100-millisecond latency thresholds. Its primary commercial purpose is to contain breach lateral movement in hybrid cloud environments where traditional castle-and-moat defenses fail. Cloud-based deployment leads solution delivery as enterprises abandon capital-intensive appliance refresh cycles, while identity and access management captures disproportionate margin pools due to federation complexity and privileged access governance requirements. Network security and endpoint security segments sustain parallel growth as organizations layer complementary controls rather than relying on single-vector protection.
FDA cybersecurity guidance for connected medical devices, FCC supply chain security rules, and NIST SP 800-207 zero-trust architecture standards collectively reshape product requirements and procurement criteria across regulated sectors. The SEC's cybersecurity disclosure rules further compel publicly traded firms to document identity governance and network segmentation controls in regulatory filings. Stakeholders must monitor how fragmentation between vendor-specific zero-trust implementations affects interoperability and switching costs as the technology matures.
Market Dynamics
Continuous verification architectures are displacing perimeter-based security models as enterprises confront distributed workforce access patterns and cloud-native application sprawl. This structural pivot compresses hardware refresh cycles while expanding recurring software revenue pools across identity federation and network segmentation layers.
Growth Catalysts
- US Federal Zero-Trust Mandates:Civilian agencies face statutory deadlines requiring architecture overhauls, creating immediate procurement pull through 2027.
- EU AI Act and NIS2 Directives:European enterprises must replace castle-and-moat defenses with continuous verification frameworks or face operational penalties.
- Connected Medical Device Expansion:FDA cybersecurity guidance for hospital networks drives micro-segmentation demand across healthcare delivery organizations.
Market Restraints
- Skilled Identity Architect Scarcity:Federation protocol expertise concentrates among specialists in the United States and Germany, inflating implementation timelines.
- Legacy Directory Migration Friction:Active Directory dependencies in financial services create technical debt that slows cloud-native proxy adoption.
- Cross-Border Data Localization:China's MIIT and Russia's data sovereignty rules fragment policy orchestration across multinational deployments.
Strategic Opportunities
- Operational Technology Convergence:IT/OT network segmentation in manufacturing plants pairs zero-trust micro-segmentation with industrial protocol gateways.
- India's Digital Public Infrastructure:Aadhaar-linked identity verification creates a regulatory tailwind for conditional access vendors serving BFSI and government sectors.
- API Security as Distribution Channel:Cloud-native API gateways embed zero-trust policies at the application layer, bypassing traditional network hardware procurement.
Industry Challenges
- Certificate Lifecycle Management:Machine identity volumes in Kubernetes clusters overwhelm existing PKI operations teams, requiring automated rotation tooling.
- Multi-Vendor Policy Orchestration:Interoperability gaps between vendor-specific zero-trust implementations force enterprises into costly integration layers.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Zero-Trust Security Market |
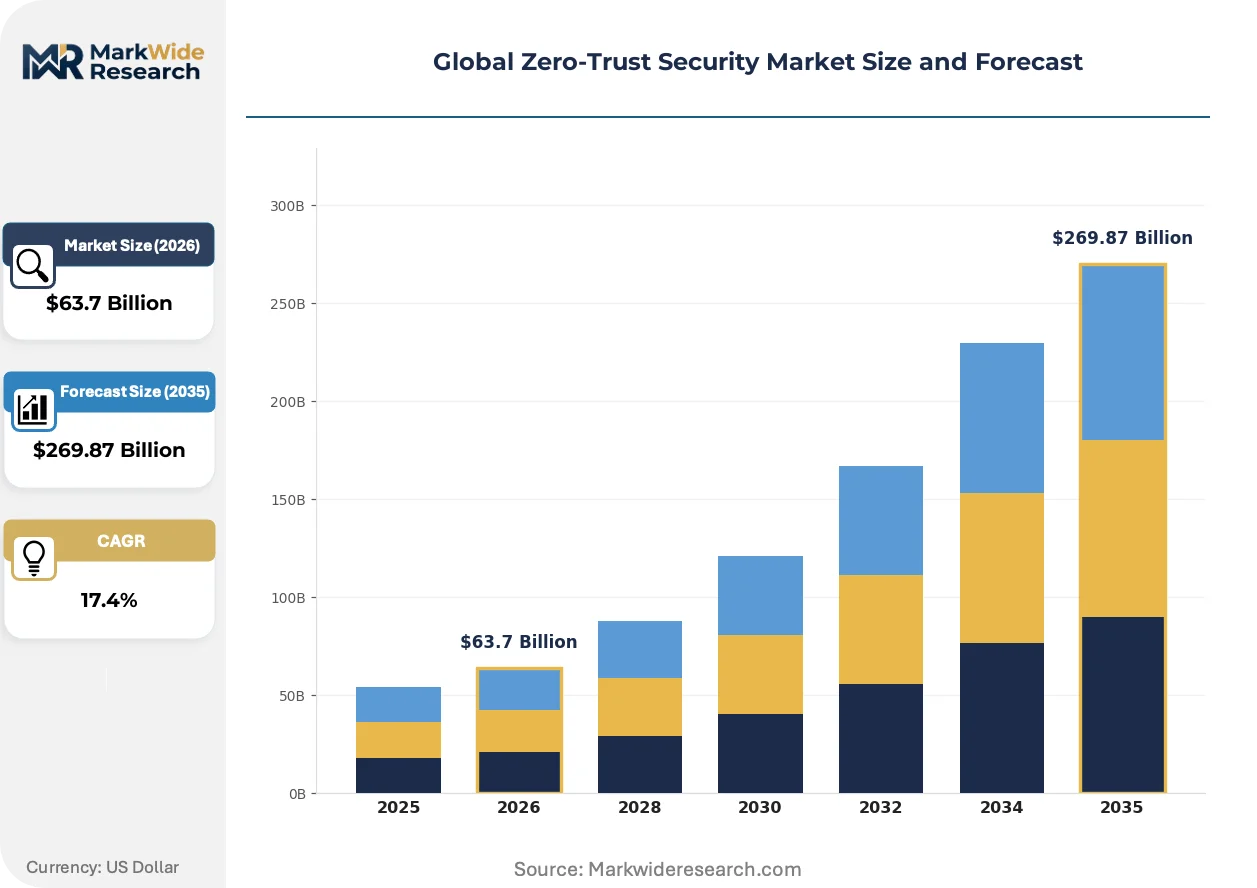
| Market Size in 2026 | $63.7 Billion |
| Market Size in 2035 | $269.87 Billion |
| CAGR (2026 – 2036) | 17.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: Cloud-Based, On-Premises, Hybrid, Edge, Multi-Cloud Solution Type: Identity & Access Management, Network Security, Endpoint Security, Data Loss Prevention, Security Analytics, Micro-Segmentation Application: Financial Institutions, Government Agencies, Telecommunications, Manufacturing, Education, Transportation End User: Large Enterprises, Small & Medium Enterprises, Managed Security Service Providers, Cloud Service Providers, System Integrators |
| Companies Covered | Palo Alto Networks, Zscaler, Cisco Systems, Microsoft, Fortinet, Check Point Software Technologies, IBM, Cloudflare, CrowdStrike, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Zero-Trust Security Market Shifts & Advancements
Artificial intelligence is compressing threat detection latency from minutes to milliseconds while reshaping how security policies adapt to behavioral anomalies. This convergence of inference speed and policy automation is redrawing competitive boundaries between platform vendors and point-product specialists.
Security orchestration platforms are automating policy adjustments based on real-time risk scoring derived from endpoint telemetry and network flow analysis. Financial institutions in Singapore and the United Kingdom deploy these systems to enforce dynamic access controls without human intervention during trading hours. The technology is automating what previously required security operations center analysts, collapsing response windows and reducing headcount growth in mature enterprises.
The EU AI Act's risk classification system for biometric authentication is forcing vendors to reengineer facial recognition and behavioral analysis modules for high-stakes use cases. Medical device manufacturers must now document continuous verification controls in pre-market submissions to notified bodies. European healthcare networks are responding by consolidating vendor relationships around platforms with pre-validated compliance mappings rather than assembling point products.
Buyer preference for consolidated security service edge contracts is displacing multi-vendor best-of-breed procurement in mid-market enterprises. Channel partners in Australia and Canada now bundle identity, network, and endpoint controls into single subscription offerings. Manufacturing verticals with lean IT staff show the strongest concentration of this behavior, trading customization depth for operational simplicity and unified support.
Global Zero-Trust Security Market Segmentation
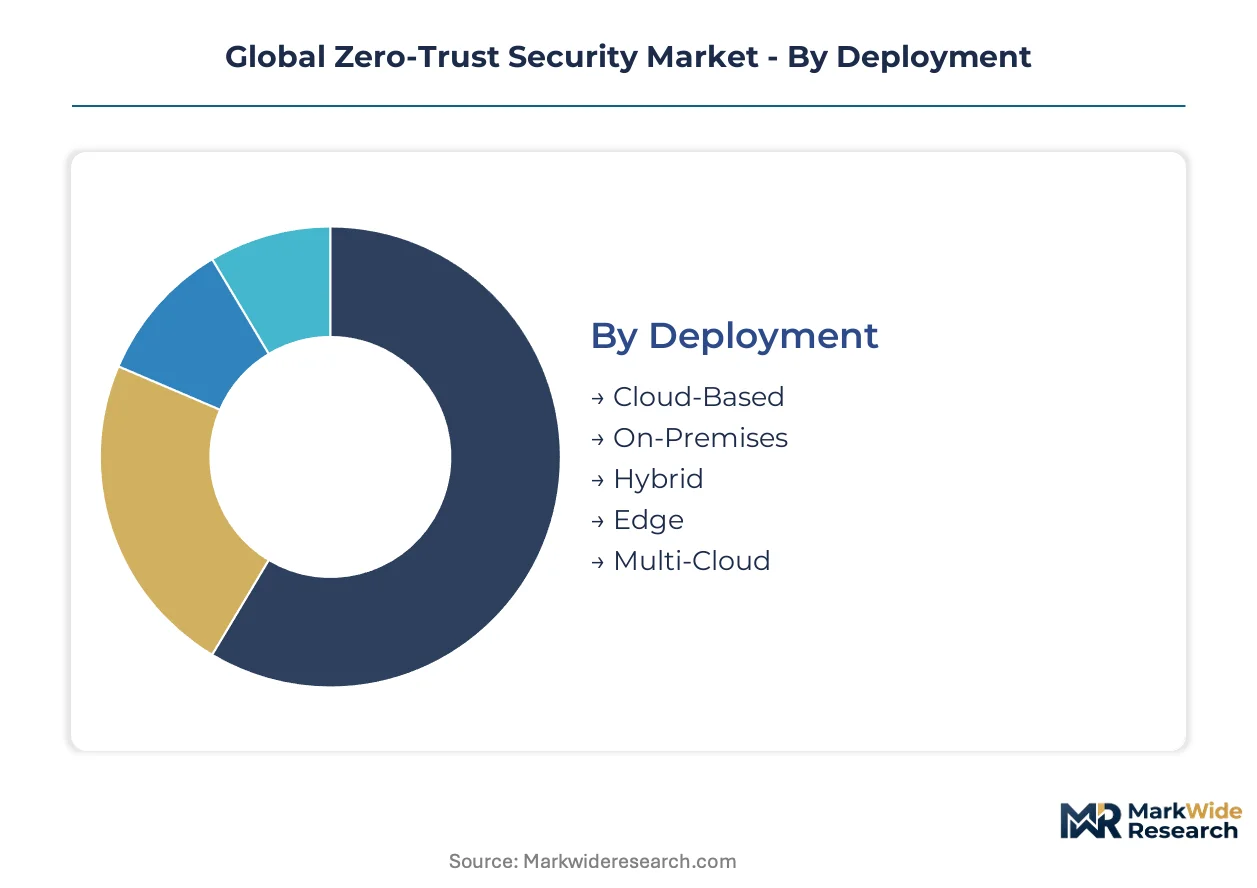
Zero-trust architectures fragment across deployment models, solution layers, and buyer sophistication tiers. Each segment carries distinct certification burdens from NIST, ISO 27001, and sector-specific regulators that shape procurement eligibility and implementation timelines.
Deployment:
FDA cybersecurity guidance for connected medical devices, FCC supply chain security rules, and China's MIIT data localization mandates each favor different deployment topologies.
- Cloud-Based:Fully managed SaaS delivery eliminates capital expenditure cycles. Financial institutions in Singapore and the United Kingdom favor this model for dynamic access controls during trading hours, though cross-border data residency requirements complicate multi-national rollouts.
- Hybrid:Combines on-premises identity stores with cloud-native policy enforcement. Manufacturing verticals with lean IT staff adopt this pattern to preserve Active Directory investments while layering continuous verification for cloud workloads.
- On-Premises:Retains hardware control for classified government networks. Defense contractors in the United States maintain this deployment to satisfy NIST SP 800-207 audit requirements.
- Edge:Distributes policy enforcement to factory floors and retail locations. Industrial protocol gateways in German automotive plants embed micro-segmentation at the network edge.
- Multi-Cloud:Orchestrates consistent policies across AWS, Azure, and Google Cloud estates. European enterprises responding to EU AI Act risk classifications adopt this to avoid vendor lock-in.
Cloud-Based sits at the top of the volume ranking, with Edge climbing the fastest.
Solution Type:
Margin concentration varies sharply across the stack, with identity federation commanding premium pricing due to protocol complexity.
- Identity & Access Management:Federation and privileged access governance form the commercial core. Banks in India link Aadhaar verification to conditional access engines, creating regulatory tailwinds for vendors serving BFSI sectors.
- Network Security:Software-defined perimeters and identity-aware proxies replace VPN appliances. Australian channel partners bundle these controls into unified security service edge subscriptions for mid-market buyers.
- Endpoint Security:Telemetry feeds real-time risk scoring into access decisions. CrowdStrike's architecture exemplifies this integration, collapsing detection-to-response windows.
- Micro-Segmentation:Container and Kubernetes workload isolation. Certificate lifecycle management automation becomes critical as machine identity volumes overwhelm PKI teams.
- Data Loss Prevention:Content inspection at application layer boundaries. Healthcare networks consolidate around platforms with pre-validated EU MDR compliance mappings.
- Security Analytics:Behavioral anomaly detection using AI inference. Singaporean financial institutions deploy these systems to automate policy adjustments without human intervention.
Identity & Access Management captures the highest margin pool, while Micro-Segmentation expands most quickly.
Application:
Regulatory intensity determines solution depth, with healthcare and finance facing the most stringent continuous verification mandates.
- Financial Institutions:Trading floor latency requirements drive sub-100-millisecond policy enforcement. SEC cybersecurity disclosure rules compel documentation of identity governance controls in regulatory filings.
- Government Agencies:US federal zero-trust mandates create statutory procurement deadlines through 2027. Civilian agencies overhaul architectures to satisfy NIST standards.
- Telecommunications:5G network slicing requires subscriber authentication at massive scale. FCC supply chain security rules reshape equipment vendor selection criteria.
- Manufacturing:IT/OT convergence demands industrial protocol gateways alongside micro-segmentation. German plants pair zero-trust controls with operational technology segmentation.
- Education:Distributed campus access patterns favor cloud-native proxy architectures. Budget constraints push toward consolidated platform contracts rather than point-product assembly.
- Transportation:Connected vehicle and logistics platform security. NHTSA guidance on automotive cybersecurity influences supplier requirements.
Financial Institutions anchor revenue concentration, with Manufacturing gaining share fastest.
End User:
Implementation capability gaps separate buyers who self-deploy from those requiring managed services.
- Large Enterprises:Internal identity architect teams handle multi-vendor orchestration. Skilled federation protocol scarcity in the United States and Germany inflates their implementation timelines.
- Managed Security Service Providers:Deliver zero-trust as-a-service to capability-constrained buyers. Canadian channel partners bundle identity, network, and endpoint controls into single subscription offerings.
- Small & Medium Enterprises:Prefer pre-integrated platform suites over best-of-breed procurement. Lean IT staff trade customization depth for operational simplicity.
- Cloud Service Providers:Embed zero-trust policies into infrastructure-as-a-service offerings. API security gateways serve as distribution channels bypassing traditional hardware procurement.
- System Integrators:Bridge legacy directory migration friction in financial services. Active Directory dependencies slow cloud-native adoption without professional services intervention.
Large Enterprises sit at the top of the volume ranking, with Managed Security Service Providers climbing the fastest.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
United States federal procurement timelines diverge sharply from European regulatory compliance windows, while Asian financial centers pursue distinct cloud-native deployment patterns.
United States
Civilian agencies face statutory deadlines mandating zero-trust architecture completion by 2027, driving concentrated vendor procurement through federal channels. NIST SP 800-207 standards reshape product requirements for defense contractors and healthcare providers alike. Washington DC-Arlington corridor hosts the densest concentration of identity architect specialists, though skilled federation protocol expertise remains scarce nationwide.
Germany
Industrial automation demand pairs zero-trust micro-segmentation with operational technology gateways across automotive manufacturing networks. EU NIS2 Directive penalties compel enterprises to abandon perimeter-based defenses by statutory timelines. Bavarian automotive plants in Munich-Augsburg cluster embed continuous verification controls alongside industrial protocol segmentation for IT/OT convergence.
Singapore
Financial institutions deploy sub-100-millisecond policy enforcement for trading floor latency requirements, automating dynamic access without human intervention. Monetary Authority of Singapore cybersecurity guidelines mandate continuous verification for banking infrastructure. Marina Bay financial district anchors regional procurement for cloud-native proxy architectures serving Southeast Asian expansion.
India
Aadhaar-linked identity verification creates regulatory tailwinds for conditional access vendors serving BFSI and government contract opportunities. Reserve Bank of India guidelines for digital payment security accelerate micro-segmentation adoption. Mumbai-Pune corridor concentrates implementation activity for financial services modernization alongside Bangalore's cloud-native development centers.
United Kingdom
Financial regulators in London enforce dynamic access controls for trading infrastructure while NHS networks respond to connected medical device cybersecurity guidance. UK National Cyber Security Centre zero-trust principles reshape procurement criteria across critical national infrastructure. London-Reading tech corridor hosts densest concentration of security service edge deployments for European financial services.
Global Zero-Trust Security Market Competitive Landscape
Top-tier vendors anchor platform consolidation strategies, while specialized point-product vendors compete on architectural differentiation. The vendor landscape exhibits tiered concentration with integrated security service edge suites commanding enterprise contract value. Three strategic archetypes dominate: cloud-native proxy specialists, endpoint telemetry integrators, and legacy network security incumbents pivoting to software-defined delivery. Competitive moves center on portfolio consolidation through acquisition and managed service packaging for mid-market penetration.
Within the cloud-native proxy tier, Zscaler exemplifies architectural differentiation through hardware elimination, while Palo Alto Networks occupies a position representing integrated platform breadth. CrowdStrike anchors endpoint-centric positioning with telemetry-fed risk scoring. These three vendors represent divergent strategic bets on where zero-trust policy enforcement optimally resides—network edge, identity layer, or endpoint substrate.
| Leading Market Players |
|---|
| Palo Alto Networks |
| Zscaler |
| Cisco Systems |
| Microsoft |
| Fortinet |
| Check Point Software Technologies |
| IBM |
| Cloudflare |
| CrowdStrike |
| Others |
Supply & Pricing Matrix
US federal zero-trust procurement mandates compressing vendor selection timelines are forcing security service edge providers to pre-certify compliance mappings, accelerating platform consolidation and squeezing point-product margins across the stack.
Pricing Analysis
Capacity additions in India and Germany are reshaping price floors for identity federation services as regional specialists scale cloud-native delivery. Subscription tiers stratify across enterprise, mid-market, and managed service provider levels, with FedRAMP authorization and EU AI Act pre-validation commanding substantial premiums. Cost compression in the mid-market tier intensifies as Australian and Canadian channel partners bundle network, endpoint, and identity controls into unified offerings. Large enterprises with internal security architect teams exhibit the lowest price sensitivity, while lean-IT manufacturing verticals prioritize operational simplicity over customization depth.
Supply Chain Analysis
China's MIIT data localization requirements and Russia's data sovereignty rules are reshaping sourcing patterns for multinational zero-trust deployments, compelling vendors to establish in-region policy orchestration nodes. Component dependencies center on cryptographic hardware security modules, AI inference accelerators, and industrial protocol gateways. Supply chain risk concentrates in single-source vulnerability for specialized federation protocol expertise concentrated in the United States and Germany. Distribution runs through hyperscaler marketplaces and managed security service providers rather than traditional hardware channel partners.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Arbitrage opportunities emerge between US federal procurement premiums and European compliance-driven replacement cycles, with NIST SP 800-207 certification costs diverging sharply from EU AI Act validation timelines.
For Market Incumbents: Hedge against point-product erosion by anchoring enterprise contracts around integrated security service edge suites spanning identity, network, and endpoint layers. Acquire specialized micro-segmentation vendors to fill Kubernetes-native certificate lifecycle gaps. Prioritize FedRAMP and EU AI Act pre-validation investments to capture statutory procurement windows. For New Entrants and Emerging Players: Managed security service providers in Canada and Australia represent the most penetrable channel for mid-market consolidation plays. Target manufacturing verticals with lean IT staff by offering pre-integrated platform subscriptions that trade customization depth for unified support. Lead with API security gateway positioning to bypass traditional network hardware procurement cycles. For Investors and Strategic Acquirers: Asymmetric upside sits with cloud-native proxy specialists possessing hardware elimination architectures and established hyperscaler marketplace distribution. Five-to-ten-year viability hinges on platform consolidation momentum versus best-of-breed fragmentation. Watch for certificate lifecycle management automation capabilities as the inflection signal for Kubernetes-native workload protection.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Consolidated Prisma SASE contracts anchor Palo Alto Networks' enterprise retention across identity and network layers. |
| Acquisition of Specialist Firm | CrowdStrike's endpoint telemetry feeds real-time risk scoring engines, collapsing detection-to-response windows for financial trading floors. |
| Geographic Expansion | Zscaler's hardware elimination architecture captures Singaporean banking infrastructure requiring sub-100-millisecond policy enforcement. |
| Strategic Partnership | Channel partners bundle identity-aware proxies with industrial protocol gateways for German automotive IT/OT convergence. |
| Product Launch | API security gateways embed zero-trust policies at application layers, bypassing FCC supply chain hardware restrictions. |
Research Methodology
Coverage spans the United States, Germany, Singapore, India, and the United Kingdom, with primary inputs from each market cluster combining interviews with CISOs, identity architects, federal procurement officers, and managed security service provider executives alongside secondary validation from NIST SP 800-207 documentation, SEC cybersecurity disclosure filings, EU AI Act regulatory texts, and FDA connected medical device guidance. Bottom-up deployment model sizing triangulates against top-down security spending forecasts.
Rate-of-change decomposition separates baseline security software growth from zero-trust-specific premium capture across deployment models, solution types, and buyer sophistication tiers. Segmentation dimensions modeled include cloud-native versus hybrid delivery, identity federation versus network segmentation solution layers, and financial services versus manufacturing application verticals. CAGRs derive from policy enforcement latency requirements, regulatory deadline clustering, and platform consolidation velocity.
Forecast confidence holds firmest in the near-window; longer-horizon outcomes carry greater sensitivity to cross-border data localization enforcement, skilled identity architect scarcity, and multi-vendor policy orchestration fragmentation. Within these boundaries, the analytical envelope holds.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Global Information Security Consulting Market
Cybersecurity
SOC As a Service Market
Cybersecurity
Ddos Protection and Mitigation Security Market
Cybersecurity
Mobile Encryption Market
Cybersecurity
North America Data Exfiltration Market
Cybersecurity
Quantum Cryptography Market
Cybersecurity
Austria Cybersecurity Market
Cybersecurity
LAMEA Deception Technology Market
Cybersecurity
Asia-Pacific Cloud DLP Market
Cybersecurity
Nordics Cybersecurity Market
Cybersecurity
Cyber Deception Market
Cybersecurity
Japan Cybersecurity Market
Cybersecurity
Network Detection and Response Market
Cybersecurity
Global Cloud Encryption Market
Cybersecurity
Latin America Cybersecurity Market
Cybersecurity
New Zealand Cybersecurity Market