
 Global Security Assessment Market | 2026-2036
Global Security Assessment Market Size, Share, and Industry Trends Forecast 2026-2036
Global Security Assessment Market Foresight
Israel is narrowing its gap with established North American cybersecurity hubs through government-backed incubator programs and military technology spin-offs. Palo Alto Networks leverages its platform consolidation strategy to capture recurring revenue from enterprise clients seeking unified threat visibility. Accenture anchors its competitive position through consulting-led engagements that bundle risk analysis with implementation services. Trellix differentiates via extended detection and response integration that reduces mean-time-to-remediation for security teams.
Security assessment encompasses systematic evaluation of information systems, networks, and applications to identify vulnerabilities, quantify risk exposure, and validate protective controls against defined threat scenarios. The discipline employs automated scanning tools, manual penetration techniques, and compliance frameworks such as NIST SP 800-30 to produce actionable remediation roadmaps for organizations. Vulnerability assessment and penetration testing dominate current spending as regulated industries face mandatory external validation requirements. Cloud-based services represent the fastest-expanding solution offering as distributed workforces eliminate the feasibility of perimeter-centric security models. Managed security services capture disproportionate margin pools through multi-year contracts that embed threat intelligence and continuous monitoring.
The US National Institute of Standards and Technology, the European Union Agency for Cybersecurity, and ISO/IEC 27001 collectively establish baseline assurance requirements that shape procurement specifications and vendor qualification criteria across jurisdictions. These frameworks create compliance-driven demand cycles where audit findings directly translate into security assessment purchasing decisions. Stakeholders must monitor how artificial intelligence governance regulations in the European Union and United States redefine the scope and methodology of automated vulnerability detection tools.
Market Dynamics
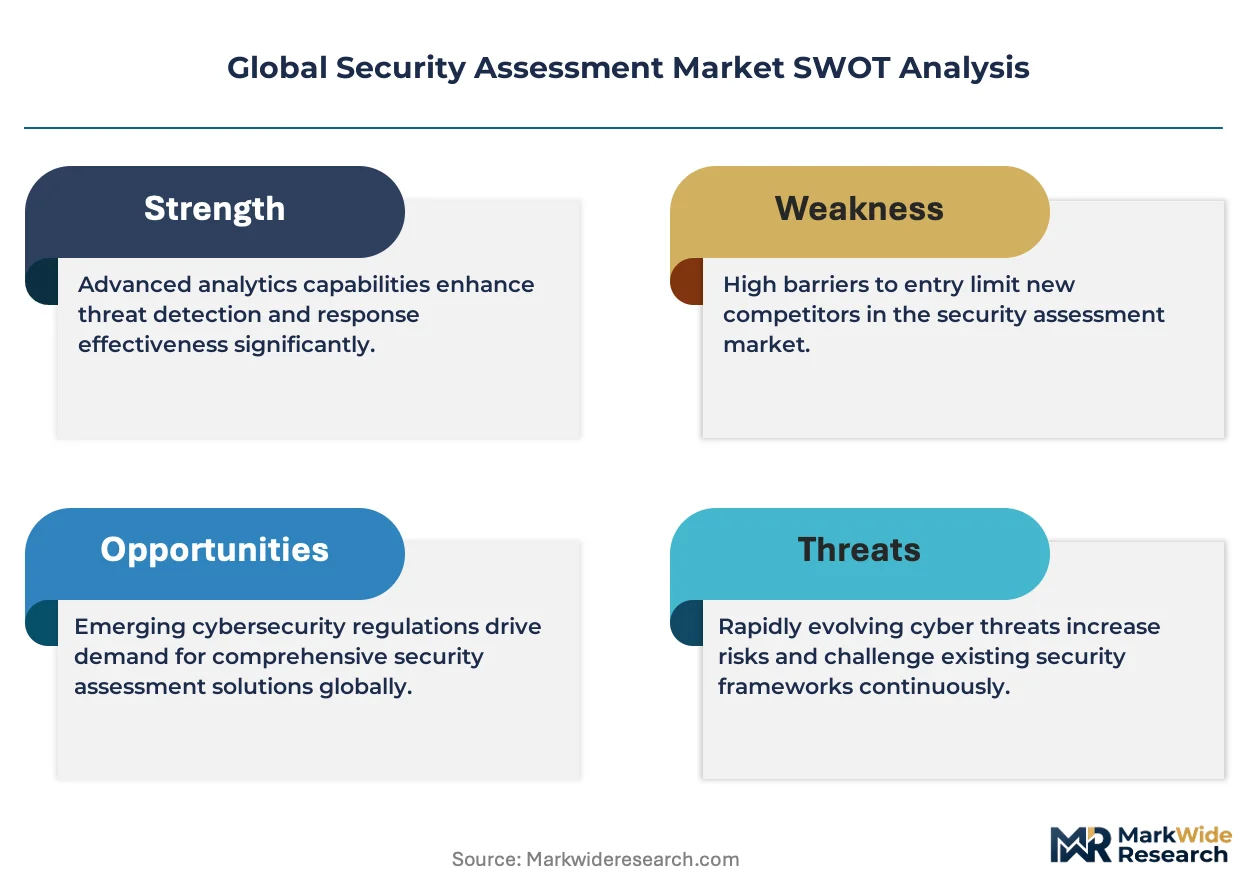
Zero-trust architecture mandates are restructuring enterprise procurement, forcing security assessment vendors to bundle continuous validation capabilities into multi-year managed service contracts rather than discrete point-in-time engagements.
Growth Catalysts
- EU AI Act compliance deadlines:Automated security systems deployed in European financial services must undergo mandatory conformity assessments, creating recurring demand for algorithmic auditing and bias detection services.
- Cloud migration acceleration:Distributed workforces across healthcare and government sectors require cloud-native vulnerability assessment tools that validate containerized workloads and serverless functions.
- Israeli military technology transfer:Government-backed incubator programs in Tel Aviv and Beer Sheva are commercializing offensive cyber capabilities into defensive assessment platforms for export markets.
Market Restraints
- Specialized talent scarcity:Certified penetration testers and red-team operators command premium compensation that inflates service delivery costs by 35-50% above general IT consulting rates.
- Tooling commoditization pressure:Open-source frameworks such as OpenVAS and OWASP ZAP erode pricing power for basic vulnerability scanning in mid-market segments.
- Cross-border data localization:Russia, China, and Vietnam mandate domestic storage of security assessment findings, fragmenting vendor operational models and duplicating infrastructure investment.
Strategic Opportunities
- Operational technology convergence:Manufacturing facilities in Germany and Japan require integrated IT/OT assessment methodologies as industrial control systems interconnect with enterprise networks.
- API security specialization:Microservices architectures in fintech and e-commerce create demand for continuous API penetration testing and schema validation services.
- Insurtech risk quantification:Cyber insurance underwriters in London and Bermuda seek standardized assessment outputs to price policies and set coverage limits.
Industry Challenges
- False positive fatigue:Security operations centers struggle with alert volumes from automated scanners, degrading trust in assessment vendor recommendations and delaying remediation workflows.
- Multi-framework mapping complexity:Enterprises must reconcile NIST SP 800-53, ISO/IEC 27001, and SOC 2 requirements simultaneously, demanding expensive custom reporting from assessment providers.
- Adversarial AI countermeasures:Attackers now deploy machine learning to evade detection signatures, forcing assessment vendors to continuously retrain detection models and validate against synthetic threat simulations.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Security Assessment Market |
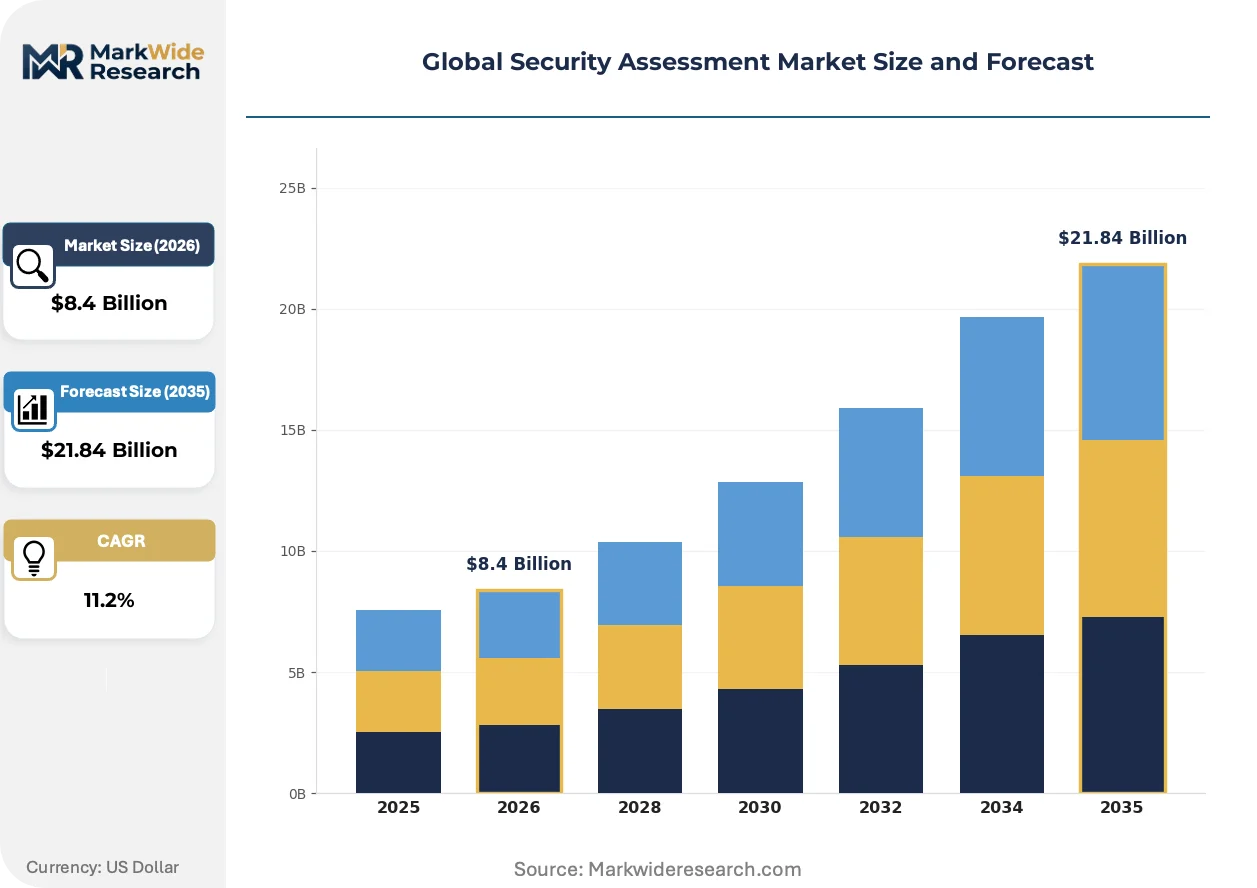
| Market Size in 2026 | $8.4 Billion |
| Market Size in 2035 | $21.84 Billion |
| CAGR (2026 – 2036) | 11.2% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Type: Vulnerability Assessment, Risk Analysis, Compliance Audit, Penetration Testing, Threat Modeling Solution Offering: On-Premises Software, Cloud-Based Services, Managed Security Services, Consulting, Training Solutions Use Case: Data Protection, Network Security, Application Security, Identity & Access Management, Incident Response End User Industry: Financial Institutions, Government Agencies, Telecommunications, Energy Providers, Educational Institutions |
| Companies Covered | IBM Corporation, Qualys Inc, Trustwave Holdings, AO Kaspersky Lab, Trellix, Microsoft Corporation, Accenture, Cisco Systems, Palo Alto Networks, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Security Assessment Market Shifts & Advancements
Security assessment delivery models are pivoting from episodic project-based engagements toward continuous monitoring architectures that embed validation directly into software development and cloud operations workflows.
Attack surface management platforms are virtualizing traditional perimeter scanning by discovering and cataloging internet-exposed assets without requiring network access credentials. Large enterprises with complex M&A histories adopt these tools to map shadow IT and forgotten infrastructure. The technology is virtualizing the initial reconnaissance phase of penetration testing, compressing assessment timelines from weeks to hours while expanding coverage scope.
The EU AI Act's risk-based classification system imposes mandatory conformity assessments on high-risk automated decision systems used in credit scoring and biometric identification. Financial institutions and government agencies must document algorithmic transparency and robustness through third-party validation. German automotive manufacturers and French healthcare providers are restructuring procurement specifications to prioritize vendors with EU-accredited AI auditing capabilities.
Enterprise buyers are consolidating vendor relationships to reduce operational fragmentation, favoring platform providers that integrate vulnerability management, penetration testing, and compliance reporting under unified contracts. This concentration pressures specialized boutique firms to embed their capabilities within larger managed security service providers or risk displacement. The pattern is most pronounced in United States federal contracting and United Kingdom critical national infrastructure sectors.
Global Security Assessment Market Segmentation
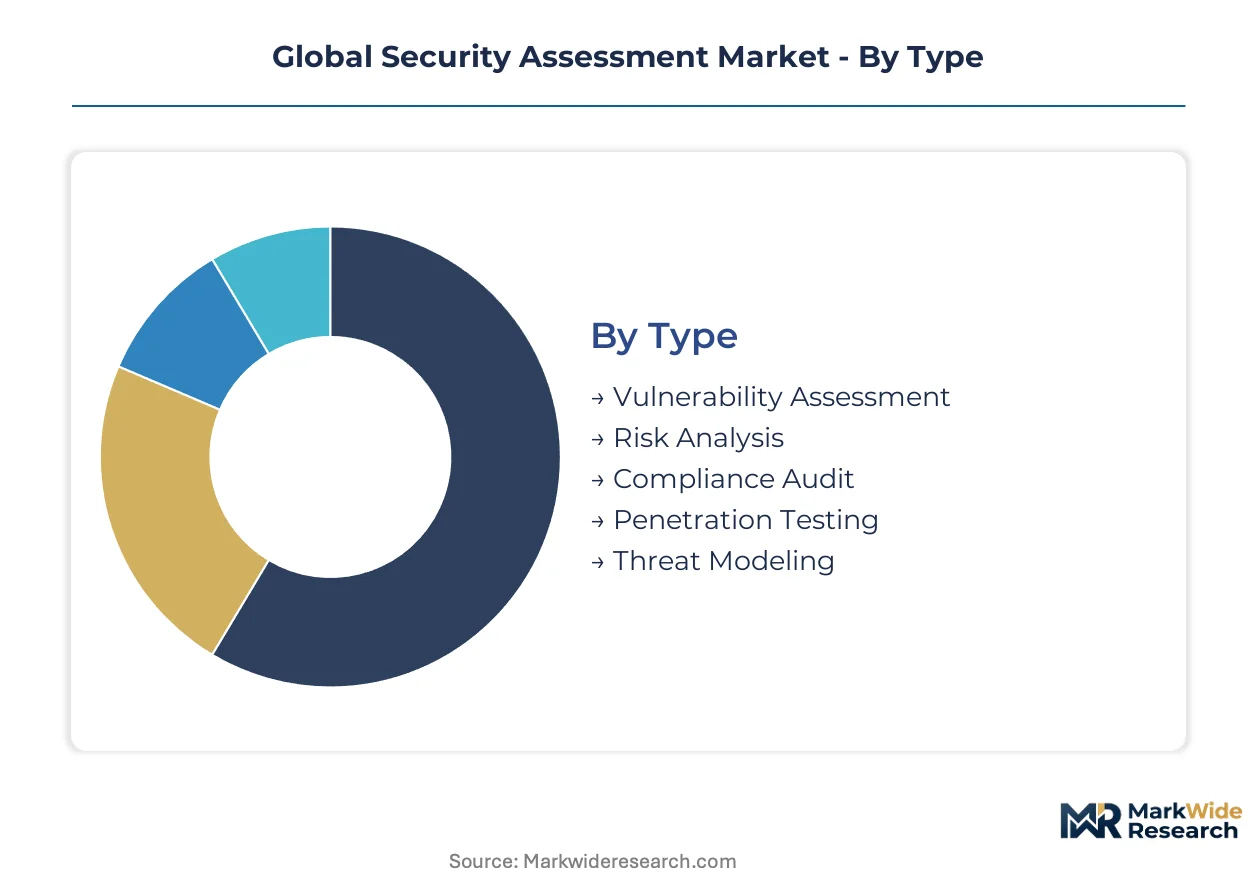
Security assessment procurement patterns diverge sharply across engagement models, technology delivery mechanisms, and regulatory exposure levels. Organizations structure vendor selection around internal capability maturity, compliance mandate intensity, and cloud migration status.
Type:
Assessment methodology selection correlates directly with regulatory mandate specificity and breach consequence severity in regulated sectors.
- Vulnerability Assessment:Automated scanning protocols inventory known CVEs across network segments and endpoints, generating prioritized patch schedules. Financial institutions in the United States deploy these tools continuously to satisfy OCC and FDIC examination expectations.
- Risk Analysis:Quantitative frameworks translate technical findings into business-impact probabilities and dollar-denominated exposure estimates. German automotive manufacturers apply these methods to ISO 27005-aligned supply chain security programs.
- Compliance Audit:Structured evaluations against NIST SP 800-53, ISO/IEC 27001, or SOC 2 control objectives produce attestation documentation for regulators and board reporting.
- Penetration Testing:Controlled adversarial simulation exercises validate detective and preventive control effectiveness through manual exploitation techniques.
- Threat Modeling:Architectural review methodologies identify design-phase vulnerabilities in software development lifecycles before deployment.
Vulnerability Assessment commands the established base. The steepest expansion runs through Threat Modeling as DevSecOps adoption accelerates.
Solution Offering:
Delivery economics and operational control preferences determine whether enterprises build internal capabilities or externalize assessment functions.
- On-Premises Software:Licensed tools deployed within customer-controlled infrastructure satisfy data residency requirements and air-gapped operational technology environments. Russian and Chinese data localization mandates preserve demand despite cloud migration trends elsewhere.
- Cloud-Based Services:SaaS vulnerability management platforms eliminate infrastructure maintenance overhead while enabling elastic scanning capacity. Healthcare providers in France and the United Kingdom favor these solutions for distributed clinical workforce support.
- Managed Security Services:Multi-year contracts embed continuous monitoring, threat intelligence integration, and dedicated analyst access. United States federal agencies procure these through FedRAMP-authorized providers.
- Consulting:Project-based engagements deliver bespoke assessment methodologies for complex M&A transactions and regulatory enforcement responses.
- Training Solutions:Certification programs and tabletop exercise facilitation build internal red-team capabilities and security awareness cultures.
On-Premises Software retains the largest installed base. Cloud-Based Services are gaining share fastest as containerized workload assessment requirements proliferate.
Use Case:
Protection priority hierarchies reflect asset classification schemes and breach history within specific industry verticals.
- Data Protection:Encryption validation, data loss prevention testing, and privacy impact assessments address GDPR, CCPA, and sector-specific confidentiality requirements. Retail and hospitality sectors in the United States concentrate spending here following high-profile payment card breaches.
- Network Security:Perimeter and segmentation testing validates zero-trust architecture implementations and software-defined perimeter configurations. Japanese manufacturing networks prioritize this segment for IT/OT convergence security.
- Application Security:Source code review, dynamic application security testing, and API schema validation secure microservices architectures. Fintech developers in Singapore and the United Kingdom drive specialized demand.
- Identity & Access Management:Privileged access control testing and multi-factor authentication bypass simulation reduce credential compromise vectors.
- Incident Response:Tabletop exercises and forensic readiness assessments validate breach containment playbooks and communication protocols.
Network Security anchors current procurement volumes. Application Security demonstrates the most rapid trajectory as API-first development expands attack surfaces.
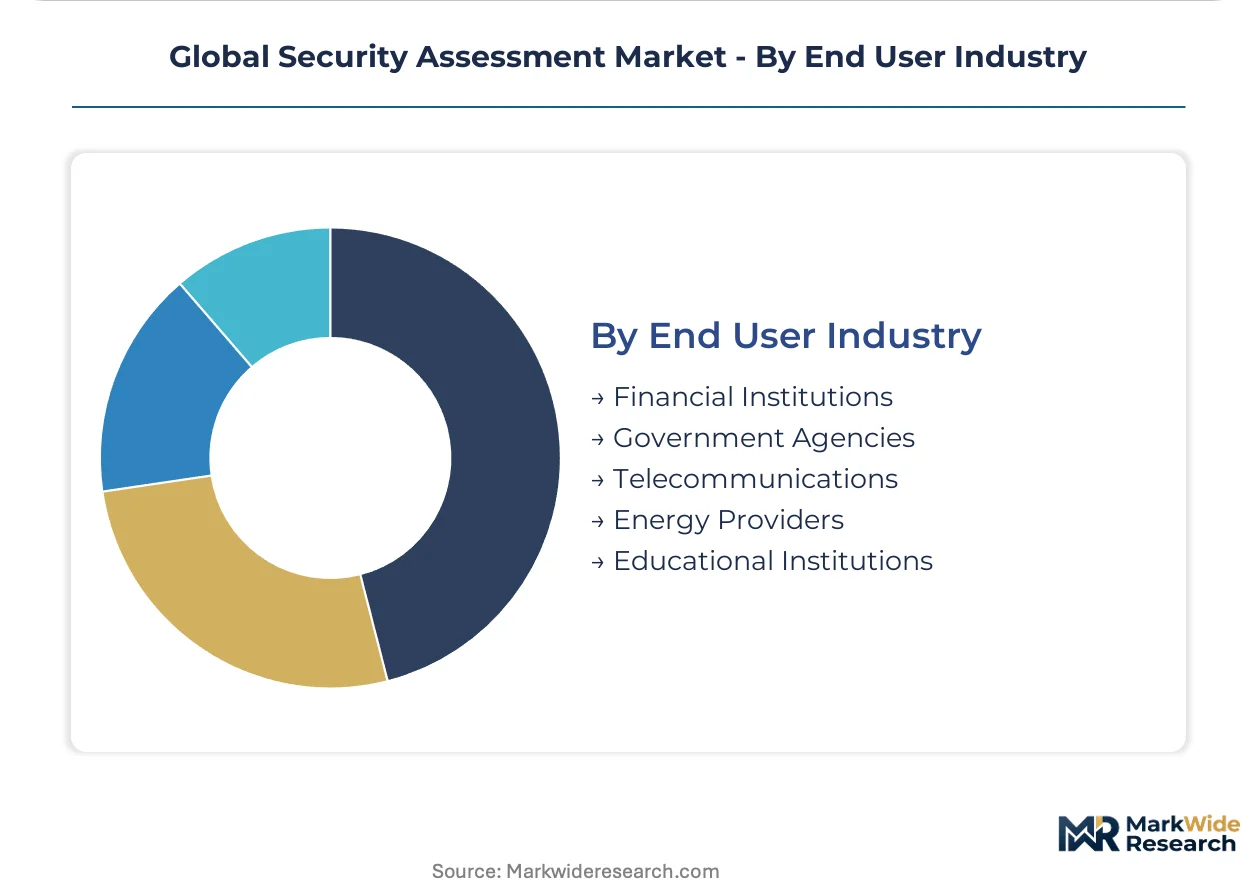
End User Industry:
Regulatory enforcement intensity and breach consequence severity create divergent spending elasticity across vertical markets.
- Financial Institutions:Banks, insurers, and payment processors face mandatory external assessment requirements from Basel Committee guidelines and national banking regulators. German and French institutions allocate substantial budgets to EU AI Act algorithmic auditing preparation.
- Government Agencies:Defense, intelligence, and civilian departments mandate FedRAMP, CMMC, or national equivalent certifications for all assessment tool procurement. Israeli government technology transfer programs stimulate domestic vendor development.
- Telecommunications:Critical infrastructure designation in the European Union and United States imposes continuous monitoring obligations and supply chain security validation.
- Energy Providers:NERC CIP compliance in North America and EU Network and Information Security Directive implementation drive OT-security assessment specialization.
- Educational Institutions:Research universities with controlled unclassified information exposure adopt assessment frameworks aligned with defense contractor requirements.
Financial Institutions represent the largest committed spending pool. Government Agencies show the most pronounced procurement acceleration as cyber warfare preparedness intensifies.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
NIST standards in the United States anchor regulatory frameworks that cascade through procurement specifications worldwide. Security assessment vendors calibrate product roadmaps to FedRAMP authorization requirements and CMMC compliance timelines.
United States
Zero-trust architecture mandates from CISA and OMB drive continuous validation procurement across federal agencies and defense contractors. FedRAMP-authorized cloud services capture disproportionate contract value as agencies consolidate vendor relationships. The Washington DC-Baltimore corridor concentrates security assessment providers serving federal demand, while Silicon Valley clusters platform vendors integrating AI-powered threat detection.
Germany
Automotive manufacturers and industrial automation firms demand integrated IT/OT assessment methodologies for smart factory deployments. The EU AI Act imposes mandatory conformity assessments on automated quality control and predictive maintenance systems. Munich and Stuttgart host specialized consultancies bundling ISO 27005 risk analysis with TISAX automotive security certification.
United Kingdom
Critical national infrastructure operators face NIS2 directive implementation deadlines requiring continuous monitoring and supply chain security validation. London's Lloyd's insurance market drives demand for standardized cyber risk quantification outputs. The Thames Valley corridor clusters managed security service providers serving financial services and telecommunications sectors.
Israel
Government-backed incubator programs in Tel Aviv and Beer Sheva commercialize military intelligence capabilities into defensive assessment platforms. Unit 8200 alumni populate vendor engineering teams with offensive cyber expertise. The country's cybersecurity export sector specializes in attack surface management and adversarial simulation tools for European and North American markets.
Japan
Manufacturing networks prioritize IT/OT convergence security as industrial control systems interconnect with enterprise cloud infrastructure. METI guidelines on critical infrastructure protection mandate external security validation for energy and telecommunications operators. Tokyo and Nagoya clusters host consultancies combining JIS standards compliance with threat modeling for automotive and electronics supply chains.
Global Security Assessment Market Competitive Landscape
Platform consolidators and consulting-led integrators split the market between recurring technology revenue and project-based advisory fees. The vendor base organizes around three strategic archetypes: unified threat visibility platforms, risk advisory bundlers, and specialized detection engineering shops. Consolidation pressure intensifies as enterprise buyers reduce operational fragmentation through multi-year managed service contracts. Acquisition activity concentrates on boutique firms with FedRAMP authorization or EU AI Act auditing credentials.
Within the platform consolidation tier, Palo Alto Networks and Microsoft Corporation exemplify vendors capturing recurring revenue through integrated security stacks. Accenture anchors the consulting-led segment, bundling risk analysis with implementation services across financial services and government verticals. Trellix occupies a specialist position, representing extended detection and response integration capabilities that compress incident response timelines.
| Leading Market Players |
|---|
| IBM Corporation |
| Qualys Inc |
| Trustwave Holdings |
| AO Kaspersky Lab |
| Trellix |
| Microsoft Corporation |
| Accenture |
| Cisco Systems |
| Palo Alto Networks |
| Others |
Supply & Pricing Matrix
Overcapacity in automated vulnerability scanning tools has compressed margins for mid-market SaaS providers and forced tier-one vendors toward bundled managed service contracts. Israeli and North American platform vendors now calibrate pricing against FedRAMP authorization costs and EU AI Act compliance investments rather than pure feature differentiation.
Pricing Analysis
Price spreads between Tel Aviv-based specialists and Washington DC-area federal contractors reach three-to-one multiples for equivalent penetration testing capabilities. The market runs on subscription-tiered SaaS pricing for continuous monitoring, with differentiation anchored in certification grade and after-sales threat intelligence integration. Cost compression in basic vulnerability scanning intensifies as open-source alternatives erode pricing power. Mid-market enterprises exhibit highest price sensitivity, while United States federal agencies prioritize FedRAMP authorization over cost minimization.
Supply Chain Analysis
United States export controls on offensive cyber capabilities restrict Israeli military technology transfer into European assessment platforms. Engineering talent concentrates in Israel, the United States, and Germany, with these markets drawing from Unit 8200 alumni pipelines, NSA-certified training programs, and TISAX-accredited consultancies respectively. Single-source vulnerability in specialized red-team operator availability elevates delivery risk. Distribution runs through direct enterprise sales for platform vendors and consulting-led channel partnerships for boutique assessment firms.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Security assessment demand is recovering from post-pandemic budget freezes as regulatory enforcement intensifies and breach consequence severity escalates. The EU AI Act implementation timeline and CMMC rollout are synchronizing procurement cycles across financial services and defense contracting.
For Market Incumbents: Harden platform stickiness by embedding continuous validation APIs directly into client DevSecOps pipelines. Deepen vertical integration into threat intelligence data feeds to differentiate against open-source tool commoditization. Invest in EU-accredited AI auditing certifications ahead of conformity assessment deadlines to capture algorithmic transparency mandates.
For New Entrants and Emerging Players: API security specialization for fintech developers in Singapore and the United Kingdom represents the most penetrable entry point. Manufacturing IT/OT convergence assessment in Germany and Japan offers second-mover advantage as incumbent platforms lack industrial control system expertise. Pursue channel partnerships with hyperscaler marketplaces to bypass direct enterprise sales infrastructure requirements.
For Investors and Strategic Acquirers: Recurring-revenue conversion is highest among managed security service providers with multi-year federal contracts. Long-term viability favors vendors combining FedRAMP authorization with EU AI Act auditing capabilities across the five-to-ten year regulatory implementation window. Boutique firms with CMMC consulting credentials and Israeli offensive cyber heritage signal acquisition priority.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies vulnerability management, penetration testing, and compliance reporting under single vendor relationships. |
| Acquisition of Specialist Firm | Captures FedRAMP-authorized boutiques or EU AI Act auditing capabilities to fill credential gaps. |
| Geographic Expansion | Establishes delivery presence in Germany and Japan for IT/OT convergence assessment demand. |
| Strategic Partnership | Embeds assessment APIs into hyperscaler DevSecOps toolchains for continuous validation workflows. |
| Product Launch | Introduces attack surface management platforms compressing reconnaissance timelines from weeks to hours. |
Research Methodology
Demand-side practitioners and supply-side operators were both consulted across primary interview programs. CISOs at financial institutions, federal procurement officers, red-team operators, DevSecOps engineers, and cyber insurance underwriters provided operational perspective. Secondary validation drew from FedRAMP authorization databases, NIST publication repositories, EU AI Act implementation guidance, CMMC accreditation body records, and SEC cybersecurity disclosure filings. Bottom-up segment sizing triangulated against top-down market aggregation.
Calibration against historical procurement data and regulatory implementation timelines anchored the analytical framework. Segmentation dimensions modeled across the analysis window encompassed assessment methodology type, solution delivery mechanism, end-user industry vertical, and geographic regulatory cluster. CAGRs were derived from regression analysis of spending elasticity against compliance mandate intensity and breach frequency data. Threat modeling adoption curves and zero-trust architecture migration rates served as industry-specific forecast inputs.
Macroeconomic conditions sit as an overlay; deviation in federal IT budget appropriations or EU regulatory enforcement intensity would shift the trajectory. Forecasts reflect documented assumptions regarding CMMC phase-in adherence and EU AI Act conformity assessment capacity buildup. Material shifts in export control regimes affecting Israeli technology transfer or in cyber insurance pricing models would require updated calibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
National Security
Asia-Pacific Non-Lethal Weapons Market
National Security
Asia-Pacific Border Security Market
National Security
Research Department Explosive (RDX) Market
National Security
Chemical, Biological, Radiological and Nuclear (CBRN) Security Market
National Security
Service Handgun Market
National Security
US Bulletproof Glass Market
National Security
Radiological and Nuclear Security Market
National Security
Global Non Lethal Weapons Market
National Security
Homeland Security Market
National Security
Europe Non-Lethal Weapons Market
National Security
Saudi Arabia Manned Security Market
National Security
North America Non Lethal Weapons Market