
 Security Operations Center Market | 2026-2036
Security Operations Center Market Size, Share, and Industry Trends Forecast 2026-2036
Security Operations Center Market Intelligence
Cloud-native SIEM architectures is tilting SOC construction away from monolithic on-premise stacks toward API-first, elastic platforms. Palo Alto Networks leverages Cortex XSIAM to unify telemetry ingestion across hybrid estates. CrowdStrike anchors its Falcon platform with native endpoint detection that eliminates third-party agent sprawl. Fortinet competes through tight integration between its FortiSIEM and FortiGate fabric, reducing alert fatigue via correlated threat intelligence.
A Security Operations Center constitutes a centralized facility where security analysts monitor, detect, analyze, and respond to cyber threats across an organization's digital infrastructure using correlated data feeds, playbooks, and automated response protocols. SIEM platforms aggregate log data at terabyte scale while SOAR engines execute scripted remediation workflows without human intervention. Managed Service deployments dominate revenue as skills scarcity pushes mid-market buyers toward outsourced analyst teams. Endpoint Detection technology captures the fastest expansion trajectory as remote work endpoints proliferate beyond traditional network perimeters. Hybrid Deployment models are gaining structural ground where regulated data must remain on-premise while cloud analytics handle scale.
NIS2 mandates across European Union member states require critical infrastructure operators to maintain 24/7 incident detection and reporting capabilities, directly expanding SOC procurement. The EU AI Act imposes conformity assessments on automated threat scoring systems, reshaping vendor product roadmaps toward explainable detection logic. HIPAA in the United States enforces audit logging and access monitoring that healthcare SOCs must operationalize. Stakeholders should evaluate whether their detection pipelines can satisfy emerging algorithmic accountability rules without degrading mean-time-to-response.
Market Dynamics
Cloud-native SIEM architectures are compressing deployment timelines from months to weeks while fragmenting vendor lock-in patterns across hybrid estates. This structural shift is redistributing procurement power toward buyers with multi-cloud footprints.
Growth Catalysts
- NIS2 Directive:European critical infrastructure operators must maintain 24/7 incident detection capabilities, forcing direct SOC procurement across energy, transport, and healthcare sectors.
- Remote endpoint proliferation:Distributed workforces have pushed endpoint detection beyond traditional network perimeters, expanding telemetry ingestion requirements.
- Financial services breach mandates:Stringent disclosure requirements in banking and insurance are compelling institutional investment in centralized monitoring infrastructure.
Market Restraints
- Analyst talent scarcity:Certified security operations specialists command premium compensation, inflating in-house SOC operating costs beyond mid-market tolerance.
- Legacy SIEM sunk costs:Enterprises with substantial on-premise log management investments face migration friction that delays cloud-native adoption.
- Data residency requirements:Regulated industries in Germany, France, and Switzerland must maintain sovereign data boundaries that complicate multi-cloud architectures.
Strategic Opportunities
- EU AI Act compliance services:Automated threat scoring systems require explainable detection logic, creating vendor differentiation through algorithmic accountability tooling.
- Managed detection expansion:Skills gaps are pushing mid-market buyers toward outsourced analyst teams, opening recurring revenue streams for service providers.
- Healthcare vertical penetration:HIPAA audit logging mandates in the United States create specialized SOC requirements for hospital systems and payers.
Industry Challenges
- Alert fatigue remediation:Correlation engine tuning requires scarce expertise to reduce false-positive rates without degrading detection coverage.
- Multi-vendor integration complexity:API standardization gaps between endpoint, network, and cloud telemetry sources prolong deployment cycles.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Security Operations Center Market |
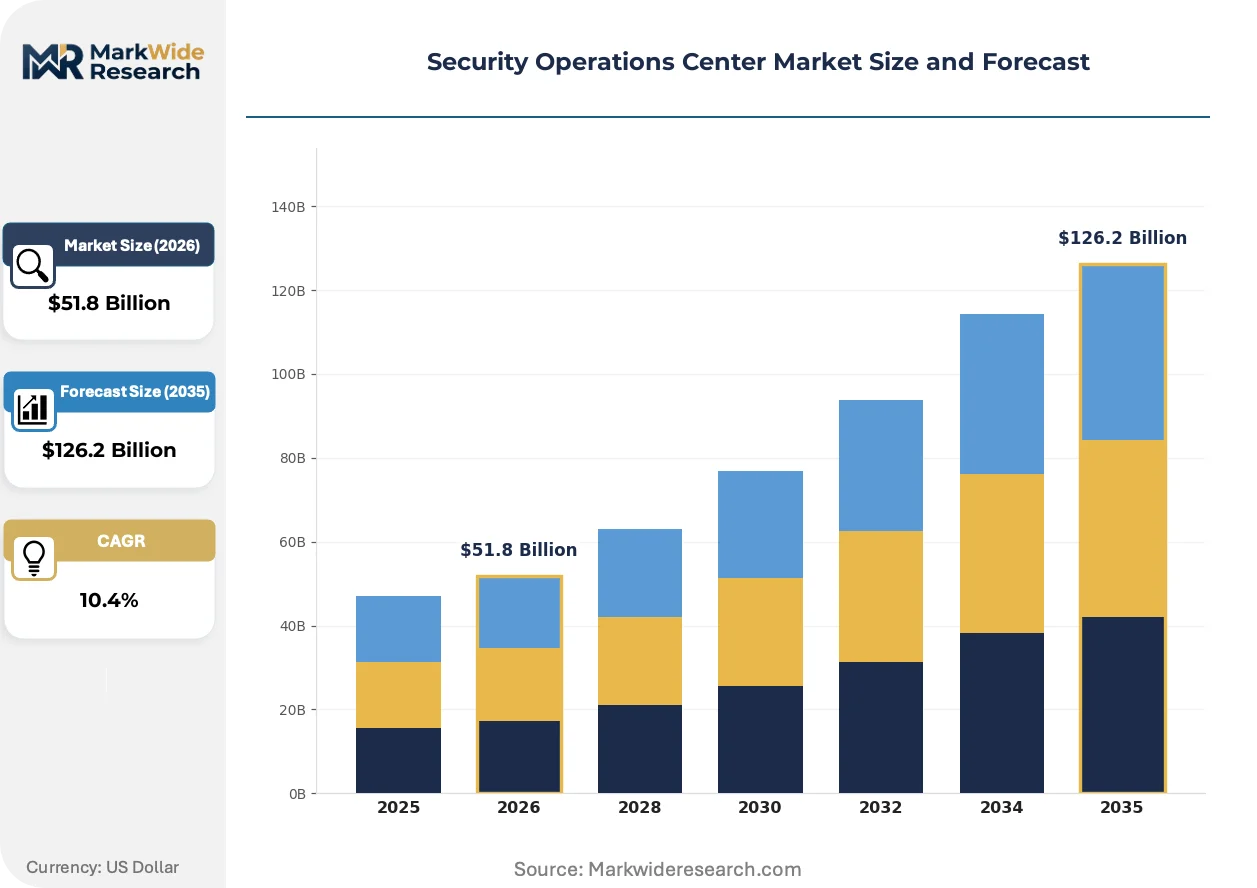
| Market Size in 2026 | $51.8 Billion |
| Market Size in 2035 | $126.2 Billion |
| CAGR (2026 – 2036) | 10.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Managed Service, On-Premise, Hybrid Deployment, Incident Response Technology: SIEM, Threat Intelligence, SOAR, Endpoint Detection End User: Government, Healthcare, Financial Services, Manufacturing Size: Large Enterprises, SMEs, Startups, Organizations |
| Companies Covered | Cisco, Exabeam, Palo Alto Networks, Alert Logic, CyberNX, CrowdStrike, SentinelOne, Huntress, Fortinet, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Security Operations Center Market Strategic Shifts & Innovations
Security operations platforms are converging detection, investigation, and response into unified workflows that compress analyst handoff delays. This integration is eliminating the historical segmentation between SIEM, SOAR, and EDR tooling categories.
Extended detection and response (XDR) platforms aggregate telemetry across endpoints, networks, and cloud workloads into single-pane investigation interfaces. Mid-market enterprises with limited specialist headcount are adopting these consolidated stacks fastest. The technology is hybridizing previously siloed security operations functions into continuous threat management pipelines.
The EU AI Act imposes conformity assessments on automated threat scoring systems that assign risk ratings without human review. Vendors must now engineer explainable detection logic that satisfies algorithmic accountability rules. European critical infrastructure operators are prioritizing platforms with built-in audit trails for machine-driven decisions.
Subscription-based managed detection services are displacing capital-intensive in-house SOC construction among resource-constrained buyers. Healthcare systems and regional banks are outsourcing tier-1 analyst functions to specialized providers. This pattern is most visible in the United States where HIPAA operational requirements outpace internal hiring capacity.
Security Operations Center Market Segmentation
SOC procurement patterns diverge sharply across deployment models, technology stacks, and buyer scale. Understanding these fault lines reveals where vendor roadmaps must pivot and which customer profiles justify specialized product investment.
Service Type:
Deployment economics separate buyers with capital reserves from those prioritizing operational flexibility and speed to capability.
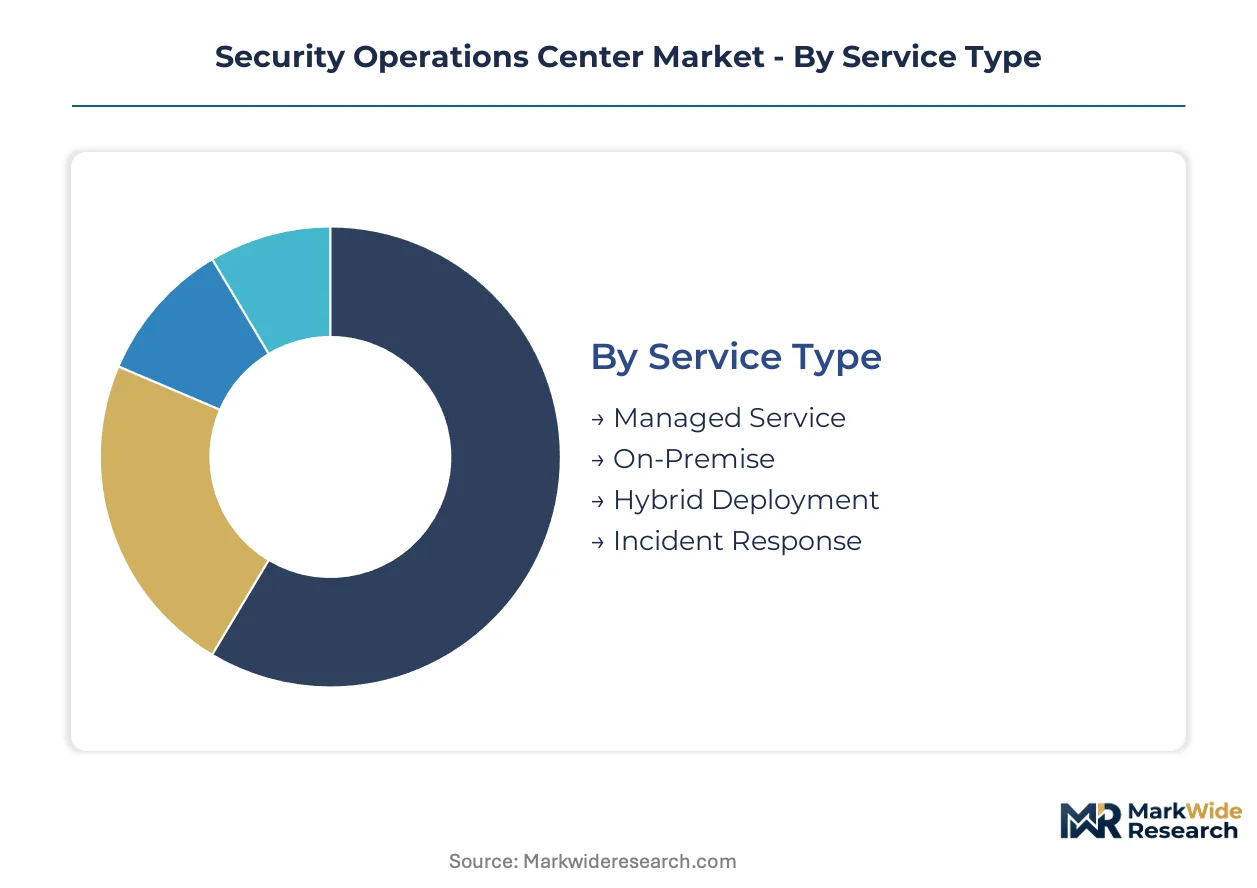
- Managed Service:Third-party analyst teams operate detection and response functions under subscription contracts. Financial services institutions in Germany and France outsource tier-1 monitoring to bypass certified talent shortages while satisfying NIS2 mandates.
- On-Premise:Dedicated facility and staff under direct organizational control. Swiss banking regulators and German energy operators maintain sovereign infrastructure to satisfy data residency requirements that cloud platforms cannot guarantee.
- Hybrid Deployment:Regulated data remains on-premise while cloud analytics handle scale. Healthcare systems in the United States segment HIPAA-protected patient records from cloud-based threat correlation engines.
- Incident Response:Retainer-based emergency containment and forensics. Manufacturing firms activate these services post-breach when internal capabilities prove insufficient for advanced persistent threat remediation.
Managed Service commands the established base. The steepest expansion runs through Hybrid Deployment.
Technology:
Platform architecture choices determine telemetry breadth, analyst workflow efficiency, and integration complexity across security estates.
- SIEM:Log aggregation engines process terabyte-scale event streams for correlation and archival. Large enterprises in the United Kingdom modernize these platforms to satisfy GDPR-mandated audit trails while compressing detection latency.
- Threat Intelligence:External feeds of indicators, tactics, and adversary profiles enrich detection logic. Critical infrastructure operators in France license sector-specific intelligence to anticipate state-sponsored targeting patterns.
- SOAR:Automated playbook execution triggers scripted remediation without human intervention. SOAR adoption concentrates where analyst headcount constraints force machines to handle tier-1 triage volume.
- Endpoint Detection:Behavioral monitoring agents capture process anomalies on laptops, servers, and mobile devices. Remote workforce expansion beyond traditional network perimeters drives this segment's velocity.
SIEM retains the largest installed footprint. Endpoint Detection is climbing the fastest as distributed endpoints multiply.
End User:
Vertical-specific compliance regimes and threat actor targeting patterns shape procurement priorities and platform configuration requirements.
- Government:National and local agencies defending classified systems and citizen data. Defense and intelligence SOCs in the United States and United Kingdom operate under classified procurement channels with vendor clearance requirements.
- Healthcare:Hospital systems and payers protecting patient records and medical device networks. HIPAA audit logging mandates in the United States force continuous monitoring investments that outpace internal hiring capacity.
- Financial Services:Banks, insurers, and payment processors managing transaction integrity and breach disclosure. EU disclosure timelines and SEC reporting rules compel 24/7 detection capabilities with documented response protocols.
- Manufacturing:Industrial control systems and operational technology environments. German automotive and chemical producers build SOCs to protect production lines from ransomware that halts assembly operations.
Financial Services anchors current spending. Healthcare is gaining share fastest as digital health records expand attack surfaces.
Size:
Organizational scale dictates whether buyers construct internal capabilities, outsource entirely, or pursue hybrid staffing models.
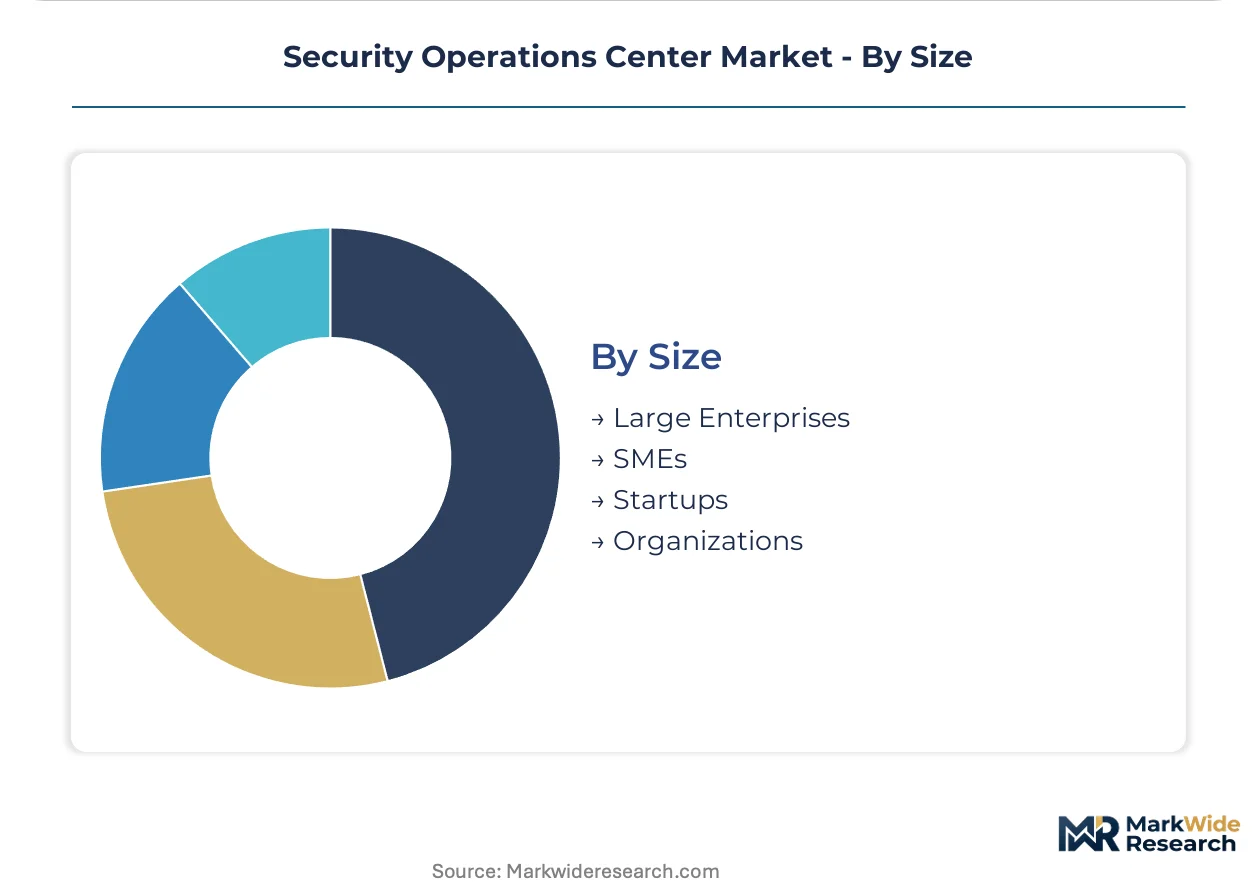
- Large Enterprises:Fortune 500 and equivalent organizations with dedicated security budgets. These buyers construct multi-tier SOCs with 24/7 coverage across Americas, EMEA, and Asia-Pacific time zones.
- SMEs:Mid-market organizations with constrained specialist headcount. United Kingdom and French SMEs disproportionately purchase managed detection to satisfy cyber insurance underwriting requirements.
- Startups:Venture-backed technology firms prioritizing speed over security investment. These buyers typically deploy cloud-native EDR with minimal log retention until customer contracts mandate formal SOC capabilities.
- Organizations:Nonprofit, educational, and membership entities with irregular security funding. Universities in Germany and the United States balance open research network access against student and faculty data protection duties.
Large Enterprises dominate absolute investment. SMEs are expanding most quickly as cyber insurance penetration deepens.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
German SOC vendors export managed detection services to French and UK critical infrastructure operators under NIS2 procurement timelines. This cross-border service flow concentrates expertise in Berlin and Munich while distributing operational capacity across European energy and transport networks.
United States
Healthcare systems and financial institutions drive SOC procurement to satisfy HIPAA audit logging and SEC breach disclosure mandates. The Department of Health and Human Services enforces continuous monitoring requirements that outpace internal hiring capacity. Hospital networks in Texas and California outsource tier-1 analyst functions to specialized providers.
Germany
Automotive and chemical producers build sovereign SOCs to protect operational technology from ransomware halting assembly lines. The Federal Office for Information Security mandates 24/7 incident detection for critical infrastructure under NIS2 transposition. Industrial clusters in Bavaria and North Rhine-Westphalia maintain on-premise telemetry to satisfy data residency requirements.
United Kingdom
Mid-market enterprises purchase managed detection services to satisfy cyber insurance underwriting requirements. The National Cyber Security Centre publishes incident response guidelines that shape procurement specifications. Financial services firms in London construct multi-tier SOCs with 24/7 coverage across Americas and EMEA time zones.
France
Energy operators and transport authorities upgrade monitoring infrastructure to meet NIS2 Directive compliance deadlines. The National Agency for Food, Environmental and Occupational Health Safety imposes sector-specific audit protocols on automated threat scoring systems. Defense contractors in Île-de-France prioritize platforms with explainable detection logic for algorithmic accountability.
Switzerland
Banking regulators require sovereign data boundaries that cloud platforms cannot guarantee for transaction monitoring. FINMA operational risk guidelines compel institutional investment in centralized logging infrastructure. Private banks in Zurich and Geneva maintain dedicated facilities with direct organizational control over sensitive customer data.
Security Operations Center Market Key Industry Players
Channel-controlling players compete with product-specialist players across fragmented procurement channels. Consolidation pressure intensifies as cloud-native architectures compress deployment timelines from months to weeks. Three archetypes dominate: platform-integrated security vendors, pure-play endpoint detection specialists, and managed service operators with certified analyst teams. M&A activity concentrates on SOAR engine capabilities and sector-specific threat intelligence feeds.
Within the platform-integrated tier, Palo Alto Networks and CrowdStrike exemplify converged detection-investigation-response workflows. Fortinet occupies a position anchoring tight SIEM-firewall integration for reduced alert fatigue. These three vendors represent distinct architectural bets on telemetry unification versus endpoint-native depth versus fabric-level correlation.
| Leading Market Players |
|---|
| Cisco |
| Exabeam |
| Palo Alto Networks |
| Alert Logic |
| CyberNX |
| CrowdStrike |
| SentinelOne |
| Huntress |
| Fortinet |
| Others |
Cost & Logistics Intelligence
Single-source dependency on certified security analyst talent pools determines both tiered pricing spreads across managed detection services and supply chain shape toward outsourced staffing models. This concentration forces buyers to absorb premium rates for 24/7 coverage or accept capability gaps in sovereign data handling.
Pricing Analysis
Legacy on-premise SIEM deployments command substantial residual premiums against cloud-native alternatives despite compressed functionality. Three-tier pricing structure across premium, standard, and economy levels segments by analyst certification depth, response-time SLAs, and vertical specialization. Cost compression in mid-market managed services is intensifying because hyperscaler infrastructure commoditizes underlying compute. Healthcare systems exhibit highest price sensitivity due to constrained capital budgets, while financial institutions in Germany and Switzerland demonstrate lowest sensitivity given regulatory non-compliance penalties.
Supply Chain Analysis
Extended payment terms from critical infrastructure operators in France and Germany are restructuring vendor cash flow requirements across European SOC providers. Talent supply concentrates in the United Kingdom, Germany, and India, drawing from cybersecurity training pipelines, military intelligence transitions, and offshore technical education programs. The supply chain rests on specialized threat intelligence feeds, elastic cloud infrastructure, and proprietary detection algorithm development. Single-source vulnerability in certified analyst availability threatens service continuity. Distribution runs through direct enterprise sales, managed security service providers, and hyperscaler marketplaces.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Security operations platforms are approaching a platform-economics inflection where API-first architectures and cross-vendor telemetry standards determine competitive survival. The EU AI Act's explainability mandates and NIS2's operational requirements are accelerating ecosystem consolidation around interoperable detection pipelines.
For Market Incumbents: Pre-empt margin erosion from cloud-native entrants by consolidating SOAR engine capabilities through targeted acquisition and deepening vertical integration into sovereign data residency infrastructure. Threat actor specialization in operational technology targeting demands sector-specific detection logic investment. Certification depth in EU AI Act conformity assessment protocols represents the priority defensive lever. For New Entrants and Emerging Players: French regional banking and German mid-market manufacturing present geographic underpenetration with limited incumbent loyalty and urgent NIS2 compliance deadlines. Healthcare systems in the United States facing HIPAA audit logging mandates offer parallel white-space opportunity. Channel partnership with established managed service providers enables rapid capability deployment without direct analyst recruitment. For Investors and Strategic Acquirers: The market sits at a consolidation phase that favors platform-integrated vendors with proven multi-tenant architectures over point-solution specialists. Long-term viability across the projection horizon rests on algorithmic accountability tooling and cross-cloud telemetry unification. Acquisition targets should demonstrate explainable detection logic and sector-specific threat intelligence feeds. The signal to watch is hyperscaler marketplace traction as distribution channel validation.| Strategic Initiative | Industry Significance |
|---|---|
| SOAR Engine Acquisition | Automated playbook execution addresses analyst scarcity in German critical infrastructure operators. |
| EU AI Act Compliance Certification | Explainable detection logic unlocks procurement from French defense contractors under ANSM guidelines. |
| Healthcare Vertical Specialization | HIPAA audit trail capabilities capture United States hospital network outsourcing demand. |
| Hyperscaler Marketplace Integration | Azure and AWS distribution channels accelerate mid-market managed detection penetration. |
| Sovereign Data Residency Infrastructure | Swiss and German banking regulators mandate on-premise telemetry for transaction monitoring systems. |
Research Approach
Initial hypotheses were tested against primary input from CISOs, SOC managers, managed security service provider executives, and regulatory compliance officers and refined through secondary validation across vendor financial disclosures, NIS2 implementation guidance from EU member state agencies, and healthcare cybersecurity procurement databases. Bottom-up sizing of endpoint detection deployments and top-down triangulation against aggregate security software expenditure produced convergent estimates.
Demand-supply-balance framing anchored the forecast framework, modeling deployment model preferences, organization size tiers, vertical regulatory intensity, and technology stack integration complexity across the analysis window. CAGRs were derived from segment-level growth differentials applied to base-year estimates. Forecast inputs incorporated NIS2 transposition timelines, remote workforce endpoint proliferation patterns, and cyber insurance underwriting requirement diffusion.
The forecast holds incumbent behavior within observed patterns; aggressive platform consolidation moves by cloud-native specialists or hyperscaler security divisions would shift outcomes. Macroeconomic contraction affecting security software budgets, accelerated EU AI Act enforcement beyond current guidance, or breakthrough autonomous detection capabilities would prompt revision.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security and Surveillance
APAC Security Testing Market
Security and Surveillance
Alarm Monitoring [Central Stations] Software Market
Security and Surveillance
Security Analytics Market
Security and Surveillance
Night Vision Binoculars Market
Security and Surveillance
Global Intrusion Detection System Market
Security and Surveillance
Global X-Ray Security Scanner Market
Security and Surveillance
Air Cargo Security Equipment Market
Security and Surveillance
Airport Security Market
Security and Surveillance
North America Security Testing Market
Security and Surveillance
Proactive Security Market
Security and Surveillance
Security and Surveillance Equipment Market
Security and Surveillance
Global Security and Vulnerability Management Market
Security and Surveillance
North America People Screening Market
Security and Surveillance
Burglar Alarm Systems Market
Security and Surveillance
Anti-Piracy Protection Market
Security and Surveillance
Prison Management Systems Market