
 Brazil Cybersecurity Market | 2026-2036
Brazil Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Brazil Cybersecurity Market Outlook
Subscription-based managed detection and response financing is narrowing the competitive field for mid-market entrants. Palo Alto Networks leverages its platform consolidation strategy to sustain premium positioning across enterprise accounts. Fortinet anchors its presence through integrated networking-security bundles that dominate price-sensitive segments. IBM Corporation differentiates via hybrid cloud security consulting that navigates complex legacy infrastructure environments.
Brazil cybersecurity encompasses technologies and services protecting digital assets from unauthorized access, disruption, or extraction through encryption protocols, behavioral analytics, and automated threat remediation. Its primary purpose is ensuring operational continuity for organizations managing sensitive data across distributed infrastructure. Managed Services and Threat Intelligence represent the fastest-expanding service categories as Brazilian enterprises outsource security operations to address talent scarcity. Endpoint Security leads technology deployment as remote work architectures expand attack surfaces beyond traditional perimeter defenses.
ANVISA enforces healthcare data protection standards that mandate encryption and access controls for patient information systems. Brazil's LGPD framework imposes penalties for personal data breaches that accelerate enterprise investment in compliance-oriented security architectures. The central bank's cybersecurity regulations for financial institutions require incident reporting and resilience testing that shape product certification requirements. Stakeholders must monitor regulatory enforcement intensity and cloud sovereignty requirements as determinants of deployment model selection.
Market Dynamics
Zero-trust architecture migration is compressing traditional perimeter-defense procurement cycles as Brazilian financial institutions dismantle legacy network boundaries in favor of continuous verification protocols.
Growth Catalysts
- LGPD enforcement intensity:Brazil's data protection authority imposes penalties for personal data breaches that accelerate enterprise investment in compliance-oriented security architectures.
- Healthcare digitization:ANVISA mandates encryption and access controls for patient information systems that expand security spending across hospital networks and telemedicine platforms.
- São Paulo enterprise corridor concentration:Multinational headquarters and financial services clusters in Brazil's southeastern economic hub generate concentrated demand for managed detection and response services.
Market Restraints
- Specialized talent scarcity:Brazil produces insufficient certified security operations center analysts relative to enterprise demand, inflating salary costs and extending implementation timelines.
- Import-dependent hardware supply:Network security appliances rely on semiconductor components concentrated in East Asian manufacturing nodes, exposing Brazilian integrators to logistics volatility.
- Legacy infrastructure inertia:Decades-old core banking and industrial control systems resist retrofitting for modern encryption protocols without operational disruption.
Strategic Opportunities
- Northeast regional expansion:Recife and Salvador technology parks attract federal innovation incentives that create underpenetrated demand for cloud-native security services.
- Operational technology convergence:Industrial IoT security platforms merge IT and OT monitoring capabilities that address manufacturing verticals previously served by separate vendors.
- Subscription financing innovation:Managed security service providers offer consumption-based pricing that lowers barriers for mid-market enterprises previously excluded from enterprise-grade protection.
Industry Challenges
- Certification timeline compression:Central bank cybersecurity regulations mandate incident reporting and resilience testing that strain product certification cycles for domestic software vendors.
- Hybrid integration complexity:Enterprises navigating multi-cloud environments face fragmented policy enforcement across Amazon Web Services, Microsoft Azure, and on-premises data centers.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Brazil Cybersecurity Market |
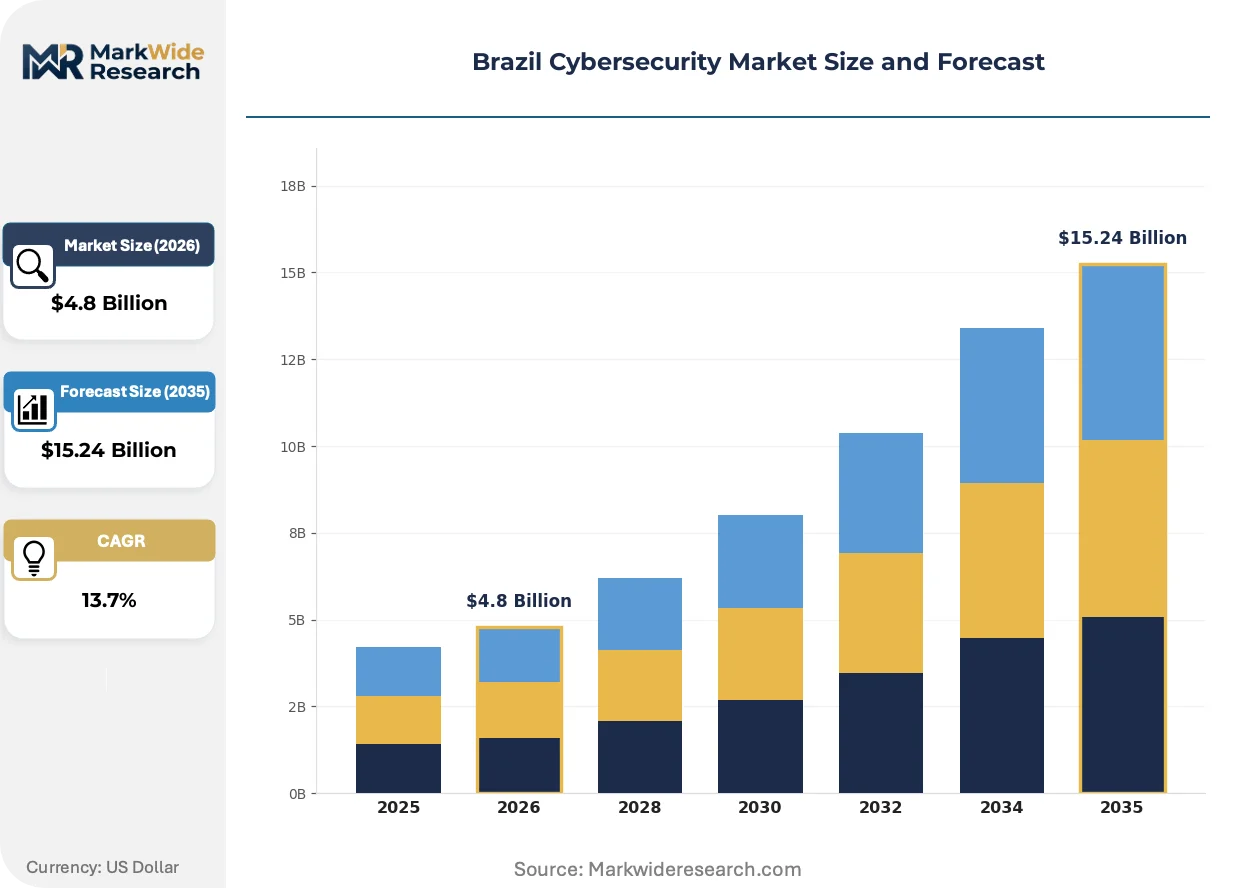
| Market Size in 2026 | $4.8 Billion |
| Market Size in 2035 | $15.24 Billion |
| CAGR (2026 – 2036) | 13.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Managed Services, Consulting, Incident Response, Threat Intelligence Technology: Firewall, Intrusion Detection System, Endpoint Security, Antivirus End User: Government, BFSI, Healthcare, IT & Telecom Deployment: On-Premises, Cloud, Hybrid, Mobile |
| Companies Covered | Palo Alto Networks, Inc., Fortinet, Inc., IBM Corporation, Trend Micro Incorporated, CrowdStrike Holdings, Inc., Microsoft Corporation, Check Point Software Technologies Ltd., Zscaler, Inc., Cisco Systems, Inc., Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Brazil Cybersecurity Market Strategic Shifts
Behavioral analytics and automated response capabilities are redistributing competitive advantage away from signature-based detection vendors toward platforms integrating artificial intelligence with human analyst workflows.
Extended detection and response platforms consolidate endpoint, network, and cloud telemetry into unified investigation interfaces. Large Brazilian financial institutions deploy these systems to compress mean-time-to-response metrics from hours to minutes. Traditional siloed security information and event management tools are rendering obsolete as buyers prioritize correlated threat visibility over log aggregation alone.
ANVISA's healthcare data protection standards now mandate encryption-at-rest for all patient information systems regardless of deployment model. Hospital networks and pharmaceutical distributors must reconfigure legacy databases and cloud migrations to satisfy access control requirements. São Paulo's private hospital chains are accelerating compliance investments ahead of scheduled enforcement audits.
Managed detection and response contracts now bundle threat hunting and incident response rather than selling these as separate professional services. Brazilian mid-market enterprises previously reliant on internal IT staff purchase comprehensive outsourcing arrangements from specialized providers. This unbundling of traditional value-added reseller relationships concentrates most visible in Rio de Janeiro's healthcare and legal services clusters.
Brazil Cybersecurity Market Segmentation
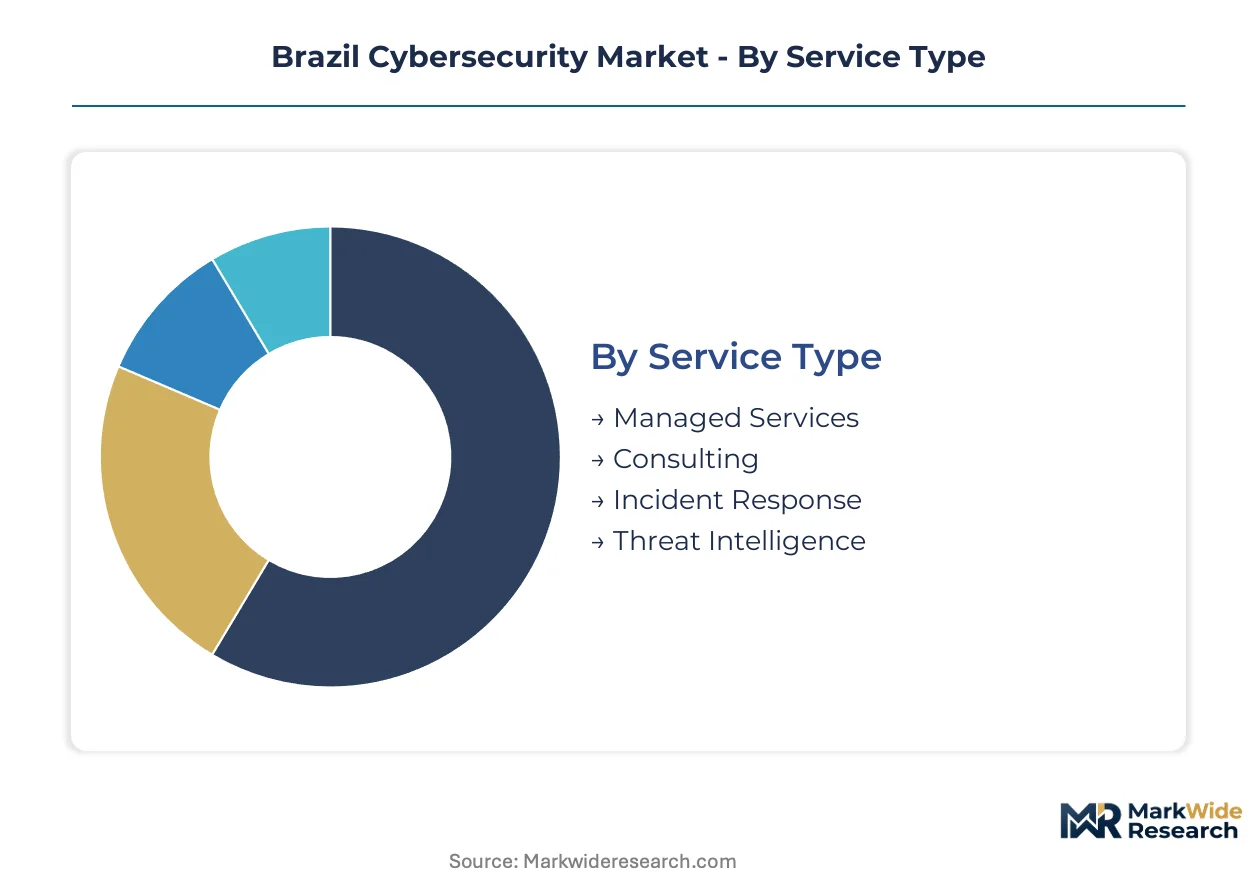
Segmentation reveals how Brazilian enterprises prioritize security investments across service models, technology stacks, and deployment architectures. Distinct procurement patterns emerge between São Paulo financial institutions and regional healthcare networks. Understanding these divides clarifies where vendors must configure specialized delivery models versus standardized platforms.
Service Type:
After-sales service intensity varies sharply across this category, with some segments demanding continuous analyst engagement while others operate on fixed-scope deliverables.
- Managed Services:Continuous monitoring and threat remediation delivered through subscription contracts with dedicated security operations centers. São Paulo financial institutions concentrate demand here as LGPD compliance deadlines compress internal hiring timelines. Talent scarcity inflates service premiums and extends onboarding durations for new clients.
- Consulting:Advisory engagements spanning risk assessment, architecture design, and compliance gap analysis. Northeast technology parks in Recife generate emerging demand as federal innovation incentives attract data center investments. Project-based pricing limits recurring revenue visibility for providers.
- Incident Response:Retainer-based emergency containment and forensic investigation following confirmed breaches.
- Threat Intelligence:Curated indicator feeds and adversary tracking reports consumed by mature security teams.
By volume, Managed Services leads. By growth pace, Threat Intelligence is ahead.
Technology:
Cost tier separation distinguishes enterprise-grade platforms from commodity tools, with mid-market buyers facing acute trade-offs between capability depth and license economics.
- Endpoint Security:Agent-based protection for laptops, servers, and mobile devices incorporating behavioral analysis and automated isolation. Remote work architectures across Rio de Janeiro professional services firms expand attack surfaces beyond traditional perimeter controls. Integration complexity with legacy identity systems strains implementation timelines.
- Firewall:Network traffic filtering appliances and virtualized equivalents governing east-west and north-south data flows. State-owned enterprises in Brasília maintain substantial on-premises deployments despite cloud migration pressures. Hardware import dependencies expose procurement to semiconductor supply volatility.
- Intrusion Detection System:Signature and anomaly-based monitoring of network segments for unauthorized access attempts.
- Antivirus:Signature-matching endpoint protection with scheduled scanning and remediation capabilities.
Endpoint Security commands the highest per-seat pricing. Antivirus shows the steepest margin compression.
End User:
Application context determines compliance burden and procurement authority concentration, with regulated verticals exhibiting fundamentally different buying committee structures than commercial enterprises.
- BFSI:Banking, financial services, and insurance institutions subject to central bank cybersecurity regulations mandating incident reporting and resilience testing. São Paulo's enterprise corridor hosts multinational headquarters generating concentrated demand for zero-trust architecture migrations. Certification requirements strain domestic software vendor timelines.
- Healthcare:Hospital networks, pharmaceutical distributors, and telemedicine platforms navigating ANVISA encryption mandates for patient information systems. Private hospital chains accelerate compliance investments ahead of scheduled enforcement audits. Legacy database retrofitting disrupts operational continuity without careful sequencing.
- Government:Federal and state agencies managing citizen data and critical infrastructure protection mandates.
- IT & Telecom:Technology service providers and telecommunications operators securing multi-tenant platforms and subscriber data.
BFSI absorbs the largest absolute security budgets. Healthcare demonstrates the most urgent compliance-driven procurement acceleration.
Deployment:
Customer type and infrastructure maturity dictate architecture preferences, with hybrid configurations dominating transitional environments where cloud-native and legacy systems coexist.
- Hybrid:Integrated on-premises and cloud security controls with unified policy enforcement across Amazon Web Services, Microsoft Azure, and data center assets. Large Brazilian financial institutions deploy these architectures to navigate fragmented multi-cloud environments. Complexity escalates operational overhead for security operations center staffing.
- Cloud:Native security controls and third-party services deployed entirely within public cloud environments. Northeast regional expansion in Salvador technology parks favors cloud-native delivery models minimizing capital expenditure requirements. Data sovereignty considerations influence provider selection for sensitive workloads.
- On-Premises:Hardware appliances and software deployed within customer-controlled data centers.
- Mobile:Device-centric protection for smartphones and tablets accessing corporate resources.
Hybrid deployment leads in current project pipelines. Cloud-native configurations are climbing fastest among mid-market entrants.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Brazilian cybersecurity procurement concentrates in financial services headquarters and healthcare networks navigating strict data protection mandates. Enterprise buyers cluster in southeastern economic corridors where regulatory enforcement intensity drives compliance spending. Regional variation reflects divergent industrial bases and federal incentive programs.
São Paulo
São Paulo anchors national cybersecurity demand through its concentration of banking headquarters and multinational enterprise operations. The central bank's cybersecurity regulations mandate incident reporting and resilience testing that shape product certification requirements for vendors serving BFSI clients. The city's enterprise corridor generates concentrated demand for managed detection and response services as LGPD compliance deadlines compress internal hiring timelines.
Rio de Janeiro
Rio de Janeiro's professional services firms and healthcare clusters drive endpoint security deployment as remote work architectures expand attack surfaces. ANVISA mandates encryption and access controls for patient information systems that accelerate compliance investments across private hospital chains. The metropolitan area's legal services and consulting sectors purchase comprehensive outsourcing arrangements from managed security service providers.
Minas Gerais
Minas Gerais hosts manufacturing and mining operations requiring operational technology security platforms that merge IT and OT monitoring capabilities. Industrial IoT security adoption addresses manufacturing verticals previously served by separate vendors with fragmented solutions. Belo Horizonte's technology parks attract federal innovation incentives that create emerging demand for cloud-native security services among mid-market enterprises.
Bahia
Bahia represents an underpenetrated expansion opportunity as Salvador technology parks benefit from federal innovation incentives attracting data center investments. Cloud-native delivery models minimize capital expenditure requirements for regional enterprises previously excluded from enterprise-grade protection. The northeastern state's distance from southeastern talent pools intensifies reliance on managed security service providers for continuous monitoring capabilities.
Rio Grande do Sul
Rio Grande do Sul maintains substantial industrial control system deployments requiring retrofitting for modern encryption protocols without operational disruption. Legacy infrastructure inertia across decades-old manufacturing systems resists rapid modernization despite regulatory pressure. Porto Alegre's enterprise base exhibits cautious procurement patterns favoring hybrid deployment architectures that preserve on-premises control over sensitive workloads.
Brazil Cybersecurity Market Competitive Environment
Channel-controlling players compete with product-specialist players across a market structure consolidating around platform consolidation strategies and integrated networking-security bundles. The vendor landscape separates into three strategic archetypes: premium platform consolidators anchoring enterprise accounts, price-optimized bundlers dominating mid-market segments, and consulting-led integrators navigating complex legacy environments. Dominant competitive moves include strategic partnerships expanding managed service delivery capabilities and portfolio diversification into adjacent cloud security segments.
Among North American platform providers, Palo Alto Networks, Inc. and CrowdStrike Holdings, Inc. occupy positions exemplifying the premium consolidation archetype, while Fortinet, Inc. anchors the integrated bundling tier. IBM Corporation represents the consulting-led integration model through its hybrid cloud security advisory positioning. These three companies collectively illustrate how competitive advantage redistributes toward behavioral analytics and automated response capabilities.
| Leading Market Players |
|---|
| Palo Alto Networks, Inc. |
| Fortinet, Inc. |
| IBM Corporation |
| Trend Micro Incorporated |
| CrowdStrike Holdings, Inc. |
| Microsoft Corporation |
| Check Point Software Technologies Ltd. |
| Zscaler, Inc. |
| Cisco Systems, Inc. |
| Others |
Value Chain & Pricing Dynamics
Semiconductor import dependency from East Asian manufacturing nodes compresses margin structures across hardware-dependent security tiers while simultaneously dictating procurement cycle lengths for Brazilian integrators. This single-source exposure widens pricing spreads between appliance-heavy deployments and software-native alternatives as logistics volatility feeds into contract indexation clauses.
Pricing Analysis
Cost-plus contracts with semiconductor price indexation dominate appliance procurement, embedding raw material volatility directly into end-customer pricing. Subscription-based SaaS tiers separate premium managed detection and response bundles from standardized endpoint protection, with certification under LGPD frameworks commanding measurable premiums. Cost compression in mid-market antivirus segments is intensifying because talent scarcity forces vendors to absorb analyst payroll inflation without full pass-through. Healthcare networks under ANVISA mandates exhibit the lowest price sensitivity, while regional manufacturing clusters in Rio Grande do Sul demonstrate acute budget constraints favoring open-source alternatives.
Supply Chain Analysis
Extended payment terms from Taiwanese and South Korean semiconductor suppliers have become standard practice, stretching working capital cycles for Brazilian hardware distributors. Network security appliance production draws from Taiwan, South Korea, and Malaysia, with specialized encryption chips and FPGA components resting on concentrated foundry capacity. Single-source vulnerability around advanced node semiconductors exposes integrators to allocation rationing during demand spikes. Distribution runs through São Paulo-based value-added resellers with direct OEM relationships, supplemented by cloud-native delivery models that bypass physical logistics entirely.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Certified security operations center analysts remain critically scarce relative to enterprise demand, creating persistent bottlenecks that advantage vendors with captive training pipelines or pre-certified partner ecosystems.
For Market Incumbents: Harden platform consolidation architectures against modular best-of-breed challengers by embedding managed services capabilities that lock in recurring revenue. Acquire or partner with specialized threat intelligence providers in Recife technology parks to preempt regional entrants from capturing federal innovation incentives. Deepen backward integration into cloud-native security controls to reduce reliance on hardware supply chains vulnerable to East Asian logistics disruption. For New Entrants and Emerging Players: Build out consumption-based pricing models targeting mid-market legal services and healthcare clusters in Rio de Janeiro previously excluded from enterprise-grade protection. Salvador technology parks in Bahia offer the most penetrable geography, with cloud-native delivery minimizing capital barriers against incumbent hardware bundles. Lead with LGPD compliance automation as the go-to-market wedge, positioning managed detection and response as bundled regulatory risk mitigation rather than technical security procurement. For Investors and Strategic Acquirers: The market sits at a consolidation phase that favors platform consolidators with recurring revenue depth over point-solution specialists facing integration pressure. Long-term viability hinges on hybrid cloud security consulting capabilities that navigate complex legacy infrastructure environments without displacement trauma. Watch ANVISA enforcement audit schedules as the inflection signal—accelerated penalty issuance will compress procurement timelines and favor pre-certified vendors with established healthcare references.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Consolidated XDR platforms displace siloed SIEM tools across São Paulo financial institutions. |
| Strategic Partnership | Managed service alliances with local integrators address certification timeline compression for domestic software vendors. |
| Geographic Expansion | Northeast regional presence in Recife and Salvador captures federal innovation incentives before incumbent saturation. |
| Acquisition of Specialist Firm | Threat intelligence boutiques add curated adversary tracking capabilities for mature security operations centers. |
| Product Launch | OT-IT convergence platforms target manufacturing verticals in Minas Gerais with unified monitoring architectures. |
Study Parameters
Desk research of regulatory filings from ANVISA and Brazil's central bank, hyperscaler capex disclosures, and customs import records preceded structured interviews with chief information security officers, managed security service provider executives, and healthcare IT procurement leads. Primary fieldwork with São Paulo-based financial institutions and Rio de Janeiro hospital networks was cross-referenced against secondary validation from LGPD enforcement databases and technology park investment trackers. Bottom-up service provider revenue aggregation was triangulated with top-down enterprise IT spending surveys across the analysis window.
Assumptions around LGPD penalty enforcement intensity, cloud sovereignty requirement evolution, and semiconductor supply normalization were held fixed at baseline levels while modeling variable scenarios for healthcare digitization pace and federal innovation incentive renewal. Segmentation modeling incorporated service type, technology stack, deployment architecture, and vertical compliance burden dimensions. CAGRs were derived from regression analysis against historical procurement patterns and regulatory deadline clustering, with endpoint security adoption curves and managed services penetration rates serving as primary forecast inputs.
Stress conditions across semiconductor logistics volatility, LGPD fine escalation trajectories, and central bank certification timeline compression were modeled; outcomes outside those bands fall beyond the analytical envelope. Forecasts reflect these documented assumptions with explicit acknowledgment that unmodeled regulatory shifts or supply chain disruptions could materially revise trajectory projections. Continuous validation against operating reality is the recommended discipline.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Belgium Cybersecurity Market
Cybersecurity
Cyber Security Consulting Market
Cybersecurity
Morocco Cybersecurity Market
Cybersecurity
Digital Forensics Market
Cybersecurity
Global Mobile Data Protection Market
Cybersecurity
Cybersecurity in Gaming Market
Cybersecurity
Global IoT Digital Forensics Market
Cybersecurity
Cloud Application Security Market
Cybersecurity
Cyber Deception Market
Cybersecurity
Global Digital Forensic Laboratory As a Service Market
Cybersecurity
IoT Security Market
Cybersecurity
CDN Security Market
Cybersecurity
Europe Software Defined Perimeter Market
Cybersecurity
Digital Security Market
Cybersecurity
Multi-Cloud Data Protection Market
Cybersecurity
Artificial Intelligence-Based Cybersecurity Market