
 Spain Cybersecurity Market | 2026-2036
Spain Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Spain Cybersecurity Market Analytics
Premium managed detection and response is decoupling from commodity antivirus licensing in Spain. Telefónica Tech leverages its national fiber infrastructure to dominate sovereign cloud security deployments. Accenture Security Spain competes through specialized financial sector threat-intelligence practices. Grupo S21Sec anchors its position with deep expertise in European critical infrastructure compliance.
Spain cybersecurity encompasses hardware, software, and services engineered to protect digital assets against unauthorized access, disruption, or exfiltration, typically integrating encryption protocols, intrusion detection systems, and security orchestration platforms operating at sub-100-millisecond response thresholds. Its primary purpose is to ensure confidentiality, integrity, and availability of information systems across commercial and governmental operations. Cloud Security leads product type expansion as Spanish enterprises migrate SAP and core banking workloads to hybrid environments. Managed Security Services captures disproportionate margin pools through long-term operational contracts with BFSI and Government end users. Endpoint Security remains mature, with pricing pressure from bundled Microsoft Defender deployments eroding standalone vendor economics.
Spain's national cybersecurity strategy aligns with EU NIS2 Directive requirements enforced by the National Cryptologic Center and the Spanish National Cybersecurity Institute, mandating risk management measures and incident reporting for essential and important entities. The EU AI Act, supervised domestically by the Spanish Agency for the Supervision of Artificial Intelligence, introduces conformity obligations for AI-enabled security tools that automate threat detection or response decisions. Stakeholders must monitor how Madrid interprets NIS2 sectoral scope expansions against Basque and Catalan regional digital sovereignty initiatives.
Market Dynamics
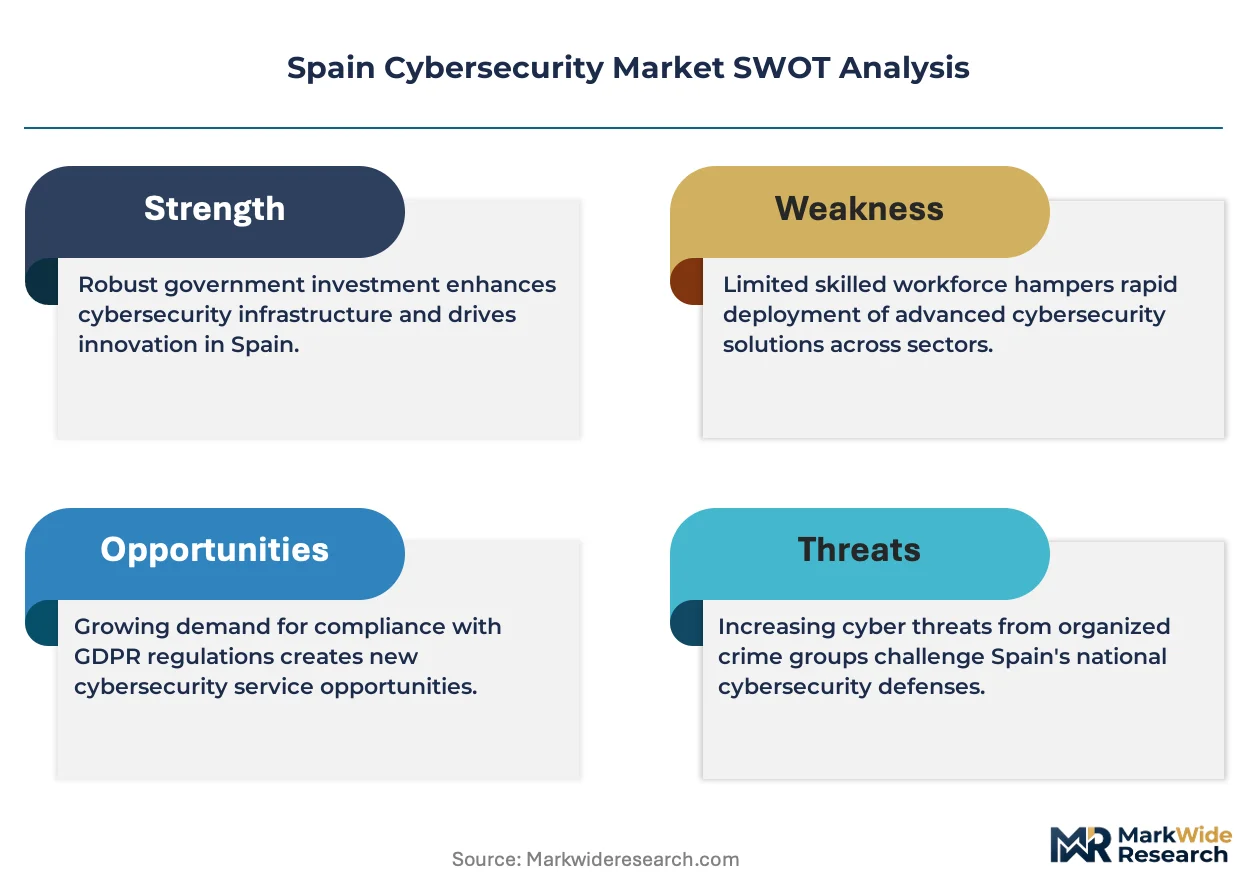
Spanish financial institutions are accelerating zero-trust architecture procurement as EU NIS2 Directive mandates compress incident reporting timelines and expand sectoral coverage beyond traditional critical infrastructure operators.
Growth Catalysts
- EU NIS2 Directive:The directive mandates stricter risk management measures and 24-hour incident reporting for essential and important entities, forcing Spanish banks and energy operators to upgrade security operations centers.
- Cloud migration:Spanish enterprises migrating SAP and core banking workloads to hybrid environments are procuring cloud-native security platforms at scale, particularly in Madrid's technology corridor.
- Sovereign cloud demand:National defense contractors and intelligence agencies require domestically controlled infrastructure, creating dedicated procurement streams for fiber-integrated security services.
Market Restraints
- Microsoft Defender bundling:Endpoint security vendors face pricing pressure as enterprise agreements increasingly include native antivirus, eroding standalone product economics.
- Skills concentration:Zero-trust architects and NIS2 compliance specialists cluster in Madrid and Barcelona, leaving Andalusian and Galician enterprises dependent on remote service delivery.
- Legacy system debt:Regional savings banks operate core banking platforms on outdated architectures that resist API-based security integration without wholesale replacement.
Strategic Opportunities
- Basque digital sovereignty:The Basque Country's industrial autonomy initiatives create demand for localized security operations centers serving manufacturing and port logistics operators.
- AI-enabled automation:The EU AI Act's conformity obligations for automated threat response tools create a compliance services market for security vendors with domestic certification expertise.
- Operational technology convergence:Spanish critical infrastructure operators are integrating IT and OT security under unified governance, opening managed services contracts for industrial control system protection.
Industry Challenges
- Certification bottlenecks:The National Cryptologic Center's evaluation timelines for high-assurance products extend 18-24 months, delaying vendor market entry and enterprise procurement cycles.
- Integration complexity:Financial institutions must reconcile NIS2 mandates with existing GDPR data protection frameworks, creating dual compliance overhead in security architecture design.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Spain Cybersecurity Market |
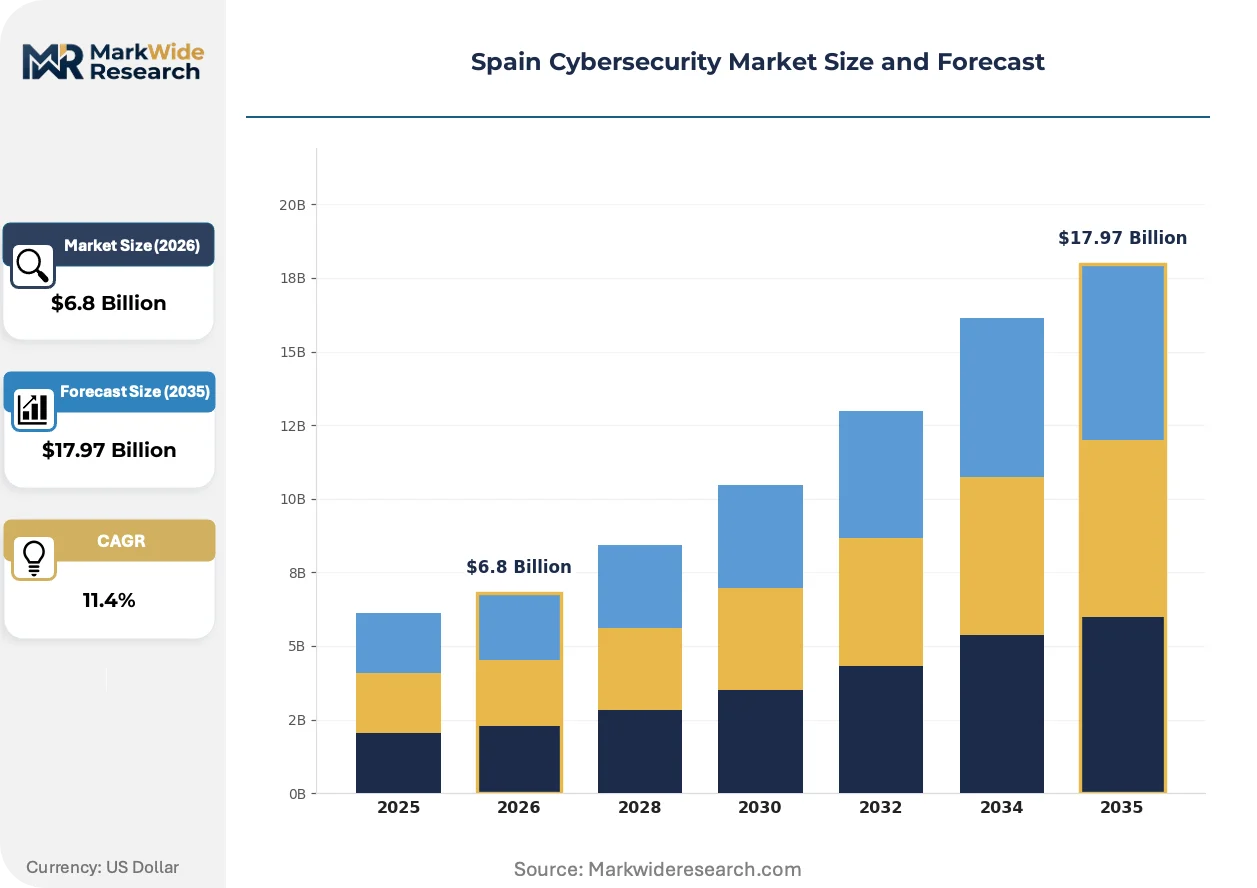
| Market Size in 2026 | $6.8 Billion |
| Market Size in 2035 | $17.97 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Network Security, Endpoint Security, Application Security, Cloud Security Service Type: Consulting, Managed Security Services, Incident Response, Risk and Compliance Deployment Model: On-Premises, Cloud-Based, Hybrid, Virtual End User: Retail, BFSI, Healthcare, Government |
| Companies Covered | Accenture Security Spain, KPMG Cybersecurity & Compliance, Telefónica Tech, Grupo S21Sec, IBM Security, Indra Sistemas, Deloitte Cyber Risk Services, GMV, Factosecure, Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Spain Cybersecurity Market Evolving Landscape
Security service delivery is fragmenting between commodity platform licensing and premium managed detection, with vendor economics diverging based on operational specialization rather than product breadth.
Extended detection and response platforms integrating endpoint, network, and cloud telemetry are overtaking siloed point solutions in Spanish enterprise procurement. Large banks and telecommunications operators are consolidating vendor relationships around unified data lakes that correlate threat intelligence across hybrid infrastructure. This consolidation is compressing standalone endpoint and network security vendor margins while elevating managed service providers with native SOAR capabilities.
The EU AI Act, supervised domestically by the Spanish Agency for the Supervision of Artificial Intelligence, imposes conformity assessment obligations on security tools that automate threat detection or response decisions. Vendors must document algorithmic transparency and human oversight mechanisms before deploying machine-learning-driven anomaly detection in regulated sectors. Financial services and healthcare providers are most affected, with procurement teams now requiring AI Act compliance attestations alongside traditional security certifications.
Spanish CISOs are unbundling security operations from infrastructure procurement, establishing direct relationships with managed detection and response providers independent of cloud or network contracts. This separation is disrupting traditional systems integrators that bundled security with broader IT transformation programs. The shift is most visible in Madrid's banking headquarters, where dedicated security procurement functions now negotiate operational contracts with specialized threat intelligence vendors.
Spain Cybersecurity Market Segmentation
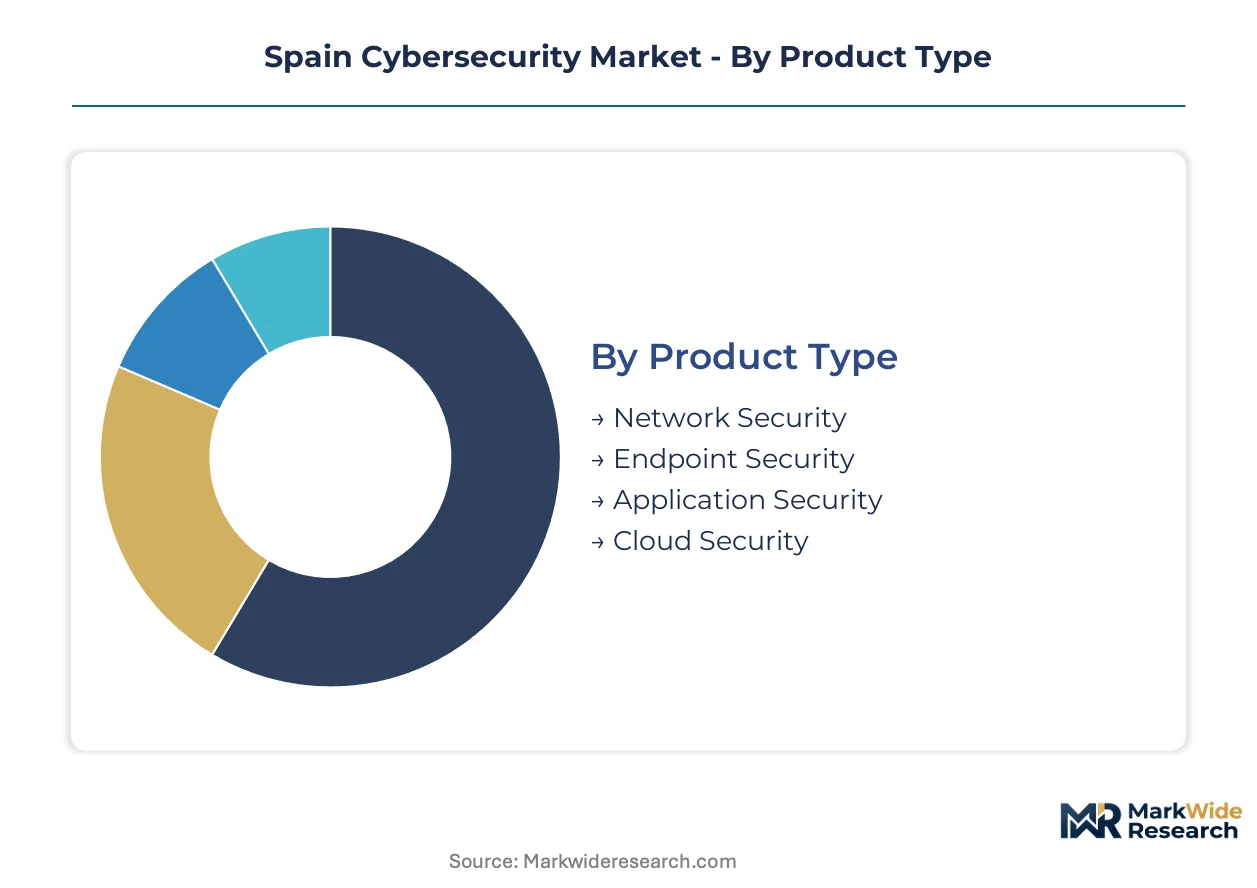
Segmentation reveals how procurement priorities diverge across Spanish enterprises confronting NIS2 compliance deadlines and hybrid cloud migrations. Buyers allocate budget based on regulatory exposure, legacy system constraints, and sovereign data requirements rather than uniform technology refresh cycles.
Product Type:
Spanish CISOs weight procurement decisions by integration complexity against existing fiber and banking infrastructure.
- Cloud Security:Platforms securing hybrid SAP and core banking workloads through encryption, identity governance, and workload protection. Madrid's technology corridor concentrates demand as financial institutions migrate sensitive data to sovereign cloud environments while maintaining on-premises transaction processing.
- Network Security:Firewalls, intrusion prevention systems, and zero-trust network access controlling traffic across branch offices and data centers. Basque manufacturing clusters and Catalan port logistics operators drive replacement cycles as operational technology networks converge with enterprise IT.
- Endpoint Security:Device-level protection including antivirus, endpoint detection and response, and mobile threat defense. Pricing pressure intensifies from Microsoft Defender bundling in enterprise agreements, compressing standalone vendor margins.
- Application Security:Code scanning, runtime application self-protection, and API security gateways. Spanish fintech startups and regional savings banks prioritize this segment to secure customer-facing digital channels without wholesale core banking replacement.
Volume sits with Network Security; growth tilts toward Cloud Security.
Service Type:
Margin pools concentrate where operational specialization meets long-term contractual relationships with regulated entities.
- Managed Security Services:Continuous monitoring, threat detection, and response operations delivered through 24/7 security operations centers. BFSI and Government end users in Madrid dominate contract value, requiring fiber-integrated service delivery with domestic data residency guarantees.
- Risk and Compliance:NIS2 readiness assessments, GDPR alignment consulting, and EU AI Act conformity documentation. The National Cryptologic Center's certification timelines create sustained demand for advisory services bridging regulatory interpretation and technical implementation.
- Consulting:Security architecture design, zero-trust transformation roadmapping, and vendor selection support. Andalusian and Galician enterprises rely heavily on remote delivery from Madrid-based specialists due to skills concentration in the capital.
- Incident Response:Retained breach response capabilities including forensic analysis, containment, and recovery coordination. Energy operators and defense contractors maintain dedicated retainers to satisfy NIS2's 24-hour reporting mandate.
Revenue concentrates in Managed Security Services; expansion accelerates fastest in Risk and Compliance.
Deployment Model:
Sovereign requirements and legacy system debt fragment adoption patterns across Spanish regions.
- Hybrid:Orchestrated security controls spanning on-premises data centers and public cloud instances. National banking headquarters favor this model to maintain transaction processing locally while leveraging cloud analytics for fraud detection.
- Cloud-Based:Fully managed security services delivered through multi-tenant platforms with API-driven policy enforcement. Mid-market enterprises in Barcelona's technology district adopt this model to bypass capital expenditure constraints.
- On-Premises:Appliance-based and software-installed security infrastructure within customer-controlled facilities. Defense contractors and intelligence agencies mandate this deployment for classified workloads under domestic supervision requirements.
- Virtual:Software-defined security functions deployed on virtualized infrastructure without dedicated hardware. Regional savings banks pursue this option to modernize protection without disrupting outdated core banking architectures.
Installed base favors Hybrid; Cloud-Based deployments are climbing the fastest.
End User:
Regulatory intensity and digital asset value determine security spending intensity across verticals.
- BFSI:Banks, insurance carriers, and payment processors subject to NIS2 essential entity classification and ECB supervisory expectations. Zero-trust architecture procurement accelerates as institutions reconcile compressed incident reporting timelines with legacy infrastructure constraints.
- Government:Central ministries, regional administrations, and municipal entities managing citizen data and critical public services. The Spanish National Cybersecurity Institute enforces procurement standards that favor vendors with domestic certification and fiber-integrated delivery capabilities.
- Healthcare:Hospital networks, pharmaceutical distributors, and medical device operators balancing GDPR patient data protection with connected device security. EU AI Act supervision by the Spanish Agency for the Supervision of Artificial Intelligence adds conformity obligations for automated diagnostic tools.
- Retail:E-commerce platforms, physical store chains, and logistics operators protecting payment systems and customer databases. PCI-DSS compliance drives baseline investment, though advanced threat detection adoption lags financial services peers.
Contract value peaks in BFSI; Government vertical shows steepest expansion trajectory.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Madrid's technology corridor concentrates Spain's cybersecurity procurement, hosting national banking headquarters and defense contractors that drive zero-trust architecture demand. The EU NIS2 Directive enforces stricter incident reporting timelines across essential and important entities, reshaping regional investment patterns. Sub-regional digital sovereignty initiatives in Basque Country and Catalonia create parallel procurement streams for localized security operations.
Madrid
Financial institutions headquartered in Madrid's technology corridor accelerate zero-trust architecture procurement to meet compressed NIS2 reporting timelines. The National Cryptologic Center enforces certification standards that favor vendors with domestic fiber-integrated delivery capabilities. BFSI and government end users dominate contract value, requiring 24/7 security operations centers with sovereign data residency guarantees.
Catalonia
Barcelona's technology district drives cloud-based security adoption among mid-market enterprises bypassing capital expenditure constraints. The Spanish Agency for the Supervision of Artificial Intelligence supervises EU AI Act conformity obligations for automated threat response tools. Catalan port logistics operators and manufacturing clusters fuel network security replacement cycles as operational technology converges with enterprise IT.
Basque Country
Industrial autonomy initiatives in the Basque region create demand for localized security operations centers serving manufacturing and port logistics operators. Regional digital sovereignty policies favor domestically controlled infrastructure for critical industrial control systems. Bilbao's industrial corridor anchors procurement for operational technology security protecting converged IT-OT environments.
Andalusia
Regional enterprises in Andalusia depend on remote service delivery from Madrid-based zero-trust architects and NIS2 compliance specialists due to skills concentration in the capital. Legacy system debt at regional savings banks resists API-based security integration without wholesale core banking replacement. Seville's public sector entities drive managed security services demand for citizen data protection.
Valencia
Valencia's growing technology sector attracts cloud security vendors targeting hybrid SAP migration workloads among mid-sized enterprises. The port authority's critical infrastructure classification under NIS2 mandates upgraded security operations centers with industrial control system protection. Regional healthcare networks balance GDPR patient data protection with connected medical device security requirements.
Spain Cybersecurity Market Competitive Landscape
Premium-margin players sit above commodity-margin players across operational specialization and sovereign delivery capabilities. Telefónica Tech leverages national fiber infrastructure to dominate domestic cloud security deployments, while Accenture Security Spain competes through financial sector threat-intelligence practices. Three strategic archetypes define the landscape: telecom-integrated infrastructure providers, global consulting networks with sector specialization, and domestic compliance specialists with critical infrastructure expertise. Competitive moves concentrate on long-term operational contracts with regulated BFSI and government end users, plus fiber-integrated service delivery with domestic data residency guarantees.
Within the telecom-integrated tier, Telefónica Tech occupies a position exemplifying sovereign cloud security dominance through national infrastructure control. Accenture Security Spain and Deloitte Cyber Risk Services represent the global consulting archetype, anchoring financial sector procurement through specialized threat-intelligence practices. Grupo S21Sec sits within the domestic compliance specialist tier, exemplifying deep expertise in European critical infrastructure certification and NIS2 readiness advisory.
| Leading Market Players |
|---|
| Accenture Security Spain |
| KPMG Cybersecurity & Compliance |
| Telefónica Tech |
| Grupo S21Sec |
| IBM Security |
| Indra Sistemas |
| Deloitte Cyber Risk Services |
| GMV |
| Factosecure |
| Others |
Value Network & Pricing Analysis
Telefónica Tech's sovereign-backed infrastructure control anchors supply discipline across Spain's cybersecurity market, translating national fiber ownership into pricing power that resists commodity erosion. This state-adjacent financing pattern concentrates procurement leverage among domestic operators while forcing global consultancies to compete on specialized outcome metrics rather than scale economics.
Pricing Analysis
Outcome-based pricing tied to mean-time-to-detect and containment success rates anchors managed detection and response contracts in Madrid's banking corridor. Three-tier pricing structure across premium, standard, and economy levels separates fiber-integrated sovereign cloud deployments from virtualized mid-market offerings and commodity endpoint bundles. Pricing pressure stems from Microsoft Defender's enterprise bundling, which compresses standalone antivirus margins. Regional savings banks in Andalusia exhibit highest price sensitivity due to legacy system replacement costs, while defense contractors accept premium tiers for domestic certification and data residency guarantees.
Supply Chain Analysis
Zero-trust architects and NIS2 compliance specialists cluster in Madrid and Barcelona, constraining service delivery capacity for peripheral regions. Spain's cybersecurity supply chain draws from Ireland and Estonia for cloud security engineering talent, Israel for threat intelligence platforms, and domestic National Cryptologic Center-certified vendors for sovereign deployments. Component dependencies include proprietary encryption modules, SOAR orchestration engines, and fiber-integrated network appliances. Single-source vulnerability concentrates in the National Cryptologic Center's 18-24 month certification pipeline. Distribution runs through direct enterprise sales teams for BFSI and government accounts, with channel partners serving mid-market manufacturing and healthcare verticals.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Spain's cybersecurity market sits in a technology-transition phase as extended detection and response platforms displace siloed endpoint and network point solutions. Legacy perimeter-based security architectures yield to unified data lakes correlating telemetry across hybrid cloud and on-premises infrastructure.
For Market Incumbents: Hedge against margin compression in endpoint security by deepening managed services specialization around NIS2 compliance and EU AI Act conformity documentation. Accenture Security Spain and Deloitte Cyber Risk Services should anchor financial sector relationships through threat-intelligence subscriptions that embed operational dependencies. Telefónica Tech must defend fiber-integrated sovereign cloud positioning against emerging domestic challengers by accelerating certification timelines for high-assurance products.
For New Entrants and Emerging Players: EU NIS2 Directive in Spain opens a window for specialized risk and compliance advisory targeting regional savings banks in Andalusia and Galicia that lack Madrid-based zero-trust expertise. Basque Country's industrial autonomy initiatives create white-space demand for localized security operations centers serving manufacturing and port logistics operators. A go-to-market angle pairing NIS2 readiness assessments with virtualized deployment options bypasses legacy core banking replacement barriers.
For Investors and Strategic Acquirers: Telefónica Tech's continued dominance in sovereign cloud security contracts is the leading indicator that state-adjacent infrastructure control commands durable premium multiples. Long-term viability across the analysis window favors domestic compliance specialists with National Cryptologic Center relationships and critical infrastructure certification expertise. Acquisition targets should exhibit deep European regulatory interpretation capabilities bridging NIS2 technical implementation and sector-specific risk frameworks. The signal to watch is compressed procurement cycles at energy operators and defense contractors as NIS2's 24-hour reporting mandate forces retained incident response capacity decisions.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifying endpoint, network, and cloud telemetry through SOAR-native data lakes elevates managed service provider margins above commodity licensing. |
| Regulatory Certification Investment | National Cryptologic Center evaluation acceleration reduces 18-24 month bottlenecks that delay vendor market entry and enterprise procurement. |
| Geographic Expansion | Localized security operations centers in Bilbao and Barcelona capture Basque and Catalan digital sovereignty procurement streams outside Madrid's orbit. |
| Strategic Partnership | Fiber-integrated delivery alliances with national telecom infrastructure anchor sovereign cloud contracts requiring domestic data residency guarantees. |
| Acquisition of Specialist Firm | NIS2 compliance advisory capabilities and EU AI Act conformity expertise address dual regulatory overhead in financial services architecture design. |
Research Methodology
Document review covered National Cryptologic Center certification guidelines, EU NIS2 Directive implementation texts, and Spanish National Cybersecurity Institute procurement standards, complemented by interviews with CISOs at Madrid-headquartered banks, security operations center directors at Telefónica Tech, NIS2 compliance consultants at Grupo S21Sec, and procurement officers at Basque manufacturing clusters. Secondary validation drew from ENISA threat landscape reports, ECB supervisory expectations for financial sector cyber resilience, and hyperscaler capex disclosures for cloud security infrastructure. Bottom-up service contract analysis and top-down regulatory mandate sizing were triangulated against fiber deployment maps and regional technology corridor employment data.
Market size and growth trajectory outputs across the analysis window reflect segmentation by product type, service type, deployment model, and end-user vertical, with additional dimensioning by regional digital sovereignty policy intensity. CAGRs were derived from procurement pipeline analysis at essential and important entities under NIS2 scope, weighted by compressed incident reporting timeline compliance deadlines and hybrid cloud migration acceleration among SAP-dependent enterprises. Forecast inputs incorporated National Cryptologic Center certification queue projections and EU AI Act conformity assessment obligation timelines supervised by the Spanish Agency for the Supervision of Artificial Intelligence.
The model assumes a particular technology adoption path favoring extended detection and response consolidation over siloed point solution procurement; alternative pathways for generative AI-enabled autonomous security operations would alter the outlook toward platform-native automation and away from human-in-the-loop managed services. Forecasts reflect assumptions regarding NIS2 sectoral scope interpretation by Madrid against Basque and Catalan regional autonomy initiatives. Material deviation in National Cryptologic Center certification timeline compression or EU AI Act enforcement intensity warrants pause and re-evaluation.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
India Network Security and Cyber Risk Management Market
Cybersecurity
Europe Web Application Firewall Market
Cybersecurity
China Cybersecurity Market
Cybersecurity
Bangladesh Cybersecurity Market
Cybersecurity
Global Network Security Firewall Market
Cybersecurity
Peru Cybersecurity Market
Cybersecurity
Argentina Cybersecurity Market
Cybersecurity
Hungary Cybersecurity Market
Cybersecurity
Global Information Security Consulting Market
Cybersecurity
Cloud Access Security Broker Market
Cybersecurity
Global IoT Digital Forensics Market
Cybersecurity
Asia-Pacific Software Defined Perimeter Market
Cybersecurity
China Ransomware Protection Market
Cybersecurity
Cybersecurity Mesh Market
Cybersecurity
Retail Cybersecurity Market
Cybersecurity
Chile Cybersecurity Market