
 Cloud Access Security Broker Market | 2026-2036
Cloud Access Security Broker Market Size, Share, and Industry Trends Forecast 2026-2036
Cloud Access Security Broker Market Intelligence
Software-defined perimeter architecture is decoupling CASB deployments from legacy hardware-bound security stacks. Netskope leverages cloud-native proxy architecture to dominate North American enterprise accounts. Palo Alto Networks anchors its Prisma Access platform through deep integration with SD-WAN and SASE portfolios. Zscaler competes on agentless deployment velocity, reducing time-to-value for mid-market buyers.
A cloud access security broker functions as an intermediary security enforcement point between on-premises infrastructure and cloud service providers, inspecting traffic through API connectors and inline proxies to enforce policies for data loss prevention, encryption, and access control. Its primary commercial purpose centers on extending organizational governance into sanctioned and unsanctioned cloud applications without degrading user experience. The solution segment shows threat protection and compliance management commanding the deepest enterprise engagement, while identity management represents the fastest-expanding capability layer as zero-trust mandates proliferate. Deployment patterns reveal hybrid cloud configurations generating the most complex policy orchestration requirements, with multi-cloud strategies demanding broker platforms that normalize controls across disparate provider environments.
The National Institute of Standards and Technology publishes zero-trust architecture guidelines that directly shape federal CASB procurement specifications, while the Securities and Exchange Commission imposes incident disclosure rules that elevate broker-based visibility into cloud data flows for publicly traded firms. State-level privacy statutes, including California's Consumer Privacy Act enforcement patterns, compel enterprises to deploy compliance management modules with automated data classification. Stakeholders must evaluate broker platforms on API coverage breadth rather than proxy throughput alone, as SaaS application sprawl outpaces traditional network-centric inspection models.
Market Dynamics
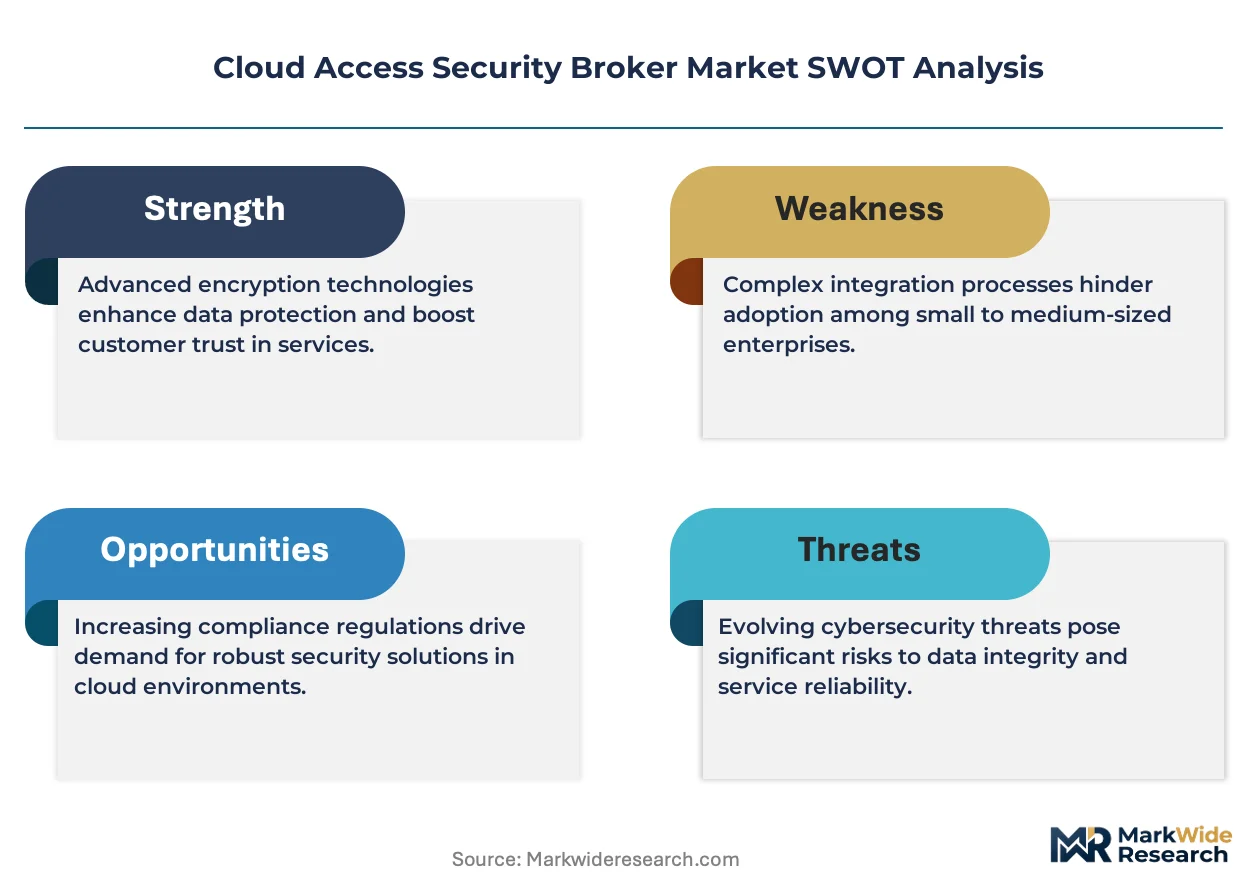
Zero-trust architecture mandates are compressing procurement cycles and forcing broker vendors to integrate identity-centric enforcement directly into cloud-native proxy stacks, displacing legacy perimeter-based inspection models.
Growth Catalysts
- FedRAMP Moderate/High Baselines:Federal cloud migration timelines in the United States mandate broker-based visibility for sanctioned SaaS inventory, accelerating enterprise deployment velocity.
- Financial Services:Multi-cloud strategies at banks and insurers require normalized policy orchestration across disparate provider environments, deepening CASB module engagement.
- API-First Inspection:SaaS application sprawl outpaces traditional network-centric models, pulling investment toward connector breadth over proxy throughput alone.
Market Restraints
- Skill Concentration:Shortage of cloud security architects with zero-trust implementation experience limits deployment scale at mid-market enterprises.
- Integration Debt:Legacy on-premises identity providers resist seamless API coupling with cloud-native brokers, extending implementation timelines.
- Shadow IT Persistence:Unsanctioned SaaS adoption by business units bypasses broker visibility, creating persistent compliance gaps.
Strategic Opportunities
- Agentless Deployment:Browser-based inspection without endpoint software reduces friction for mid-market buyers seeking rapid time-to-value.
- State Privacy Statutes:California Consumer Privacy Act enforcement patterns compel automated data classification modules, expanding addressable module attach rates.
- SD-WAN Convergence:SASE architecture integration creates bundled procurement channels through networking vendors, reshaping go-to-market economics.
Industry Challenges
- Certificate Management Complexity:TLS inspection at scale requires continuous certificate lifecycle orchestration, consuming operational resources.
- False Positive Tuning:Data loss prevention rule calibration demands specialized security analyst hours, constraining policy refinement velocity.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cloud Access Security Broker Market |
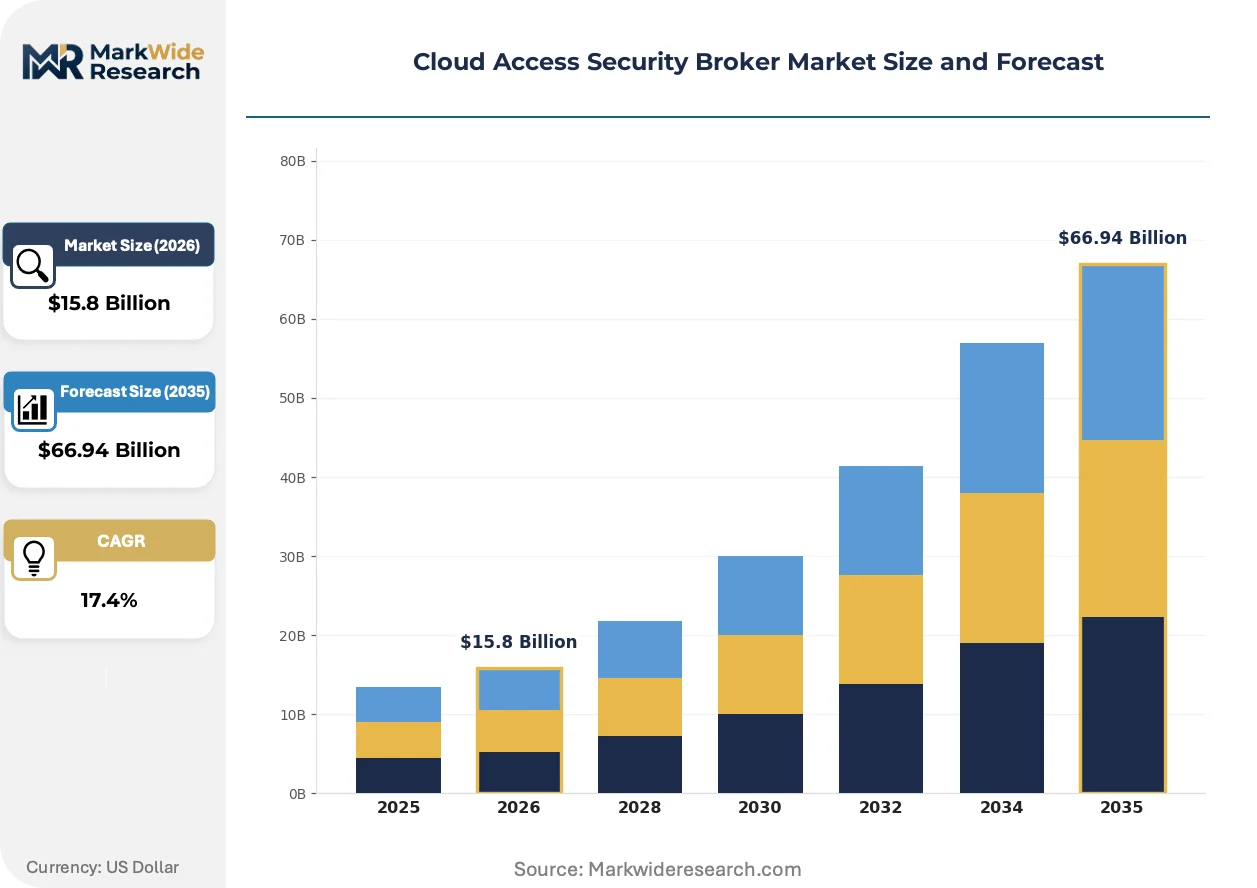
| Market Size in 2026 | $15.8 Billion |
| Market Size in 2035 | $66.94 Billion |
| CAGR (2026 – 2036) | 17.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: Public Cloud, Private Cloud, Hybrid Cloud, Multi-Cloud Solution: Data Loss Prevention, Threat Protection, Compliance Management, Identity Management End User: Small Enterprises, Medium Enterprises, Large Enterprises, Government Agencies Service Type: Managed Services, Professional Services, Consulting Services, Technical Support |
| Companies Covered | Netskope, Zscaler, Palo Alto Networks, Broadcom, McAfee, Microsoft, Forcepoint, Cisco, Proofpoint, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cloud Access Security Broker Market Strategic Shifts & Innovations
Artificial intelligence is embedding into broker platforms to compress detection latency and reduce manual policy maintenance overhead across distributed cloud footprints.
Machine learning-based data classification is automating sensitive data discovery across SaaS repositories. Financial services institutions deploy these engines to map unstructured data sprawl without predefined regex patterns. The technology is automating compliance workload reduction that previously required dedicated data steward teams.
NIST zero-trust architecture guidelines reshape federal procurement specifications for cloud security tooling. Contractors must demonstrate continuous verification capabilities rather than periodic access reviews. Defense and civilian agencies now embed these requirements into RFP technical evaluation criteria, filtering vendor pools before price competition begins.
Enterprise buyers now demand consumption-based licensing aligned with actual SaaS user counts rather than upfront perpetual seat purchases. Channel partners and direct sales teams must restructure compensation models around annual recurring revenue recognition. This shift concentrates in United States federal and financial services verticals where procurement modernization programs prioritize operational expenditure flexibility.
Cloud Access Security Broker Market Segmentation
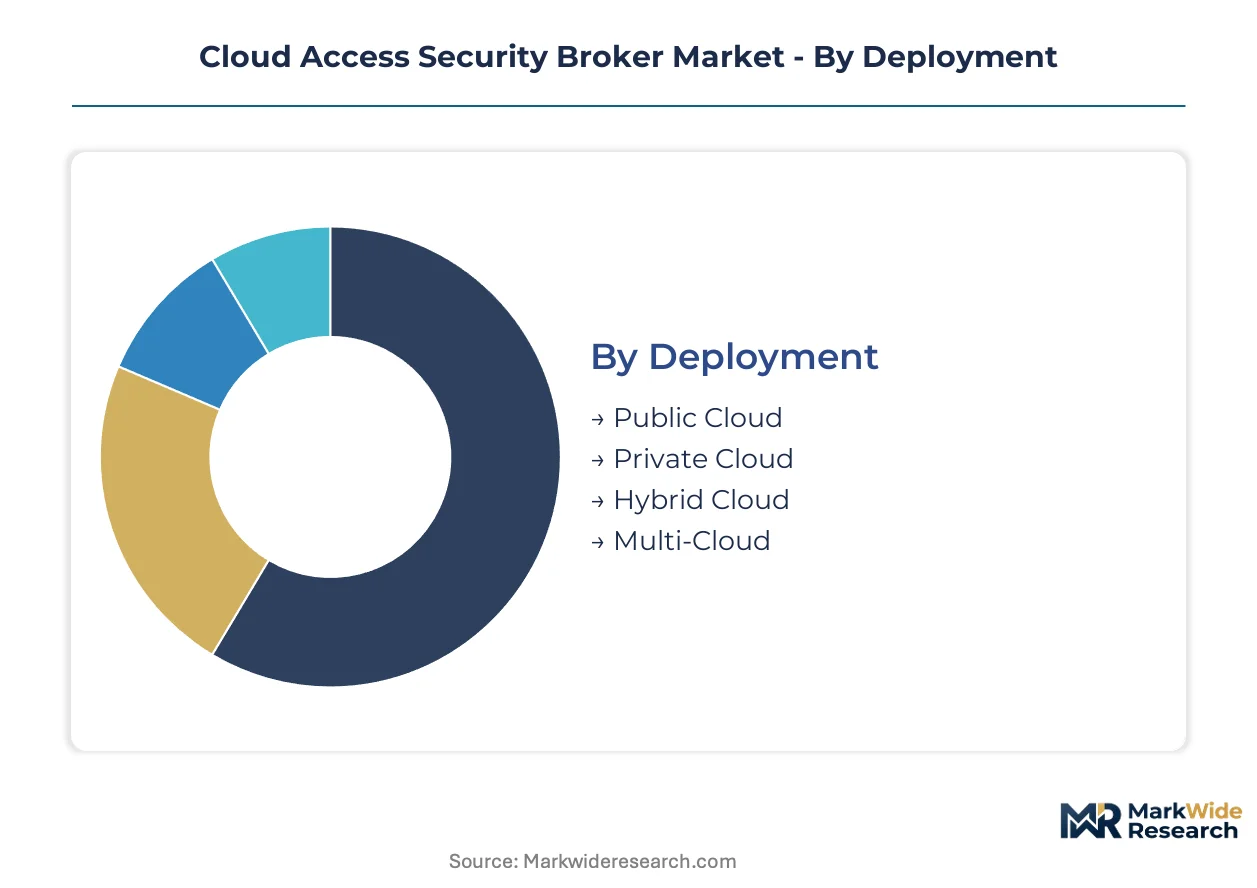
CASB procurement patterns diverge sharply by infrastructure maturity and regulatory exposure. Deployment architecture, solution capability, and service model choices reflect distinct risk appetites and compliance postures across buyer segments.
Deployment:
Customization intensity spans from standardized public cloud configurations to highly tailored multi-cloud orchestration stacks.
- Public Cloud:Single-tenant broker instances deployed within hyperscaler environments enable rapid policy activation without capital expenditure. Demand concentrates among mid-market enterprises in the United States seeking FedRAMP-authorized SaaS visibility without infrastructure ownership.
- Private Cloud:Dedicated broker appliances within customer-controlled data centers enforce policies for regulated workloads with data residency requirements. Financial services institutions in New York and Chicago deploy these for trading platform protection where cloud egress is restricted.
- Hybrid Cloud:Unified policy engines bridge on-premises identity systems with cloud-native proxies. The configuration demands API normalization across legacy Active Directory and modern OAuth providers, extending implementation timelines.
- Multi-Cloud:Broker platforms normalize controls across AWS, Azure, and Google Cloud environments simultaneously. Federal agencies pursuing cloud-agnostic strategies require these deployments to avoid vendor lock-in during multi-year modernization contracts.
Most installed capacity flows through Public Cloud deployments. Expansion is steepest in Multi-Cloud configurations.
Solution:
Capability layering follows a maturity curve from foundational data protection to identity-centric zero-trust enforcement.
- Data Loss Prevention:Content inspection engines apply regex, fingerprinting, and machine learning classification to block sensitive data exfiltration. Banks in California deploy these modules to automate CCPA compliance for customer records across unsanctioned SaaS uploads.
- Threat Protection:Inline malware scanning and sandboxing intercept malicious payloads before cloud repository ingestion. The capability commands premium pricing in federal contracts where NIST 800-207 zero-trust mandates require continuous traffic inspection.
- Compliance Management:Automated policy mapping against regulatory frameworks reduces audit preparation workload. Healthcare systems use these tools to maintain HIPAA documentation for cloud-hosted patient data.
- Identity Management:Contextual access decisions integrate user behavior analytics with device posture signals. The fastest-expanding capability layer as zero-trust architectures displace perimeter-based VPN models.
Threat Protection and Data Loss Prevention absorb the majority of current enterprise spending. Identity Management is climbing the fastest as organizations retrofit legacy access architectures.
End User:
Procurement sophistication scales with internal security team capacity and regulatory scrutiny intensity.
- Small Enterprises:Agentless browser-based inspection reduces deployment friction for organizations without dedicated cloud security architects. The segment favors consumption-based licensing aligned with actual SaaS user counts.
- Medium Enterprises:Hybrid deployment models balance cost control with compliance requirements. Manufacturing firms in Texas and Ohio select these configurations to protect intellectual property without full SASE transformation.
- Large Enterprises:Multi-module platforms with custom API development support complex policy orchestration across global SaaS portfolios. Integration debt with legacy identity providers extends implementation timelines.
- Government Agencies:FedRAMP High baseline authorization filters vendor pools before technical evaluation. Civilian and defense buyers embed NIST zero-trust requirements directly into RFP scoring criteria.
Large Enterprises command the deepest module engagement per account. Government Agencies are gaining share fastest as federal cloud migration timelines accelerate.
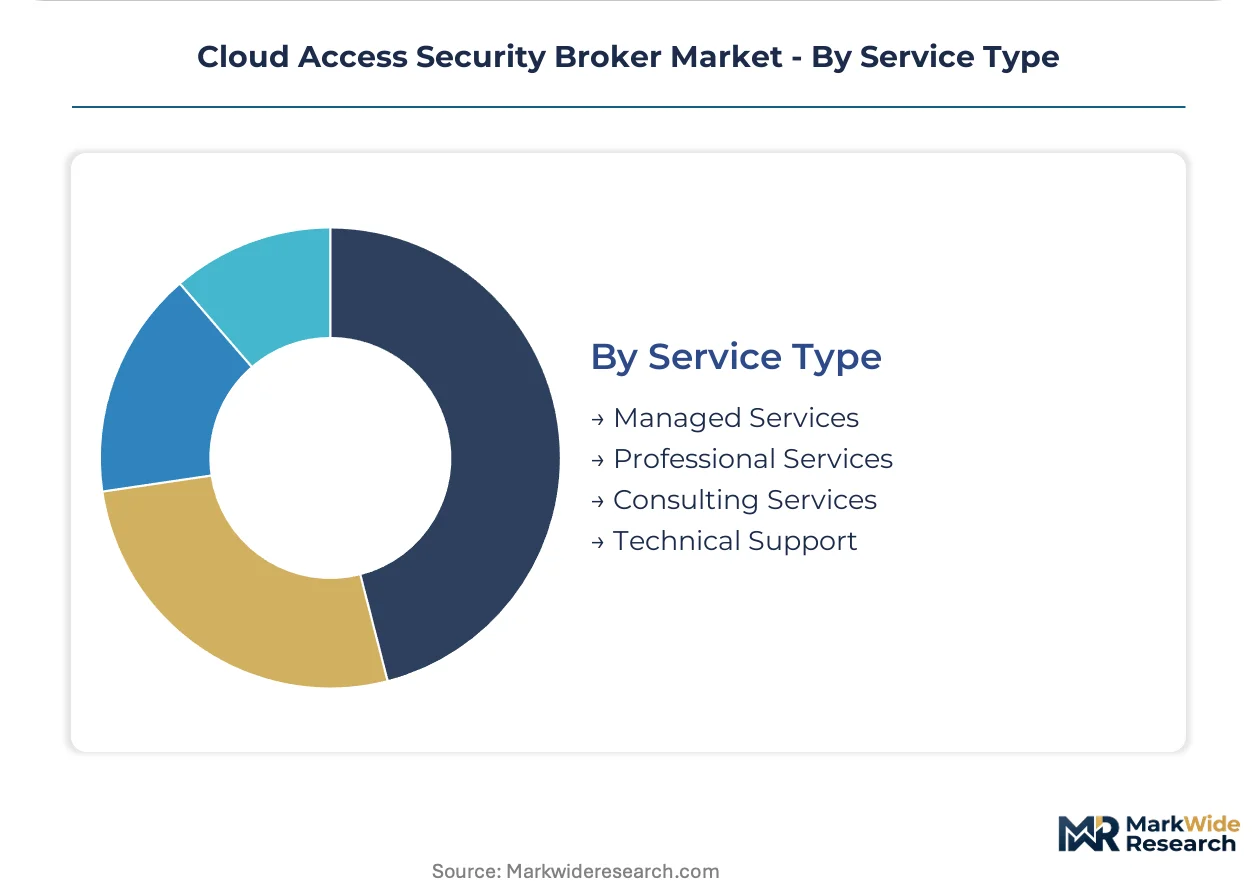
Service Type:
Value capture shifts from transactional support contracts to recurring managed detection relationships.
- Managed Services:Third-party analysts operate broker policies and investigate alerts on customer behalf. Financial services buyers in London and Singapore outsource certificate lifecycle management and false positive tuning to address skill shortages.
- Professional Services:Implementation architects configure API connectors and migrate legacy DLP rules. The segment peaks during initial deployment waves and contracts as self-service tooling matures.
- Consulting Services:Strategic advisors map zero-trust roadmaps and design multi-cloud governance frameworks. Demand surges preceding federal fiscal year procurement cycles.
- Technical Support:Break-fix resolution and patch management maintain platform availability. Standard inclusion in subscription tiers limits standalone revenue contribution.
Managed Services capture the highest recurring revenue per customer. Consulting Services show the steepest expansion trajectory as zero-trust mandates compress planning horizons.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
United States federal cloud migration timelines and FedRAMP compliance requirements anchor CASB demand concentration across North America, while financial services clusters in London and Singapore drive parallel procurement intensity.
United States
Federal agencies and Wall Street institutions dominate CASB procurement velocity. NIST zero-trust architecture guidelines reshape RFP technical evaluation criteria for defense and civilian buyers. New York financial services firms deploy multi-cloud broker platforms to normalize controls across AWS, Azure, and Google Cloud environments simultaneously.
United Kingdom
London-based financial institutions and government digital transformation programs accelerate broker adoption. The National Cyber Security Centre publishes cloud security guidance that elevates API-first inspection requirements in procurement specifications. The City of London cluster demands automated compliance management modules for GDPR and emerging UK data protection frameworks.
Germany
Automotive manufacturers and industrial conglomerates in Baden-Württemberg and Bavaria drive hybrid cloud broker deployments. The Federal Office for Information Security mandates strict data residency controls that favor private cloud broker appliances. Frankfurt financial services institutions integrate CASB platforms with legacy identity systems to bridge on-premises Active Directory with cloud-native proxies.
Japan
Tokyo metropolitan enterprises and Osaka manufacturing hubs pursue agentless deployment models to reduce implementation friction. METI digital transformation incentives accelerate SaaS migration among mid-market manufacturers. The Kanto region concentrates demand for threat protection modules as NIST-aligned zero-trust architectures displace perimeter-based VPN models.
Singapore
Regional headquarters of multinational banks and maritime trading firms generate concentrated CASB demand. The Monetary Authority of Singapore imposes technology risk management guidelines that elevate cloud data flow visibility requirements. The Marina Bay financial district outsources certificate lifecycle management and false positive tuning to managed service providers addressing skill shortages.
Cloud Access Security Broker Market Key Industry Players
Global majors compete with regional champions across cloud-native proxy architecture and SASE integration depth. Market structure tilts toward consolidated platform vendors with bundled networking-security portfolios rather than standalone broker specialists. Three archetypes dominate: cloud-native pure-plays with agentless velocity, platform conglomerates with SD-WAN convergence, and legacy security vendors retrofitting API connectors. Competitive moves concentrate on SASE portfolio bundling and consumption-based licensing restructuring.
Within the cloud-native pure-play tier, Netskope and Zscaler exemplify architectures decoupled from legacy hardware stacks. Palo Alto Networks occupies a position anchoring broker functionality within broader SASE platform integration. These three entities represent distinct strategic bets on deployment velocity versus ecosystem breadth versus networking convergence.
| Leading Market Players |
|---|
| Netskope |
| Zscaler |
| Palo Alto Networks |
| Broadcom |
| McAfee |
| Microsoft |
| Forcepoint |
| Cisco |
| Proofpoint |
| Others |
Cost & Logistics Intelligence
Backward integration into cloud-native proxy infrastructure anchors pricing power for vendors controlling both software development and hyperscaler compute allocation. SASE portfolio bundling by networking incumbents compresses standalone broker margins while consumption-based licensing reshapes revenue recognition across federal and financial services verticals.
Pricing Analysis
Input-cost pass-through from hyperscaler compute and API connector development shapes subscription tiering across the market. Three-tier pricing structure across premium, standard, and economy levels separates FedRAMP-authorized deployments with managed services from self-service mid-market configurations. Pricing pressure stems from SASE bundling by networking vendors offering broker functionality as loss-leader modules. Federal agencies show lowest price sensitivity due to compliance mandates, while mid-market manufacturers prioritize consumption-based flexibility.
Supply Chain Analysis
Direct-to-enterprise channels handle hyperscale buyer demand for customized multi-cloud orchestration, while channel partners serve mid-market velocity plays. Development concentrates in the United States, Israel, and Ireland where cloud security engineering talent clusters. Raw material dependencies include hyperscaler compute capacity, TLS certificate infrastructure, and machine learning training data. Single-source vulnerability runs through AWS, Azure, and Google Cloud API stability for connector maintenance. Distribution runs through systems integrators, managed security service providers, and direct vendor sales teams.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Margin expansion opportunities concentrate in managed services attach rates and premium-tier zero-trust modules, justified by skill shortages that prevent customer self-management of certificate lifecycle and policy tuning.
For Market Incumbents: To counter agentless deployment velocity by cloud-native pure-plays, incumbents must deepen API coverage breadth across SaaS application sprawl and integrate identity-centric enforcement directly into SASE portfolios. Channel control through managed service provider certification programs extends implementation leverage where customer skill gaps persist. For New Entrants and Emerging Players: Mid-market manufacturers in Japan and Germany represent underserved buyer archetypes seeking rapid time-to-value without dedicated cloud security architects. Browser-based inspection without endpoint software addresses deployment friction, while METI digital transformation incentives in Japan create procurement tailwinds for simplified onboarding. For Investors and Strategic Acquirers: Roll-up economics work for regional managed security service providers because federal cloud migration timelines compress planning horizons and create recurring revenue concentration. Acquisition targets should demonstrate FedRAMP authorization progress and zero-trust architecture consulting depth. The signal to watch is NIST guideline revision cycles that reshape RFP technical evaluation criteria.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | SASE architecture bundling reshapes go-to-market economics through networking vendor channels. |
| Acquisition of Specialist Firm | API connector boutiques address SaaS application sprawl outpacing organic development velocity. |
| Product Launch | Agentless browser-based inspection reduces friction for mid-market buyers without security architects. |
| Strategic Partnership | Hyperscaler alliances secure compute allocation and co-sell positioning for federal contracts. |
| Geographic Expansion | Tokyo and Frankfurt hubs address data residency mandates in Japan and Germany. |
Research Approach
Coverage spans North America, Europe, and Asia-Pacific, with primary inputs from each region combining interviews with CISOs, cloud security architects, federal procurement officers, and managed service provider executives alongside secondary validation. SEC filings, FedRAMP authorization databases, hyperscaler capex disclosures, and NIST guideline publications anchor quantitative triangulation. Bottom-up deployment modeling and top-down regulatory mandate sizing cross-validate segment estimates.
Rate-of-change decomposition separates zero-trust mandate velocity, SaaS application sprawl, and federal cloud migration timelines across the analysis window. Segmentation dimensions include deployment architecture, solution capability layering, organization size tier, and regional regulatory cluster. CAGRs derive from policy activation velocity curves and module attach rate progression. Forecast inputs incorporate NIST 800-207 adoption timelines and FedRAMP authorization pipeline data.
Underlying measurement precision varies by segment; federal and financial services verticals carry tighter precision due to procurement transparency requirements than mid-market manufacturing. Forecasts reflect assumptions about zero-trust architecture mandate continuity and hyperscaler API stability. Periodic stress-testing of base assumptions is recommended against regulatory revision cycles and cloud provider pricing volatility.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
New Zealand Cybersecurity Market
Cybersecurity
United Kingdom Ransomware Protection Market
Cybersecurity
Next-Generation Firewall Market
Cybersecurity
Cloud Security in Banking Market
Cybersecurity
China Cybersecurity Market
Cybersecurity
Asia-Pacific Cloud DLP Market
Cybersecurity
Spear Phishing Solution Market
Cybersecurity
IoT Security Market
Cybersecurity
E-Mail Security Market
Cybersecurity
Post-Quantum Cryptography Market
Cybersecurity
Web Application Firewall Market
Cybersecurity
Global Ddos Protection Market
Cybersecurity
France Cybersecurity Market
Cybersecurity
Global Patch Management Market
Cybersecurity
Global API Security Market
Cybersecurity
AI in Cybersecurity Market