
 Asia-Pacific Extended Detection and Response Market | 2026-2036
Asia-Pacific Extended Detection and Response Market Size, Share, and Industry Trends Forecast 2026-2036
Asia-Pacific Extended Detection and Response Market Insights
Australia's Security of Critical Infrastructure Act is shifting procurement priorities toward integrated threat-detection platforms across energy and telecommunications operators. Palo Alto Networks leverages its Cortex XDR architecture to anchor enterprise deployments across Sydney and Melbourne financial districts. Microsoft Corp sustains competitive pressure through native Azure Sentinel integration with Microsoft Defender for Endpoint. CrowdStrike Inc dominates in managed detection and response services for mid-market enterprises seeking cloud-native telemetry consolidation.
Extended Detection and Response fuses endpoint, network, and cloud telemetry into unified analytics engines that correlate alerts across attack surfaces in real time. The architecture ingests telemetry from firewalls, identity systems, and SaaS applications to reduce mean-time-to-detect below fifteen minutes for advanced persistent threats. Cloud deployment models lead adoption momentum as Australian and Japanese enterprises migrate security operations to distributed architectures with elastic compute scaling. Managed services represent the fastest-expanding segment as skills shortages in Singapore and South Korea drive outsourcing of tier-one and tier-two security operations to specialized providers.
Australia's APRA enforces CPS 234 prudential standards mandating capability to detect and respond to information security incidents within seventy-two hours. Japan's METI coordinates cybersecurity guidelines through JPCERT/CC that shape vendor certification requirements for critical infrastructure operators. Singapore's Cyber Security Agency administers the Cybersecurity Act licensing framework that gates market access for managed security service providers. Stakeholders must monitor divergence between national incident-reporting timelines and cross-border data-localization mandates that complicate regional platform architecture decisions.
Market Dynamics
Japan's METI cybersecurity guidelines and Australia's APRA CPS 234 prudential standards are compressing incident-response timelines, forcing enterprises to abandon siloed security tools for unified telemetry platforms that correlate endpoint, network, and cloud data in real time.
Growth Catalysts
- APRA CPS 234 Mandate:Australian prudential standards require financial institutions to detect and respond to security incidents within seventy-two hours, accelerating procurement of integrated XDR platforms across banking and superannuation sectors.
- Japan Critical Infrastructure:METI-coordinated guidelines through JPCERT/CC shape vendor certification requirements for energy and telecommunications operators, creating regulated demand for managed detection and response services.
- Cloud Migration Velocity:Australian and Japanese enterprises migrating security operations to distributed architectures with elastic compute scaling favor cloud-native XDR deployment models over on-premises alternatives.
Market Restraints
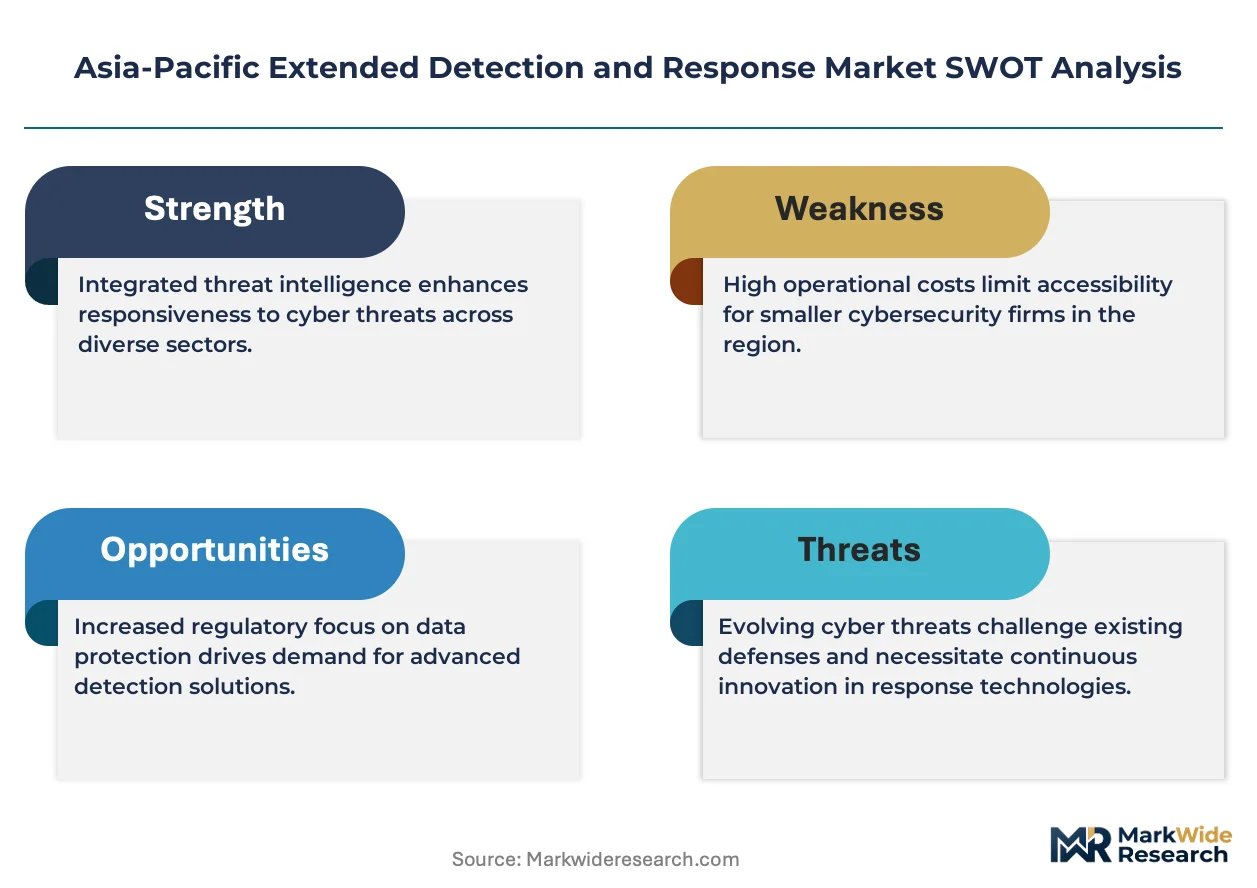
- Skills Concentration Risk:Singapore and South Korea face acute shortages of tier-one and tier-two security analysts, forcing enterprises to outsource operations and increasing dependency on managed service providers.
- Data Localization Friction:Divergent national incident-reporting timelines and cross-border data-localization mandates complicate regional platform architecture decisions for vendors operating across multiple jurisdictions.
- Integration Technical Debt:Legacy SIEM investments in established Australian financial institutions create path dependency, slowing full-stack XDR adoption despite regulatory pressure.
Strategic Opportunities
- South Korea Enterprise Gap:Mid-market manufacturers and chaebol subsidiaries remain underpenetrated by native XDR offerings, presenting whitespace for localized managed security service entry.
- AI-Native Correlation Convergence:Machine learning telemetry analysis combined with automated response orchestration enables fifteen-minute mean-time-to-detect for advanced persistent threats, differentiating next-generation platforms.
- Singapore MSSP Licensing:Cyber Security Agency's Cybersecurity Act licensing framework gates market access, creating regulatory moats for certified providers serving ASEAN hub operations.
Industry Challenges
- Multi-Cloud Telemetry Fragmentation:Enterprises operating across AWS, Azure, and Google Cloud environments struggle to normalize alert formats and correlation rules, extending deployment timelines.
- Certification Bottleneck:JPCERT/CC and CSA certification requirements for critical infrastructure operators create twelve-to-eighteen month vendor qualification cycles, compressing sales velocity.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Asia-Pacific Extended Detection and Response Market |
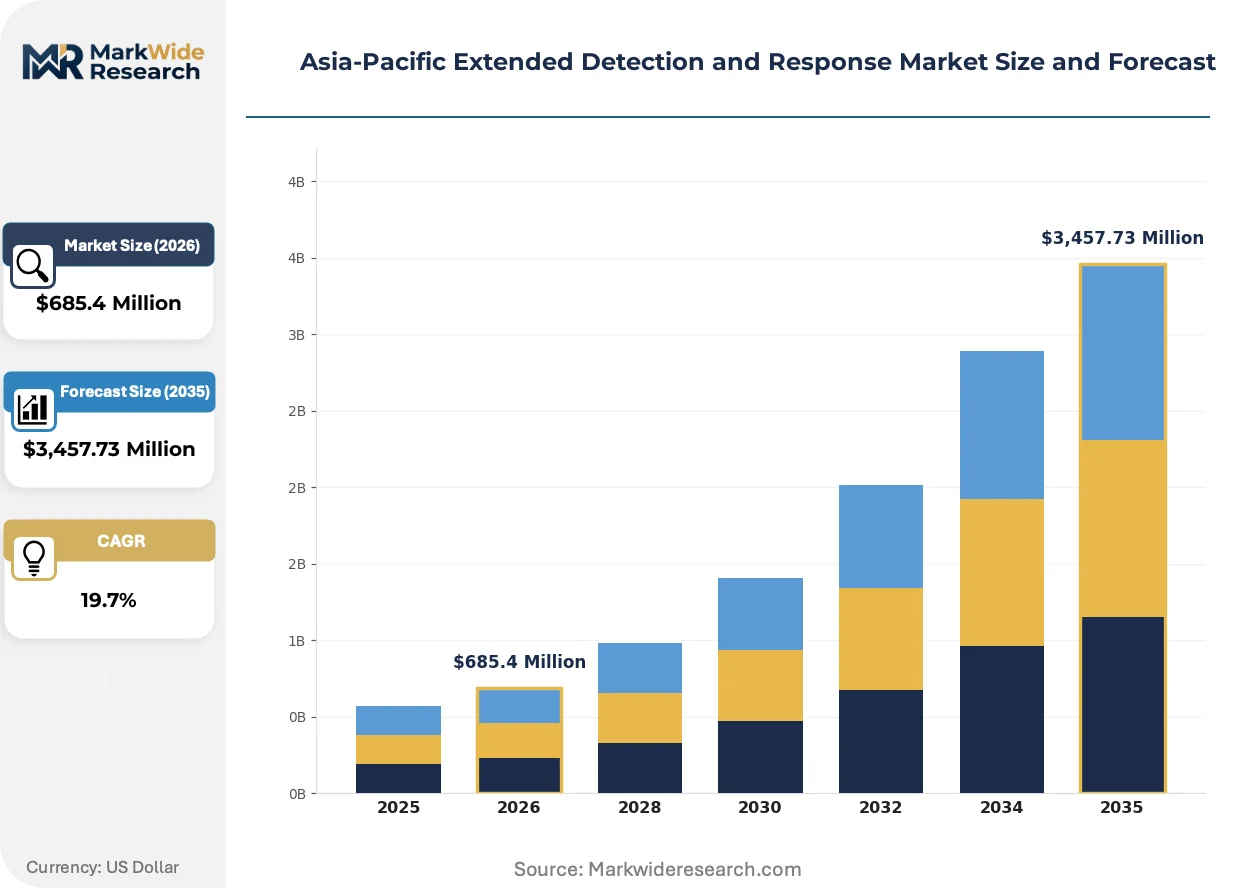
| Market Size in 2026 | $685.4 Million |
| Market Size in 2035 | $3,457.73 Million |
| CAGR (2026 – 2036) | 19.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Threat Intelligence, Endpoint Detection, Network Security, Security Information Management Deployment Model: Cloud, On-Premises, Hybrid, Managed Services End User: SMBs, Healthcare Sector, Financial Institutions, Government Agencies Organization Size: Small Enterprises, Medium Enterprises, Large Businesses, Corporates |
| Companies Covered | Palo Alto Networks Inc, Microsoft Corp, Cisco Systems Inc, Fortinet Inc, Broadcom Inc, Check Point Software Technologies Ltd, Sophos Ltd, Cybereason Inc, CrowdStrike Inc, Others |
| Regions Covered | Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Asia-Pacific Extended Detection and Response Market Trends and Innovations
Security operations centers across the Asia-Pacific are abandoning reactive alert triage for predictive threat hunting, driven by ransomware campaign sophistication and regulatory penalty structures that monetize response latency.
Autonomous XDR engines that ingest firewall, identity, and SaaS telemetry without human-tuned correlation rules are rewriting how Australian banks and Japanese insurers architect security operations. Sydney and Melbourne financial districts are deploying these platforms at eighteen-month refresh cycles, compressing the traditional three-year SIEM replacement timeline and enabling real-time attack surface visibility that static rule-based systems cannot match.
Singapore's Cyber Security Agency has tightened licensing requirements for managed security service providers under its Cybersecurity Act framework, mandating incident-response capabilities that exceed previous voluntary standards. This regulatory elevation is disqualifying uncertified regional competitors while creating procurement preference for providers with in-country Security Operations Centers, reshaping competitive dynamics for ASEAN enterprise contracts.
Mid-market enterprises in South Korea and Australia are unbundling tier-one monitoring from tier-two investigation and tier-three response, purchasing these functions from separate vendors rather than single-stack providers. This service decomposition is fragmenting procurement budgets across multiple contracts and favoring specialized managed detection and response vendors over platform-integrated offerings, particularly in manufacturing and logistics verticals where capital constraints limit full-platform commitments.
Asia-Pacific Extended Detection and Response Market Segmentation
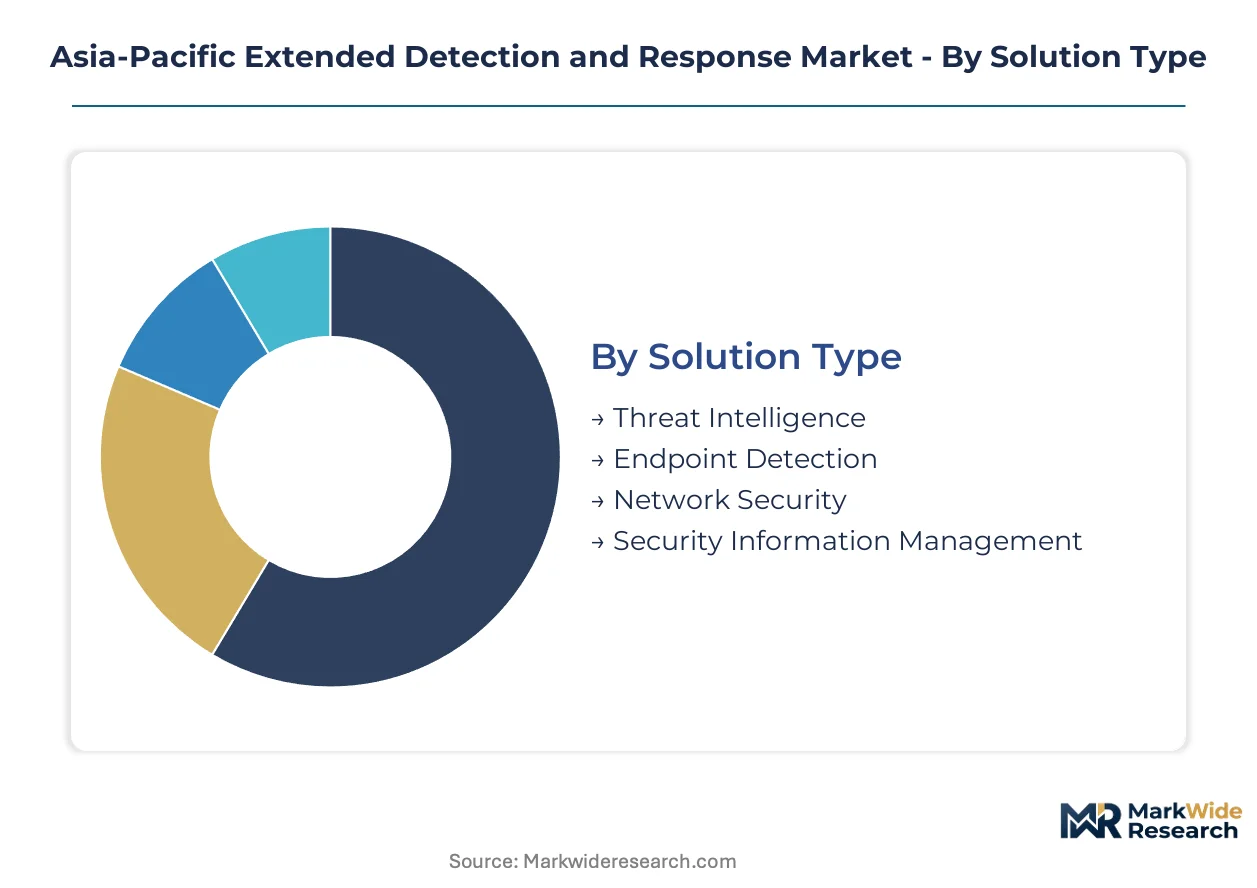
Technology refresh cycles across Asia-Pacific financial centers are compressing from thirty-six to eighteen months as regulatory mandates force unified platform replacements. Segmentation reveals how procurement budgets fragment across solution architectures, deployment preferences, and organizational tiers with distinct capability requirements.
Solution Type:
Platform consolidation decisions hinge on telemetry breadth and correlation engine sophistication as enterprises retire legacy point solutions.
- Threat Intelligence:Aggregates adversary indicators, attack patterns, and vulnerability disclosures into predictive risk scoring. Australian banks and Japanese insurers prioritize this capability for proactive hunt operations against ransomware affiliates targeting critical infrastructure.
- Endpoint Detection:Deploys lightweight agents capturing process execution, file system modifications, and behavioral anomalies across workstations and servers. Singaporean healthcare networks and South Korean manufacturing plants drive volume here as remote workforce expansion extends the attack surface.
- Network Security:Inspects north-south and east-west traffic flows for lateral movement signatures and data exfiltration patterns.
- Security Information Management:Normalizes log formats from disparate security tools into queryable data lakes for compliance reporting and forensic reconstruction.
Volume placements concentrate in Endpoint Detection; the faster expansion belongs to Threat Intelligence.
Deployment Model:
Cost tier differentiation separates capital-constrained mid-market buyers from enterprises seeking operational expenditure predictability.
- Cloud:Delivers elastic compute scaling for telemetry ingestion and machine learning model training without infrastructure ownership. Australian superannuation funds and Japanese telecommunications operators favor this model for distributed security operations center architectures.
- Managed Services:Outsources tier-one monitoring, tier-two investigation, and tier-three response to specialized providers with certified analyst benches. Singapore's Cyber Security Agency licensing requirements and South Korea's skills shortage accelerate procurement here.
- On-Premises:Retains data sovereignty and sub-millisecond query latency for air-gapped environments in defense and classified government facilities.
- Hybrid:Combines cloud analytics engines with on-premises data collectors to satisfy data-localization mandates while leveraging elastic processing.
Volume placements concentrate in Cloud; the steepest expansion trajectory belongs to Managed Services.
End User:
Application-specific compliance obligations shape feature prioritization and integration depth requirements across vertical sectors.
- Financial Institutions:Australia's APRA CPS 234 and Japan's FSA guidelines mandate seventy-two-hour incident detection and response capabilities. Banking and insurance procurement emphasizes automated playbooks, audit trail completeness, and cross-border data governance controls.
- Government Agencies:National security classifications and critical infrastructure designations require sovereign cloud deployments, supply chain attestation, and vendor personnel security clearances.
- SMBs:Limited security operations staffing drives preference for consolidated platforms with managed service overlays rather than self-operated toolchains.
- Healthcare Sector:Patient data protection regulations and medical device connectivity risks create demand for IoT-aware detection and clinical workflow preservation.
Volume placements concentrate in Financial Institutions; the fastest share gain belongs to Government Agencies.
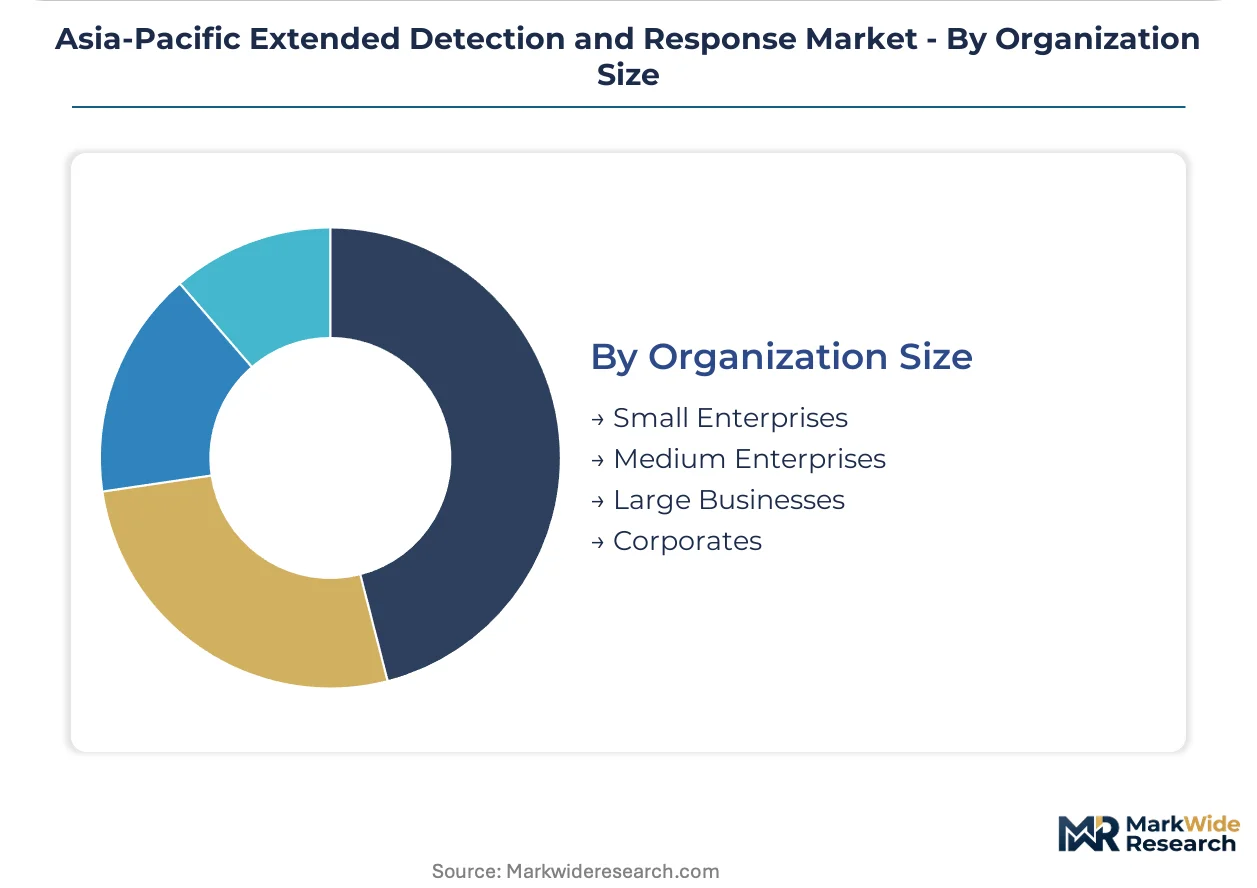
Organization Size:
Customer type segmentation reflects divergent procurement authority, integration complexity tolerance, and vendor relationship models.
- Large Businesses:Maintain dedicated security operations centers with fifty-plus analysts requiring open APIs, custom detection rule authoring, and multi-tenant platform administration. Australian mining conglomerates and Japanese automotive manufacturers exemplify this profile.
- Corporates:Multi-divisional enterprises with federated IT governance need centralized visibility with delegated response autonomy across subsidiaries.
- Medium Enterprises:Ten-to-fifty person IT departments seek pre-integrated platforms reducing deployment friction and training overhead.
- Small Enterprises:Outsource security operations entirely, purchasing outcomes rather than technology licenses through managed detection and response contracts.
Volume placements concentrate in Large Businesses; the most rapid scaling belongs to Medium Enterprises.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Sydney and Melbourne financial districts anchor Asia-Pacific XDR procurement, with banking and superannuation sectors driving platform consolidation under compressed eighteen-month refresh cycles.
Australia
APRA's CPS 234 prudential standards mandate seventy-two-hour incident detection and response capabilities across banking and superannuation sectors. The Security of Critical Infrastructure Act tightens mandatory reporting timelines for energy and telecommunications operators. Sydney's financial district and Melbourne's technology corridor concentrate enterprise deployments as institutions retire legacy SIEM investments.
Japan
METI coordinates cybersecurity guidelines through JPCERT/CC that shape vendor certification requirements for critical infrastructure operators. The updated national cybersecurity framework compresses incident-response timelines for energy and telecommunications sectors. Tokyo and Osaka metropolitan areas dominate procurement as insurers and automotive manufacturers migrate security operations to distributed cloud architectures.
Singapore
The Cyber Security Agency administers the Cybersecurity Act licensing framework that gates market access for managed security service providers. Skills shortages in tier-one and tier-two security analysis accelerate outsourcing demand. The city-state's enterprise hub operations and ASEAN regional headquarters concentrate procurement preference for providers with in-country Security Operations Centers.
South Korea
Acute shortages of certified security analysts force enterprises to outsource tier-one monitoring and tier-two investigation functions. Mid-market manufacturers and chaebol subsidiaries remain underpenetrated by native XDR offerings. Seoul Capital Area and Busan-Ulsan industrial corridors present whitespace for localized managed security service entry.
India
RBI cybersecurity guidelines and SEBI market infrastructure regulations shape procurement requirements for financial institutions. The country's technology services sector drives demand for cloud-native telemetry consolidation platforms. Mumbai's financial district and Bangalore's technology corridor concentrate enterprise deployments as institutions build distributed security operations center architectures.
Asia-Pacific Extended Detection and Response Market Competitive Landscape
The competitive structure tilts toward platform-integrated specialists with native cloud telemetry capabilities. Vendor concentration remains moderate, with established network security incumbents competing against endpoint-native challengers and cloud-hyperscale entrants. Three archetypes dominate: full-stack platform providers with unified analytics engines, managed detection and response specialists with certified analyst benches, and cloud-native entrants leveraging hyperscale infrastructure. Competitive intensity centers on M&A activity consolidating adjacent security capabilities and strategic partnerships embedding XDR modules into broader IT service contracts.
Within the platform-integrated tier, Palo Alto Networks and Microsoft Corp exemplify divergent architectural approaches to telemetry unification. CrowdStrike Inc occupies a position representing the managed detection and response specialist archetype, anchoring competitive dynamics for mid-market enterprises seeking cloud-native consolidation without internal security operations center investment.
| Leading Market Players |
|---|
| Palo Alto Networks Inc |
| Microsoft Corp |
| Cisco Systems Inc |
| Fortinet Inc |
| Broadcom Inc |
| Check Point Software Technologies Ltd |
| Sophos Ltd |
| Cybereason Inc |
| CrowdStrike Inc |
| Others |
Pricing and Supply Chain Analysis
APRA's CPS 234 seventy-two-hour incident-response mandate is compressing procurement cycles across Australian banking and superannuation sectors, forcing vendors to absorb certification and localization costs that reshape margin structures across the Asia-Pacific XDR landscape.
Pricing Analysis
Outcome-based pricing tied to mean-time-to-detect guarantees anchors enterprise contracts across Sydney and Melbourne financial districts. Subscription tiers stratify across cloud-native deployment, managed service overlay, and hybrid integration levels, with APRA-regulated institutions showing lowest price sensitivity due to penalty exposure. Cost compression in mid-market managed services intensifies as Singapore's Cyber Security Agency licensing requirements raise compliance overhead. Small enterprises outsourcing tier-one through tier-three functions exhibit highest price sensitivity, favoring per-endpoint pricing over platform-wide commitments.
Supply Chain Analysis
Dual-sourcing requirements from Australian critical infrastructure operators and Japanese METI-certified vendors mandate multi-cloud telemetry partnerships, fragmenting vendor concentration across AWS, Azure, and Google Cloud environments. Core analytics engines draw from semiconductor fabrication in Taiwan, software development talent pools in India, and data center infrastructure in Singapore. Single-source vulnerability in cloud hyperscaler dependencies creates concentration risk for regional platform architectures. Distribution runs through certified managed security service providers with in-country Security Operations Centers, particularly in Singapore and South Korea where regulatory licensing gates market access.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Asia-Pacific XDR competitive dynamics favor consolidation plays as regulatory certification requirements and compressed refresh cycles squeeze sub-scale vendors unable to sustain multi-jurisdiction compliance investments.
For Market Incumbents: Deploy native AI correlation engines to differentiate against point-solution challengers lacking unified telemetry breadth. Anchor enterprise relationships through APRA CPS 234 and JPCERT/CC certification investments that create twelve-to-eighteen month qualification moats. Acquire tier-two managed detection specialists in South Korea and Singapore to capture outsourcing demand from skills-constrained mid-market enterprises.
For New Entrants and Emerging Players: Capture whitespace in South Korean manufacturing and chaebol subsidiaries where native XDR penetration remains limited. Target Australian healthcare and logistics verticals with decomposed service offerings separating tier-one monitoring from tier-three response. Enter through localized managed security service partnerships rather than direct platform sales to bypass capital-intensive certification cycles.
For Investors and Strategic Acquirers: The window for entry favors managed detection specialists with certified analyst benches and established Cyber Security Agency licensing. Long-term viability rests on cloud-native architecture and multi-cloud telemetry normalization capabilities. Watch for divergence between national data-localization mandates and cross-border incident-response requirements as the signal for platform architecture inflection.
| Strategic Initiative | Industry Significance |
|---|---|
| JPCERT/CC Certification Investment | Twelve-to-eighteen month qualification cycles compress sales velocity for uncertified competitors in Japan. |
| Managed Detection Service Launch | Singapore's Cyber Security Agency licensing creates regulatory moats for ASEAN hub operations. |
| Multi-Cloud Telemetry Integration | AWS-Azure-Google Cloud normalization addresses fragmentation pain points extending enterprise deployment timelines. |
| AI-Native Correlation Engine Development | Fifteen-minute mean-time-to-detect capabilities differentiate next-generation platforms in Australian banking procurement. |
| Regional SOC Partnership | In-country Security Operations Centers satisfy Singapore's Cybersecurity Act licensing requirements for managed service providers. |
Research Methodology
Document review covered regulatory filings from APRA, METI, and Singapore's Cyber Security Agency, complemented by interviews with chief information security officers at Australian banking and superannuation institutions, managed security service provider executives in Singapore and South Korea, and platform engineering leads at Japanese telecommunications operators. Secondary validation drew from JPCERT/CC certification databases, Cyber Security Agency licensing registries, and hyperscaler security service disclosures. Bottom-up deployment estimates triangulated against top-down addressable market calculations across the analysis window.
Historical refresh cycle compression patterns cross-referenced against panel input from procurement officers at financial institutions and critical infrastructure operators. Segmentation modeling incorporated solution type, deployment model, end-user vertical, and organization size dimensions. CAGRs derived from elasticity-adjusted adoption curves reflecting regulatory mandate enforcement timelines and cloud migration velocity across Australian and Japanese enterprises.
Forecast confidence holds firmest in the near-window; longer-horizon outcomes carry greater sensitivity to divergence between national data-localization mandates and cross-border incident-response timeline requirements. Deviation in METI cybersecurity guideline updates or APRA CPS 234 enforcement intensity would shift the outlook materially.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Ultra-Secure Smartphone Market
Security Software
Mobile Data Protection Solutions and Services Market
Security Software
Risk-Based Authentication (RBA) Market
Security Software
Facial Recognition Market
Security Software
Parental Monitoring Software Market
Security Software
Asia Pacific Anti Money Laundering Solutions Market
Security Software
Global Secure Access Service Edge Market
Security Software
Asia-Pacific Fraud Detection & Prevention Market
Security Software
Global Security Software in Telecom Market
Security Software
Identity and Access Management (IAM) Market
Security Software
Antivirus Software Package Market
Security Software
Phone Antivirus Software Market
Security Software
Encryption Software Market
Security Software
Network Camera and Video Analytics Market
Security Software
Saudi Arabia Managed Security Services Market
Security Software
Sound Masking Systems Market