
 POS Security Market | 2026-2036
POS Security Market Size, Share, and Industry Trends Forecast 2026-2036
POS Security Market Analysis
The EU AI Act is realigning how payment terminal vendors engineer automated threat-detection modules. Shift4 leverages its integrated software-hardware stack to sustain compliance velocity across European merchant portfolios. Verifone anchors its competitive stance through dedicated R&D labs focused on biometric authentication firmware. Ingenico competes aggressively on channel control, dominating direct distribution networks across Tier-1 retail banks in France and Italy.
POS security encompasses hardware modules, software protocols, and managed services that encrypt, tokenize, or biometrically authenticate payment card data at the physical point of transaction, typically processing transactions within sub-200-millisecond latency windows to avoid checkout friction. Its primary commercial purpose is to neutralize card-present fraud, malware injection, and skimming attacks while preserving transaction throughput. Hardware-based encryption appliances still occupy the largest margin pool among product categories, though cloud-based deployment architectures are attracting the fastest-growing share of new enterprise contracts. Biometric technology segments lead innovation velocity as retailers in hospitality and food service pilot palm-vein and facial-recognition checkout systems.
PCI Security Standards Council frameworks, GDPR through CNIL enforcement in France, and the EU AI Act collectively shape product certification requirements and liability exposure for terminal manufacturers. FDA has no direct role here, though healthcare end users must thread HIPAA obligations into their POS data architectures. Stakeholders must decide whether to build in-house tokenization engines or outsource to specialized providers as regulatory fragmentation between European and North American compliance regimes intensifies.
Market Dynamics
Cloud-based encryption architectures are compressing deployment timelines from months to weeks, forcing terminal manufacturers to restructure their service portfolios around recurring revenue models rather than hardware margins.
Growth Catalysts
- PCI DSS 4.0:The updated framework mandates stronger encryption-at-rest protocols, compelling retail chains to accelerate terminal refresh cycles across their estates.
- Palm-vein authentication:Food service operators in Japan and South Korea are piloting biometric checkout systems that eliminate PIN entry friction during peak hours.
- EMV liability shift:Fuel station operators across the United States face mounting fraud exposure, driving demand for outdoor-rated secure terminals with tamper-evident hardware.
Market Restraints
- Semiconductor supply concentration:Taiwan-based foundries control the bulk of secure element chip production, creating vulnerability in terminal manufacturing pipelines.
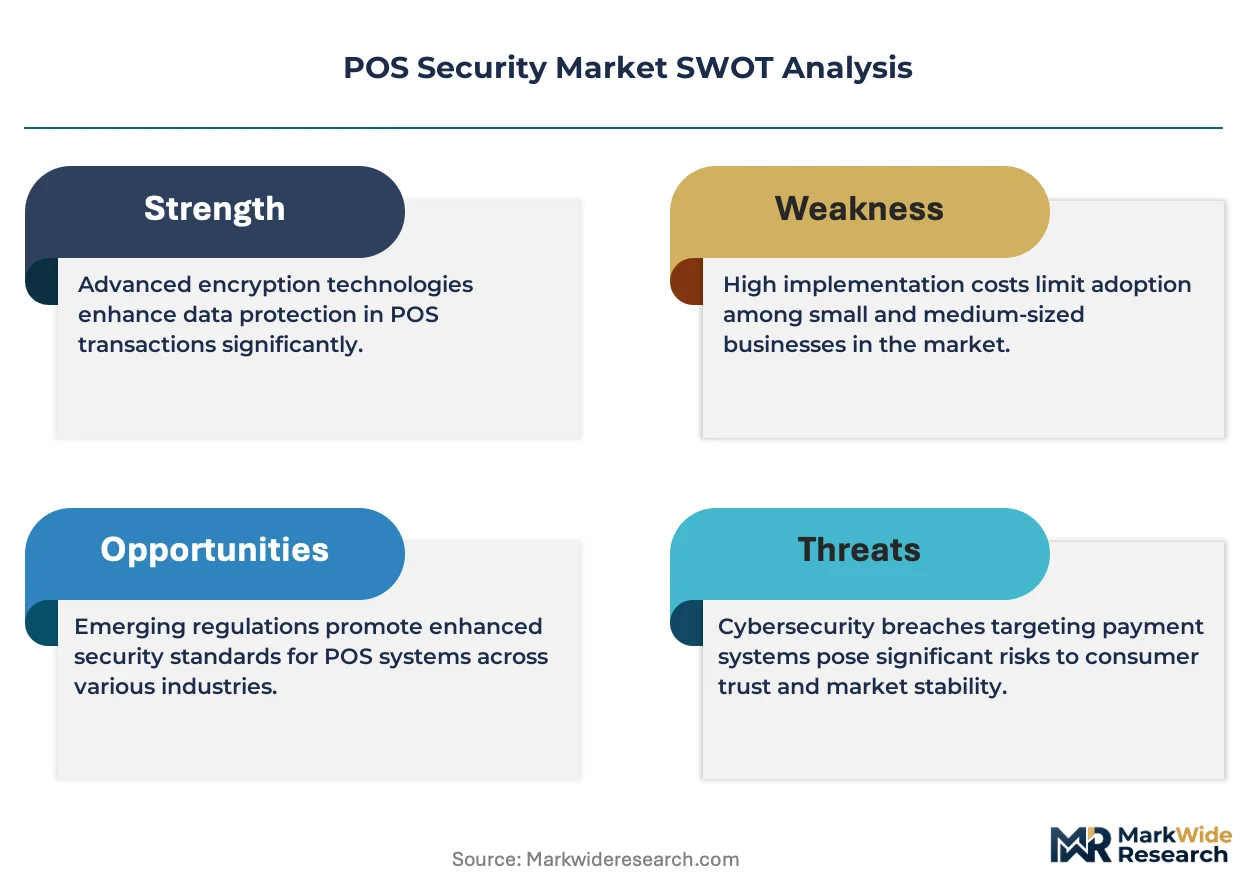
- EU AI Act compliance costs:Automated threat-detection modules now require algorithmic transparency documentation, adding six-figure certification burdens per product line.
- Mobile wallet substitution:Smartphone-based NFC payments reduce merchant reliance on dedicated POS terminals in low-ticket retail environments.
Strategic Opportunities
- India:The RBI's push for contactless transaction limits above the current threshold creates opening for biometric-integrated terminal deployments in Tier-2 cities.
- Healthcare-HPOS convergence:HIPAA-compliant payment terminals that integrate with electronic health record systems address a gap in hospital outpatient pharmacies.
- Subscription-based security monitoring:Managed detection and response services for terminal fleets represent underdeveloped recurring revenue streams for channel partners.
Industry Challenges
- Firmware signing key management:The complexity of secure boot architectures exceeds the capabilities of many regional system integrators, slowing deployment velocity.
- Legacy terminal obsolescence:End-of-life hardware running deprecated operating systems cannot receive security patches, forcing rip-and-replace decisions ahead of budget cycles.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | POS Security Market |
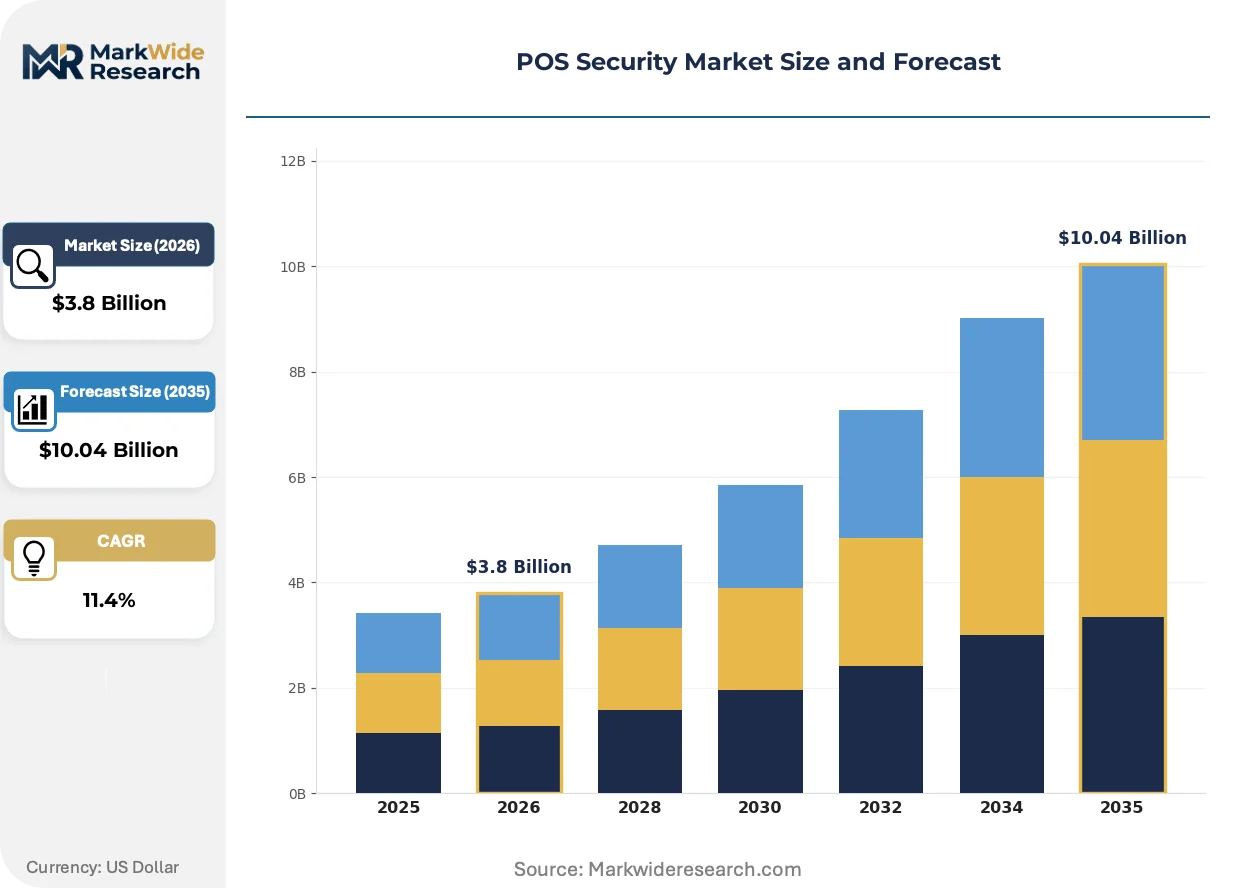
| Market Size in 2026 | $3.8 Billion |
| Market Size in 2035 | $10.04 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Hardware, Software, Services, Solutions End User: Retail, Hospitality, Healthcare, Food Service Deployment: On-premises, Cloud-based, Hybrid, Mobile Technology: Encryption, Tokenization, Biometrics, NFC |
| Companies Covered | Shift4, First Data, Verifone, Heartland Payment Systems, Elavon, Ingenico, Worldpay, Stripe, PAX Technology, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
POS Security Market Emerging Trajectories
Payment terminal architecture is fragmenting into composable software layers that decouple security functions from hardware, enabling faster certification cycles and vendor flexibility.
Point-to-point encryption is modularizing across the transaction stack. The technology encrypts card data at the moment of swipe or tap, rendering intercepted signals useless to attackers. Large hospitality chains are adopting this capability within eighteen-month refresh windows. This modularizing trend is compressing the traditional hardware-software bundling that locked merchants into single-vendor ecosystems.
The EU AI Act is reshaping how automated fraud detection systems gain market access. Algorithmic decision-making in payment terminals must now meet explainability standards and human oversight requirements. Biometric authentication modules face the strictest scrutiny, with France's CNIL already rejecting several palm-vein recognition submissions for inadequate data retention disclosures.
Merchant acquisition patterns are fragmenting as independent software vendors embed payment acceptance into vertical-specific platforms. Restaurant management systems now bundle pre-certified security modules, bypassing traditional terminal distributors. This disintermediation is most pronounced in the United States, where Square and Toast have captured substantial share from bank-led merchant service programs.
POS Security Market Segmentation
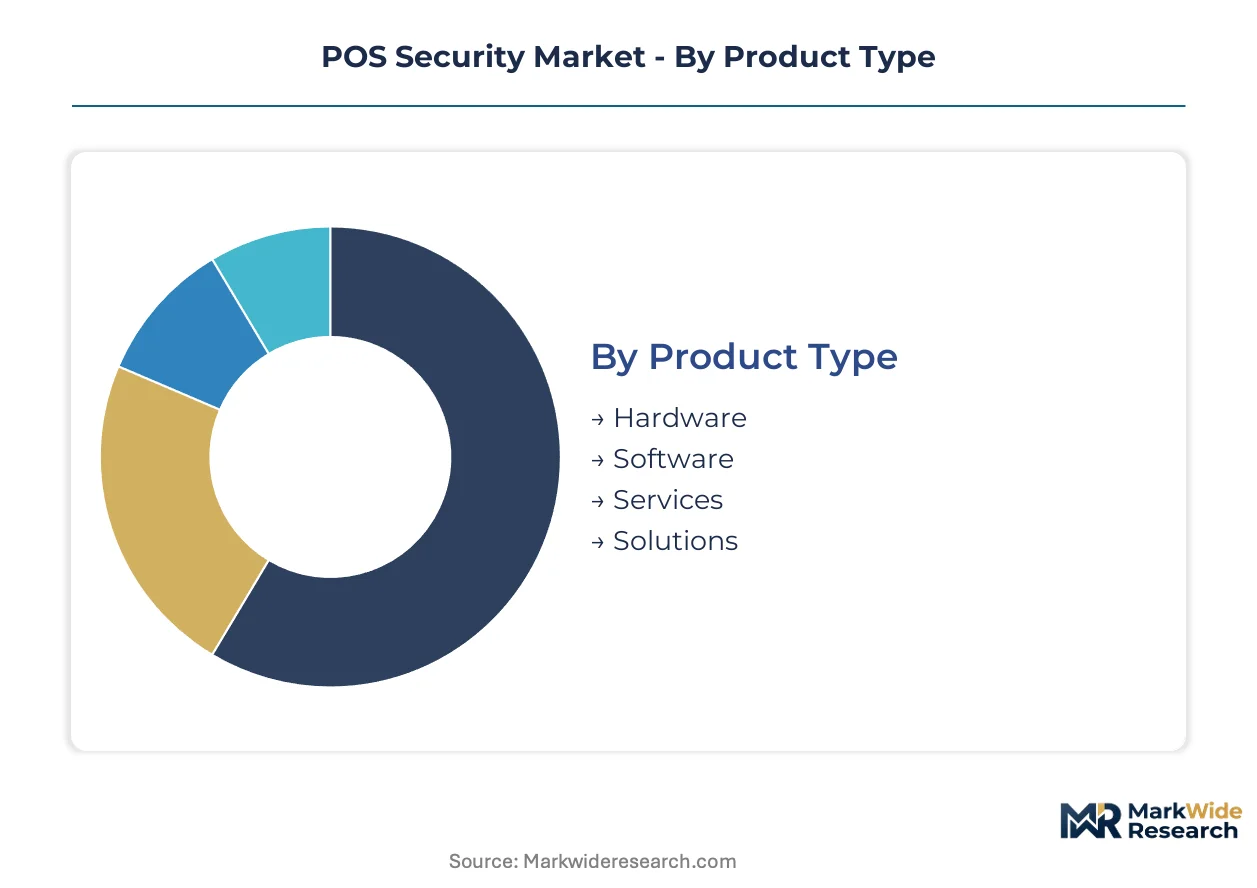
POS security procurement splits sharply between capital-intensive hardware refreshes and recurring software subscriptions. Understanding where buyers allocate budget across these four dimensions reveals which vendors capture margin versus volume.
Product Type:
Hardware commands the premium tier while services expand fastest through recurring revenue models.
- Hardware:Encryption appliances and secure element modules constitute the highest-margin product tier. Tier-1 retail chains in the United States and France prioritize tamper-evident terminal designs to satisfy PCI DSS 4.0 mandates for physical security attestation.
- Software:Firmware stacks for point-to-point encryption and tokenization engines run on merchant servers or terminal operating systems. Cloud-native architectures are displacing on-device codebases as hospitality operators demand faster patch cycles without hardware truck rolls.
- Services:Managed detection and response for terminal fleets, penetration testing, and compliance audit support.
- Solutions:Bundled hardware-software-service packages targeting specific vertical compliance requirements.
Today's leader: Hardware. Tomorrow's challenger: Software.
End User:
Application context dictates security architecture — retail demands throughput, healthcare demands data segregation.
- Retail:High-volume transaction environments including department stores, grocery chains, and specialty merchants. EMV-compliant terminal density is climbing fastest in fuel station forecourts across the United States as outdoor-rated secure hardware addresses liability shift exposure.
- Hospitality:Hotels and resorts require integrated property management system connectivity with PCI-compliant data flows. Biometric checkout pilots in Japanese and South Korean food service operations are validating palm-vein authentication for peak-hour throughput.
- Healthcare:Hospital outpatient pharmacies and clinic payment counters. HIPAA obligations thread through every terminal deployment, requiring encryption protocols that segregate payment data from electronic health record systems.
- Food Service:Quick-service restaurants and full-service dining. Pre-certified security modules embedded in restaurant management platforms are disintermediating traditional terminal distributors.
Retail absorbs the largest absolute spend. Healthcare offers the steepest expansion trajectory as compliance convergence creates premium pricing power.
Deployment:
Cloud architectures compress certification timelines while hybrid models preserve legacy infrastructure investments.
- On-premises:Terminal-resident encryption and local tokenization vaults. Regional banks in France and Italy maintain these configurations for direct control over cryptographic key ceremonies.
- Cloud-based:Encryption-as-a-service and centralized tokenization platforms. Deployment timelines have compressed from months to weeks, forcing manufacturers to restructure portfolios around recurring revenue.
- Hybrid:Edge encryption with cloud-based key management and policy orchestration.
- Mobile:Smartphone-based acceptance with software-based security modules.
Cloud-based deployments are gaining share fastest. Hybrid architectures dominate current installed bases.
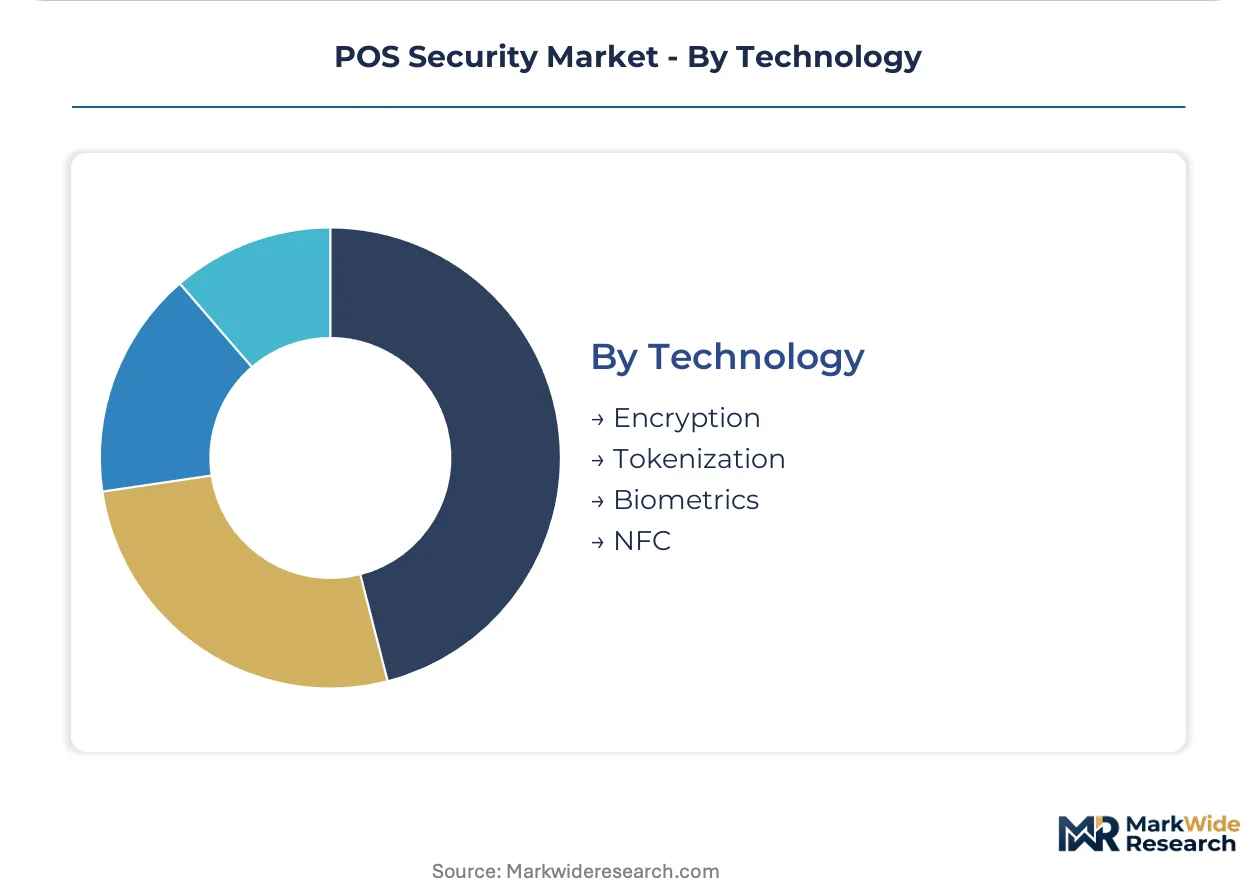
Technology:
Encryption anchors current spend while biometrics capture innovation investment.
- Encryption:Point-to-point and end-to-end protocols protecting data from card read to processor. Large hospitality chains in North America adopt these capabilities within accelerated refresh windows to neutralize interception risks.
- Tokenization:Vault-based and vaultless schemes replacing primary account numbers with surrogate values. Merchants must decide between in-house engines and specialized providers as regulatory fragmentation intensifies.
- Biometrics:Fingerprint, palm-vein, and facial recognition authentication. France's CNIL has already rejected several palm-vein submissions for inadequate data retention disclosures under GDPR and EU AI Act requirements.
- NFC:Contactless transaction security protocols and tap-to-pay acceptance infrastructure.
Encryption generates current revenue. Biometrics represents the frontier where compliance velocity determines market access.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The POS security industry traces its commercial roots to the United States, where early magnetic-stripe fraud drove the first encryption appliance deployments in the 1990s. EMV migration in Europe and Asia subsequently transferred technical leadership across the Atlantic and Pacific. Today, regulatory divergence between PCI DSS jurisdictions and EU AI Act mandates shapes where vendors prioritize certification investments.
United States
Fuel station operators face acute fraud exposure from EMV liability shifts, accelerating demand for outdoor-rated tamper-evident terminals. PCI DSS 4.0 mandates stronger encryption-at-rest protocols, compelling retail chains to compress refresh cycles. Atlanta and Dallas host dense clusters of payment processors integrating cloud-based encryption services into merchant portfolios.
France
Tier-1 retail banks in Paris and Lyon maintain direct distribution control over terminal networks, favoring on-premises cryptographic key ceremonies. CNIL enforces strict GDPR and EU AI Act compliance for biometric authentication modules, rejecting palm-vein submissions over data retention disclosures. The Île-de-France corridor concentrates vendor R&D facilities focused on algorithmic transparency documentation.
Germany
Automotive parts retailers and supermarket chains drive demand for hybrid deployment architectures preserving legacy infrastructure investments. The national data protection authority enforces stringent breach notification timelines affecting terminal fleet management. Munich and Frankfurt anchor engineering centers developing secure boot firmware for European market access.
Japan
Food service operators in Tokyo and Osaka pilot palm-vein biometric checkout systems to eliminate PIN friction during peak hours. METI promotes contactless transaction infrastructure upgrades through standardization initiatives. The Kanto region hosts terminal manufacturers integrating hospitality property management system connectivity with PCI-compliant data flows.
India
RBI's push to raise contactless transaction limits creates openings for biometric-integrated terminal deployments in Tier-2 cities. The central bank's tokenization guidelines force merchants to decide between in-house engines and specialized providers. Bangalore and Mumbai concentrate fintech development labs adapting cloud-native security architectures for domestic compliance requirements.
POS Security Market Vendor Landscape
Capital-heavy terminal manufacturers compete with asset-light encryption service providers across divergent margin structures. The vendor base splits between integrated hardware-software stacks and modular component suppliers. Three archetypes dominate: full-stack platform operators, specialized biometric firmware developers, and cloud-native encryption specialists. Competitive moves center on portfolio diversification into recurring revenue services and strategic partnerships with independent software vendors embedding payment acceptance into vertical platforms.
Within the full-stack tier, Shift4 and Verifone exemplify integrated platform strategies spanning hardware certification and compliance velocity management. Ingenico occupies a position emphasizing channel control through direct distribution relationships with major European retail banks. These three entities anchor distinct competitive vectors—software-hardware integration, biometric authentication R&D, and bank-centric distribution density—without exclusive claim to any single market segment.
| Leading Market Players |
|---|
| Shift4 |
| First Data |
| Verifone |
| Heartland Payment Systems |
| Elavon |
| Ingenico |
| Worldpay |
| Stripe |
| PAX Technology |
| Others |
Supply Flow & Price Mechanics
Private-equity-rolled-up encryption service providers anchor supply-side discipline through recurring revenue models that reshape terminal manufacturer pricing power across North America and Europe. Their portfolio consolidation compresses hardware margins while elevating subscription-based security monitoring as the value-capture mechanism.
Pricing Analysis
Three-tier pricing structure across premium, standard, and economy levels separates PCI DSS 4.0-certified terminals from legacy EMV-compliant hardware and unencrypted legacy estates. Certification grade and volume scale drive price differentiation, with Tier-1 retail chains commanding steepest discounts. Cost compression in economy tiers is intensifying because mobile wallet substitution erodes dedicated terminal demand in low-ticket environments. Fuel station operators show least price sensitivity due to EMV liability shift exposure, while independent restaurants exhibit highest sensitivity to upfront hardware costs.
Supply Chain Analysis
Dual-sourcing requirements for secure element chips mandate multi-supplier qualification across Taiwan, South Korea, and Japan to mitigate single-source vulnerability. Terminal manufacturing draws from Taiwan-based foundries for secure elements, Japanese component houses for biometric sensors, and German engineering centers for firmware development. Semiconductor supply concentration creates tariff exposure as geopolitical friction disrupts chip fabrication timelines. Distribution runs through direct bank-led merchant service programs in France and Italy, alongside ISV-embedded channels disintermediating traditional distributors in the United States.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The POS security market functions as a regulatory compounder where PCI DSS 4.0 mandates and EU AI Act compliance timelines perpetually refresh demand cycles across merchant estates.
For Market Incumbents: Deepen backward integration into secure element sourcing to offset Taiwan foundry concentration risk. Expand managed detection and response service attach rates to defend against cloud-native encryption specialists eroding hardware margins. Prioritize algorithmic transparency documentation investments to sustain EU AI Act certification velocity for biometric product lines.
For New Entrants and Emerging Players: Independent software vendors embedding payment acceptance represent the most penetrable channel archetype. Target healthcare-HPOS convergence in hospital outpatient pharmacies where HIPAA compliance creates premium pricing power and incumbent blind spots persist. Pursue white-label biometric firmware partnerships with Tier-2 terminal manufacturers lacking in-house R&D capabilities.
For Investors and Strategic Acquirers: Valuations sit cheapest among regional system integrators struggling with firmware signing key management complexity. Long-term viability favors subscription-revenue-heavy encryption service providers over capital-intensive hardware manufacturers. Watch RBI contactless limit adjustments and biometric-integrated terminal deployment signals in Indian Tier-2 cities as inflection indicators for emerging market expansion viability.
| Strategic Initiative | Industry Significance |
|---|---|
| Cloud-Native Encryption Service Launch | Compresses deployment timelines from months to weeks for hospitality chains. |
| Biometric Firmware Certification Investment | Secures EU AI Act market access ahead of CNIL enforcement deadlines. |
| ISV Partnership for Embedded Payment Modules | Captures share from bank-led merchant service programs in US food service. |
| Healthcare-HPOS Integration Development | Addresses HIPAA-compliant payment gaps in hospital outpatient pharmacies. |
| Managed Detection and Response Service Expansion | Builds recurring revenue streams from terminal fleet monitoring contracts. |
Methodological Framework
Coverage spans North America, Europe, and Asia-Pacific, with primary inputs from each region combining interviews with payment terminal manufacturers, merchant acquiring executives, and compliance audit specialists. Secondary validation draws from PCI Security Standards Council framework documentation, RBI tokenization guidelines, CNIL enforcement decisions, and SEC filings from publicly traded payment processors. Bottom-up terminal deployment estimates triangulate against top-down merchant acquiring revenue analysis.
Rate-of-change decomposition separates hardware refresh cycles from software subscription growth and services expansion across the projection horizon. Segmentation dimensions modeled include product type, end user vertical, deployment architecture, and technology category. CAGRs derive from weighted average of historical terminal replacement patterns and regulatory mandate compliance timelines. Industry-specific inputs incorporate EMV liability shift deadlines and EU AI Act certification burden estimates.
Forecast confidence holds firmest in the near-window; longer-horizon outcomes carry greater sensitivity to semiconductor supply disruption and mobile wallet substitution acceleration. Deviation in RBI contactless limit policy or CNIL biometric rejection patterns would shift the outlook materially.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Home Webcam Market
Security Software
Global Enterprise Key Management Market
Security Software
Ultra-Secure Smartphone Market
Security Software
Certification Authority Market
Security Software
Data Loss Prevention Market
Security Software
Spain Endpoint Detection and Response Market
Security Software
Global Electronic Offender Monitoring Solutions Market
Security Software
Global Hardware Security Modules (HSM) Market
Security Software
Geofencing Market
Security Software
Content Protection and Watermarking Market
Security Software
Latin America Fraud Detection and Prevention Market
Security Software
Mass Notification System Market
Security Software
Facial Recognition Market
Security Software
Automotive Endpoint Authentication Market
Security Software
Digital Risk Protection Platform Market
Security Software
Global Electronic Passports Market