
 Digital Risk Protection Platform Market | 2026-2036
Digital Risk Protection Platform Market Size, Share, and Industry Trends Forecast 2026-2036
Digital Risk Protection Platform Market Analysis
Agentic artificial intelligence is rewriting how security platforms autonomously hunt, validate, and neutralize threats across external attack surfaces. CrowdStrike leverages native endpoint telemetry to extend protection into adversary infrastructure monitoring. Recorded Future anchors its competitive position through machine-readable threat intelligence spanning dark web forums and leaked credential repositories. ZeroFox specializes in brand protection and executive digital risk, occupying a distinct niche against broader platform competitors.
A digital risk protection platform constitutes an integrated cybersecurity system that continuously monitors external digital assets—domains, social media, code repositories, and leaked databases—for threats beyond the corporate perimeter, typically employing automated collection, natural language processing, and machine learning classification to score and prioritize alerts. The platform's primary commercial purpose is to compress the mean time to detect impersonation, data leakage, and supply chain compromise before adversaries operationalize these exposures. Threat intelligence and cloud-based deployment represent the fastest-expanding configuration, as financial services and government end users shift from periodic audits to continuous external monitoring. Managed services within the service type dimension capture disproportionate margin pools, since clients lack internal staffing to interpret high-volume alert streams.
The EU AI Act, GDPR, and NIS2 Directive collectively mandate algorithmic transparency and incident reporting timelines that reshape platform procurement criteria across European financial services and healthcare buyers. In the United States, SEC cybersecurity disclosure rules and HIPAA breach notification standards compel regulated entities to document external threat detection capabilities. Stakeholders must evaluate whether their current vendor relationships deliver autonomous response workflows or merely passive alerting, as this capability gap determines operational resilience during concentrated attack campaigns.
Market Dynamics
Agentic AI architectures compress threat detection cycles from hours to minutes, forcing platform vendors to reengineer alert-to-response pipelines around autonomous decision workflows rather than human-in-the-loop triage.
Growth Catalysts
- EU AI Act compliance mandates:European financial services firms must demonstrate algorithmic transparency in automated threat scoring, accelerating replacement of opaque legacy systems with auditable machine learning pipelines.
- Cloud-native telemetry convergence:Endpoint detection vendors extend natively into external attack surface monitoring, collapsing procurement cycles for integrated platform suites versus point solutions.
- Digital supply chain exposures:Software bill of materials requirements and third-party code repository monitoring create standing demand for continuous external asset discovery across technology and healthcare verticals.
Market Restraints
- Alert fatigue and false positive rates:High-volume automated collection generates noise-to-signal ratios that strain security operations center staffing, particularly in mid-market enterprises without dedicated threat intelligence analysts.
- Data residency and sovereignty constraints:Cross-border intelligence sharing faces fragmentation under divergent national cybersecurity frameworks, complicating platform architecture for multinational deployments.
- Specialist talent scarcity:Shortage of analysts capable of contextualizing dark web intelligence and attribution patterns limits customer self-sufficiency, tethering revenue to high-touch managed services.
Strategic Opportunities
- India's digital public infrastructure expansion:Unified Payments Interface and Aadhaar-linked service proliferation create attack surface complexity that domestic enterprises lack tools to monitor, opening white space for localized platform deployment.
- Convergence of threat intelligence and exposure management:Integration of automated pentesting validation with continuous external monitoring enables outcome-based security posture scoring for cyber insurance underwriting.
- SEC cybersecurity disclosure rules:Mandated incident reporting timelines compel US-listed firms to document external detection capabilities, creating procurement urgency distinct from voluntary security investment cycles.
Industry Challenges
- Multi-cloud integration complexity:Enterprises operating across AWS, Azure, and Google Cloud environments require unified external monitoring that normalizes disparate API schemas and logging formats.
- Attribution standardization gaps:Absence of industry-wide frameworks for confidence-scoring threat actor linkage forces vendors to maintain proprietary taxonomies that complicate customer migration and interoperability.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Digital Risk Protection Platform Market |
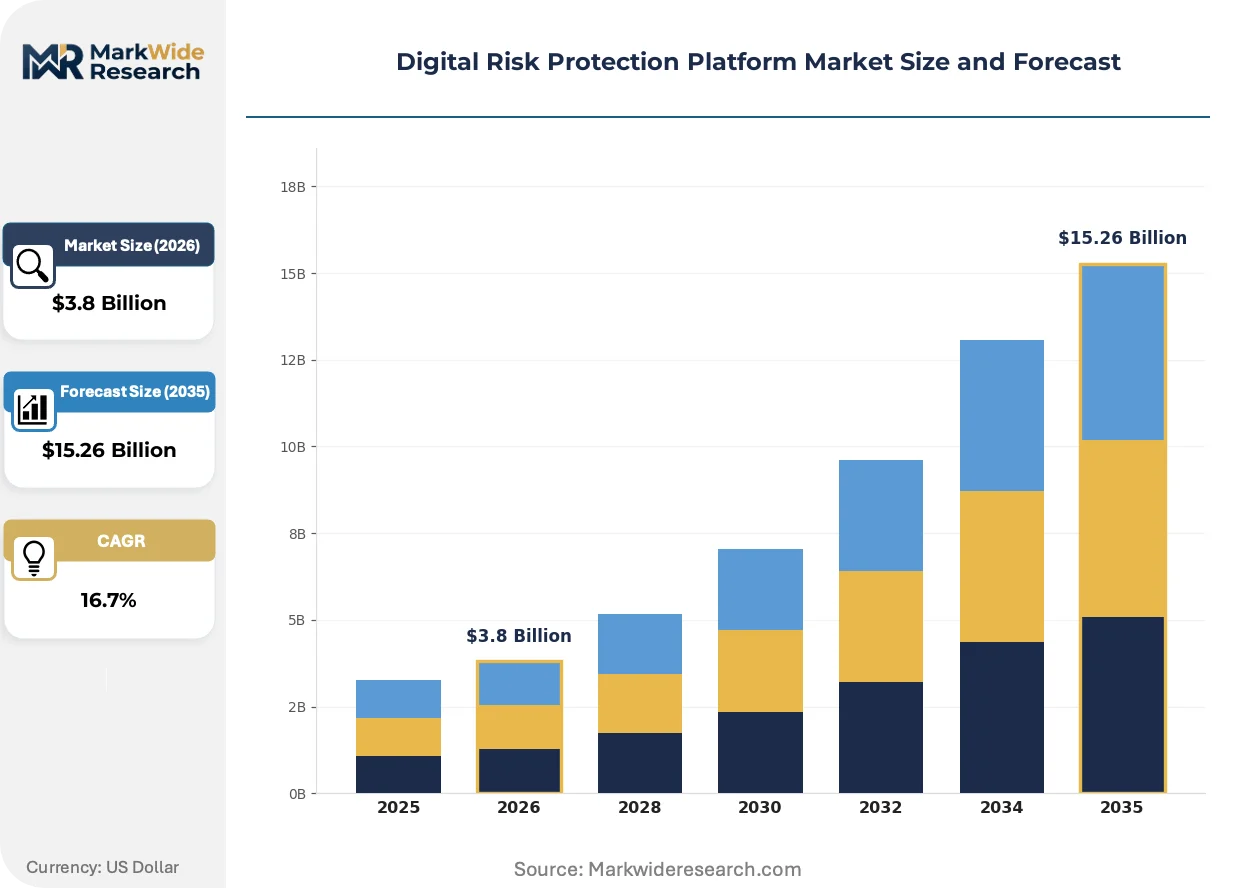
| Market Size in 2026 | $3.8 Billion |
| Market Size in 2035 | $15.26 Billion |
| CAGR (2026 – 2036) | 16.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Threat Intelligence, Vulnerability Management, Incident Response, Compliance Monitoring Deployment: Cloud-Based, On-Premises, Hybrid, SaaS End User: Financial Services, Healthcare, Government, Education Service Type: Consulting, Implementation, Maintenance, Managed Services |
| Companies Covered | BlueVoyant, CrowdStrike, Proofpoint, UpGuard, Rapid7, ZeroFox, Recorded Future, Group-IB, ReliaQuest, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Digital Risk Protection Platform Market Emerging Trajectories
Autonomous response orchestration is displacing passive alerting as the baseline competitive requirement, with platform differentiation shifting from data collection breadth to action automation depth.
Large language model-powered natural language processing is digitizing dark web forum monitoring and phishing lure analysis at scale. Financial services security teams deploy these pipelines to process foreign-language threat actor chatter without human translator bottlenecks. The compression of multilingual intelligence processing is collapsing the time between adversary planning and defender notification.
The EU AI Act's risk classification framework for automated decision systems imposes documentation burdens on machine learning-based threat scoring algorithms. Platform vendors serving European regulated entities must retrofit model explainability features and audit trail capabilities. Healthcare and critical infrastructure buyers in Germany and France now prioritize vendors with pre-built compliance documentation over raw detection performance.
Consolidated platform procurement is displacing best-of-breed point solution stacking among enterprise security teams. CISOs at Fortune 500 manufacturers and energy firms now mandate single-vendor accountability for external attack surface coverage. This preference shift favors integrated suite providers over specialized brand protection or dark web monitoring vendors in North American and Western European competitive evaluations.
Digital Risk Protection Platform Market Segmentation
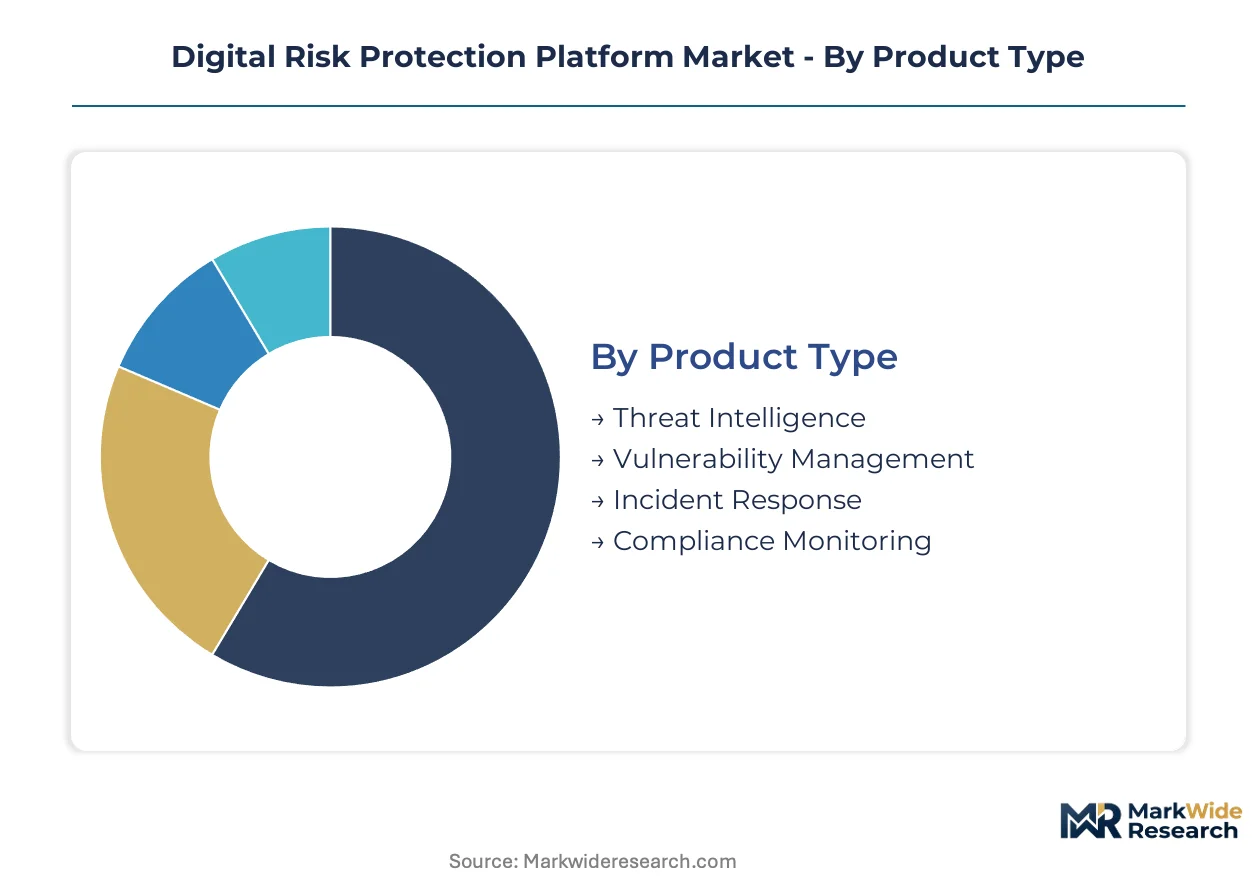
Segmentation in digital risk protection platforms determines procurement architecture and margin capture. Buyers prioritize integrated configurations that compress detection-to-response cycles across external attack surfaces.
Product Type:
Use-case spectrum spans proactive threat hunting through reactive incident containment, with automation depth determining commercial value capture.
- Threat Intelligence:Machine-readable feeds aggregate dark web forums, leaked credential repositories, and adversary infrastructure indicators for automated scoring. Financial services firms in the United States and Germany consume these feeds to satisfy SEC and EU AI Act algorithmic transparency mandates. This segment commands premium pricing through real-time enrichment and attribution confidence scoring.
- Vulnerability Management:Continuous external asset discovery maps domains, subdomains, and code repositories against known exploit databases. Healthcare providers deploy these tools to monitor digital supply chain exposures from third-party medical device vendors. Integration with software bill of materials frameworks accelerates procurement among technology and manufacturing verticals.
- Incident Response:Orchestrated playbooks automate containment workflows for impersonation and data leakage events. Demand concentrates in mid-market enterprises lacking dedicated security operations centers.
- Compliance Monitoring:Automated mapping of external threats to GDPR, HIPAA, and NIS2 reporting requirements reduces audit preparation cycles. European regulated entities prioritize pre-built compliance documentation over raw detection performance.
Established volume favors Threat Intelligence; emerging adoption favors Vulnerability Management.
Deployment:
Architecture choice reflects data sovereignty requirements and existing security infrastructure investments.
- Cloud-Based:Native API integration with AWS, Azure, and Google Cloud enables elastic scaling of external monitoring capacity. Financial services and government end users in India and the United States shift from periodic audits to continuous deployment. This configuration collapses procurement cycles through rapid time-to-value.
- SaaS:Multi-tenant platforms deliver threat intelligence without infrastructure ownership, capturing mid-market price sensitivity. German healthcare providers favor SaaS delivery to minimize internal staffing requirements under GDPR processor agreement constraints.
- Hybrid:Split architectures retain sensitive data on-premises while leveraging cloud analytics for scale. Energy and critical infrastructure operators mandate hybrid deployment for operational technology segmentation.
- On-Premises:Air-gapped installations serve defense and intelligence community requirements with strict data residency controls. Procurement volumes remain constrained by capital expenditure approval cycles.
Cloud-Native configurations are climbing the fastest; On-Premises maintains share in regulated defense verticals.
End User:
Vertical specialization determines feature prioritization and compliance integration depth.
- Financial Services:Banks, insurers, and payment processors deploy comprehensive external monitoring to detect executive impersonation and phishing infrastructure. EU AI Act and SEC disclosure rules accelerate replacement of legacy periodic assessment tools.
- Government:National security and civilian agencies mandate continuous attack surface monitoring for supply chain integrity. India's digital public infrastructure expansion creates white space for localized platform deployment.
- Healthcare:Hospital systems and pharmaceutical manufacturers monitor for leaked patient records and clinical trial data exposure. HIPAA breach notification standards compel documented external detection capabilities.
- Education:Universities and research institutions face escalating ransomware exposure through remote learning infrastructure. Budget constraints favor SaaS delivery over capital-intensive on-premises deployment.
Financial Services dominates current procurement volumes; Government represents the steepest expansion trajectory through mandated supply chain monitoring.
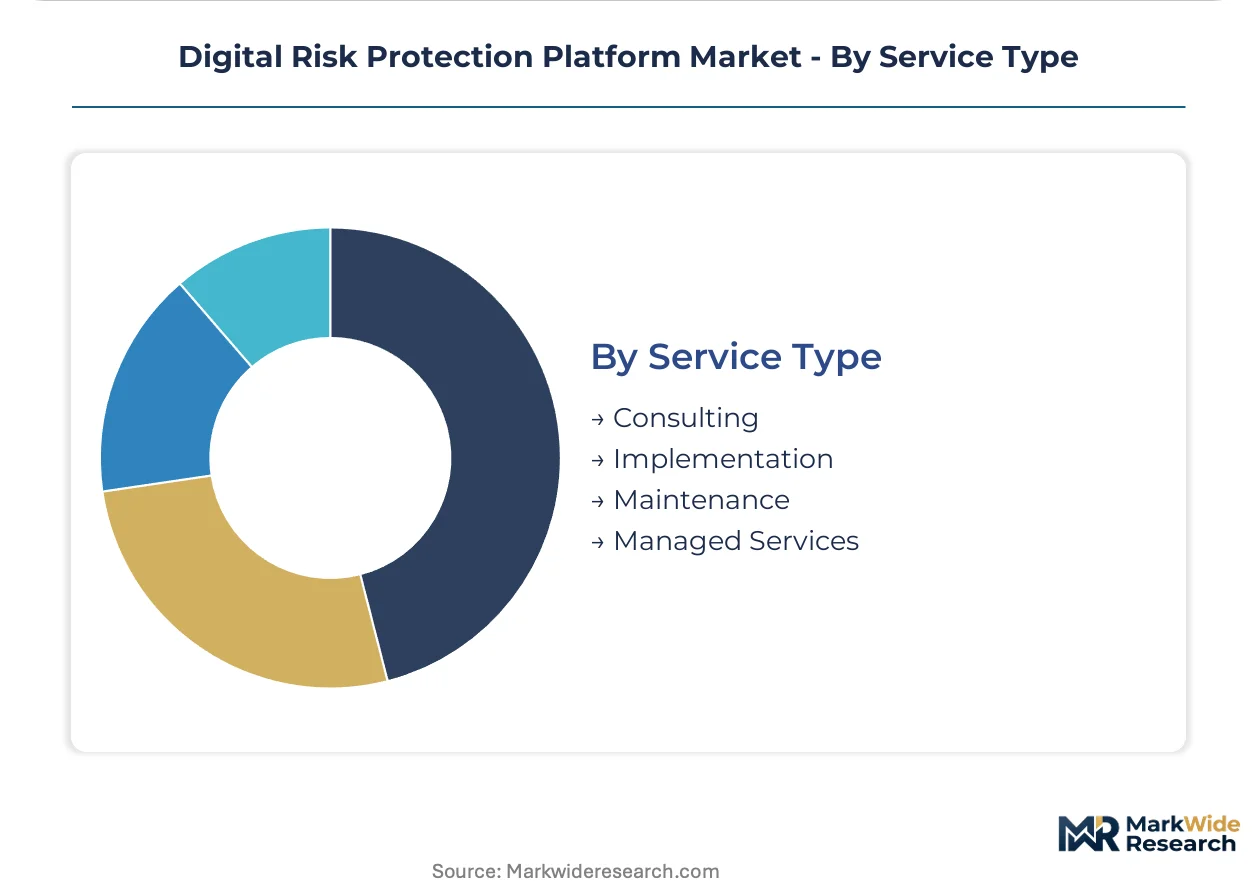
Service Type:
Delivery model selection correlates with internal analyst staffing levels and threat intelligence maturity.
- Managed Services:Vendor-operated security operations centers interpret high-volume alert streams and deliver contextualized incident reports. Mid-market enterprises without dedicated threat intelligence analysts tether procurement to recurring service contracts. This segment captures disproportionate margin pools through analyst labor arbitrage.
- Consulting:Advisory engagements assess external attack surface posture and design monitoring architecture. Large enterprises deploy consulting to rationalize fragmented point solution portfolios ahead of platform consolidation.
- Implementation:Technical deployment services integrate platform telemetry with existing security information and event management infrastructure. Complex multi-cloud environments drive demand for specialized integration expertise.
- Maintenance:Ongoing platform updates and threat feed refresh cycles ensure detection relevance against evolving adversary tactics. Subscription renewal rates depend on demonstrated reduction in mean time to detect.
Managed Services commands premium pricing through talent scarcity; Consulting gains share fastest through platform consolidation mandates.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
United States-based platform vendors export threat intelligence services to European financial institutions confronting EU AI Act compliance deadlines. German banks and French insurers now mandate algorithmic transparency documentation that domestic European vendors struggle to deliver at scale.
United States
SEC cybersecurity disclosure rules compel listed firms to document external threat detection capabilities within mandated reporting timelines. Financial services regulators in New York and California enforce breach notification standards that accelerate procurement of continuous monitoring platforms. The San Francisco Bay Area and Boston security clusters host vendors extending endpoint telemetry into adversary infrastructure monitoring.
Germany
Industrial manufacturers and automotive suppliers deploy external attack surface monitoring to protect digital supply chains from third-party code compromises. The EU AI Act and NIS2 Directive mandate algorithmic transparency in automated threat scoring systems used by Frankfurt financial institutions. Bavaria's Munich security hub concentrates vendors retrofitting machine learning pipelines with model explainability features for healthcare and critical infrastructure buyers.
India
Domestic enterprises lack indigenous tools to monitor attack surface complexity from Unified Payments Interface and Aadhaar-linked service proliferation. The central bank's cybersecurity guidelines for payment system operators drive procurement of cloud-native external monitoring. Bangalore and Hyderabad technology corridors attract platform deployments targeting digital public infrastructure expansion.
United Kingdom
London financial institutions integrate threat intelligence feeds to detect executive impersonation and phishing infrastructure targeting payment systems. The Financial Conduct Authority's operational resilience requirements compress procurement cycles for continuous external monitoring. The Cambridge security cluster develops natural language processing pipelines for multilingual dark web forum analysis.
France
Healthcare providers and pharmaceutical manufacturers monitor for leaked clinical trial data and patient record exposures. ANSM and CNIL enforcement of GDPR processor agreement constraints favors SaaS delivery models minimizing internal staffing requirements. The Paris-Saclay cybersecurity cluster concentrates vendors building pre-built compliance documentation for EU AI Act risk classification frameworks.
Digital Risk Protection Platform Market Vendor Landscape
Channel-controlling players compete with product-specialist players across a market structure consolidating around integrated platform suites versus fragmented point solutions. Endpoint detection vendors leverage native telemetry to collapse procurement cycles for external attack surface coverage. Three archetypes dominate: cloud-native suite providers, specialized brand protection vendors, and managed security service operators. M&A activity concentrates on threat intelligence feed consolidation, while strategic partnerships target multi-cloud API normalization.
Within the cloud-native suite tier, CrowdStrike and Recorded Future occupy positions anchoring competitive positioning through telemetry convergence and machine-readable intelligence aggregation. ZeroFox exemplifies the specialization archetype, representing brand protection and executive digital risk monitoring against broader platform competitors. These three vendors illustrate the strategic divergence between integrated external monitoring and niche use-case depth.
| Leading Market Players |
|---|
| BlueVoyant |
| CrowdStrike |
| Proofpoint |
| UpGuard |
| Rapid7 |
| ZeroFox |
| Recorded Future |
| Group-IB |
| ReliaQuest |
| Others |
Supply Flow & Price Mechanics
Threat intelligence feed aggregation from United States-based security vendors concentrates upstream data sourcing, directing margin capture toward managed service tiers that package analyst interpretation rather than raw telemetry delivery. Cloud-native platform providers leverage this concentration to extract recurring revenue premiums while compressing price points for standalone software access.
Pricing Analysis
Next-generation agentic AI capabilities command substantial premiums over legacy rule-based detection systems, while prior-generation signature-matching tools face accelerated price erosion. Three-tier pricing structure across premium, standard, and economy levels separates enterprise managed detection and response bundles from mid-market SaaS tiers and basic threat feed subscriptions. Price differentiation rests on automation depth and EU AI Act compliance documentation completeness. Pricing pressure stems from endpoint detection vendors bundling external monitoring at marginal cost. Mid-market enterprises without dedicated security operations centers exhibit highest price sensitivity, while regulated financial services buyers prioritize detection performance over cost.
Supply Chain Analysis
Contract manufacturing of security hardware appliances concentrates with Foxconn, Jabil, and Flex facilities across Taiwan, China, and Mexico. Platform software development draws from engineering talent pools in the United States, India, and Israel. Raw material dependencies include specialized semiconductors for network appliances, cloud compute capacity from hyperscalers, and multilingual natural language processing training data. Supply chain risk centers on single-source vulnerability for GPU acceleration hardware essential to large language model inference. Distribution runs through direct enterprise sales teams, channel partners, and hyperscaler marketplaces.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Agentic artificial intelligence architectures are compressing detection-to-response cycles from hours to minutes, creating structural disruption as autonomous decision workflows displace human-in-the-loop triage. EU AI Act algorithmic transparency mandates compound this inflection by retrofitting procurement criteria across European financial services and healthcare buyers.
For Market Incumbents: Build telemetry integration moats by natively converging endpoint detection with external attack surface monitoring. Incumbents should acquire specialized dark web intelligence feed providers to consolidate data sourcing advantages. Cloud-native suite providers face substitution threat from endpoint vendors bundling external monitoring at marginal cost. Capacity addition in India addresses digital public infrastructure expansion while securing GDPR-compliant EU data residency through regional cloud regions. For New Entrants and Emerging Players: Mid-market managed security service providers in India and Southeast Asia represent the most penetrable entry point for localized platform deployment. Healthcare providers in France and Germany lacking internal threat intelligence analysts offer white-space demand for compliance-integrated SaaS delivery. Go-to-market execution should anchor through channel partnerships with existing security information and event management vendors rather than direct enterprise sales investment. For Investors and Strategic Acquirers: Secondary-cycle assets sit with private equity-backed managed security service operators holding recurring revenue contracts but lacking autonomous response orchestration capabilities. Five-to-ten year viability hinges on successful platform consolidation plays that collapse point solution fragmentation. Acquisition target archetype: regional managed services providers with established customer relationships in EU AI Act-regulated verticals. Signal to watch: customer churn acceleration among legacy periodic assessment tool vendors as continuous monitoring becomes baseline procurement requirement.| Strategic Initiative | Industry Significance |
|---|---|
| Autonomous Response Orchestration Development | CrowdStrike and Recorded Future anchor competitive positioning through native telemetry convergence and machine-readable intelligence aggregation. |
| EU AI Act Compliance Documentation Buildout | German healthcare and French pharmaceutical buyers now prioritize vendors with pre-built algorithmic transparency frameworks over raw detection performance. |
| Threat Intelligence Feed Consolidation | Machine-readable dark web and leaked credential repositories command premium pricing through real-time enrichment and attribution confidence scoring. |
| Multi-Cloud API Normalization Partnership | Enterprises operating across AWS, Azure, and Google Cloud environments require unified external monitoring that normalizes disparate logging formats. |
| India Digital Public Infrastructure Localization | Unified Payments Interface and Aadhaar-linked service proliferation creates attack surface complexity that domestic enterprises lack tools to monitor. |
Methodological Framework
Desk research of threat intelligence platform technical documentation, regulatory filing databases, and cloud security architecture whitepapers preceded structured interviews with chief information security officers, threat intelligence analysts, security operations center directors, and procurement officers at financial services and healthcare enterprises. Secondary validation drew from SEC cybersecurity disclosure filings, EU AI Act implementation guidance, NIS2 Directive technical standards, and cloud provider marketplace transaction data. Bottom-up segment sizing triangulated against top-down market envelope estimates from platform vendor revenue disclosures and managed security service contract values.
Forecast assumptions held fixed the current regulatory enforcement trajectory for algorithmic transparency mandates while varying cloud-native deployment penetration rates and autonomous response adoption curves across the analysis window. Segmentation dimensions modeled include product type, deployment architecture, end-user vertical, and service delivery model, with additional granularity on EU AI Act risk classification tiers. CAGRs were derived from logistic diffusion curves fitted to historical platform procurement cycles and regulatory compliance deadline clustering. Industry-specific inputs incorporated software bill of materials adoption velocity and cyber insurance underwriting integration timelines.
Practitioners should monitor EU AI Act enforcement consistency, SEC cybersecurity disclosure litigation trends, and hyperscaler security marketplace commission structures for early signals of forecast revision. Quarterly review of threat intelligence platform customer churn rates, managed security service contract renewal pricing, and autonomous response workflow deployment metrics is advised to detect inflection.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Video Intercom Devices and Equipment Market
Security Software
Global Dynamic Application Security Testing Market
Security Software
Mobile Security Market
Security Software
Consumer Endpoint Security Market
Security Software
Internet Filter Software Market
Security Software
Patch and Remediation Software Market
Security Software
Geofencing Market
Security Software
Security Software Market
Security Software
Data Masking Technology Market
Security Software
Global Optical Encryption Market
Security Software
Embedded Security Market
Security Software
Stalkerware Market
Security Software
Asia-Pacific Fraud Detection & Prevention Market
Security Software
Cyber Attack Simulation Software Market
Security Software
Sound Masking Systems Market
Security Software
Latin America Fraud Detection and Prevention Market