
 Open-Source Intelligence (OSINT) Market | 2026-2036
Open-Source Intelligence (OSINT) Market Size, Share, and Industry Trends Forecast 2026-2036
Open-Source Intelligence (OSINT) Market Analysis
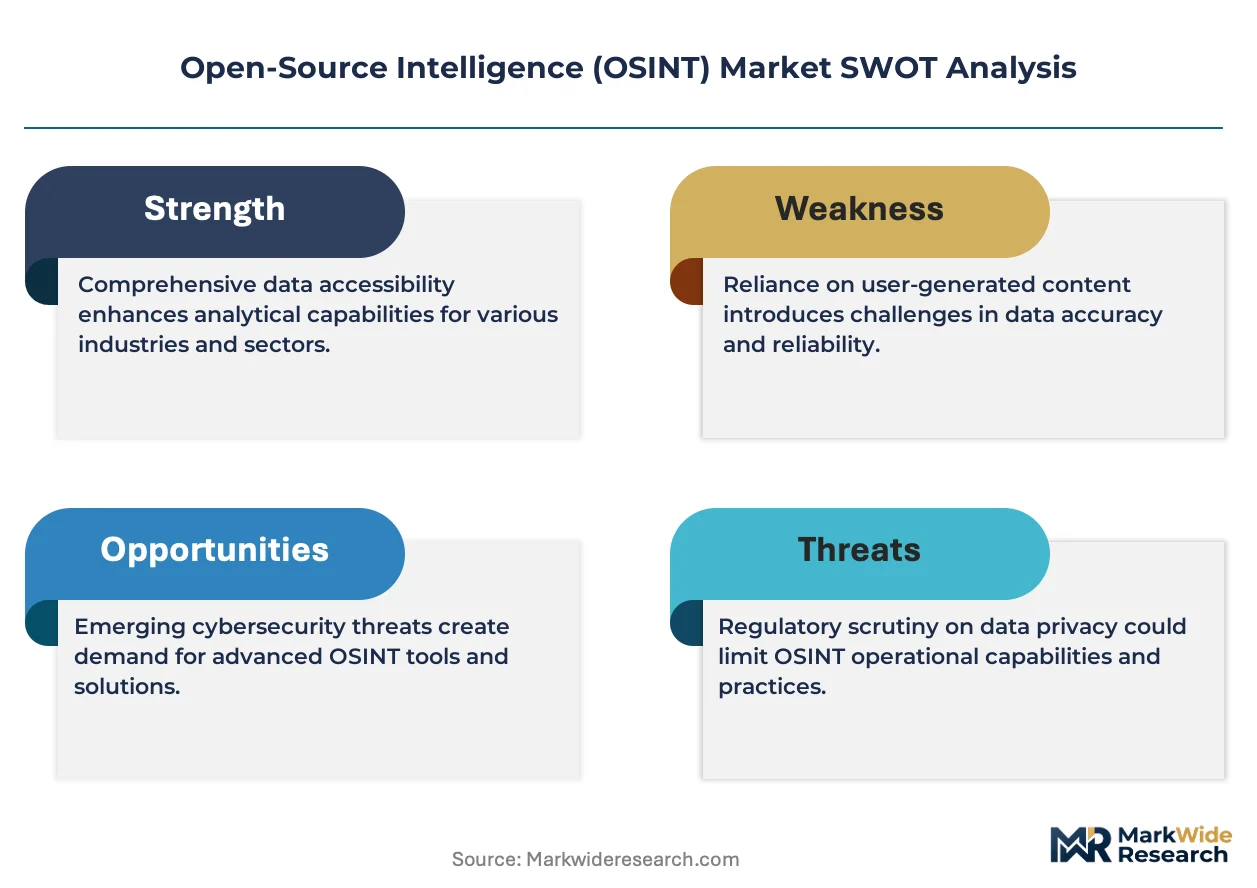
ISO 27001 certification is rotating as a baseline qualification for vendors bidding on government OSINT contracts. Palantir Technologies leverages its existing intelligence-community relationships to sustain long-term platform deployments. Recorded Future anchors its position through specialized threat-intelligence data feeds that differentiate it from general-purpose competitors.
Open-source intelligence encompasses the collection, processing, and analysis of publicly available data from digital sources including social media, satellite imagery, and open databases to produce actionable assessments for security and commercial decision-making. Platforms integrate machine learning pipelines with natural language processing engines to filter multilingual content across millions of sources in near real-time. Cybersecurity applications currently dominate contract value, while risk management deployments are expanding fastest among multinational corporations seeking supply-chain visibility. Cloud-based delivery models capture the majority of new procurement, though hybrid architectures persist in defense settings with classified data requirements.
The Federal Acquisition Regulation and Defense Federal Acquisition Regulation Supplement shape contracting eligibility for US vendors, while the EU AI Act imposes risk-classification obligations on automated OSINT systems processing personal data. GDPR compliance costs constrain European platform architectures, particularly for social-media monitoring tools. Stakeholders must weigh regulatory fragmentation against the operational advantage of unified global data pipelines when selecting deployment strategies.
Market Dynamics
Machine learning inference at the network edge is fragmenting OSINT platform architectures, forcing vendors to redistribute computational workloads between cloud clusters and localized processing nodes to satisfy latency-sensitive defense applications.
Growth Catalysts
- EU AI Act risk classification:Automated OSINT systems processing personal data now face mandatory conformity assessments, creating procurement urgency among European government agencies seeking compliant platforms before enforcement deadlines.
- Satellite imagery resolution advances:Commercial providers now deliver sub-meter optical and synthetic aperture radar products, enabling defense contractors to monitor border infrastructure and maritime traffic without classified satellite access.
- Multinational supply chain visibility mandates:Fortune 500 risk management departments are deploying OSINT tools to map tier-three supplier networks across Southeast Asian manufacturing hubs.
Market Restraints
- GDPR Article 25 data minimization:European platform architectures incur substantial engineering costs to embed privacy-by-design into social-media monitoring pipelines, compressing margins relative to North American competitors.
- GPU cluster supply concentration:Training-scale NVIDIA H100 availability remains bottlenecked through Taiwan Semiconductor Manufacturing contract allocations, delaying model refinement cycles for six to nine months.
- Multilingual NLP performance gaps:Low-resource language models for Arabic dialects and Central Asian Turkic languages exhibit entity extraction error rates three to four times higher than English baselines.
Strategic Opportunities
- India BIS cybersecurity certification pathway:Domestic platform vendors can capture central and state government contracts by obtaining Bureau of Indian Standards marks for critical information infrastructure protection tools.
- Convergence of OSINT and blockchain analytics:Cryptocurrency transaction tracing capabilities are merging with traditional open-source pipelines to address ransomware payment investigations and sanctions evasion detection.
- Japan METI data free flow with trust initiative:Cross-border data transfer frameworks between Japan and ASEAN economies create compliant architectures for regional threat intelligence sharing without GDPR-equivalent restrictions.
Industry Challenges
- Security clearance timelines:Personnel with active TS/SCI clearances capable of operating in classified hybrid environments remain scarce, extending deployment staffing cycles by four to six months.
- ISO 27001 certification backlog:Accredited auditors face eighteen-month queues for initial certification and surveillance audits, delaying vendor eligibility for federal procurement vehicles.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Open-Source Intelligence (OSINT) Market |
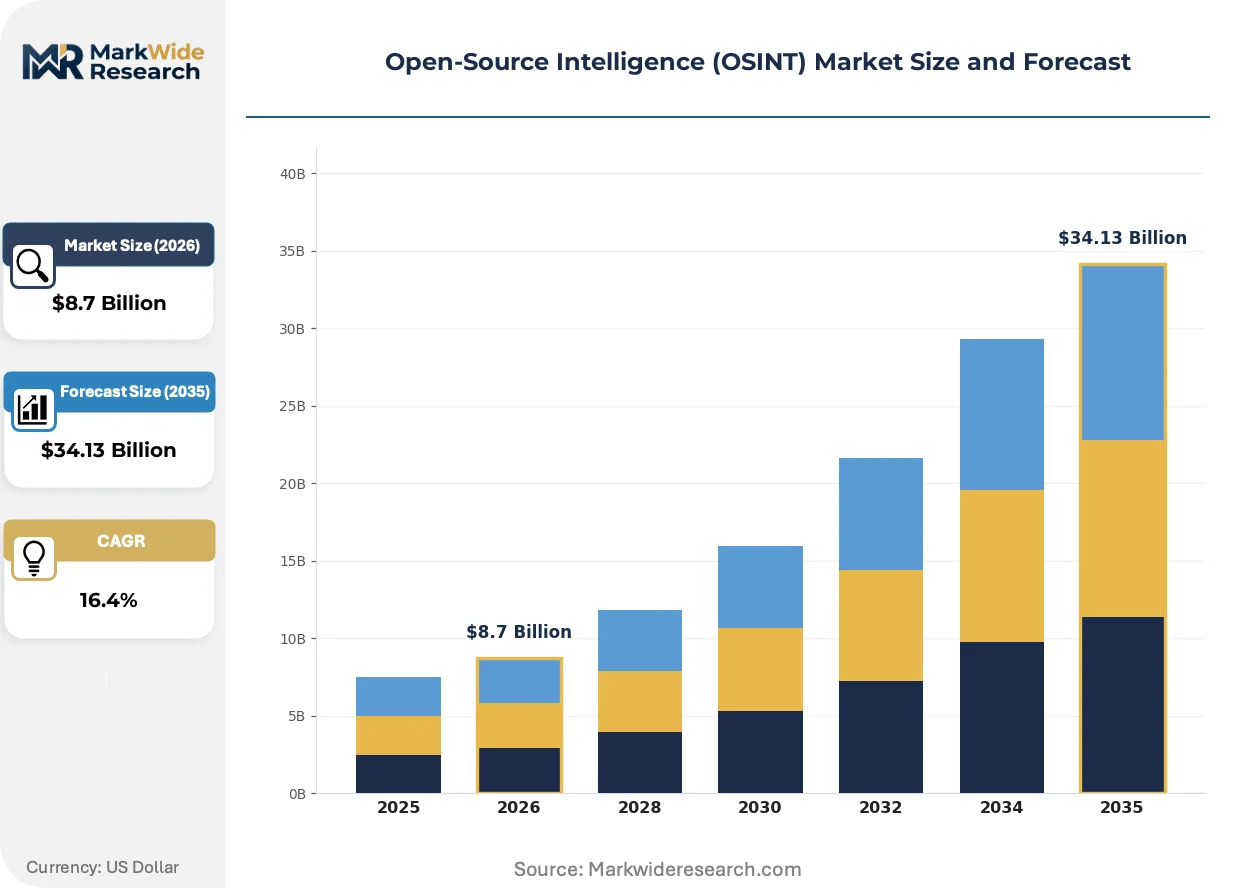
| Market Size in 2026 | $8.7 Billion |
| Market Size in 2035 | $34.13 Billion |
| CAGR (2026 – 2036) | 16.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Application: Cybersecurity, Risk Management, Fraud Detection, Competitive Intelligence End User: Government Agencies, Private Sector, Nonprofits, Law Enforcement Deployment: Cloud, On-premise, Hybrid, SaaS Technology: Data Mining, Machine Learning, Natural Language Processing, Visualization Tools |
| Companies Covered | Babel Street, Thales Group, Palantir Technologies, Social Links, Dataminr, Recorded Future, ShadowDragon, Oceanir, Google LLC, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Open-Source Intelligence (OSINT) Market Emerging Trajectories
Foundation model architectures are compressing development cycles for specialized OSINT applications, enabling smaller teams to field competitive platforms without decade-long training data accumulation.
Federated learning frameworks are fragmenting OSINT model training across sovereign data boundaries. Defense agencies in Germany, France, and the United Kingdom now train shared threat detection models without centralizing classified or personal data repositories. This architecture preserves national data jurisdiction while achieving collective model performance previously requiring pooled datasets.
The EU AI Act high-risk system obligations are restructuring vendor compliance investments. Automated OSINT platforms processing biometric or behavioral data must now maintain risk management systems, data governance protocols, and human oversight mechanisms documented for market surveillance authority review. European security procurement officers are prioritizing vendors with existing conformity assessments over unverified alternatives.
Subscription-based threat intelligence delivery is displacing perpetual license arrangements in corporate security departments. CISOs at financial services and energy firms now demand continuous data feed access with quarterly model retraining rather than static platform deployments. This shift concentrates recurring revenue with established feed providers and raises capital requirements for new entrants seeking to build proprietary source networks.
Open-Source Intelligence (OSINT) Market Segmentation
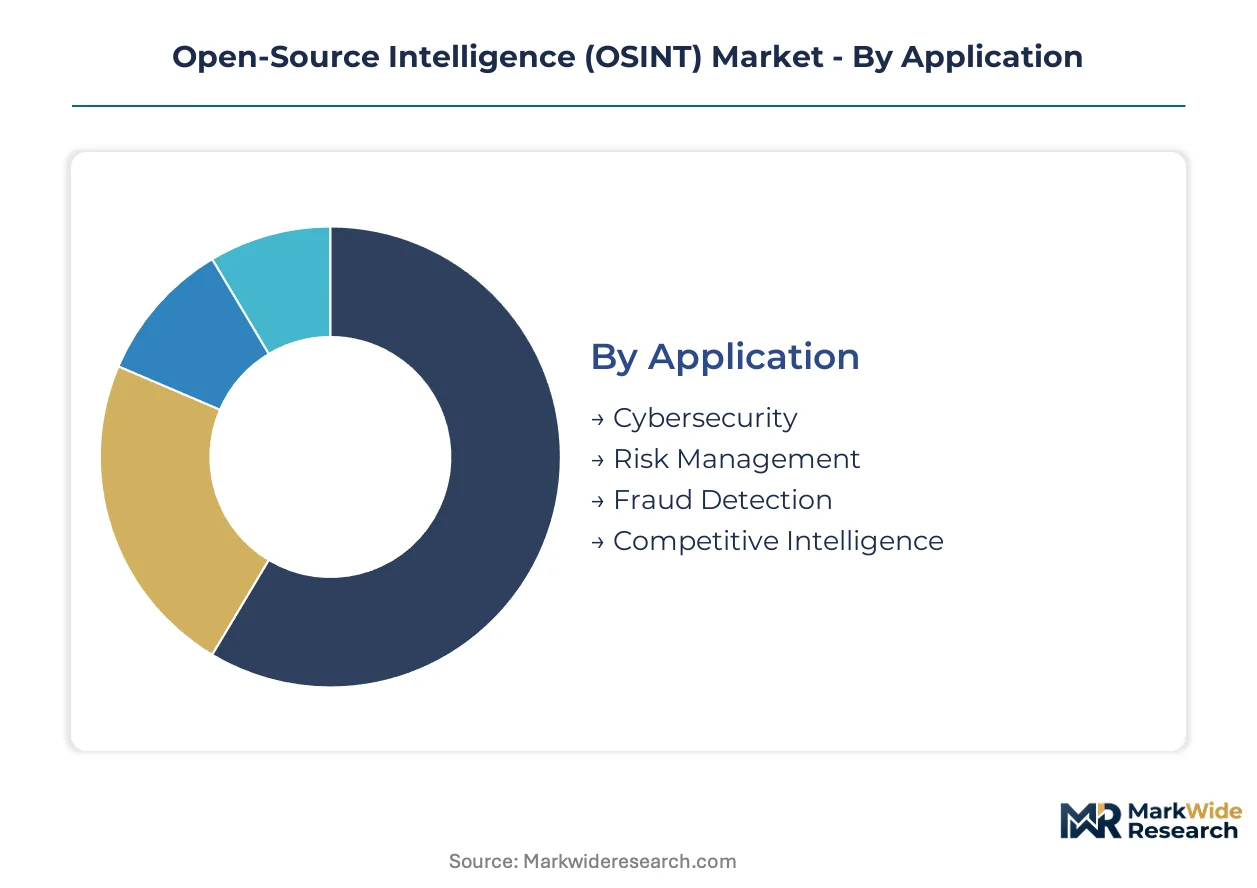
OSINT procurement patterns diverge sharply across application types and deployment models, with regulatory jurisdiction determining platform architecture choices. Buyers segment investments by data sensitivity tiers and operational tempo requirements rather than uniform capability suites.
Application:
EU AI Act risk classifications reshape procurement eligibility across use cases, with high-risk biometric processing triggering mandatory conformity assessments that low-risk competitive intelligence avoids.
- Cybersecurity:Platforms ingest threat indicators from dark web forums, paste sites, and certificate transparency logs to identify credential leaks and infrastructure vulnerabilities. Defense agencies in the United States and United Kingdom dominate contract value, driven by classified network protection mandates and continuous monitoring requirements for critical infrastructure operators.
- Risk Management:Supply chain mapping tools aggregate satellite imagery, shipping registries, and corporate filing data to flag supplier concentration and geopolitical exposure. Multinational manufacturers in Germany and Japan are expanding deployments fastest, responding to due diligence obligations under the German Supply Chain Due Diligence Act and METI guidance on cross-border data governance.
- Fraud Detection:Transaction pattern analysis combines open corporate records with adverse media screening for insurance and financial services verification.
- Competitive Intelligence:Patent monitoring, job posting analysis, and earnings call transcription serve strategic planning functions with lighter regulatory touch.
Established volume favors Cybersecurity; emerging adoption favors Risk Management.
End User:
Procurement scale and data classification requirements fragment the customer base across clearance thresholds and commercial sophistication levels.
- Government Agencies:National security and border control operations require TS/SCI-cleared personnel and hybrid architectures separating classified from open-source processing. United States federal contracts specify FedRAMP authorization and ISO 27001 certification as baseline eligibility, compressing vendor pools to established defense integrators.
- Private Sector:Financial services, energy, and technology firms purchase subscription threat feeds with quarterly model retraining rather than perpetual licenses. Banking regulators in Singapore and Hong Kong now mandate continuous adverse media screening for correspondent banking relationships, accelerating procurement cycles.
- Nonprofits:Human rights documentation and conflict monitoring operations rely on grant-funded platform access with limited customization.
- Law Enforcement:Domestic counterterrorism and organized crime units face GDPR Article 25 constraints on social media monitoring that constrain deployment scope in European jurisdictions.
Budget concentration sits with Government Agencies; capability innovation originates in Private Sector deployments.
Deployment:
Latency requirements and data residency rules redistribute computational workloads between cloud clusters and localized processing nodes.
- Cloud:Scalable inference pipelines serve commercial threat intelligence delivery with sub-second query response. AWS, Azure, and Google Cloud regions in Frankfurt, Singapore, and Sydney capture regional data localization requirements without on-premise capital expenditure.
- On-premise:Air-gapped installations preserve operational security for classified hybrid environments where external connectivity is prohibited. German and French defense ministries mandate sovereign infrastructure for biometric processing under national security exemptions to EU data transfer restrictions.
- Hybrid:Sensitive data remains on-site while model training and non-critical analytics shift to cloud infrastructure.
- SaaS:Browser-based dashboards lower entry barriers for mid-market security teams without dedicated data science staff.
Cloud deployments dominate new procurement; hybrid architectures persist where classified data segregation is mandatory.
Technology:
Foundation model architectures compress development cycles, enabling competitive platforms without decade-long training data accumulation.
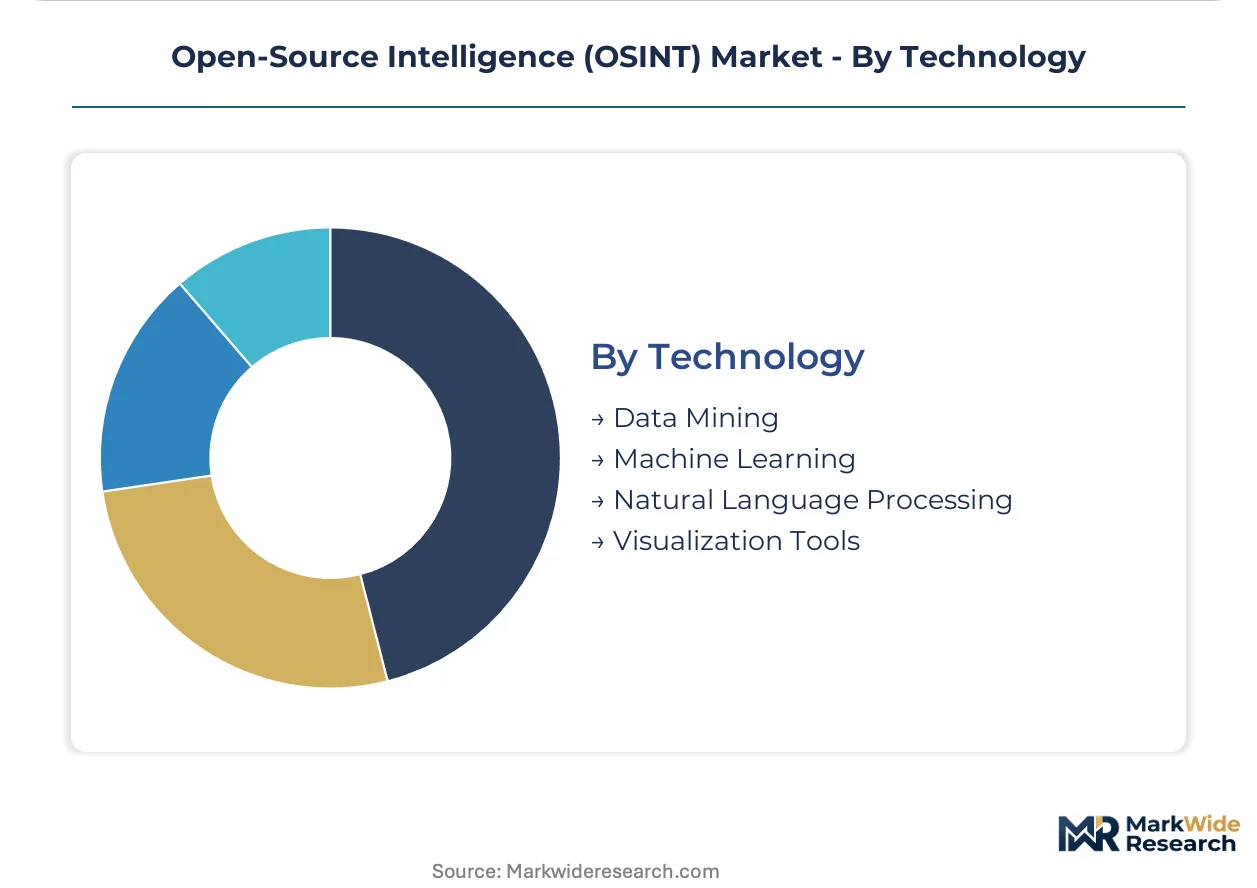
- Data Mining:Automated collection pipelines scrape structured and unstructured sources across surface web, deep web, and dark web repositories. Specialized crawlers for Arabic dialects and Central Asian Turkic languages exhibit entity extraction error rates three to four times higher than English baselines, constraining coverage in priority intelligence targets.
- Machine Learning:Federated learning frameworks enable German, French, and British defense agencies to train shared threat detection models without centralizing classified repositories. GPU cluster supply concentration through Taiwan Semiconductor Manufacturing contract allocations delays model refinement cycles for six to nine months.
- Natural Language Processing:Multilingual entity extraction and sentiment classification filter millions of sources in near-real-time.
- Visualization Tools:Network graph and geospatial overlays translate raw data into actionable assessments for analyst consumption.
Machine Learning attracts capital investment fastest; Visualization Tools differentiate mature platform offerings.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Federal procurement expansion and EU AI Act compliance deadlines are redistributing platform investments across national security apparatuses. Defense agencies in multiple jurisdictions now prioritize vendors with pre-certified conformity assessments.
United States
Border monitoring contracts and TS/SCI-cleared personnel requirements concentrate demand within the intelligence community. The Federal Acquisition Regulation and Defense Federal Acquisition Regulation Supplement mandate FedRAMP authorization and ISO 27001 certification as baseline eligibility. Washington DC and Northern Virginia host the densest cluster of defense integrators deploying hybrid architectures for classified data environments.
Germany
Federated learning frameworks enable shared threat detection training without centralizing classified repositories across German, French, and British defense agencies. National security exemptions to EU data transfer restrictions mandate sovereign infrastructure for biometric processing. Bavaria and Baden-Württemberg anchor development centers where vendors engineer privacy-by-design into social-media monitoring pipelines under GDPR Article 25 constraints.
United Kingdom
Continuous monitoring requirements for critical infrastructure operators drive cybersecurity platform procurement. The UK National Cyber Security Centre shapes vendor qualification standards for threat intelligence delivery. London and the Southeast concentrate financial services deployments where CISOs demand subscription-based threat feeds with quarterly model retraining.
India
Central and state government contracts for critical information infrastructure protection tools accelerate domestic platform adoption. Bureau of Indian Standards cybersecurity certification creates procurement pathways for local vendors. Karnataka and Telangana host technology clusters where engineering teams adapt multilingual NLP pipelines for Arabic dialects and Central Asian Turkic languages.
Japan
METI data free flow with trust initiatives establish cross-border frameworks for regional threat intelligence sharing without GDPR-equivalent restrictions. Manufacturing supply chain visibility mandates from METI guidance accelerate OSINT deployment among multinational corporations. Tokyo and Osaka anchor corporate security departments mapping tier-three supplier networks across Southeast Asian manufacturing hubs.
Open-Source Intelligence (OSINT) Market Vendor Landscape
Listed leaders compete with private specialists across government certification pathways and subscription pricing models. The vendor base concentrates around defense integrators with active security clearances and commercial threat feed providers with proprietary source networks. Three archetypes dominate: legacy defense contractors with hybrid deployment expertise, cloud-native platforms with scalable inference pipelines, and specialized data feed operators with multilingual collection infrastructure. Competitive moves center on ISO 27001 certification acquisition and federated learning partnerships across sovereign data boundaries.
Within the defense-integrated tier, Palantir Technologies and Thales Group exemplify vendors leveraging long-term intelligence-community relationships for sustained platform deployments. Recorded Future anchors the specialized data feed segment through differentiated threat-intelligence pipelines that separate it from general-purpose competitors. Among cloud-native operators, Dataminr and Babel Street occupy positions serving commercial security departments with near-real-time alerting capabilities. Google LLC represents technology conglomerates extending existing cloud infrastructure into compliant government procurement vehicles.
| Leading Market Players |
|---|
| Babel Street |
| Thales Group |
| Palantir Technologies |
| Social Links |
| Dataminr |
| Recorded Future |
| ShadowDragon |
| Oceanir |
| Google LLC |
| Others |
Supply Flow & Price Mechanics
GPU cluster utilization rates at Taiwan Semiconductor Manufacturing contract allocations establish scale thresholds that compress unit economics for model training while elevating price floors for compliant platform deployments. This concentration dynamic forces vendors to absorb eighteen-month ISO 27001 certification queues into upfront cost structures, reshaping competitive entry barriers across defense and commercial segments.
Pricing Analysis
Certification level creates the primary spread between platform tiers, with FedRAMP-authorized and ISO 27001-certified deployments commanding premium positioning against uncertified alternatives. Three-tier pricing structure separates government-grade hybrid architectures from cloud-native SaaS subscriptions and entry-level visualization tools. Cost compression in the mid-market tier is intensifying because GDPR Article 25 engineering requirements compress European vendor margins relative to North American competitors. Government agencies exhibit the lowest price sensitivity due to mandated compliance thresholds, while mid-market security teams without dedicated data science staff drive hardest bargain hunting.
Supply Chain Analysis
Eighteen-month lead times for NVIDIA H100 GPU allocations through Taiwan Semiconductor Manufacturing contract queues constrain model refinement cycles for vendors across all tiers. Supply concentrates in Taiwan for advanced semiconductor fabrication, the United States for cloud infrastructure provisioning, and Germany for privacy-by-design engineering talent. Raw material dependencies span specialized AI accelerators, multilingual NLP training datasets, and cleared personnel pipelines for TS/SCI environments. Single-source vulnerability in Taiwan Semiconductor Manufacturing contract allocations presents the dominant structural risk. Distribution runs through direct federal procurement vehicles in the United States, certified defense integrators in Europe, and domestic platform vendors in India leveraging Bureau of Indian Standards pathways.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market functions as a defensive-moat story where regulatory entrenchment creates durable competitive positioning. Switching costs for government clients escalate through security clearance requirements and hybrid architecture investments that resist vendor displacement.
For Market Incumbents: Secure federated learning partnerships across German, French, and British defense agencies to lock in collective model training architectures without centralizing classified repositories. Deepen vertical integration into proprietary multilingual NLP pipelines for Arabic dialects and Central Asian Turkic languages to differentiate against general-purpose competitors. Threat: Cloud-native platforms with scalable inference pipelines are eroding mid-market share through subscription pricing flexibility.
For New Entrants and Emerging Players: Bureau of Indian Standards cybersecurity certification fast-tracks access to central and state government contracts for critical information infrastructure protection tools in India. Target corporate risk management departments at multinational manufacturers in Japan responding to METI supply chain visibility mandates. Go-to-market angle: Subscription-based threat intelligence delivery with quarterly model retraining displaces perpetual license arrangements among CISOs at financial services and energy firms.
For Investors and Strategic Acquirers: Recurring-revenue conversion is highest among specialized data feed operators with proprietary source networks and established threat-intelligence pipelines. Long-term viability favors vendors with pre-certified conformity assessments under EU AI Act high-risk system obligations, as European security procurement officers prioritize assessed platforms over unverified alternatives. Acquisition target archetype: Cloud-native platforms with scalable inference pipelines serving commercial security departments. Signal to watch: ISO 27001 certification backlog resolution timelines as indicator of vendor pool expansion.
| Strategic Initiative | Industry Significance |
|---|---|
| Federated Learning Partnership | Enables German, French, and British defense agencies to train shared threat detection models without centralizing classified repositories. |
| ISO 27001 Certification Investment | Unlocks eligibility for United States federal procurement vehicles under Federal Acquisition Regulation baseline requirements. |
| Multilingual NLP Pipeline Development | Addresses entity extraction error rate gaps for Arabic dialects and Central Asian Turkic languages in priority intelligence targets. |
| Subscription Model Transition | Captures recurring revenue concentration as CISOs at financial services and energy firms demand continuous data feed access. |
| Hybrid Architecture Deployment | Preserves operational security for classified environments where external connectivity is prohibited under national security exemptions. |
Methodological Framework
A standing panel of defense procurement officers, platform engineering leads, threat intelligence analysts, and regulatory compliance specialists provided ongoing calibration across primary interview cycles. Secondary validation drew from Federal Acquisition Regulation amendments, EU AI Act implementation guidance, Bureau of Indian Standards certification databases, and hyperscaler capex disclosures. Bottom-up segmentation modeling triangulated against top-down market sizing from defense contract award notifications and commercial threat feed subscription disclosures.
Consistency checks validated volume and value outputs against external benchmarks including federal procurement databases, venture capital financing flows into OSINT platforms, and cloud infrastructure spending patterns across AWS, Azure, and Google Cloud government regions. The analytical framework modeled deployment architecture, end-user classification, application sensitivity tier, and regional regulatory cluster across the projection horizon. CAGRs derived from logistic adoption curves fitted to historical procurement cycles and compliance deadline acceleration effects. Industry-specific forecast inputs incorporated GPU cluster supply constraints through Taiwan Semiconductor Manufacturing contract allocations and ISO 27001 auditor queue durations.
The analysis sits within stated boundaries; outcomes outside sustained federal procurement expansion or EU AI Act enforcement acceleration would require recalibration. Forecasts reflect documented assumptions regarding clearance timeline stability and multilingual NLP performance convergence rates. Outputs are directional rather than point-estimates.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Digital Solutions
Agent-Oriented Enterprise Architecture Market
Digital Solutions
Cloud Manufacturing Execution System (MES) Market
Digital Solutions
Workspace As a Service Market
Digital Solutions
Cinema Point of Sale (POS) Solutions Market
Digital Solutions
Global Connected Workplace Market
Digital Solutions
Turkey ICT Market
Digital Solutions
Cloud-Based POS Market
Digital Solutions
Cloud Based Drug Discovery Platform Market
Digital Solutions
Asia-Pacific Intelligent Document Processing Market
Digital Solutions
Game Engines Market
Digital Solutions
Precision Agriculture Software Market
Digital Solutions
Beacons Management Software Market
Digital Solutions
Data Monetization Solutions for Life Science Companies Market
Digital Solutions
Digital Rights Management (DRM) Market
Digital Solutions
Global Domain and Hosting Market
Digital Solutions
AI In Packaging Design Market