
 Managed File Transfer (MFT) Market | 2026-2036
Managed File Transfer (MFT) Market Size, Share, and Industry Trends Forecast 2026-2036
Managed File Transfer (MFT) Market Foresight
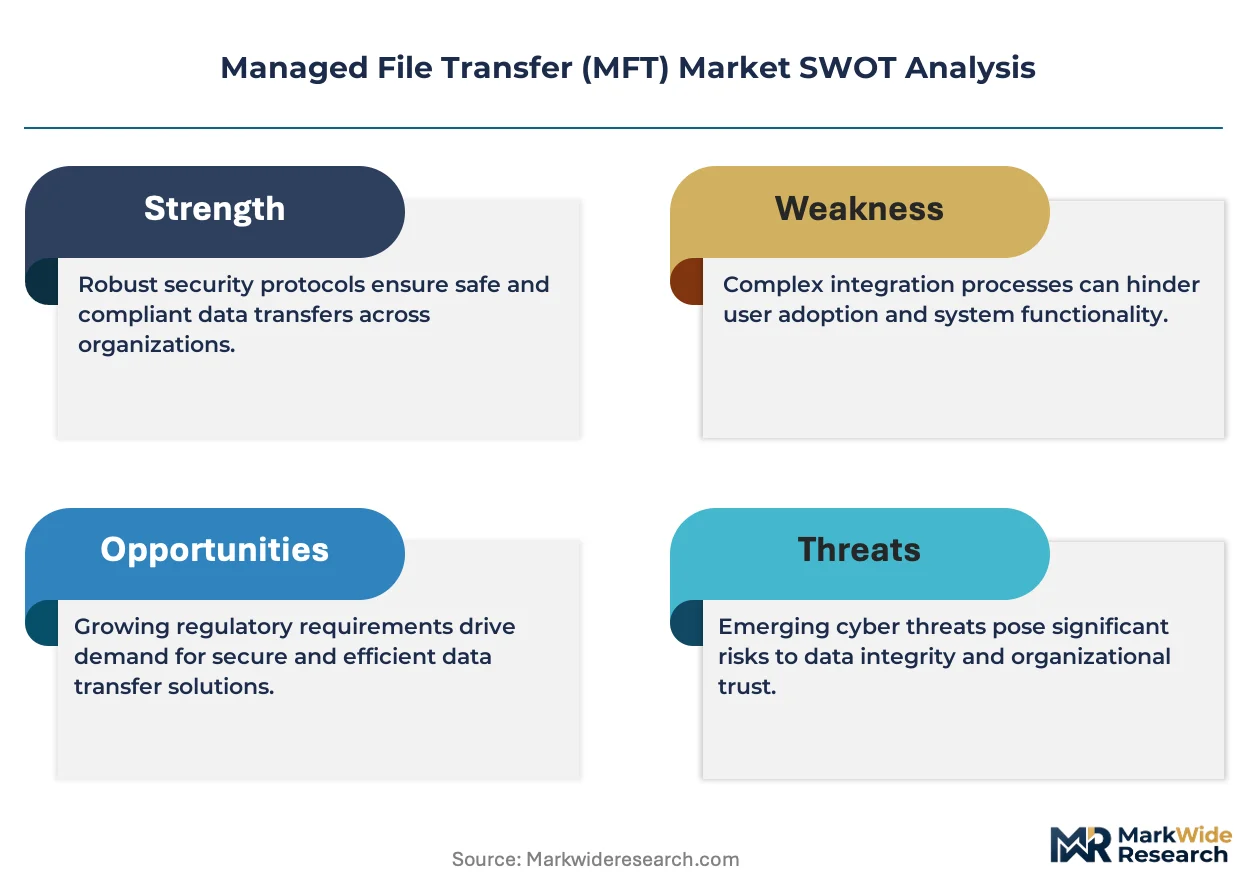
North American enterprise software vendors is restructuring supply capacity around zero-trust architecture and API-native delivery models. IBM sustains technology leadership through its Sterling File Gateway and Aspera portfolio, combining legacy protocol support with high-speed transfer optimization. Kiteworks differentiates through content-defined security policies that govern file access across regulated industries. Fortra anchors mid-market penetration with its GoAnywhere MFT platform, emphasizing workflow automation without heavy infrastructure investment.
Managed File Transfer denotes an enterprise-grade software solution that automates, secures, and audits the exchange of structured and unstructured data between systems, users, and external partners, typically supporting protocols such as SFTP, AS2, and HTTPS with end-to-end encryption and non-repudiation logging. Its primary commercial purpose centers on replacing ad-hoc file sharing with governed, traceable pipelines that satisfy compliance mandates while reducing operational risk. Cloud-Based deployment now captures the fastest expansion as organizations retire on-premise FTP servers in favor of elastic, API-driven SaaS architectures that shift capital expenditure to operational models. Within Service Type, Compliance Management commands premium pricing because audit trails and regulatory attestation functions embed directly into procurement evaluations, particularly at financial institutions and healthcare networks.
The US HIPAA Security Rule and the EU GDPR jointly shape product roadmaps by mandating encryption-at-rest, access logging, and breach notification capabilities as baseline features rather than optional modules. The US Federal Risk and Authorization Management Program and ISO 27001 certification further gate market access for vendors serving government and defense supply chains. Procurement teams must weigh protocol interoperability against emerging post-quantum cryptography standards that NIST is finalizing, as algorithm transitions will force refresh cycles across installed MFT infrastructure within the coming decade.
Market Dynamics
Zero-trust architecture mandates are forcing enterprises to dismantle perimeter-based file transfer models and rebuild around identity-verified, least-privilege data pipelines that treat every transfer as untrusted by default.
Growth Catalysts
- HIPAA Security Rule enforcement:US healthcare networks must deploy encrypted, auditable file transfer infrastructure for patient data exchange, accelerating compliance-driven procurement cycles at hospital systems and insurers.
- API-native SaaS architectures:Cloud migration by defense contractors and federal agencies under FedRAMP authorization requirements is displacing on-premise FTP servers with elastic, consumption-based delivery models.
- Post-quantum cryptography standards:NIST's algorithm finalization timeline is creating immediate upgrade urgency across financial services and government installations with long data-retention obligations.
Market Restraints
- Certificate management complexity:Multi-tenant cloud deployments require continuous rotation of X.509 credentials across thousands of endpoints, elevating operational overhead and failure-domain risk.
- Protocol interoperability debt:Legacy AS2 and SFTP implementations at manufacturing and logistics firms resist API migration without expensive gateway abstraction layers.
- Skills scarcity in cryptographic engineering:Enterprise IT organizations lack personnel fluent in TLS 1.3 configuration, HSM integration, and key-escrow procedures, slowing production deployments.
Strategic Opportunities
- Underpenetrated healthcare networks in Germany:GDPR Article 32 compliance requirements at university hospitals and regional health insurers create demand for managed services with embedded legal attestation.
- Convergence of MFT with data loss prevention:Integrated platforms combining transfer governance with content inspection are capturing budget from separate DLP procurement lines at European financial institutions.
- Channel partner certification programs:Vendor investment in specialized reseller accreditation for HIPAA and ISO 27001 consulting is unlocking mid-market accounts without direct sales investment.
Industry Challenges
- FedRAMP authorization timelines:Cloud providers face 12-18 month assessment cycles with third-party assessment organizations, delaying federal market entry and consuming substantial compliance resources.
- Integration friction with ERP systems:SAP and Oracle environments require custom adapter development for native MFT workflow triggers, extending implementation schedules and professional services dependency.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Managed File Transfer (MFT) Market |
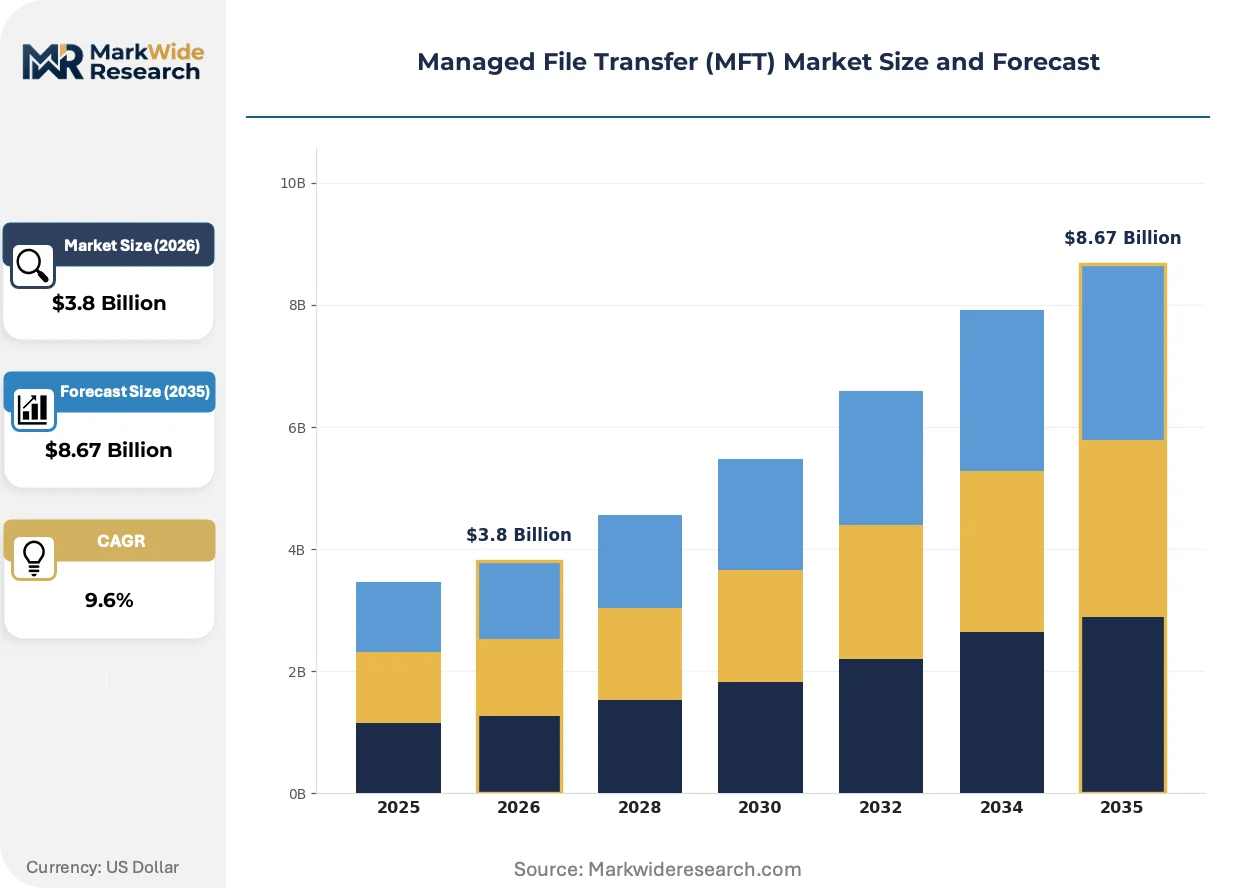
| Market Size in 2026 | $3.8 Billion |
| Market Size in 2035 | $8.67 Billion |
| CAGR (2026 – 2036) | 9.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premise, Cloud-Based, Hybrid, SaaS Technology: FTP, SFTP, AS2, HTTPS End User: Financial Services, Healthcare, Retail, Manufacturing Service Type: File Transfer, Data Integration, Workflow Automation, Compliance Management |
| Companies Covered | Axway, Kiteworks, Fortra (GoAnywhere MFT), Coviant Software (Diplomat MFT), South River Technologies (Titan MFT), Progress Software (MOVEit), Couchdrop, MASV, IBM (Sterling File Gateway and Aspera), Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Managed File Transfer (MFT) Market Shifts & Advancements
Artificial intelligence is embedding into file transfer operations through automated anomaly detection and predictive failure remediation, compressing mean-time-to-resolution and reducing security operations center alert fatigue.
Machine learning-based threat detection is integrating behavioral analytics that establish baseline transfer patterns and flag deviations indicating credential compromise or data exfiltration. Financial institutions and payment processors are deploying these capabilities at scale, with models trained on petabytes of transaction metadata. The technology is integrating security operations and data governance functions that previously operated in separate organizational silos.
GDPR Article 32 and Article 33 breach notification requirements are mandating encryption-at-rest and 72-hour incident reporting capabilities as standard procurement specifications rather than premium add-ons. European data protection authorities have issued fines exceeding regulatory thresholds for inadequate transfer logging, creating direct financial consequences for non-compliance. Healthcare and banking verticals in France, Germany, and the Netherlands are responding with consolidated platform evaluations that privilege vendors offering pre-configured compliance templates.
Subscription-based consumption models are displacing perpetual license arrangements as procurement teams prioritize operational expenditure flexibility and vendor-managed infrastructure maintenance. Mid-market manufacturing and professional services firms are abandoning capital-intensive on-premise deployments in favor of multi-tenant SaaS instances with API-driven provisioning. This pattern is most visible in the United States, where federal contractor pricing structures and state-level procurement frameworks have accelerated cloud-first mandates.
Managed File Transfer (MFT) Market Segmentation
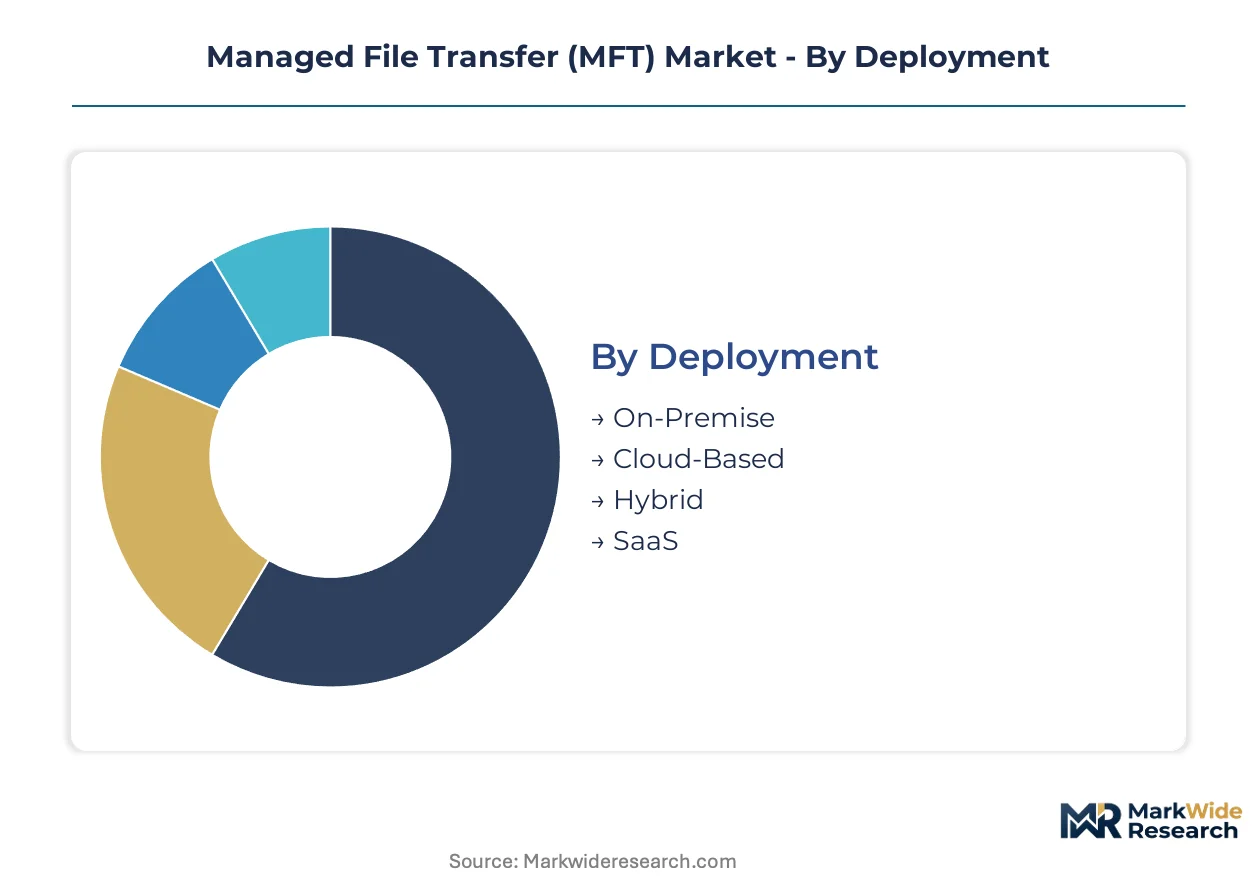
Managed File Transfer procurement decisions hinge on infrastructure maturity, regulatory exposure, and integration complexity. Segmentation reveals how buyers trade off control against operational agility across deployment models, transport protocols, and service bundles.
Deployment:
Cloud-native elasticity is displacing capital-intensive infrastructure commitments.
- On-Premise:Organizations retain full hardware control with dedicated server clusters behind corporate firewalls. Defense contractors and classified federal installations in the United States favor this model for air-gapped security compliance.
- Cloud-Based:Multi-tenant architectures deliver elastic throughput scaling without data center overhead. Healthcare networks migrating off legacy FTP servers are consolidating onto these platforms to satisfy HIPAA audit requirements.
- Hybrid:Split configurations route sensitive transfers through on-premise nodes while pushing bulk operations to cloud endpoints. Manufacturing supply chains with mixed supplier security postures deploy this architecture to bridge trust boundaries.
- SaaS:Fully managed instances abstract all infrastructure maintenance to vendor operations teams. Mid-market professional services firms in Germany are adopting this model to convert capital expenditure into predictable operational budgets.
Cloud-Based leads on scale; SaaS leads on momentum.
Technology:
Protocol selection determines encryption strength, transfer velocity, and partner interoperability.
- FTP:Unencrypted legacy transport persists in internal networks where speed outweighs security. Retail inventory synchronization systems still rely on these channels for high-volume batch operations.
- SFTP:SSH-encrypted tunnels protect credentials and payload data in transit. Financial services clearinghouses in France mandate this protocol for SWIFT-adjacent file movements.
- AS2:Drummond-certified implementations provide non-repudiation receipts for B2B transactions. Healthcare EDI networks exchanging HIPAA 837 claim files require AS2 for trading partner accountability.
- HTTPS:RESTful API transfers leverage TLS 1.3 for browser-compatible security without dedicated client software. E-commerce payment processors are standardizing on this protocol for mobile-first integration patterns.
SFTP dominates installed base; HTTPS climbs the fastest on API-native adoption.
End User:
Vertical-specific compliance regimes reshape feature prioritization across buyer categories.
- Financial Services:Trading floors and payment processors demand microsecond latency with immutable audit trails. PCI-DSS Level 1 merchants in the United States drive premium pricing for tokenized transfer paths.
- Healthcare:Hospital systems and insurers require PHI encryption with automated breach notification workflows. GDPR Article 32 enforcement at Dutch university hospitals is accelerating platform consolidation.
- Retail:Omnichannel inventory synchronization and supplier onboarding dominate procurement criteria. Seasonal demand spikes push these buyers toward consumption-based pricing models.
- Manufacturing:Shop-floor integration with ERP systems and IoT device firmware distribution create hybrid edge-to-cloud requirements. German automotive suppliers prioritize AS2 interoperability for just-in-sequence supply chains.
Healthcare leads on compliance-driven replacement cycles; Financial Services leads on transaction volume density.
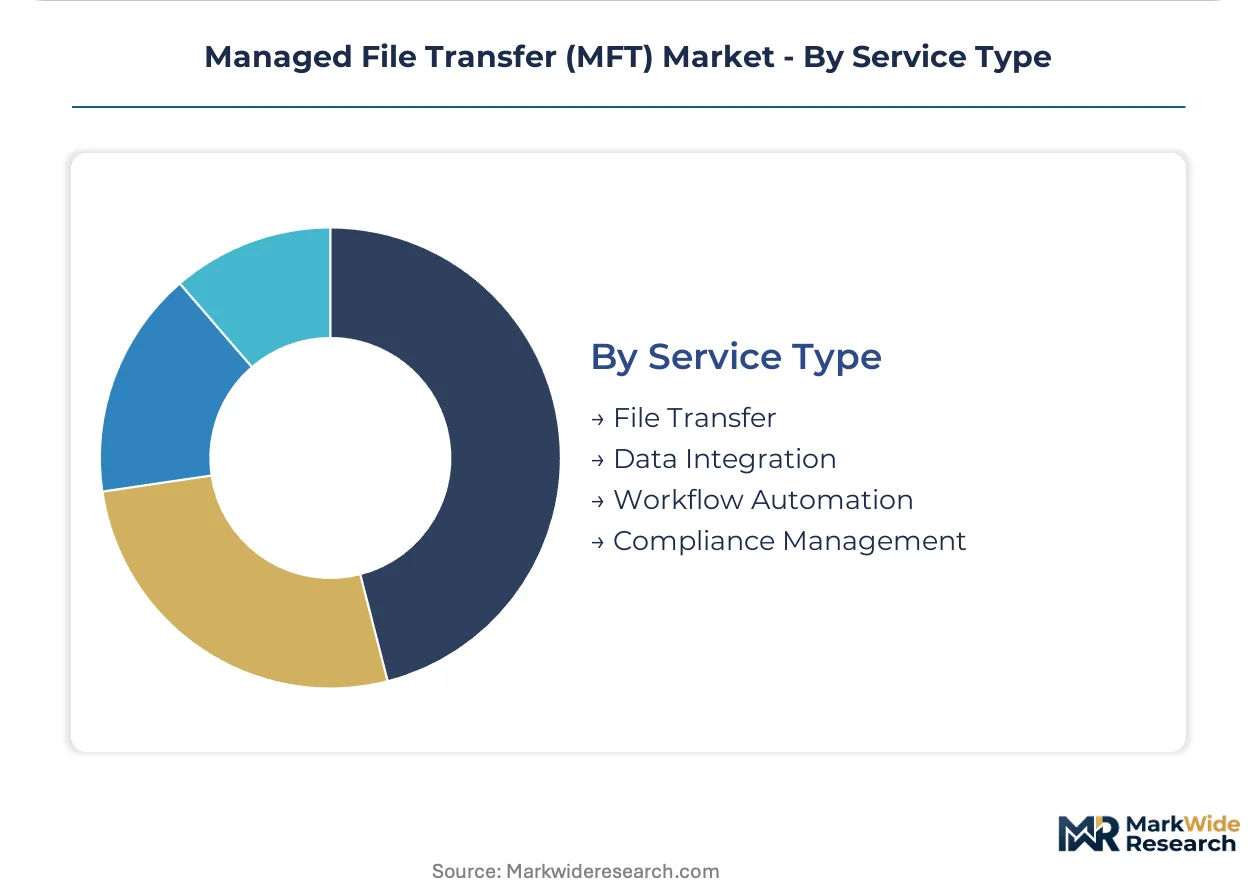
Service Type:
Buyers increasingly bundle governance capabilities rather than procuring point solutions.
- File Transfer:Core payload movement with protocol abstraction and checkpoint restart. Logistics coordinators at freight forwarders rely on these functions for multi-gigabyte manifest exchanges.
- Data Integration:Schema transformation and mapping between disparate application formats. Oracle and SAP environments in manufacturing require these adapters for native workflow triggers.
- Workflow Automation:Conditional routing, exception handling, and SLA monitoring without custom code. Insurance claims processors deploy these capabilities to compress straight-through processing rates.
- Compliance Management:Embedded audit trails, retention policies, and regulatory attestation templates. GDPR and HIPAA procurement evaluations now treat these features as baseline requirements rather than premium modules.
File Transfer anchors revenue; Compliance Management gains share fastest on regulatory enforcement tightening.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Regulatory-arbitrage dynamics are reshaping procurement geography as compliance cost differentials push healthcare and financial services buyers toward jurisdictions with clearer certification pathways. The United States, Germany, United Kingdom, France, and Netherlands concentrate MFT deployment velocity due to overlapping HIPAA, GDPR, and FedRAMP enforcement timelines.
United States
Federal contractors and defense supply chains drive cloud-first mandates under FedRAMP authorization requirements. HIPAA Security Rule enforcement at hospital systems accelerates encrypted file transfer procurement cycles. Healthcare networks in Boston and federal agencies in Washington D.C. metro are retiring legacy FTP infrastructure for API-native SaaS architectures.
Germany
University hospitals and regional health insurers face GDPR Article 32 compliance deadlines for patient data encryption. The country's national data protection regulator intensifies audit scrutiny on transfer logging capabilities. Automotive suppliers in Bavaria prioritize AS2 interoperability for just-in-sequence supply chain synchronization with cloud-hybrid deployments.
United Kingdom
Financial services clearinghouses demand microsecond latency with immutable audit trails for SWIFT-adjacent file movements. The Information Commissioner's Office enforces breach notification timelines that compress vendor evaluation cycles. London-based payment processors are consolidating separate DLP and MFT procurement lines into integrated governance platforms.
France
Healthcare verticals respond to CNIL enforcement actions with consolidated platform evaluations privileging pre-configured compliance templates. GDPR Article 33 fine thresholds create direct financial consequences for inadequate transfer logging. Banking clusters in Paris and pharmaceutical manufacturers in Lyon drive premium pricing for tokenized transfer paths with embedded legal attestation.
Netherlands
Dutch university hospitals accelerate platform consolidation under GDPR Article 32 enforcement for PHI encryption with automated breach notification workflows. The country's data protection authority mandates 72-hour incident reporting as standard procurement specification. Amsterdam-based logistics coordinators deploy multi-gigabyte manifest exchanges through consumption-based SaaS pricing models.
Managed File Transfer (MFT) Market Competitive Landscape
United States vendors anchor the enterprise tier with FedRAMP-authorized cloud portfolios; European specialists hold compliance-intensive segments through GDPR-attested managed services. Market structure tilts toward consolidation as API-native delivery models absorb mid-market accounts previously served by on-premise installers. Three archetypes dominate: legacy protocol consolidators, zero-trust cloud native platforms, and workflow automation specialists. Competitive moves center on channel partner certification programs for HIPAA and ISO 27001 consulting, plus convergence plays bundling transfer governance with data loss prevention.
Within the legacy-to-cloud transition tier, IBM and Fortra exemplify divergent scale strategies. IBM anchors enterprise installations through protocol breadth and high-speed transfer optimization. Fortra occupies a position emphasizing workflow automation without heavy infrastructure investment. Kiteworks sits within the content-defined security policy segment, representing vendors that govern file access across regulated industries through embedded legal attestation. These three illustrate how vendor archetypes map to buyer infrastructure maturity and regulatory exposure.
| Leading Market Players |
|---|
| Axway |
| Kiteworks |
| Fortra (GoAnywhere MFT) |
| Coviant Software (Diplomat MFT) |
| South River Technologies (Titan MFT) |
| Progress Software (MOVEit) |
| Couchdrop |
| MASV |
| IBM (Sterling File Gateway and Aspera) |
| Others |
Supply & Pricing Matrix
FedRAMP authorization timelines and HIPAA Security Rule attestation requirements gate qualified supply for federal healthcare deployments, concentrating premium-tier pricing power among vendors with pre-certified cloud infrastructure. Buyers face 12-18 month procurement cycles for compliant SaaS instances, elevating switching costs and sustaining margin premiums for accredited providers.
Pricing Analysis
Direct-to-enterprise discounts dominate federal contractor pricing, while channel partners extract 15-25 point spreads on mid-market healthcare deployments. Subscription-based SaaS tiers stratify across consumption bands, with HIPAA-compliant managed services commanding premiums over standard cloud instances. Cost compression in the legacy on-premise segment intensifies as hospitals accelerate FTP server retirements. Price-sensitive mid-market manufacturing buyers favor consumption-based models, while defense contractors demonstrate lowest sensitivity due to mandate-driven replacement cycles.
Supply Chain Analysis
Domestic-content requirements under FedRAMP authorization reshape sourcing toward US-based data center operators and sovereign cloud instances. Software development concentrates in the United States, Germany, and Israel, with cryptographic engineering talent anchoring R&D placement. Cloud infrastructure rests on hyperscaler compute and specialized HSM hardware from limited qualified vendors. Single-source vulnerability in FIPS 140-2 certified module supply creates procurement bottlenecks. Distribution runs through direct enterprise sales for federal accounts and specialized healthcare IT resellers for hospital networks.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Geographic arbitrage between US FedRAMP compliance costs and European GDPR attestation overhead creates margin expansion opportunities for vendors with dual-certification infrastructure. Regulatory divergence allows pricing premiums in the higher-compliance jurisdiction.
For Market Incumbents: Deploy post-quantum cryptography migration services as a retention lever against cloud-native challengers. Incumbents should anchor enterprise accounts through protocol breadth investments while accelerating API abstraction layers for legacy AS2 installations. Certificate management automation and embedded compliance templates defend against workflow automation specialists encroaching from below. For New Entrants and Emerging Players: GDPR Article 32 enforcement in Germany opens a window for managed services with embedded legal attestation at university hospitals. New entrants should target underpenetrated regional health insurers in Bavaria and Baden-Württemberg with SaaS-native deployment models. Channel partner certification for ISO 27001 consulting accelerates mid-market access without direct sales infrastructure. For Investors and Strategic Acquirers: Valuations sit cheapest among hybrid-deployment specialists with healthcare vertical concentration. Long-term viability hinges on quantum-safe algorithm transition capabilities and FedRAMP authorization pipeline depth. Acquisition targets should demonstrate pre-built SAP and Oracle adapters. The signal to watch is NIST algorithm standardization announcements forcing refresh cycle timing.| Strategic Initiative | Industry Significance |
|---|---|
| Post-Quantum Cryptography Migration | NIST algorithm finalization forces infrastructure refresh across financial and federal installations. |
| API-Native SaaS Expansion | Elastic consumption models displace capital-intensive on-premise deployments at mid-market healthcare networks. |
| Channel Partner Certification Investment | Specialized reseller accreditation for HIPAA consulting unlocks hospital system accounts without direct sales overhead. |
| Convergence with Data Loss Prevention | Integrated governance platforms capture budget consolidation at European financial institutions under GDPR enforcement. |
| FedRAMP Authorization Acceleration | Third-party assessment organization pre-certification reduces federal market entry timelines from 18 to 12 months. |
Research Methodology
Coverage spans North America, Western Europe, and Asia-Pacific, with primary inputs from each region balanced against secondary validation. The research combines structured interviews with CISOs, healthcare IT procurement directors, federal contracting officers, and MFT platform engineers with secondary analysis of FedRAMP authorization databases, HIPAA breach notification filings, and hyperscaler compliance disclosure documents. Bottom-up deployment counts triangulate against top-down vendor revenue estimates across cloud, on-premise, and hybrid delivery models.
Rate-of-change decomposition separates volume expansion from pricing evolution across the projection horizon. The analytical framework models deployment model, organization size, vertical regulatory exposure, integration complexity, and regional certification pattern as core segmentation dimensions. CAGRs derive from fitted trend extrapolation adjusted for mandate-driven replacement cycle timing. Forecast inputs incorporate FedRAMP pipeline velocity, GDPR fine enforcement patterns, and NIST post-quantum standardization timelines.
Forecast precision tightens around the base case; tail outcomes carry wider variance under accelerated quantum computing breakthroughs or federal procurement freeze scenarios. Projections reflect documented assumptions regarding compliance timeline adherence and cloud migration velocity. Within these boundaries, the analytical envelope holds.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Digital Solutions
Online Voting System Market
Digital Solutions
Dataops Platform Market
Digital Solutions
Web Content Management Market
Digital Solutions
Digital Rights Management (DRM) Market
Digital Solutions
Global BYOD and Enterprise Mobility Market
Digital Solutions
Global Transport Management Software Market
Digital Solutions
Asia-Pacific Digital Pen Market
Digital Solutions
Virtual Hiring Tools Market
Digital Solutions
Global Digital Experience Management Market
Digital Solutions
Precision Agriculture Software Market
Digital Solutions
Mobile Resource Management Solutions Market
Digital Solutions
Community Engagement Software Market
Digital Solutions
Global Tracking As a Service Market
Digital Solutions
Webrtc Market
Digital Solutions
Digital Signage Services Market
Digital Solutions
Europe Warranty Management System Market