
 Global Network Security Software Market | 2026-2036
Global Network Security Software Market Size, Share, and Industry Trends Forecast 2026-2036
Global Network Security Software Market Foresight
Multi-source procurement of network security software is hardening across enterprise IT departments wary of supply-chain concentration risk. Palo Alto Networks leverages its platform consolidation strategy to capture bundled firewall and SD-WAN contracts. Fortinet sustains competitive pressure through custom ASIC development that lowers per-packet inspection costs. Zscaler navigates the shift from perimeter-based hardware to cloud-native secure access by positioning its zero-trust architecture as a replacement for legacy VPN concentrators.
Network security software encompasses programs and services that inspect, filter, and log traffic traversing organizational networks, typically operating at throughput thresholds exceeding 100 Gbps in carrier-grade deployments and integrating deep packet inspection with behavioral analytics. Its primary purpose is to enforce access policies, detect anomalous payloads, and maintain confidentiality across distributed endpoints. Firewall solutions anchor the largest revenue pool as perimeter hardening remains non-negotiable for regulated industries, while cloud deployment models represent the fastest-expanding segment as SaaS migration outpaces data-center refresh cycles. Hybrid architectures capture concentrated margin pools where managed service providers bundle consulting with ongoing policy tuning.
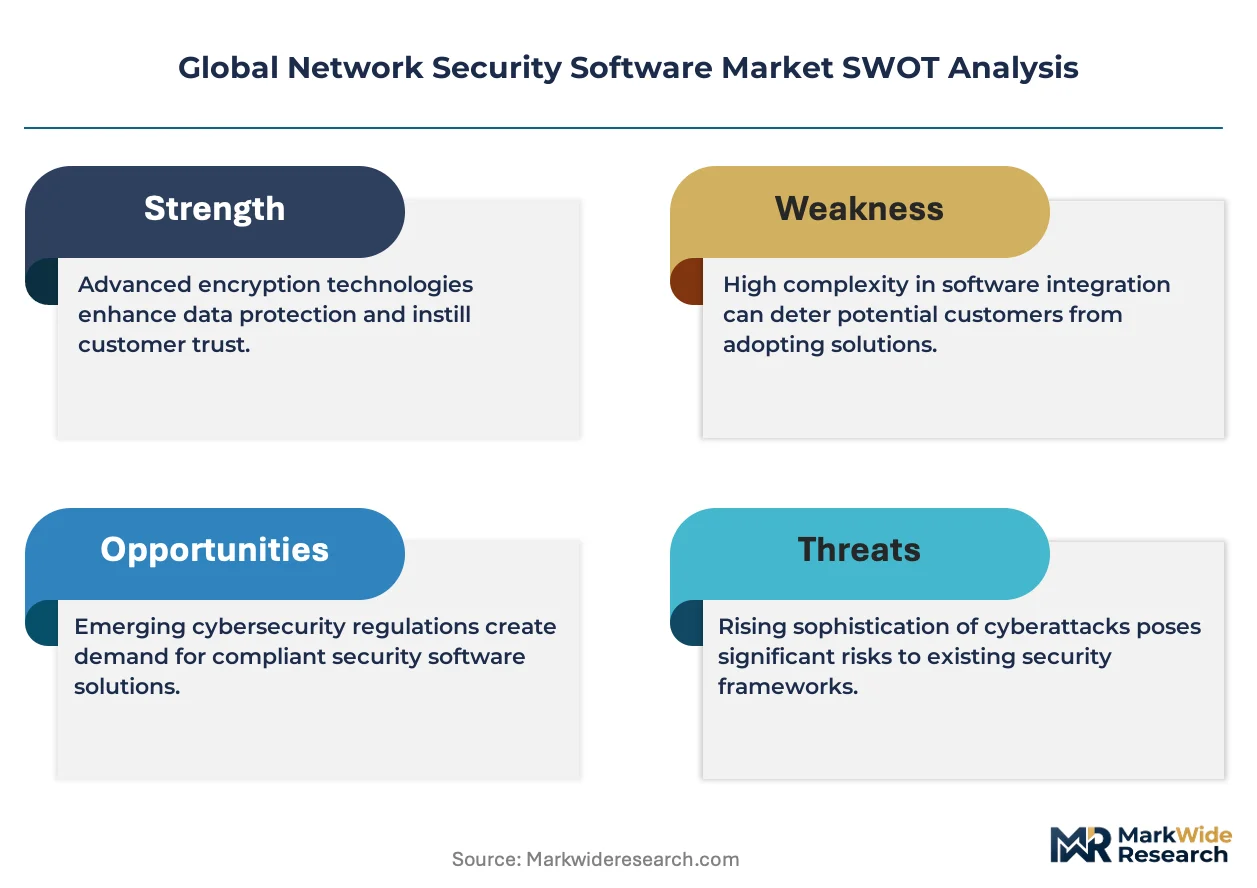
FDA cybersecurity guidance for networked medical devices, the EU AI Act's risk classification of autonomous threat-response systems, and Japan's METI critical infrastructure standards collectively elevate baseline security requirements and expand addressable demand. China's NMPA and GB standards for connected healthcare equipment impose additional localization mandates that fragment vendor certification pathways. Stakeholders must monitor divergence between sovereign data-residency rules and cloud-provider regions when architecting distributed security stacks.
Market Dynamics
Zero-trust architecture mandates are compressing procurement cycles as financial services CISOs retire perimeter-based VPN concentrators in favor of continuous verification models. Sovereign data residency rules across Germany, Japan, and the United States are fragmenting vendor certification pathways and forcing multi-cloud security stack duplication.
Growth Catalysts
- EU NIS2 Directive:Critical infrastructure operators must deploy incident response capabilities and supply-chain risk management by October 2024, expanding managed security service contracts.
- Medical device connectivity:FDA cybersecurity guidance for networked hospital equipment mandates pre-market submission of software bills of materials, driving embedded security module procurement.
- Custom ASIC economics:Hardware-optimized deep packet inspection at sub-microsecond latency enables 400 Gbps firewall deployments in carrier networks previously cost-prohibitive.
Market Restraints
- Silicon supply concentration:Advanced networking ASIC fabrication depends on TSMC's 7nm and 5nm capacity in Taiwan, creating geopolitical exposure for firewall hardware refresh cycles.
- Skills scarcity:Zero-trust architecture deployment requires cross-functional expertise spanning identity management, cloud networking, and behavioral analytics that exceeds current workforce supply.
- Regulatory fragmentation:China's GB standards for data localization and Russia's sovereign internet requirements force product variants that dilute engineering resources.
Strategic Opportunities
- India's digital infrastructure:Data center expansion under the MeitY cloud policy creates demand for software-defined perimeter solutions without legacy hardware displacement costs.
- Converged SASE platforms:Integration of SD-WAN, cloud access security broker, and zero-trust network access into unified policy engines reduces vendor consolidation friction.
- Japan METI critical infrastructure standards:Mandatory security monitoring for electricity, gas, and water utilities opens recurring revenue managed detection and response contracts.
Industry Challenges
- Certificate lifecycle management:Machine-to-machine authentication at scale requires automated public key infrastructure rotation that most enterprises have not operationalized.
- Multi-cloud policy consistency:Security posture drift between AWS, Azure, and Google Cloud environments creates compliance audit failures despite individual control maturity.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Network Security Software Market |
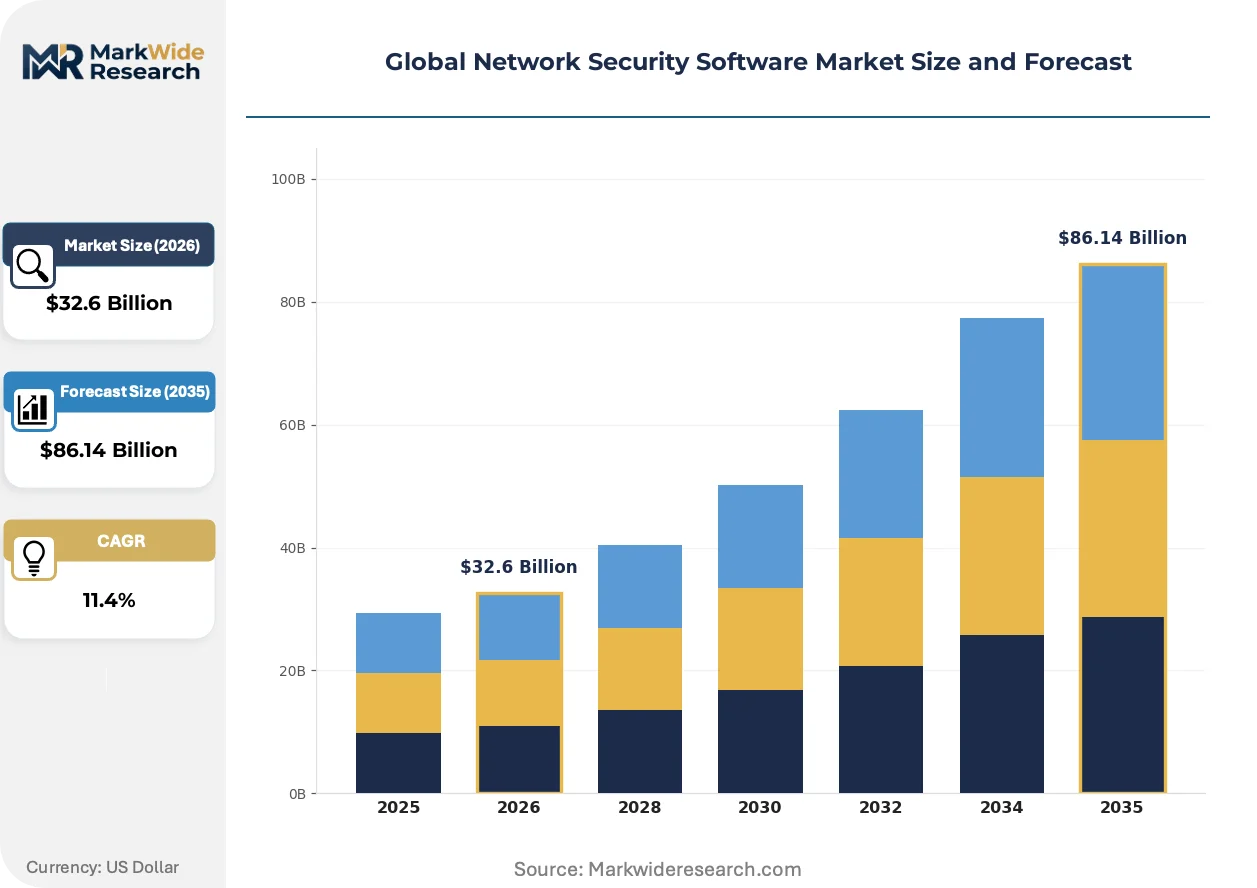
| Market Size in 2026 | $32.6 Billion |
| Market Size in 2035 | $86.14 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Firewall, Intrusion Detection System, VPN, Antivirus Deployment Model: On-Premises, Cloud, Hybrid, Managed End User: SMEs, Enterprises, Government, Educational Institutions Service Type: Consulting, Implementation, Support, Training |
| Companies Covered | Palo Alto Networks Inc., Fortinet Inc., Cisco Systems Inc., Check Point Software Tech Ltd., Trend Micro Inc., Zscaler Inc., Cloudflare Inc., Akamai Technologies Inc., Juniper Networks Inc., Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Network Security Software Market Shifts & Advancements
Artificial intelligence is compressing threat detection latency from hours to seconds while regulatory mandates harden baseline security requirements across critical infrastructure sectors. Vendor consolidation around platform architectures is displacing point-solution procurement.
Extended detection and response platforms are automating correlation across endpoint, network, and identity telemetry to reduce mean-time-to-containment. Financial services security operations centers in London and Singapore are deploying these systems at enterprise scale. The technology is automating tier-1 analyst triage workflows and compressing security operations center staffing requirements.
The EU AI Act's risk classification framework subjects autonomous threat-response systems to conformity assessment and CE marking obligations. Security vendors must document training data provenance and algorithmic transparency for high-risk applications. Healthcare and transportation CISOs in France and Germany are delaying procurement of AI-enabled deception technology pending certification clarity.
Enterprise buyers are unbundling hardware procurement from managed service contracts, favoring subscription-based security-as-a-service models with embedded professional services. Regional system integrators in São Paulo and Dubai are capturing margin pools previously held by multinational distributors. This shift is most visible in mid-market manufacturing verticals with limited in-house security engineering capacity.
Global Network Security Software Market Segmentation
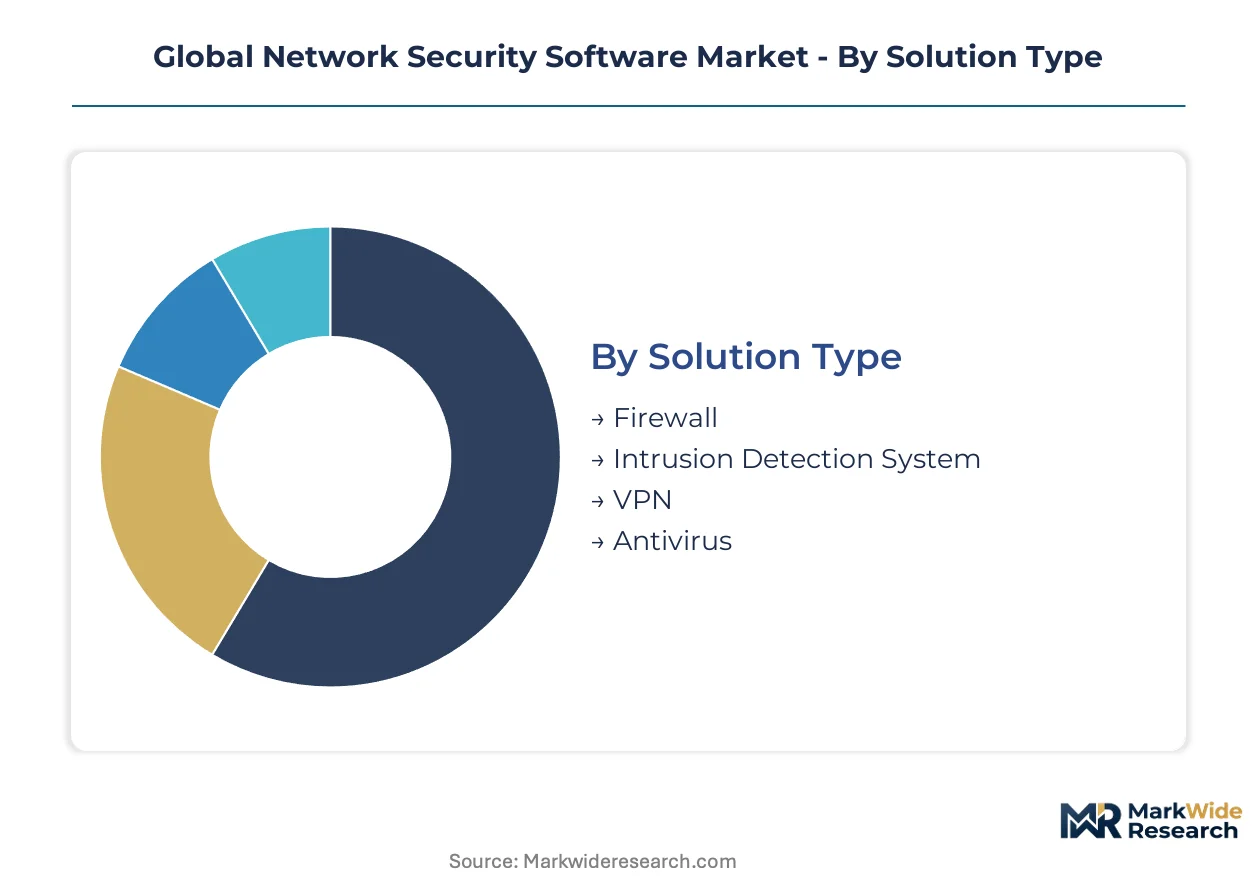
Network security software procurement patterns diverge sharply across organizational scale and infrastructure maturity. Understanding these segment boundaries clarifies where platform consolidation displaces point solutions versus where specialized tooling retains pricing power.
Solution Type:
Firewall refresh cycles dominate enterprise capital allocation as perimeter hardening remains non-negotiable for regulated industries.
- Firewall:Next-generation firewalls integrate deep packet inspection with application-layer visibility at throughput thresholds exceeding 100 Gbps. Financial services firms in Germany and the United States are accelerating replacement of legacy stateful inspection appliances with zero-trust-capable platforms.
- Intrusion Detection System:Network-based IDS analyzes traffic patterns against behavioral baselines to flag anomalous payloads without inline blocking. Healthcare networks in Japan deploy these systems to satisfy METI critical infrastructure monitoring mandates without disrupting surgical robot connectivity.
- VPN:Secure remote access tunnels are experiencing displacement pressure as zero-trust network access architectures retire perimeter-based concentrators.
- Antivirus:Signature-based endpoint protection is ceding share to extended detection and response platforms with machine-learning classification.
Firewall sits at the top of the volume ranking, with intrusion detection systems climbing the fastest.
Deployment Model:
Cost tier structures separate capital-intensive hardware ownership from operational expenditure models favored by mid-market buyers.
- On-Premises:Physical appliance deployment retains dominance in carrier networks requiring sub-microsecond latency for 400 Gbps inspection. Sovereign data residency rules in Germany and Japan compel government agencies to maintain localized hardware stacks.
- Cloud:SaaS-delivered security services eliminate data-center refresh cycles and enable elastic capacity scaling. India's MeitY cloud policy is accelerating software-defined perimeter adoption without legacy hardware displacement costs.
- Hybrid:Split architectures capture concentrated margin pools where managed service providers bundle consulting with ongoing policy tuning across on-premises and cloud footprints.
- Managed:Fully outsourced security operations transfer staffing risk to specialized providers, appealing to educational institutions with limited in-house engineering capacity.
On-premises retains the largest installed base, though cloud deployment is expanding most quickly.
End User:
Application maturity varies dramatically between centralized procurement in government and fragmented purchasing across small and medium enterprises.
- SMEs:Resource-constrained organizations favor bundled security-as-a-service subscriptions with embedded professional services over discrete product procurement.
- Enterprises:Large organizations are consolidating vendor rosters around platform architectures that unify firewall, SD-WAN, and zero-trust network access under single policy engines.
- Government:Public sector procurement is hardening under the EU NIS2 Directive's incident response mandates, expanding managed security service contracts for critical infrastructure operators.
- Educational Institutions:Universities and research networks face unique exposure from bring-your-own-device policies and open network architectures that complicate access control standardization.
Enterprises command the largest contract values, with government segment showing steepest expansion trajectory.
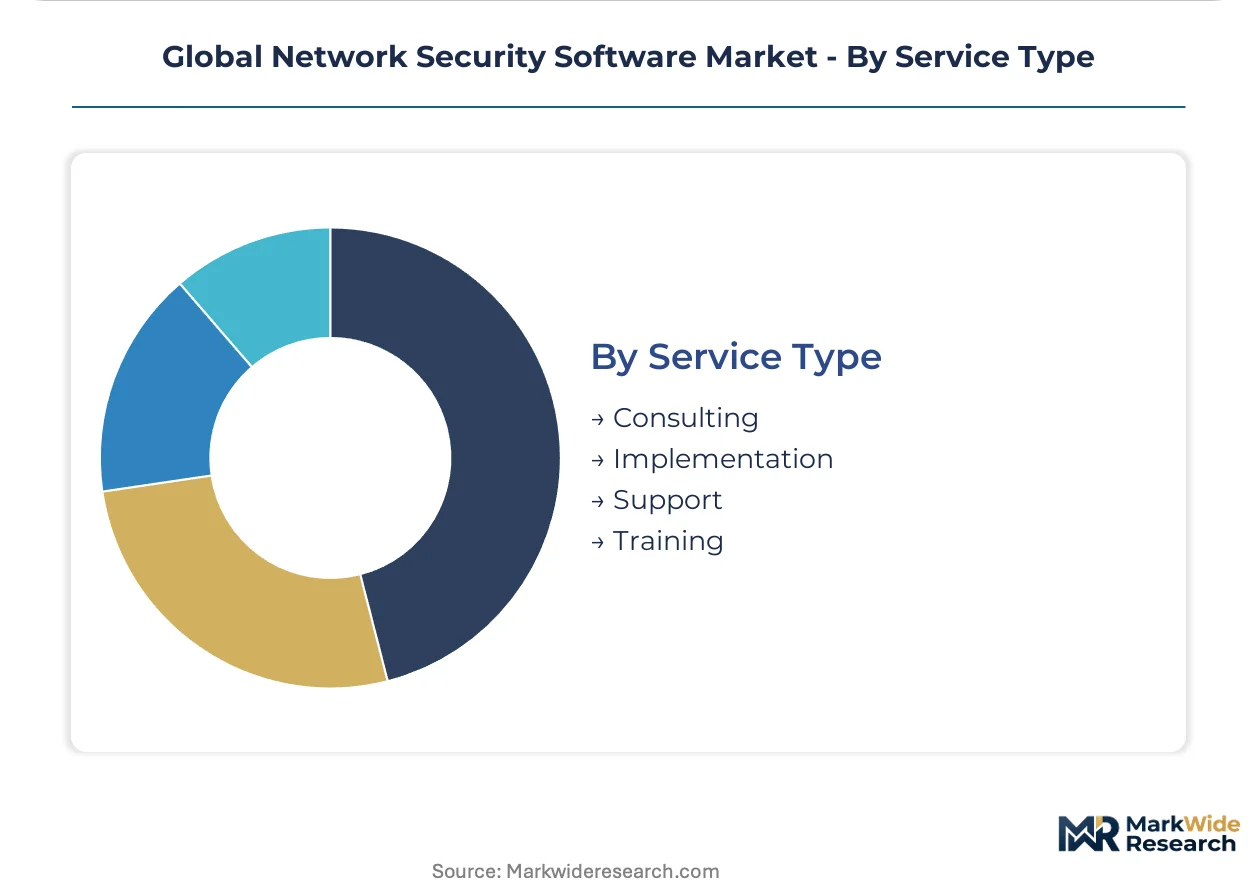
Service Type:
Customer type determines whether professional services attach as embedded subscription components or standalone consulting engagements.
- Consulting:Architecture design and compliance readiness assessments command premium pricing where zero-trust transformation requires cross-functional expertise spanning identity management and cloud networking.
- Implementation:Deployment services bridge the gap between product procurement and operational security outcomes, particularly for certificate lifecycle management automation that most enterprises have not operationalized.
- Support:Tiered response commitments differentiate vendor offerings, with 24/7 coverage mandatory for financial services security operations centers.
- Training:Workforce development addresses acute skills scarcity in behavioral analytics and multi-cloud policy consistency.
Implementation services generate the highest attach rates, with consulting gaining share fastest.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The San Francisco Bay Area anchors global network security software development, housing headquarters for multiple platform vendors and venture capital firms financing zero-trust innovation. Sovereign data residency mandates are fragmenting procurement patterns across Germany, Japan, and the United States as financial services CISOs accelerate vendor diversification.
United States
Financial services firms in New York and Chicago are retiring legacy VPN concentrators for zero-trust architectures at unprecedented velocity. The SEC cybersecurity disclosure rules finalized in 2023 mandate incident reporting within four business days, compressing procurement cycles for managed detection and response services. Silicon Valley clusters in Santa Clara and San Mateo counties concentrate platform engineering talent developing converged SASE offerings.
Germany
Automotive manufacturers in Stuttgart and Munich are embedding network security modules into connected vehicle platforms under EU NIS2 Directive pressure. Germany's BSI federal cybersecurity agency mandates baseline protection for critical infrastructure operators, expanding managed security service contracts for utilities and transport networks. Frankfurt's financial district drives demand for sub-microsecond latency inspection engines handling high-frequency trading flows.
Japan
Tokyo-based financial institutions are deploying cloud-native secure access solutions to satisfy METI critical infrastructure standards for banking and securities sectors. The country's cybersecurity basic law requires designated infrastructure operators to maintain continuous monitoring capabilities, opening recurring revenue contracts for managed detection and response providers. Osaka's manufacturing belt generates specialized demand for industrial control system segmentation without disrupting operational technology networks.
India
Bangalore's technology services corridor is absorbing software-defined perimeter solutions as multinational corporations establish captive development centers under MeitY cloud policy guidelines. Mumbai's financial district drives procurement of zero-trust network access for hybrid workforce models spanning domestic and offshore operations. Hyderabad's data center cluster is expanding under sovereign data localization requirements, creating greenfield opportunities without legacy hardware displacement costs.
United Kingdom
London's security operations centers are automating tier-1 analyst workflows using extended detection and response platforms to address acute skills scarcity in behavioral analytics. The UK National Cyber Security Centre's assurance schemes for network monitoring products create certification barriers that favor established platform vendors over point-solution specialists. Edinburgh's fintech cluster generates specialized demand for API security integration with open banking infrastructure.
Global Network Security Software Market Competitive Landscape
Global majors compete with regional champions across platform consolidation versus point-solution specialization. The vendor base organizes into three tiers: integrated platform providers unifying firewall, SD-WAN, and zero-trust access; hardware-optimized specialists leveraging custom silicon for carrier-grade throughput; and cloud-native pure-plays displacing perimeter appliances with SaaS delivery models. Dominant competitive moves include strategic partnerships between networking vendors and managed service providers, plus vertical integration into custom ASIC development to lower per-packet inspection economics.
Among platform-consolidation specialists, Palo Alto Networks Inc. and Fortinet Inc. occupy positions exemplifying the integrated architecture archetype, while Zscaler Inc. represents the cloud-native displacement model. These three entities anchor distinct strategic vectors within the competitive matrix—on-premises platform extension, hardware-optimized performance, and perimeter-replacement SaaS delivery—each capturing margin pools aligned with customer infrastructure maturity and regulatory posture.
| Leading Market Players |
|---|
| Palo Alto Networks Inc. |
| Fortinet Inc. |
| Cisco Systems Inc. |
| Check Point Software Tech Ltd. |
| Trend Micro Inc. |
| Zscaler Inc. |
| Cloudflare Inc. |
| Akamai Technologies Inc. |
| Juniper Networks Inc. |
| Others |
Supply & Pricing Matrix
TSMC wafer pricing indices cascade through firewall hardware manufacturing, compressing margins for appliance-dependent vendors while amplifying pricing power for cloud-native software providers insulated from silicon cycle volatility.
Pricing Analysis
Input-cost pass-through from advanced networking ASIC fabrication concentrates in carrier-grade hardware tiers, where 7nm and 5nm wafer costs feed into three-tier pricing structure across premium, standard, and economy levels. Certification grade under EU NIS2 Directive and Japan METI standards differentiates premium tiers, while volume scale drives economy pricing for mid-market manufacturing buyers. Pricing pressure stems from skills scarcity in zero-trust deployment, forcing vendors to embed professional services at compressed margins. SMEs exhibit highest price sensitivity, favoring subscription-based security-as-a-service models over capital-intensive appliance procurement.
Supply Chain Analysis
Direct-to-OEM channels handle hyperscale buyer demand for 400 Gbps inspection engines, while value-added distributors serve mid-market segments requiring implementation support. Taiwan, South Korea, and the United States anchor advanced ASIC fabrication capacity, with silicon supply concentration creating geopolitical exposure for hardware refresh cycles. Deep packet inspection chipsets, high-speed memory modules, and specialized cooling assemblies constitute critical component dependencies. Single-source vulnerability at TSMC's foundry operations represents the dominant structural risk. Distribution runs through managed service providers bundling consulting with ongoing policy tuning, particularly in Germany and Japan where sovereign data residency rules compel localized deployment.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The Global Network Security Software Market operates as a stable compounder, with regulatory mandates across the EU NIS2 Directive, Japan METI standards, and FDA cybersecurity guidance generating durable procurement tailwinds irrespective of macroeconomic cycles.
For Market Incumbents: Deploy platform consolidation as the primary defensive lever. Palo Alto Networks and Fortinet capture bundled firewall and SD-WAN contracts by unifying policy engines, while custom ASIC development lowers per-packet inspection costs to defend against cloud-native displacement. Incumbents must monitor Zscaler's perimeter-replacement SaaS model, which threatens hardware-dependent revenue pools in financial services verticals. Certification investment in EU AI Act conformity assessment preserves access to high-risk autonomous threat-response applications in healthcare and transportation sectors. For New Entrants and Emerging Players: Regional system integrators in São Paulo and Dubai represent the most accessible channel partners for mid-market manufacturing verticals with limited in-house security engineering capacity. India's MeitY cloud policy creates white-space opportunity for software-defined perimeter solutions without legacy hardware displacement costs. Japan's electricity, gas, and water utilities under METI mandatory monitoring standards offer recurring revenue managed detection and response contracts. Converged SASE platforms integrating SD-WAN, cloud access security broker, and zero-trust network access provide the strongest go-to-market angle against fragmented point-solution incumbents. For Investors and Strategic Acquirers: Asymmetric upside sits with cloud-native pure-plays displacing perimeter appliances, as sovereign data residency rules fragment procurement patterns and favor SaaS delivery models capable of multi-cloud policy consistency. The five-to-ten year viability window favors vendors with demonstrated AI-enabled threat detection capabilities subject to EU AI Act transparency requirements. Acquisition targets should exhibit embedded security module expertise for networked medical devices under FDA guidance. Certificate lifecycle management automation readiness serves as the critical inflection indicator for enterprise scalability.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies firewall, SD-WAN, and zero-trust access under single policy engines for financial services procurement. |
| Custom ASIC Development | Lowers per-packet inspection costs at 400 Gbps throughput for carrier network deployments. |
| Strategic Partnership | Links networking vendors with managed service providers to capture hybrid architecture margin pools. |
| Geographic Expansion | Establishes localized certification pathways under Germany BSI and Japan METI sovereign data mandates. |
| Acquisition of Specialist Firm | Absorbs certificate lifecycle management automation capabilities for machine-to-machine authentication at scale. |
Research Methodology
Direct dialogue with CISOs at financial services firms, healthcare technology officers, critical infrastructure operators, and managed security service providers grounded qualitative findings in operational procurement realities. Secondary validation drew from SEC cybersecurity disclosure filings, EU NIS2 Directive implementation guidance, FDA pre-market submission databases, and Japan METI critical infrastructure standards. Bottom-up segment sizing across deployment models and organization scales triangulated against top-down market boundary analysis.
Segmentation outputs across solution type, deployment model, end user category, and service type fed into analytical framework spanning the projection horizon. CAGRs derived from regression analysis of historical procurement velocity against regulatory mandate timelines, with cloud adoption curves and zero-trust architecture penetration serving as industry-specific forecast inputs.
Forecast confidence holds firmest in the near-window; longer-horizon outcomes carry greater sensitivity to silicon supply concentration at TSMC, geopolitical fragmentation of certification pathways, and workforce scarcity in behavioral analytics. Forecasts reflect assumptions regarding regulatory enforcement consistency and cloud provider region expansion. Periodic stress-testing of base assumptions is recommended.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Cloud Data Loss Prevention Solution Market
Security Software
Remote Access Management Market
Security Software
Keystroke Dynamics Market
Security Software
Global Mobile Security Software Market
Security Software
Global Error Monitoring Software Market
Security Software
POS Security Market
Security Software
Application Control Market
Security Software
Cloud Security Software Market
Security Software
Anomaly Detection Market
Security Software
Wi-Fi Based Home Camera Market
Security Software
Global Security Software in Telecom Market
Security Software
Asia-Pacific Fraud Detection & Prevention Market
Security Software
Ultra-Secure Smartphone Market
Security Software
Employee Surveillance and Monitoring Software Market
Security Software
Cloud Intrusion Protection Software Market
Security Software
Europe Enterprise Firewall Market