
 Cybersecurity in Banking Market | 2026-2036
Cybersecurity in Banking Market Size, Share, and Industry Trends Forecast 2026-2036
Cybersecurity in Banking Market Outlook
The banking cybersecurity landscape is pivoting on a widening capability gap between premium-tier institutions with autonomous security operations centers and commodity players dependent on outsourced alert monitoring. JP Morgan Chase sustains one of the industry's largest in-house threat intelligence divisions, deploying proprietary behavioral analytics across its global transaction networks. Goldman Sachs differentiates through deep specialization in quantitative risk models that map cyber exposure to trading book volatility. Deutsche Bank anchors its European defense posture through concentrated investment in Frankfurt-based security engineering talent.
Cybersecurity in banking encompasses the integrated hardware, software, and procedural safeguards that protect financial transaction integrity, customer data confidentiality, and operational continuity against unauthorized access or disruption. Core functional parameters include sub-100-millisecond threat detection latency, AES-256 encryption standards for data at rest, and multi-factor authentication protocols with adaptive risk scoring. Network security and identity access management command the largest current spending allocations as institutions retrofit legacy core banking systems with zero-trust architectures. Cloud-based deployment models represent the fastest-growing structural segment, though on-premises infrastructure retains dominant share among systematically important banks subject to national data sovereignty requirements.
US institutions navigate layered oversight from the SEC, OCC, and state-level banking regulators that mandate incident disclosure timelines and capital reserves for operational risk. European banks face parallel compliance obligations under GDPR data breach notification rules and the Digital Operational Resilience Act's mandatory penetration testing cycles. Stakeholders must weigh the trade-off between cloud agility and jurisdictional control as fragmented regulatory frameworks across multiple geographies complicate unified security governance.
Market Dynamics
Cloud migration mandates from US and European regulators are compressing deployment timelines for zero-trust architectures, forcing banks to restructure security procurement around continuous validation models rather than perimeter-based licensing.
Growth Catalysts
- GLBA Safeguards Rule enforcement:US regulators now mandate annual penetration testing and multi-factor authentication for all customer-facing systems, accelerating identity access management procurement cycles.
- Quantum-resistant cryptography standards:NIST's post-quantum encryption guidelines are driving hardware security module refresh programs across systematically important financial institutions.
- Real-time payment network expansion:FedNow and SEPA Instant adoption in the United States and Germany is requiring sub-50-millisecond fraud detection capabilities that legacy rule-based systems cannot deliver.
Market Restraints
- Specialized talent scarcity:Zero-trust architects and threat intelligence analysts command compensation premiums exceeding 40% above general IT security roles, constraining mid-tier bank hiring.
- Legacy core banking integration costs:Mainframe-dependent institutions face 18-36 month modernization timelines to embed API security gateways without disrupting overnight batch processing.
- Fragmented sovereignty requirements:Russia's data localization laws and China's cybersecurity reviews prevent unified cloud security governance for multinational banks operating across these jurisdictions.
Strategic Opportunities
- India's digital public infrastructure:The Account Aggregator framework and UPI expansion create demand for consent-based data security architectures that Western vendors can adapt from GDPR-compliant designs.
- AI-driven security orchestration:Convergence of large language models with security information and event management platforms enables autonomous threat response that reduces mean-time-to-remediation from hours to minutes.
- Managed detection and services channel:Regional banks in Italy and Spain are outsourcing security operations to specialized providers, creating recurring revenue streams distinct from perpetual license models.
Industry Challenges
- Zero-trust skill deficit:Security teams lack expertise in micro-segmentation and software-defined perimeter deployment, delaying architecture rollouts by 6-12 months.
- Third-party risk cascade management:Banks must map and monitor security postures across 200+ fintech API connections, overwhelming existing vendor assessment workflows.
- Cross-border incident response coordination:Divergent breach notification timelines between GDPR's 72-hour rule and US state-level requirements complicate unified crisis management.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cybersecurity in Banking Market |
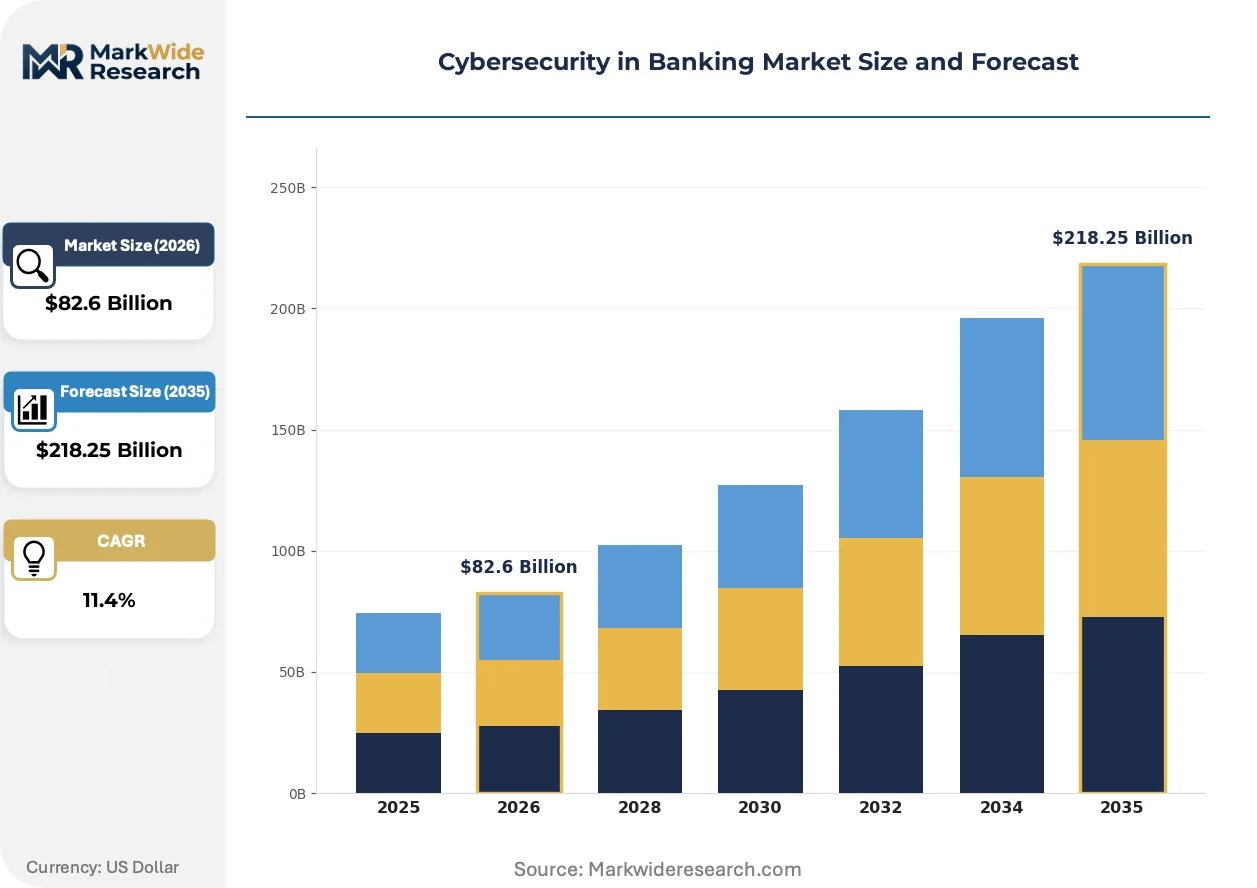
| Market Size in 2026 | $82.6 Billion |
| Market Size in 2035 | $218.25 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Network Security, End-Point Protection, Identity Access Management, Data Loss Prevention Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Services End User: Retail Banks, Investment Banks, Credit Unions, Non-Banking Financial Companies Compliance Standard: PCI DSS, GLBA, SOX, GDPR |
| Companies Covered | JP Morgan Chase, Goldman Sachs, HSBC, Bank of America, Citigroup, BNP Paribas, Deutsche Bank, Santander, DBS Bank, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cybersecurity in Banking Market Strategic Shifts
Security infrastructure procurement is pivoting from perimeter defense to continuous identity verification, with behavioral biometrics and decentralized credential systems displacing static password architectures across retail and commercial banking segments.
Extended detection and response platforms are modularizing security tool integration by unifying endpoint, network, and cloud telemetry into single-pane-of-glass consoles. Mid-sized US banks with 5,000-50,000 employees are adopting these consolidated stacks fastest, compressing vendor consolidation timelines from multi-year rip-and-replace cycles to phased 6-month rollouts. This modularization is reducing integration overhead and enabling faster threat correlation across previously siloed security domains.
The Digital Operational Resilience Act's mandatory threat-led penetration testing and ICT risk management requirements are forcing European banks to restructure third-party due diligence. Critical ICT service providers must now meet baseline security standards to maintain contracts with EU credit institutions, shifting procurement evaluation criteria toward certified resilience attestations. German and French banks are responding by embedding DORA compliance checkpoints into vendor onboarding workflows 18-24 months ahead of full enforcement.
Chief information security officers are consolidating vendor relationships around integrated platform providers rather than best-of-breed point solutions. This preference compression is displacing standalone encryption, firewall, and endpoint protection vendors in favor of consolidated security suites with native interoperability. The shift is most pronounced among North American regional banks seeking to reduce operational complexity and streamline security operations center staffing.
Cybersecurity in Banking Market Segmentation
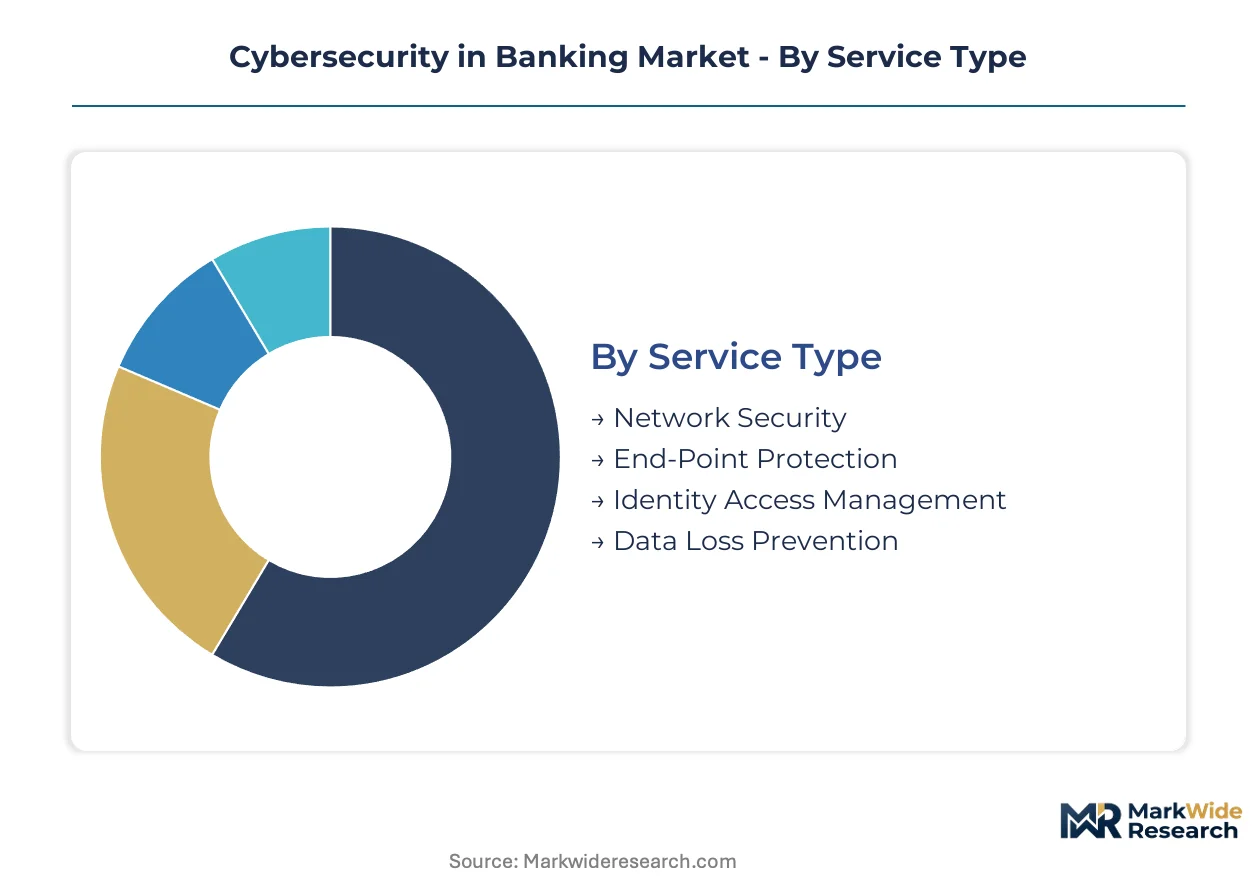
Cybersecurity procurement in banking diverges sharply by institutional scale and regulatory exposure. Segment-specific requirements determine whether institutions pursue integrated platforms or specialized point solutions across their technology stacks.
Service Type:
Standardized commodity tools dominate smaller institutions while tier-one banks commission bespoke architectures calibrated to proprietary risk models.
- Network Security:Firewalls, intrusion detection systems, and secure web gateways form the perimeter defense layer. Demand concentrates among US regional banks retrofitting legacy branch networks for zero-trust segmentation as OCC guidance tightens.
- Identity Access Management:Multi-factor authentication, privileged access management, and adaptive risk scoring engines verify user credentials dynamically. Investment banks in London and Frankfurt drive premium demand for behavioral biometrics integration under DORA's authentication mandates.
- End-Point Protection:Antivirus, endpoint detection and response, and device control solutions secure workstations and mobile banking devices.
- Data Loss Prevention:Content inspection, encryption, and egress monitoring tools prevent unauthorized data exfiltration.
Leading the category by volume: Network Security. Growing fastest: Identity Access Management.
Deployment Model:
Cost tier stratification separates sovereign-data institutions from agility-focused competitors.
- Cloud-Based:Scalable security-as-a-service delivery with API-native integration. Retail banks across Italy and Spain adopt fastest to bypass capital-intensive infrastructure builds while meeting ECB cloud risk guidelines.
- Hybrid:Orchestrated on-premises and cloud workloads with unified policy enforcement. Systematically important banks in Germany and France favor this model to satisfy data localization requirements without sacrificing development velocity.
- On-Premises:Dedicated hardware and software within institution-controlled facilities.
- Managed Services:Outsourced security operations center functions with SLA-guaranteed response times.
Hybrid deployments command premium pricing. Cloud-based solutions are expanding most quickly among mid-tier institutions.
End User:
Application complexity varies from transaction-heavy retail operations to algorithm-sensitive trading environments.
- Retail Banks:Branch networks, digital banking platforms, and ATM fleets serving mass-market customers. US credit unions and community banks drive volume procurement of standardized endpoint protection suites.
- Investment Banks:Trading infrastructure, research platforms, and client-facing analytics requiring sub-millisecond latency. Firms in New York and London commission custom threat intelligence feeds mapped to market volatility patterns.
- Credit Unions:Member-owned cooperative institutions with constrained IT budgets.
- Non-Banking Financial Companies:Payment processors, mortgage servicers, and fintech lenders subject to bank-grade security expectations.
Retail banks anchor procurement volume. Investment banks generate the steepest expansion trajectory for specialized services.
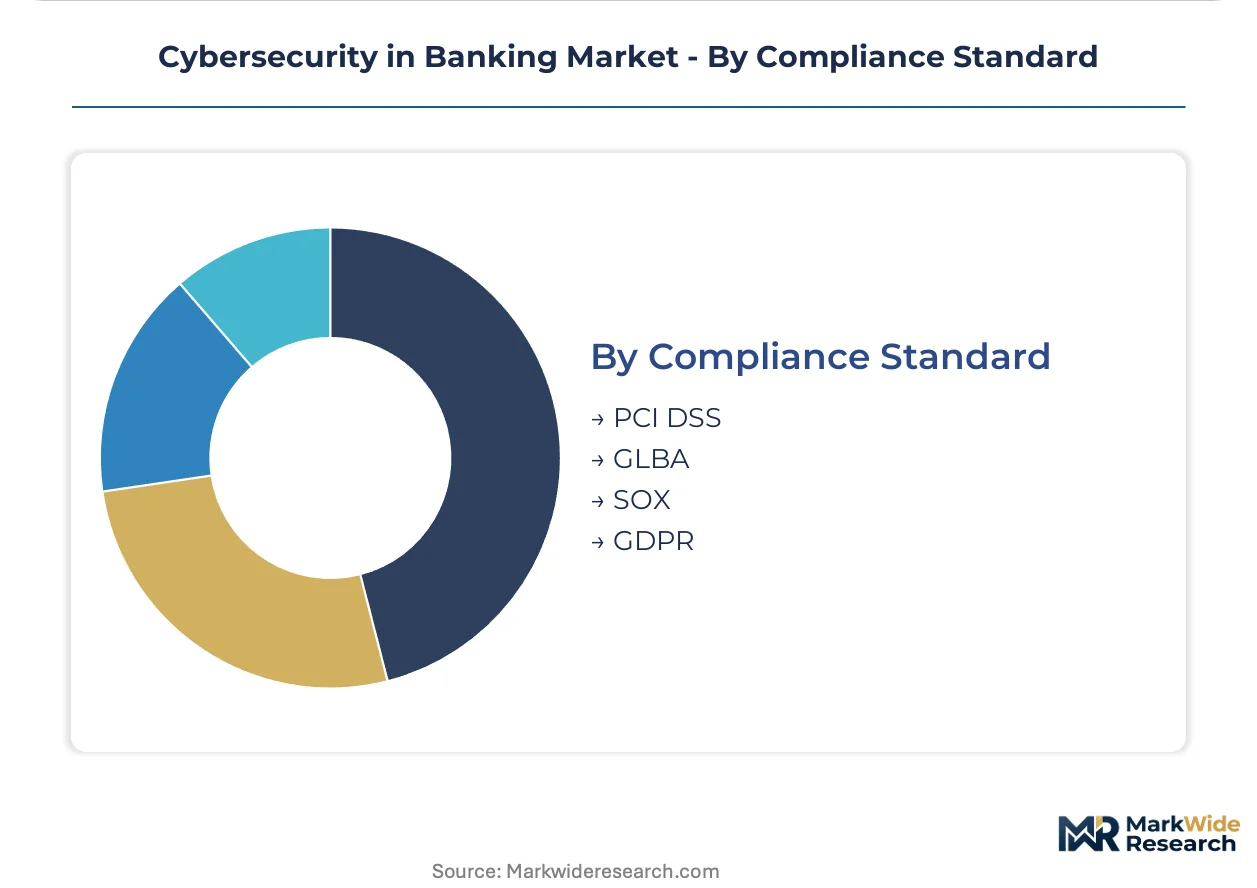
Compliance Standard:
Geographic footprint dictates which regulatory frameworks govern security architecture design.
- PCI DSS:Payment card industry data security standards mandating encryption and access controls for cardholder data. US acquirers and processors face continuous audit cycles driving recurring compliance tool demand.
- GDPR:European data protection rules requiring breach notification and privacy-by-design. Banks with EU operations embed these requirements into cross-border data flows regardless of headquarters location.
- GLBA:US Gramm-Leach-Bliley Act safeguarding customer financial information.
- SOX:Sarbanes-Oxley financial reporting controls applicable to publicly traded institutions.
PCI DSS compliance tools lead by deployment volume. GDPR-aligned privacy engineering represents the fastest-climbing investment category.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Frankfurt's concentration of ECB-regulated institutions and security engineering talent anchors European cybersecurity procurement for banking infrastructure. New York and London maintain parallel dominance through investment bank threat intelligence spending. Singapore and Mumbai emerge as Asia-Pacific demand centers.
United States
JP Morgan Chase and Goldman Sachs sustain in-house threat intelligence divisions with proprietary behavioral analytics. The SEC and OCC mandate incident disclosure timelines and capital reserves for operational risk. New York's financial district concentrates autonomous security operations center investment.
Germany
Deutsche Bank anchors European defense posture through Frankfurt-based security engineering recruitment. The Digital Operational Resilience Act mandates threat-led penetration testing cycles for credit institutions. Bavaria's technology corridor hosts specialized zero-trust architecture consultancies serving systematically important banks.
United Kingdom
HSBC and investment banks in the City of London commission custom threat intelligence feeds mapped to market volatility. The Financial Conduct Authority enforces operational resilience requirements with mandatory recovery time objectives. London's cybersecurity cluster supplies quantitative risk modeling expertise to trading infrastructure.
Singapore
DBS Bank drives cloud-native security adoption across Southeast Asian retail networks. The Monetary Authority of Singapore's Technology Risk Management Guidelines mandate multi-factor authentication for all digital financial services. The island's fintech hub concentrates API security gateway development for cross-border payment networks.
India
The Account Aggregator framework and UPI expansion create demand for consent-based data security architectures. The Reserve Bank of India mandates baseline cybersecurity standards for payment system operators. Mumbai's financial district and Bangalore's technology corridor host joint ventures adapting GDPR-compliant designs for digital public infrastructure.
Cybersecurity in Banking Market Competitive Environment
Premium-margin players sit above commodity-margin players across threat intelligence specialization and proprietary analytics capabilities. The vendor base stratifies between integrated platform providers with native interoperability and standalone point solution vendors facing displacement. Three archetypes dominate: autonomous security operations centers with captive engineering, managed detection and response specialists with SLA-guaranteed response times, and cloud-native platform vendors with API-native integration. Consolidation pressures favor M&A activity among endpoint protection vendors and strategic partnerships between regional banks and specialized security operations providers.
Within the autonomous security operations tier, JP Morgan Chase exemplifies premium-tier investment in proprietary behavioral analytics across global transaction networks. Goldman Sachs occupies a position calibrated to quantitative risk models that map cyber exposure to trading book volatility. Deutsche Bank represents European concentration in Frankfurt-based security engineering talent for DORA compliance.
| Leading Market Players |
|---|
| JP Morgan Chase |
| Goldman Sachs |
| HSBC |
| Bank of America |
| Citigroup |
| BNP Paribas |
| Deutsche Bank |
| Santander |
| DBS Bank |
| Others |
Value Chain & Pricing Dynamics
Zero-trust security architects in the San Francisco Bay Area and Frankfurt technology corridors command compensation premiums exceeding 40% above general IT security roles, widening the labor-cost differential between premium-tier autonomous security operations and commodity outsourced monitoring tiers.
Pricing Analysis
Outcome-based pricing tied to mean-time-to-detection and breach prevention metrics anchors value propositions for managed detection and response providers. Three-tier pricing structure across premium, standard, and economy levels separates institutions with sub-100-millisecond latency guarantees from mid-tier banks accepting 4-hour response SLAs. Cost compression in the standard tier is intensifying because regional banks in Italy and Spain are consolidating vendor relationships around integrated platform providers. Credit unions with constrained IT budgets exhibit the highest price sensitivity, while investment banks in London and New York prioritize performance guarantees over unit economics.
Supply Chain Analysis
Dual-sourcing requirements for hardware security modules and encryption key management systems are now standard in procurement contracts from systematically important banks. Manufacturing concentrates in the United States, Germany, and Taiwan for specialized cryptographic processors and secure enclave components. Supply chains draw from semiconductor foundries, certified firmware developers, and quantum-resistant algorithm libraries. Single-source vulnerability in NIST-certified post-quantum cryptography modules poses concentrated risk as refresh programs accelerate. Distribution runs through direct enterprise sales teams and specialized cybersecurity value-added resellers serving regional banking segments.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Specialized talent scarcity in zero-trust architecture and threat intelligence analysis props pricing power for vendors with captive engineering capacity, constraining supply elasticity across all tiers.
For Market Incumbents: Extend proprietary behavioral analytics capabilities into adjacent fraud detection verticals, particularly real-time payment networks requiring sub-50-millisecond response. Consolidate endpoint protection vendors through selective acquisition to eliminate interoperability friction in security operations center workflows. Threat intelligence commoditization from open-source feeds erodes differentiation unless paired with quantitative risk modeling expertise. For New Entrants and Emerging Players: AI-driven security orchestration platforms integrating large language models with security information and event management systems offer the most penetrable wedge for mid-tier US banks with 5,000-50,000 employees. Target India's Account Aggregator framework and UPI expansion for consent-based data security architectures adapted from GDPR-compliant designs. Channel partnerships with established managed services providers accelerate credentialing against DORA and GLBA compliance requirements. For Investors and Strategic Acquirers: The window for entry favors managed detection and response specialists with SLA-guaranteed response times and recurring revenue models distinct from perpetual license structures. Long-term viability hinges on platform consolidation tailwinds displacing standalone encryption, firewall, and endpoint protection vendors. Monitor NIST post-quantum cryptography standardization timelines as inflection indicator for hardware security module refresh cycle acceleration.| Strategic Initiative | Industry Significance |
|---|---|
| Zero-Trust Architecture Deployment | GLBA and DORA mandates compress implementation timelines for continuous validation models across legacy core banking systems. |
| Quantum-Resistant Cryptography Migration | NIST guidelines drive hardware security module refresh programs among systematically important financial institutions. |
| Managed Security Services Outsourcing | Regional banks in Southern Europe reduce operational complexity through SLA-guaranteed security operations center functions. |
| AI-Driven Threat Response Integration | Convergence with large language models reduces mean-time-to-remediation from hours to minutes for retail networks. |
| Cloud-Native Security Platform Adoption | ECB cloud risk guidelines accelerate API-native integration among Italian and Spanish retail banking institutions. |
Study Parameters
SEC filings, OCC regulatory guidance documents, and ECB cloud risk assessment frameworks formed the secondary backbone for market sizing and compliance requirement mapping. Primary interviews with chief information security officers, zero-trust architecture consultants, managed detection and response sales directors, and GLBA audit specialists validated procurement cycle timelines and budget allocation patterns. Bottom-up segmentation modeling across service type, deployment model, and end-user categories triangulated against top-down regulatory spend estimates derived from enforcement action disclosures.
Historical trendline analysis of identity access management and network security expenditure patterns informed growth trajectory projections across the analysis window. Segmentation dimensions modeled include service type, deployment architecture, institutional scale tier, and geographic regulatory cluster. CAGRs were derived through regression analysis of disclosed technology budgets and enforcement-driven compliance investment mandates. Forecast inputs incorporated FedNow and SEPA Instant adoption curves for real-time fraud detection capability requirements.
Several conditions sit outside the modeled scope, including nation-state attribution of specific breach incidents and classified threat intelligence from government partnerships. Forecasts reflect documented assumptions regarding regulatory enforcement intensity and cloud migration adoption curves. Deviation in NIST post-quantum cryptography standardization timelines or DORA penalty structures would shift the outlook materially.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Banking
Letter of Credit Confirmation Market
Banking
China Data Analytics in Banking Market
Banking
Australia Neobanking Market
Banking
Europe Machine Learning in Banking Market
Banking
Retail Banking IT Spending Market
Banking
Credit Intermediation Market
Banking
Commercial Banking Market
Banking
Machine Learning in Banking Market
Banking
Contactless Smart Cards in Banking Sales Market
Banking
UK Banking as a Service Market
Banking
Digital LED Retail Banking Market
Banking
US Commercial Banking Market
Banking
Cloud-Based Core Banking Market
Banking
Brazil Retail Banking Market
Banking
Australia Data Analytics in Banking Market
Banking
Latin America Data Analytics in Banking Market