
 Global Software Composition Analysis Market | 2026-2036
Global Software Composition Analysis Market Size, Share, and Industry Trends Forecast 2026-2036
Global Software Composition Analysis Market Foresight
North American cybersecurity vendor capacity is consolidating as enterprise buyers demand unified software supply chain visibility. Synopsys leverages its semiconductor design heritage to anchor SCA within broader application security portfolios. Snyk competes through developer-native workflows that embed composition scanning directly into IDE environments. Sonatype specializes in repository-centric governance, controlling artifact provenance across Maven Central and npm ecosystems.
Software Composition Analysis identifies and catalogs third-party and open-source components within proprietary codebases, mapping license obligations and known Common Vulnerabilities and Exposures against dependency trees to prevent legal exposure and security breaches. The technique operates through manifest parsing, binary fingerprinting, and hash matching against curated vulnerability databases such as the NVD and vendor-specific feeds. Cloud-Based deployment leads solution type distribution as organizations prioritize elastic scanning capacity across distributed development teams, while Vulnerability Management captures the dominant margin pool due to breach-cost sensitivity. DevSecOps application segments are maturing fastest as CI/CD pipeline integration becomes standard, though Policy Enforcement represents the emerging growth frontier as regulated industries codify material change thresholds.
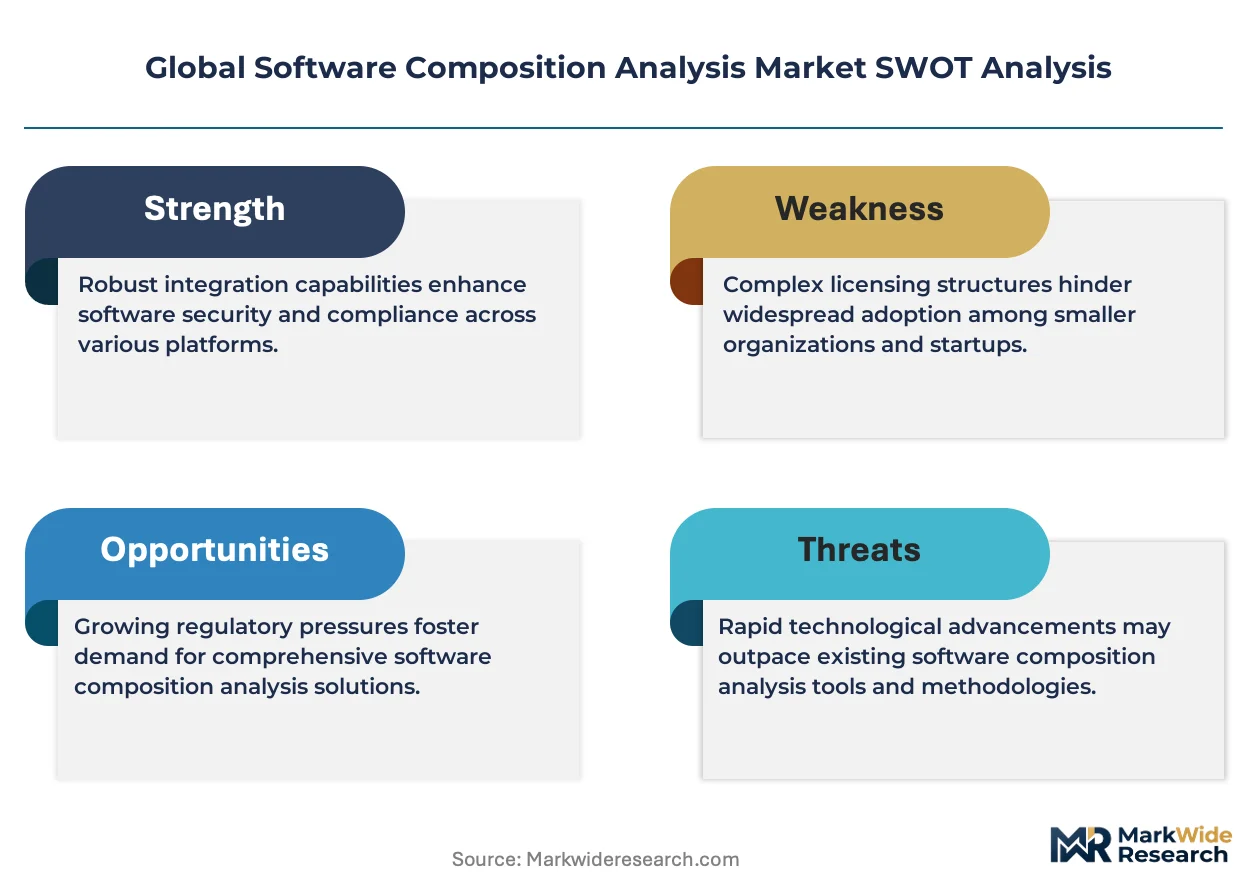
The EU Cyber Resilience Act mandates software bill of materials disclosure for connected products, compelling vendors to maintain auditable component inventories or face market exclusion. FDA software validation guidelines for medical devices extend similar traceability requirements to healthcare technology suppliers, while NIST Secure Software Development Framework standards shape procurement criteria across US federal contractors. Stakeholders must monitor whether emerging AI-generated code pipelines fragment existing SCA detection methodologies or create adjacent verification tool categories.
Market Dynamics
Regulatory mandates for software transparency are compressing procurement cycles as enterprises race to comply with mandatory disclosure regimes before enforcement deadlines.
Growth Catalysts
- EU Cyber Resilience Act:Connected product manufacturers must maintain auditable software bills of materials, creating baseline demand for automated component inventory tools across European electronics and automotive supply chains.
- Financial services:Banking and insurance regulators in the United States, Germany, and Japan are embedding open-source governance requirements into operational risk frameworks, mandating pre-deployment vulnerability scanning.
- AI-generated code pipelines:Large language model outputs introduce unvetted dependencies at scale, forcing organizations to expand SCA coverage beyond traditional package managers to generated artifacts.
Market Restraints
- Curated database maintenance costs:Continuous ingestion and correlation of NVD, vendor advisories, and proprietary feeds requires substantial ongoing investment, concentrating capability among well-capitalized vendors.
- False positive fatigue:Dependency tree complexity generates noise-to-signal ratios that erode developer trust, particularly in polyglot codebases with transitive dependency depth exceeding five layers.
- Fragmented license interpretation:Ambiguous open-source license compatibility across copyleft, permissive, and custom variants creates legal exposure that automated tooling cannot fully resolve without human review.
Strategic Opportunities
- Medical device software validation:FDA guidelines for healthcare technology suppliers extend traceability requirements to third-party components, opening specialized compliance workflows for regulated healthcare manufacturers.
- Binary fingerprinting convergence:Integration of static analysis with runtime behavior monitoring enables detection of compromised dependencies that manifest only during execution, not at build time.
- India's software export sector:IT services firms serving European and North American clients face escalating customer audit requirements for component provenance, driving localized SCA adoption.
Industry Challenges
- Developer workflow friction:Security scanning that interrupts commit cycles faces resistance from engineering teams measured on velocity metrics, requiring careful integration design to preserve productivity.
- Legacy codebase inventory:Organizations with decades of accumulated software lack accurate dependency manifests, forcing expensive manual reconstruction or incomplete automated discovery.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Software Composition Analysis Market |
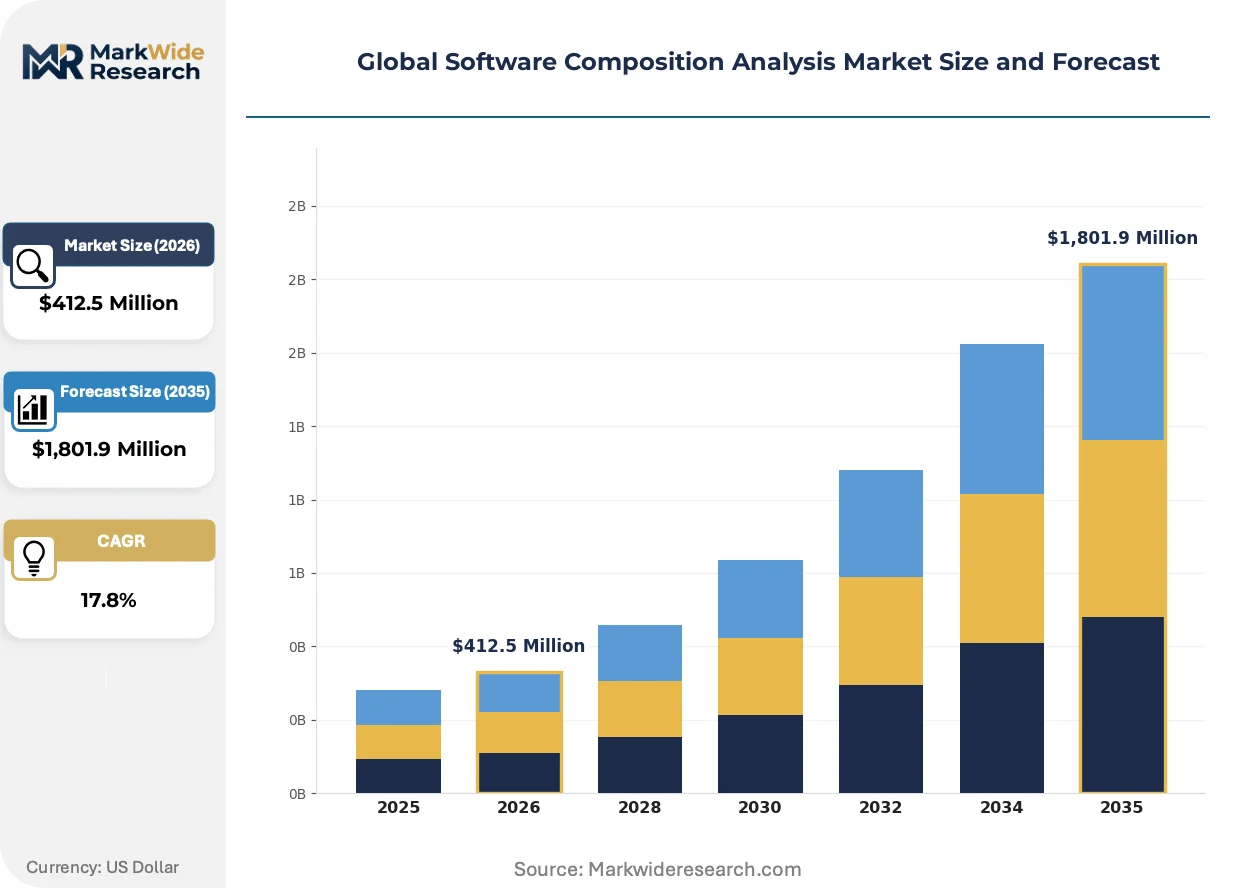
| Market Size in 2026 | $412.5 Million |
| Market Size in 2035 | $1,801.9 Million |
| CAGR (2026 – 2036) | 17.8% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premise, Cloud-Based, Hybrid, Private Cloud, Public Cloud Solution Type: License Compliance, Vulnerability Management, Risk Analysis, Policy Enforcement, Component Identification Application: DevSecOps, Continuous Integration, Software Development, Security Assessment, Open Source Management, Quality Assurance End User: IT Enterprises, Software Vendors, Government Agencies, Financial Institutions, E-Commerce Firms, Telecommunications Providers |
| Companies Covered | Synopsys, Veracode, Snyk, Sonatype, Mend.io, Checkmarx, Black Duck Software, FOSSA, JFrog, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Software Composition Analysis Market Shifts & Advancements
Intelligent automation is compressing the window between vulnerability disclosure and remediation, while regulatory complexity forces tooling consolidation.
Reachability analysis is automating the prioritization of component vulnerabilities by mapping actual code execution paths rather than flagging every present dependency. Financial institutions and healthcare technology suppliers are adopting this capability fastest, driven by breach-cost sensitivity and FDA validation requirements. The technique is automating the elimination of noise that previously consumed engineering hours on non-exploitable findings.
REACH chemical safety documentation requirements have established precedent for extended producer responsibility in digital supply chains, with EU policymakers now applying similar logic to software component disclosure. The Cyber Resilience Act mandates machine-readable SBOM formats that vendors must provide to downstream customers. Medical device manufacturers and industrial automation suppliers face the steepest compliance curves, with many restructuring procurement contracts to pass disclosure obligations to component vendors.
Enterprise buyers are consolidating vendor relationships, demanding unified platforms that span SCA, static application security testing, and runtime protection rather than point solutions. Systems integrators and managed security providers are capturing increasing influence over tooling selection, displacing direct procurement by development teams. This concentration is most visible in the United States and Germany, where Fortune 500 technology procurement functions have centralized software supply chain risk management under dedicated vendor governance teams.
Global Software Composition Analysis Market Segmentation
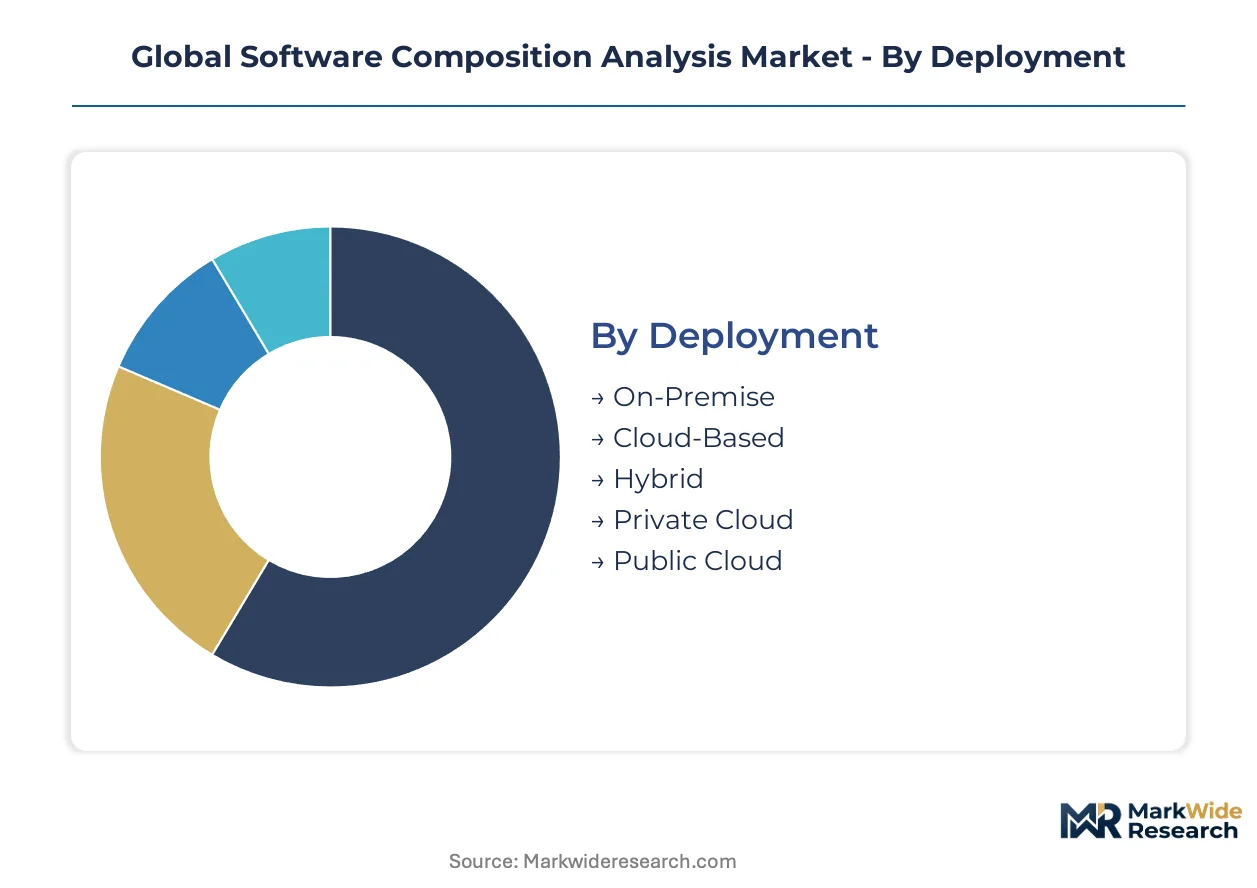
Software Composition Analysis deployment patterns diverge sharply based on organizational cloud maturity, regulatory exposure, and developer workflow integration requirements. Segment boundaries are blurring as vendors bundle capabilities across deployment modes and solution types to capture expanding procurement budgets.
Deployment:
Cloud infrastructure choices determine scanning architecture elasticity and data residency controls.
- Cloud-Based:Elastic compute pools enable distributed development teams to scale scanning capacity without capital expenditure. Demand concentrates among mid-market enterprises in the United States and Germany prioritizing rapid deployment over customization.
- On-Premise:Air-gapped scanning environments satisfy classified government workloads and financial institutions with strict data sovereignty requirements. Regulatory pressure from the EU Cyber Resilience Act is sustaining deployment in European defense and critical infrastructure sectors.
- Hybrid:Split architectures route sensitive scans on-premise while leveraging cloud elasticity for routine dependency checks.
- Private Cloud:Dedicated tenant environments serve healthcare technology suppliers navigating FDA software validation guidelines.
- Public Cloud:Shared infrastructure delivers lowest unit economics for startups and independent software vendors with limited compliance exposure.
Mature deployment sits with On-Premise. Newer deployment is concentrated in Cloud-Based.
Solution Type:
Functional modules align with distinct buyer personas across legal, security, and engineering functions.
- Vulnerability Management:CVE correlation engines map dependency trees against NVD feeds to prioritize remediation by exploitability. Breach-cost sensitivity drives adoption among United States financial institutions and Japanese automotive electronics suppliers.
- License Compliance:Automated license identification flags copyleft contamination risks in proprietary distributions. Legal teams at German industrial automation firms deploy this capability to satisfy supply chain audit requirements.
- Risk Analysis:Composite scoring algorithms weight vulnerability severity against business criticality metrics.
- Policy Enforcement:Pre-deployment gates block commits violating organizational risk thresholds. This segment is expanding most quickly as regulated industries codify material change controls.
- Component Identification:Manifest parsing and binary fingerprinting establish baseline software bill of materials inventories.
Established procurement concentrates on Vulnerability Management. Policy Enforcement is gaining share fastest among compliance-driven buyers.
Application:
Integration points span the software development lifecycle from ideation through production monitoring.
- DevSecOps:CI/CD pipeline embedding shifts security left without interrupting developer velocity. United States technology enterprises and Indian IT services exporters are standardizing this integration to meet customer audit demands.
- Continuous Integration:Automated scanning triggers on every build artifact generation. Japanese electronics manufacturers deploy this capability to satisfy supply chain transparency mandates.
- Software Development:IDE-integrated composition analysis provides real-time feedback during coding.
- Security Assessment:Point-in-time audits satisfy procurement due diligence and M&A technical diligence requirements.
- Open Source Management:Centralized governance portals track component provenance across enterprise portfolios.
- Quality Assurance:Pre-release validation gates ensure deployment readiness.
Volume leadership sits with DevSecOps. Security Assessment shows the steepest expansion trajectory among regulated healthcare and financial services buyers.
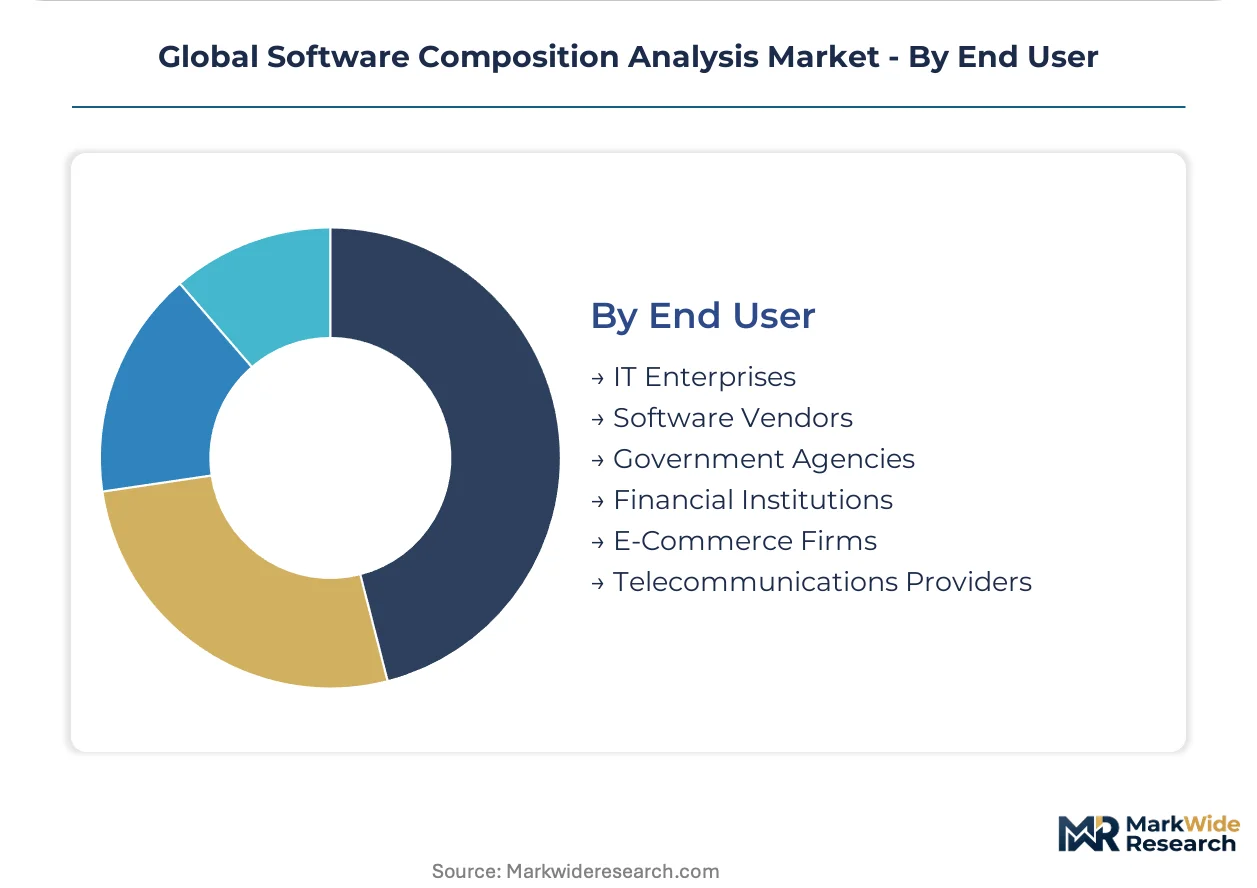
End User:
Organizational scale and regulatory exposure shape solution complexity requirements and procurement authority structures.
- Financial Institutions:Banking and insurance regulators in the United States, Germany, and Japan mandate pre-deployment vulnerability scanning. Operational risk frameworks drive the most sophisticated policy enforcement deployments.
- IT Enterprises:Fortune 500 technology procurement functions have centralized software supply chain risk management under dedicated vendor governance teams in the United States and Germany.
- Software Vendors:Customer audit requirements force component provenance disclosure to enterprise buyers.
- Government Agencies:NIST Secure Software Development Framework standards shape procurement criteria across United States federal contractors.
- E-Commerce Firms:Payment card industry compliance drives baseline vulnerability scanning adoption.
- Telecommunications Providers:Critical infrastructure designation elevates supply chain security to board-level priority.
Procurement maturity concentrates with Financial Institutions. Telecommunications Providers are climbing the fastest as network equipment security attracts regulatory scrutiny.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Silicon Valley's open-source governance clusters anchor North American demand generation, while regulatory mandates across multiple jurisdictions reshape procurement geography.
United States
Financial institutions in New York and San Francisco deploy sophisticated policy enforcement workflows to satisfy SEC operational risk frameworks. The FDA's software validation guidelines for medical devices extend traceability requirements to healthcare technology suppliers across Massachusetts and Minnesota. Boston's medical device corridor concentrates specialized compliance tooling adoption as manufacturers restructure procurement contracts.
Germany
Industrial automation firms in Munich and Stuttgart face escalating supply chain audit requirements from automotive OEMs. The EU Cyber Resilience Act mandates machine-readable SBOM formats that Bavarian electronics manufacturers must provide to downstream customers. Frankfurt's banking sector anchors the most mature vulnerability management deployments in continental Europe.
Japan
METI guidelines on software supply chain security drive adoption among Tokyo-based automotive electronics suppliers. Japanese banking regulators embed open-source governance into operational risk frameworks comparable to US and German standards. Osaka's manufacturing technology cluster standardizes CI/CD pipeline integration to satisfy customer transparency mandates.
India
IT services exporters in Bangalore and Hyderabad face escalating audit requirements from European and North American clients for component provenance. The country's software export sector drives localized SCA adoption as delivery centers restructure quality assurance protocols. Mumbai's financial services hub implements pre-deployment scanning to align with RBI cybersecurity guidelines.
United Kingdom
London's fintech sector consolidates vendor relationships under dedicated software supply chain risk management functions. The UK National Cyber Security Centre shapes procurement criteria for critical infrastructure operators across the Southeast. Cambridge's enterprise software cluster exemplifies developer-native workflow integration as competitive differentiation.
Global Software Composition Analysis Market Competitive Landscape
Established producers occupy the standard tier; emerging entrants pursue adjacent verification spaces around AI-generated code pipelines. The vendor base organizes around three strategic archetypes: semiconductor design heritage platforms, developer-native workflow specialists, and repository-centric governance controllers. Consolidation pressures intensify as enterprise buyers demand unified application security portfolios spanning composition analysis, static testing, and runtime protection. M&A activity concentrates on filling portfolio gaps, while strategic partnerships target CI/CD ecosystem integration.
Within the repository-centric tier, Sonatype exemplifies artifact provenance control across Maven Central and npm ecosystems. Synopsys and Snyk occupy differentiated positions—one leveraging semiconductor design heritage to anchor broader security portfolios, the other embedding composition scanning directly into IDE environments for developer-native workflows. These three represent how competitive positioning fragments across workflow integration philosophies rather than converging on uniform delivery models.
| Leading Market Players |
|---|
| Synopsys |
| Veracode |
| Snyk |
| Sonatype |
| Mend.io |
| Checkmarx |
| Black Duck Software |
| FOSSA |
| JFrog |
| Others |
Supply & Pricing Matrix
Cloud-native scanning architectures are compressing infrastructure costs while concentrating procurement leverage among hyperscaler-aligned vendors. This technology shift simultaneously erodes on-premise premium pricing and rewards vendors with elastic compute partnerships across United States and German enterprise accounts.
Pricing Analysis
Service bundling separates vulnerability database freshness from workflow integration depth, with premium tiers adding reachability analysis and SBOM attestation services. Price differentiation hinges on deployment elasticity and API call volume thresholds, not core scanning functionality. Cost compression in mid-market segments is intensifying because vendor consolidation is standardizing baseline feature parity. Startups and independent software vendors exhibit the highest price sensitivity, while financial institutions in New York and Frankfurt absorb premium pricing for policy enforcement modules.
Supply Chain Analysis
Certification gating through FedRAMP and ISO 27001 accreditation restricts viable vendor participation in government and healthcare procurement channels. Supply concentrates among United States, Israel, and Ireland-based vendors with established cloud infrastructure partnerships. Raw material dependencies include curated vulnerability feeds from NIST, GitHub Advisory Database, and proprietary vendor research teams. Single-source vulnerability in the NVD pipeline creates systemic exposure if federal funding disruptions delay CVE publication. Distribution runs through hyperscaler marketplaces and direct enterprise sales teams with embedded solutions architects.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Curated database maintenance capacity constrains viable vendor expansion, propping pricing power for established players with sustained R&D investment. This supply bottleneck insulates incumbents from pure-play price competition.
For Market Incumbents: To counter AI-generated code pipeline fragmentation, anchor SCA capabilities within unified application security platforms spanning static analysis and runtime protection. Acquire reachability analysis specialists to differentiate vulnerability prioritization beyond CVE correlation. Invest in FedRAMP authorization to capture United States federal procurement demand under NIST Secure Software Development Framework mandates.
For New Entrants and Emerging Players: The EU Cyber Resilience Act in Europe opens a window for specialized SBOM attestation services targeting Bavarian automotive electronics and Dutch medical device manufacturers. Target India's IT services exporters facing European client audit requirements with localized compliance automation. Pursue channel partnerships with systems integrators serving mid-market German industrial automation firms.
For Investors and Strategic Acquirers: Exit pathways concentrate in platform consolidation plays by semiconductor design heritage vendors seeking application security portfolio completion. Long-term viability favors vendors with demonstrated CI/CD ecosystem integration depth and recurring revenue concentration above seventy percent. Watch for inflection when FDA software validation guidelines expand beyond medical devices to diagnostic software categories.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies SCA with static analysis and runtime protection to capture enterprise consolidation budgets. |
| Acquisition of Specialist Firm | Adds reachability analysis or binary fingerprinting capabilities that differentiate vulnerability prioritization. |
| Strategic Partnership | Embeds scanning into GitHub, GitLab, or Jenkins marketplaces to capture developer-native workflow adoption. |
| Geographic Expansion | Establishes localized presence in Bangalore and Hyderabad to serve Indian IT services exporter demand. |
| Product Launch | Introduces AI-generated code verification modules addressing LLM dependency contamination risks. |
Research Methodology
Document review covered SEC filings, hyperscaler marketplace disclosures, and regulatory dockets from FDA and EU Cyber Resilience Act proceedings, complemented by interviews with chief technology officers, DevSecOps platform engineers, IT procurement officers at Fortune 500 enterprises, and channel partners specializing in application security distribution. Secondary validation drew from NIST vulnerability database metrics, CI/CD platform adoption surveys, and healthcare technology supplier compliance disclosures. Bottom-up deployment estimates and top-down security software spending analysis were triangulated against vendor-reported customer metrics.
Historical growth patterns were cross-referenced against expert panel inputs from financial services technology risk officers and medical device software validation leads. The analytical framework modeled deployment mode, organization size, vertical regulatory exposure, and integration complexity across the projection horizon. CAGRs were derived from segment-level growth rate reconciliation against aggregate market expansion. Forecast inputs included EU Cyber Resilience Act implementation timelines and FDA software validation guideline adoption curves.
The model assumes a particular technology adoption path; alternative pathways for AI-generated code verification would alter the outlook if LLM providers embed native composition scanning. Forecasts reflect assumptions about regulatory enforcement consistency and vulnerability disclosure velocity. A model refresh is warranted upon material change in NVD funding stability or EU Cyber Resilience Act penalty enforcement thresholds.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Software & Services
Advanced Process Control Software Market
Software & Services
Global Customer Journey Mapping Software Market
Software & Services
Camp Management Software Market
Software & Services
Media Planning Software Market
Software & Services
Design Collaboration Software Market
Software & Services
File Sharing Software Market
Software & Services
Global Healthcare Contract Management Software Market
Software & Services
Smartphone Music Production Software Market
Software & Services
Programmable Automation Controller (PAC) Programming Software Market
Software & Services
Email Applications Market
Software & Services
PCB Design Software Market
Software & Services
Global Screen and Script Writing Software Market
Software & Services
Global Development Tools Software Market
Software & Services
Global Jewelry Store Management Software Market
Software & Services
Email Marketing Software Market
Software & Services
Data Integration Software Market