
 Europe Risk Management Market | 2026-2036
Europe Risk Management Market Size, Share, and Industry Trends Forecast 2026-2036
Europe Risk Management Market Insights
Legacy on-premise risk infrastructure is restructuring around cloud-native architectures, compressing deployment cycles and reshaping product economics for European buyers. SAP SE leverages its embedded ERP footprint to anchor risk workflows inside existing financial systems. SAS Institute differentiates through advanced analytics engines that process real-time regulatory calculations. Deloitte sustains consulting-led implementation models that bridge policy design with technology deployment.
Risk management encompasses the systematic identification, quantification, and mitigation of threats to organizational objectives through statistical modeling, control frameworks, and continuous monitoring protocols. Its primary purpose centers on protecting capital adequacy, operational continuity, and regulatory compliance across complex institutional environments. Software solutions now dominate procurement budgets as automation replaces manual assessment workflows. Enterprise Risk Management occupies the mature core of spending, while Cybersecurity Solutions represents the fastest-expanding margin pool as attack surfaces multiply. Financial Institutions remain the largest client type, though Government Agencies are accelerating adoption of sovereign-grade resilience frameworks.
The EU Digital Operational Resilience Act (DORA), GDPR, and the EU AI Act collectively reshape product standards by mandating auditable risk controls, data governance, and algorithmic transparency. EMA guidelines for pharmacovigilance risk systems and ECB banking supervision standards further segment compliance requirements across verticals. Stakeholders must decide whether to build unified platforms spanning multiple regulatory regimes or specialize in jurisdiction-specific modules.
Market Dynamics
The EU Digital Operational Resilience Act (DORA) is compressing procurement timelines as financial institutions race to meet compliance deadlines by January 2025, forcing wholesale replacement of legacy governance frameworks with auditable, real-time risk infrastructure.
Growth Catalysts
- Regulatory Mandate Density:DORA, GDPR, and the EU AI Act create overlapping compliance obligations that compel institutions to purchase integrated platforms rather than point solutions. German banking supervisors are enforcing the strictest interpretation timelines.
- Cloud Migration Velocity:Financial institutions are abandoning on-premise risk engines for containerized architectures that compress deployment from 18 months to 8 weeks. This technical shift unlocks budget for continuous monitoring capabilities.
- Cyberattack Surface Expansion:Open banking APIs and third-party fintech integrations multiply vulnerability vectors. Incident reporting thresholds under DORA require automated detection systems that legacy tools cannot provide.
Market Restraints
- Specialized Talent Scarcity:The intersection of quantitative risk modeling and EU regulatory interpretation commands premium compensation. Frankfurt and London recruitment markets show acute shortages of DORA-certified implementation specialists.
- Vendor Concentration Risk:Cloud infrastructure for risk workloads depends on a narrow set of hyperscale providers. AWS, Microsoft Azure, and Google Cloud dominate sovereign-grade hosting certifications across EU member states.
- Legacy System Entrenchment:Core banking systems running COBOL-based risk calculations resist API-based integration. Rip-and-replace costs for these architectures often exceed three-year compliance fines.
Strategic Opportunities
- Poland and CEE Expansion:Warsaw and Prague emerging as shared service centers for risk operations. Lower labor costs and EU regulatory equivalence attract banking captives seeking DORA-compliant outsourcing.
- Climate Risk Integration:ECB stress testing mandates incorporate forward-looking climate scenarios. Platforms embedding physical and transition risk models capture incremental budget from sustainability officers.
- AI-Augmented Surveillance:Natural language processing of regulatory filings and anomaly detection in transaction patterns converge. Early movers are bundling these capabilities into unified control towers.
Industry Challenges
- Cross-Border Interpretation Variance:BaFin, ACPR, and Bank of Italy apply DORA implementation standards inconsistently. Multi-jurisdictional institutions face duplicated compliance engineering for equivalent controls.
- Third-Party Risk Cascade:ICT service provider concentration under DORA Article 28 requires continuous monitoring of vendors' vendors. Mapping fourth-party dependencies exhausts available risk analyst capacity.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Europe Risk Management Market |
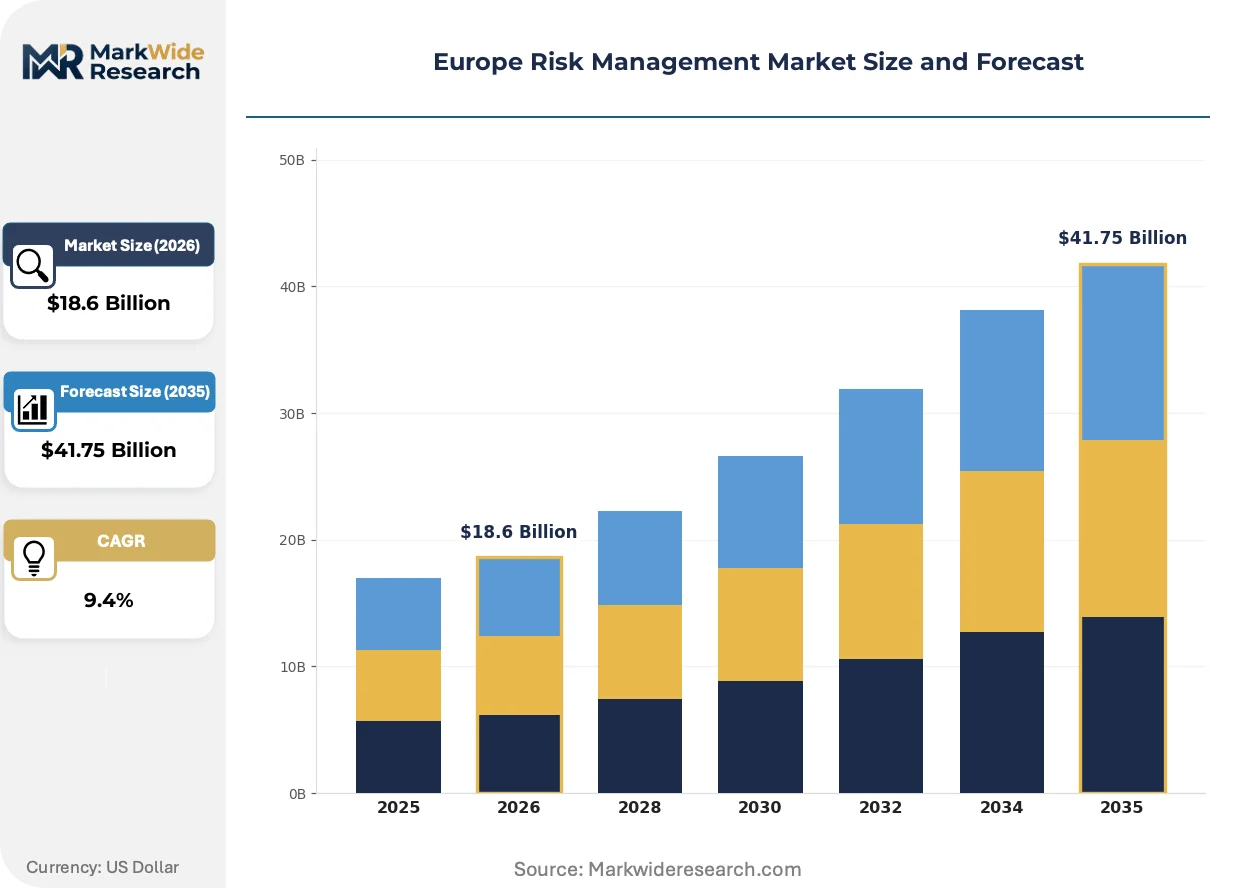
| Market Size in 2026 | $18.6 Billion |
| Market Size in 2035 | $41.75 Billion |
| CAGR (2026 – 2036) | 9.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Consulting, Software, Training, Support Client Type: Corporates, Government Agencies, Financial Institutions, Non-Profits Industry Vertical: Healthcare, Manufacturing, Energy, Retail Solution: Enterprise Risk Management, Compliance Management, Operational Risk Management, Cybersecurity Solutions |
| Companies Covered | SAP SE, MetricStream, NAVEX Global, Deloitte, PwC, Ernst & Young Global Consulting Services, SAS Institute, LogicGate, Riskonnect, Others |
| Regions Covered | Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Europe Risk Management Market Trends and Innovations
DORA's January 2025 enforcement deadline is catalyzing three distinct technical and organizational shifts: unified control architectures replacing siloed point solutions, regulatory calculation engines moving to real-time processing, and procurement authority consolidating into specialized risk technology functions.
Graph-based risk data models are unifying previously disconnected credit, operational, and cyber risk datasets into queryable relationship networks. Tier 1 banks in Frankfurt and Paris are deploying these systems to satisfy DORA's unified incident reporting requirements. The technology is unifying vendor selection criteria around API-native architectures that compress integration timelines from quarters to weeks.
The EU AI Act's risk-based classification system is mandating algorithmic audit trails for high-risk financial applications. Automated decision systems used in credit scoring and fraud detection now require documented risk management procedures. French and Dutch regulators are issuing the first compliance guidance, pushing institutions to retrofit existing machine learning pipelines with explainability layers.
Centralized risk technology procurement functions are displacing distributed buying across business lines. Chief Risk Officers in London and Zurich are consolidating vendor relationships to capture scale discounts and simplify DORA accountability. This concentration is visible most acutely in German banking groups, where procurement teams now report directly to board-level risk committees rather than IT functions.
Europe Risk Management Market Segmentation
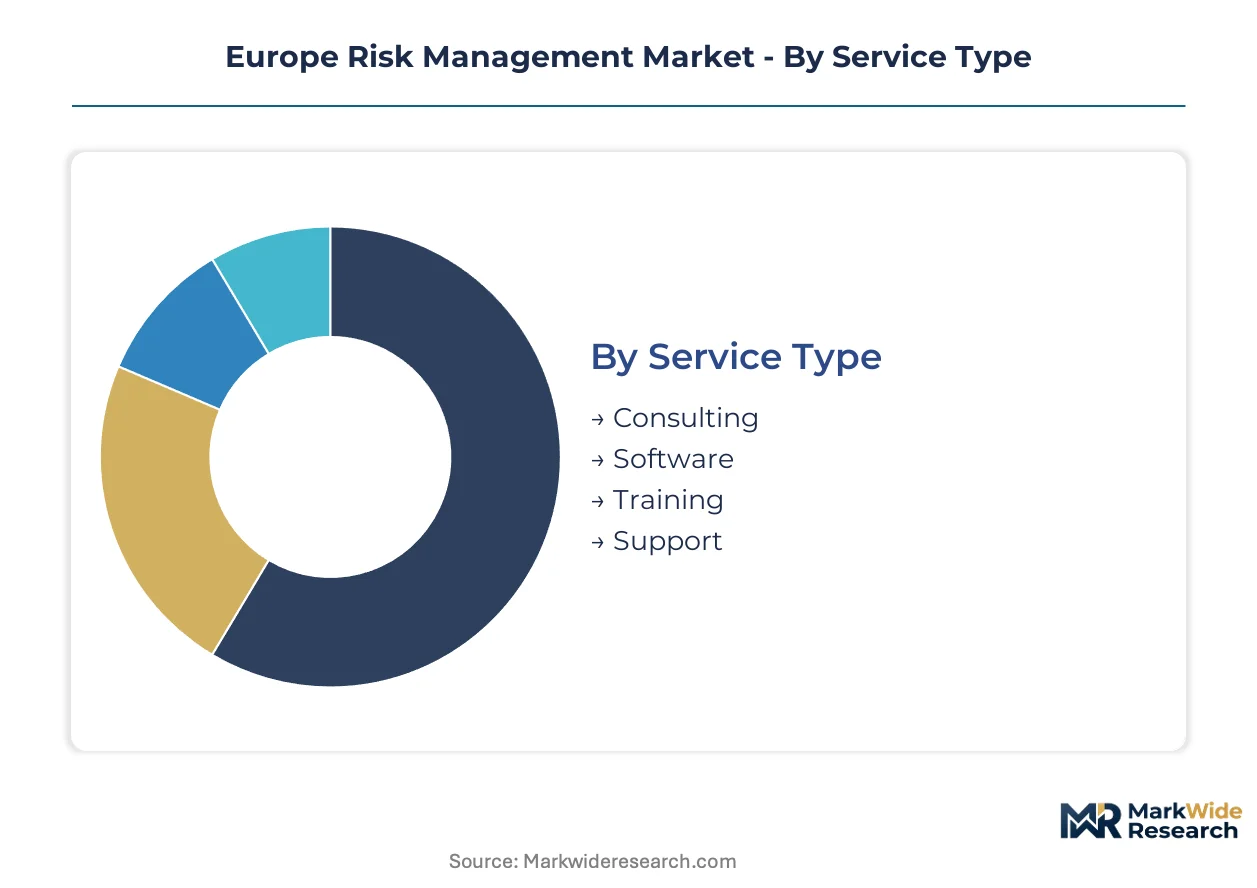
European risk management procurement fragments across four intersecting dimensions that determine contract value, implementation complexity, and regulatory exposure. Vendors must map these segments precisely to align product roadmaps with buyer capital cycles and compliance deadlines.
Service Type:
Software solutions demand the heaviest upfront capital deployment, with cloud-native platforms requiring infrastructure investments that dwarf consulting engagements.
- Software:Cloud-native risk platforms integrate real-time calculation engines with containerized deployment architectures. German banking groups in Frankfurt and Munich are consolidating procurement around these systems to meet DORA's unified control requirements, compressing implementation timelines from quarters to weeks.
- Consulting:Advisory services bridge regulatory interpretation with technology implementation, commanding premium fees for DORA-certified specialists. BaFin's strict interpretation timelines in Germany create concentrated demand for policy design support.
- Training:Certification programs address acute scarcity of professionals combining quantitative modeling with EU regulatory expertise. Programs focus on DORA, GDPR, and EU AI Act compliance pathways.
- Support:Managed services maintain risk infrastructure post-deployment, with 24/7 monitoring mandates under DORA's incident reporting thresholds.
Software absorbs the bulk of installed capacity; consulting is expanding most quickly as institutions race to interpret overlapping regulatory regimes.
Client Type:
Contract values scale with organizational complexity and regulatory scrutiny, creating distinct procurement patterns across institutional categories.
- Financial Institutions:Banks, insurers, and asset managers face the densest regulatory obligations under DORA, GDPR, and ECB supervision standards. These entities drive demand for integrated platforms spanning credit, operational, and cyber risk domains.
- Government Agencies:Sovereign-grade resilience frameworks accelerate adoption across defense, treasury, and critical infrastructure ministries. French and Dutch regulators issue early compliance guidance for algorithmic audit trails.
- Corporates:Industrial conglomerates and multinational enterprises deploy risk management for supply chain continuity and ESG disclosure under CSRD requirements.
- Non-Profits:Charitable foundations and NGOs adopt streamlined risk frameworks focused on operational continuity and donor accountability.
Financial Institutions command the largest contract values; Government Agencies are climbing the fastest as sovereign resilience mandates proliferate.
Industry Vertical:
Sector-specific regulatory density shapes solution customization requirements and sales cycle duration.
- Healthcare:EMA pharmacovigilance guidelines and patient data protections under GDPR create specialized risk system requirements. Hospital networks and pharmaceutical manufacturers invest in integrated compliance platforms.
- Energy:Critical infrastructure designation under EU cybersecurity directives mandates continuous monitoring of operational technology systems. Grid operators and renewable asset managers face ECB climate stress testing integration.
- Manufacturing:Supply chain resilience and product liability frameworks drive adoption of operational risk management tools. German automotive and industrial equipment sectors lead procurement volume.
- Retail:Payment system security and consumer data governance priorities concentrate demand in e-commerce and omnichannel operators.
Healthcare and Energy absorb the bulk of vertical-specific investment; Energy is gaining share fastest as critical infrastructure protections expand.
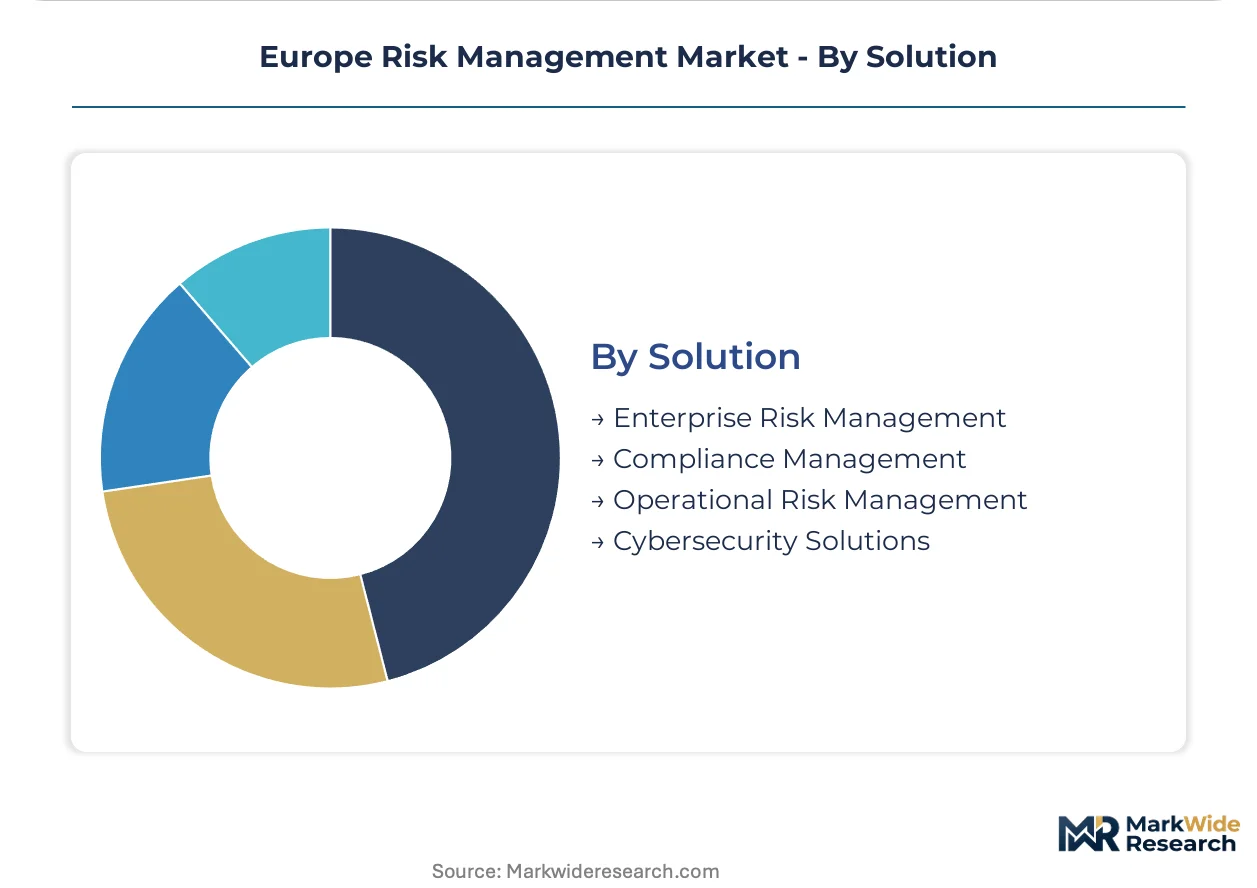
Solution:
Platform maturity and technology architecture determine integration complexity and renewal economics.
- Enterprise Risk Management:Mature core platforms unify credit, market, and operational risk calculations into single governance frameworks. These systems anchor procurement budgets at major banking groups in London, Zurich, and Frankfurt.
- Cybersecurity Solutions:Real-time threat detection and automated incident reporting address DORA's ICT risk mandates. Open banking APIs and third-party fintech integrations multiply vulnerability vectors requiring continuous surveillance.
- Operational Risk Management:Workflow automation replaces manual assessment protocols, with particular emphasis on third-party vendor monitoring under DORA Article 28.
- Compliance Management:Regulatory calculation engines process multi-jurisdictional obligations, with French and Dutch authorities issuing the first EU AI Act implementation guidance.
Enterprise Risk Management retains the largest installed base; Cybersecurity Solutions show the steepest expansion trajectory as attack surfaces multiply.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
German banking groups concentrate the heaviest procurement activity, with Frankfurt and Munich driving cloud-native platform adoption ahead of DORA's enforcement timeline.
Germany
BaFin's strict interpretation of DORA compliance deadlines accelerates replacement of legacy governance frameworks. The Digital Operational Resilience Act mandates auditable real-time risk infrastructure by January 2025. Frankfurt's banking density creates concentrated demand for integrated platforms, with procurement teams now reporting directly to board-level risk committees.
United Kingdom
London-based financial institutions navigate overlapping post-Brexit regulatory obligations alongside EU alignment pressures. The Prudential Regulation Authority and Financial Conduct Authority enforce operational resilience standards that mirror DORA requirements. Chief Risk Officers in the City are consolidating vendor relationships to capture scale discounts and simplify accountability structures.
France
ACPR supervision drives adoption of algorithmic audit trails for high-risk financial applications under the EU AI Act. Parisian banking groups deploy graph-based risk data models to unify credit, operational, and cyber datasets. The Autorité de Contrôle Prudentiel et de Résolution issues early compliance guidance for automated decision systems in credit scoring.
Netherlands
Dutch regulators advance implementation standards for the EU AI Act's risk-based classification system. Amsterdam's fintech ecosystem multiplies third-party integration points requiring continuous ICT risk monitoring. De Nederlandsche Bank supervises stringent incident reporting thresholds that demand automated detection capabilities.
Switzerland
Zurich-based asset managers and private banks invest in sovereign-grade resilience frameworks beyond EU jurisdiction. FINMA operational risk requirements converge with DORA-equivalent standards for cross-border institutions. The Lake Geneva corridor attracts specialized risk technology procurement functions consolidating previously distributed buying authority.
Europe Risk Management Market Competitive Landscape
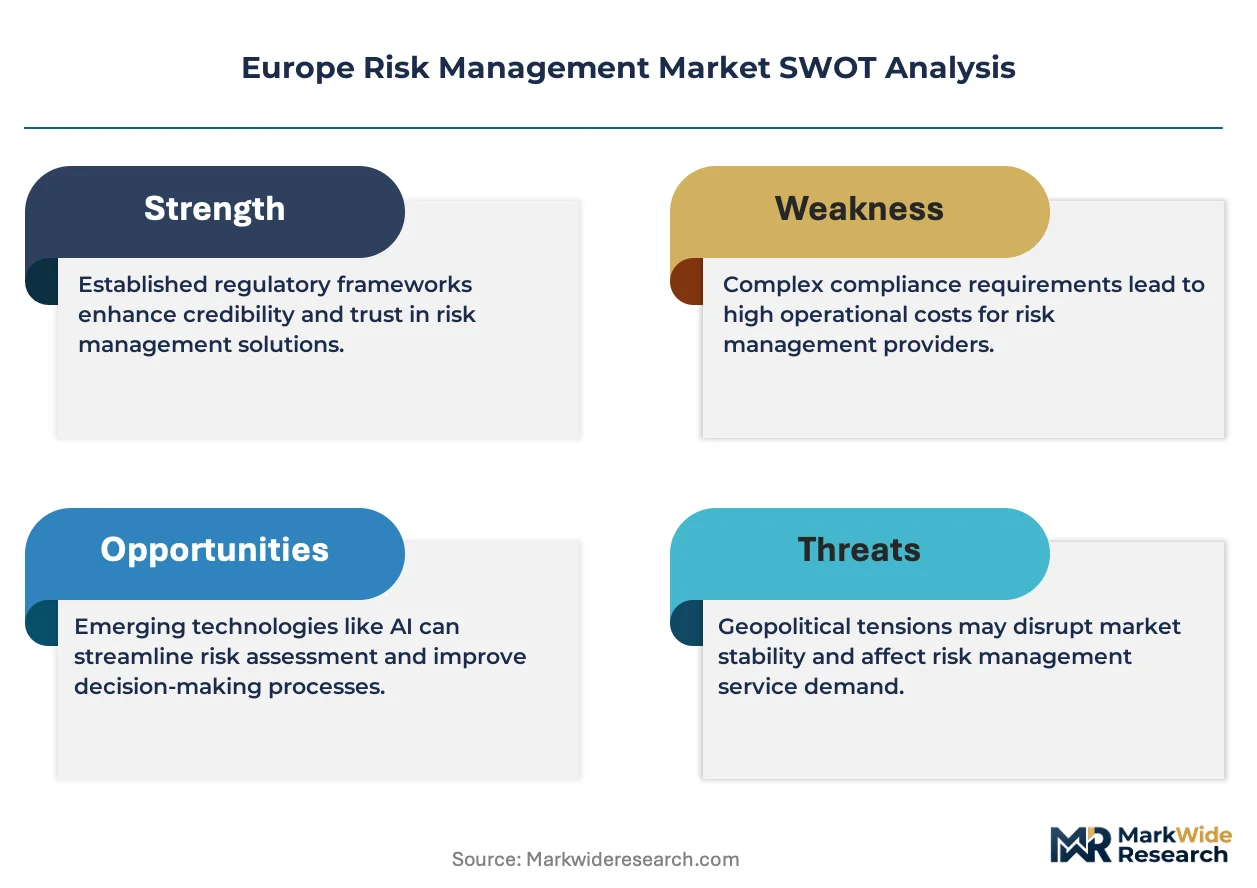
Strategic partnerships dominate the current landscape as vendors race to bundle regulatory interpretation with technology deployment. The market structures around three tiers: ERP-embedded platforms, specialized analytics engines, and consulting-led implementation models. Two strategic archetypes prevail — integrated suite providers leveraging existing financial system footprints, and boutique specialists offering jurisdiction-specific compliance modules. M&A activity and cloud certification partnerships represent the dominant competitive moves as firms seek DORA-ready delivery capabilities.
Among Germany-based enterprise software providers, SAP SE anchors the ERP-embedded tier with risk workflows integrated inside existing financial infrastructure. SAS Institute exemplifies the analytics-specialist archetype through advanced engines processing real-time regulatory calculations. Deloitte occupies the consulting-led implementation position, bridging policy design with technology deployment across multi-jurisdictional institutions. These three patterns represent the structural options available to European buyers consolidating procurement authority ahead of enforcement deadlines.
| Leading Market Players |
|---|
| SAP SE |
| MetricStream |
| NAVEX Global |
| Deloitte |
| PwC |
| Ernst & Young Global Consulting Services |
| SAS Institute |
| LogicGate |
| Riskonnect |
| Others |
Pricing and Supply Chain Analysis
German banking groups concentrating procurement authority ahead of DORA deadlines anchor pricing power with vendors. Cloud-native platform providers command premium subscription tiers for real-time regulatory calculation engines, while consulting-heavy implementations face margin compression from talent scarcity.
Pricing Analysis
Volume concentrates in SaaS-tiered subscriptions for integrated risk platforms, while margin pools in specialized DORA implementation consulting. Three-tier pricing structure across premium, standard, and economy levels separates sovereign-grade hosting certifications from mid-market cloud deployments. Pricing pressure stems from hyperscale provider concentration in AWS, Azure, and Google Cloud. Tier 1 banks in Frankfurt show lowest price sensitivity; mid-market insurers in Poland exhibit highest.
Supply Chain Analysis
EU sovereign-grade hosting certifications gate supply chain participation for risk workload infrastructure. Cloud infrastructure concentrates in Ireland, Germany, and the Netherlands for data residency compliance. Software development draws from specialized quantitative risk modeling talent pools in London and Zurich. Single-source vulnerability runs through narrow hyperscale provider sets. Distribution runs through direct enterprise sales with embedded professional services.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
DORA-certified implementation specialists represent the binding capacity constraint propping vendor margins. Procurement compression timelines limit buyer negotiation leverage against qualified providers.
For Market Incumbents: Acquire specialized DORA consulting capabilities to capture implementation premium before talent scarcity eases. Consolidate cloud certification partnerships across AWS, Azure, and Google Cloud to reduce sovereign hosting risk. Deepen API-native architecture investments to compress integration timelines against boutique competitors.
For New Entrants and Emerging Players: Begin with climate risk integration modules targeting ECB stress testing mandates as the most penetrable white space. Poland and Czech Republic shared service centers offer lower-cost DORA-compliant delivery entry points. Lead with sustainability officer relationships rather than risk committee access.
For Investors and Strategic Acquirers: The window for entry favors boutique regulatory interpretation specialists with established BaFin or ACPR relationships. Long-term viability hinges on bundled platform-consulting capabilities rather than pure software or pure advisory. Watch for DORA enforcement variance across national supervisors as inflection signal.
| Strategic Initiative | Industry Significance |
|---|---|
| Cloud Certification Partnership | Secures sovereign-grade hosting eligibility under DORA data residency requirements. |
| Regulatory Interpretation Acquisition | Captures BaFin-certified specialist capacity ahead of compliance deadline compression. |
| Climate Risk Module Development | Addresses ECB forward-looking scenario mandates for physical and transition risk. |
| API-Native Architecture Investment | Compresses integration timelines from quarters to weeks for German banking groups. |
| CEE Shared Service Expansion | Exploits Warsaw and Prague labor cost advantages for DORA-compliant outsourcing. |
Research Methodology
Trade association data, regulatory filings, and customs records anchored secondary inputs for this Europe Risk Management Market analysis. Primary interviews with Chief Risk Officers, procurement leads at Frankfurt banking groups, DORA implementation specialists, and cloud platform engineers combined with BaFin enforcement guidance, ECB supervision standards, and EIOPA insurance data. Bottom-up platform deployment tracking and top-down regulatory spend estimates were triangulated.
Segment-level modeling captured software versus consulting versus training service types, financial institution versus government agency client categories, and cybersecurity versus enterprise risk management solution archetypes across the projection horizon. CAGRs derived from deployment velocity curves and compliance deadline clustering. Forecast inputs included DORA enforcement variance scenarios and cloud migration acceleration patterns.
Underlying measurement precision varies by segment; software platform sizing carries tighter precision than consulting revenue allocation. Forecasts reflect assumptions around regulatory interpretation consistency and hyperscale provider certification maintenance. A model refresh is warranted upon material change in DORA enforcement timelines or EU AI Act implementation guidance.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Risk Management and Compliance
UK Anti Money Laundering Solutions Market
Risk Management and Compliance
Global Risk and Compliance Consulting Services Market
Risk Management and Compliance
Global Compliance Management Software Market
Risk Management and Compliance
Europe Strategy Consulting Market
Risk Management and Compliance
Quality Warranty Management Market
Risk Management and Compliance
Corporate Investigation Services Market
Risk Management and Compliance
BFSI Security Market
Risk Management and Compliance
Southeast Asia Credit and Risk Management Market
Risk Management and Compliance
Surety Market
Risk Management and Compliance
Treasury and Risk Management Market
Risk Management and Compliance
NPL Management Market
Risk Management and Compliance
Europe Strategic Consulting Services Market
Risk Management and Compliance
AI in Fraud Management Market
Risk Management and Compliance
Third Party Risk Management Market
Risk Management and Compliance
Fraud Detection and Prevention (FDP) Market
Risk Management and Compliance
Global Energy Trading and Risk Management (ETRM) Market