
 Policy Orchestration Market | 2026-2036
Policy Orchestration Market Size, Share, and Industry Trends Forecast 2026-2036
Policy Orchestration Market Analytics
Cloud security architect talent scarcity is reorganizing how enterprises evaluate policy orchestration vendors. Immuta Inc leverages native data access controls to anchor cloud-native deployments across regulated industries. Tufin competes through firewall workflow automation that sustains enterprise network segmentation at scale. FireMon dominates hybrid visibility use cases where policy drift detection determines compliance posture.
Policy orchestration denotes the automated design, deployment, monitoring, and reconciliation of security and governance rules across distributed IT estates, typically operating through API-driven policy engines that enforce intent-based configurations in real time. The discipline eliminates manual rule translation between network layers, cloud consoles, and identity systems to prevent access misconfigurations and audit failures. Cloud-based deployment now captures the fastest expansion as multi-cloud sprawl outpaces on-premises refresh cycles. Compliance management applications concentrate margin pools where continuous control monitoring replaces point-in-time audits. Financial services end users lead contract value despite longer procurement cycles tied to regulatory validation requirements.
The EU AI Act, GDPR, and NIS2 Directive collectively mandate auditable policy enforcement with prescribed response timelines, compelling vendors to embed automated evidence collection into core architectures. The SEC cybersecurity disclosure rules and HIPAA security standards extend this pattern across Atlantic-facing enterprises. Stakeholders must weigh interoperability commitments against vendor lock-in risks as regulatory fragmentation deepens across jurisdictions.
Market Dynamics
Cross-border data sovereignty mandates are fragmenting policy enforcement architectures, forcing enterprises to deploy jurisdiction-specific policy engines rather than centralized rule sets. This structural pressure is compressing vendor consolidation timelines while elevating interoperability requirements.
Growth Catalysts
- EU AI Act enforcement:Auditable automated decision-making mandates are accelerating procurement of integrated governance platforms across financial services and healthcare sectors.
- Cloud-native security stacks:Kubernetes-native policy controllers are displacing legacy network-layer enforcement, enabling real-time reconciliation across multi-cloud estates.
- Germany:The NIS2 Directive implementation is driving federal agency and critical infrastructure operator investment in continuous control monitoring systems.
Market Restraints
- Specialized talent scarcity:Cloud security architect shortages inflate implementation costs and extend deployment timelines by 40-60% for complex hybrid environments.
- API dependency concentration:Reliance on hyperscaler-native policy APIs creates vendor lock-in exposure and complicates multi-cloud portability.
- Regulatory fragmentation:Divergent breach notification timelines between GDPR, state-level US privacy laws, and sector-specific mandates multiply compliance engineering overhead.
Strategic Opportunities
- France:Underpenetrated mid-market manufacturing verticals present whitespace for policy-as-code solutions targeting operational technology convergence.
- Zero trust architecture convergence:Integration of identity-aware proxies with data access policy engines opens unified enforcement platforms.
- UK digital identity frameworks:Emerging government-verified identity standards create demand for attribute-based policy orchestration in public sector procurement.
Industry Challenges
- Legacy mainframe integration:Mainframe security rule extraction and translation to cloud-native policy languages requires specialized tooling scarce in vendor ecosystems.
- Evidence collection standardization:Divergent audit trail formats across policy engines complicate continuous compliance reporting for multinational enterprises.
- Cross-functional alignment:Security, legal, and data engineering teams maintain conflicting policy interpretation frameworks, delaying production deployments.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Policy Orchestration Market |
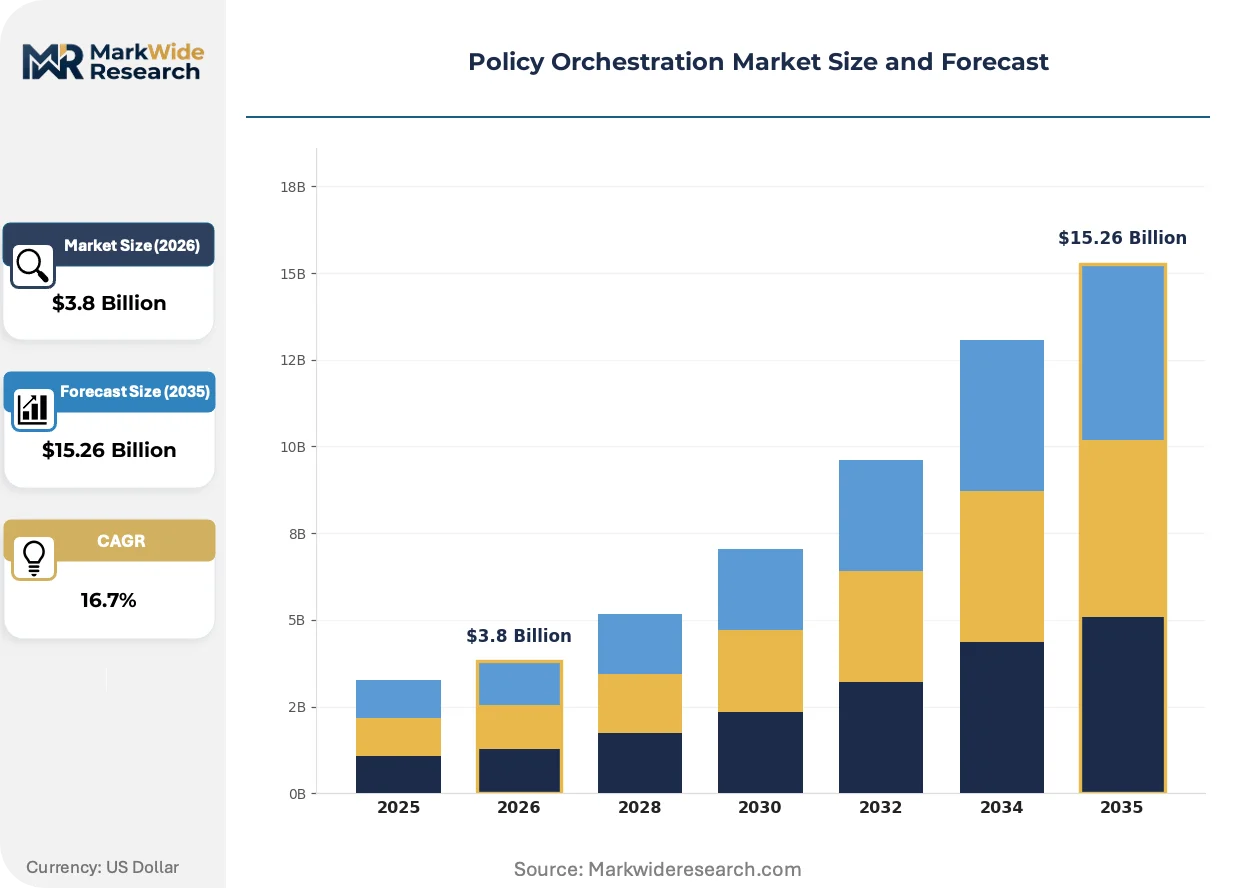
| Market Size in 2026 | $3.8 Billion |
| Market Size in 2035 | $15.26 Billion |
| CAGR (2026 – 2036) | 16.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premises, Cloud-Based, Hybrid, Multi-Cloud Application: Network Security, Data Protection, Compliance Management, Incident Response End User: Enterprises, Government Agencies, Educational Institutions, Financial Services Solution: Policy Management, Workflow Automation, Integration Tools, Monitoring Systems |
| Companies Covered | Immuta Inc, Trellix, Apolicy, TrueOps, McAfee, PolicyIQ, Tufin, FireMon, PolicyHub, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Policy Orchestration Market Evolving Landscape
Policy enforcement architectures are undergoing fundamental restructuring as static rule-based systems give way to dynamic, context-aware engines. Three convergent developments are compressing traditional vendor positioning and reshaping procurement criteria.
Intent-based policy definition languages are decomposing monolithic firewall rule sets into declarative, version-controlled configurations. Financial services institutions in London and Frankfurt are adopting these languages at the fastest pace, replacing manual change tickets with automated CI/CD pipelines. This decomposition is collapsing the traditional separation between network security and DevSecOps tooling categories.
The EU AI Act's risk classification framework is mandating algorithmic impact assessments with prescribed documentation standards. Industrial consequence includes embedding policy enforcement telemetry directly into machine learning pipelines rather than treating governance as post-hoc audit activity. High-risk AI system deployers in healthcare diagnostics and credit scoring are responding by procuring integrated MLOps-governance platforms.
Enterprise buyers are consolidating vendor relationships around platforms offering unified network, cloud, and data policy enforcement. System integrators and managed security providers are capturing deployment and operational contracts that previously flowed to point-solution vendors. This concentration is most visible in the United Kingdom, where NHS trusts and financial regulators are driving framework agreements with multi-domain coverage requirements.
Policy Orchestration Market Segmentation
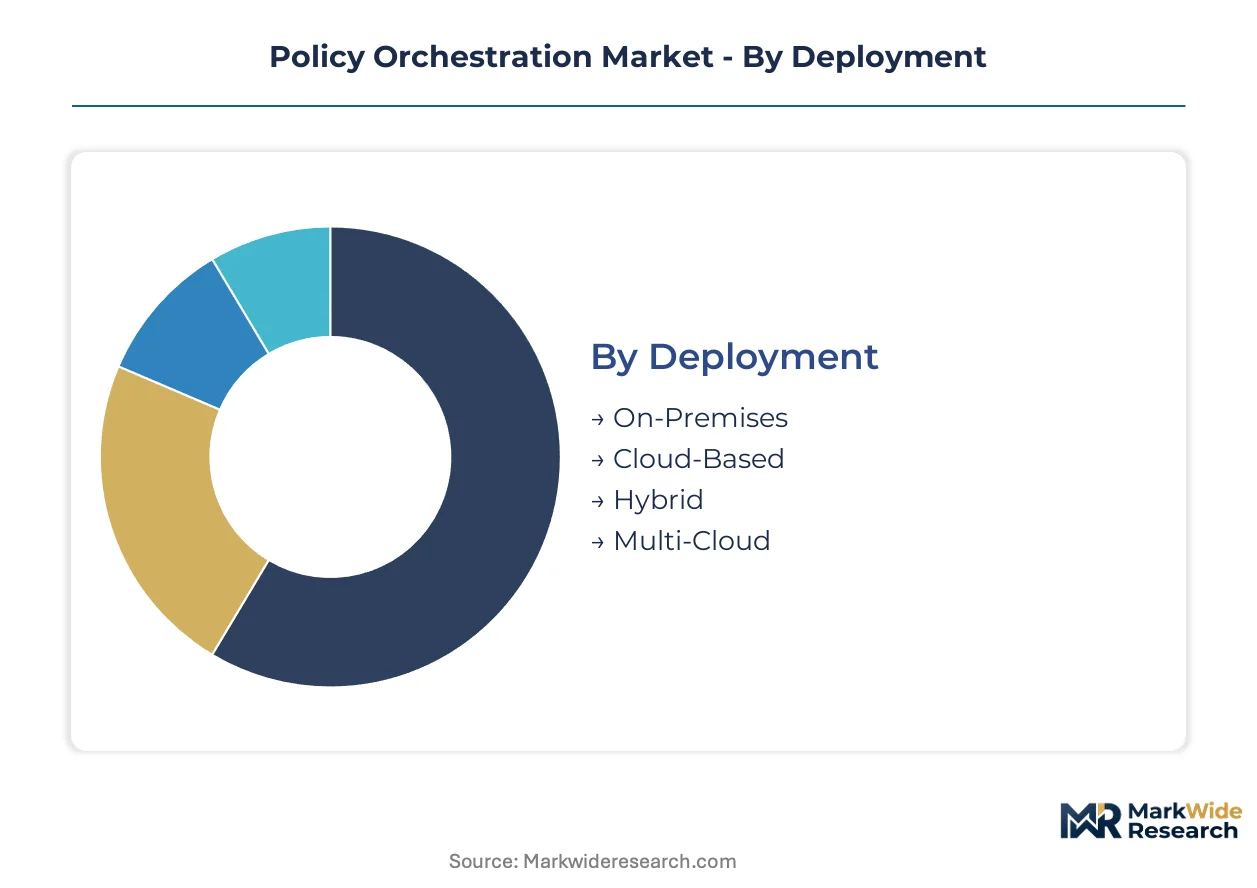
Policy orchestration procurement patterns diverge sharply across deployment architectures and governance applications. Segmentation reveals how regulatory complexity and cloud migration timelines reshape vendor positioning across enterprise technology stacks.
Deployment:
EU AI Act and GDPR mandate distinct data residency controls that reshape infrastructure choices across jurisdictions.
- Cloud-Based:Native API-driven policy engines enforce configurations across AWS, Azure, and GCP estates without on-premises hardware. Financial services institutions in Frankfurt and London prioritize these deployments to satisfy GDPR Article 44 transfer mechanism requirements while maintaining audit trails.
- Hybrid:Split architectures maintain sensitive policy logic on-premises while extending enforcement to cloud workloads through secure federation protocols. German critical infrastructure operators under NIS2 Directive obligations favor this model for operational continuity guarantees.
- On-Premises:Air-gapped installations serve defense contractors and classified government facilities with zero external connectivity mandates.
- Multi-Cloud:Abstraction layers normalize policy syntax across heterogeneous provider environments, addressing portability concerns for US-EU dual-headquartered enterprises.
Cloud-Based handles the majority of throughput; Multi-Cloud is the fastest mover on share.
Application:
Procurement priorities cluster around continuous compliance validation rather than point-in-time security hardening.
- Compliance Management:Automated control monitoring replaces manual audit preparation with real-time evidence collection aligned to SEC disclosure rules and EU AI Act documentation standards. Healthcare systems managing HIPAA security rule attestations drive contract value concentration here.
- Network Security:Intent-based firewall rule orchestration collapses change windows from weeks to minutes through CI/CD pipeline integration. London-based investment banks deploy these capabilities to satisfy Prudential Regulation Authority operational resilience expectations.
- Data Protection:Dynamic data access policies enforce least-privilege principles across structured and unstructured repositories.
- Incident Response:Automated policy suspension and quarantine workflows accelerate breach containment within regulatory notification timelines.
Compliance Management commands the highest per-seat pricing; Network Security shows the steepest expansion trajectory.
End User:
Contract complexity scales with regulatory scrutiny intensity and cross-border operational footprint.
- Financial Services:Multi-jurisdictional banks require unified policy engines spanning Basel III operational risk frameworks, SEC cybersecurity disclosures, and GDPR accountability obligations. Extended procurement cycles reflect three-party validation between security, legal, and risk functions.
- Government Agencies:Federal and state entities mandate FedRAMP or equivalent certifications with sovereign cloud deployment options. French ANSSI-qualified platforms capture defense and interior ministry frameworks.
- Enterprises:Fortune 500 manufacturers prioritize OT-IT convergence policy standardization.
- Educational Institutions:Research universities balance open collaboration mandates against export control compliance for dual-use technology access.
Financial Services contributes the dominant share of annual contract value; Government Agencies are climbing fastest on procurement volume.
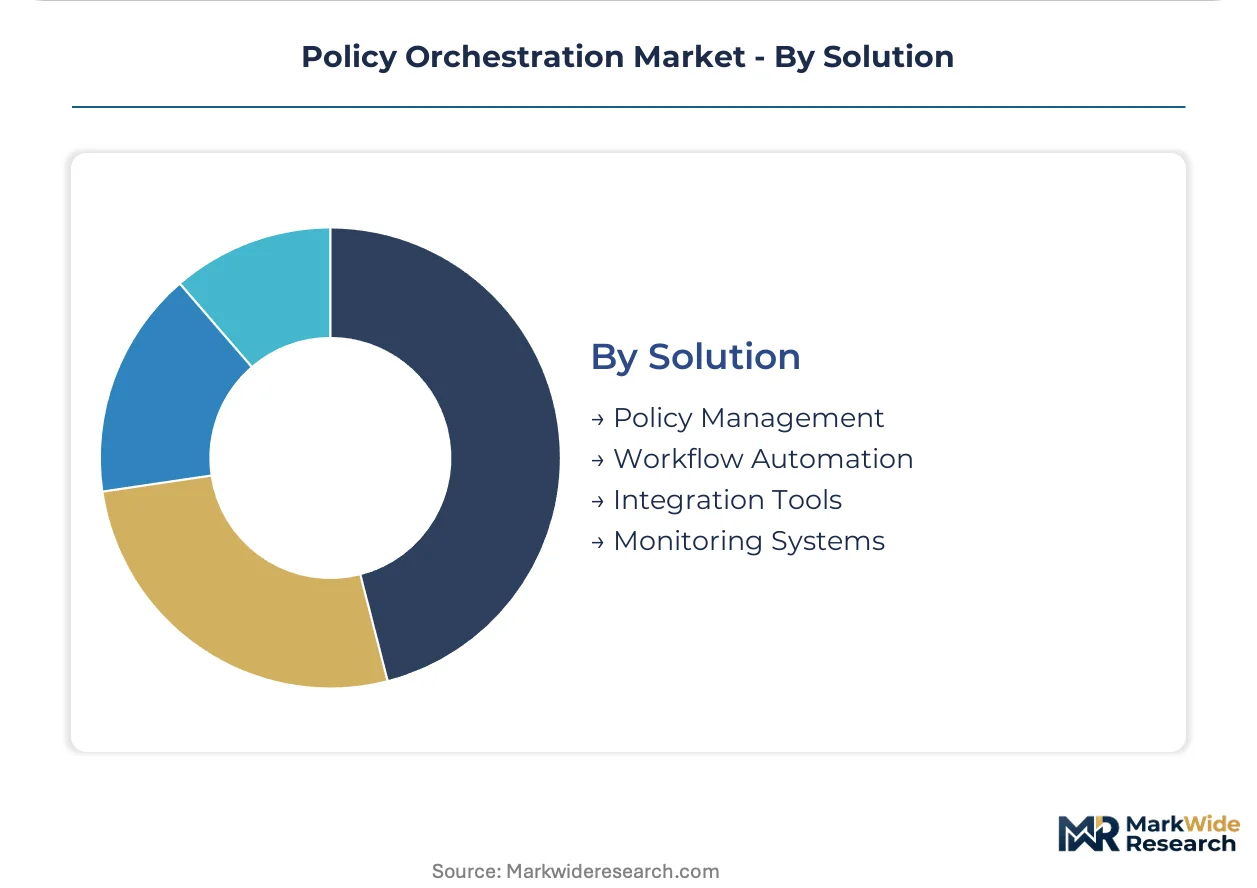
Solution:
Platform consolidation favors vendors offering unified policy lifecycle management over point-tool integration.
- Policy Management:Centralized rule repositories with version control, impact simulation, and rollback capabilities anchor enterprise deployments. These systems translate natural-language governance requirements into machine-enforceable configurations across network, cloud, and identity layers.
- Workflow Automation:Change orchestration pipelines eliminate manual ticket handoffs between security operations and infrastructure teams. UK NHS trusts deploy these capabilities to accelerate digital service accreditation timelines.
- Integration Tools:Pre-built connectors to ServiceNow, Jira, and SIEM platforms reduce custom development overhead.
- Monitoring Systems:Continuous drift detection and compliance posture dashboards satisfy auditor evidence requirements without manual sampling.
Policy Management anchors the largest installed base; Workflow Automation is expanding most quickly as DevSecOps practices mature.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
German procurement teams command 15-20% pricing premiums over French buyers for equivalent policy orchestration platforms, reflecting divergent compliance engineering requirements and vendor negotiation leverage across Continental Europe.
Germany
Federal agencies and critical infrastructure operators under NIS2 Directive obligations drive sustained demand for hybrid deployment architectures. The national cybersecurity authority BSI mandates sovereign cloud certification for federal procurement frameworks. Frankfurt's financial services cluster anchors the largest enterprise contract values, with Commerzbank and Deutsche Börse deploying continuous control monitoring systems.
United Kingdom
NHS trusts and Prudential Regulation Authority-regulated banks consolidate vendor relationships around multi-domain coverage requirements. The UK National Cyber Security Centre publishes binding operational resilience guidelines with prescribed policy enforcement telemetry standards. London's investment banking quarter leads adoption of intent-based firewall orchestration, collapsing change windows from weeks to minutes.
France
Mid-market manufacturing verticals present underpenetrated whitespace for policy-as-code solutions targeting operational technology convergence. ANSSI-qualified platforms capture defense and interior ministry framework agreements with stringent sovereign deployment mandates. The Île-de-France region concentrates aerospace and defense contractor demand for air-gapped policy engines.
United States
SEC cybersecurity disclosure rules and HIPAA security standards extend auditable policy enforcement requirements across Atlantic-facing enterprises. The Federal Risk and Authorization Management Program (FedRAMP) certification gates federal agency procurement cycles. New York's financial services corridor drives contract value concentration despite extended three-party validation between security, legal, and risk functions.
India
Reserve Bank of India operational risk guidelines and SEBI cybersecurity circulars accelerate financial sector procurement of automated governance platforms. The country's data localization requirements under the Digital Personal Data Protection Act fragment policy enforcement architectures. Mumbai's banking headquarters and Bengaluru's technology services clusters diverge in deployment preferences, with the former prioritizing compliance management and the latter cloud-native security stacks.
Policy Orchestration Market Competitive Landscape
Technology leadership and cost leadership are held by different player archetypes, creating a tiered market structure where specialized governance platforms coexist with broad cybersecurity suites. The vendor base organizes around three strategic archetypes: cloud-native data access specialists, network-layer firewall workflow automators, and hybrid visibility platform providers. Consolidation pressure intensifies as enterprise buyers demand unified network, cloud, and data policy enforcement from single relationships. System integrators and managed security providers capture deployment contracts that previously flowed to point-solution vendors.
Within the cloud-native specialist tier, Immuta Inc and Apolicy occupy positions anchored by native data access control capabilities. Tufin, FireMon, and Trellix exemplify the network-centric workflow automation archetype, with Tufin sustaining enterprise segmentation at scale and FireMon dominating hybrid visibility use cases where policy drift detection determines compliance posture. McAfee and PolicyIQ represent broader cybersecurity platform players extending into policy orchestration through portfolio integration.
| Leading Market Players |
|---|
| Immuta Inc |
| Trellix |
| Apolicy |
| TrueOps |
| McAfee |
| PolicyIQ |
| Tufin |
| FireMon |
| PolicyHub |
| Others |
Value Network & Pricing Analysis
Cloud-native platform scale economies compress unit economics for vendors serving multi-tenant deployments, concentrating supply-side leverage among hyperscaler-certified providers while elevating price floors for air-gapped and sovereign-cloud configurations. German federal procurement frameworks under BSI certification requirements sustain 15-20% pricing premiums over equivalent French deployments, reflecting compliance engineering overhead and vendor qualification scarcity.
Pricing Analysis
Configured-to-order pricing for hybrid deployments commands substantial premiums over standard SaaS tiers, with annual contract values scaling on integration complexity and jurisdiction count. Three-tier pricing structure across enterprise, mid-market, and specialist levels segments buyer archetypes, with financial services institutions showing lowest price sensitivity due to regulatory validation requirements. Cost compression in cloud-native tiers is intensifying because hyperscaler marketplace listings commoditize baseline policy engine functionality. Government agencies exhibit highest price sensitivity where FedRAMP and ANSSI certification costs are amortized across constrained procurement budgets.
Supply Chain Analysis
Container availability constraints on Asia-Europe trade lanes elevate inbound logistics costs for hardware-dependent on-premises deployments, though software-centric delivery models mitigate physical supply chain exposure. Engineering talent concentrates in India, Germany, and the United States, with Bengaluru and Frankfurt anchoring platform development centers for vendor R&D operations. Component dependencies span cryptographic modules from Netherlands-based suppliers, identity federation libraries from US open-source foundations, and audit logging infrastructure from Irish data residency providers. Single-source vulnerability in cloud security architect talent pools threatens deployment velocity for complex hybrid environments. Distribution runs through direct enterprise sales with systems integrator overlay, particularly for NHS trusts and German critical infrastructure operators.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The policy orchestration market rewards vendors controlling scarce cloud security architect talent pools and sovereign certification pathways, with capability gaps in legacy mainframe integration and cross-functional policy translation creating structural barriers for undifferentiated entrants.
For Market Incumbents: Compound platform consolidation momentum by embedding automated evidence collection architectures that satisfy EU AI Act documentation standards and SEC cybersecurity disclosure timelines. Acquire specialized workflow automation capabilities in London and Frankfurt financial services corridors to preempt emerging MLOps-governance convergence. Prioritize BSI and ANSSI certification maintenance as competitive moats against cloud-native challengers lacking federal framework presence. For New Entrants and Emerging Players: ANSSI fast-track qualification for mid-market manufacturing verticals in France opens whitespace where operational technology convergence demands outpace incumbent solution coverage. Target policy-as-code deployments for industrial IoT environments underpenetrated by network-centric legacy vendors. Pursue channel partnerships with French aerospace subcontractors seeking air-gapped policy engines without multi-year federal procurement cycles. For Investors and Strategic Acquirers: Mid-cycle technology positioning favors hybrid visibility platforms with drift detection telemetry and continuous control monitoring revenue streams over point-solution firewall workflow automators. Long-term viability hinges on unified network-cloud-data enforcement consolidation, with acquisition premiums accruing to vendors demonstrating NHS trust or German critical infrastructure referenceability. Monitor Kubernetes-native policy controller displacement rates as inflection indicator for legacy network-layer obsolescence timing.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies network, cloud, and data policy enforcement for NHS trust framework compliance. |
| Certification Investment | BSI sovereign cloud qualification gates German federal agency procurement cycles. |
| Acquisition of Specialist Firm | Legacy mainframe rule extraction capabilities address scarce tooling gaps in vendor ecosystems. |
| Strategic Partnership | Systems integrator alliances capture operational contracts from point-solution vendors. |
| Geographic Expansion | Frankfurt and London financial services clusters anchor highest enterprise contract values. |
Research Methodology
Findings reconcile primary fieldwork against secondary review of vendor certification databases, hyperscaler marketplace disclosures, and regulatory filing repositories to establish deployment pattern baselines. Interviews with cloud security architects, compliance officers at multinational banks, federal procurement specialists, and systems integrator deployment leads inform implementation timeline and pricing validation. Secondary sources include BSI certification registries, ANSSI qualified product lists, NHS digital service accreditation records, SEC cybersecurity disclosure filings, and EU AI Act implementation guidance documents. Bottom-up contract value aggregation triangulates against top-down market sizing from platform revenue disclosures.
Segmentation dimensions modeled span deployment architecture, governance application, end-user vertical, and solution component across the projection horizon. Deployment splits capture cloud-based, hybrid, on-premises, and multi-cloud infrastructure choices shaped by GDPR Article 44 transfer mechanisms and NIS2 Directive obligations. Application segmentation tracks compliance management, network security, data protection, and incident response procurement priorities. CAGR derivation incorporates policy engine seat expansion rates, regulatory deadline clustering effects, and cloud migration timeline acceleration from Kubernetes-native controller adoption.
Decision-makers should treat outputs as directional under sustained EU AI Act enforcement and SEC disclosure rule adherence assumptions; material deviation in regulatory timeline delays or hyperscaler API deprecation would warrant model refresh. Forecasts assume continued cloud security architect scarcity extending deployment timelines for complex hybrid environments. Outcomes outside this envelope would require model recalibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Digital Solutions
Multichannel Order Management Market
Digital Solutions
Business Document Work Process Management Market
Digital Solutions
Global Computer Aided Dispatch Market
Digital Solutions
Electronic Data Interchange [EDI] Solution Market
Digital Solutions
Parking Management Systems Market
Digital Solutions
POS Restaurant Management System Market
Digital Solutions
Data Fusion Solutions Market
Digital Solutions
UK High Performance Computing Market
Digital Solutions
Social Employee Recognition Systems Market
Digital Solutions
Contact Tracing Application Market
Digital Solutions
Australia Cloud OSS BSS Market
Digital Solutions
Global Drilling Data Management Systems Market
Digital Solutions
Online Home Service Market
Digital Solutions
Remote Integration Solutions Market
Digital Solutions
Global Smart Offices Market
Digital Solutions
North America API Management Market