

Medical Device Cyber Risk Quantification Market Size, Share, and Industry Trends Forecast 2026-2036
Medical Device Cyber Risk Quantification Market Insights
Subscription-based risk scoring is pivoting how cyber risk quantification vendors monetize their platforms, shifting from perpetual licenses to recurring revenue models tied to device fleet size and threat exposure metrics. Palo Alto Networks leverages its firewall-installed base to cross-sell medical device visibility modules into hospital networks. Armis specializes in passive device discovery, occupying a defensible niche in agentless monitoring for legacy clinical equipment. ClearDATA anchors its offering with HIPAA-compliant cloud infrastructure, extending managed security services to mid-size device manufacturers lacking in-house security operations.
Medical device cyber risk quantification encompasses the systematic measurement, scoring, and financial estimation of cybersecurity exposure across connected clinical assets, typically employing probabilistic threat models, vulnerability severity indices, and business impact calculations to translate technical risk into dollar-denominated loss expectancies. Software solutions and risk analytics platforms command the largest revenue share, while managed security services represent the fastest-expanding margin pool as hospitals outsource continuous monitoring. Deployment via cloud-based architectures is displacing on-premises installations, though hybrid configurations persist where patient data residency requirements intersect with real-time edge processing needs for surgical robots and infusion pumps.
The FDA's premarket and post-market cybersecurity guidance, alongside the EU MDR's general safety and performance requirements enforced by notified bodies, mandates structured risk documentation that directly stimulates demand for quantification tools. NIST's Cybersecurity Framework and ISO 27001 adoption within hospital procurement criteria further standardize vendor qualification, compressing market access for solutions lacking certified methodologies. Stakeholders must monitor how FDA harmonization with international medical device regulator forum standards reshapes the evidentiary burden for cyber risk claims in regulatory submissions.
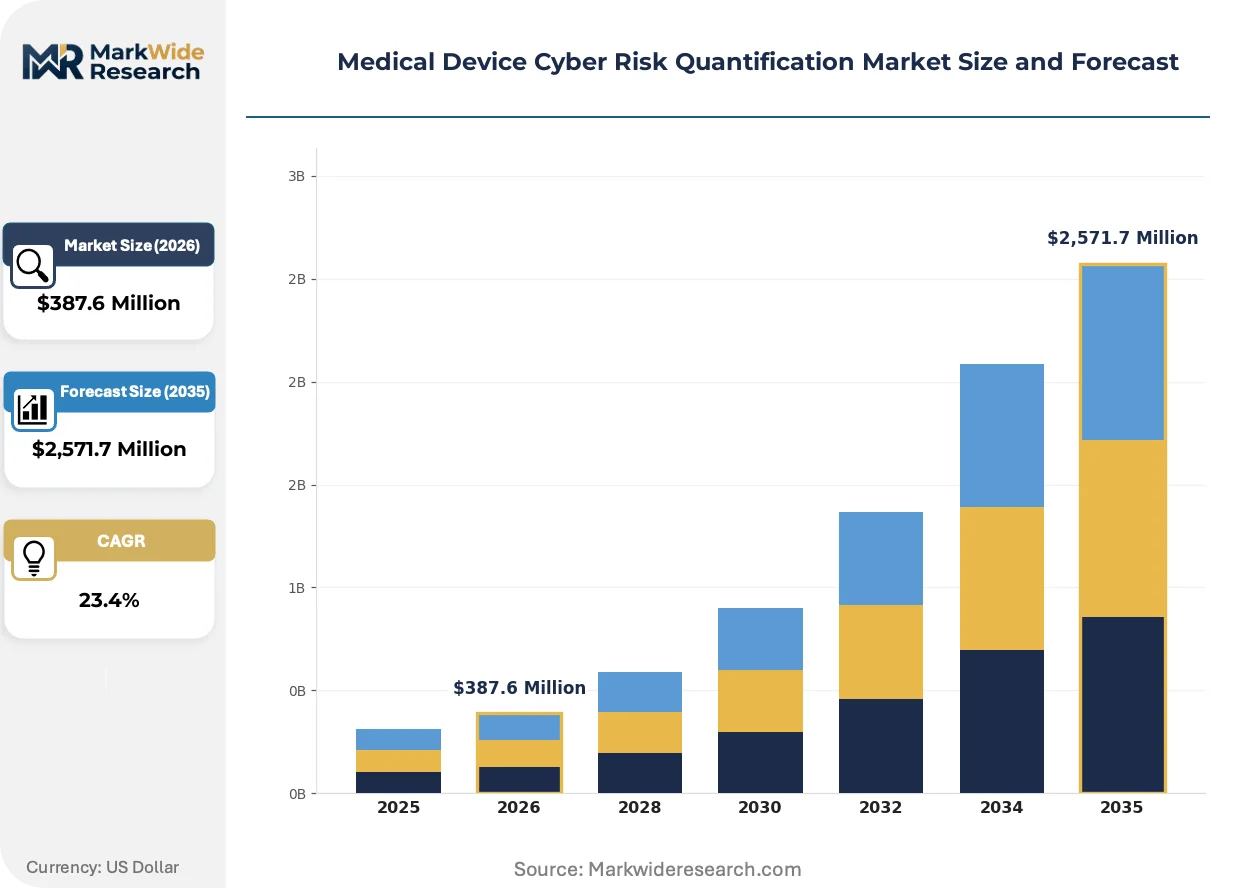
Market Dynamics
Hospital IT departments are consolidating cyber risk oversight under centralized governance frameworks, forcing quantification vendors to integrate with existing electronic health record infrastructure and security information platforms rather than deploy standalone point solutions.
Growth Catalysts
- FDA Post-Market Cybersecurity Guidance:The guidance mandates continuous monitoring and documentation of connected device vulnerabilities, compelling manufacturers to adopt automated risk scoring tools for regulatory compliance.
- Agentless Network Monitoring:Passive discovery technologies eliminate deployment friction on legacy clinical equipment that cannot accommodate endpoint agents, expanding addressable device populations in aging hospital fleets.
- Health System Consolidation:Merged delivery networks in the United States are standardizing enterprise security stacks across acquired facilities, creating procurement scale for integrated risk quantification platforms.
Market Restraints
- Specialized Cybersecurity Talent Scarcity:Hospitals and device manufacturers face acute shortages of professionals trained in both clinical engineering and threat intelligence analysis.
- Legacy Device Longevity:Infusion pumps and patient monitors with decade-long service lives lack modern operating system support, creating persistent unpatched vulnerability exposure.
- Interoperability Certification Costs:ISO 27001 and NIST Cybersecurity Framework validation impose substantial documentation and audit burdens on smaller quantification vendors.
Strategic Opportunities
- EU MDR Annex I Enforcement:Notified bodies are interpreting general safety and performance requirements to encompass cybersecurity documentation, opening procurement pathways for risk quantification tools in European health systems.
- Cloud-Native Risk Analytics:Convergence of serverless architectures with real-time threat feeds enables elastic scaling of computational risk models for seasonal demand fluctuations.
- Mid-Size Device Manufacturers:Outsourced security operations represent an underpenetrated segment where managed risk quantification services can substitute for in-house security operations centers.
Industry Challenges
- False Positive Triage Burden:Risk scoring algorithms generate voluminous alerts requiring clinical engineering review, straining already constrained biomedical technician capacity.
- Patient Data Residency Constraints:Hybrid deployment architectures must reconcile cloud-based analytics with state-level privacy mandates governing protected health information storage.
Report Scope
MarkWide ResearchGet the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Medical Device Cyber Risk Quantification Market Trends and Innovations
Edge computing architectures are redistributing analytical workloads from centralized data centers to hospital network perimeters, enabling sub-second risk scoring for surgical robots and anesthesia systems where latency tolerance approaches zero.
Blockchain-anchored device identity registries are decentralizing trust verification across multi-vendor clinical environments. Health systems in Germany and Switzerland are piloting distributed ledger implementations to authenticate firmware provenance on implantable cardiac devices. This architecture compresses reliance on manufacturer-hosted certificate authorities while enabling peer-to-peer attestation between competing vendor platforms.
The FDA's harmonization with International Medical Device Regulator Forum technical guidance is standardizing evidentiary requirements for cyber risk claims in premarket submissions. Device manufacturers must now document quantitative risk methodologies rather than qualitative assessments, stimulating demand for certified scoring frameworks. European notified bodies are adopting parallel stringency under MDR Article 10, creating transatlantic alignment in documentation expectations.
Health system procurement committees are unbundling cyber risk quantification from broader security service contracts, establishing direct vendor relationships for clinical asset monitoring. This pattern is most pronounced in United States academic medical centers where dedicated biomedical informatics groups negotiate separate statements of work. Purchasing autonomy is compressing traditional channel relationships between hospitals and generalist cybersecurity distributors.
Medical Device Cyber Risk Quantification Market Segmentation
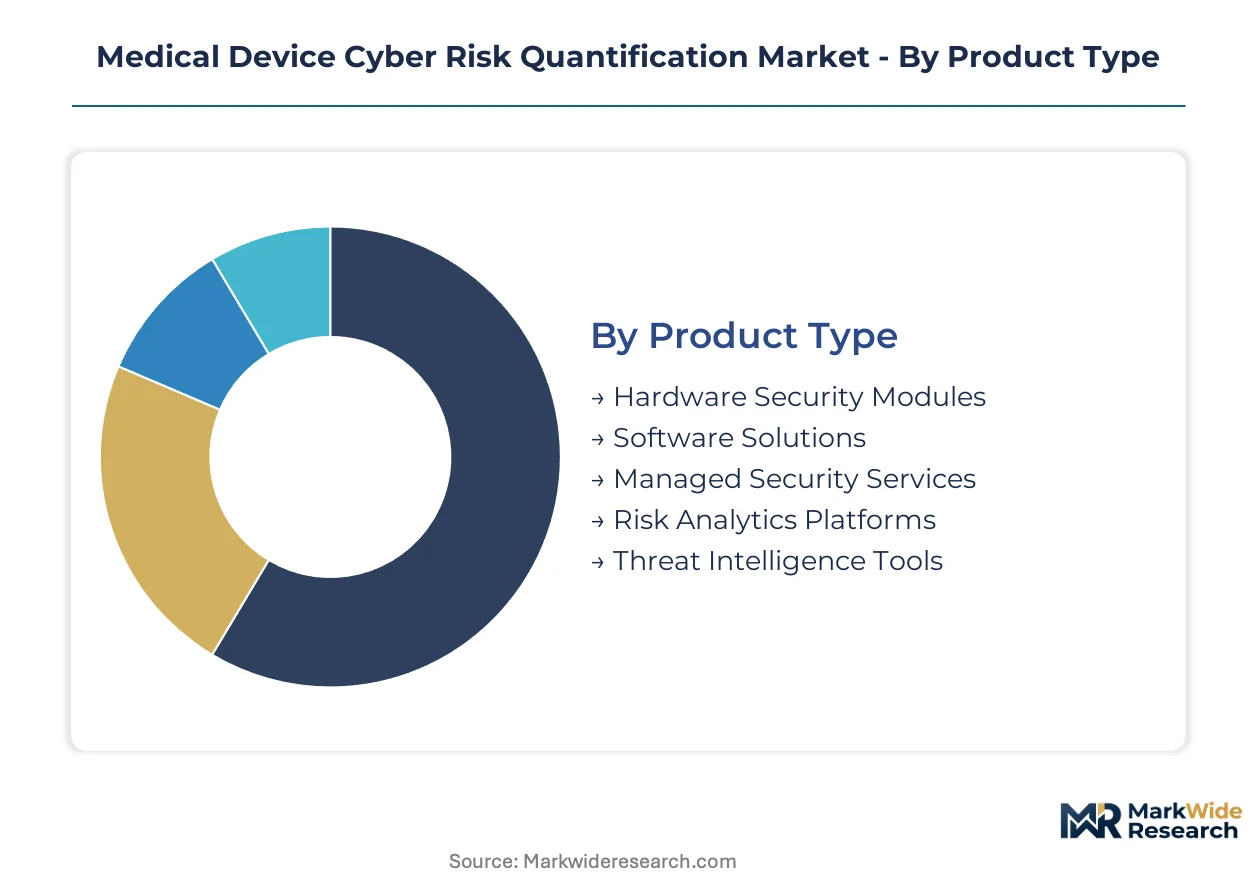
Medical device cyber risk quantification demands precise segmentation alignment with clinical workflows and regulatory documentation requirements. Each category reflects distinct procurement priorities across hospital IT departments and device manufacturers navigating FDA post-market guidance and EU MDR compliance obligations.
Product Type:
The customization-to-standardization spectrum spans from bespoke hardware deployments to configurable SaaS platforms, with hybrid architectures dominating mid-market health systems seeking modular scalability.
- Software Solutions:Configurable risk scoring engines integrate probabilistic threat models with vulnerability severity indices. Hospital IT departments in the United States prioritize these for enterprise-wide device fleet visibility under consolidated governance frameworks.
- Managed Security Services:Outsourced continuous monitoring substitutes for in-house security operations centers at mid-size device manufacturers. This segment climbs the fastest as regulatory documentation burdens intensify and specialized cybersecurity talent scarcity persists across clinical engineering.
- Hardware Security Modules:Tamper-resistant cryptographic processors anchor trust boundaries for high-assurance environments.
- Risk Analytics Platforms:Unified dashboards aggregate multi-source telemetry into dollar-denominated loss expectancies.
- Threat Intelligence Tools:Real-time feeds of medical device-specific indicators of compromise supplement core quantification engines.
Leading the category by volume: Software Solutions. Expanding most quickly: Managed Security Services.
Application:
Cost tier differentiation separates enterprise-grade integrated suites from point solutions targeting specific compliance documentation gaps.
- Vulnerability Assessment:Automated scanning of connected clinical assets identifies unpatched operating systems on legacy infusion pumps and patient monitors. FDA post-market guidance mandates continuous documentation, driving procurement in United States academic medical centers with dedicated biomedical informatics groups.
- Compliance Management:Structured risk documentation frameworks align with NIST Cybersecurity Framework and ISO 27001 certification requirements. European health systems under EU MDR Annex I enforcement represent the steepest expansion trajectory as notified bodies interpret general safety requirements to encompass cybersecurity.
- Threat Modeling:Probabilistic attack path analysis quantifies exposure for premarket submission packages.
- Incident Response:Orchestrated containment workflows address active compromises of surgical robots and anesthesia systems.
- Security Posture Evaluation:Benchmarking dashboards compare device fleet maturity against peer health systems.
Highest procurement concentration: Vulnerability Assessment. Fastest-growing demand: Compliance Management.
End User:
Customer type fragmentation splits between regulated entities bearing direct liability and advisory intermediaries structuring procurement decisions.
- Hospital IT Departments:Centralized governance frameworks consolidate cyber risk oversight across merged delivery networks, creating procurement scale for integrated platforms. United States health system consolidation accelerates standardization of enterprise security stacks.
- Medical Device Manufacturers:Premarket and post-market submission obligations under FDA guidance and EU MDR Article 10 require quantitative risk methodologies rather than qualitative assessments. This segment gains share fastest as evidentiary burdens harmonize across transatlantic regulators.
- Health Information Managers:Data stewardship responsibilities intersect with patient privacy mandates governing protected health information residency.
- Regulatory Agencies:Supervisory bodies leverage vendor platforms for sector-wide risk surveillance.
- Cybersecurity Consultants:Advisory services bundle quantification tools into broader security transformation engagements.
Dominant procurement volume: Hospital IT Departments. Accelerating most rapidly: Medical Device Manufacturers.
Deployment Mode:
Volume concentration favors architectures reconciling real-time edge processing with centralized analytics, particularly for latency-intolerant surgical environments.
- Cloud-Based:Serverless architectures enable elastic scaling of computational risk models for seasonal demand fluctuations. German and Swiss health systems pilot distributed ledger integrations for firmware provenance verification on implantable cardiac devices.
- Hybrid:Split processing reconciles cloud-based analytics with state-level patient data privacy mandates. United States health systems with multi-state footprints require this architecture to satisfy divergent health information storage regulations.
- On-Premises:Air-gapped installations persist where patient data residency constraints prohibit external transmission.
- Edge Computing:Sub-second risk scoring for surgical robots and anesthesia systems redistributes analytical workloads to network perimeters.
- Virtualized Environments:Containerized deployments support rapid instantiation for temporary clinical facilities and disaster response scenarios.
Highest deployment share: Cloud-Based. Sharpest growth curve: Hybrid.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
United States health systems consume the majority of deployed risk quantification platforms, while European and Asian markets accelerate procurement to meet tightening regulatory deadlines. Production of core analytics engines concentrates among software vendors headquartered in North America and Israel. Regional adoption patterns diverge sharply based on reimbursement structures and notified body enforcement timelines.
United States
Hospital consolidation across merged delivery networks creates procurement scale for enterprise-grade cyber risk platforms. FDA post-market cybersecurity guidance mandates continuous vulnerability documentation, compelling manufacturers to automate risk scoring. Academic medical centers in Boston and the San Francisco Bay Area negotiate direct vendor contracts for clinical asset monitoring.
Germany
Notified bodies under EU MDR Annex I interpret general safety requirements to encompass structured cybersecurity documentation. University hospitals in Berlin and Munich pilot blockchain-anchored device identity registries for implantable cardiac equipment. German health information managers face dual pressure from GDPR data residency rules and real-time surgical system latency requirements.
Switzerland
Swissmedic enforcement of MDR cybersecurity provisions drives demand for quantitative risk methodologies in premarket submissions. Zurich and Basel cluster medical device manufacturers seeking outsourced security operations to substitute for scarce in-house talent. Swiss health systems experiment with distributed ledger architectures for multi-vendor firmware attestation.
Japan
PMDA alignment with IMDRF technical guidance standardizes evidentiary requirements for cyber risk claims in device registrations. Tokyo and Osaka metropolitan hospitals consolidate IT governance under centralized frameworks. Japanese manufacturers accelerate adoption of agentless monitoring to address legacy equipment with decade-long service lives.
United Kingdom
MHRA post-Brexit regulatory autonomy maintains parallel stringency to EU MDR cybersecurity expectations. London and Cambridge health technology clusters attract risk quantification vendors targeting mid-size device manufacturers. NHS procurement committees unbundle cyber risk tools from broader security contracts to establish direct platform relationships.
Medical Device Cyber Risk Quantification Market Competitive Landscape
Top-tier vendors anchor enterprise health system deployments, while specialized boutiques occupy agentless monitoring niches and mid-market managed services. The vendor base stratifies across three tiers: network security incumbents with medical device modules, pure-play healthcare cybersecurity specialists, and cloud-native risk analytics platforms. Strategic archetypes include firewall-installed-base cross-sellers, passive discovery technologists, and HIPAA-compliant infrastructure extenders. Dominant competitive moves encompass strategic partnerships with electronic health record vendors and portfolio diversification into managed security services.
Within the network security incumbent tier, Palo Alto Networks and Cisco Systems represent cross-selling archetypes leveraging existing hospital firewall relationships. Armis exemplifies the pure-play specialist model focused on agentless device discovery. ClearDATA anchors the cloud-native infrastructure segment, extending managed services to manufacturers lacking internal security operations. These three vendors collectively illustrate how market position derives from installed base leverage, technical specialization, or compliance-centric infrastructure anchoring.
| Leading Market Players |
|---|
| Palo Alto Networks |
| Armis |
| Check Point Software Technologies |
| Forescout |
| ORDR |
| Medcrypt |
| ClearDATA |
| Philips |
| Cisco Systems |
| Others |
Pricing and Supply Chain Analysis
Cybersecurity talent concentration in Israel and the United States Northeast widens pricing-tier spreads, as labor-cost differentials between these hubs and emerging delivery centers force vendors to stratify subscription rates across premium analyst-augmented tiers and automated economy offerings.
Pricing Analysis
Margin tightening in mid-market SaaS tiers reflects ISO 27001 certification overhead and HIPAA compliance audit costs. Three-tier pricing structure across premium, standard, and economy levels separates white-glove managed detection and response from self-service risk dashboards. Price differentiation traces to certification grade and device fleet scale, with academic medical centers showing lowest sensitivity and rural critical-access hospitals highest. Cost-down pressure on standard tiers accelerates because cloud infrastructure providers commoditize base analytics engines.
Supply Chain Analysis
Domestic-content mandates in United States federal health IT procurement reshape sourcing toward domestic threat-intelligence feed curation and local data-center hosting. Software development concentrates in the United States, Israel, and Ireland. Core platform architecture draws from open-source probabilistic modeling libraries and proprietary clinical device signature databases. Single-source vulnerability rests on concentrated cloud infrastructure providers. Distribution runs through direct enterprise sales teams and health system GPO contracts.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
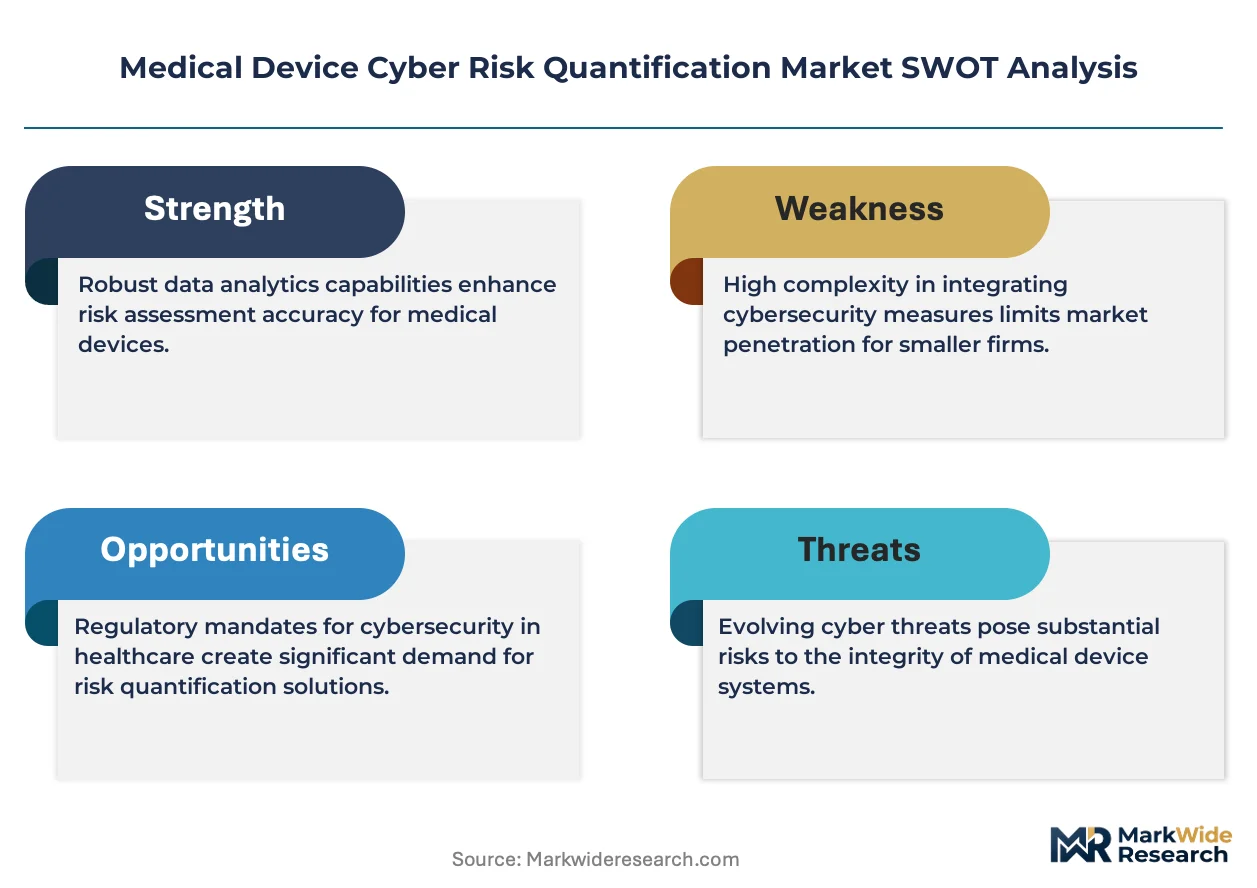
This market functions as a cost-of-compliance arena where FDA post-market cybersecurity guidance erects documentation barriers that reward incumbent vendors with certified methodologies and punishes unvalidated entrants.
For Market Incumbents: Deepen vertical control over threat-intelligence curation by acquiring specialized medical device security research boutiques. Fortify channel relationships with Epic and Cerner integration partnerships before emerging cloud-native platforms disintermediate standalone risk analytics. Prioritize ISO 27701 privacy certification investment to preempt GDPR enforcement escalation in European hospital procurement criteria. For New Entrants and Emerging Players: Capture mid-size device manufacturers in Switzerland and Germany where EU MDR Annex I enforcement outpaces vendor supply. White-space concentration sits with outsourced security operations for manufacturers lacking FDA submission expertise. Go-to-market leverage rests on pre-built documentation templates for 510(k) cybersecurity sections. For Investors and Strategic Acquirers: Re-rating potential sits with agentless monitoring specialists given health system consolidation demand for legacy device visibility without endpoint deployment friction. Long-term viability favors platforms with embedded clinical workflow integration rather than standalone risk scoring. Signal to watch: FDA harmonization with IMDRF standards accelerating evidentiary burden for quantitative risk claims.| Strategic Initiative | Industry Significance |
|---|---|
| FDA Submission Support | Pre-built 510(k) cybersecurity documentation modules compress manufacturer regulatory preparation timelines. |
| Hospital System Partnership | Direct GPO contracts with merged United States delivery networks secure multi-year recurring revenue commitments. |
| CE Marking Pathway | EU MDR Annex I compliance tooling opens procurement channels in German and Swiss university hospital systems. |
| Software Companion Development | Embedded risk scoring within Epic and Cerner workflows reduces standalone platform displacement risk. |
| Reimbursement Strategy | CMS quality metric alignment positions cyber risk quantification as operational necessity for value-based care contracts. |
Research Methodology
Independent corroboration across hospital CISO interviews, biomedical engineering directors, and medical device regulatory affairs leads underwrites the qualitative findings. Primary fieldwork encompassed discussions with GPO contracts managers and health system procurement committees. Secondary validation drew from FDA 510(k) submission databases, CMS hospital cost reports, and EU MDR notified body guidance documents. Bottom-up device fleet sizing triangulates against top-down health IT spending estimates.
Rate-of-change decomposition across the analysis window segments growth by product type, application, end user, and deployment architecture. Modeled dimensions include device fleet size tiers, regulatory jurisdiction clusters, and cloud-native versus hybrid infrastructure preferences. CAGRs derive from elasticity-adjusted adoption curves and compliance deadline clustering. Industry-specific inputs encompass FDA enforcement action frequency and EU notified body capacity constraints.
Forecast confidence holds firmest in the near-window; longer-horizon outcomes carry greater sensitivity to FDA harmonization timing and EU MDR enforcement stringency variation. Projections reflect assumptions regarding health system consolidation velocity and cloud infrastructure cost trajectories. Within these boundaries, the analytical envelope holds.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.