
 Global Risk Management Software Market | 2026-2036
Global Risk Management Software Market Size, Share, and Industry Trends Forecast 2026-2036
Global Risk Management Software Market Foresight
Legacy on-premise infrastructure is pivoting toward containerized microservices architectures, collapsing implementation timelines from months to weeks. IBM Corporation leverages its Watson analytics stack to anchor governance-risk-compliance workflows for multinational banks. Oracle Corporation competes through embedded database-layer security controls that sustain uptime commitments under Basel III operational resilience rules. SAP SE differentiates via native ERP integration, occupying a dominant position in European manufacturing risk orchestration.
Risk management software encompasses algorithmic platforms that quantify, monitor, and mitigate operational, financial, and compliance exposures through statistical modeling, real-time data ingestion, and automated control testing. Core functional parameters include sub-second latency for transaction monitoring, ISO 31000-aligned risk taxonomy engines, and API-first architectures enabling interoperability with existing enterprise systems. Cloud-based deployment leads solution type adoption as regulated entities abandon capital-intensive server farms, while security risk modules represent the fastest-expanding segment due to ransomware frequency and SEC cyber disclosure mandates. Compliance risk retains the deepest margin pools given recurring audit-update subscriptions and jurisdiction-specific rule libraries.
The US SEC, EU EBA, and Monetary Authority of Singapore shape demand through mandatory climate risk stress testing, operational resilience deadlines, and third-party vendor oversight rules that force software procurement cycles. ISO 31000 and NIST CSF certifications function as market access filters, disqualifying uncredentialed vendors from RFP shortlists at tier-one financial institutions. Stakeholders must monitor divergence between US prudential standards and EU Digital Operational Resilience Act requirements, as regulatory fragmentation threatens single-platform deployment economics.
Market Dynamics
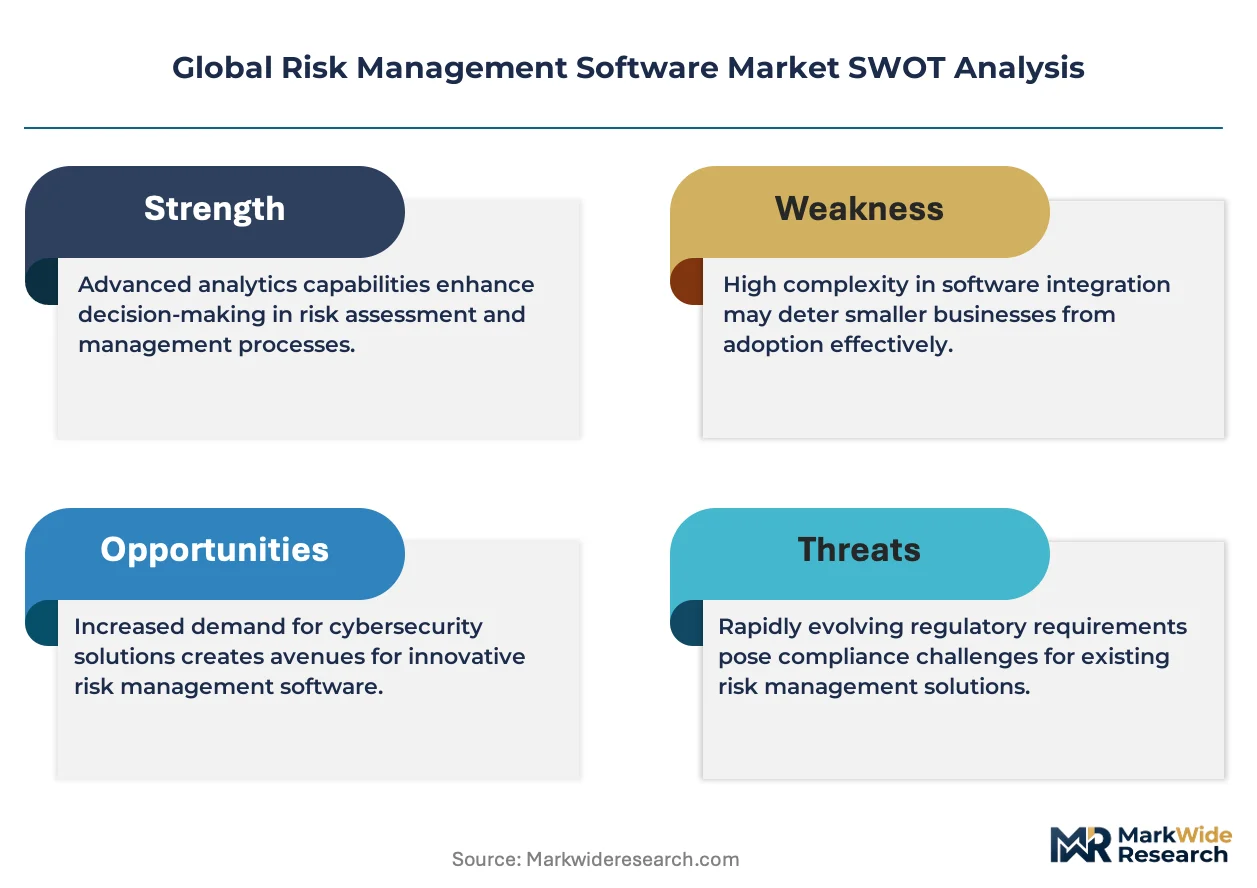
Cloud migration is collapsing deployment timelines from months to weeks while Basel III operational resilience mandates force banks to replace legacy on-premise stacks with API-first architectures that sustain sub-second transaction monitoring latency.
Growth Catalysts
- EU Digital Operational Resilience Act:Mandatory third-party vendor oversight rules across European banking are forcing procurement cycles for integrated risk platforms that automate control testing and audit trails.
- Containerized microservices:Banking institutions are abandoning capital-intensive server farms for Kubernetes-orchestrated deployments that compress implementation windows and reduce infrastructure overhead.
- Singapore:The Monetary Authority of Singapore's climate risk stress testing framework is driving demand for scenario modeling engines among ASEAN financial institutions expanding their sustainability risk capabilities.
Market Restraints
- Specialized talent scarcity:Shortages of professionals combining quantitative risk modeling with cloud-native engineering are inflating implementation costs and extending project timelines for tier-one deployments.
- Data sovereignty fragmentation:Divergent cross-border data localization requirements between the EU, China, and United States are fragmenting single-platform economics and forcing redundant infrastructure investments.
- Legacy system entanglement:Decades-old core banking architectures in established financial institutions create integration friction that slows API-first risk platform adoption despite regulatory deadlines.
Strategic Opportunities
- Manufacturing ERP convergence:Native integration between risk orchestration modules and SAP S/4HANA environments represents underpenetrated white space in European industrial supply chains.
- SEC cyber disclosure mandates:New rules requiring material incident reporting are creating recurring revenue pools for automated security risk modules with real-time breach detection capabilities.
- AI governance tooling:The EU AI Act's algorithmic accountability requirements are opening demand for model risk management platforms that document training data lineage and bias testing protocols.
Industry Challenges
- ISO 31000 certification bottlenecks:Accreditation backlogs are disqualifying uncredentialed vendors from RFP shortlists at tier-one financial institutions, compressing competitive access.
- Multi-jurisdiction rule library maintenance:Jurisdiction-specific compliance content requires continuous legal monitoring and quarterly subscription updates that strain vendor content operations.
- Real-time data pipeline engineering:Sub-second latency requirements for transaction monitoring demand specialized stream-processing architectures that few implementations achieve at scale.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Risk Management Software Market |
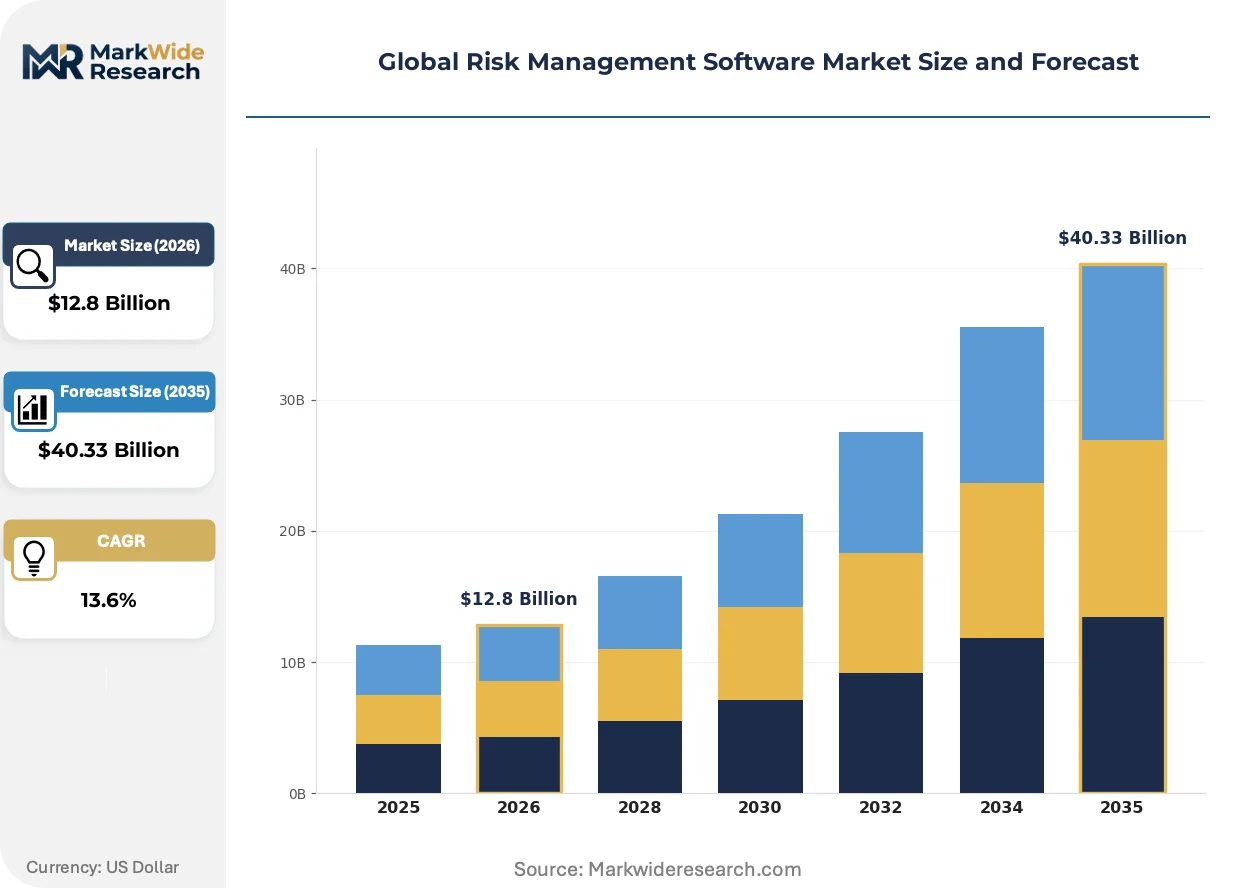
| Market Size in 2026 | $12.8 Billion |
| Market Size in 2035 | $40.33 Billion |
| CAGR (2026 – 2036) | 13.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premise, Cloud-Based, Hybrid, Private Cloud, Public Cloud Solution Type: Operational Risk, Financial Risk, Compliance Risk, Strategic Risk, Security Risk Application: Fraud Detection, Incident Management, Business Continuity, Incident Response, Vendor Risk End User Industry: Banking, Insurance, Telecommunications, Manufacturing, Energy |
| Companies Covered | IBM Corporation, Oracle Corporation, SAP SE, ServiceNow Inc., SAS Institute Inc., MetricStream Inc., NAVEX Global Inc., LogicGate Inc., Riskonnect Inc., Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Risk Management Software Market Shifts & Advancements
Generative AI is embedding into risk workflows while regulatory divergence between US prudential standards and EU mandates is fragmenting platform architectures. Procurement patterns are compressing toward continuous deployment models.
Natural language processing is automating regulatory text analysis and control mapping for compliance teams. Banking procurement departments are piloting these tools to collapse the 12-week rule interpretation cycles that currently delay system updates. The technology is automating the translation of jurisdiction-specific mandates into configurable workflow templates, compressing vendor update delivery from quarters to weeks.
The EU AI Act's risk classification framework is mandating algorithmic impact assessments for high-stakes financial decisions. Credit scoring and fraud detection systems now require documented training data provenance and human oversight interfaces. European banks are responding by embedding model risk management modules directly into their governance-risk-compliance stacks rather than treating AI governance as a separate procurement category.
Subscription-based consumption is displacing perpetual license models as regulated entities prioritize operational expenditure treatment over capital allocation. Tier-two banks and regional insurers are driving this shift, demanding usage-based pricing that aligns software costs with transaction volumes. Germany and Singapore exhibit the strongest momentum, with supervisory technology frameworks explicitly encouraging cloud-native procurement to accelerate compliance velocity.
Global Risk Management Software Market Segmentation
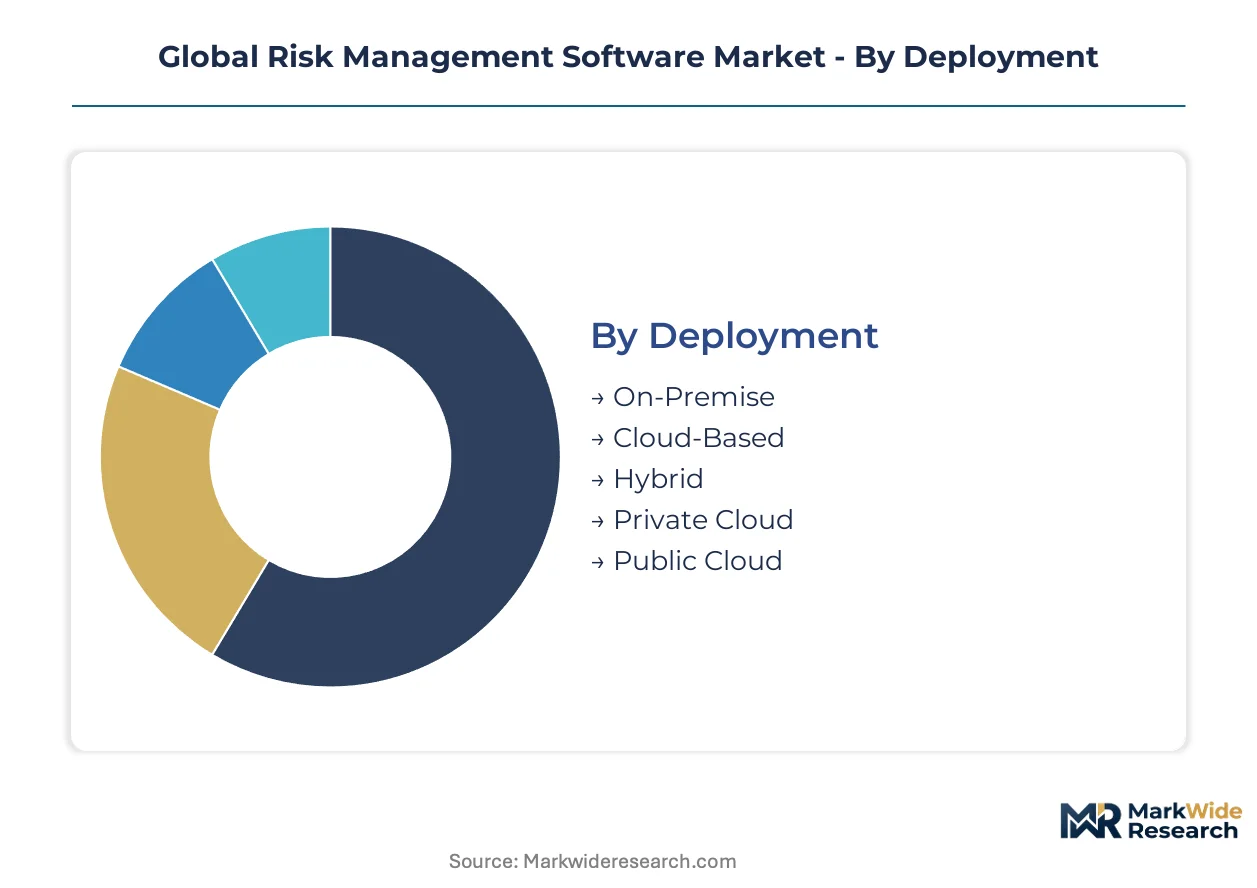
Risk management software procurement patterns diverge sharply by deployment architecture and regulatory jurisdiction. Segment-specific requirements around latency, data residency, and integration depth determine vendor selection and pricing structures across banking, insurance, and industrial end uses.
Deployment:
Capital intensity varies dramatically across deployment modes, with on-premise installations demanding substantial server infrastructure while cloud alternatives shift costs toward recurring operational expenditure.
- Cloud-Based:Multi-tenant architectures with API-first design enable sub-second transaction monitoring for tier-one banks. Demand concentrates among ASEAN financial institutions responding to Monetary Authority of Singapore supervisory technology frameworks that explicitly encourage cloud-native procurement.
- On-Premise:Dedicated hardware stacks in controlled data centers sustain air-gapped environments for classified government banking operations. German manufacturing conglomerates retain these deployments to satisfy Bundesbank operational resilience mandates requiring physical infrastructure control.
- Hybrid:Split workloads between private cloud for sensitive analytics and public cloud for burst capacity.
- Private Cloud:Single-tenant virtualized environments delivering cloud agility with dedicated resource isolation.
- Public Cloud:Shared infrastructure with consumption-based pricing attractive to mid-market insurers.
Most installed capacity flows through On-Premise legacy stacks. Expansion is steepest in Cloud-Based configurations as Basel III deadlines force architecture refreshes.
Solution Type:
Margin profiles separate recurring audit-update subscriptions from one-time implementation fees, with compliance modules commanding premium pricing due to jurisdiction-specific content maintenance burdens.
- Compliance Risk:Automated control testing engines with quarterly rule library updates for GDPR, EU AI Act, and SEC mandates. Banking procurement teams in the United States and Germany prioritize these modules for audit trail automation.
- Security Risk:Real-time breach detection with ransomware response orchestration. Demand surges among US financial institutions facing SEC cyber disclosure rules requiring material incident reporting within four business days.
- Operational Risk:Workflow engines for business process failure modeling and control documentation.
- Financial Risk:Quantitative modeling platforms for credit, market, and liquidity exposure calculation.
- Strategic Risk:Scenario planning tools for merger integration and competitive positioning analysis.
Compliance Risk modules generate the deepest recurring revenue pools. Security Risk solutions are gaining share fastest as cyber mandates tighten disclosure timelines.
Application:
Functional specialization determines integration complexity, with fraud detection requiring real-time data pipeline engineering that few implementations achieve at production scale.
- Fraud Detection:Machine learning pipelines analyzing transaction patterns across payment networks with sub-second scoring latency. Singaporean banks deploy these systems under Monetary Authority climate risk stress testing frameworks that embed fraud monitoring within broader risk orchestration.
- Incident Management:Automated escalation workflows with regulatory notification triggers. German insurers prioritize these capabilities for EU Digital Operational Resilience Act compliance deadlines.
- Business Continuity:Recovery procedure documentation with automated failover testing.
- Incident Response:Forensic data collection and containment orchestration for security breaches.
- Vendor Risk:Third-party assessment portals with continuous monitoring of supplier financial health.
Fraud Detection carries the highest technical implementation costs. Vendor Risk applications are expanding most quickly as DORA mandates force automated oversight of critical service providers.
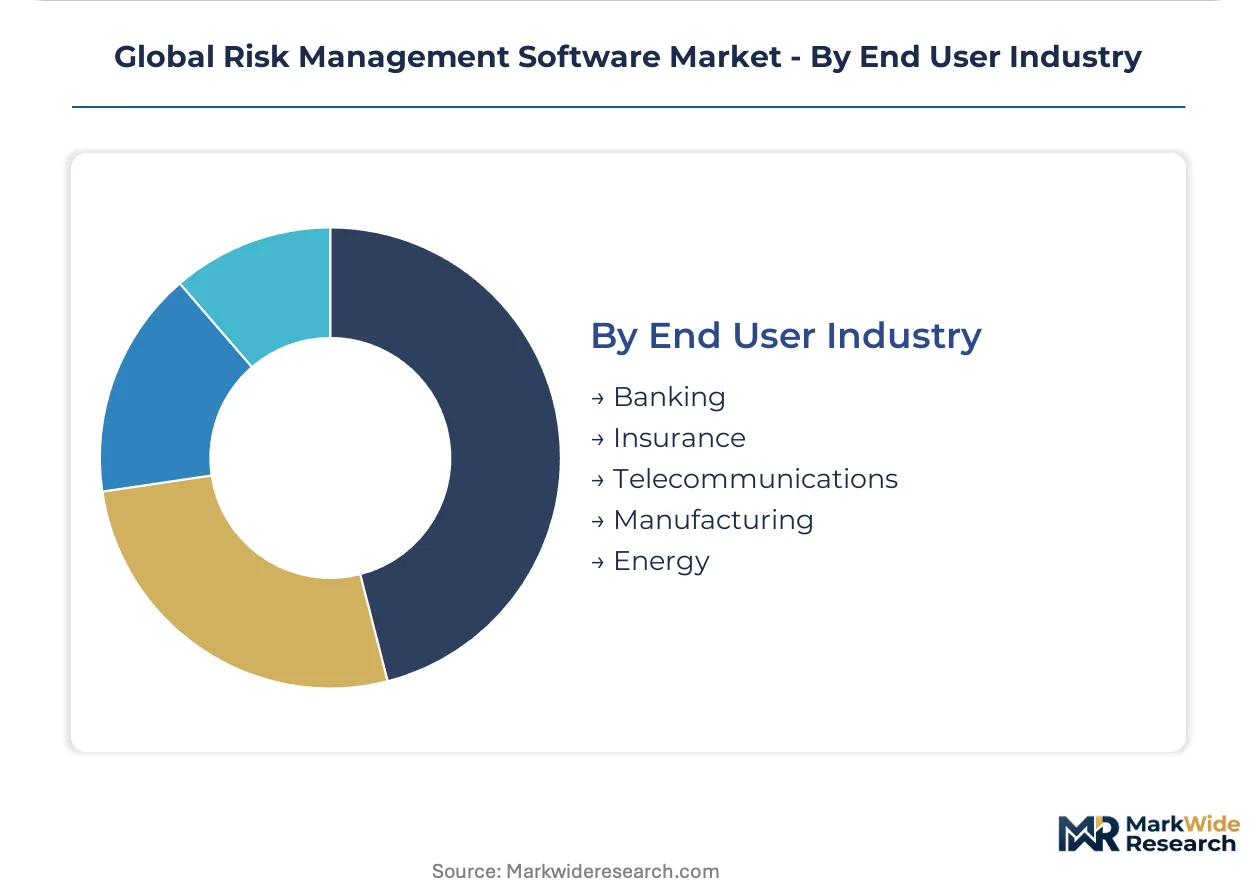
End User Industry:
Procurement sophistication separates regulated financial services from industrial adopters, with banking institutions demanding ISO 31000-certified platforms that disqualify uncredentialed vendors from RFP shortlists.
- Banking:Governance-risk-compliance stacks with Basel III operational resilience certification and API connectivity to core banking systems. US and German institutions lead procurement volume as supervisory frameworks mandate technology refreshes.
- Insurance:Actuarial integration with policy administration systems for catastrophe risk modeling. Singaporean carriers drive regional demand through Monetary Authority climate stress testing requirements.
- Manufacturing:ERP-embedded risk orchestration for supply chain continuity and quality management.
- Telecommunications:Network resilience monitoring with service-level agreement enforcement.
- Energy:Operational technology security for critical infrastructure protection.
Banking accounts for the largest installed base. Manufacturing is climbing the fastest as SAP S/4HANA integration creates native risk module demand across European industrial supply chains.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Financial services clusters in Singapore, New York, Frankfurt, and London drive procurement concentration for risk management platforms. Regulatory technology mandates across these jurisdictions compress implementation timelines. Cloud-native architectures dominate new deployments as Basel III deadlines approach.
United States
New York-based banking consortia demand sub-second transaction monitoring latency for fraud detection pipelines. SEC cyber disclosure rules mandate four-day material incident reporting windows. Chicago and San Francisco fintech clusters adopt API-first governance-risk-compliance stacks to satisfy operational resilience certification requirements.
Germany
Frankfurt's banking hub procures ISO 31000-certified platforms for EU Digital Operational Resilience Act compliance deadlines. Bundesbank operational resilience mandates require physical infrastructure control for classified operations. Munich and Stuttgart manufacturing conglomerates embed SAP-native risk orchestration modules across industrial supply chains.
Singapore
ASEAN financial institutions cluster around Monetary Authority climate risk stress testing frameworks. Supervisory technology procurement guidelines explicitly encourage cloud-native deployment architectures. Marina Bay and Raffles Place banking towers drive regional demand for scenario modeling engines with sustainability risk capabilities.
United Kingdom
London's Square Mile concentrates demand for GDPR-aligned algorithmic accountability tooling. Prudential Regulation Authority operational resilience deadlines force legacy system replacements. Edinburgh and Manchester insurance clusters procure actuarial-integrated catastrophe risk modeling platforms.
Japan
Tokyo's banking district responds to Financial Services Agency third-party vendor oversight guidelines. METI digital transformation incentives accelerate containerized microservices adoption for risk workflows. Osaka manufacturing keiretsu demand ERP-embedded operational risk modules for supply chain continuity.
Global Risk Management Software Market Competitive Landscape
Global majors compete with regional champions across certification depth and integration architecture. The vendor base stratifies into three tiers: full-stack platform providers, specialized compliance module vendors, and ERP-native risk orchestration specialists. Consolidation pressure intensifies as ISO 31000 certification backlogs disqualify uncredentialed vendors from tier-one financial institution RFP shortlists. Dominant competitive moves include strategic partnerships for regulatory content libraries and geographic expansion through supervisory technology framework alignment.
Within the full-stack platform tier, IBM Corporation and Oracle Corporation exemplify divergent architectural philosophies. IBM's Watson-anchored governance-risk-compliance workflows target multinational banks requiring statistical modeling depth. Oracle occupies a position emphasizing database-layer security controls that sustain uptime commitments under operational resilience rules. SAP SE represents the ERP-native archetype, dominating European manufacturing risk orchestration through native S/4HANA integration.
| Leading Market Players |
|---|
| IBM Corporation |
| Oracle Corporation |
| SAP SE |
| ServiceNow Inc. |
| SAS Institute Inc. |
| MetricStream Inc. |
| NAVEX Global Inc. |
| LogicGate Inc. |
| Riskonnect Inc. |
| Others |
Supply & Pricing Matrix
Private-equity-rolled-up compliance specialists have consolidated fragmented rule-library vendors across the United States and Germany, concentrating pricing power with platforms holding ISO 31000 certification and quarterly subscription renewal bases. This ownership pattern tightens supply-side discipline while forcing tier-two buyers toward modular, unbundled procurement.
Pricing Analysis
Input-cost pass-through from cloud infrastructure providers and specialized engineering talent pools is compressing margins for mid-tier vendors. Three-tier pricing structure across enterprise, professional, and standard levels dominates, with differentiation anchored in certification depth and API throughput capacity. Pricing pressure stems from containerized microservices commoditizing deployment architectures. Tier-two regional banks exhibit highest price sensitivity; tier-one multinational banks prioritize latency guarantees over cost.
Supply Chain Analysis
Single-source vulnerability sits with hyperscale cloud providers in the United States, Germany, and Singapore for compute infrastructure serving financial services deployments. The software stack draws from open-source stream-processing frameworks, proprietary regulatory content libraries, and specialized machine-learning model training pipelines. Tariff exposure on cross-border data transit threatens single-platform economics. Distribution runs through direct enterprise sales teams and systems integrator partnerships.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market functions as a regulatory compounder where EU Digital Operational Resilience Act deadlines and SEC cyber disclosure mandates create recurring procurement cycles that deepen vendor switching costs.
For Market Incumbents: To counter ISO 31000 certification bottlenecks disqualifying uncredentialed rivals, anchor governance-risk-compliance stacks with native ERP integration and automate quarterly rule-library updates. Prioritize SAP S/4HANA partnership depth in European manufacturing verticals.
For New Entrants and Emerging Players: AI governance tooling embedding model risk management into existing compliance workflows offers the most penetrable wedge. Target ASEAN financial institutions responding to Monetary Authority of Singapore climate stress testing frameworks. Lead with usage-based pricing aligning software costs to transaction volumes.
For Investors and Strategic Acquirers: Cloud infrastructure providers are the most active acquirer in this space, seeking vertical application layers to anchor consumption growth. The long-term viability window favors platforms with jurisdiction-specific content operations spanning EU, US, and Singapore regulatory clusters. Watch ISO 31000 accreditation backlogs as inflection signal for competitive access compression.
| Strategic Initiative | Industry Significance |
|---|---|
| Regulatory Content Library Expansion | Quarterly EU AI Act and SEC cyber rule updates sustain subscription renewal rates. |
| ERP-Native Integration Development | SAP S/4HANA-embedded modules capture European manufacturing risk orchestration demand. |
| Cloud Infrastructure Partnership | Hyperscaler alliances accelerate ASEAN deployment under Monetary Authority guidelines. |
| Acquisition of Specialist Compliance Vendors | Rule-library depth defends against ISO 31000 certification disqualification. |
| Geographic Expansion Through Supervisory Alignment | Monetary Authority of Singapore framework certification opens ASEAN procurement channels. |
Research Methodology
Multiple input streams — primary interviews with chief risk officers, IT procurement officers, and platform integration specialists; secondary validation against SEC filings, EU regulatory registers, and Monetary Authority of Singapore supervisory technology guidelines; plus hyperscaler capex disclosures — were reconciled through bottom-up and top-down triangulation.
Data-stream reconciliation anchored the analytical framework across deployment models, organization size tiers, vertical integration complexity, and regional adoption patterns. CAGRs were derived from segment-level growth rate reconciliation. Forecast inputs included Basel III operational resilience deadline schedules and EU AI Act implementation phase transitions.
The model holds under steady regulatory enforcement intensity; deviation in cross-border data localization rulings or ISO 31000 accreditation processing delays would shift vendor competitive positioning. Outcomes are best read as a band of plausibility, not a single trajectory.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Risk Management and Compliance
Sustainable Finance Market
Risk Management and Compliance
Stress Testing Solutions Market
Risk Management and Compliance
Travel Risk Management Services Market
Risk Management and Compliance
Asia-Pacific BFSI Biometrics Market
Risk Management and Compliance
Healthcare Safety and Risk Management Solutions Market
Risk Management and Compliance
Enterprise Risk Management Market
Risk Management and Compliance
United States Governance, Risk and Compliance Platform Market
Risk Management and Compliance
Global Patient Safety and Risk Management Softwares Market
Risk Management and Compliance
Medical Device Cyber Risk Quantification Market
Risk Management and Compliance
Loan Compliance Management Software Market
Risk Management and Compliance
Clinical Risk Grouping Solutions Market
Risk Management and Compliance
Global Asset Integrity Management Market
Risk Management and Compliance
Asia-Pacific Operational Risk Management Consulting Services in Manufacturing Market
Risk Management and Compliance
Anti-Money Laundering (AML) Market
Risk Management and Compliance
Financial Services Security Software Market
Risk Management and Compliance
Europe Sustainable Finance Market