
 Risk Assessment Software Market | 2026-2036
Risk Assessment Software Market Size, Share, and Industry Trends Forecast 2026-2036
Risk Assessment Software Market Insights
GDPR enforcement is consolidating the cost-of-entry calculus for risk assessment software vendors selling into European financial services. IBM Corporation leverages its Watson analytics platform to anchor enterprise-grade compliance automation across multiple jurisdictions. Oracle Corporation sustains database-integrated risk modeling capabilities that dominate large-scale operational risk deployments. MetricStream specializes in GRC workflow orchestration, competing primarily through channel control and industry-specific content libraries.
Risk assessment software comprises algorithmic platforms that ingest structured and unstructured data to quantify probability distributions of adverse events, typically operating through Monte Carlo simulation engines, natural language processing of regulatory texts, and real-time API feeds from external threat databases. Cloud-based deployment leads solution architecture as financial institutions abandon on-premise maintenance burdens, while cyber risk modules within the solution type dimension attract the fastest capability investment due to ransomware exposure escalation. Insurance underwriting use cases command premium pricing because carriers require proprietary scoring models that integrate actuarial datasets with dynamic external risk signals.
The SEC's cyber disclosure rules, the EU's DORA framework, and the UK Financial Conduct Authority's operational resilience requirements collectively mandate auditable risk quantification at the board-reporting level. These standards force vendors to embed regulatory change management as a core platform function rather than peripheral service. Stakeholders must monitor whether emerging AI governance mandates fragment compliance workflows or consolidate them onto unified platforms.
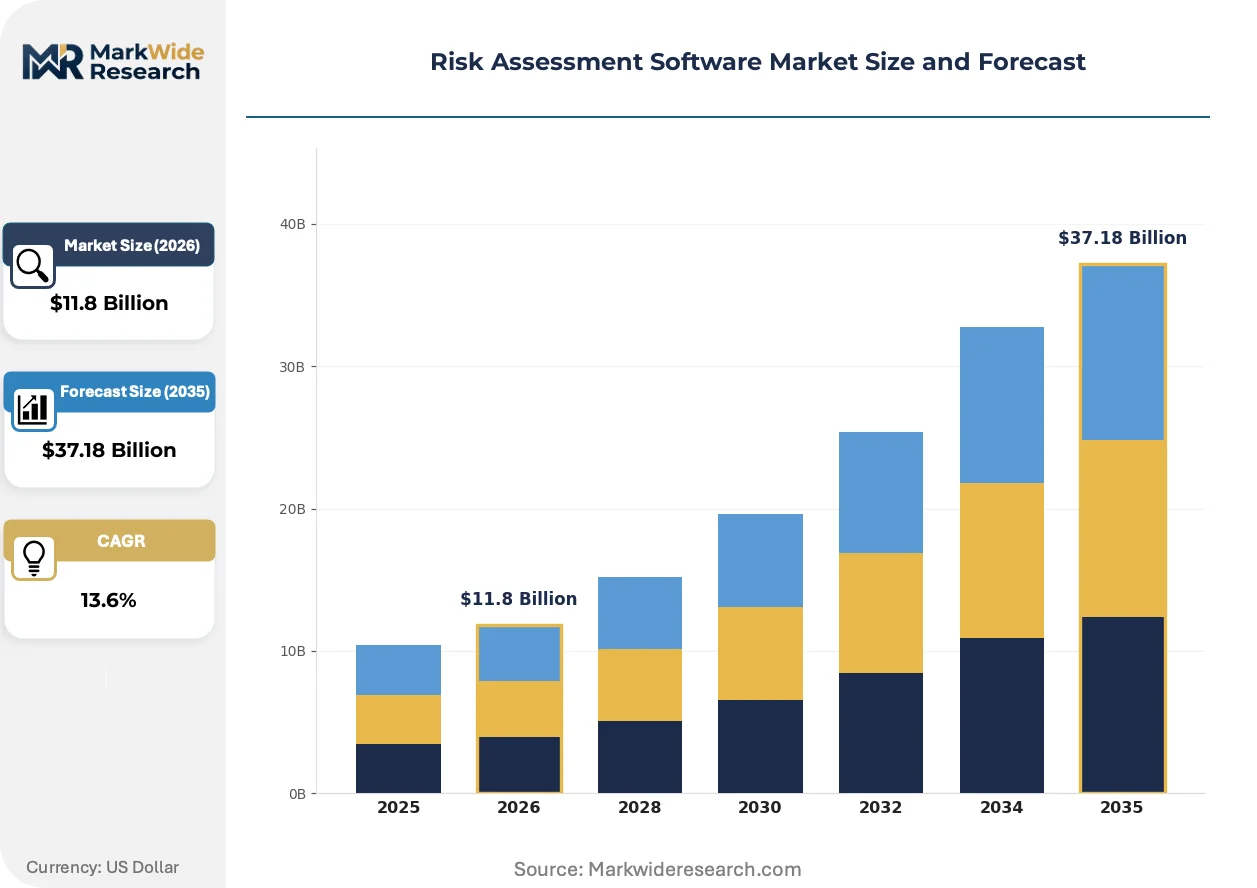
Market Dynamics
Continuous compliance mandates from the SEC, EU AI Act, and DORA framework are compressing procurement cycles for risk assessment platforms as financial institutions race to deploy auditable quantification tools before enforcement deadlines.
Growth Catalysts
- EU AI Act enforcement:Financial services firms across Germany, France, and Italy must deploy algorithmic risk scoring systems that document decision pathways, creating immediate procurement urgency for explainable AI modules.
- Ransomware frequency:Cyber insurance carriers in the United States now require continuous threat exposure monitoring as a condition of coverage, pulling real-time risk quantification platforms into standard underwriting workflows.
- Cloud migration:Operational risk teams at tier-one banks are abandoning on-premise Monte Carlo engines for API-native alternatives that ingest external threat feeds without infrastructure overhead.
Market Restraints
- Specialized talent scarcity:Firms seeking quantitative risk modelers with both actuarial training and Python engineering capabilities face 8-14 month hiring cycles in London and New York.
- Data localization requirements:China's Cybersecurity Law and Russia's data sovereignty rules fragment cloud deployment architectures, forcing vendors to maintain jurisdiction-specific infrastructure stacks.
- Model validation costs:SR 11-7 compliance for US bank holding companies requires independent validation of every quantitative model, adding 15-25% to total cost of ownership.
Strategic Opportunities
- Insurance underwriting automation:Property-catastrophe carriers seek dynamic risk scoring that integrates satellite imagery, climate projections, and real-time claims data into renewal pricing algorithms.
- CSRD reporting integration:European corporates must disclose sustainability risks in audited financial statements, opening workflow automation demand that links ESG data to traditional operational risk platforms.
- API marketplace models:Vendors can monetize proprietary risk scoring algorithms through per-call licensing to fintech lenders lacking in-house quantification capabilities.
Industry Challenges
- Multi-jurisdiction rule synchronization:Compliance teams must reconcile conflicting definitions of "material risk" across SEC cyber disclosure rules, UK FCA operational resilience requirements, and EU DORA technical standards.
- Legacy system integration:Core banking platforms running COBOL-based risk engines require expensive middleware development to connect with modern cloud-native quantification tools.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Risk Assessment Software Market |
| Market Size in 2026 | $11.8 Billion |
| Market Size in 2035 | $37.18 Billion |
| CAGR (2026 – 2036) | 13.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premise, Cloud-Based, Hybrid, Hosted, Private Cloud Solution Type: Operational Risk, Credit Risk, Market Risk, Compliance Risk, Cyber Risk Use Case: Fraud Detection, Portfolio Management, Insurance Underwriting, Vendor Risk Management, Threat Intelligence End User: Financial Services, Insurance Providers, Government Agencies, Energy Sector, Telecommunications |
| Companies Covered | IBM Corporation, Oracle Corporation, SAP SE, SAS Institute Inc., MetricStream, OneTrust, AuditBoard, Archer Technologies, Resolver, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Risk Assessment Software Market Trends and Innovations
Natural language processing engines are now parsing regulatory texts in real-time, automatically flagging rule changes that trigger model recalibration requirements for compliance officers.
Large language models are integrating with structured risk data pipelines to generate narrative explanations of quantitative outputs. US regional banks are deploying these hybrid systems to satisfy board-level requests for plain-language risk summaries. The technology is integrating probabilistic simulation results with conversational interfaces that non-technical directors can interrogate directly.
The EU's DORA framework mandates annual resilience testing with scenario severity calibrated to systemic disruption levels. Operational risk teams must now demonstrate recovery time objectives under extreme but plausible conditions. European asset managers are restructuring vendor due diligence to prioritize platforms with pre-certified DORA control libraries.
Subscription pricing for risk modules is displacing perpetual license models as chief risk officers seek to align software costs with fluctuating balance sheet exposures. Tier-two insurers in the United Kingdom are leading this shift, negotiating usage-based contracts that scale with policy count rather than fixed enterprise fees. The change compresses vendor revenue recognition cycles while reducing buyer capital commitment.
Risk Assessment Software Market Segmentation
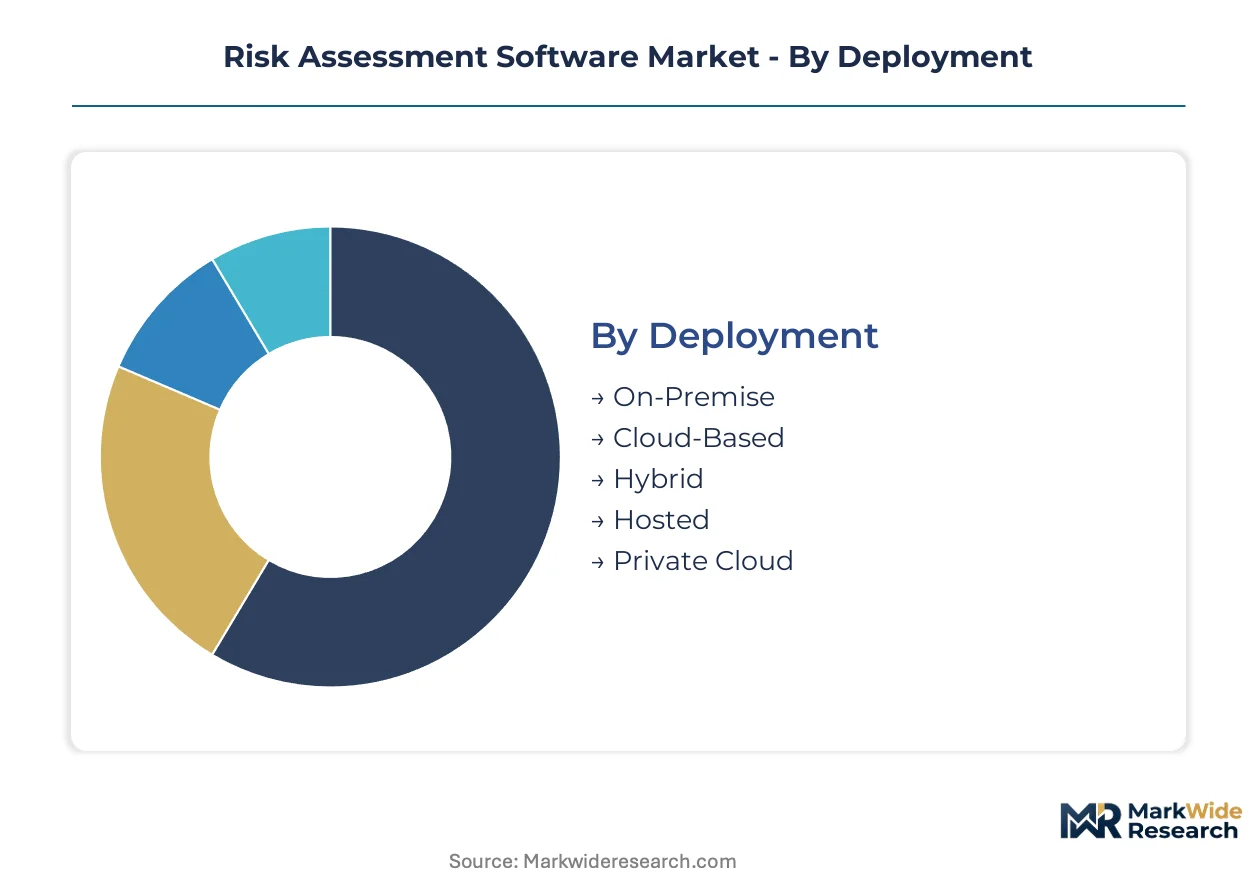
Risk assessment software procurement follows distinct technical and commercial logics across deployment architectures, risk domains, and institutional contexts. Vendors must align platform capabilities with specific buyer constraints around data sovereignty, regulatory jurisdiction, and legacy system integration.
Deployment:
Chief information security officers weigh total cost of ownership against data residency requirements when selecting infrastructure models.
- Cloud-Based:API-native architectures ingest external threat feeds without on-premise maintenance overhead. Tier-one banks in the United States and Germany are abandoning self-hosted Monte Carlo engines for these alternatives as regulatory deadlines compress implementation windows.
- On-Premise:Air-gapped installations persist where national security classifications or strict data localization mandates prohibit external data transmission. Government agencies in Russia and China maintain these deployments despite higher operational overhead.
- Hybrid:Split architectures isolate sensitive risk calculations on-premise while pushing reporting workloads to public cloud instances. European asset managers favor this model under GDPR's data minimization principles.
- Hosted:Single-tenant managed services reduce capital expenditure while preserving configuration control. Mid-tier insurers in the United Kingdom negotiate these arrangements to avoid infrastructure talent scarcity.
- Private Cloud:Dedicated infrastructure pools deliver elasticity without multi-tenant exposure. Swiss private banks deploy these configurations to satisfy FINMA operational resilience requirements.
Cloud-Based leads on scale; Private Cloud leads on momentum.
Solution Type:
Regulatory mandate intensity varies sharply across risk domains, driving divergent investment priority.
- Cyber Risk:Real-time quantification platforms integrate ransomware exposure metrics with insurance underwriting workflows. United States cyber carriers now mandate continuous threat monitoring as a coverage condition, pulling these modules into standard procurement cycles.
- Operational Risk:DORA framework compliance requires annual resilience testing with scenario severity calibrated to systemic disruption levels. European banks prioritize platforms with pre-certified control libraries for these obligations.
- Compliance Risk:NLP engines parse regulatory texts automatically, flagging rule changes that trigger model recalibration. Financial services firms deploy these tools to manage multi-jurisdiction obligation synchronization.
- Credit Risk:Proprietary scoring models integrate traditional bureau data with alternative signals for fintech lending decisions. API marketplace licensing is expanding access for non-bank originators.
- Market Risk:Monte Carlo simulation engines quantify portfolio exposure to macroeconomic shocks. Asset managers in London and New York maintain these capabilities for stress testing under SR 11-7 guidelines.
Operational Risk commands the steepest expansion trajectory; Cyber Risk captures the highest procurement urgency.
Use Case:
Workflow automation requirements differ fundamentally between real-time detection and periodic assessment contexts.
- Insurance Underwriting:Dynamic risk scoring integrates satellite imagery, climate projections, and real-time claims data into renewal pricing algorithms. Property-catastrophe carriers command premium pricing for these proprietary capabilities.
- Fraud Detection:Transaction monitoring systems apply machine learning to payment flows for anomaly identification. Retail banks in India deploy these tools under RBI's fraud risk management guidelines.
- Threat Intelligence:External data feeds enrich internal security operations with indicators of compromise. United States federal agencies mandate continuous cyber risk monitoring through these integrations.
- Portfolio Management:Risk-adjusted return analytics support asset allocation decisions for institutional investors. Pension funds in the Netherlands utilize these platforms for liability-driven investment strategies.
- Vendor Risk Management:Third-party assessment workflows automate due diligence across supply chain tiers. DORA's ICT risk management requirements are accelerating European adoption.
Insurance Underwriting generates the highest revenue per deployment; Threat Intelligence is climbing the fastest.
End User:
Industry-specific regulatory frameworks dictate functional requirements and procurement authority structures.
- Financial Services:Banks and asset managers face overlapping SEC cyber disclosure rules, EU DORA technical standards, and UK FCA operational resilience requirements. These mandates force board-level auditable risk quantification.
- Insurance Providers:Carriers require actuarial-grade models that integrate proprietary datasets with dynamic external signals. Solvency II and NAIC reporting standards shape platform specifications.
- Government Agencies:National security and civilian regulators demand air-gapped or sovereign cloud deployments. FedRAMP authorization gates access to United States federal markets.
- Energy Sector:Critical infrastructure operators align risk assessment with NERC CIP standards and emerging EU cybersecurity requirements for electricity networks.
- Telecommunications:Operators manage supply chain exposure across 5G equipment vendors under national security screening regimes. Australia's TSR and United States FCC supply chain rules drive procurement.
Financial Services dominates absolute spend; Government Agencies represent the most restrictive deployment specifications.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Quantitative risk modeling talent concentrates in the financial centers of London, New York, and Singapore, anchoring procurement authority for enterprise-grade platforms. Regulatory divergence across jurisdictions fragments deployment architectures and compliance workflows. Vendors must maintain jurisdiction-specific infrastructure stacks to satisfy data sovereignty mandates.
United States
SEC cyber disclosure rules and FedRAMP authorization requirements drive procurement urgency among regional banks and federal agencies. The Department of Treasury mandates continuous threat monitoring for critical financial infrastructure operators. New York's concentration of tier-one banks and cyber insurance carriers sustains the highest per-capita spending on real-time risk quantification platforms.
Germany
BaFin's implementation of EU DORA technical standards forces operational risk teams to demonstrate recovery time objectives under systemic disruption scenarios. The country's automotive finance and industrial insurance sectors require proprietary scoring models that integrate climate transition risks into credit portfolios. Frankfurt's asset management cluster leads European adoption of NLP-enabled regulatory change management tools.
United Kingdom
FCA operational resilience requirements mandate board-level auditable risk quantification with scenario severity calibrated to extreme but plausible conditions. Lloyd's of London syndicates command premium pricing for dynamic risk scoring that integrates satellite imagery and real-time claims data. The City's regulatory technology vendors specialize in multi-jurisdiction rule synchronization for cross-border banking groups.
Switzerland
FINMA operational resilience requirements and private banking secrecy laws sustain demand for dedicated private cloud deployments. Zurich and Geneva's wealth management clusters prioritize platforms with pre-certified control libraries for cross-border client reporting. The country's reinsurance giants require actuarial-grade models that integrate proprietary datasets with dynamic external catastrophe signals.
Singapore
Monetary Authority of Singapore's technology risk management guidelines accelerate cloud-native procurement among ASEAN-facing banks. The country's position as regional headquarters for commodity trading houses generates specialized demand for market risk modules that quantify exposure to energy transition scenarios. Marina Bay's fintech cluster drives API marketplace licensing for alternative credit scoring algorithms.
Risk Assessment Software Market Competitive Landscape
Diversified conglomerates compete with focused pure-play specialists across a tiered vendor landscape. Enterprise technology holding companies leverage database integration and existing client relationships to anchor large-scale operational risk deployments. Pure-play governance, risk, and compliance vendors compete through channel control and industry-specific content libraries. Dominant competitive moves include strategic partnerships with cyber insurance carriers and vertical integration into regulatory change management capabilities.
Within the diversified technology tier, IBM Corporation and Oracle Corporation occupy positions anchored by enterprise infrastructure relationships and database-integrated modeling capabilities. MetricStream exemplifies the pure-play specialist archetype, competing through GRC workflow orchestration and pre-certified control libraries. These three companies represent the strategic positioning spectrum: infrastructure-anchored conglomerates versus content-driven specialists.
| Leading Market Players |
|---|
| IBM Corporation |
| Oracle Corporation |
| SAP SE |
| SAS Institute Inc. |
| MetricStream |
| OneTrust |
| AuditBoard |
| Archer Technologies |
| Resolver |
| Others |
Pricing and Supply Chain Analysis
Enterprise-grade certification tiers split the market between FedRAMP-authorized deployments and standard SaaS offerings, with the former commanding three-to-fivefold premiums and requiring captive infrastructure in sovereign data centers. This bifurcation concentrates supply chain investment among hyperscale cloud providers with cleared personnel facilities, while tier-two vendors compete on API velocity and usage-based economics.
Pricing Analysis
Subscription tiers separate perpetual-license incumbents from consumption-native challengers. FedRAMP authorization and DORA pre-certification drive premium pricing for government and EU financial services buyers. Cost compression in mid-market SaaS tiers intensifies as venture-backed entrants undercut established vendors on per-seat rates. Cyber insurance carriers show least price sensitivity due to coverage mandate urgency, while regional banks in secondary US markets negotiate aggressively on total cost of ownership.
Supply Chain Analysis
Dual-sourcing requirements from US federal agencies and EU critical infrastructure operators mandate redundant cloud infrastructure qualification across AWS, Azure, and Google Cloud. Compute capacity concentrates in the United States, Germany, and Singapore. Proprietary risk scoring algorithms hinge on licensed threat intelligence feeds from Mandiant and Recorded Future. Tariff exposure on semiconductor components for on-premise appliances threatens margin stability at hardware-anchored vendors. Distribution runs through systems integrators and cyber insurance broker channels.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Quality specifications tighten as DORA and SEC cyber disclosure rules mandate auditable quantification at board-reporting level, favoring vendors with pre-certified control libraries over configurable toolkits.
For Market Incumbents: Anticipate margin compression from API-native challengers by hardening vertical integration into regulatory change management content and exclusive carrier partnerships. Prioritize DORA and FedRAMP certification maintenance as defensive moats against mid-market SaaS erosion. For New Entrants and Emerging Players: Begin with CSRD reporting integration workflows for European mid-cap corporates lacking ESG-to-operational-risk linkages. Target usage-based pricing for tier-two UK insurers as the most penetrable segment. Pursue cyber insurance broker channel partnerships for rapid credibility transfer. For Investors and Strategic Acquirers: Consolidation pressure builds where fragmented GRC point solutions lack the capital to achieve multi-jurisdiction certification coverage. Five-to-ten year viability favors platforms with embedded NLP regulatory parsing and pre-certified DORA control libraries. Watch for carrier mandating continuous monitoring as standard coverage condition as the inflection signal.| Strategic Initiative | Industry Significance |
|---|---|
| Regulatory Certification Acceleration | FedRAMP and DORA pre-certification gates access to highest-spending buyer segments. |
| Cyber Insurance Carrier Partnership | Mandated monitoring requirements pull platforms into standard underwriting workflows. |
| NLP Regulatory Engine Development | Real-time parsing of SEC, EU AI Act, and DORA texts automates compliance recalibration. |
| API Marketplace Licensing | Per-call monetization extends reach to fintech lenders lacking in-house quantification. |
| Private Cloud Infrastructure Expansion | Swiss and German data residency mandates require dedicated sovereign deployments. |
Research Methodology
Multiple input streams — chief risk officer interviews, regulatory filing analysis, and vendor procurement documentation — were reconciled to construct segment-level demand estimates. Primary fieldwork engaged CROs at tier-one banks, GRC platform engineers, cyber insurance underwriters, and compliance technology procurement officers. Secondary validation drew from SEC 10-K cyber risk disclosures, EU DORA implementation guidance, FedRAMP authorized product listings, and carrier underwriting requirement bulletins. Bottom-up deployment counts and top-down enterprise software spend estimates were triangulated to anchor value projections.
Data-stream reconciliation across deployment architecture, risk domain, and end-user industry dimensions structured the analytical framework. Segmentation modeled cloud versus on-premise uptake, cyber versus operational risk module priority, and financial services versus insurance provider spending patterns. CAGRs were derived from elasticity-adjusted adoption curves and regulatory deadline acceleration effects. Forecast inputs incorporated DORA enforcement timeline uncertainty and cyber insurance coverage mandate diffusion rates.
Caveats apply where AI governance mandate fragmentation or legacy system integration cost overruns could materially shift the outlook. Deviation in SEC enforcement intensity or EU DORA technical standard finalization would shift the outlook materially.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Risk Management and Compliance
Revenue Assurance Market
Risk Management and Compliance
Travel Risk Management Services Market
Risk Management and Compliance
United States Governance, Risk and Compliance Platform Market
Risk Management and Compliance
Healthcare Safety and Risk Management Solutions Market
Risk Management and Compliance
Global Asset Integrity Management Market
Risk Management and Compliance
Risk Analytics Market
Risk Management and Compliance
Enterprise Governance, Risk, and Compliance (Egrc) Market
Risk Management and Compliance
Artificial Intelligence and Regtech Market
Risk Management and Compliance
Global Strategy Consulting Market
Risk Management and Compliance
China Enterprise Risk Management Market
Risk Management and Compliance
Europe Strategy Consulting Market
Risk Management and Compliance
Asset Liability Management (ALM) Solution Market
Risk Management and Compliance
Stress Testing Services Market
Risk Management and Compliance
Risk-Based Monitoring Software Market
Risk Management and Compliance
Europe Governance, Risk and Compliance Platform Market
Risk Management and Compliance
Treasury and Risk Management Application Market