
 Global Wireless Intrusion Prevention System Market | 2026-2036
Global Wireless Intrusion Prevention System Market Size, Share, and Industry Trends Forecast 2026-2036
Global Wireless Intrusion Prevention System Market Foresight
Market Context
Israel is tilting toward cybersecurity export capacity with dedicated WIPS R&D clusters near Tel Aviv. Cisco Systems leverages deep enterprise routing integration to bundle wireless threat detection across campus networks. Fortinet sustains competitive pressure through converged firewall-WIPS appliances that reduce appliance sprawl. Palo Alto Networks anchors cloud-native WIPS delivery through its Prisma platform, competing directly with hardware-centric rivals.
Technical Definition and Segment Structure
A Wireless Intrusion Prevention System constitutes an active security platform that monitors radio frequency spectrum for unauthorized access points, rogue devices, and protocol-level attacks, then automatically terminates malicious sessions through countermeasure injection or access point containment. The system operates primarily to enforce continuous wireless perimeter integrity across enterprise, government, and defense environments where unmanaged Wi-Fi introduces lateral movement risk. Cloud-Based deployment captures the fastest expansion trajectory as distributed workforces abandon fixed perimeter architectures, while On-Premises solutions retain dominance in defense and classified settings where data sovereignty overrides operational flexibility. Signature-Based detection occupies the mature revenue pool with predictable refresh cycles, though Behavioral analytics represents the margin-accretive frontier where machine learning differentiation commands pricing premiums.
Regulatory Framework and Outlook
FCC spectrum enforcement in the United States shapes WIPS functionality by defining permissible interference thresholds for automated countermeasures, while the EU AI Act imposes algorithmic transparency requirements on behavioral detection engines deployed across European member states. NIST SP 800-48 revision pressure in federal procurement channels elevates product certification costs but simultaneously filters marginal vendors from government supply chains. Stakeholders must monitor how quantum-resistant encryption standards rewrite wireless protocol vulnerability profiles before current detection heuristics expire.
Market Dynamics
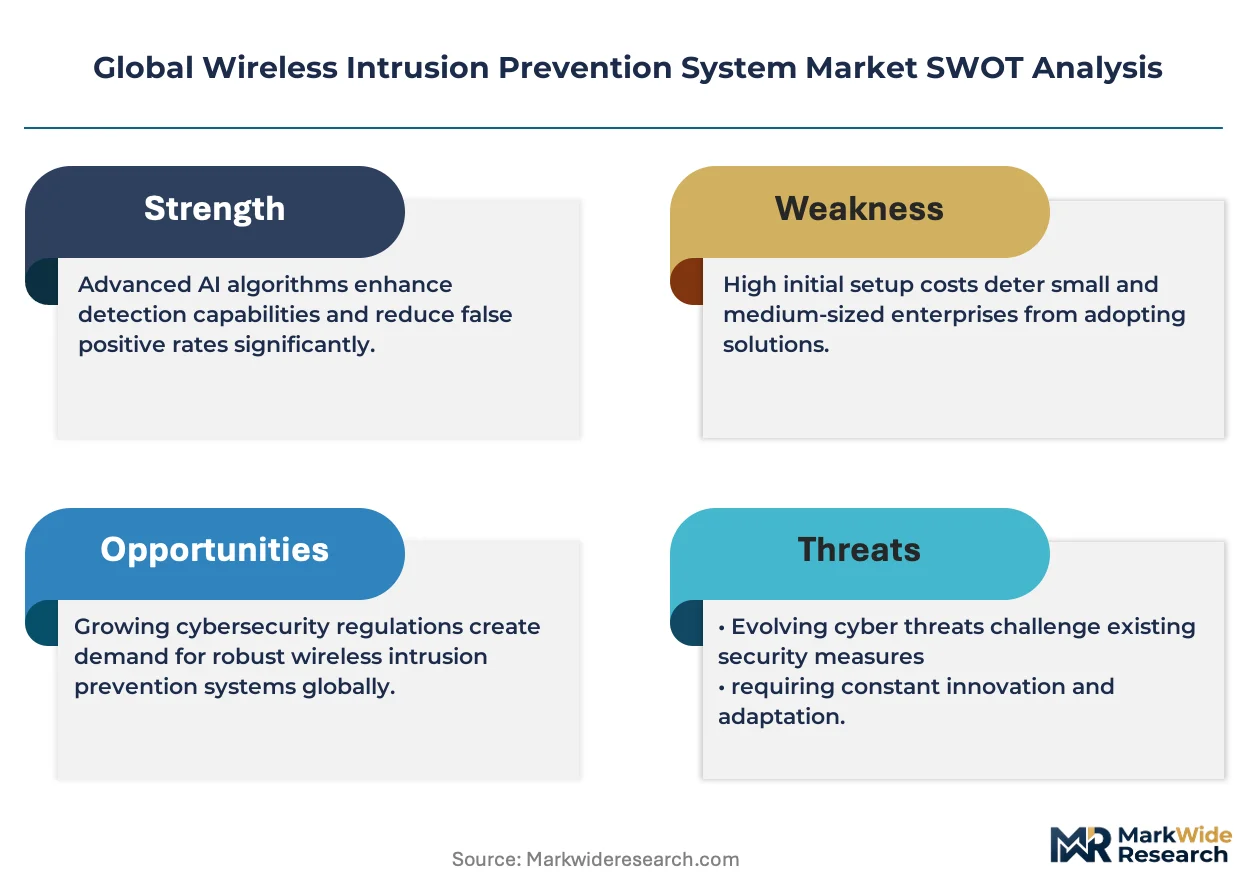
Enterprise security teams are abandoning perimeter-centric architectures as distributed workforces and IoT proliferation fragment network boundaries, forcing WIPS vendors to embed detection engines directly into cloud-native security fabrics rather than standalone appliances.
Growth Catalysts
- EU NIS2 Directive:Critical infrastructure operators across European member states face mandatory wireless perimeter monitoring obligations, triggering replacement cycles for legacy passive scanning tools.
- Healthcare network expansion:Hospital systems deploying wireless medical devices require continuous RF spectrum monitoring to prevent patient data interception through rogue access points.
- Behavioral analytics engines:Machine learning-powered anomaly detection is displacing signature-based methods in financial services campuses, enabling real-time threat neutralization without human intervention.
Market Restraints
- FCC interference thresholds:Automated countermeasure injection faces strict power-limitation rules in the United States, constraining containment effectiveness in high-density urban RF environments.
- Semiconductor supply concentration:Specialized RF silicon fabrication concentrates in East Asian foundries, exposing WIPS hardware vendors to geopolitical disruption in component sourcing.
- Legacy Wi-Fi protocol persistence:Enterprise reluctance to deprecate 802.11n infrastructure forces WIPS platforms to maintain backward-compatible detection heuristics, bloating sensor firmware and slowing update cycles.
Strategic Opportunities
- India's smart manufacturing corridors:The country's PLI scheme for electronics production is drawing industrial automation investments that require hardened wireless perimeters around automated guided vehicles and robotic assembly lines.
- Converged SASE-WIPS bundles:Secure Access Service Edge platforms are absorbing wireless threat detection as a native module, creating white space for cloud-native vendors without hardware legacy.
- Defense classified networks:NATO member states are mandating TEMPEST-grade RF monitoring for sensitive facilities, opening premium procurement channels for accredited on-premises solutions.
Industry Challenges
- RF engineering talent scarcity:The specialized skill set combining wireless protocol analysis with adversarial machine learning remains concentrated among defense contractors, constraining vendor R&D scaling.
- Multi-vendor integration complexity:Enterprise buyers demand seamless orchestration between WIPS sensors and existing SIEM/SOAR stacks, forcing vendors to absorb costly professional services overhead.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Wireless Intrusion Prevention System Market |
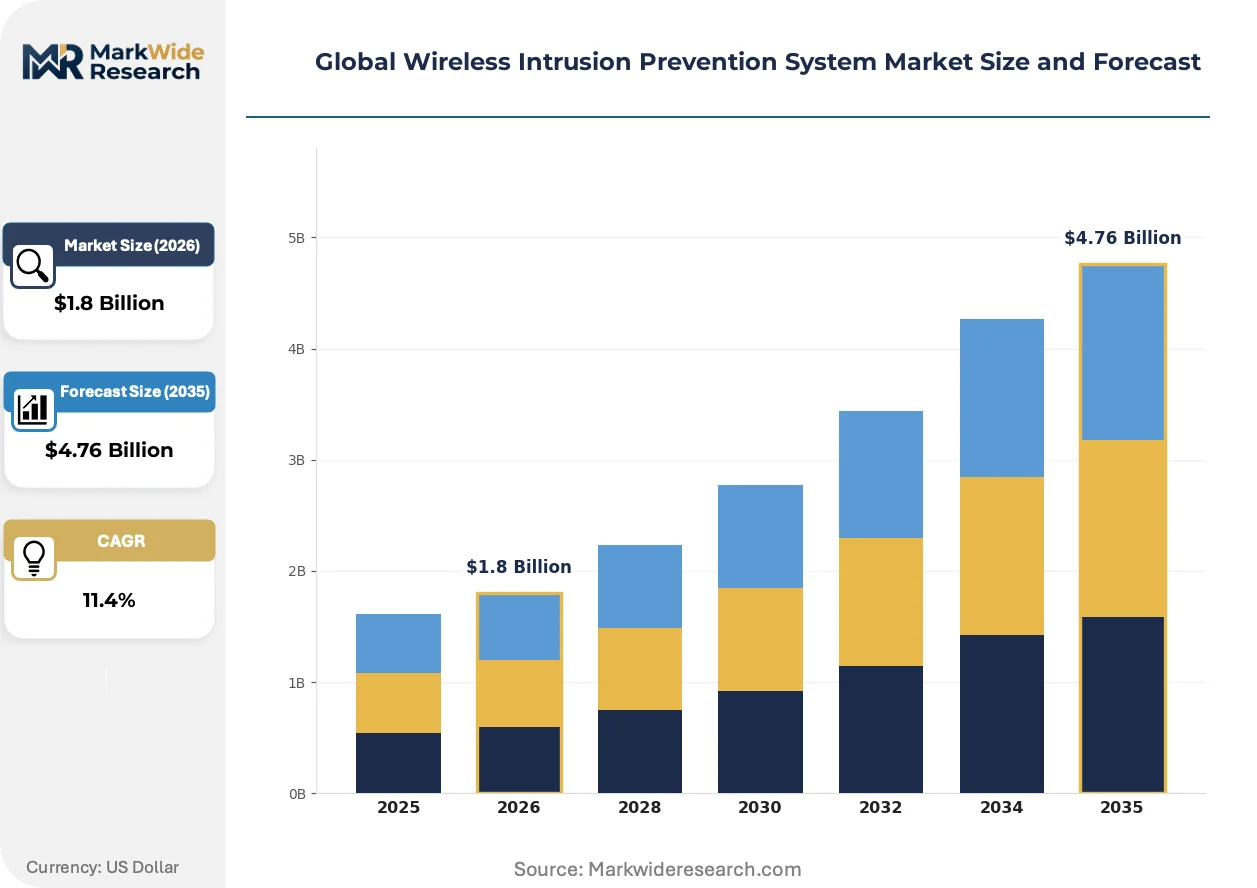
| Market Size in 2026 | $1.8 Billion |
| Market Size in 2035 | $4.76 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: Cloud-Based, On-Premises, Hybrid, Virtualized Solution: Signature-Based, Anomaly-Based, Behavioral, Hybrid Detection Use Case: Enterprise Security, Government Security, Military Defense, Financial Services, Educational Institutions Customer Type: Small & Medium Enterprises, Large Enterprises, Managed Security Service Providers, System Integrators |
| Companies Covered | WatchGuard Technologies, Trend Micro, Cisco Systems, Trellix, Fortinet, Check Point Software, Aruba, NetScout, Palo Alto Networks, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Wireless Intrusion Prevention System Market Shifts & Advancements
Wireless security architectures are undergoing fundamental reconstruction as cloud delivery models displace hardware-centric deployment, while regulatory mandates force algorithmic transparency and quantum-resistant encryption reshape detection methodologies.
Edge-native WIPS sensors are collapsing the distinction between detection and response latency. These compact devices perform localized threat analysis without backhauling raw RF captures to central servers. Manufacturing facilities in Germany's industrial corridor are deploying them at machine-line density, compressing incident response from minutes to milliseconds. The architecture eliminates bandwidth bottlenecks that previously constrained large campus deployments.
The EU AI Act imposes explainability requirements on behavioral detection engines deployed across European member states. Vendors must now document decision pathways for automated access point containment actions, adding compliance engineering overhead but simultaneously filtering opaque black-box systems from government procurement channels. Financial institutions in Frankfurt and Paris are prioritizing certified transparent algorithms over raw detection accuracy metrics.
Hospital procurement committees are unbundling wireless security from broader network infrastructure contracts, creating standalone WIPS evaluation workflows. This pattern concentrates in the United States where HIPAA breach penalties have elevated RF monitoring to board-level visibility. Medical device manufacturers now face direct liability for wireless vulnerabilities, pushing them toward pre-integrated detection modules rather than aftermarket sensor overlays.
Global Wireless Intrusion Prevention System Market Segmentation
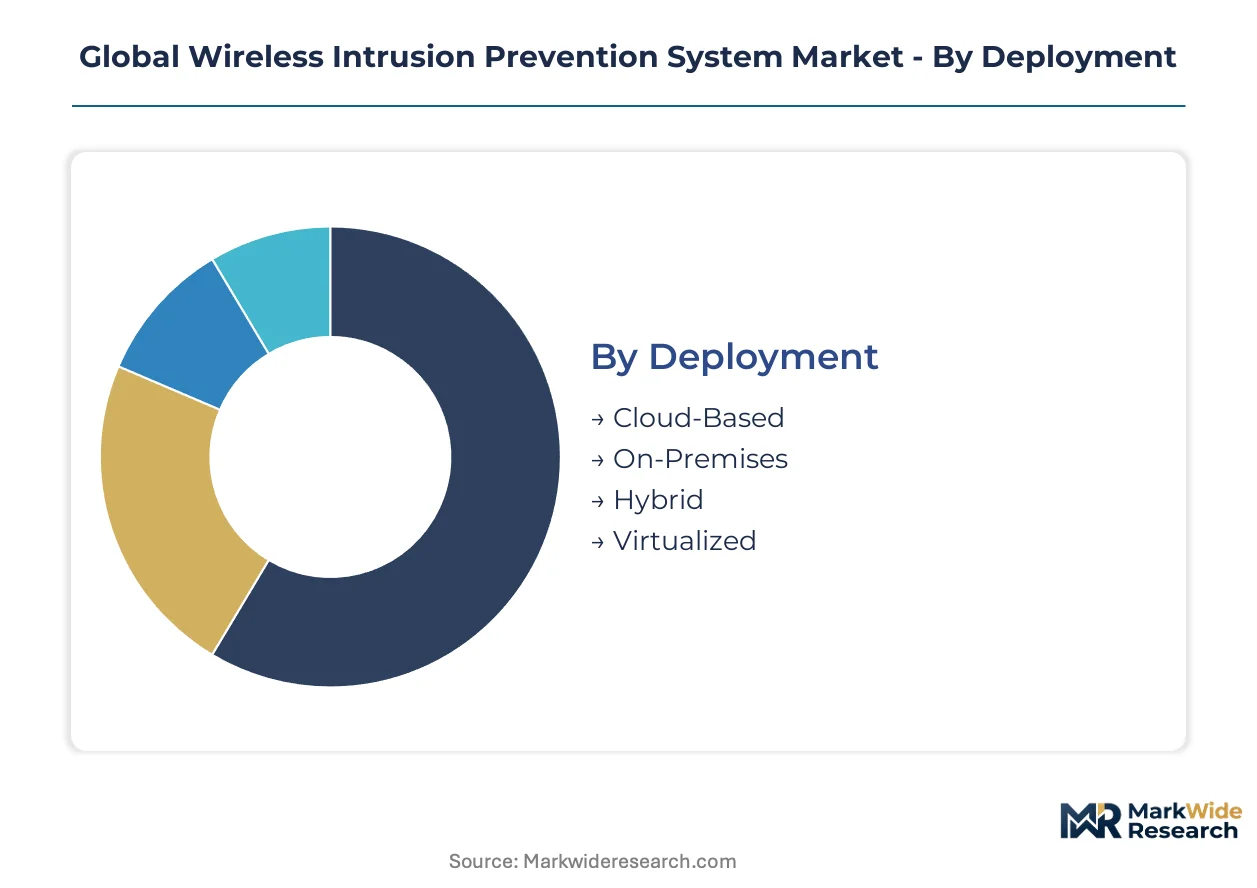
WIPS procurement patterns diverge sharply across deployment architectures, detection methodologies, and institutional risk profiles. Understanding these fault lines reveals where vendors must concentrate engineering resources versus where standardization prevails.
Deployment:
Cloud-native delivery dominates distributed workforce scenarios where fixed perimeter assumptions have collapsed, while hardened facilities retain physical appliance requirements.
- Cloud-Based:Multi-tenant architectures enable centralized threat intelligence correlation across fragmented branch locations. Healthcare networks in the United States and Germany's industrial corridor are migrating here to eliminate sensor maintenance overhead at remote clinics and factory floors.
- On-Premises:Air-gapped installations process RF captures locally without external data transmission. Defense agencies across NATO member states mandate this architecture for classified facilities under TEMPEST and data sovereignty requirements.
- Hybrid:Split processing keeps sensitive detection logic on-site while leveraging cloud analytics for threat signature updates. Financial services campuses in Frankfurt and Singapore deploy this to balance regulatory compartmentalization with operational agility.
- Virtualized:Software-defined sensors run on commodity compute infrastructure, reducing hardware refresh cycles. Educational institutions with constrained capital budgets favor this approach for campus-wide coverage.
The dominant share belongs to Cloud-Based deployments, while Hybrid configurations are closing the gap fastest as regulated industries seek compromise architectures.
Solution:
Detection engine selection hinges on threat actor sophistication and acceptable false-positive rates, with machine learning differentiation commanding pricing premiums.
- Signature-Based:Pattern-matching against known attack definitions delivers predictable performance with minimal computational overhead. Legacy enterprise campuses retain this for baseline coverage of common rogue access point signatures.
- Anomaly-Based:Statistical deviation analysis flags protocol behaviors outside established baselines. Manufacturing facilities deploying automated guided vehicles rely on this to detect RF interference from unauthorized devices without predefined threat libraries.
- Behavioral:Machine learning models correlate user, device, and network behaviors to identify compromised credentials or insider threats. EU AI Act transparency requirements are filtering opaque implementations from government procurement channels.
- Hybrid Detection:Layered engines combine signature speed with behavioral depth, routing alerts through appropriate analysis tiers. Managed security service providers standardize on this to serve heterogeneous client portfolios.
Signature-Based solutions retain the largest installed base, though Behavioral analytics is expanding most quickly as financial services and healthcare prioritize zero-day coverage.
Use Case:
Institutional risk tolerance and regulatory exposure shape detection sensitivity requirements, with critical infrastructure operators facing the strictest monitoring mandates.
- Enterprise Security:Campus-wide coverage protects against lateral movement through unmanaged Wi-Fi. Corporate headquarters in Tel Aviv's cybersecurity cluster deploy edge-native sensors to compress response latency.
- Government Security:Federal facilities require continuous RF spectrum monitoring under NIST SP 800-48 and equivalent frameworks. Compliance certification filters uncredentialed vendors from procurement channels.
- Military Defense:TEMPEST-grade countermeasures prevent electromagnetic emanation exploitation. NATO classified networks mandate accredited on-premises solutions with documented supply chain provenance.
- Financial Services:Real-time transaction protection drives investment in behavioral analytics. Frankfurt and Paris institutions prioritize algorithmic explainability under EU AI Act constraints.
- Educational Institutions:Open campus architectures complicate device inventory and trust boundaries. Universities balance coverage breadth against constrained security staffing.
Enterprise Security commands the greatest absolute spending, yet Military Defense exhibits the steepest expansion trajectory as geopolitical tensions elevate RF monitoring budgets.
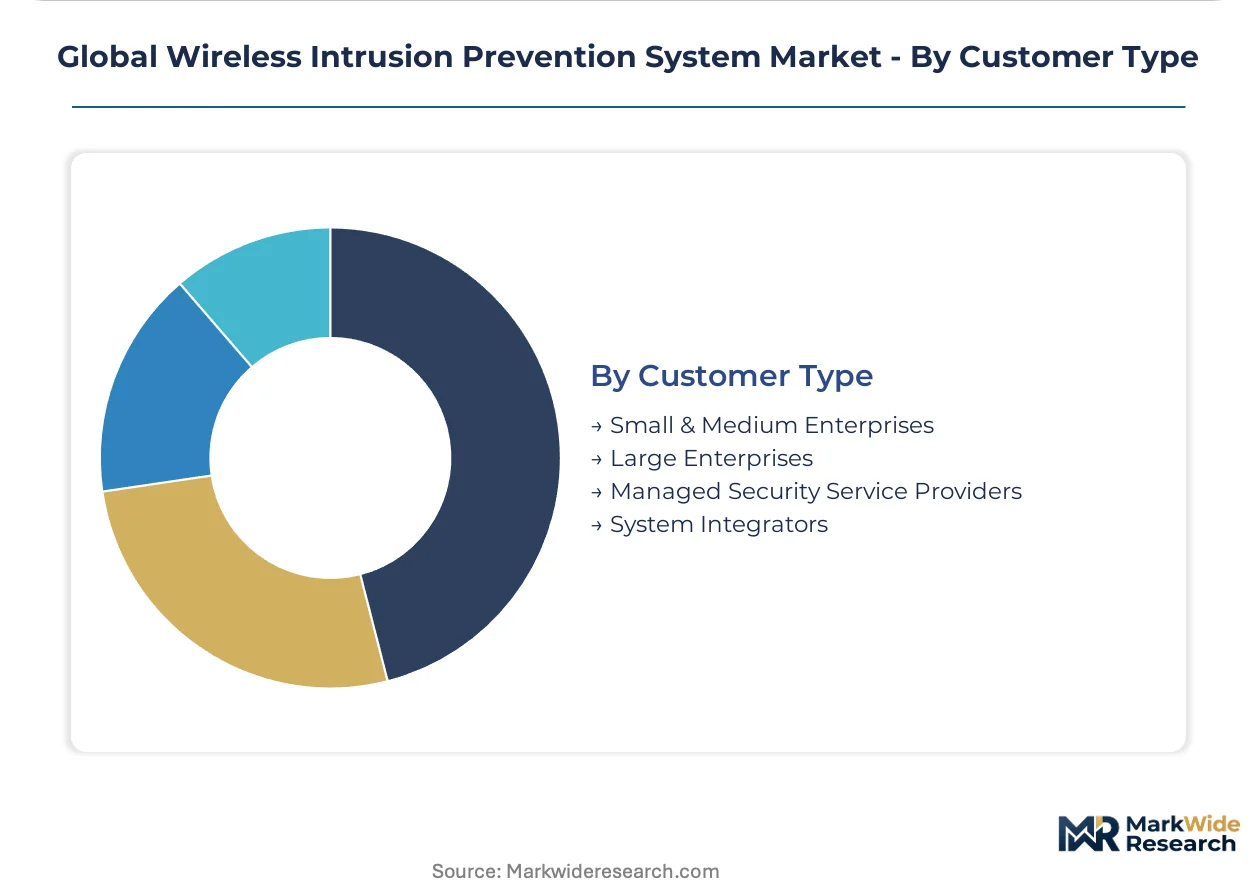
Customer Type:
Procurement sophistication and integration complexity vary dramatically across organizational scale and security outsourcing maturity.
- Small & Medium Enterprises:Cloud-delivered WIPS eliminates capital expenditure and specialized staffing requirements. Virtualized deployment options align with limited IT infrastructure.
- Large Enterprises:Dedicated security teams demand API-rich platforms for SIEM/SOAR orchestration. Multi-vendor integration complexity drives professional services absorption.
- Managed Security Service Providers:Multi-tenant architectures enable economies of scale across client portfolios. Hybrid detection standardization reduces operational variance.
- System Integrators:Project-based deployment of customized sensor networks for specialized facilities. RF engineering talent scarcity constrains scaling capacity.
Large Enterprises currently represent the deepest revenue pool, though Managed Security Service Providers are gaining share fastest as mid-market outsourcing accelerates.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
FCC spectrum enforcement in the United States anchors the dominant geography, defining permissible interference thresholds for automated countermeasures while EU AI Act transparency requirements reshape behavioral detection deployment across European member states.
United States
Hospital systems and financial campuses drive demand for continuous RF spectrum monitoring. FCC power-limitation rules constrain containment effectiveness in high-density urban environments. Enterprise security teams in New York and Chicago metro areas prioritize cloud-native delivery to eliminate sensor maintenance overhead at distributed branch locations.
Germany
Manufacturing facilities deploying automated guided vehicles require hardened wireless perimeters around robotic assembly lines. EU NIS2 Directive mandates critical infrastructure operators to replace legacy passive scanning tools. Industrial automation investments concentrate in Baden-Württemberg and North Rhine-Westphalia where edge-native sensors compress incident response latency.
India
Smart manufacturing corridors under the PLI scheme for electronics production draw industrial automation investments requiring wireless threat detection. TRAI spectrum management frameworks influence deployment architectures. Karnataka and Tamil Nadu host expanding cybersecurity R&D clusters serving domestic and export markets.
Israel
Cybersecurity export capacity tilts toward dedicated WIPS R&D clusters near Tel Aviv. Defense agencies mandate TEMPEST-grade RF monitoring for sensitive facilities. The country's national security regulator shapes procurement standards that filter into commercial product roadmaps.
United Kingdom
Financial services campuses in London deploy behavioral analytics under emerging algorithmic transparency requirements. NIST SP 800-48 revision pressure elevates product certification costs for federal procurement channels. Managed security service providers standardize on hybrid detection to serve heterogeneous client portfolios across the Southeast and Midlands.
Global Wireless Intrusion Prevention System Market Competitive Landscape
Capability concentration sits with specialized RF engineering vendors; scale advantage sits with converged security platform providers. The vendor base organizes around three strategic archetypes: networking incumbents bundling wireless threat detection into broader infrastructure portfolios, pure-play cybersecurity specialists with deep protocol analysis expertise, and cloud-native platforms absorbing WIPS as a native SASE module. Dominant competitive moves include strategic partnerships for multi-vendor SIEM/SOAR orchestration and geographic expansion into India's smart manufacturing corridors.
Within the networking incumbent tier, Cisco Systems and Aruba exemplify platform bundling strategies that leverage deep enterprise routing integration. Fortinet occupies a position bridging hardware-centric and cloud-native delivery through converged firewall-WIPS appliances. Palo Alto Networks anchors cloud-native WIPS delivery, competing directly with appliance-dependent rivals through its Prisma platform architecture.
| Leading Market Players |
|---|
| WatchGuard Technologies |
| Trend Micro |
| Cisco Systems |
| Trellix |
| Fortinet |
| Check Point Software |
| Aruba |
| NetScout |
| Palo Alto Networks |
| Others |
Supply & Pricing Matrix
Taipei's specialized RF silicon foundries anchor component availability for WIPS hardware vendors, translating concentrated upstream capacity into asymmetric pricing power for cloud-native platform providers over appliance-dependent rivals. Defense procurement channels absorb premium markups for TEMPEST-certified on-premises solutions, while mid-market enterprises pressure SaaS pricing through consolidated MSSP purchasing.
Pricing Analysis
Price spreads between North American and Asia-Pacific deployments compress as cloud delivery models standardize across geographies. Three-tier pricing structure across premium, standard, and economy levels segments buyers by detection engine sophistication, with behavioral analytics commanding certification premiums under EU AI Act transparency mandates. Cost compression in the virtualized tier intensifies because educational institutions and SMEs aggregate demand through MSSP channels. Large enterprises with dedicated security teams exhibit lowest price sensitivity, prioritizing API richness and SIEM integration over per-seat costs.
Supply Chain Analysis
Specialized RF silicon feeds from Taiwan, South Korea, and Japan, with advanced node fabrication concentrating in Hsinchu Science Park and Pyeongtaek semiconductor clusters. GaN power amplifiers, FPGA signal processors, and precision RF filters constitute critical input dependencies. Single-source vulnerability in East Asian foundry capacity exposes hardware vendors to geopolitical disruption in component sourcing. Distribution runs through direct enterprise sales for large deployments, while channel partners and MSSPs dominate mid-market access.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Buyer power is concentrating through MSSP consolidation and enterprise security team centralization, shifting procurement leverage toward vendors with multi-tenant cloud architectures and API-native integration capabilities.
For Market Incumbents: Harden cloud-native delivery platforms against emerging pure-play behavioral analytics specialists by embedding quantum-resistant encryption modules ahead of protocol vulnerability expiration. Prioritize backward integration into edge-native sensor firmware development to reduce dependency on RF engineering talent concentrated among defense contractors. Defensive consolidation through certification investment for EU AI Act algorithmic transparency mandates filters opaque black-box systems from government procurement channels. For New Entrants and Emerging Players: Establish a beachhead in India's smart manufacturing corridors where PLI scheme investments in electronics production create demand for hardened wireless perimeters around automated guided vehicles. Target virtualized deployment adoption among educational institutions with constrained capital budgets, offering software-defined sensors on commodity compute infrastructure. Go-to-market leverage through system integrator partnerships bypasses direct competition with Cisco and Fortinet in enterprise routing-integrated channels. For Investors and Strategic Acquirers: Mid-cycle technology positioning favors cloud-native platforms with SASE integration capabilities over hardware-centric appliance vendors facing semiconductor supply concentration risks. Long-term viability rests on behavioral analytics differentiation and quantum-resistant protocol adaptation. Acquisition target archetype: specialized RF engineering firms with adversarial machine learning expertise concentrated near Tel Aviv or Tel Aviv-adjacent defense contractor spinouts. Signal to watch: FCC relaxation of automated countermeasure power thresholds in high-density urban RF environments.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Converged SASE-WIPS bundles absorb wireless threat detection as native modules, displacing standalone appliances. |
| Strategic Partnership | Multi-vendor SIEM/SOAR orchestration agreements reduce professional services overhead for enterprise buyers. |
| Acquisition of Specialist Firm | RF engineering talent scarcity drives consolidation of adversarial machine learning expertise from defense contractors. |
| Geographic Expansion | India's PLI scheme for electronics production draws industrial automation investments requiring wireless perimeter hardening. |
| Product Launch | Edge-native sensors with localized threat analysis compress incident response latency for Germany's industrial corridor. |
Research Methodology
The analysis maps cloud-native, on-premises, hybrid, and virtualized deployment architectures, each validated through chief information security officers, MSSP operations directors, RF engineering leads, and healthcare network procurement managers. Primary interviews with these stakeholders combined secondary validation through FCC spectrum enforcement filings, EU NIS2 Directive implementation guidance, NIST SP 800-48 revision documentation, and semiconductor trade flow data. Bottom-up sensor deployment estimates and top-down security spending allocations triangulate market sizing.
Assumptions held fixed include regulatory enforcement timelines for EU AI Act transparency requirements and FCC interference threshold interpretations, while variables included cloud migration velocity across healthcare networks and defense budget allocation shifts for TEMPEST-grade RF monitoring. Segmentation dimensions modeled span deployment architecture, detection methodology, use case risk profile, and customer type procurement sophistication. CAGRs derive from installed base refresh cycles and net new deployment trajectories across the projection horizon. Forecast inputs incorporate HIPAA breach penalty escalation patterns and NATO member state classified network modernization commitments.
Sensitivities concentrate around quantum-resistant encryption standardization timelines and East Asian semiconductor supply disruption scenarios. Forecasts reflect documented assumptions regarding distributed workforce permanence and critical infrastructure operator compliance deadlines. Cross-checking against hyperscaler security capex disclosures and hospital system IT budget surveys is advised before commitment-grade decisions.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Privileged Identity Management Market
Security Software
Global Data Privacy Management Software Tools Market
Security Software
Video Intercom Devices and Equipment Market
Security Software
DC and PKI Market
Security Software
Remote Access Management Market
Security Software
Global Data Breach Notification Software Market
Security Software
Website Monitoring Software Market
Security Software
Intrusion Detection System / Intrusion Prevention System (IDS / IPS) Market
Security Software
Web Content Filtering Market
Security Software
Global Digital Signature Software Market
Security Software
DNS Protection Software Market
Security Software
Mobile Data Protection Solutions and Services Market
Security Software
Doorbell Camera Market
Security Software
Identity-As-A-Service (Idaas) Market
Security Software
Unified Threat Management (UTM) Market
Security Software
Information Rights Management Market