
 Global Health IT Security Market | 2026-2036
Global Health IT Security Market Size, Share, and Industry Trends Forecast 2026-2036
Global Health IT Security Market Foresight
Multi-source vendor consolidation is expanding across enterprise health systems as CISOs reduce fragmentation in threat-response workflows. Cisco Systems Inc. dominates network-layer security deployments across integrated delivery networks. Palo Alto Networks leverages cloud-native segmentation for telemedicine infrastructure. CrowdStrike specializes in endpoint detection for clinical workstations and connected medical devices.
Health IT security encompasses the technologies, policies, and operational protocols that protect electronic health records, medical devices, and clinical networks from unauthorized access, disruption, or data exfiltration. Core functional parameters include real-time anomaly detection thresholds measured in milliseconds, AES-256 encryption standards for data at rest, and role-based access controls mapped to clinical workflow hierarchies. Identity and access management solutions capture the largest margin pools as health systems migrate from legacy Active Directory to biometric-multi-factor authentication stacks. Cloud-based deployment is displacing on-premises architectures fastest among telemedicine providers operating distributed clinician networks. Endpoint protection remains mature in hospital settings but underpenetrated in diagnostic imaging centers with legacy Windows-based modalities.
FDA cybersecurity guidance for premarket medical devices, HIPAA Security Rule enforcement by the Department of Health and Human Services, and the EU AI Act's risk-classification framework for clinical decision-support algorithms are collectively elevating baseline procurement standards. These frameworks compel vendors to embed security-by-design documentation into product development cycles and restrict market access for uncertified platforms. Stakeholders must monitor how NIST's forthcoming health sector cybersecurity framework revisions reshape liability allocation between software vendors and health system operators.
Market Dynamics
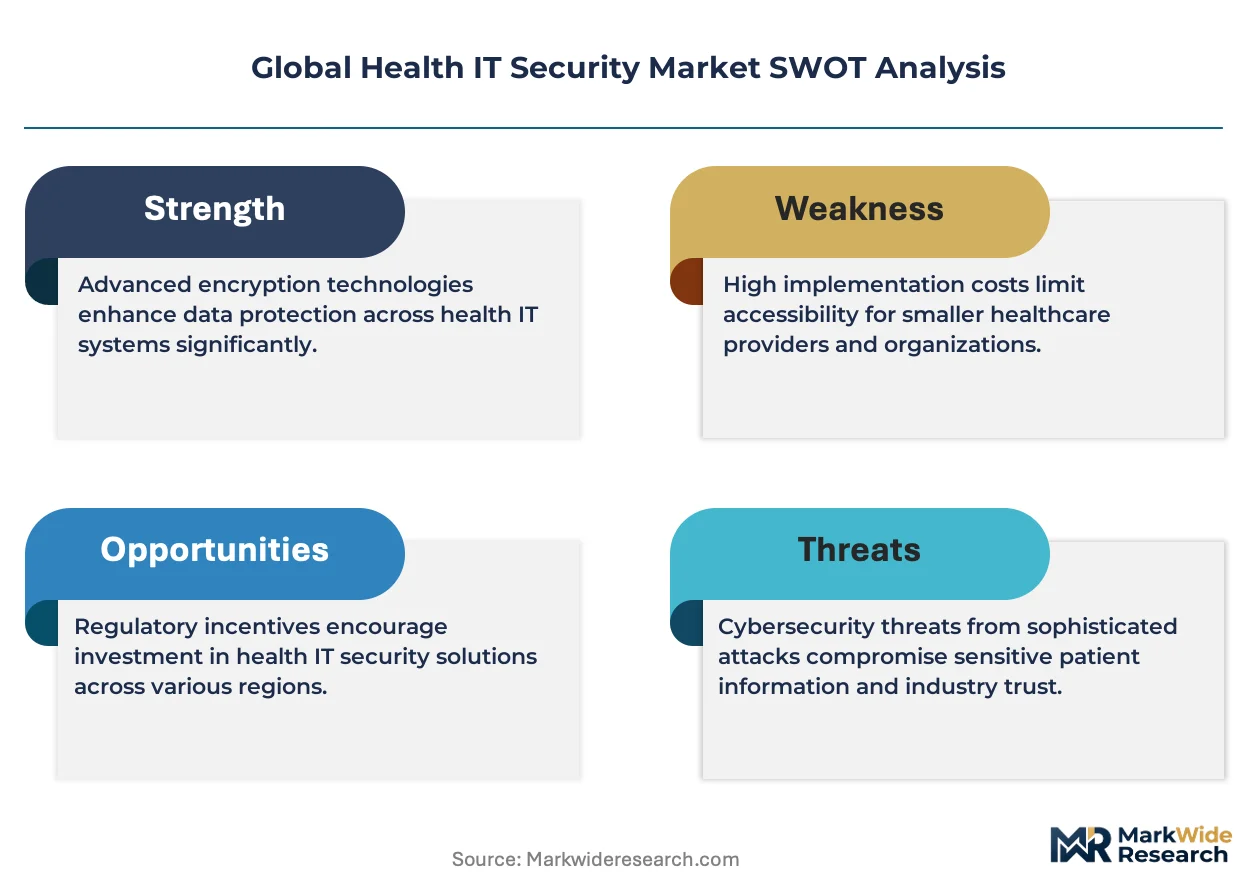
Zero-trust architecture mandates from hospital network CISOs are compressing procurement cycles and forcing vendor consolidation across integrated delivery networks.
Growth Catalysts
- EU AI Act risk-classification framework:Clinical decision-support algorithms now face mandatory pre-market conformity assessments, creating procurement pull for certified security-by-design platforms.
- Telemedicine infrastructure expansion:Distributed clinician networks require cloud-native segmentation tools that enforce micro-perimeters around patient data flows.
- Germany's university hospital consortia:Consolidated vendor relationships in Bavaria and Baden-Württemberg are establishing template procurement frameworks across Central Europe.
Market Restraints
- Legacy Windows-based diagnostic imaging modalities:Capital replacement cycles for MRI and CT workstations lag endpoint protection refresh timelines by four to seven years.
- HIPAA Security Rule enforcement variance:Inconsistent penalty structures across US Department of Health and Human Services regional offices create compliance-cost uncertainty.
- Biometric sensor supply concentration:Fingerprint and iris-scan hardware depends on Taiwanese and South Korean component manufacturers facing export-license bottlenecks.
Strategic Opportunities
- India's hospital digitization:Ayushman Bharat Health Account infrastructure creates greenfield demand for identity and access management stacks in tier-two cities.
- Convergence of AI inference and edge security:On-device anomaly detection for connected medical devices merges NVIDIA Clara deployments with runtime threat monitoring.
- Brazil's ANVISA cybersecurity resolution:Mandatory incident reporting for Class III and IV medical devices opens compliance-service revenue streams for regional integrators.
Industry Challenges
- Millisecond-latency detection engineering:Real-time anomaly thresholds for surgical robot networks require specialized firmware talent scarce outside Israel and Finland.
- NIST health sector framework revision timing:Pending liability-allocation rules between software vendors and hospital operators freeze multi-year security architecture commitments.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Health IT Security Market |
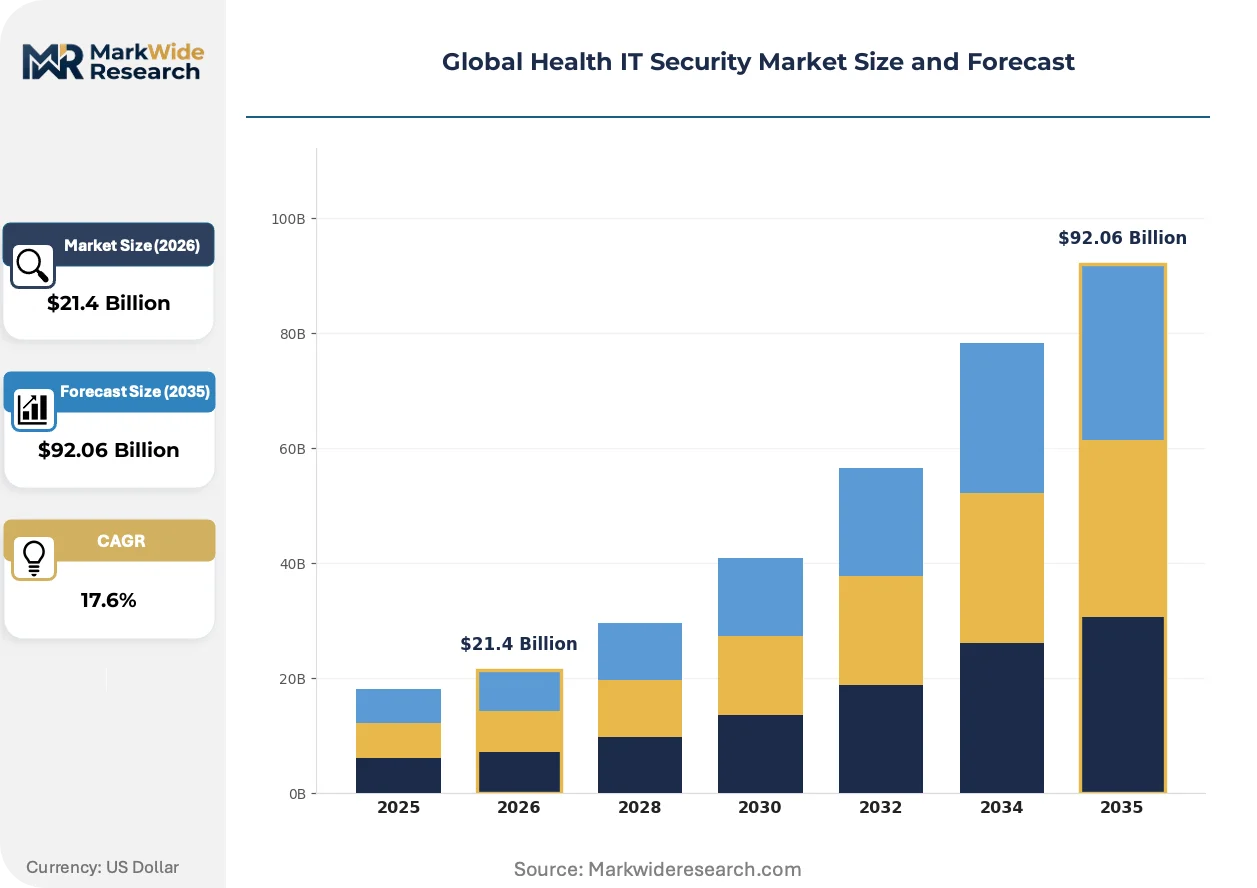
| Market Size in 2026 | $21.4 Billion |
| Market Size in 2035 | $92.06 Billion |
| CAGR (2026 – 2036) | 17.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution/Offering: Firewall Systems, Encryption Tools, Identity & Access Management, Intrusion Detection Systems, Endpoint Protection Deployment: On-Premises, Cloud-Based, Hybrid, Managed Security Services Application: Patient Data Protection, Network Security, Mobile Device Management, Compliance Management, Risk Assessment End User: Hospitals, Telemedicine Providers, Health Insurance Firms, Diagnostic Centers, Research Institutions |
| Companies Covered | IBM Corporation, Cisco Systems Inc., Palo Alto Networks, Fortinet Inc., AO Kaspersky Lab, McAfee LLC, CrowdStrike, Trend Micro Incorporated, Check Point Software Technologies, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Health IT Security Market Shifts & Advancements
Security-by-design documentation is becoming a non-negotiable procurement filter as pre-market certification requirements harden across FDA, EMA, and NMPA jurisdictions.
Confidential computing architectures for multi-party health data analytics are absorbing hardware-based trusted execution environments from cloud providers. Pharmaceutical consortiums running federated machine-learning on patient cohorts are adopting Intel SGX and AMD SEV enclaves at contract signature. This silicon-layer security is absorbing liability concerns that previously blocked cross-institutional data sharing.
Japan's PMDA issued draft cybersecurity guidance for software as a medical device in March, mandating structured threat-modeling documentation for SaMD submissions. Domestic manufacturers must now embed SBOM generation into CI/CD pipelines before market authorization. Cardiology and radiology AI tools face the steepest compliance ramps, with several Tokyo-based startups restructuring quality-management systems.
Subscription-based security operations center services are displacing perpetual-license endpoint protection in US community hospital systems. Rural facilities with limited internal security staff favor managed detection and response contracts with guaranteed mean-time-to-response clauses. This preference compression is visible across Kansas, Nebraska, and Oklahoma health networks where CISO roles remain unfilled.
Global Health IT Security Market Segmentation
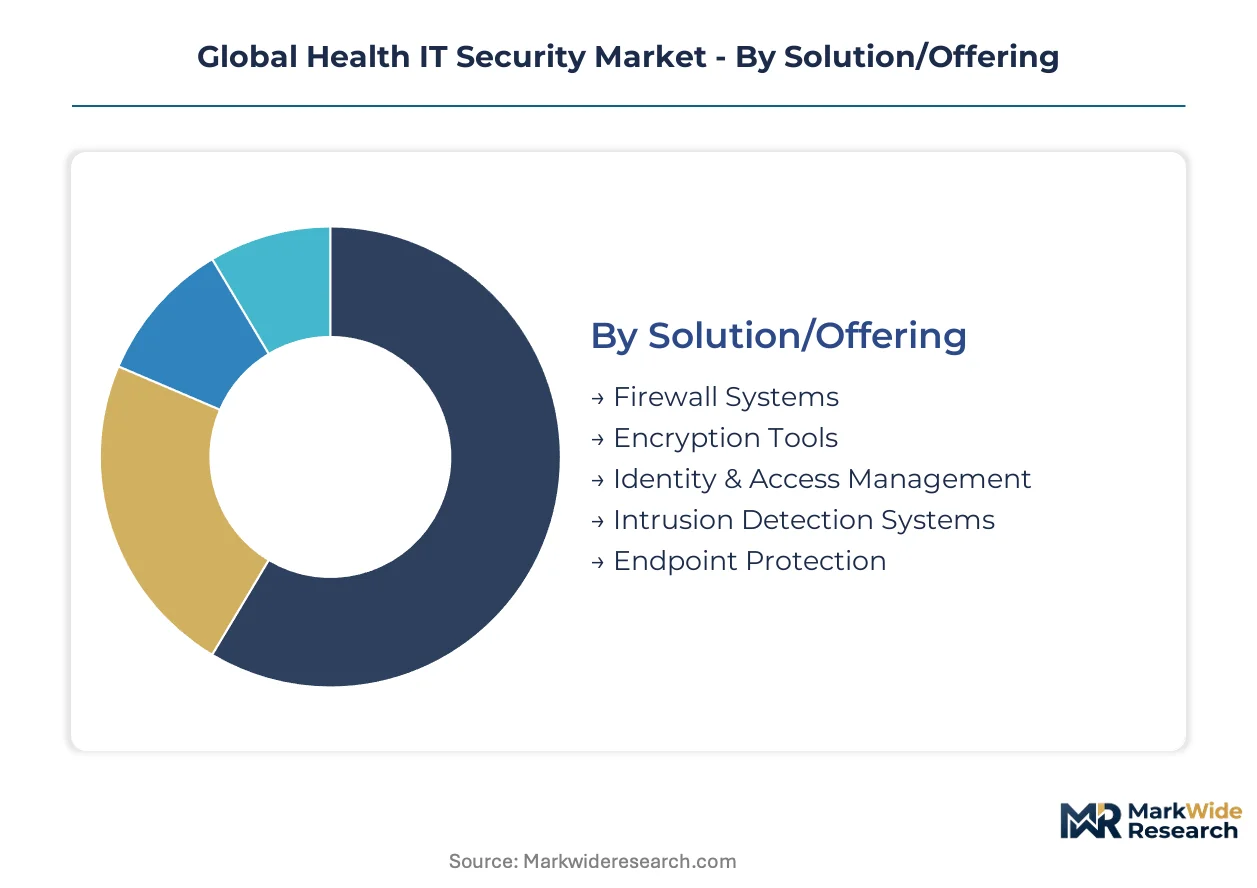
Health IT security procurement patterns diverge sharply across solution architectures, deployment models, and institutional risk profiles. CISOs segment vendor selection by latency tolerance, legacy infrastructure constraints, and regulatory exposure rather than generic feature checklists.
Solution/Offering:
Volume deployments concentrate in perimeter defense tools, while premium margins flow to identity-centric platforms requiring biometric integration.
- Identity & Access Management:Biometric-multi-factor authentication stacks with FIDO2 compliance capture the largest margin pools as health systems abandon legacy Active Directory. Demand concentrates in Germany's university hospital consortia, where consolidated procurement frameworks mandate zero-trust credential architectures.
- Encryption Tools:AES-256 implementations for data at rest and TLS 1.3 for data in transit form the baseline procurement filter across FDA and EMA jurisdictions. Deployment is accelerating among telemedicine providers in the United States operating distributed clinician networks with cross-border patient flows.
- Firewall Systems:Next-generation platforms with application-layer inspection for HL7 and DICOM traffic.
- Intrusion Detection Systems:Millisecond-latency anomaly detection for surgical robot networks and connected medical devices.
- Endpoint Protection:Mature in hospital settings but underpenetrated in diagnostic imaging centers with legacy Windows-based modalities.
Mature deployment sits with Firewall Systems. Newer deployment is concentrated in Identity & Access Management.
Deployment:
Cloud-native architectures are displacing on-premises installations fastest among telemedicine providers, while hybrid models dominate integrated delivery networks with mixed legacy-modern infrastructure.
- Cloud-Based:Micro-segmentation tools enforce perimeters around patient data flows in distributed clinician networks. Demand is climbing the fastest among telemedicine providers operating across state and national boundaries where data residency requirements complicate single-tenant architectures.
- Managed Security Services:Subscription-based SOC offerings with guaranteed mean-time-to-response clauses are displacing perpetual licenses in US community hospital systems. Concentrated demand appears across Kansas, Nebraska, and Oklahoma health networks where CISO roles remain unfilled.
- On-Premises:Air-gapped deployments for Class III medical device networks requiring FDA cybersecurity guidance compliance.
- Hybrid:Split architectures preserving on-premises control for imaging modalities while cloud-enabling analytics workloads.
Established procurement favors On-Premises for capital-intensive imaging infrastructure. Expansion is sharpest in Managed Security Services.
Application:
Compliance-driven applications command budget priority, while risk quantification tools face longer sales cycles due to ROI measurement complexity.
- Patient Data Protection:Real-time de-identification pipelines and audit logging for HIPAA and GDPR compliance. Demand concentrates in EU member states implementing the EU AI Act's risk-classification framework for clinical decision-support algorithms handling protected health information.
- Compliance Management:Automated evidence collection for FDA premarket submissions, HIPAA Security Rule attestations, and EU MDR technical documentation. Deployment is gaining share fastest among medical device manufacturers restructuring quality-management systems for Japan's PMDA cybersecurity guidance.
- Network Security:Zero-trust segmentation for clinical networks spanning multiple facilities.
- Mobile Device Management:Containerization for bring-your-own-device policies among home health nursing staff.
- Risk Assessment:Quantitative cyber risk modeling for cyber insurance procurement and board reporting.
Concentrated investment targets Patient Data Protection. Emerging demand is shifting toward Risk Assessment.
End User:
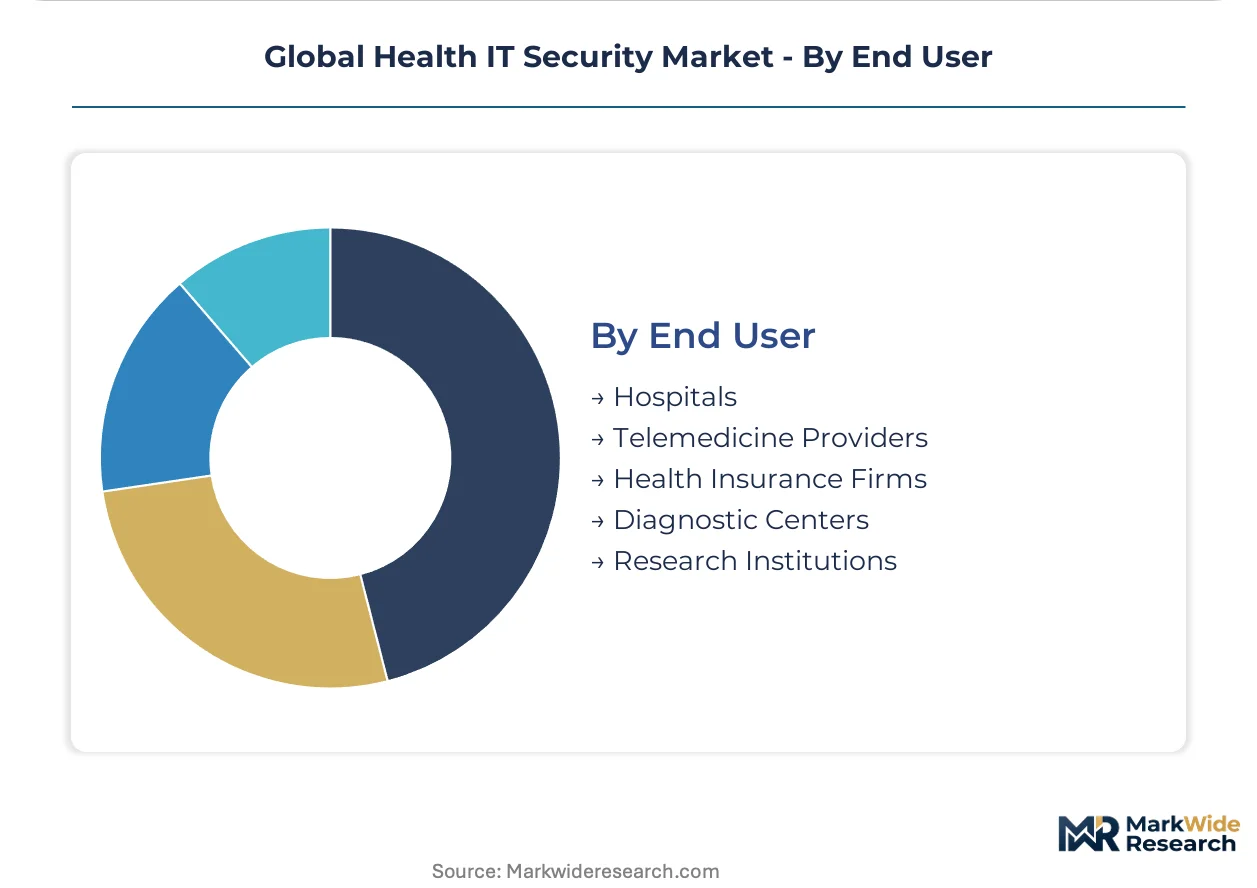
Hospital networks drive solution complexity requirements, while diagnostic centers prioritize cost-minimized endpoint protection due to capital replacement cycle constraints.
- Hospitals:Integrated delivery networks with zero-trust architecture mandates compressing procurement cycles and forcing vendor consolidation. Bavaria and Baden-Württemberg university hospital consortia are establishing template frameworks replicated across Central Europe.
- Telemedicine Providers:Cloud-native security stacks supporting distributed clinician networks with sub-50ms latency requirements for real-time video consultation. Expansion is steepest among platforms operating across Brazil, where ANVISA cybersecurity resolution mandates incident reporting for connected devices.
- Diagnostic Centers:Legacy Windows-based MRI and CT workstations with endpoint protection lagging hospital refresh timelines.
- Health Insurance Firms:Fraud detection integration with claims processing systems and member portal security.
- Research Institutions:Confidential computing for multi-party health data analytics using hardware enclaves.
Deep integration sits with Hospitals. Fastest uptake is appearing in Telemedicine Providers.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Silicon Valley's cybersecurity talent density anchors North American health IT security innovation, while German precision engineering clusters and Israeli military-derived technology ecosystems supply critical threat-detection capabilities to hospital networks worldwide.
United States
Hospital CISOs at integrated delivery networks in Texas and California are compressing procurement cycles for zero-trust architecture platforms. HIPAA enforcement actions by the Department of Health and Human Services tightened penalty structures for patient data breaches in 2023. The Mayo Clinic in Rochester, Minnesota, established a template vendor-consolidation framework now replicated across Midwestern health systems.
Germany
University hospital consortia in Bavaria and Baden-Württemberg are consolidating cybersecurity vendor relationships around biometric-multi-factor authentication stacks. The EU AI Act's risk-classification framework mandates pre-market conformity assessments for clinical decision-support algorithms. Berlin's Charité hospital network is deploying cloud-native segmentation tools for distributed telemedicine infrastructure.
Israel
Surgical robot manufacturers and connected medical device developers source millisecond-latency anomaly detection firmware from Tel Aviv and Haifa engineering clusters. The country's national cyber directorate publishes threat-intelligence briefings adopted by FDA premarket review teams. CyberArk and Check Point alumni populate startup ecosystems supplying endpoint protection to US diagnostic imaging centers.
Japan
PMDA's March draft cybersecurity guidance for software as a medical device is restructuring quality-management systems at Tokyo-based cardiology AI startups. METI funding programs accelerate confidential computing adoption for multi-party health data analytics. Osaka's pharmaceutical consortiums are piloting Intel SGX enclaves for federated machine-learning on patient cohorts.
Brazil
Telemedicine platforms operating across São Paulo and Rio de Janeiro states face ANVISA cybersecurity resolution mandates for incident reporting on Class III and IV medical devices. The national health surveillance agency's compliance requirements are opening revenue streams for regional security integrators. Hospital Albert Einstein in São Paulo established a managed detection and response contract template for community hospital systems.
Global Health IT Security Market Competitive Landscape
Global majors compete with regional champions across threat-detection specialization and geographic proximity to hospital procurement centers. The vendor base stratifies into three tiers: network-layer incumbents with integrated delivery network relationships, cloud-native specialists capturing telemedicine infrastructure contracts, and endpoint protection vendors serving diagnostic imaging centers. Dominant competitive moves include vendor consolidation through zero-trust architecture mandates and strategic partnerships with medical device manufacturers for security-by-design documentation.
Within the network-security archetype, Cisco Systems Inc. exemplifies the incumbent position through its dominance across US hospital network-layer deployments. Palo Alto Networks occupies the cloud-native segmentation tier for telemedicine infrastructure. CrowdStrike represents the endpoint-detection specialization for clinical workstations and connected medical devices.
| Leading Market Players |
|---|
| IBM Corporation |
| Cisco Systems Inc. |
| Palo Alto Networks |
| Fortinet Inc. |
| AO Kaspersky Lab |
| McAfee LLC |
| CrowdStrike |
| Trend Micro Incorporated |
| Check Point Software Technologies |
| Others |
Supply & Pricing Matrix
Private-equity-rolled-up managed security service providers anchor supply consolidation across US community hospital systems, translating fragmented endpoint protection procurement into subscription-based SOC contracts with guaranteed response-time clauses. This ownership pattern compresses vendor margins while concentrating pricing power with platforms that embed biometric hardware and cloud-native segmentation into unified offerings.
Pricing Analysis
Warranty and service bundling separates premium-tier zero-trust architecture deployments from unbundled endpoint protection licenses sold to diagnostic imaging centers. Three-tier pricing structure across premium, standard, and economy levels reflects certification grade differentiation, with FDA cybersecurity guidance compliance and EU AI Act conformity assessments commanding substantial premiums. Cost compression in standard-tier firewall systems is intensifying because Taiwanese biometric sensor manufacturers face export-license bottlenecks. Diagnostic imaging centers with legacy Windows-based modalities exhibit the highest price sensitivity, while integrated delivery networks pursuing vendor consolidation show the least.
Supply Chain Analysis
Reverse-logistics flows for surgical robot firmware and connected medical device security patches remain underdeveloped, with most vendors lacking structured refurbishment programs for deprecated threat-detection modules. Hardware-based trusted execution environments draw from Taiwan, South Korea, and Israel, while biometric sensor components rest on South Korean and Taiwanese manufacturing clusters. Firmware engineering talent scarcity in millisecond-latency anomaly detection creates single-source vulnerability for surgical network deployments. Distribution runs through hospital GPO contracts and direct enterprise sales to integrated delivery networks, with regional security integrators capturing emerging market share in Brazil and India.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Vertical integration into biometric hardware manufacturing and confidential computing silicon represents the critical upstream lever that security vendors are racing to control, as hardware-layer trust anchors become non-negotiable procurement filters.
For Market Incumbents: To counter cloud-native specialists capturing telemedicine infrastructure contracts, Cisco Systems and Palo Alto Networks should deepen backward integration into FIDO2-compliant biometric authentication hardware. Incumbents must also secure exclusive partnerships with medical device manufacturers for embedded security-by-design documentation, locking out uncertified competitors from FDA premarket submission workflows. For New Entrants and Emerging Players: Rural US community hospital systems with unfilled CISO roles present the most penetrable buyer archetype for subscription-based managed detection and response offerings. New entrants should target tier-two Indian cities where Ayushman Bharat Health Account infrastructure creates greenfield identity and access management demand, entering through regional system integrators with established hospital relationships rather than direct enterprise sales. For Investors and Strategic Acquirers: NIST's forthcoming health sector cybersecurity framework revision is the leading indicator that liability allocation rules between software vendors and hospital operators will reshape M&A valuations across the analysis window. Acquisition targets should display vertical integration into firmware-layer security for connected medical devices, with particular emphasis on Israeli engineering clusters where millisecond-latency detection talent concentrates. Practitioners should monitor FDA enforcement action patterns and EU AI Act premarket certification timelines for early signals of vendor consolidation acceleration.| Strategic Initiative | Industry Significance |
|---|---|
| Security-by-Design Partnership | Embedded FDA documentation requirements lock out uncertified competitors from hospital procurement cycles. |
| Biometric Hardware Integration | Backward control over FIDO2-compliant authentication stacks captures margin pools abandoned by software-only vendors. |
| Confidential Computing Deployment | Intel SGX and AMD SEV enclaves enable pharmaceutical federated learning contracts previously blocked by liability concerns. |
| Regional Integrator Acquisition | Brazilian and Indian security integrators hold ANVISA and Ayushman Bharat compliance relationships that accelerate market entry. |
| Zero-Trust Architecture Consolidation | Template procurement frameworks at Mayo Clinic and Charité hospital networks establish replicable vendor consolidation playbooks. |
Research Methodology
Trade association data, regulatory filings, and customs records anchored secondary inputs for this analysis, combining primary interviews with hospital CISOs, biomedical engineers, GPO contracts managers, and medical device quality assurance leads with bottom-up and top-down triangulation. FDA 510(k) submissions, EU MDR technical documentation databases, HIPAA breach notification archives, and ANVISA cybersecurity resolution compliance records provided structured secondary validation. Primary fieldwork captured procurement cycle compression patterns and vendor consolidation dynamics across integrated delivery networks.
Granularity-level modeling deployed solution architecture, deployment model, application compliance driver, and end-user institutional type as core segmentation dimensions, with regional regulatory cluster and latency tolerance threshold added as health IT security-specific forecast inputs. CAGRs were derived through demand-side penetration modeling and supply-side capacity assessment across the analysis window, incorporating telemedicine infrastructure expansion rates and medical device connectivity adoption curves as industry-specific forecast inputs.
Revisions become necessary when NIST health sector framework liability allocation rules, EU AI Act enforcement patterns, or biometric sensor export-license restrictions materialize differently than modeled assumptions anticipate. Forecasts reflect documented assumptions about zero-trust architecture mandate adoption curves and cloud-native displacement rates. Practitioners should monitor FDA premarket cybersecurity guidance updates and German university hospital consortium procurement template diffusion for early signals.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Health Informatics
Healthcare Automatic Identification and Data Capture (AIDC) Market
Health Informatics
Healthcare Laboratory Informatics Market
Health Informatics
Healthcare or Medical Analytics Market
Health Informatics
Global Laboratory Information Management System (LIMS) Market
Health Informatics
United States Healthcare Fraud Detection Market
Health Informatics
Artificial Intelligence (AI) Healthcare Market
Health Informatics
Global Laboratory Information System Market
Health Informatics
Global Ambulatory EHR Market
Health Informatics
Healthcare Application Programming Interfaces Market
Health Informatics
North America Laboratory Information System Market
Health Informatics
Laboratory Informatics Market
Health Informatics
Healthcare Prescriptive Analytics Market
Health Informatics
Healthcare Human Resources (HR) Software Market
Health Informatics
IHE XDS.B Market
Health Informatics
Global Healthcare Business Intelligence (BI) Market
Health Informatics
North America Artificial Intelligence in Healthcare Market